ReactOS 0.4.17-dev-1218-gfae4549
proc.c File Reference
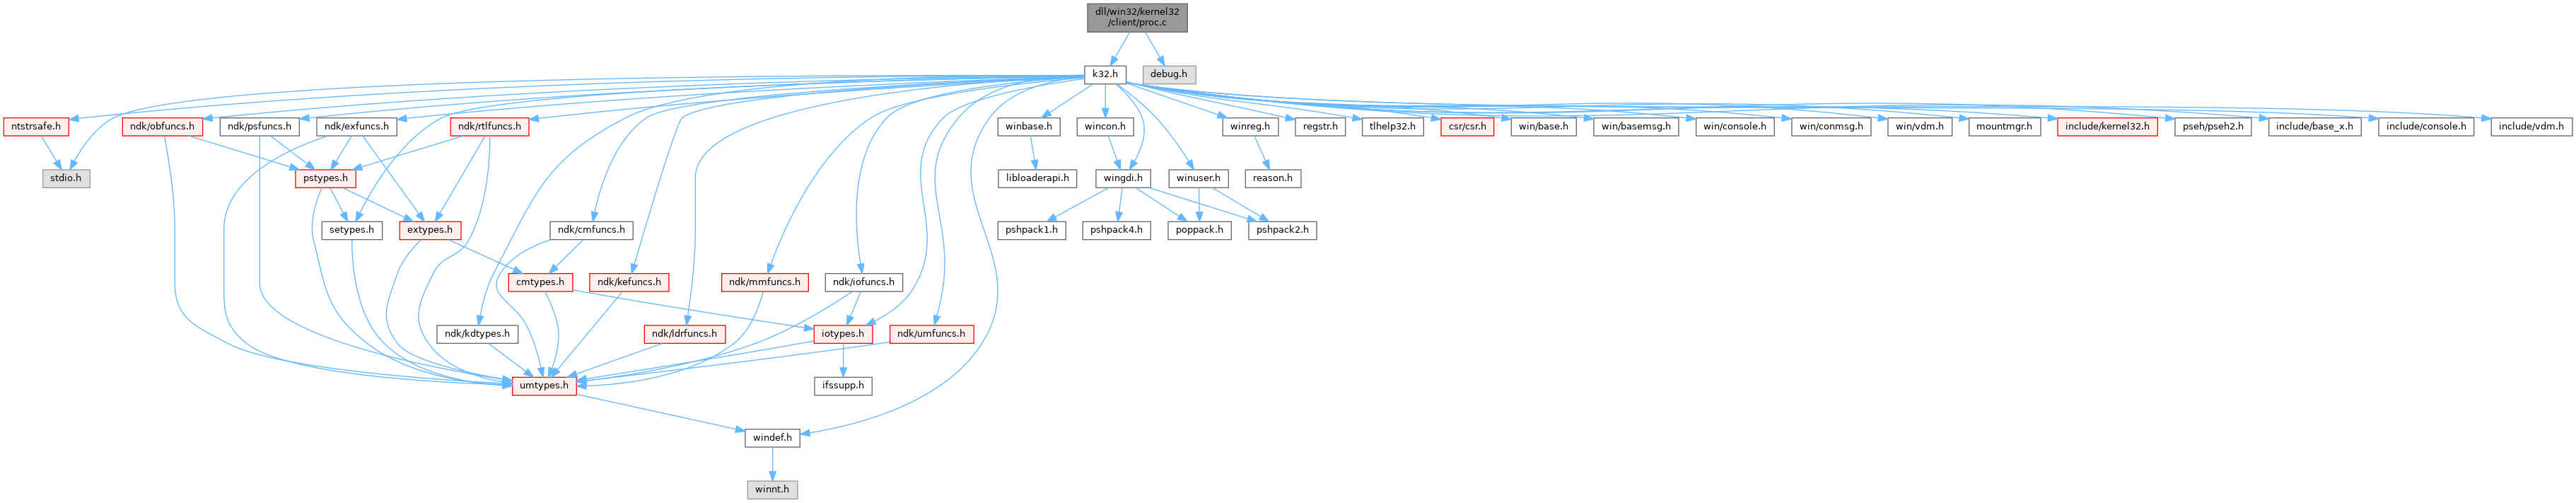
#include <k32.h>
#include <debug.h>
Include dependency graph for proc.c:

Go to the source code of this file.

Macros

#define NDEBUG
 
#define THREAD_ALL_ACCESS_NT6   (STANDARD_RIGHTS_REQUIRED|SYNCHRONIZE|0xFFFF)
 
#define CMD_STRING   L"cmd /c "
 
#define THEONLYGROUP   0
 
#define AddToHandle(x, y)   ((x) = (HANDLE)((ULONG_PTR)(x) | (y)))
 
#define RemoveFromHandle(x, y)   ((x) = (HANDLE)((ULONG_PTR)(x) & ~(y)))
 

Functions

VOID WINAPI RegisterWaitForInputIdle (WaitForInputIdleType lpfnRegisterWaitForInputIdle)
 
VOID WINAPI StuffStdHandle (IN HANDLE ProcessHandle, IN HANDLE StandardHandle, IN PHANDLE Address)
 
BOOLEAN WINAPI BuildSubSysCommandLine (IN LPCWSTR SubsystemName, IN LPCWSTR ApplicationName, IN LPCWSTR CommandLine, OUT PUNICODE_STRING SubsysCommandLine)
 
BOOLEAN WINAPI BasepIsImageVersionOk (IN ULONG ImageMajorVersion, IN ULONG ImageMinorVersion)
 
NTSTATUS WINAPI BasepCheckWebBladeHashes (IN HANDLE FileHandle)
 
NTSTATUS NTAPI BasepSaveAppCertRegistryValue (IN PLIST_ENTRY List, IN PWCHAR ComponentName, IN PWCHAR DllName)
 
NTSTATUS NTAPI BasepConfigureAppCertDlls (IN PWSTR ValueName, IN ULONG ValueType, IN PVOID ValueData, IN ULONG ValueLength, IN PVOID Context, IN PVOID EntryContext)
 
NTSTATUS WINAPI BasepIsProcessAllowed (IN LPWSTR ApplicationName)
 
NTSTATUS WINAPI BasepReplaceProcessThreadTokens (IN HANDLE TokenHandle, IN HANDLE ProcessHandle, IN HANDLE ThreadHandle)
 
VOID WINAPI BasepSxsCloseHandles (IN PBASE_MSG_SXS_HANDLES Handles)
 
DECLSPEC_NORETURN VOID WINAPI BaseProcessStartup (_In_ PPROCESS_START_ROUTINE lpStartAddress)
 
BOOLEAN WINAPI BasePushProcessParameters (IN ULONG ParameterFlags, IN HANDLE ProcessHandle, IN PPEB RemotePeb, IN LPCWSTR ApplicationPathName, IN LPWSTR lpCurrentDirectory, IN LPWSTR lpCommandLine, IN LPVOID lpEnvironment, IN LPSTARTUPINFOW StartupInfo, IN DWORD CreationFlags, IN BOOL InheritHandles, IN ULONG ImageSubsystem, IN PVOID AppCompatData, IN ULONG AppCompatDataSize)
 
VOID WINAPI InitCommandLines (VOID)
 
BOOL WINAPI GetProcessAffinityMask (IN HANDLE hProcess, OUT PDWORD_PTR lpProcessAffinityMask, OUT PDWORD_PTR lpSystemAffinityMask)
 
BOOL WINAPI SetProcessAffinityMask (IN HANDLE hProcess, IN DWORD_PTR dwProcessAffinityMask)
 
WORD WINAPI GetActiveProcessorGroupCount (VOID)
 
static DWORD GetProcessorCountInfo (IN WORD GroupNumber, IN BOOL Maximum)
 
DWORD WINAPI GetActiveProcessorCount (IN WORD GroupNumber)
 
DWORD WINAPI GetMaximumProcessorCount (IN WORD GroupNumber)
 
BOOL WINAPI GetProcessShutdownParameters (OUT LPDWORD lpdwLevel, OUT LPDWORD lpdwFlags)
 
BOOL WINAPI SetProcessShutdownParameters (IN DWORD dwLevel, IN DWORD dwFlags)
 
BOOL WINAPI GetProcessWorkingSetSizeEx (IN HANDLE hProcess, OUT PSIZE_T lpMinimumWorkingSetSize, OUT PSIZE_T lpMaximumWorkingSetSize, OUT PDWORD Flags)
 
BOOL WINAPI GetProcessWorkingSetSize (IN HANDLE hProcess, OUT PSIZE_T lpMinimumWorkingSetSize, OUT PSIZE_T lpMaximumWorkingSetSize)
 
BOOL WINAPI SetProcessWorkingSetSizeEx (IN HANDLE hProcess, IN SIZE_T dwMinimumWorkingSetSize, IN SIZE_T dwMaximumWorkingSetSize, IN DWORD Flags)
 
BOOL WINAPI SetProcessWorkingSetSize (IN HANDLE hProcess, IN SIZE_T dwMinimumWorkingSetSize, IN SIZE_T dwMaximumWorkingSetSize)
 
BOOL WINAPI GetProcessTimes (IN HANDLE hProcess, IN LPFILETIME lpCreationTime, IN LPFILETIME lpExitTime, IN LPFILETIME lpKernelTime, IN LPFILETIME lpUserTime)
 
HANDLE WINAPI GetCurrentProcess (VOID)
 
HANDLE WINAPI GetCurrentThread (VOID)
 
DWORD WINAPI GetCurrentProcessId (VOID)
 
BOOL WINAPI GetExitCodeProcess (IN HANDLE hProcess, IN LPDWORD lpExitCode)
 
DWORD WINAPI GetProcessId (IN HANDLE Process)
 
HANDLE WINAPI OpenProcess (IN DWORD dwDesiredAccess, IN BOOL bInheritHandle, IN DWORD dwProcessId)
 
VOID WINAPI GetStartupInfoW (IN LPSTARTUPINFOW lpStartupInfo)
 
BOOL WINAPI FlushInstructionCache (IN HANDLE hProcess, IN LPCVOID lpBaseAddress, IN SIZE_T nSize)
 
VOID WINAPI ExitProcess (IN UINT uExitCode)
 
BOOL WINAPI TerminateProcess (IN HANDLE hProcess, IN UINT uExitCode)
 
VOID WINAPI FatalAppExitA (UINT uAction, LPCSTR lpMessageText)
 
VOID WINAPI FatalAppExitW (IN UINT uAction, IN LPCWSTR lpMessageText)
 
VOID WINAPI FatalExit (IN int ExitCode)
 
DWORD WINAPI GetPriorityClass (IN HANDLE hProcess)
 
BOOL WINAPI SetPriorityClass (IN HANDLE hProcess, IN DWORD dwPriorityClass)
 
DWORD WINAPI GetProcessVersion (IN DWORD ProcessId)
 
BOOL WINAPI GetProcessIoCounters (IN HANDLE hProcess, OUT PIO_COUNTERS lpIoCounters)
 
BOOL WINAPI GetProcessPriorityBoost (IN HANDLE hProcess, OUT PBOOL pDisablePriorityBoost)
 
BOOL WINAPI SetProcessPriorityBoost (IN HANDLE hProcess, IN BOOL bDisablePriorityBoost)
 
BOOL WINAPI GetProcessHandleCount (IN HANDLE hProcess, OUT PDWORD pdwHandleCount)
 
BOOL WINAPI IsWow64Process (IN HANDLE hProcess, OUT PBOOL Wow64Process)
 
LPSTR WINAPI GetCommandLineA (VOID)
 
LPWSTR WINAPI GetCommandLineW (VOID)
 
BOOL NTAPI ReadProcessMemory (IN HANDLE hProcess, IN LPCVOID lpBaseAddress, IN LPVOID lpBuffer, IN SIZE_T nSize, OUT SIZE_T *lpNumberOfBytesRead)
 
BOOL NTAPI WriteProcessMemory (IN HANDLE hProcess, IN LPVOID lpBaseAddress, IN LPCVOID lpBuffer, IN SIZE_T nSize, OUT SIZE_T *lpNumberOfBytesWritten)
 
BOOL WINAPI ProcessIdToSessionId (IN DWORD dwProcessId, OUT PDWORD pSessionId)
 
 C_ASSERT (PROCESS_PRIORITY_CLASS_REALTIME==(PROCESS_PRIORITY_CLASS_HIGH+1))
 
BOOL WINAPI CreateProcessInternalW (IN HANDLE hUserToken, IN LPCWSTR lpApplicationName, IN LPWSTR lpCommandLine, IN LPSECURITY_ATTRIBUTES lpProcessAttributes, IN LPSECURITY_ATTRIBUTES lpThreadAttributes, IN BOOL bInheritHandles, IN DWORD dwCreationFlags, IN LPVOID lpEnvironment, IN LPCWSTR lpCurrentDirectory, IN LPSTARTUPINFOW lpStartupInfo, IN LPPROCESS_INFORMATION lpProcessInformation, OUT PHANDLE hNewToken)
 
BOOL WINAPI DECLSPEC_HOTPATCH CreateProcessW (LPCWSTR lpApplicationName, LPWSTR lpCommandLine, LPSECURITY_ATTRIBUTES lpProcessAttributes, LPSECURITY_ATTRIBUTES lpThreadAttributes, BOOL bInheritHandles, DWORD dwCreationFlags, LPVOID lpEnvironment, LPCWSTR lpCurrentDirectory, LPSTARTUPINFOW lpStartupInfo, LPPROCESS_INFORMATION lpProcessInformation)
 

Variables

UNICODE_STRING BaseUnicodeCommandLine
 
ANSI_STRING BaseAnsiCommandLine
 
UNICODE_STRING BasePathVariableName = RTL_CONSTANT_STRING(L"PATH")
 
PLDR_DATA_TABLE_ENTRY BasepExeLdrEntry
 
BOOLEAN g_AppCertInitialized
 
BOOLEAN g_HaveAppCerts
 
LIST_ENTRY BasepAppCertDllsList
 
RTL_CRITICAL_SECTION gcsAppCert
 
PBASEP_APPCERT_EMBEDDED_FUNC fEmbeddedCertFunc
 
NTSTATUS g_AppCertStatus
 
RTL_QUERY_REGISTRY_TABLE BasepAppCertTable [2]
 
PSAFER_REPLACE_PROCESS_THREAD_TOKENS g_SaferReplaceProcessThreadTokens
 
HMODULE gSaferHandle = (HMODULE)-1
 

Macro Definition Documentation

◆ AddToHandle

#define AddToHandle (   x,
  y 
)    ((x) = (HANDLE)((ULONG_PTR)(x) | (y)))

Definition at line 2126 of file proc.c.

◆ CMD_STRING

#define CMD_STRING   L"cmd /c "

Definition at line 51 of file proc.c.

◆ NDEBUG

#define NDEBUG

Definition at line 15 of file proc.c.

◆ RemoveFromHandle

#define RemoveFromHandle (   x,
  y 
)    ((x) = (HANDLE)((ULONG_PTR)(x) & ~(y)))

Definition at line 2127 of file proc.c.

◆ THEONLYGROUP

#define THEONLYGROUP   0

Definition at line 914 of file proc.c.

◆ THREAD_ALL_ACCESS_NT6

#define THREAD_ALL_ACCESS_NT6   (STANDARD_RIGHTS_REQUIRED|SYNCHRONIZE|0xFFFF)

Definition at line 18 of file proc.c.

Function Documentation

◆ BasepCheckWebBladeHashes()

NTSTATUS WINAPI BasepCheckWebBladeHashes ( IN HANDLE  FileHandle)

Definition at line 149 of file proc.c.

150{
152 CHAR Hash[16];
153
154 /* Get all the MD5 hashes */
156 if (!NT_SUCCESS(Status)) return Status;
157
158 /* Depending on which suite this is, run a bsearch and block the appropriate ones */
160 {
161 DPRINT1("Egad! This is a ReactOS Compute Server and we should prevent you from using certain APIs...but we won't.");
162 }
163 else if (SharedUserData->SuiteMask & VER_SUITE_STORAGE_SERVER)
164 {
165 DPRINT1("Gasp! This is a ReactOS Storage Server and we should prevent you from using certain APIs...but we won't.");
166 }
167 else if (SharedUserData->SuiteMask & VER_SUITE_BLADE)
168 {
169 DPRINT1("Golly! This is a ReactOS Web Blade Server and we should prevent you from using certain APIs...but we won't.");
170 }
171
172 /* Actually, fuck it, don't block anything, we're open source */
173 return STATUS_SUCCESS;
174}
LONG NTSTATUS
Definition: precomp.h:26
#define DPRINT1
Definition: precomp.h:8
#define NT_SUCCESS(StatCode)
Definition: apphelp.c:33
NTSYSAPI NTSTATUS NTAPI RtlComputeImportTableHash(IN HANDLE FileHandle, OUT PCHAR Hash, IN ULONG ImportTableHashSize)
Definition: libsupp.c:1202
static int Hash(const char *)
Definition: reader.c:2237
_Must_inspect_result_ _In_opt_ PFLT_INSTANCE _Out_ PHANDLE FileHandle
Definition: fltkernel.h:1231
Status
Definition: gdiplustypes.h:24
#define VER_SUITE_STORAGE_SERVER
#define VER_SUITE_COMPUTE_SERVER
#define VER_SUITE_BLADE
char CHAR
Definition: pedump.c:57
#define SharedUserData
#define STATUS_SUCCESS
Definition: shellext.h:65

Referenced by CreateProcessInternalW().

◆ BasepConfigureAppCertDlls()

NTSTATUS NTAPI BasepConfigureAppCertDlls ( IN PWSTR  ValueName,
IN ULONG  ValueType,
IN PVOID  ValueData,
IN ULONG  ValueLength,
IN PVOID  Context,
IN PVOID  EntryContext 
)

Definition at line 189 of file proc.c.

195{
196 /* Add this to the certification list */
198}
NTSTATUS NTAPI BasepSaveAppCertRegistryValue(IN PLIST_ENTRY List, IN PWCHAR ComponentName, IN PWCHAR DllName)
Definition: proc.c:178
_In_ GUID _In_ PVOID ValueData
Definition: hubbusif.h:312
_In_ PIRP _In_ PIO_COMPLETION_ROUTINE _In_ PVOID Context
Definition: kse.h:81
_Must_inspect_result_ _In_ WDFKEY _In_ PCUNICODE_STRING ValueName
Definition: wdfregistry.h:243

◆ BasepIsImageVersionOk()

BOOLEAN WINAPI BasepIsImageVersionOk ( IN ULONG  ImageMajorVersion,
IN ULONG  ImageMinorVersion 
)

Definition at line 123 of file proc.c.

125{
126 /* Accept images for NT 3.1 or higher */
127 if (ImageMajorVersion > 3 ||
128 (ImageMajorVersion == 3 && ImageMinorVersion >= 10))
129 {
130 /* ReactOS-specific: Accept images even if they are newer than our internal NT version. */
131 if (ImageMajorVersion > SharedUserData->NtMajorVersion ||
132 (ImageMajorVersion == SharedUserData->NtMajorVersion && ImageMinorVersion > SharedUserData->NtMinorVersion))
133 {
134 DPRINT1("Accepting image version %lu.%lu, although ReactOS is an NT %hu.%hu OS!\n",
135 ImageMajorVersion,
136 ImageMinorVersion,
137 SharedUserData->NtMajorVersion,
138 SharedUserData->NtMinorVersion);
139 }
140
141 return TRUE;
142 }
143
144 return FALSE;
145}
#define TRUE
Definition: types.h:120
#define FALSE
Definition: types.h:117

Referenced by CreateProcessInternalW().

◆ BasepIsProcessAllowed()

NTSTATUS WINAPI BasepIsProcessAllowed ( IN LPWSTR  ApplicationName)

Definition at line 202 of file proc.c.

203{
204 NTSTATUS Status, Status1;
206 UINT Length;
207 HMODULE TrustLibrary;
209 ULONG CertFlag;
210 PLIST_ENTRY NextEntry;
212 UNICODE_STRING CertKey = RTL_CONSTANT_STRING(L"\\Registry\\MACHINE\\System\\CurrentControlSet\\Control\\Session Manager\\AppCertDlls");
214
215 /* Try to initialize the certification subsystem */
216 while (!g_AppCertInitialized)
217 {
218 /* Defaults */
220 Buffer = NULL;
221
222 /* Acquire the lock while initializing and see if we lost a race */
224 if (g_AppCertInitialized) break;
225
226 /* On embedded, there is a special DLL */
227 if (SharedUserData->SuiteMask & VER_SUITE_EMBEDDEDNT)
228 {
229 /* Allocate a buffer for the name */
230 Buffer = RtlAllocateHeap(RtlGetProcessHeap(),
231 0,
232 MAX_PATH * sizeof(WCHAR) +
233 sizeof(UNICODE_NULL));
234 if (!Buffer)
235 {
236 /* Fail if no memory */
238 }
239 else
240 {
241 /* Now get the system32 directory in our buffer, make sure it fits */
242 Length = GetSystemDirectoryW(Buffer, MAX_PATH - sizeof("EmbdTrst.DLL"));
243 if ((Length) && (Length <= MAX_PATH - sizeof("EmbdTrst.DLL")))
244 {
245 /* Add a slash if needed, and add the embedded cert DLL name */
246 if (Buffer[Length - 1] != '\\') Buffer[Length++] = '\\';
248 L"EmbdTrst.DLL",
249 sizeof(L"EmbdTrst.DLL"));
250
251 /* Try to load it */
252 TrustLibrary = LoadLibraryW(Buffer);
253 if (TrustLibrary)
254 {
255 /* And extract the special function out of it */
256 fEmbeddedCertFunc = (PVOID)GetProcAddress(TrustLibrary,
257 "ImageOkToRunOnEmbeddedNT");
258 }
259 }
260
261 /* If we didn't get this far, set a failure code */
263 }
264 }
265 else
266 {
267 /* Other systems have a registry entry for this */
269 if (NT_SUCCESS(Status1))
270 {
271 /* Close it, we'll query it through Rtl */
273
274 /* Do the query, which will call a special callback */
276 L"Session Manager",
278 NULL,
279 NULL);
281 {
283 }
284 }
285 }
286
287 /* Free any buffer if we had one */
288 if (Buffer) RtlFreeHeap(RtlGetProcessHeap(), 0, Buffer);
289
290 /* Check for errors, or a missing embedded/custom certification DLL */
291 if (!NT_SUCCESS(Status) ||
293 {
294 /* The subsystem is not active on this machine, so give up */
297 }
298 else
299 {
300 /* We have certification DLLs active, remember this */
302 }
303
304 /* We are done the initialization phase, release the lock */
307 }
308
309 /* If there's no certification DLLs present, return the failure code */
310 if (!g_HaveAppCerts) return g_AppCertStatus;
311
312 /* Otherwise, assume success and make sure we have *something* */
315
316 /* If the something is an embedded certification DLL, call it and return */
318
319 /* Otherwise we have custom certification DLLs, parse them */
320 NextEntry = BasepAppCertDllsList.Flink;
321 CertFlag = 2;
322 while (NextEntry != &BasepAppCertDllsList)
323 {
324 /* Make sure the entry has a callback */
326 ASSERT(Entry->fPluginCertFunc != NULL);
327
328 /* Call it and check if it failed */
329 Status = Entry->fPluginCertFunc(ApplicationName, 1);
330 if (!NT_SUCCESS(Status)) CertFlag = 3;
331
332 /* Move on */
333 NextEntry = NextEntry->Flink;
334 }
335
336 /* Now loop them again */
337 NextEntry = BasepAppCertDllsList.Flink;
338 while (NextEntry != &BasepAppCertDllsList)
339 {
340 /* Make sure the entry has a callback */
342 ASSERT(Entry->fPluginCertFunc != NULL);
343
344 /* Call it, this time with the flag from the loop above */
345 Status = Entry->fPluginCertFunc(ApplicationName, CertFlag);
346 }
347
348 /* All done, return the status */
349 return Status;
350}
PVOID NTAPI RtlAllocateHeap(IN PVOID HeapHandle, IN ULONG Flags, IN SIZE_T Size)
Definition: heap.c:616
BOOLEAN NTAPI RtlFreeHeap(IN PVOID HeapHandle, IN ULONG Flags, IN PVOID HeapBase)
Definition: heap.c:634
Definition: bufpool.h:45
#define STATUS_NO_MEMORY
Definition: d3dkmdt.h:51
#define NULL
Definition: types.h:112
#define RTL_CONSTANT_STRING(s)
Definition: combase.c:35
#define GetProcAddress(x, y)
Definition: compat.h:753
#define MAX_PATH
Definition: compat.h:34
#define LoadLibraryW(x)
Definition: compat.h:747
UINT WINAPI GetSystemDirectoryW(OUT LPWSTR lpBuffer, IN UINT uSize)
Definition: path.c:2331
PBASEP_APPCERT_EMBEDDED_FUNC fEmbeddedCertFunc
Definition: proc.c:30
RTL_QUERY_REGISTRY_TABLE BasepAppCertTable[2]
Definition: proc.c:32
RTL_CRITICAL_SECTION gcsAppCert
Definition: proc.c:29
LIST_ENTRY BasepAppCertDllsList
Definition: proc.c:28
BOOLEAN g_AppCertInitialized
Definition: proc.c:26
BOOLEAN g_HaveAppCerts
Definition: proc.c:27
NTSTATUS g_AppCertStatus
Definition: proc.c:31
#define L(x)
Definition: resources.c:13
#define IsListEmpty(ListHead)
Definition: env_spec_w32.h:954
unsigned int UINT
Definition: sysinfo.c:13
#define ASSERT(a)
Definition: mode.c:44
PVOID PVOID PWCHAR ApplicationName
Definition: env.c:47
_Must_inspect_result_ _Out_ PNDIS_STATUS _In_ NDIS_HANDLE _In_ ULONG _Out_ PNDIS_STRING _Out_ PNDIS_HANDLE KeyHandle
Definition: ndis.h:4715
NTSYSAPI NTSTATUS NTAPI RtlEnterCriticalSection(_In_ PRTL_CRITICAL_SECTION CriticalSection)
NTSYSAPI NTSTATUS NTAPI RtlLeaveCriticalSection(_In_ PRTL_CRITICAL_SECTION CriticalSection)
#define RTL_REGISTRY_CONTROL
Definition: nt_native.h:163
NTSYSAPI NTSTATUS NTAPI NtOpenKey(OUT PHANDLE KeyHandle, IN ACCESS_MASK DesiredAccess, IN POBJECT_ATTRIBUTES ObjectAttributes)
Definition: ntapi.c:335
#define KEY_READ
Definition: nt_native.h:1026
NTSTATUS NTAPI NtClose(IN HANDLE Handle)
Definition: obhandle.c:3434
#define UNICODE_NULL
#define VER_SUITE_EMBEDDEDNT
_In_ ULONG _In_ ULONG _In_ ULONG Length
Definition: ntddpcm.h:102
#define RTL_CONSTANT_OBJECT_ATTRIBUTES(n, a)
short WCHAR
Definition: pedump.c:58
#define OBJ_CASE_INSENSITIVE
Definition: winternl.h:228
Entry
Definition: section.c:5216
Definition: kernel32.h:386
Definition: typedefs.h:120
struct _LIST_ENTRY * Flink
Definition: typedefs.h:121
void * PVOID
Definition: typedefs.h:50
#define RtlCopyMemory(Destination, Source, Length)
Definition: typedefs.h:263
uint16_t * PWCHAR
Definition: typedefs.h:56
#define CONTAINING_RECORD(address, type, field)
Definition: typedefs.h:260
uint32_t ULONG
Definition: typedefs.h:59
#define STATUS_UNSUCCESSFUL
Definition: udferr_usr.h:132
#define STATUS_OBJECT_NAME_NOT_FOUND
Definition: udferr_usr.h:149
_Must_inspect_result_ _In_ WDFDEVICE _In_ ULONG _In_ ACCESS_MASK _In_opt_ PWDF_OBJECT_ATTRIBUTES KeyAttributes
Definition: wdfdevice.h:2666
NTSYSAPI NTSTATUS WINAPI RtlQueryRegistryValues(ULONG, PCWSTR, PRTL_QUERY_REGISTRY_TABLE, PVOID, PVOID)

Referenced by CreateProcessInternalW().

◆ BasepReplaceProcessThreadTokens()

NTSTATUS WINAPI BasepReplaceProcessThreadTokens ( IN HANDLE  TokenHandle,
IN HANDLE  ProcessHandle,
IN HANDLE  ThreadHandle 
)

Definition at line 354 of file proc.c.

357{
359 ANSI_STRING SaferiReplaceProcessThreadTokens = RTL_CONSTANT_STRING("SaferiReplaceProcessThreadTokens");
360
361 /* Enter the application certification lock */
363
364 /* Check if we already know the function */
366 {
367 /* Call it */
370 ThreadHandle) ?
373 }
374 else
375 {
376 /* Check if the app certification DLL isn't loaded */
377 if (!(gSaferHandle) ||
378 (gSaferHandle == (HMODULE)-1) ||
379 (gSaferHandle == (HMODULE)-2))
380 {
381 /* Then we can't call the function */
383 }
384 else
385 {
386 /* We have the DLL, find the address of the Safer function */
388 &SaferiReplaceProcessThreadTokens,
389 0,
391 if (NT_SUCCESS(Status))
392 {
393 /* Found it, now call it */
396 ThreadHandle) ?
399 }
400 else
401 {
402 /* We couldn't find it, so this must be an unsupported DLL */
406 }
407 }
408 }
409
410 /* Release the lock and return the result */
412 return Status;
413}
HMODULE gSaferHandle
Definition: proc.c:46
PSAFER_REPLACE_PROCESS_THREAD_TOKENS g_SaferReplaceProcessThreadTokens
Definition: proc.c:45
NTSTATUS NTAPI LdrUnloadDll(_In_ PVOID BaseAddress)
Definition: ldrapi.c:1305
NTSTATUS NTAPI LdrGetProcedureAddress(_In_ PVOID BaseAddress, _In_opt_ _When_(Ordinal==0, _Notnull_) PANSI_STRING Name, _In_opt_ _When_(Name==NULL, _In_range_(>, 0)) ULONG Ordinal, _Out_ PVOID *ProcedureAddress)
Definition: ldrapi.c:789
_In_ HANDLE ProcessHandle
Definition: mmfuncs.h:407
_In_ ACCESS_MASK _In_ ULONG _Out_ PHANDLE TokenHandle
Definition: psfuncs.h:772
#define STATUS_ENTRYPOINT_NOT_FOUND
Definition: ntstatus.h:643

Referenced by CreateProcessInternalW().

◆ BaseProcessStartup()

DECLSPEC_NORETURN VOID WINAPI BaseProcessStartup ( _In_ PPROCESS_START_ROUTINE  lpStartAddress)

Definition at line 451 of file proc.c.

453{
455 {
456 /* Set our Start Address */
459 &lpStartAddress,
460 sizeof(PPROCESS_START_ROUTINE));
461
462 /* Call the Start Routine */
463 ExitThread(lpStartAddress());
464 }
466 {
467 /* Get the Exit code from the SEH Handler */
469 {
470 /* Kill the whole process, usually */
472 }
473 else
474 {
475 /* If running inside CSRSS, kill just this thread */
477 }
478 }
479 _SEH2_END;
480}
@ ThreadQuerySetWin32StartAddress
Definition: compat.h:944
BOOLEAN BaseRunningInServerProcess
Definition: dllmain.c:20
LONG WINAPI UnhandledExceptionFilter(IN PEXCEPTION_POINTERS ExceptionInfo)
Definition: except.c:269
VOID WINAPI ExitProcess(IN UINT uExitCode)
Definition: proc.c:1382
VOID WINAPI ExitThread(IN DWORD uExitCode)
Definition: thread.c:367
DWORD(WINAPI * PPROCESS_START_ROUTINE)(VOID)
Definition: kernel32.h:246
NTSTATUS NTAPI NtSetInformationThread(_In_ HANDLE ThreadHandle, _In_ THREADINFOCLASS ThreadInformationClass, _In_reads_bytes_(ThreadInformationLength) PVOID ThreadInformation, _In_ ULONG ThreadInformationLength)
Definition: query.c:2301
#define _SEH2_GetExceptionCode()
Definition: pseh2_64.h:204
#define _SEH2_EXCEPT(...)
Definition: pseh2_64.h:104
#define _SEH2_GetExceptionInformation()
Definition: pseh2_64.h:203
#define _SEH2_END
Definition: pseh2_64.h:194
#define _SEH2_TRY
Definition: pseh2_64.h:93
#define NtCurrentThread()
Definition: winternl.h:5372

Referenced by BaseInitializeContext().

◆ BasepSaveAppCertRegistryValue()

NTSTATUS NTAPI BasepSaveAppCertRegistryValue ( IN PLIST_ENTRY  List,
IN PWCHAR  ComponentName,
IN PWCHAR  DllName 
)

Definition at line 178 of file proc.c.

181{
182 /* Pretty much the only thing this key is used for, is malware */
185}
#define UNIMPLEMENTED
Definition: ntoskrnl.c:15
#define STATUS_NOT_IMPLEMENTED
Definition: d3dkmdt.h:42

Referenced by BasepConfigureAppCertDlls().

◆ BasepSxsCloseHandles()

VOID WINAPI BasepSxsCloseHandles ( IN PBASE_MSG_SXS_HANDLES  Handles)

Definition at line 417 of file proc.c.

418{
420
421 /* Sanity checks */
422 ASSERT(Handles != NULL);
423 ASSERT(Handles->Process == NULL || Handles->Process == NtCurrentProcess());
424
425 /* Close the file handle */
426 if (Handles->File)
427 {
428 Status = NtClose(Handles->File);
430 }
431
432 /* Close the section handle */
433 if (Handles->Section)
434 {
435 Status = NtClose(Handles->Section);
437 }
438
439 /* Unmap the section view */
440 if (Handles->ViewBase.QuadPart)
441 {
443 (PVOID)(ULONG_PTR)Handles->ViewBase.QuadPart);
445 }
446}
NTSTATUS NTAPI NtUnmapViewOfSection(IN HANDLE ProcessHandle, IN PVOID BaseAddress)
Definition: section.c:3505
#define NtCurrentProcess()
Definition: nt_native.h:1660
uint32_t ULONG_PTR
Definition: typedefs.h:65

Referenced by CreateProcessInternalW().

◆ BasePushProcessParameters()

BOOLEAN WINAPI BasePushProcessParameters ( IN ULONG  ParameterFlags,
IN HANDLE  ProcessHandle,
IN PPEB  RemotePeb,
IN LPCWSTR  ApplicationPathName,
IN LPWSTR  lpCurrentDirectory,
IN LPWSTR  lpCommandLine,
IN LPVOID  lpEnvironment,
IN LPSTARTUPINFOW  StartupInfo,
IN DWORD  CreationFlags,
IN BOOL  InheritHandles,
IN ULONG  ImageSubsystem,
IN PVOID  AppCompatData,
IN ULONG  AppCompatDataSize 
)

Definition at line 484 of file proc.c.

497{
498 WCHAR FullPath[MAX_PATH + 5];
499 PWCHAR Remaining, DllPathString, ScanChar;
500 PRTL_USER_PROCESS_PARAMETERS ProcessParameters, RemoteParameters;
501 PVOID RemoteAppCompatData;
502 UNICODE_STRING DllPath, ImageName, CommandLine, CurrentDirectory;
505 ULONG EnviroSize;
506 SIZE_T Size;
507 BOOLEAN HavePebLock = FALSE, Result;
509
510 /* Get the full path name */
511 Size = GetFullPathNameW(ApplicationPathName,
512 MAX_PATH + 4,
513 FullPath,
514 &Remaining);
515 if ((Size) && (Size <= (MAX_PATH + 4)))
516 {
517 /* Get the DLL Path */
518 DllPathString = BaseComputeProcessDllPath(FullPath, lpEnvironment);
519 if (!DllPathString)
520 {
521 /* Fail */
523 return FALSE;
524 }
525
526 /* Initialize Strings */
527 RtlInitUnicodeString(&DllPath, DllPathString);
528 RtlInitUnicodeString(&ImageName, FullPath);
529 }
530 else
531 {
532 /* Couldn't get the path name. Just take the original path */
533 DllPathString = BaseComputeProcessDllPath((LPWSTR)ApplicationPathName,
534 lpEnvironment);
535 if (!DllPathString)
536 {
537 /* Fail */
539 return FALSE;
540 }
541
542 /* Initialize Strings */
543 RtlInitUnicodeString(&DllPath, DllPathString);
544 RtlInitUnicodeString(&ImageName, ApplicationPathName);
545 }
546
547 /* Initialize Strings */
548 RtlInitUnicodeString(&CommandLine, lpCommandLine);
549 RtlInitUnicodeString(&CurrentDirectory, lpCurrentDirectory);
550
551 /* Initialize more Strings from the Startup Info */
552 if (StartupInfo->lpDesktop)
553 {
554 RtlInitUnicodeString(&Desktop, StartupInfo->lpDesktop);
555 }
556 else
557 {
559 }
560 if (StartupInfo->lpReserved)
561 {
562 RtlInitUnicodeString(&Shell, StartupInfo->lpReserved);
563 }
564 else
565 {
567 }
568 if (StartupInfo->lpTitle)
569 {
570 RtlInitUnicodeString(&Title, StartupInfo->lpTitle);
571 }
572 else
573 {
574 RtlInitUnicodeString(&Title, ApplicationPathName);
575 }
576
577 /* This one is special because the length can differ */
578 Runtime.Buffer = (LPWSTR)StartupInfo->lpReserved2;
579 Runtime.MaximumLength = Runtime.Length = StartupInfo->cbReserved2;
580
581 /* Enforce no app compat data if the pointer was NULL */
582 if (!AppCompatData) AppCompatDataSize = 0;
583
584 /* Create the Parameter Block */
585 ProcessParameters = NULL;
586 DPRINT("ImageName: '%wZ'\n", &ImageName);
587 DPRINT("DllPath : '%wZ'\n", &DllPath);
588 DPRINT("CurDir : '%wZ'\n", &CurrentDirectory);
589 DPRINT("CmdLine : '%wZ'\n", &CommandLine);
590 DPRINT("Title : '%wZ'\n", &Title);
591 DPRINT("Desktop : '%wZ'\n", &Desktop);
592 DPRINT("Shell : '%wZ'\n", &Shell);
593 DPRINT("Runtime : '%wZ'\n", &Runtime);
594 Status = RtlCreateProcessParameters(&ProcessParameters,
595 &ImageName,
596 &DllPath,
597 lpCurrentDirectory ?
599 &CommandLine,
600 lpEnvironment,
601 &Title,
602 &Desktop,
603 &Shell,
604 &Runtime);
605 if (!NT_SUCCESS(Status)) goto FailPath;
606
607 /* Clear the current directory handle if not inheriting */
608 if (!InheritHandles) ProcessParameters->CurrentDirectory.Handle = NULL;
609
610 /* Check if the user passed in an environment */
611 if (lpEnvironment)
612 {
613 /* We should've made it part of the parameters block, enforce this */
614 lpEnvironment = ProcessParameters->Environment;
615 }
616 else
617 {
618 /* The user did not, so use the one from the current PEB */
619 HavePebLock = TRUE;
621 lpEnvironment = Peb->ProcessParameters->Environment;
622 }
623
624 /* Save pointer and start lookup */
625 ScanChar = lpEnvironment;
626 if (lpEnvironment)
627 {
628 /* Find the environment size */
629 while (*ScanChar++) while (*ScanChar++);
630 EnviroSize = (ULONG)((ULONG_PTR)ScanChar - (ULONG_PTR)lpEnvironment);
631
632 /* Allocate and Initialize new Environment Block */
633 Size = EnviroSize;
634 ProcessParameters->Environment = NULL;
636 (PVOID*)&ProcessParameters->Environment,
637 0,
638 &Size,
641 if (!NT_SUCCESS(Status)) goto FailPath;
642
643 /* Write the Environment Block */
645 ProcessParameters->Environment,
646 lpEnvironment,
647 EnviroSize,
648 NULL);
649
650 /* No longer need the PEB lock anymore */
651 if (HavePebLock)
652 {
653 /* Release it */
655 HavePebLock = FALSE;
656 }
657
658 /* Check if the write failed */
659 if (!NT_SUCCESS(Status)) goto FailPath;
660 }
661
662 /* Write new parameters */
663 ProcessParameters->StartingX = StartupInfo->dwX;
664 ProcessParameters->StartingY = StartupInfo->dwY;
665 ProcessParameters->CountX = StartupInfo->dwXSize;
666 ProcessParameters->CountY = StartupInfo->dwYSize;
667 ProcessParameters->CountCharsX = StartupInfo->dwXCountChars;
668 ProcessParameters->CountCharsY = StartupInfo->dwYCountChars;
669 ProcessParameters->FillAttribute = StartupInfo->dwFillAttribute;
670 ProcessParameters->WindowFlags = StartupInfo->dwFlags;
671 ProcessParameters->ShowWindowFlags = StartupInfo->wShowWindow;
672
673 /* Write the handles only if we have to */
674 if (StartupInfo->dwFlags &
675 (STARTF_USESTDHANDLES | STARTF_USEHOTKEY | STARTF_SHELLPRIVATE))
676 {
677 ProcessParameters->StandardInput = StartupInfo->hStdInput;
678 ProcessParameters->StandardOutput = StartupInfo->hStdOutput;
679 ProcessParameters->StandardError = StartupInfo->hStdError;
680 }
681
682 /* Use Special Flags for ConDllInitialize in Kernel32 */
683 if (CreationFlags & DETACHED_PROCESS)
684 {
685 ProcessParameters->ConsoleHandle = HANDLE_DETACHED_PROCESS;
686 }
687 else if (CreationFlags & CREATE_NEW_CONSOLE)
688 {
689 ProcessParameters->ConsoleHandle = HANDLE_CREATE_NEW_CONSOLE;
690 }
691 else if (CreationFlags & CREATE_NO_WINDOW)
692 {
693 ProcessParameters->ConsoleHandle = HANDLE_CREATE_NO_WINDOW;
694 }
695 else
696 {
697 /* Inherit our Console Handle */
698 ProcessParameters->ConsoleHandle = Peb->ProcessParameters->ConsoleHandle;
699
700 /* Make sure that the shell isn't trampling on our handles first */
701 if (!(StartupInfo->dwFlags &
702 (STARTF_USESTDHANDLES | STARTF_USEHOTKEY | STARTF_SHELLPRIVATE)))
703 {
704 /* Copy the handle if we are inheriting or if it's a console handle */
705 if ((InheritHandles) ||
707 {
708 ProcessParameters->StandardInput = Peb->ProcessParameters->StandardInput;
709 }
710 if ((InheritHandles) ||
712 {
713 ProcessParameters->StandardOutput = Peb->ProcessParameters->StandardOutput;
714 }
715 if ((InheritHandles) ||
717 {
718 ProcessParameters->StandardError = Peb->ProcessParameters->StandardError;
719 }
720 }
721 }
722
723 /* Also set the Console Flag */
724 if ((CreationFlags & CREATE_NEW_PROCESS_GROUP) &&
725 (!(CreationFlags & CREATE_NEW_CONSOLE)))
726 {
727 ProcessParameters->ConsoleFlags = 1;
728 }
729
730 /* Check if there's a .local file present */
731 if (ParameterFlags & 1)
732 {
734 }
735
736 /* Check if we failed to open the IFEO key */
737 if (ParameterFlags & 2)
738 {
740 }
741
742 /* Allocate memory for the parameter block */
743 Size = ProcessParameters->Length;
744 RemoteParameters = NULL;
746 (PVOID*)&RemoteParameters,
747 0,
748 &Size,
751 if (!NT_SUCCESS(Status)) goto FailPath;
752
753 /* Set the allocated size */
754 ProcessParameters->MaximumLength = Size;
755
756 /* Handle some Parameter Flags */
757 ProcessParameters->Flags |= (CreationFlags & PROFILE_USER) ?
759 ProcessParameters->Flags |= (CreationFlags & PROFILE_KERNEL) ?
761 ProcessParameters->Flags |= (CreationFlags & PROFILE_SERVER) ?
763 ProcessParameters->Flags |= (Peb->ProcessParameters->Flags &
765
766 /* Write the Parameter Block */
768 RemoteParameters,
769 ProcessParameters,
770 ProcessParameters->Length,
771 NULL);
772 if (!NT_SUCCESS(Status)) goto FailPath;
773
774 /* Write the PEB Pointer */
776 &RemotePeb->ProcessParameters,
777 &RemoteParameters,
778 sizeof(PVOID),
779 NULL);
780 if (!NT_SUCCESS(Status)) goto FailPath;
781
782 /* Check if there's any app compat data to write */
783 RemoteAppCompatData = NULL;
784 if (AppCompatData)
785 {
786 /* Allocate some space for the application compatibility data */
787 Size = AppCompatDataSize;
789 &RemoteAppCompatData,
790 0,
791 &Size,
794 if (!NT_SUCCESS(Status)) goto FailPath;
795
796 /* Write the application compatibility data */
798 RemoteAppCompatData,
799 AppCompatData,
800 AppCompatDataSize,
801 NULL);
802 if (!NT_SUCCESS(Status)) goto FailPath;
803 }
804
805 /* Write the PEB Pointer to the app compat data (might be NULL) */
807 &RemotePeb->pShimData,
808 &RemoteAppCompatData,
809 sizeof(PVOID),
810 NULL);
811 if (!NT_SUCCESS(Status)) goto FailPath;
812
813 /* Now write Peb->ImageSubSystem */
814 if (ImageSubsystem)
815 {
817 &RemotePeb->ImageSubsystem,
818 &ImageSubsystem,
819 sizeof(ImageSubsystem),
820 NULL);
821 }
822
823 /* Success path */
824 Result = TRUE;
825
826Quickie:
827 /* Cleanup */
828 if (HavePebLock) RtlReleasePebLock();
829 RtlFreeHeap(RtlGetProcessHeap(), 0, DllPath.Buffer);
830 if (ProcessParameters) RtlDestroyProcessParameters(ProcessParameters);
831 return Result;
832FailPath:
833 DPRINT1("Failure to create process parameters: %lx\n", Status);
835 Result = FALSE;
836 goto Quickie;
837}
#define NtCurrentPeb()
Definition: FLS.c:22
unsigned char BOOLEAN
Definition: actypes.h:127
WCHAR CurrentDirectory[1024]
Definition: chkdsk.c:74
#define ERROR_NOT_ENOUGH_MEMORY
Definition: dderror.h:7
static CHAR Desktop[MAX_PATH]
Definition: dem.c:256
static CHAR Title[MAX_PATH]
Definition: dem.c:257
#define SetLastError(x)
Definition: compat.h:752
PPEB Peb
Definition: dllmain.c:27
LPWSTR WINAPI BaseComputeProcessDllPath(IN LPWSTR FullPath, IN PVOID Environment)
Definition: path.c:478
DWORD WINAPI GetFullPathNameW(IN LPCWSTR lpFileName, IN DWORD nBufferLength, OUT LPWSTR lpBuffer, OUT LPWSTR *lpFilePart)
Definition: path.c:1164
#define HANDLE_CREATE_NEW_CONSOLE
Definition: console.h:14
#define HANDLE_CREATE_NO_WINDOW
Definition: console.h:15
#define HANDLE_DETACHED_PROCESS
Definition: console.h:13
#define ULONG_PTR
Definition: config.h:101
if(dx< 0)
Definition: linetemp.h:194
NTSYSAPI NTSTATUS NTAPI RtlDestroyProcessParameters(_In_ PRTL_USER_PROCESS_PARAMETERS ProcessParameters)
NTSYSAPI NTSTATUS NTAPI RtlCreateProcessParameters(_Out_ PRTL_USER_PROCESS_PARAMETERS *ProcessParameters, _In_ PUNICODE_STRING ImagePathName, _In_opt_ PUNICODE_STRING DllPath, _In_opt_ PUNICODE_STRING CurrentDirectory, _In_opt_ PUNICODE_STRING CommandLine, _In_opt_ PWSTR Environment, _In_opt_ PUNICODE_STRING WindowTitle, _In_opt_ PUNICODE_STRING DesktopInfo, _In_opt_ PUNICODE_STRING ShellInfo, _In_opt_ PUNICODE_STRING RuntimeInfo)
#define RTL_USER_PROCESS_PARAMETERS_IMAGE_KEY_MISSING
Definition: rtltypes.h:54
#define RTL_USER_PROCESS_PARAMETERS_PROFILE_KERNEL
Definition: rtltypes.h:43
#define RTL_USER_PROCESS_PARAMETERS_PROFILE_SERVER
Definition: rtltypes.h:44
#define RTL_USER_PROCESS_PARAMETERS_LOCAL_DLL_PATH
Definition: rtltypes.h:53
#define RTL_USER_PROCESS_PARAMETERS_PROFILE_USER
Definition: rtltypes.h:42
#define RTL_USER_PROCESS_PARAMETERS_DISABLE_HEAP_CHECKS
Definition: rtltypes.h:49
#define PAGE_READWRITE
Definition: nt_native.h:1307
NTSYSAPI VOID NTAPI RtlInitUnicodeString(PUNICODE_STRING DestinationString, PCWSTR SourceString)
#define MEM_COMMIT
Definition: nt_native.h:1316
NTSTATUS NTAPI NtWriteVirtualMemory(IN HANDLE ProcessHandle, IN PVOID BaseAddress, IN PVOID Buffer, IN SIZE_T NumberOfBytesToWrite, OUT PSIZE_T NumberOfBytesWritten OPTIONAL)
Definition: virtual.c:2895
NTSTATUS NTAPI NtAllocateVirtualMemory(IN HANDLE ProcessHandle, IN OUT PVOID *UBaseAddress, IN ULONG_PTR ZeroBits, IN OUT PSIZE_T URegionSize, IN ULONG AllocationType, IN ULONG Protect)
Definition: virtual.c:4457
#define STARTF_USEHOTKEY
Definition: pch.h:41
DWORD BaseSetLastNTError(IN NTSTATUS Status)
Definition: reactos.cpp:167
#define IsConsoleHandle(h)
Definition: console.h:14
#define DPRINT
Definition: sndvol32.h:73
HANDLE Handle
Definition: rtltypes.h:1391
PRTL_USER_PROCESS_PARAMETERS ProcessParameters
Definition: btrfs_drv.h:1913
USHORT MaximumLength
Definition: env_spec_w32.h:370
uint16_t * LPWSTR
Definition: typedefs.h:56
ULONG_PTR SIZE_T
Definition: typedefs.h:80
static int Shell(const char **args)
Definition: vfdcmd.c:1020
_Must_inspect_result_ _In_ WDFDEVICE _In_ PWDF_DEVICE_PROPERTY_DATA _In_ DEVPROPTYPE _In_ ULONG Size
Definition: wdfdevice.h:4539
#define PROFILE_SERVER
Definition: winbase.h:220
#define CREATE_NO_WINDOW
Definition: winbase.h:217
#define CREATE_NEW_PROCESS_GROUP
Definition: winbase.h:190
#define PROFILE_KERNEL
Definition: winbase.h:219
#define PROFILE_USER
Definition: winbase.h:218
#define STARTF_USESTDHANDLES
Definition: winbase.h:476
#define DETACHED_PROCESS
Definition: winbase.h:184
#define CREATE_NEW_CONSOLE
Definition: winbase.h:185
NTSYSAPI void WINAPI RtlReleasePebLock(void)
Definition: libsupp.c:95
NTSYSAPI void WINAPI RtlAcquirePebLock(void)
Definition: libsupp.c:85
_At_(*)(_In_ PWSK_CLIENT Client, _In_opt_ PUNICODE_STRING NodeName, _In_opt_ PUNICODE_STRING ServiceName, _In_opt_ ULONG NameSpace, _In_opt_ GUID *Provider, _In_opt_ PADDRINFOEXW Hints, _Outptr_ PADDRINFOEXW *Result, _In_opt_ PEPROCESS OwningProcess, _In_opt_ PETHREAD OwningThread, _Inout_ PIRP Irp Result)(Mem)) NTSTATUS(WSKAPI *PFN_WSK_GET_ADDRESS_INFO
Definition: wsk.h:409

Referenced by CreateProcessInternalW().

◆ BuildSubSysCommandLine()

BOOLEAN WINAPI BuildSubSysCommandLine ( IN LPCWSTR  SubsystemName,
IN LPCWSTR  ApplicationName,
IN LPCWSTR  CommandLine,
OUT PUNICODE_STRING  SubsysCommandLine 
)

Definition at line 89 of file proc.c.

93{
94 UNICODE_STRING CommandLineString, ApplicationNameString;
97
98 /* Convert to unicode strings */
99 RtlInitUnicodeString(&CommandLineString, ApplicationName);
100 RtlInitUnicodeString(&ApplicationNameString, CommandLine);
101
102 /* Allocate buffer for the output string */
103 Length = CommandLineString.MaximumLength + ApplicationNameString.MaximumLength + 32;
104 Buffer = RtlAllocateHeap(RtlGetProcessHeap(), 0, Length);
105 RtlInitEmptyUnicodeString(SubsysCommandLine, Buffer, (USHORT)Length);
106 if (!Buffer)
107 {
108 /* Fail, no memory */
110 return FALSE;
111 }
112
113 /* Build the final subsystem command line */
114 RtlAppendUnicodeToString(SubsysCommandLine, SubsystemName);
115 RtlAppendUnicodeStringToString(SubsysCommandLine, &CommandLineString);
116 RtlAppendUnicodeToString(SubsysCommandLine, L" /C ");
117 RtlAppendUnicodeStringToString(SubsysCommandLine, &ApplicationNameString);
118 return TRUE;
119}
NTSTATUS RtlAppendUnicodeToString(IN PUNICODE_STRING Str1, IN PWSTR Str2)
Definition: string_lib.cpp:62
NTSYSAPI NTSTATUS NTAPI RtlAppendUnicodeStringToString(PUNICODE_STRING Destination, PUNICODE_STRING Source)
unsigned short USHORT
Definition: pedump.c:61

Referenced by CreateProcessInternalW().

◆ C_ASSERT()

◆ CreateProcessInternalW()

BOOL WINAPI CreateProcessInternalW ( IN HANDLE  hUserToken,
IN LPCWSTR  lpApplicationName,
IN LPWSTR  lpCommandLine,
IN LPSECURITY_ATTRIBUTES  lpProcessAttributes,
IN LPSECURITY_ATTRIBUTES  lpThreadAttributes,
IN BOOL  bInheritHandles,
IN DWORD  dwCreationFlags,
IN LPVOID  lpEnvironment,
IN LPCWSTR  lpCurrentDirectory,
IN LPSTARTUPINFOW  lpStartupInfo,
IN LPPROCESS_INFORMATION  lpProcessInformation,
OUT PHANDLE  hNewToken 
)

Definition at line 2135 of file proc.c.

2147{
2148 //
2149 // Core variables used for creating the initial process and thread
2150 //
2151 SECURITY_ATTRIBUTES LocalThreadAttributes, LocalProcessAttributes;
2152 OBJECT_ATTRIBUTES LocalObjectAttributes;
2154 SECTION_IMAGE_INFORMATION ImageInformation;
2157 ULONG NoWindow, StackSize, ErrorCode, Flags;
2159 USHORT ImageMachine;
2160 ULONG ParameterFlags, PrivilegeValue, HardErrorMode, ErrorResponse;
2161 ULONG_PTR ErrorParameters[2];
2162 BOOLEAN InJob, SaferNeeded, UseLargePages, HavePrivilege;
2163 BOOLEAN QuerySection, SkipSaferAndAppCompat;
2165 BASE_API_MESSAGE CsrMsg[2];
2166 PBASE_CREATE_PROCESS CreateProcessMsg;
2167 PCSR_CAPTURE_BUFFER CaptureBuffer;
2168 PVOID BaseAddress, PrivilegeState, RealTimePrivilegeState;
2169 HANDLE DebugHandle, TokenHandle, JobHandle, KeyHandle, ThreadHandle;
2170 HANDLE FileHandle, SectionHandle, ProcessHandle;
2172 PROCESS_PRIORITY_CLASS PriorityClass;
2173 NTSTATUS Status, AppCompatStatus, SaferStatus, IFEOStatus, ImageDbgStatus;
2174 PPEB Peb, RemotePeb;
2175 PTEB Teb;
2176 INITIAL_TEB InitialTeb;
2177 PVOID TibValue;
2178 PIMAGE_NT_HEADERS NtHeaders;
2179 STARTUPINFOW StartupInfo;
2180 PRTL_USER_PROCESS_PARAMETERS ProcessParameters;
2181 UNICODE_STRING DebuggerString;
2182 BOOL Result;
2183 //
2184 // Variables used for command-line and argument parsing
2185 //
2186 PCHAR pcScan;
2187 SIZE_T n;
2188 WCHAR SaveChar;
2189 ULONG Length, FileAttribs, CmdQuoteLength;
2190 ULONG ResultSize;
2191 SIZE_T EnvironmentLength, CmdLineLength;
2192 PWCHAR QuotedCmdLine, AnsiCmdCommand, ExtBuffer, CurrentDirectory;
2193 PWCHAR NullBuffer, ScanString, NameBuffer, SearchPath, DebuggerCmdLine;
2194 ANSI_STRING AnsiEnv;
2195 UNICODE_STRING UnicodeEnv, PathName;
2196 BOOLEAN SearchRetry, QuotesNeeded, CmdLineIsAppName, HasQuotes;
2197
2198 //
2199 // Variables used for Fusion/SxS (Side-by-Side Assemblies)
2200 //
2201 RTL_PATH_TYPE SxsPathType, PathType;
2202#if _SXS_SUPPORT_ENABLED_
2203 PRTL_BUFFER ByteBuffer;
2204 PRTL_UNICODE_STRING_BUFFER ThisBuffer, Buffer, SxsStaticBuffers[5];
2205 PRTL_UNICODE_STRING_BUFFER* BufferHead, SxsStringBuffer;
2206 RTL_UNICODE_STRING_BUFFER SxsWin32ManifestPath, SxsNtManifestPath;
2207 RTL_UNICODE_STRING_BUFFER SxsWin32PolicyPath, SxsNtPolicyPath;
2208 RTL_UNICODE_STRING_BUFFER SxsWin32AssemblyDirectory;
2209 BASE_MSG_SXS_HANDLES MappedHandles, Handles, FileHandles;
2210 PVOID CapturedStrings[3];
2211 SXS_WIN32_NT_PATH_PAIR ExePathPair, ManifestPathPair, PolicyPathPair;
2212 SXS_OVERRIDE_MANIFEST OverrideManifest;
2213 UNICODE_STRING FreeString, SxsNtExePath;
2214 PWCHAR SxsConglomeratedBuffer, StaticBuffer;
2215 ULONG ConglomeratedBufferSizeBytes, StaticBufferSize, i;
2216#endif
2218
2219 //
2220 // Variables used for path conversion (and partially Fusion/SxS)
2221 //
2222 PWCHAR FilePart, PathBuffer, FreeBuffer;
2223 BOOLEAN TranslationStatus;
2224 RTL_RELATIVE_NAME_U SxsWin32RelativePath;
2225 UNICODE_STRING PathBufferString, SxsWin32ExePath;
2226
2227 //
2228 // Variables used by Application Compatibility (and partially Fusion/SxS)
2229 //
2230 PVOID AppCompatSxsData, AppCompatData;
2231 ULONG AppCompatSxsDataSize, AppCompatDataSize;
2232 //
2233 // Variables used by VDM (Virtual Dos Machine) and WOW32 (16-bit Support)
2234 //
2235 ULONG BinarySubType, VdmBinaryType, VdmTask, VdmReserve;
2236 ULONG VdmUndoLevel;
2237 BOOLEAN UseVdmReserve;
2238 HANDLE VdmWaitObject;
2239 ANSI_STRING VdmAnsiEnv;
2240 UNICODE_STRING VdmString, VdmUnicodeEnv;
2241 BOOLEAN IsWowApp;
2242 PBASE_CHECK_VDM CheckVdmMsg;
2243
2244 /* Zero out the initial core variables and handles */
2245 QuerySection = FALSE;
2246 InJob = FALSE;
2247 SkipSaferAndAppCompat = FALSE;
2248 ParameterFlags = 0;
2249 Flags = 0;
2250 DebugHandle = NULL;
2251 JobHandle = NULL;
2252 TokenHandle = NULL;
2253 FileHandle = NULL;
2254 SectionHandle = NULL;
2256 ThreadHandle = NULL;
2258 BaseAddress = (PVOID)1;
2259
2260 /* Zero out initial SxS and Application Compatibility state */
2261 AppCompatData = NULL;
2262 AppCompatDataSize = 0;
2263 AppCompatSxsData = NULL;
2264 AppCompatSxsDataSize = 0;
2265 CaptureBuffer = NULL;
2266#if _SXS_SUPPORT_ENABLED_
2267 SxsConglomeratedBuffer = NULL;
2268#endif
2269 FusionFlags = 0;
2270
2271 /* Zero out initial parsing variables -- others are initialized later */
2272 DebuggerCmdLine = NULL;
2273 PathBuffer = NULL;
2274 SearchPath = NULL;
2275 NullBuffer = NULL;
2276 FreeBuffer = NULL;
2277 NameBuffer = NULL;
2279 FilePart = NULL;
2280 DebuggerString.Buffer = NULL;
2281 HasQuotes = FALSE;
2282 QuotedCmdLine = NULL;
2283
2284 /* Zero out initial VDM state */
2285 VdmAnsiEnv.Buffer = NULL;
2286 VdmUnicodeEnv.Buffer = NULL;
2287 VdmString.Buffer = NULL;
2288 VdmTask = 0;
2289 VdmUndoLevel = 0;
2290 VdmBinaryType = 0;
2291 VdmReserve = 0;
2292 VdmWaitObject = NULL;
2293 UseVdmReserve = FALSE;
2294 IsWowApp = FALSE;
2295
2296 /* Set message structures */
2297 CreateProcessMsg = &CsrMsg[0].Data.CreateProcessRequest;
2298 CheckVdmMsg = &CsrMsg[1].Data.CheckVDMRequest;
2299
2300 /* Clear the more complex structures by zeroing out their entire memory */
2301 RtlZeroMemory(&Context, sizeof(Context));
2302#if _SXS_SUPPORT_ENABLED_
2303 RtlZeroMemory(&FileHandles, sizeof(FileHandles));
2304 RtlZeroMemory(&MappedHandles, sizeof(MappedHandles));
2305 RtlZeroMemory(&Handles, sizeof(Handles));
2306#endif
2307 RtlZeroMemory(&CreateProcessMsg->Sxs, sizeof(CreateProcessMsg->Sxs));
2308 RtlZeroMemory(&LocalProcessAttributes, sizeof(LocalProcessAttributes));
2309 RtlZeroMemory(&LocalThreadAttributes, sizeof(LocalThreadAttributes));
2310
2311 /* Zero out output arguments as well */
2312 RtlZeroMemory(lpProcessInformation, sizeof(*lpProcessInformation));
2313 if (hNewToken) *hNewToken = NULL;
2314
2315 /* Capture the special window flag */
2316 NoWindow = dwCreationFlags & CREATE_NO_WINDOW;
2317 dwCreationFlags &= ~CREATE_NO_WINDOW;
2318
2319#if _SXS_SUPPORT_ENABLED_
2320 /* Setup the SxS static string arrays and buffers */
2321 SxsStaticBuffers[0] = &SxsWin32ManifestPath;
2322 SxsStaticBuffers[1] = &SxsWin32PolicyPath;
2323 SxsStaticBuffers[2] = &SxsWin32AssemblyDirectory;
2324 SxsStaticBuffers[3] = &SxsNtManifestPath;
2325 SxsStaticBuffers[4] = &SxsNtPolicyPath;
2326 ExePathPair.Win32 = &SxsWin32ExePath;
2327 ExePathPair.Nt = &SxsNtExePath;
2328 ManifestPathPair.Win32 = &SxsWin32ManifestPath.String;
2329 ManifestPathPair.Nt = &SxsNtManifestPath.String;
2330 PolicyPathPair.Win32 = &SxsWin32PolicyPath.String;
2331 PolicyPathPair.Nt = &SxsNtPolicyPath.String;
2332#endif
2333
2334 DPRINT("CreateProcessInternalW: '%S' '%S' %lx\n", lpApplicationName, lpCommandLine, dwCreationFlags);
2335
2336 /* Finally, set our TEB and PEB */
2337 Teb = NtCurrentTeb();
2338 Peb = NtCurrentPeb();
2339
2340 /* This combination is illegal (see MSDN) */
2341 if ((dwCreationFlags & (DETACHED_PROCESS | CREATE_NEW_CONSOLE)) ==
2343 {
2344 DPRINT1("Invalid flag combo used\n");
2346 return FALSE;
2347 }
2348
2349 /* Convert the priority class */
2350 if (dwCreationFlags & IDLE_PRIORITY_CLASS)
2351 {
2353 }
2354 else if (dwCreationFlags & BELOW_NORMAL_PRIORITY_CLASS)
2355 {
2357 }
2358 else if (dwCreationFlags & NORMAL_PRIORITY_CLASS)
2359 {
2361 }
2362 else if (dwCreationFlags & ABOVE_NORMAL_PRIORITY_CLASS)
2363 {
2365 }
2366 else if (dwCreationFlags & HIGH_PRIORITY_CLASS)
2367 {
2369 }
2370 else if (dwCreationFlags & REALTIME_PRIORITY_CLASS)
2371 {
2373 PriorityClass.PriorityClass += (BasepIsRealtimeAllowed(FALSE) != NULL);
2374 }
2375 else
2376 {
2378 }
2379
2380 /* Done with the priority masks, so get rid of them */
2381 PriorityClass.Foreground = FALSE;
2382 dwCreationFlags &= ~(NORMAL_PRIORITY_CLASS |
2388
2389 /* You cannot request both a shared and a separate WoW VDM */
2390 if ((dwCreationFlags & CREATE_SEPARATE_WOW_VDM) &&
2391 (dwCreationFlags & CREATE_SHARED_WOW_VDM))
2392 {
2393 /* Fail such nonsensical attempts */
2394 DPRINT1("Invalid WOW flags\n");
2396 return FALSE;
2397 }
2398 else if (!(dwCreationFlags & CREATE_SHARED_WOW_VDM) &&
2400 {
2401 /* A shared WoW VDM was not requested but system enforces separation */
2402 dwCreationFlags |= CREATE_SEPARATE_WOW_VDM;
2403 }
2404
2405 /* If a shared WoW VDM is used, make sure the process isn't in a job */
2406 if (!(dwCreationFlags & CREATE_SEPARATE_WOW_VDM) &&
2408 {
2409 /* Remove the shared flag and add the separate flag */
2410 dwCreationFlags = (dwCreationFlags &~ CREATE_SHARED_WOW_VDM) |
2412 }
2413
2414 /* Convert the environment */
2415 if ((lpEnvironment) && !(dwCreationFlags & CREATE_UNICODE_ENVIRONMENT))
2416 {
2417 /* Scan the environment to calculate its Unicode size */
2418 AnsiEnv.Buffer = pcScan = (PCHAR)lpEnvironment;
2419 while ((*pcScan) || (*(pcScan + 1))) ++pcScan;
2420
2421 /* Make sure the environment is not too large */
2422 EnvironmentLength = (pcScan + sizeof(ANSI_NULL) - (PCHAR)lpEnvironment);
2423 if (EnvironmentLength > MAXUSHORT)
2424 {
2425 /* Fail */
2427 return FALSE;
2428 }
2429
2430 /* Create our ANSI String */
2431 AnsiEnv.Length = (USHORT)EnvironmentLength;
2432 AnsiEnv.MaximumLength = AnsiEnv.Length + sizeof(ANSI_NULL);
2433
2434 /* Allocate memory for the Unicode Environment */
2435 UnicodeEnv.Buffer = NULL;
2436 RegionSize = AnsiEnv.MaximumLength * sizeof(WCHAR);
2438 (PVOID)&UnicodeEnv.Buffer,
2439 0,
2440 &RegionSize,
2441 MEM_COMMIT,
2443 if (!NT_SUCCESS(Status))
2444 {
2445 /* Fail */
2447 return FALSE;
2448 }
2449
2450 /* Use the allocated size and convert */
2451 UnicodeEnv.MaximumLength = (USHORT)RegionSize;
2452 Status = RtlAnsiStringToUnicodeString(&UnicodeEnv, &AnsiEnv, FALSE);
2453 if (!NT_SUCCESS(Status))
2454 {
2455 /* Fail */
2457 (PVOID)&UnicodeEnv.Buffer,
2458 &RegionSize,
2459 MEM_RELEASE);
2461 return FALSE;
2462 }
2463
2464 /* Now set the Unicode environment as the environment string pointer */
2465 lpEnvironment = UnicodeEnv.Buffer;
2466 }
2467
2468 /* Make a copy of the caller's startup info since we'll modify it */
2469 StartupInfo = *lpStartupInfo;
2470
2471 /* Check if private data is being sent on the same channel as std handles */
2472 if ((StartupInfo.dwFlags & STARTF_USESTDHANDLES) &&
2473 (StartupInfo.dwFlags & (STARTF_USEHOTKEY | STARTF_SHELLPRIVATE)))
2474 {
2475 /* Cannot use the std handles since we have monitor/hotkey values */
2476 StartupInfo.dwFlags &= ~STARTF_USESTDHANDLES;
2477 }
2478
2479 /* If there's a debugger, or we have to launch cmd.exe, we go back here */
2480AppNameRetry:
2481 /* New iteration -- free any existing name buffer */
2482 if (NameBuffer)
2483 {
2484 RtlFreeHeap(RtlGetProcessHeap(), 0, NameBuffer);
2485 NameBuffer = NULL;
2486 }
2487
2488 /* New iteration -- free any existing free buffer */
2489 if (FreeBuffer)
2490 {
2491 RtlFreeHeap(RtlGetProcessHeap(), 0, FreeBuffer);
2492 FreeBuffer = NULL;
2493 }
2494
2495 /* New iteration -- close any existing file handle */
2496 if (FileHandle)
2497 {
2499 FileHandle = NULL;
2500 }
2501
2502 /* Set the initial parsing state. This code can loop -- don't move this! */
2503 ErrorCode = 0;
2504 SearchRetry = TRUE;
2505 QuotesNeeded = FALSE;
2506 CmdLineIsAppName = FALSE;
2507
2508 /* First check if we don't have an application name */
2509 if (!lpApplicationName)
2510 {
2511 /* This should be the first time we attempt creating one */
2512 ASSERT(NameBuffer == NULL);
2513
2514 /* Allocate a buffer to hold it */
2515 NameBuffer = RtlAllocateHeap(RtlGetProcessHeap(),
2516 0,
2517 MAX_PATH * sizeof(WCHAR));
2518 if (!NameBuffer)
2519 {
2521 Result = FALSE;
2522 goto Quickie;
2523 }
2524
2525 /* Initialize the application name and our parsing parameters */
2526 lpApplicationName = NullBuffer = ScanString = lpCommandLine;
2527
2528 /* Check for an initial quote*/
2529 if (*lpCommandLine == L'\"')
2530 {
2531 /* We found a quote, keep searching for another one */
2532 SearchRetry = FALSE;
2533 ScanString++;
2534 lpApplicationName = ScanString;
2535 while (*ScanString)
2536 {
2537 /* Have we found the terminating quote? */
2538 if (*ScanString == L'\"')
2539 {
2540 /* We're done, get out of here */
2541 NullBuffer = ScanString;
2542 HasQuotes = TRUE;
2543 break;
2544 }
2545
2546 /* Keep searching for the quote */
2547 ScanString++;
2548 NullBuffer = ScanString;
2549 }
2550 }
2551 else
2552 {
2553StartScan:
2554 /* We simply make the application name be the command line*/
2555 lpApplicationName = lpCommandLine;
2556 while (*ScanString)
2557 {
2558 /* Check if it starts with a space or tab */
2559 if ((*ScanString == L' ') || (*ScanString == L'\t'))
2560 {
2561 /* Break out of the search loop */
2562 NullBuffer = ScanString;
2563 break;
2564 }
2565
2566 /* Keep searching for a space or tab */
2567 ScanString++;
2568 NullBuffer = ScanString;
2569 }
2570 }
2571
2572 /* We have found the end of the application name, terminate it */
2573 SaveChar = *NullBuffer;
2574 *NullBuffer = UNICODE_NULL;
2575
2576 /* New iteration -- free any existing saved path */
2577 if (SearchPath)
2578 {
2579 RtlFreeHeap(RtlGetProcessHeap(), 0, SearchPath);
2580 SearchPath = NULL;
2581 }
2582
2583 /* Now compute the final EXE path based on the name */
2584 SearchPath = BaseComputeProcessExePath((LPWSTR)lpApplicationName);
2585 DPRINT("Search Path: %S\n", SearchPath);
2586 if (!SearchPath)
2587 {
2589 Result = FALSE;
2590 goto Quickie;
2591 }
2592
2593 /* And search for the executable in the search path */
2595 lpApplicationName,
2596 L".exe",
2597 MAX_PATH,
2598 NameBuffer,
2599 NULL);
2600
2601 /* Did we find it? */
2602 if ((Length) && (Length < MAX_PATH))
2603 {
2604 /* Get file attributes */
2605 FileAttribs = GetFileAttributesW(NameBuffer);
2606 if ((FileAttribs != INVALID_FILE_ATTRIBUTES) &&
2607 (FileAttribs & FILE_ATTRIBUTE_DIRECTORY))
2608 {
2609 /* This was a directory, fail later on */
2610 Length = 0;
2611 }
2612 else
2613 {
2614 /* It's a file! */
2615 Length++;
2616 }
2617 }
2618
2619 DPRINT("Length: %lu Buffer: %S\n", Length, NameBuffer);
2620
2621 /* Check if there was a failure in SearchPathW */
2622 if ((Length) && (Length < MAX_PATH))
2623 {
2624 /* Everything looks good, restore the name */
2625 *NullBuffer = SaveChar;
2626 lpApplicationName = NameBuffer;
2627 }
2628 else
2629 {
2630 /* Check if this was a relative path, which would explain it */
2631 PathType = RtlDetermineDosPathNameType_U(lpApplicationName);
2633 {
2634 /* This should fail, and give us a detailed LastError */
2635 FileHandle = CreateFileW(lpApplicationName,
2639 NULL,
2642 NULL);
2644 {
2645 /* It worked? Return a generic error */
2647 FileHandle = NULL;
2649 }
2650 }
2651 else
2652 {
2653 /* Path was absolute, which means it doesn't exist */
2655 }
2656
2657 /* Did we already fail once? */
2658 if (ErrorCode)
2659 {
2660 /* Set the error code */
2662 }
2663 else
2664 {
2665 /* Not yet, cache it */
2667 }
2668
2669 /* Put back the command line */
2670 *NullBuffer = SaveChar;
2671 lpApplicationName = NameBuffer;
2672
2673 /* It's possible there's whitespace in the directory name */
2674 if (!(*ScanString) || !(SearchRetry))
2675 {
2676 /* Not the case, give up completely */
2677 Result = FALSE;
2678 goto Quickie;
2679 }
2680
2681 /* There are spaces, so keep trying the next possibility */
2682 ScanString++;
2683 NullBuffer = ScanString;
2684
2685 /* We will have to add a quote, since there is a space */
2686 QuotesNeeded = TRUE;
2687 HasQuotes = TRUE;
2688 goto StartScan;
2689 }
2690 }
2691 else if (!(lpCommandLine) || !(*lpCommandLine))
2692 {
2693 /* We don't have a command line, so just use the application name */
2694 CmdLineIsAppName = TRUE;
2695 lpCommandLine = (LPWSTR)lpApplicationName;
2696 }
2697
2698 /* Convert the application name to its NT path */
2699 TranslationStatus = RtlDosPathNameToRelativeNtPathName_U(lpApplicationName,
2700 &PathName,
2701 NULL,
2702 &SxsWin32RelativePath);
2703 if (!TranslationStatus)
2704 {
2705 /* Path must be invalid somehow, bail out */
2706 DPRINT1("Path translation for SxS failed\n");
2708 Result = FALSE;
2709 goto Quickie;
2710 }
2711
2712 /* Setup the buffer that needs to be freed at the end */
2713 ASSERT(FreeBuffer == NULL);
2714 FreeBuffer = PathName.Buffer;
2715
2716 /* Check what kind of path the application is, for SxS (Fusion) purposes */
2717 RtlInitUnicodeString(&SxsWin32ExePath, lpApplicationName);
2718 SxsPathType = RtlDetermineDosPathNameType_U(lpApplicationName);
2719 if ((SxsPathType != RtlPathTypeDriveAbsolute) &&
2720 (SxsPathType != RtlPathTypeLocalDevice) &&
2721 (SxsPathType != RtlPathTypeRootLocalDevice) &&
2722 (SxsPathType != RtlPathTypeUncAbsolute))
2723 {
2724 /* Relative-type path, get the full path */
2725 RtlInitEmptyUnicodeString(&PathBufferString, NULL, 0);
2726 Status = RtlGetFullPathName_UstrEx(&SxsWin32ExePath,
2727 NULL,
2728 &PathBufferString,
2729 NULL,
2730 NULL,
2731 NULL,
2732 &SxsPathType,
2733 NULL);
2734 if (!NT_SUCCESS(Status))
2735 {
2736 /* Fail the rest of the create */
2737 RtlReleaseRelativeName(&SxsWin32RelativePath);
2739 Result = FALSE;
2740 goto Quickie;
2741 }
2742
2743 /* Use this full path as the SxS path */
2744 SxsWin32ExePath = PathBufferString;
2745 PathBuffer = PathBufferString.Buffer;
2746 PathBufferString.Buffer = NULL;
2747 DPRINT("SxS Path: %S\n", PathBuffer);
2748 }
2749
2750 /* Also set the .EXE path based on the path name */
2751#if _SXS_SUPPORT_ENABLED_
2752 SxsNtExePath = PathName;
2753#endif
2754 if (SxsWin32RelativePath.RelativeName.Length)
2755 {
2756 /* If it's relative, capture the relative name */
2757 PathName = SxsWin32RelativePath.RelativeName;
2758 }
2759 else
2760 {
2761 /* Otherwise, it's absolute, make sure no relative dir is used */
2762 SxsWin32RelativePath.ContainingDirectory = NULL;
2763 }
2764
2765 /* Now use the path name, and the root path, to try opening the app */
2766 DPRINT("Path: %wZ. Dir: %p\n", &PathName, SxsWin32RelativePath.ContainingDirectory);
2767 InitializeObjectAttributes(&LocalObjectAttributes,
2768 &PathName,
2770 SxsWin32RelativePath.ContainingDirectory,
2771 NULL);
2773 SYNCHRONIZE |
2777 &LocalObjectAttributes,
2782 if (!NT_SUCCESS(Status))
2783 {
2784 /* Try to open the app just for execute purposes instead */
2787 &LocalObjectAttributes,
2792 }
2793
2794 /* Failure path, display which file failed to open */
2795 if (!NT_SUCCESS(Status))
2796 DPRINT1("Open file failed: %lx (%wZ)\n", Status, &PathName);
2797
2798 /* Cleanup in preparation for failure or success */
2799 RtlReleaseRelativeName(&SxsWin32RelativePath);
2800
2801 if (!NT_SUCCESS(Status))
2802 {
2803 /* Failure path, try to understand why */
2804 if (RtlIsDosDeviceName_U(lpApplicationName))
2805 {
2806 /* If a device is being executed, return this special error code */
2808 Result = FALSE;
2809 goto Quickie;
2810 }
2811 else
2812 {
2813 /* Otherwise return the converted NT error code */
2815 Result = FALSE;
2816 goto Quickie;
2817 }
2818 }
2819
2820 /* Did the caller specify a desktop? */
2821 if (!StartupInfo.lpDesktop)
2822 {
2823 /* Use the one from the current process */
2825 }
2826
2827 /* Create a section for this file */
2828 Status = NtCreateSection(&SectionHandle,
2830 NULL,
2831 NULL,
2833 SEC_IMAGE,
2834 FileHandle);
2835 DPRINT("Section status: %lx\n", Status);
2836 if (NT_SUCCESS(Status))
2837 {
2838 /* Are we running on Windows Embedded, Datacenter, Blade or Starter? */
2839 if (SharedUserData->SuiteMask & (VER_SUITE_EMBEDDEDNT |
2843 {
2844 /* These SKUs do not allow running certain applications */
2847 {
2848 /* And this is one of them! */
2849 DPRINT1("Invalid Blade hashes!\n");
2851 Result = FALSE;
2852 goto Quickie;
2853 }
2854
2855 /* Did we get some other failure? */
2856 if (!NT_SUCCESS(Status))
2857 {
2858 /* If we couldn't check the hashes, assume nefariousness */
2859 DPRINT1("Tampered Blade hashes!\n");
2861 Result = FALSE;
2862 goto Quickie;
2863 }
2864 }
2865
2866 /* Now do Winsafer, etc, checks */
2867 Status = BasepIsProcessAllowed((LPWSTR)lpApplicationName);
2868 if (!NT_SUCCESS(Status))
2869 {
2870 /* Fail if we're not allowed to launch the process */
2871 DPRINT1("Process not allowed to launch: %lx\n", Status);
2873 if (SectionHandle)
2874 {
2875 NtClose(SectionHandle);
2876 SectionHandle = NULL;
2877 }
2878 Result = FALSE;
2879 goto Quickie;
2880 }
2881
2882 /* Is a DOS VDM being forced, but we already have a WOW32 instance ready? */
2883 if ((dwCreationFlags & CREATE_FORCEDOS) &&
2885 {
2886 /* This request can't be satisfied, instead, a separate VDM is needed */
2887 dwCreationFlags &= ~(CREATE_FORCEDOS | CREATE_SHARED_WOW_VDM);
2888 dwCreationFlags |= CREATE_SEPARATE_WOW_VDM;
2889
2890 /* Set a failure code, ask for VDM reservation */
2892 UseVdmReserve = TRUE;
2893
2894 /* Close the current handle */
2895 NtClose(SectionHandle);
2896 SectionHandle = NULL;
2897
2898 /* Don't query the section later */
2899 QuerySection = FALSE;
2900 }
2901 }
2902
2903 /* Did we already do these checks? */
2904 if (!SkipSaferAndAppCompat)
2905 {
2906 /* Is everything OK so far, OR do we have an non-MZ, non-DOS app? */
2907 if ((NT_SUCCESS(Status)) ||
2909 !(BaseIsDosApplication(&PathName, Status))))
2910 {
2911 /* Clear the machine type in case of failure */
2912 ImageMachine = 0;
2913
2914 /* Clean any app compat data that may have accumulated */
2915 BasepFreeAppCompatData(AppCompatData, AppCompatSxsData);
2916 AppCompatData = NULL;
2917 AppCompatSxsData = NULL;
2918
2919 /* Do we have a section? */
2920 if (SectionHandle)
2921 {
2922 /* Have we already queried it? */
2923 if (QuerySection)
2924 {
2925 /* Nothing to do */
2926 AppCompatStatus = STATUS_SUCCESS;
2927 }
2928 else
2929 {
2930 /* Get some information about the executable */
2931 AppCompatStatus = NtQuerySection(SectionHandle,
2933 &ImageInformation,
2934 sizeof(ImageInformation),
2935 NULL);
2936 }
2937
2938 /* Do we have section information now? */
2939 if (NT_SUCCESS(AppCompatStatus))
2940 {
2941 /* Don't ask for it again, save the machine type */
2942 QuerySection = TRUE;
2943 ImageMachine = ImageInformation.Machine;
2944 }
2945 }
2946
2947 /* Is there a reason/Shim we shouldn't run this application? */
2948 AppCompatStatus = BasepCheckBadapp(FileHandle,
2949 FreeBuffer,
2950 lpEnvironment,
2951 ImageMachine,
2952 &AppCompatData,
2953 &AppCompatDataSize,
2954 &AppCompatSxsData,
2955 &AppCompatSxsDataSize,
2956 &FusionFlags);
2957 if (!NT_SUCCESS(AppCompatStatus))
2958 {
2959 /* This is usually the status we get back */
2960 DPRINT1("App compat launch failure: %lx\n", AppCompatStatus);
2961 if (AppCompatStatus == STATUS_ACCESS_DENIED)
2962 {
2963 /* Convert it to something more Win32-specific */
2965 }
2966 else
2967 {
2968 /* Some other error */
2969 BaseSetLastNTError(AppCompatStatus);
2970 }
2971
2972 /* Did we have a section? */
2973 if (SectionHandle)
2974 {
2975 /* Clean it up */
2976 NtClose(SectionHandle);
2977 SectionHandle = NULL;
2978 }
2979
2980 /* Fail the call */
2981 Result = FALSE;
2982 goto Quickie;
2983 }
2984 }
2985 }
2986
2987 //ASSERT((dwFusionFlags & ~SXS_APPCOMPACT_FLAG_APP_RUNNING_SAFEMODE) == 0);
2988
2989 /* Have we already done, and do we need to do, SRP (WinSafer) checks? */
2990 if (!(SkipSaferAndAppCompat) &&
2991 ~(dwCreationFlags & CREATE_PRESERVE_CODE_AUTHZ_LEVEL))
2992 {
2993 /* Assume yes */
2994 SaferNeeded = TRUE;
2995 switch (Status)
2996 {
3001 /* For all DOS, 16-bit, OS/2 images, we do*/
3002 break;
3003
3005 /* For invalid files, we don't, unless it's a .BAT file */
3006 if (BaseIsDosApplication(&PathName, Status)) break;
3007
3008 default:
3009 /* Any other error codes we also don't */
3010 if (!NT_SUCCESS(Status))
3011 {
3012 SaferNeeded = FALSE;
3013 }
3014
3015 /* But for success, we do */
3016 break;
3017 }
3018
3019 /* Okay, so what did the checks above result in? */
3020 if (SaferNeeded)
3021 {
3022 /* We have to call into the WinSafer library and actually check */
3024 (LPWSTR)lpApplicationName,
3025 FileHandle,
3026 &InJob,
3027 &TokenHandle,
3028 &JobHandle);
3029 if (SaferStatus == 0xFFFFFFFF)
3030 {
3031 /* Back in 2003, they didn't have an NTSTATUS for this... */
3032 DPRINT1("WinSafer blocking process launch\n");
3034 Result = FALSE;
3035 goto Quickie;
3036 }
3037
3038 /* Other status codes are not-Safer related, just convert them */
3039 if (!NT_SUCCESS(SaferStatus))
3040 {
3041 DPRINT1("Error checking WinSafer: %lx\n", SaferStatus);
3042 BaseSetLastNTError(SaferStatus);
3043 Result = FALSE;
3044 goto Quickie;
3045 }
3046 }
3047 }
3048
3049 /* The last step is to figure out why the section object was not created */
3050 switch (Status)
3051 {
3053 {
3054 /* 16-bit binary. Should we use WOW or does the caller force VDM? */
3055 if (!(dwCreationFlags & CREATE_FORCEDOS))
3056 {
3057 /* Remember that we're launching WOW */
3058 IsWowApp = TRUE;
3059
3060 /* Create the VDM environment, it's valid for WOW too */
3061 Result = BaseCreateVDMEnvironment(lpEnvironment,
3062 &VdmAnsiEnv,
3063 &VdmUnicodeEnv);
3064 if (!Result)
3065 {
3066 DPRINT1("VDM environment for WOW app failed\n");
3067 goto Quickie;
3068 }
3069
3070 /* We're going to try this twice, so do a loop */
3071 while (TRUE)
3072 {
3073 /* Pick which kind of WOW mode we want to run in */
3074 VdmBinaryType = (dwCreationFlags &
3077
3078 /* Get all the VDM settings and current status */
3079 Status = BaseCheckVDM(VdmBinaryType,
3080 lpApplicationName,
3081 lpCommandLine,
3082 lpCurrentDirectory,
3083 &VdmAnsiEnv,
3084 &CsrMsg[1],
3085 &VdmTask,
3086 dwCreationFlags,
3087 &StartupInfo,
3088 hUserToken);
3089
3090 /* If it worked, no need to try again */
3091 if (NT_SUCCESS(Status)) break;
3092
3093 /* Check if it's disallowed or if it's our second time */
3095 if ((Status == STATUS_VDM_DISALLOWED) ||
3096 (VdmBinaryType == BINARY_TYPE_SEPARATE_WOW) ||
3098 {
3099 /* Fail the call -- we won't try again */
3100 DPRINT1("VDM message failure for WOW: %lx\n", Status);
3101 Result = FALSE;
3102 goto Quickie;
3103 }
3104
3105 /* Try one more time, but with a separate WOW instance */
3106 dwCreationFlags |= CREATE_SEPARATE_WOW_VDM;
3107 }
3108
3109 /* Check which VDM state we're currently in */
3110 switch (CheckVdmMsg->VDMState & (VDM_NOT_LOADED |
3112 VDM_READY))
3113 {
3114 case VDM_NOT_LOADED:
3115 /* VDM is not fully loaded, so not that much to undo */
3116 VdmUndoLevel = VDM_UNDO_PARTIAL;
3117
3118 /* Reset VDM reserve if needed */
3119 if (UseVdmReserve) VdmReserve = 1;
3120
3121 /* Get the required parameters and names for launch */
3122 Result = BaseGetVdmConfigInfo(lpCommandLine,
3123 VdmTask,
3124 VdmBinaryType,
3125 &VdmString,
3126 &VdmReserve);
3127 if (!Result)
3128 {
3129 DPRINT1("VDM Configuration failed for WOW\n");
3131 goto Quickie;
3132 }
3133
3134 /* Update the command-line with the VDM one instead */
3135 lpCommandLine = VdmString.Buffer;
3136 lpApplicationName = NULL;
3137
3138 /* We don't want a console, detachment, nor a window */
3139 dwCreationFlags |= CREATE_NO_WINDOW;
3140 dwCreationFlags &= ~(CREATE_NEW_CONSOLE | DETACHED_PROCESS);
3141
3142 /* Force feedback on */
3143 StartupInfo.dwFlags |= STARTF_FORCEONFEEDBACK;
3144 break;
3145
3146
3147 case VDM_READY:
3148 /* VDM is ready, so we have to undo everything */
3149 VdmUndoLevel = VDM_UNDO_REUSE;
3150
3151 /* Check if CSRSS wants us to wait on VDM */
3152 VdmWaitObject = CheckVdmMsg->WaitObjectForParent;
3153 break;
3154
3155 case VDM_NOT_READY:
3156 /* Something is wrong with VDM, we'll fail the call */
3157 DPRINT1("VDM is not ready for WOW\n");
3159 Result = FALSE;
3160 goto Quickie;
3161
3162 default:
3163 break;
3164 }
3165
3166 /* Since to get NULL, we allocate from 0x1, account for this */
3167 VdmReserve--;
3168
3169 /* This implies VDM is ready, so skip everything else */
3170 if (VdmWaitObject) goto VdmShortCircuit;
3171
3172 /* Don't inherit handles since we're doing VDM now */
3173 bInheritHandles = FALSE;
3174
3175 /* Had the user passed in environment? If so, destroy it */
3176 if ((lpEnvironment) &&
3177 !(dwCreationFlags & CREATE_UNICODE_ENVIRONMENT))
3178 {
3179 RtlDestroyEnvironment(lpEnvironment);
3180 }
3181
3182 /* We've already done all these checks, don't do them again */
3183 SkipSaferAndAppCompat = TRUE;
3184 goto AppNameRetry;
3185 }
3186
3187 // There is no break here on purpose, so FORCEDOS drops down!
3188 }
3189
3193 {
3194 /* We're launching an executable application */
3195 BinarySubType = BINARY_TYPE_EXE;
3196
3197 /* We can drop here from other "cases" above too, so check */
3200 (BinarySubType = BaseIsDosApplication(&PathName, Status)))
3201 {
3202 /* We're launching a DOS application */
3203 VdmBinaryType = BINARY_TYPE_DOS;
3204
3205 /* Based on the caller environment, create a VDM one */
3206 Result = BaseCreateVDMEnvironment(lpEnvironment,
3207 &VdmAnsiEnv,
3208 &VdmUnicodeEnv);
3209 if (!Result)
3210 {
3211 DPRINT1("VDM environment for DOS failed\n");
3212 goto Quickie;
3213 }
3214
3215 /* Check the current state of the VDM subsystem */
3216 Status = BaseCheckVDM(VdmBinaryType | BinarySubType,
3217 lpApplicationName,
3218 lpCommandLine,
3219 lpCurrentDirectory,
3220 &VdmAnsiEnv,
3221 &CsrMsg[1],
3222 &VdmTask,
3223 dwCreationFlags,
3224 &StartupInfo,
3225 NULL);
3226 if (!NT_SUCCESS(Status))
3227 {
3228 /* Failed to inquire about VDM, fail the call */
3229 DPRINT1("VDM message failure for DOS: %lx\n", Status);
3231 Result = FALSE;
3232 goto Quickie;
3233 };
3234
3235 /* Handle possible VDM states */
3236 switch (CheckVdmMsg->VDMState & (VDM_NOT_LOADED |
3238 VDM_READY))
3239 {
3240 case VDM_NOT_LOADED:
3241 /* If VDM is not loaded, we'll do a partial undo */
3242 VdmUndoLevel = VDM_UNDO_PARTIAL;
3243
3244 /* A VDM process can't also be detached, so fail */
3245 if (dwCreationFlags & DETACHED_PROCESS)
3246 {
3247 DPRINT1("Detached process but no VDM, not allowed\n");
3249 return FALSE;
3250 }
3251
3252 /* Get the required parameters and names for launch */
3253 Result = BaseGetVdmConfigInfo(lpCommandLine,
3254 VdmTask,
3255 VdmBinaryType,
3256 &VdmString,
3257 &VdmReserve);
3258 if (!Result)
3259 {
3260 DPRINT1("VDM Configuration failed for DOS\n");
3262 goto Quickie;
3263 }
3264
3265 /* Update the command-line to launch VDM instead */
3266 lpCommandLine = VdmString.Buffer;
3267 lpApplicationName = NULL;
3268 break;
3269
3270 case VDM_READY:
3271 /* VDM is ready, so we have to undo everything */
3272 VdmUndoLevel = VDM_UNDO_REUSE;
3273
3274 /* Check if CSRSS wants us to wait on VDM */
3275 VdmWaitObject = CheckVdmMsg->WaitObjectForParent;
3276 break;
3277
3278 case VDM_NOT_READY:
3279 /* Something is wrong with VDM, we'll fail the call */
3280 DPRINT1("VDM is not ready for DOS\n");
3282 Result = FALSE;
3283 goto Quickie;
3284
3285 default:
3286 break;
3287 }
3288
3289 /* Since to get NULL, we allocate from 0x1, account for this */
3290 VdmReserve--;
3291
3292 /* This implies VDM is ready, so skip everything else */
3293 if (VdmWaitObject) goto VdmShortCircuit;
3294
3295 /* Don't inherit handles since we're doing VDM now */
3296 bInheritHandles = FALSE;
3297
3298 /* Had the user passed in environment? If so, destroy it */
3299 if ((lpEnvironment) &&
3300 !(dwCreationFlags & CREATE_UNICODE_ENVIRONMENT))
3301 {
3302 RtlDestroyEnvironment(lpEnvironment);
3303 }
3304
3305 /* Use our VDM Unicode environment instead */
3306 lpEnvironment = VdmUnicodeEnv.Buffer;
3307 }
3308 else
3309 {
3310 /* It's a batch file, get the extension */
3311 ExtBuffer = &PathName.Buffer[PathName.Length / sizeof(WCHAR) - 4];
3312
3313 /* Make sure the extensions are correct */
3314 if ((PathName.Length < (4 * sizeof(WCHAR))) ||
3315 ((_wcsnicmp(ExtBuffer, L".bat", 4)) &&
3316 (_wcsnicmp(ExtBuffer, L".cmd", 4))))
3317 {
3318 DPRINT1("'%wZ': Invalid EXE, and not a batch or script file\n", &PathName);
3320 Result = FALSE;
3321 goto Quickie;
3322 }
3323
3324 /* Check if we need to account for quotes around the path */
3325 CmdQuoteLength = CmdLineIsAppName || HasQuotes;
3326 if (!CmdLineIsAppName)
3327 {
3328 if (HasQuotes) CmdQuoteLength++;
3329 }
3330 else
3331 {
3332 CmdQuoteLength++;
3333 }
3334
3335 /* Calculate the length of the command line */
3336 CmdLineLength = wcslen(lpCommandLine);
3337 CmdLineLength += wcslen(CMD_STRING);
3338 CmdLineLength += CmdQuoteLength + sizeof(ANSI_NULL);
3339 CmdLineLength *= sizeof(WCHAR);
3340
3341 /* Allocate space for the new command line */
3342 AnsiCmdCommand = RtlAllocateHeap(RtlGetProcessHeap(),
3343 0,
3344 CmdLineLength);
3345 if (!AnsiCmdCommand)
3346 {
3348 Result = FALSE;
3349 goto Quickie;
3350 }
3351
3352 /* Build it */
3353 wcscpy(AnsiCmdCommand, CMD_STRING);
3354 if ((CmdLineIsAppName) || (HasQuotes))
3355 {
3356 wcscat(AnsiCmdCommand, L"\"");
3357 }
3358 wcscat(AnsiCmdCommand, lpCommandLine);
3359 if ((CmdLineIsAppName) || (HasQuotes))
3360 {
3361 wcscat(AnsiCmdCommand, L"\"");
3362 }
3363
3364 /* Create it as a Unicode String */
3365 RtlInitUnicodeString(&DebuggerString, AnsiCmdCommand);
3366
3367 /* Set the command line to this */
3368 lpCommandLine = DebuggerString.Buffer;
3369 lpApplicationName = NULL;
3370 DPRINT1("Retrying with: %S\n", lpCommandLine);
3371 }
3372
3373 /* We've already done all these checks, don't do them again */
3374 SkipSaferAndAppCompat = TRUE;
3375 goto AppNameRetry;
3376 }
3377
3379 {
3380 /* 64-bit binaries are not allowed to run on 32-bit ReactOS */
3381 DPRINT1("64-bit binary, failing\n");
3383 Result = FALSE;
3384 goto Quickie;
3385 }
3386
3388 {
3389 /* Set the correct last error for this */
3390 DPRINT1("File is offline, failing\n");
3392 break;
3393 }
3394
3395 default:
3396 {
3397 /* Any other error, convert it to a generic Win32 error */
3398 if (!NT_SUCCESS(Status))
3399 {
3400 DPRINT1("Failed to create section: %lx\n", Status);
3402 Result = FALSE;
3403 goto Quickie;
3404 }
3405
3406 /* Otherwise, this must be success */
3408 break;
3409 }
3410 }
3411
3412 /* Is this not a WOW application, but a WOW32 VDM was requested for it? */
3413 if (!(IsWowApp) && (dwCreationFlags & CREATE_SEPARATE_WOW_VDM))
3414 {
3415 /* Ignore the nonsensical request */
3416 dwCreationFlags &= ~CREATE_SEPARATE_WOW_VDM;
3417 }
3418
3419 /* Did we already check information for the section? */
3420 if (!QuerySection)
3421 {
3422 /* Get some information about the executable */
3423 Status = NtQuerySection(SectionHandle,
3425 &ImageInformation,
3426 sizeof(ImageInformation),
3427 NULL);
3428 if (!NT_SUCCESS(Status))
3429 {
3430 /* We failed, bail out */
3431 DPRINT1("Section query failed\n");
3433 Result = FALSE;
3434 goto Quickie;
3435 }
3436
3437 /* Don't check this later */
3438 QuerySection = TRUE;
3439 }
3440
3441 /* Check if this was linked as a DLL */
3442 if (ImageInformation.ImageCharacteristics & IMAGE_FILE_DLL)
3443 {
3444 /* These aren't valid images to try to execute! */
3445 DPRINT1("Trying to launch a DLL, failing\n");
3447 Result = FALSE;
3448 goto Quickie;
3449 }
3450
3451 /* Don't let callers pass in this flag -- we'll only get it from IFEO */
3452 Flags &= ~PROCESS_CREATE_FLAGS_LARGE_PAGES;
3453
3454 /* Clear the IFEO-missing flag, before we know for sure... */
3455 ParameterFlags &= ~2;
3456
3457 /* If the process is being debugged, only read IFEO if the PEB says so */
3458 if (!(dwCreationFlags & (DEBUG_PROCESS | DEBUG_ONLY_THIS_PROCESS)) ||
3460 {
3461 /* Let's do this! Attempt to open IFEO */
3462 IFEOStatus = LdrOpenImageFileOptionsKey(&PathName, 0, &KeyHandle);
3463 if (!NT_SUCCESS(IFEOStatus))
3464 {
3465 /* We failed, set the flag so we store this in the parameters */
3466 if (IFEOStatus == STATUS_OBJECT_NAME_NOT_FOUND) ParameterFlags |= 2;
3467 }
3468 else
3469 {
3470 /* Was this our first time going through this path? */
3471 if (!DebuggerCmdLine)
3472 {
3473 /* Allocate a buffer for the debugger path */
3474 DebuggerCmdLine = RtlAllocateHeap(RtlGetProcessHeap(),
3475 0,
3476 MAX_PATH * sizeof(WCHAR));
3477 if (!DebuggerCmdLine)
3478 {
3479 /* Close IFEO on failure */
3480 IFEOStatus = NtClose(KeyHandle);
3481 ASSERT(NT_SUCCESS(IFEOStatus));
3482
3483 /* Fail the call */
3485 Result = FALSE;
3486 goto Quickie;
3487 }
3488 }
3489
3490 /* Now query for the debugger */
3492 L"Debugger",
3493 REG_SZ,
3494 DebuggerCmdLine,
3495 MAX_PATH * sizeof(WCHAR),
3496 &ResultSize);
3497 if (!(NT_SUCCESS(IFEOStatus)) ||
3498 (ResultSize < sizeof(WCHAR)) ||
3499 (DebuggerCmdLine[0] == UNICODE_NULL))
3500 {
3501 /* If it's not there, or too small, or invalid, ignore it */
3502 RtlFreeHeap(RtlGetProcessHeap(), 0, DebuggerCmdLine);
3503 DebuggerCmdLine = NULL;
3504 }
3505
3506 /* Also query if we should map with large pages */
3508 L"UseLargePages",
3509 REG_DWORD,
3510 &UseLargePages,
3511 sizeof(UseLargePages),
3512 NULL);
3513 if ((NT_SUCCESS(IFEOStatus)) && (UseLargePages))
3514 {
3515 /* Do it! This is the only way this flag can be set */
3517 }
3518
3519 /* We're done with IFEO, can close it now */
3520 IFEOStatus = NtClose(KeyHandle);
3521 ASSERT(NT_SUCCESS(IFEOStatus));
3522 }
3523 }
3524
3525 /* Make sure the image was compiled for this processor */
3526 if ((ImageInformation.Machine < SharedUserData->ImageNumberLow) ||
3527 (ImageInformation.Machine > SharedUserData->ImageNumberHigh))
3528 {
3529 /* It was not -- raise a hard error */
3530 ErrorResponse = ResponseOk;
3531 ErrorParameters[0] = (ULONG_PTR)&PathName;
3533 1,
3534 1,
3535 ErrorParameters,
3536 OptionOk,
3537 &ErrorResponse);
3539 {
3540 /* If it's really old, return this error */
3542 }
3543 else
3544 {
3545 /* Otherwise, return a more modern error */
3547 }
3548
3549 /* Go to the failure path */
3550 DPRINT1("Invalid image architecture: %lx\n", ImageInformation.Machine);
3551 Result = FALSE;
3552 goto Quickie;
3553 }
3554
3555 /* Check if this isn't a Windows image */
3556 if ((ImageInformation.SubSystemType != IMAGE_SUBSYSTEM_WINDOWS_GUI) &&
3557 (ImageInformation.SubSystemType != IMAGE_SUBSYSTEM_WINDOWS_CUI))
3558 {
3559 /* Get rid of section-related information since we'll retry */
3560 NtClose(SectionHandle);
3561 SectionHandle = NULL;
3562 QuerySection = FALSE;
3563
3564 /* The only other non-Windows image type we support here is POSIX */
3565 if (ImageInformation.SubSystemType != IMAGE_SUBSYSTEM_POSIX_CUI)
3566 {
3567 /* Bail out if it's something else */
3569 Result = FALSE;
3570 goto Quickie;
3571 }
3572
3573 /* Now build the command-line to have posix launch this image */
3574 Result = BuildSubSysCommandLine(L"POSIX /P ",
3575 lpApplicationName,
3576 lpCommandLine,
3577 &DebuggerString);
3578 if (!Result)
3579 {
3580 /* Bail out if that failed */
3581 DPRINT1("Subsystem command line failed\n");
3582 goto Quickie;
3583 }
3584
3585 /* And re-try launching the process, with the new command-line now */
3586 lpCommandLine = DebuggerString.Buffer;
3587 lpApplicationName = NULL;
3588
3589 /* We've already done all these checks, don't do them again */
3590 SkipSaferAndAppCompat = TRUE;
3591 DPRINT1("Retrying with: %S\n", lpCommandLine);
3592 goto AppNameRetry;
3593 }
3594
3595 /* Was this image built for a version of Windows whose images we can run? */
3597 ImageInformation.SubSystemMinorVersion);
3598 if (!Result)
3599 {
3600 /* It was not, bail out */
3601 DPRINT1("Invalid subsystem version: %hu.%hu\n",
3602 ImageInformation.SubSystemMajorVersion,
3603 ImageInformation.SubSystemMinorVersion);
3605 goto Quickie;
3606 }
3607
3608 /* Check if there is a debugger associated with the application */
3609 if (DebuggerCmdLine)
3610 {
3611 /* Get the length of the command line */
3612 n = wcslen(lpCommandLine);
3613 if (!n)
3614 {
3615 /* There's no command line, use the application name instead */
3616 lpCommandLine = (LPWSTR)lpApplicationName;
3617 n = wcslen(lpCommandLine);
3618 }
3619
3620 /* Protect against overflow */
3622 {
3624 Result = FALSE;
3625 goto Quickie;
3626 }
3627
3628 /* Now add the length of the debugger command-line */
3629 n += wcslen(DebuggerCmdLine);
3630
3631 /* Again make sure we don't overflow */
3633 {
3635 Result = FALSE;
3636 goto Quickie;
3637 }
3638
3639 /* Account for the quotes and space between the two */
3640 n += sizeof("\" \"") - sizeof(ANSI_NULL);
3641
3642 /* Convert to bytes, and make sure we don't overflow */
3643 n *= sizeof(WCHAR);
3645 {
3647 Result = FALSE;
3648 goto Quickie;
3649 }
3650
3651 /* Allocate space for the string */
3652 DebuggerString.Buffer = RtlAllocateHeap(RtlGetProcessHeap(), 0, n);
3653 if (!DebuggerString.Buffer)
3654 {
3656 Result = FALSE;
3657 goto Quickie;
3658 }
3659
3660 /* Set the length */
3661 RtlInitEmptyUnicodeString(&DebuggerString,
3662 DebuggerString.Buffer,
3663 (USHORT)n);
3664
3665 /* Now perform the command line creation */
3666 ImageDbgStatus = RtlAppendUnicodeToString(&DebuggerString,
3667 DebuggerCmdLine);
3668 ASSERT(NT_SUCCESS(ImageDbgStatus));
3669 ImageDbgStatus = RtlAppendUnicodeToString(&DebuggerString, L" ");
3670 ASSERT(NT_SUCCESS(ImageDbgStatus));
3671 ImageDbgStatus = RtlAppendUnicodeToString(&DebuggerString, lpCommandLine);
3672 ASSERT(NT_SUCCESS(ImageDbgStatus));
3673
3674 /* Make sure it all looks nice */
3675 DbgPrint("BASE: Calling debugger with '%wZ'\n", &DebuggerString);
3676
3677 /* Update the command line and application name */
3678 lpCommandLine = DebuggerString.Buffer;
3679 lpApplicationName = NULL;
3680
3681 /* Close all temporary state */
3682 NtClose(SectionHandle);
3683 SectionHandle = NULL;
3684 QuerySection = FALSE;
3685
3686 /* Free all temporary memory */
3687 RtlFreeHeap(RtlGetProcessHeap(), 0, NameBuffer);
3688 NameBuffer = NULL;
3689 RtlFreeHeap(RtlGetProcessHeap(), 0, FreeBuffer);
3690 FreeBuffer = NULL;
3691 RtlFreeHeap(RtlGetProcessHeap(), 0, DebuggerCmdLine);
3692 DebuggerCmdLine = NULL;
3693 DPRINT1("Retrying with: %S\n", lpCommandLine);
3694 goto AppNameRetry;
3695 }
3696
3697 /* Initialize the process object attributes */
3698 ObjectAttributes = BaseFormatObjectAttributes(&LocalObjectAttributes,
3699 lpProcessAttributes,
3700 NULL);
3701 if ((hUserToken) && (lpProcessAttributes))
3702 {
3703 /* Augment them with information from the user */
3704
3705 LocalProcessAttributes = *lpProcessAttributes;
3706 LocalProcessAttributes.lpSecurityDescriptor = NULL;
3707 ObjectAttributes = BaseFormatObjectAttributes(&LocalObjectAttributes,
3708 &LocalProcessAttributes,
3709 NULL);
3710 }
3711
3712 /* CREATE_BREAKAWAY_FROM_JOB allows the child process to break
3713 * away from the job associated with the calling process */
3714 if (dwCreationFlags & CREATE_BREAKAWAY_FROM_JOB)
3715 {
3717 }
3718
3719 /* Check if we're going to be debugged */
3720 if (dwCreationFlags & (DEBUG_PROCESS | DEBUG_ONLY_THIS_PROCESS))
3721 {
3722 /* Connect to DbgUi */
3724 if (!NT_SUCCESS(Status))
3725 {
3726 DPRINT1("Failed to connect to DbgUI!\n");
3728 Result = FALSE;
3729 goto Quickie;
3730 }
3731
3732 /* Get the debug object */
3733 DebugHandle = DbgUiGetThreadDebugObject();
3734
3735 /* Check if only this process will be debugged */
3736 if (dwCreationFlags & DEBUG_ONLY_THIS_PROCESS)
3737 {
3738 /* Set process flag */
3740 }
3741 }
3742
3743 /* Set inherit flag */
3744 if (bInheritHandles) Flags |= PROCESS_CREATE_FLAGS_INHERIT_HANDLES;
3745
3746 /* Check if the process should be created with large pages */
3747 HavePrivilege = FALSE;
3748 PrivilegeState = NULL;
3750 {
3751 /* Acquire the required privilege so that the kernel won't fail the call */
3752 PrivilegeValue = SE_LOCK_MEMORY_PRIVILEGE;
3753 Status = RtlAcquirePrivilege(&PrivilegeValue, 1, 0, &PrivilegeState);
3754 if (NT_SUCCESS(Status))
3755 {
3756 /* Remember to release it later */
3757 HavePrivilege = TRUE;
3758 }
3759 }
3760
3761 /* Save the current TIB value since kernel overwrites it to store PEB */
3762 TibValue = Teb->NtTib.ArbitraryUserPointer;
3763
3764 /* Tell the kernel to create the process */
3769 Flags,
3770 SectionHandle,
3771 DebugHandle,
3772 NULL,
3773 InJob);
3774
3775 /* Load the PEB address from the hacky location where the kernel stores it */
3776 RemotePeb = Teb->NtTib.ArbitraryUserPointer;
3777
3778 /* And restore the old TIB value */
3779 Teb->NtTib.ArbitraryUserPointer = TibValue;
3780
3781 /* Release the large page privilege if we had acquired it */
3782 if (HavePrivilege) RtlReleasePrivilege(PrivilegeState);
3783
3784 /* And now check if the kernel failed to create the process */
3785 if (!NT_SUCCESS(Status))
3786 {
3787 /* Go to failure path */
3788 DPRINT1("Failed to create process: %lx\n", Status);
3790 Result = FALSE;
3791 goto Quickie;
3792 }
3793
3794 /* Check if there is a priority class to set */
3795 if (PriorityClass.PriorityClass)
3796 {
3797 /* Reset current privilege state */
3798 RealTimePrivilegeState = NULL;
3799
3800 /* Is realtime priority being requested? */
3802 {
3803 /* Check if the caller has real-time access, and enable it if so */
3804 RealTimePrivilegeState = BasepIsRealtimeAllowed(TRUE);
3805 }
3806
3807 /* Set the new priority class and release the privilege */
3810 &PriorityClass,
3811 sizeof(PROCESS_PRIORITY_CLASS));
3812 if (RealTimePrivilegeState) RtlReleasePrivilege(RealTimePrivilegeState);
3813
3814 /* Check if we failed to set the priority class */
3815 if (!NT_SUCCESS(Status))
3816 {
3817 /* Bail out on failure */
3818 DPRINT1("Failed to set priority class: %lx\n", Status);
3820 Result = FALSE;
3821 goto Quickie;
3822 }
3823 }
3824
3825 /* Check if the caller wants the default error mode */
3826 if (dwCreationFlags & CREATE_DEFAULT_ERROR_MODE)
3827 {
3828 /* Set Error Mode to only fail on critical errors */
3829 HardErrorMode = SEM_FAILCRITICALERRORS;
3832 &HardErrorMode,
3833 sizeof(ULONG));
3834 }
3835
3836 /* Check if this was a VDM binary */
3837 if (VdmBinaryType)
3838 {
3839 /* Update VDM by telling it the process has now been created */
3840 VdmWaitObject = ProcessHandle;
3842 &VdmWaitObject,
3843 VdmTask,
3844 VdmBinaryType);
3845
3846 if (!Result)
3847 {
3848 /* Bail out on failure */
3849 DPRINT1("Failed to update VDM with wait object\n");
3850 VdmWaitObject = NULL;
3851 goto Quickie;
3852 }
3853
3854 /* At this point, a failure means VDM has to undo all the state */
3855 VdmUndoLevel |= VDM_UNDO_FULL;
3856 }
3857
3858 /* Check if VDM needed reserved low-memory */
3859 if (VdmReserve)
3860 {
3861 /* Reserve the requested allocation */
3862 RegionSize = VdmReserve;
3864 &BaseAddress,
3865 0,
3866 &RegionSize,
3869 if (!NT_SUCCESS(Status))
3870 {
3871 /* Bail out on failure */
3872 DPRINT1("Failed to reserve memory for VDM: %lx\n", Status);
3874 Result = FALSE;
3875 goto Quickie;
3876 }
3877
3878 VdmReserve = (ULONG)RegionSize;
3879 }
3880
3881 /* Check if we've already queried information on the section */
3882 if (!QuerySection)
3883 {
3884 /* We haven't, so get some information about the executable */
3885 Status = NtQuerySection(SectionHandle,
3887 &ImageInformation,
3888 sizeof(ImageInformation),
3889 NULL);
3890 if (!NT_SUCCESS(Status))
3891 {
3892 /* Bail out on failure */
3893 DPRINT1("Failed to query section: %lx\n", Status);
3895 Result = FALSE;
3896 goto Quickie;
3897 }
3898
3899 /* If we encounter a restart, don't re-query this information again */
3900 QuerySection = TRUE;
3901 }
3902
3903 /* Do we need to apply SxS to this image? (On x86 this flag is set by PeFmtCreateSection) */
3905 {
3906 /* Too bad, we don't support this yet */
3907 DPRINT("Image should receive SxS Fusion Isolation\n");
3908 }
3909
3910 /* There's some SxS flag that we need to set if fusion flags have 1 set */
3911 if (FusionFlags & 1) CreateProcessMsg->Sxs.Flags |= 0x10;
3912
3913 /* Check if we have a current directory */
3914 if (lpCurrentDirectory)
3915 {
3916 /* Allocate a buffer so we can keep a Unicode copy */
3917 DPRINT("Current directory: %S\n", lpCurrentDirectory);
3918 CurrentDirectory = RtlAllocateHeap(RtlGetProcessHeap(),
3919 0,
3920 (MAX_PATH * sizeof(WCHAR)) +
3921 sizeof(UNICODE_NULL));
3922 if (!CurrentDirectory)
3923 {
3924 /* Bail out if this failed */
3926 Result = FALSE;
3927 goto Quickie;
3928 }
3929
3930 /* Get the length in Unicode */
3931 Length = GetFullPathNameW(lpCurrentDirectory,
3932 MAX_PATH,
3934 &FilePart);
3935 if (Length > MAX_PATH)
3936 {
3937 /* The directory is too long, so bail out */
3939 Result = FALSE;
3940 goto Quickie;
3941 }
3942
3943 /* Make sure the directory is actually valid */
3944 FileAttribs = GetFileAttributesW(CurrentDirectory);
3945 if ((FileAttribs == INVALID_FILE_ATTRIBUTES) ||
3946 !(FileAttribs & FILE_ATTRIBUTE_DIRECTORY))
3947 {
3948 /* It isn't, so bail out */
3949 DPRINT1("Current directory is invalid\n");
3951 Result = FALSE;
3952 goto Quickie;
3953 }
3954 }
3955
3956 /* Insert quotes if needed */
3957 if ((QuotesNeeded) || (CmdLineIsAppName))
3958 {
3959 /* Allocate our buffer, plus enough space for quotes and a NULL */
3960 QuotedCmdLine = RtlAllocateHeap(RtlGetProcessHeap(),
3961 0,
3962 (wcslen(lpCommandLine) * sizeof(WCHAR)) +
3963 (2 * sizeof(L'\"') + sizeof(UNICODE_NULL)));
3964 if (QuotedCmdLine)
3965 {
3966 /* Copy the first quote */
3967 wcscpy(QuotedCmdLine, L"\"");
3968
3969 /* Save the current null-character */
3970 if (QuotesNeeded)
3971 {
3972 SaveChar = *NullBuffer;
3973 *NullBuffer = UNICODE_NULL;
3974 }
3975
3976 /* Copy the command line and the final quote */
3977 wcscat(QuotedCmdLine, lpCommandLine);
3978 wcscat(QuotedCmdLine, L"\"");
3979
3980 /* Copy the null-char back */
3981 if (QuotesNeeded)
3982 {
3983 *NullBuffer = SaveChar;
3984 wcscat(QuotedCmdLine, NullBuffer);
3985 }
3986 }
3987 else
3988 {
3989 /* We can't put quotes around the thing, so try it anyway */
3990 if (QuotesNeeded) QuotesNeeded = FALSE;
3991 if (CmdLineIsAppName) CmdLineIsAppName = FALSE;
3992 }
3993 }
3994
3995 /* Use isolation if needed */
3996 if (CreateProcessMsg->Sxs.Flags & 1) ParameterFlags |= 1;
3997
3998 /* Set the new command-line if needed */
3999 if ((QuotesNeeded) || (CmdLineIsAppName)) lpCommandLine = QuotedCmdLine;
4000
4001 /* Call the helper function in charge of RTL_USER_PROCESS_PARAMETERS */
4002 Result = BasePushProcessParameters(ParameterFlags,
4004 RemotePeb,
4005 lpApplicationName,
4007 lpCommandLine,
4008 lpEnvironment,
4009 &StartupInfo,
4010 dwCreationFlags | NoWindow,
4011 bInheritHandles,
4012 IsWowApp ? IMAGE_SUBSYSTEM_WINDOWS_GUI: 0,
4013 AppCompatData,
4014 AppCompatDataSize);
4015 if (!Result)
4016 {
4017 /* The remote process would have an undefined state, so fail the call */
4018 DPRINT1("BasePushProcessParameters failed\n");
4019 goto Quickie;
4020 }
4021
4022 /* Free the VDM command line string as it's no longer needed */
4023 RtlFreeUnicodeString(&VdmString);
4024 VdmString.Buffer = NULL;
4025
4026 /* Non-VDM console applications usually inherit handles unless specified */
4027 if (!(VdmBinaryType) &&
4028 !(bInheritHandles) &&
4029 !(StartupInfo.dwFlags & STARTF_USESTDHANDLES) &&
4030 !(dwCreationFlags & (CREATE_NO_WINDOW |
4032 DETACHED_PROCESS)) &&
4033 (ImageInformation.SubSystemType == IMAGE_SUBSYSTEM_WINDOWS_CUI))
4034 {
4035 /* Get the remote parameters */
4037 &RemotePeb->ProcessParameters,
4038 &ProcessParameters,
4040 NULL);
4041 if (NT_SUCCESS(Status))
4042 {
4043 /* Duplicate standard input unless it's a console handle */
4045 {
4048 &ProcessParameters->StandardInput);
4049 }
4050
4051 /* Duplicate standard output unless it's a console handle */
4053 {
4056 &ProcessParameters->StandardOutput);
4057 }
4058
4059 /* Duplicate standard error unless it's a console handle */
4061 {
4064 &ProcessParameters->StandardError);
4065 }
4066 }
4067 }
4068
4069 /* Create the Thread's Stack */
4070 StackSize = max(256 * 1024, ImageInformation.MaximumStackSize);
4072 ImageInformation.CommittedStackSize,
4073 StackSize,
4074 &InitialTeb);
4075 if (!NT_SUCCESS(Status))
4076 {
4077 DPRINT1("Creating the thread stack failed: %lx\n", Status);
4079 Result = FALSE;
4080 goto Quickie;
4081 }
4082
4083 /* Create the Thread's Context */
4085 RemotePeb,
4086 ImageInformation.TransferAddress,
4087 InitialTeb.StackBase,
4088 0);
4089
4090 /* Convert the thread attributes */
4091 ObjectAttributes = BaseFormatObjectAttributes(&LocalObjectAttributes,
4092 lpThreadAttributes,
4093 NULL);
4094 if ((hUserToken) && (lpThreadAttributes))
4095 {
4096 /* If the caller specified a user token, zero the security descriptor */
4097 LocalThreadAttributes = *lpThreadAttributes;
4098 LocalThreadAttributes.lpSecurityDescriptor = NULL;
4099 ObjectAttributes = BaseFormatObjectAttributes(&LocalObjectAttributes,
4100 &LocalThreadAttributes,
4101 NULL);
4102 }
4103
4104 /* Create the Kernel Thread Object */
4105 Status = NtCreateThread(&ThreadHandle,
4109 &ClientId,
4110 &Context,
4111 &InitialTeb,
4112 TRUE);
4113 if (!NT_SUCCESS(Status))
4114 {
4115 /* A process is not allowed to exist without a main thread, so fail */
4116 DPRINT1("Creating the main thread failed: %lx\n", Status);
4118 Result = FALSE;
4119 goto Quickie;
4120 }
4121
4122 /* Begin filling out the CSRSS message, first with our IDs and handles */
4123 CreateProcessMsg->ProcessHandle = ProcessHandle;
4124 CreateProcessMsg->ThreadHandle = ThreadHandle;
4125 CreateProcessMsg->ClientId = ClientId;
4126
4127 /* Write the remote PEB address and clear it locally, we no longer use it */
4128 CreateProcessMsg->PebAddressNative = RemotePeb;
4129#ifdef _WIN64
4130 DPRINT("TODO: WOW64 is not supported yet\n");
4131 CreateProcessMsg->PebAddressWow64 = 0;
4132#else
4133 CreateProcessMsg->PebAddressWow64 = (ULONG)RemotePeb;
4134#endif
4135 RemotePeb = NULL;
4136
4137 /* Now check what kind of architecture this image was made for */
4138 switch (ImageInformation.Machine)
4139 {
4140 /* IA32, IA64 and AMD64 are supported in Server 2003 */
4143 break;
4146 break;
4149 break;
4150
4151 /* Anything else results in image unknown -- but no failure */
4152 default:
4153 DbgPrint("kernel32: No mapping for ImageInformation.Machine == %04x\n",
4154 ImageInformation.Machine);
4156 break;
4157 }
4158
4159 /* Write the input creation flags except any debugger-related flags */
4160 CreateProcessMsg->CreationFlags = dwCreationFlags &
4162
4163 /* CSRSS needs to know if this is a GUI app or not */
4164 if ((ImageInformation.SubSystemType == IMAGE_SUBSYSTEM_WINDOWS_GUI) ||
4165 (IsWowApp))
4166 {
4167 /*
4168 * For GUI apps we turn on the 2nd bit. This allow CSRSS server dlls
4169 * (basesrv in particular) to know whether or not this is a GUI or a
4170 * TUI application.
4171 */
4172 AddToHandle(CreateProcessMsg->ProcessHandle, 2);
4173
4174 /* Also check if the parent is also a GUI process */
4176 if ((NtHeaders) &&
4178 {
4179 /* Let it know that it should display the hourglass mouse cursor */
4180 AddToHandle(CreateProcessMsg->ProcessHandle, 1);
4181 }
4182 }
4183
4184 /* For all apps, if this flag is on, the hourglass mouse cursor is shown.
4185 * Likewise, the opposite holds as well, and no-feedback has precedence. */
4186 if (StartupInfo.dwFlags & STARTF_FORCEONFEEDBACK)
4187 {
4188 AddToHandle(CreateProcessMsg->ProcessHandle, 1);
4189 }
4190 if (StartupInfo.dwFlags & STARTF_FORCEOFFFEEDBACK)
4191 {
4192 RemoveFromHandle(CreateProcessMsg->ProcessHandle, 1);
4193 }
4194
4195 /* Also store which kind of VDM app (if any) this is */
4196 CreateProcessMsg->VdmBinaryType = VdmBinaryType;
4197
4198 /* And if it really is a VDM app... */
4199 if (VdmBinaryType)
4200 {
4201 /* Store the VDM console handle (none if inherited or WOW app) and the task ID */
4202 CreateProcessMsg->hVDM = VdmTask ? NULL : Peb->ProcessParameters->ConsoleHandle;
4203 CreateProcessMsg->VdmTask = VdmTask;
4204 }
4205 else if (VdmReserve)
4206 {
4207 /* Extended VDM, set a flag */
4208 CreateProcessMsg->VdmBinaryType |= BINARY_TYPE_WOW_EX;
4209 }
4210
4211 /* Check if there's side-by-side assembly data associated with the process */
4212 if (CreateProcessMsg->Sxs.Flags)
4213 {
4214 /* This should not happen in ReactOS yet */
4215 DPRINT1("This is an SxS Message -- should not happen yet\n");
4218 Result = FALSE;
4219 goto Quickie;
4220 }
4221
4222 /* We are finally ready to call CSRSS to tell it about our new process! */
4224 CaptureBuffer,
4227 sizeof(*CreateProcessMsg));
4228
4229 /* CSRSS has returned, free the capture buffer now if we had one */
4230 if (CaptureBuffer)
4231 {
4232 CsrFreeCaptureBuffer(CaptureBuffer);
4233 CaptureBuffer = NULL;
4234 }
4235
4236 /* Check if CSRSS failed to accept ownership of the new Windows process */
4237 if (!NT_SUCCESS(CsrMsg[0].Status))
4238 {
4239 /* Terminate the process and enter failure path with the CSRSS status */
4240 DPRINT1("Failed to tell csrss about new process\n");
4241 BaseSetLastNTError(CsrMsg[0].Status);
4243 Result = FALSE;
4244 goto Quickie;
4245 }
4246
4247 /* Check if we have a token due to Authz/Safer, not passed by the user */
4248 if ((TokenHandle) && !(hUserToken))
4249 {
4250 /* Replace the process and/or thread token with the one from Safer */
4253 ThreadHandle);
4254 if (!NT_SUCCESS(Status))
4255 {
4256 /* If this failed, kill the process and enter the failure path */
4257 DPRINT1("Failed to update process token: %lx\n", Status);
4260 Result = FALSE;
4261 goto Quickie;
4262 }
4263 }
4264
4265 /* Check if a job was associated with this process */
4266 if (JobHandle)
4267 {
4268 /* Bind the process and job together now */
4270 if (!NT_SUCCESS(Status))
4271 {
4272 /* Kill the process and enter the failure path if binding failed */
4273 DPRINT1("Failed to assign process to job: %lx\n", Status);
4276 Result = FALSE;
4277 goto Quickie;
4278 }
4279 }
4280
4281 /* Finally, resume the thread to actually get the process started */
4282 if (!(dwCreationFlags & CREATE_SUSPENDED))
4283 {
4284 NtResumeThread(ThreadHandle, &ResumeCount);
4285 }
4286
4287VdmShortCircuit:
4288 /* We made it this far, meaning we have a fully created process and thread */
4289 Result = TRUE;
4290
4291 /* Anyone doing a VDM undo should now undo everything, since we are done */
4292 if (VdmUndoLevel) VdmUndoLevel |= VDM_UNDO_COMPLETED;
4293
4294 /* Having a VDM wait object implies this must be a VDM process */
4295 if (VdmWaitObject)
4296 {
4297 /* Check if it's a 16-bit separate WOW process */
4298 if (VdmBinaryType == BINARY_TYPE_SEPARATE_WOW)
4299 {
4300 /* OR-in the special flag to indicate this, and return to caller */
4301 AddToHandle(VdmWaitObject, 2);
4302 lpProcessInformation->hProcess = VdmWaitObject;
4303
4304 /* Check if this was a re-used VDM */
4305 if (VdmUndoLevel & VDM_UNDO_REUSE)
4306 {
4307 /* No Client ID should be returned in this case */
4310 }
4311 }
4312 else
4313 {
4314 /* OR-in the special flag to indicate this is not a separate VDM,
4315 * and return the handle to the caller */
4316 AddToHandle(VdmWaitObject, 1);
4317 lpProcessInformation->hProcess = VdmWaitObject;
4318 }
4319
4320 /* Close the original process handle, since it's not needed for VDM */
4322 }
4323 else
4324 {
4325 /* This is a regular process, so return the real process handle */
4326 lpProcessInformation->hProcess = ProcessHandle;
4327 }
4328
4329 /* Return the rest of the process information based on what we have so far */
4330 lpProcessInformation->hThread = ThreadHandle;
4331 lpProcessInformation->dwProcessId = HandleToUlong(ClientId.UniqueProcess);
4332 lpProcessInformation->dwThreadId = HandleToUlong(ClientId.UniqueThread);
4333
4334 /* NULL these out here so we know to treat this as a success scenario */
4336 ThreadHandle = NULL;
4337
4338Quickie:
4339 /* Free the debugger command line if one was allocated */
4340 if (DebuggerCmdLine) RtlFreeHeap(RtlGetProcessHeap(), 0, DebuggerCmdLine);
4341
4342 /* Check if an SxS full path as queried */
4343 if (PathBuffer)
4344 {
4345 /* Reinitialize the executable path */
4346 RtlInitEmptyUnicodeString(&SxsWin32ExePath, NULL, 0);
4347 SxsWin32ExePath.Length = 0;
4348
4349 /* Free the path buffer */
4350 RtlFreeHeap(RtlGetProcessHeap(), 0, PathBuffer);
4351 }
4352
4353#if _SXS_SUPPORT_ENABLED_
4354 /* Check if this was a non-VDM process */
4355 if (!VdmBinaryType)
4356 {
4357 /* Then it must've had SxS data, so close the handles used for it */
4358 BasepSxsCloseHandles(&Handles);
4359 BasepSxsCloseHandles(&FileHandles);
4360
4361 /* Check if we built SxS byte buffers for this create process request */
4362 if (SxsConglomeratedBuffer)
4363 {
4364 /* Loop all of them */
4365 for (i = 0; i < 5; i++)
4366 {
4367 /* Check if this one was allocated */
4368 ThisBuffer = SxsStaticBuffers[i];
4369 if (ThisBuffer)
4370 {
4371 /* Get the underlying RTL_BUFFER structure */
4372 ByteBuffer = &ThisBuffer->ByteBuffer;
4373 if ((ThisBuffer != (PVOID)-8) && (ByteBuffer->Buffer))
4374 {
4375 /* Check if it was dynamic */
4376 if (ByteBuffer->Buffer != ByteBuffer->StaticBuffer)
4377 {
4378 /* Free it from the heap */
4379 FreeString.Buffer = (PWCHAR)ByteBuffer->Buffer;
4381 }
4382
4383 /* Reset the buffer to its static data */
4384 ByteBuffer->Buffer = ByteBuffer->StaticBuffer;
4385 ByteBuffer->Size = ByteBuffer->StaticSize;
4386 }
4387
4388 /* Reset the string to the static buffer */
4389 RtlInitEmptyUnicodeString(&ThisBuffer->String,
4390 (PWCHAR)ByteBuffer->StaticBuffer,
4391 ByteBuffer->StaticSize);
4392 if (ThisBuffer->String.Buffer)
4393 {
4394 /* Also NULL-terminate it */
4395 *ThisBuffer->String.Buffer = UNICODE_NULL;
4396 }
4397 }
4398 }
4399 }
4400 }
4401#endif
4402 /* Check if an environment was passed in */
4403 if ((lpEnvironment) && !(dwCreationFlags & CREATE_UNICODE_ENVIRONMENT))
4404 {
4405 /* Destroy it */
4406 RtlDestroyEnvironment(lpEnvironment);
4407
4408 /* If this was the VDM environment too, clear that as well */
4409 if (VdmUnicodeEnv.Buffer == lpEnvironment) VdmUnicodeEnv.Buffer = NULL;
4410 lpEnvironment = NULL;
4411 }
4412
4413 /* Unconditionally free all the name parsing buffers we always allocate */
4414 RtlFreeHeap(RtlGetProcessHeap(), 0, QuotedCmdLine);
4415 RtlFreeHeap(RtlGetProcessHeap(), 0, NameBuffer);
4416 RtlFreeHeap(RtlGetProcessHeap(), 0, CurrentDirectory);
4417 RtlFreeHeap(RtlGetProcessHeap(), 0, FreeBuffer);
4418
4419 /* Close open file/section handles */
4421 if (SectionHandle) NtClose(SectionHandle);
4422
4423 /* If we have a thread handle, this was a failure path */
4424 if (ThreadHandle)
4425 {
4426 /* So kill the process and close the thread handle */
4428 NtClose(ThreadHandle);
4429 }
4430
4431 /* If we have a process handle, this was a failure path, so close it */
4433
4434 /* Thread/process handles, if any, are now processed. Now close this one. */
4435 if (JobHandle) NtClose(JobHandle);
4436
4437 /* Check if we had created a token */
4438 if (TokenHandle)
4439 {
4440 /* And if the user asked for one */
4441 if (hUserToken)
4442 {
4443 /* Then return it */
4444 *hNewToken = TokenHandle;
4445 }
4446 else
4447 {
4448 /* User didn't want it, so we used it temporarily -- close it */
4450 }
4451 }
4452
4453 /* Free any temporary app compatibility data, it's no longer needed */
4454 BasepFreeAppCompatData(AppCompatData, AppCompatSxsData);
4455
4456 /* Free a few strings. The API takes care of these possibly being NULL */
4457 RtlFreeUnicodeString(&VdmString);
4458 RtlFreeUnicodeString(&DebuggerString);
4459
4460 /* Check if we had built any sort of VDM environment */
4461 if ((VdmAnsiEnv.Buffer) || (VdmUnicodeEnv.Buffer))
4462 {
4463 /* Free it */
4464 BaseDestroyVDMEnvironment(&VdmAnsiEnv, &VdmUnicodeEnv);
4465 }
4466
4467 /* Check if this was any kind of VDM application that we ended up creating */
4468 if ((VdmUndoLevel) && (!(VdmUndoLevel & VDM_UNDO_COMPLETED)))
4469 {
4470 /* Send an undo */
4472 (PHANDLE)&VdmTask,
4473 VdmUndoLevel,
4474 VdmBinaryType);
4475
4476 /* And close whatever VDM handle we were using for notifications */
4477 if (VdmWaitObject) NtClose(VdmWaitObject);
4478 }
4479
4480 /* Check if we ended up here with an allocated search path, and free it */
4481 if (SearchPath) RtlFreeHeap(RtlGetProcessHeap(), 0, SearchPath);
4482
4483 /* Finally, return the API's result */
4484 return Result;
4485}
NTSTATUS NTAPI NtCreateSection(OUT PHANDLE SectionHandle, IN ACCESS_MASK DesiredAccess, IN POBJECT_ATTRIBUTES ObjectAttributes OPTIONAL, IN PLARGE_INTEGER MaximumSize OPTIONAL, IN ULONG SectionPageProtection OPTIONAL, IN ULONG AllocationAttributes, IN HANDLE FileHandle OPTIONAL)
Definition: section.c:3097
static IN ULONG IN PWSTR OUT PCWSTR OUT PBOOLEAN OUT PATH_TYPE_AND_UNKNOWN * PathType
static ULONG StackSize
Definition: StackOverflow.c:21
NTSTATUS WINAPI BasepCheckBadapp(IN HANDLE FileHandle, IN PWCHAR ApplicationName, IN PWCHAR Environment, IN USHORT ExeType, IN PVOID *SdbQueryAppCompatData, IN PULONG SdbQueryAppCompatDataSize, IN PVOID *SxsData, IN PULONG SxsDataSize, OUT PULONG FusionFlags)
Definition: appcache.c:374
VOID WINAPI BasepFreeAppCompatData(IN PVOID AppCompatData, IN PVOID AppCompatSxsData)
Definition: appcache.c:444
#define REG_SZ
Definition: layer.c:22
#define FILE_NON_DIRECTORY_FILE
Definition: constants.h:492
HANDLE hUserToken
Definition: install.c:39
static DWORD ResumeCount
Definition: database.c:31
@ BasepCreateProcess
Definition: basemsg.h:21
#define BASESRV_SERVERDLL_INDEX
Definition: basemsg.h:15
#define HandleToUlong(h)
Definition: basetsd.h:73
IN PUNICODE_STRING IN POBJECT_ATTRIBUTES ObjectAttributes
Definition: conport.c:36
#define CSR_CREATE_API_NUMBER(ServerId, ApiId)
Definition: csrmsg.h:37
_In_ PIO_STATUS_BLOCK IoStatusBlock
Definition: dispmprt.h:608
_In_ D3DDDI_VIDEO_PRESENT_TARGET_ID _In_ ULONG _In_ ULONG Flags
Definition: dispmprt.h:245
#define CloseHandle
Definition: compat.h:739
#define ERROR_INVALID_PARAMETER
Definition: compat.h:101
#define OPEN_EXISTING
Definition: compat.h:775
#define INVALID_HANDLE_VALUE
Definition: compat.h:731
#define GENERIC_READ
Definition: compat.h:135
#define RtlImageNtHeader
Definition: compat.h:806
#define CreateFileW
Definition: compat.h:741
#define FILE_ATTRIBUTE_NORMAL
Definition: compat.h:137
#define ERROR_ACCESS_DENIED
Definition: compat.h:97
#define FILE_SHARE_READ
Definition: compat.h:136
PBASE_STATIC_SERVER_DATA BaseStaticServerData
Definition: dllmain.c:19
DWORD WINAPI GetFileAttributesW(LPCWSTR lpFileName)
Definition: fileinfo.c:636
LPWSTR WINAPI BaseComputeProcessExePath(IN LPWSTR FullPath)
Definition: path.c:463
DWORD WINAPI SearchPathW(IN LPCWSTR lpPath OPTIONAL, IN LPCWSTR lpFileName, IN LPCWSTR lpExtension OPTIONAL, IN DWORD nBufferLength, OUT LPWSTR lpBuffer, OUT LPWSTR *lpFilePart OPTIONAL)
Definition: path.c:1397
BOOLEAN WINAPI BasePushProcessParameters(IN ULONG ParameterFlags, IN HANDLE ProcessHandle, IN PPEB RemotePeb, IN LPCWSTR ApplicationPathName, IN LPWSTR lpCurrentDirectory, IN LPWSTR lpCommandLine, IN LPVOID lpEnvironment, IN LPSTARTUPINFOW StartupInfo, IN DWORD CreationFlags, IN BOOL InheritHandles, IN ULONG ImageSubsystem, IN PVOID AppCompatData, IN ULONG AppCompatDataSize)
Definition: proc.c:484
NTSTATUS WINAPI BasepCheckWebBladeHashes(IN HANDLE FileHandle)
Definition: proc.c:149
VOID WINAPI StuffStdHandle(IN HANDLE ProcessHandle, IN HANDLE StandardHandle, IN PHANDLE Address)
Definition: proc.c:57
BOOLEAN WINAPI BuildSubSysCommandLine(IN LPCWSTR SubsystemName, IN LPCWSTR ApplicationName, IN LPCWSTR CommandLine, OUT PUNICODE_STRING SubsysCommandLine)
Definition: proc.c:89
NTSTATUS WINAPI BasepIsProcessAllowed(IN LPWSTR ApplicationName)
Definition: proc.c:202
#define AddToHandle(x, y)
Definition: proc.c:2126
NTSTATUS WINAPI BasepReplaceProcessThreadTokens(IN HANDLE TokenHandle, IN HANDLE ProcessHandle, IN HANDLE ThreadHandle)
Definition: proc.c:354
#define THREAD_ALL_ACCESS_NT6
Definition: proc.c:18
VOID WINAPI BasepSxsCloseHandles(IN PBASE_MSG_SXS_HANDLES Handles)
Definition: proc.c:417
#define CMD_STRING
Definition: proc.c:51
#define RemoveFromHandle(x, y)
Definition: proc.c:2127
BOOLEAN WINAPI BasepIsImageVersionOk(IN ULONG ImageMajorVersion, IN ULONG ImageMinorVersion)
Definition: proc.c:123
NTSTATUS WINAPI BaseCreateStack(_In_ HANDLE hProcess, _In_opt_ SIZE_T StackCommit, _In_opt_ SIZE_T StackReserve, _Out_ PINITIAL_TEB InitialTeb)
Definition: utils.c:381
VOID WINAPI BaseInitializeContext(IN PCONTEXT Context, IN PVOID Parameter, IN PVOID StartAddress, IN PVOID StackAddress, IN ULONG ContextType)
Definition: utils.c:540
POBJECT_ATTRIBUTES WINAPI BaseFormatObjectAttributes(OUT POBJECT_ATTRIBUTES ObjectAttributes, IN PSECURITY_ATTRIBUTES SecurityAttributes OPTIONAL, IN PUNICODE_STRING ObjectName)
Definition: utils.c:331
NTSTATUS WINAPI BasepCheckWinSaferRestrictions(IN HANDLE UserToken, IN LPWSTR ApplicationName, IN HANDLE FileHandle, OUT PBOOLEAN InJob, OUT PHANDLE NewToken, OUT PHANDLE JobHandle)
Definition: utils.c:949
PVOID WINAPI BasepIsRealtimeAllowed(IN BOOLEAN Keep)
Definition: utils.c:692
ULONG WINAPI BaseIsDosApplication(IN PUNICODE_STRING PathName, IN NTSTATUS Status)
Definition: vdm.c:66
BOOL NTAPI BaseDestroyVDMEnvironment(IN PANSI_STRING AnsiEnv, IN PUNICODE_STRING UnicodeEnv)
Definition: vdm.c:1034
BOOL WINAPI BaseGetVdmConfigInfo(IN LPCWSTR CommandLineReserved, IN ULONG DosSeqId, IN ULONG BinaryType, IN PUNICODE_STRING CmdLineString, OUT PULONG VdmSize)
Definition: vdm.c:652
BOOL WINAPI BaseUpdateVDMEntry(IN ULONG UpdateIndex, IN OUT PHANDLE WaitHandle, IN ULONG IndexInfo, IN ULONG BinaryType)
Definition: vdm.c:542
BOOL NTAPI BaseCreateVDMEnvironment(IN PWCHAR lpEnvironment, OUT PANSI_STRING AnsiEnv, OUT PUNICODE_STRING UnicodeEnv)
Definition: vdm.c:744
NTSTATUS WINAPI BaseCheckVDM(IN ULONG BinaryType, IN PCWCH ApplicationName, IN PCWCH CommandLine, IN PCWCH CurrentDirectory, IN PANSI_STRING AnsiEnvironment, IN PBASE_API_MESSAGE ApiMessage, IN OUT PULONG iTask, IN DWORD CreationFlags, IN LPSTARTUPINFOW StartupInfo, IN HANDLE hUserToken OPTIONAL)
Definition: vdm.c:91
_ACRTIMP size_t __cdecl wcslen(const wchar_t *)
Definition: wcs.c:2988
_ACRTIMP int __cdecl _wcsnicmp(const wchar_t *, const wchar_t *, size_t)
Definition: wcs.c:200
unsigned int BOOL
Definition: ntddk_ex.h:94
#define FILE_SYNCHRONOUS_IO_NONALERT
Definition: from_kernel.h:31
GLdouble n
Definition: glext.h:7729
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble const GLfloat const GLdouble const GLfloat GLint i
Definition: glfuncs.h:248
#define DbgPrint
Definition: hal.h:12
NTSTATUS NTAPI NtRaiseHardError(IN NTSTATUS ErrorStatus, IN ULONG NumberOfParameters, IN ULONG UnicodeStringParameterMask, IN PULONG_PTR Parameters, IN ULONG ValidResponseOptions, OUT PULONG Response)
Definition: harderr.c:551
#define PROCESS_CREATE_FLAGS_BREAKAWAY
Definition: pstypes.h:87
#define PROCESS_PRIORITY_CLASS_IDLE
Definition: pstypes.h:103
#define PROCESS_CREATE_FLAGS_INHERIT_HANDLES
Definition: pstypes.h:89
#define PROCESS_PRIORITY_CLASS_INVALID
Definition: pstypes.h:102
#define PROCESS_PRIORITY_CLASS_NORMAL
Definition: pstypes.h:104
#define PROCESS_PRIORITY_CLASS_HIGH
Definition: pstypes.h:105
#define PROCESS_PRIORITY_CLASS_ABOVE_NORMAL
Definition: pstypes.h:108
#define PROCESS_CREATE_FLAGS_LARGE_PAGES
Definition: pstypes.h:91
#define PROCESS_PRIORITY_CLASS_BELOW_NORMAL
Definition: pstypes.h:107
#define PROCESS_PRIORITY_CLASS_REALTIME
Definition: pstypes.h:106
#define PROCESS_CREATE_FLAGS_NO_DEBUG_INHERIT
Definition: pstypes.h:88
#define NtCurrentTeb
NTSTATUS NTAPI LdrQueryImageFileKeyOption(_In_ HANDLE KeyHandle, _In_ PCWSTR ValueName, _In_ ULONG Type, _Out_ PVOID Buffer, _In_ ULONG BufferSize, _Out_opt_ PULONG ReturnedLength)
Definition: ldrinit.c:188
NTSTATUS NTAPI LdrOpenImageFileOptionsKey(_In_ PUNICODE_STRING SubKey, _In_ BOOLEAN Wow64, _Out_ PHANDLE NewKeyHandle)
Definition: ldrinit.c:115
#define PCHAR
Definition: match.c:90
PVOID PVOID PWCHAR PVOID USHORT PULONG PVOID PULONG PVOID PULONG PULONG FusionFlags
Definition: env.c:49
#define SE_LOCK_MEMORY_PRIVILEGE
Definition: security.c:558
#define InitializeObjectAttributes(p, n, a, r, s)
Definition: reg.c:115
_In_ NDIS_ERROR_CODE ErrorCode
Definition: ndis.h:4436
@ OptionOk
Definition: extypes.h:192
@ ResponseOk
Definition: extypes.h:210
#define PROCESSOR_ARCHITECTURE_IA64
Definition: ketypes.h:111
#define PROCESSOR_ARCHITECTURE_UNKNOWN
Definition: ketypes.h:115
#define PROCESSOR_ARCHITECTURE_AMD64
Definition: ketypes.h:114
#define PROCESSOR_ARCHITECTURE_INTEL
Definition: ketypes.h:105
_In_ HANDLE _Outptr_result_bytebuffer_ ViewSize _Pre_valid_ PVOID * BaseAddress
Definition: mmfuncs.h:408
__kernel_entry _Inout_ _Inout_ PSIZE_T RegionSize
Definition: mmfuncs.h:176
#define SEC_IMAGE
Definition: mmtypes.h:97
@ SectionImageInformation
Definition: mmtypes.h:196
NTSYSAPI ULONG NTAPI RtlIsDosDeviceName_U(_In_ PCWSTR Name)
NTSYSAPI NTSTATUS NTAPI RtlAcquirePrivilege(_In_ PULONG Privilege, _In_ ULONG NumPriv, _In_ ULONG Flags, _Out_ PVOID *ReturnedState)
NTSTATUS NTAPI RtlGetFullPathName_UstrEx(_In_ PUNICODE_STRING FileName, _In_opt_ PUNICODE_STRING StaticString, _In_opt_ PUNICODE_STRING DynamicString, _Out_opt_ PUNICODE_STRING *StringUsed, _Out_opt_ PSIZE_T FilePartSize, _Out_opt_ PBOOLEAN NameInvalid, _Out_ RTL_PATH_TYPE *PathType, _Out_opt_ PSIZE_T LengthNeeded)
VOID NTAPI RtlReleaseRelativeName(_In_ PRTL_RELATIVE_NAME_U RelativeName)
NTSYSAPI VOID NTAPI RtlDestroyEnvironment(_In_ PWSTR Environment)
Definition: env.c:116
NTSYSAPI RTL_PATH_TYPE NTAPI RtlDetermineDosPathNameType_U(_In_ PCWSTR Path)
NTSYSAPI VOID NTAPI RtlReleasePrivilege(_In_ PVOID ReturnedState)
NTSYSAPI BOOLEAN NTAPI RtlDosPathNameToRelativeNtPathName_U(_In_ PCWSTR DosName, _Out_ PUNICODE_STRING NtName, _Out_ PCWSTR *PartName, _Out_ PRTL_RELATIVE_NAME_U RelativeName)
#define SEM_FAILCRITICALERRORS
Definition: rtltypes.h:69
@ RtlPathTypeRootLocalDevice
Definition: rtltypes.h:483
@ RtlPathTypeRelative
Definition: rtltypes.h:481
@ RtlPathTypeUncAbsolute
Definition: rtltypes.h:477
@ RtlPathTypeLocalDevice
Definition: rtltypes.h:482
@ RtlPathTypeDriveAbsolute
Definition: rtltypes.h:478
enum _RTL_PATH_TYPE RTL_PATH_TYPE
VOID WINAPI FreeString(_In_ LPWSTR pszString)
Definition: netsh.c:281
NTSYSAPI NTSTATUS NTAPI NtOpenFile(OUT PHANDLE phFile, IN ACCESS_MASK DesiredAccess, IN POBJECT_ATTRIBUTES ObjectAttributes, OUT PIO_STATUS_BLOCK pIoStatusBlock, IN ULONG ShareMode, IN ULONG OpenMode)
Definition: file.c:3951
#define FILE_SHARE_WRITE
Definition: nt_native.h:681
#define SYNCHRONIZE
Definition: nt_native.h:61
#define FILE_READ_DATA
Definition: nt_native.h:628
#define SECTION_ALL_ACCESS
Definition: nt_native.h:1296
#define FILE_READ_ATTRIBUTES
Definition: nt_native.h:647
#define PROCESS_ALL_ACCESS
Definition: nt_native.h:1327
NTSYSAPI NTSTATUS NTAPI RtlAnsiStringToUnicodeString(PUNICODE_STRING DestinationString, PANSI_STRING SourceString, BOOLEAN AllocateDestinationString)
#define PAGE_EXECUTE
Definition: nt_native.h:1309
NTSTATUS NTAPI NtTerminateProcess(HANDLE ProcessHandle, LONG ExitStatus)
#define FILE_SHARE_DELETE
Definition: nt_native.h:682
#define FILE_EXECUTE
Definition: nt_native.h:642
#define FILE_ATTRIBUTE_DIRECTORY
Definition: nt_native.h:705
NTSYSAPI VOID NTAPI RtlFreeUnicodeString(PUNICODE_STRING UnicodeString)
#define MEM_RESERVE
Definition: nt_native.h:1317
#define MEM_RELEASE
Definition: nt_native.h:1319
NTSYSAPI NTSTATUS NTAPI NtCreateThread(OUT PHANDLE phThread, IN ACCESS_MASK AccessMask, IN POBJECT_ATTRIBUTES ObjectAttributes, IN HANDLE hProcess, OUT PCLIENT_ID pClientId, IN PCONTEXT pContext, OUT PSTACKINFO pStackInfo, IN BOOLEAN bSuspended)
#define PAGE_EXECUTE_READWRITE
Definition: nt_native.h:1311
#define UNICODE_STRING_MAX_CHARS
#define UNICODE_STRING_MAX_BYTES
#define VER_SUITE_DATACENTER
#define VER_SUITE_PERSONAL
#define ANSI_NULL
#define IMAGE_SUBSYSTEM_POSIX_CUI
Definition: ntimage.h:440
#define IMAGE_SUBSYSTEM_WINDOWS_CUI
Definition: ntimage.h:438
#define IMAGE_SUBSYSTEM_WINDOWS_GUI
Definition: ntimage.h:437
#define IMAGE_DLLCHARACTERISTICS_NO_ISOLATION
Definition: ntimage.h:458
#define IMAGE_FILE_MACHINE_AMD64
Definition: ntimage.h:17
#define IMAGE_FILE_MACHINE_IA64
Definition: ntimage.h:22
NTSTATUS NTAPI NtFreeVirtualMemory(IN HANDLE ProcessHandle, IN PVOID *UBaseAddress, IN PSIZE_T URegionSize, IN ULONG FreeType)
Definition: virtual.c:5192
NTSTATUS NTAPI NtReadVirtualMemory(IN HANDLE ProcessHandle, IN PVOID BaseAddress, OUT PVOID Buffer, IN SIZE_T NumberOfBytesToRead, OUT PSIZE_T NumberOfBytesRead OPTIONAL)
Definition: virtual.c:2781
NTSTATUS NTAPI NtIsProcessInJob(_In_ HANDLE ProcessHandle, _In_opt_ HANDLE JobHandle)
Definition: job.c:2014
NTSTATUS NTAPI NtAssignProcessToJobObject(_In_ HANDLE JobHandle, _In_ HANDLE ProcessHandle)
Definition: job.c:1928
NTSTATUS NTAPI NtCreateProcessEx(OUT PHANDLE ProcessHandle, IN ACCESS_MASK DesiredAccess, IN POBJECT_ATTRIBUTES ObjectAttributes OPTIONAL, IN HANDLE ParentProcess, IN ULONG Flags, IN HANDLE SectionHandle OPTIONAL, IN HANDLE DebugPort OPTIONAL, IN HANDLE ExceptionPort OPTIONAL, IN BOOLEAN InJob)
Definition: process.c:1384
NTSTATUS NTAPI NtSetInformationProcess(_In_ HANDLE ProcessHandle, _In_ PROCESSINFOCLASS ProcessInformationClass, _In_reads_bytes_(ProcessInformationLength) PVOID ProcessInformation, _In_ ULONG ProcessInformationLength)
Definition: query.c:1422
NTSTATUS NTAPI NtResumeThread(IN HANDLE ThreadHandle, OUT PULONG SuspendCount OPTIONAL)
Definition: state.c:290
PVOID *typedef PHANDLE
Definition: ntsecpkg.h:455
#define STATUS_INVALID_IMAGE_WIN_64
Definition: ntstatus.h:1029
#define STATUS_INVALID_IMAGE_WIN_16
Definition: ntstatus.h:635
#define STATUS_INVALID_IMAGE_NE_FORMAT
Definition: ntstatus.h:613
#define STATUS_IMAGE_MACHINE_TYPE_MISMATCH_EXE
Definition: ntstatus.h:224
#define STATUS_INVALID_IMAGE_NOT_MZ
Definition: ntstatus.h:633
#define STATUS_INVALID_IMAGE_PROTECT
Definition: ntstatus.h:634
#define STATUS_VDM_DISALLOWED
Definition: ntstatus.h:1089
#define STATUS_FILE_IS_OFFLINE
Definition: ntstatus.h:862
#define STATUS_NAME_TOO_LONG
Definition: ntstatus.h:592
#define IMAGE_FILE_MACHINE_I386
Definition: pedump.c:174
#define IMAGE_FILE_DLL
Definition: pedump.c:169
#define REG_DWORD
Definition: sdbapi.c:615
VOID NTAPI CsrFreeCaptureBuffer(_In_ _Frees_ptr_ PCSR_CAPTURE_BUFFER CaptureBuffer)
Definition: capture.c:210
NTSTATUS NTAPI CsrClientCallServer(_Inout_ PCSR_API_MESSAGE ApiMessage, _Inout_opt_ PCSR_CAPTURE_BUFFER CaptureBuffer, _In_ CSR_API_NUMBER ApiNumber, _In_ ULONG DataLength)
Definition: connect.c:368
#define BINARY_TYPE_WOW
Definition: vdm.h:40
#define VDM_UNDO_PARTIAL
Definition: vdm.h:27
#define VDM_UNDO_COMPLETED
Definition: vdm.h:30
#define BINARY_TYPE_WOW_EX
Definition: vdm.h:41
#define VDM_NOT_READY
Definition: vdm.h:47
#define BINARY_TYPE_SEPARATE_WOW
Definition: vdm.h:39
#define VDM_UNDO_REUSE
Definition: vdm.h:29
@ VdmEntryUndo
Definition: vdm.h:19
@ VdmEntryUpdateProcess
Definition: vdm.h:20
#define VDM_UNDO_FULL
Definition: vdm.h:28
#define BINARY_TYPE_DOS
Definition: vdm.h:38
#define VDM_READY
Definition: vdm.h:48
#define VDM_NOT_LOADED
Definition: vdm.h:46
#define BINARY_TYPE_EXE
Definition: vdm.h:35
wcscat
wcscpy
NTSTATUS NTAPI NtQuerySection(_In_ HANDLE SectionHandle, _In_ SECTION_INFORMATION_CLASS SectionInformationClass, _Out_ PVOID SectionInformation, _In_ SIZE_T SectionInformationLength, _Out_opt_ PSIZE_T ResultLength)
Definition: section.c:3812
USHORT MaximumLength
Definition: env_spec_w32.h:377
BASE_CREATE_PROCESS CreateProcessRequest
Definition: basemsg.h:283
BASE_CHECK_VDM CheckVDMRequest
Definition: basemsg.h:287
union _BASE_API_MESSAGE::@4362 Data
USHORT VDMState
Definition: basemsg.h:147
HANDLE WaitObjectForParent
Definition: basemsg.h:123
BASE_SXS_CREATEPROCESS_MSG Sxs
Definition: basemsg.h:96
USHORT ProcessorArchitecture
Definition: basemsg.h:99
ULONG PebAddressWow64
Definition: basemsg.h:98
HANDLE ProcessHandle
Definition: basemsg.h:89
CLIENT_ID ClientId
Definition: basemsg.h:91
HANDLE ThreadHandle
Definition: basemsg.h:90
PVOID PebAddressNative
Definition: basemsg.h:97
BOOLEAN IsWowTaskReady
Definition: base.h:135
BOOLEAN DefaultSeparateVDM
Definition: base.h:134
HANDLE UniqueThread
Definition: compat.h:826
HANDLE UniqueProcess
Definition: compat.h:825
IMAGE_OPTIONAL_HEADER32 OptionalHeader
Definition: ntddk_ex.h:184
PVOID StackBase
Definition: pstypes.h:757
PVOID ArbitraryUserPointer
Definition: compat.h:719
BOOLEAN ReadImageFileExecOptions
Definition: ntddk_ex.h:240
ULONG ImageSubsystemMajorVersion
Definition: ntddk_ex.h:305
SIZE_T StaticSize
Definition: rtltypes.h:1923
PUCHAR StaticBuffer
Definition: rtltypes.h:1921
PUCHAR Buffer
Definition: rtltypes.h:1920
SIZE_T Size
Definition: rtltypes.h:1922
UNICODE_STRING RelativeName
Definition: rtltypes.h:1402
HANDLE ContainingDirectory
Definition: rtltypes.h:1403
UNICODE_STRING String
Definition: rtltypes.h:1930
UNICODE_STRING DesktopInfo
Definition: rtltypes.h:1602
LPVOID lpSecurityDescriptor
Definition: compat.h:193
PUNICODE_STRING Win32
Definition: kernel32.h:402
PUNICODE_STRING Nt
Definition: kernel32.h:403
Definition: compat.h:836
NT_TIB NtTib
Definition: ntddk_ex.h:332
#define max(a, b)
Definition: svc.c:63
#define RtlZeroMemory(Destination, Length)
Definition: typedefs.h:262
#define MAXUSHORT
Definition: typedefs.h:83
char * PCHAR
Definition: typedefs.h:51
#define STATUS_ACCESS_DENIED
Definition: udferr_usr.h:145
#define INVALID_FILE_ATTRIBUTES
Definition: vfdcmd.c:23
#define NORMAL_PRIORITY_CLASS
Definition: winbase.h:186
#define STARTF_FORCEOFFFEEDBACK
Definition: winbase.h:475
#define CREATE_BREAKAWAY_FROM_JOB
Definition: winbase.h:214
DWORD WINAPI GetLastError(void)
Definition: except.c:1042
#define CREATE_FORCEDOS
Definition: winbase.h:194
#define REALTIME_PRIORITY_CLASS
Definition: winbase.h:189
#define BELOW_NORMAL_PRIORITY_CLASS
Definition: winbase.h:195
#define CREATE_UNICODE_ENVIRONMENT
Definition: winbase.h:191
#define HIGH_PRIORITY_CLASS
Definition: winbase.h:188
#define CREATE_SHARED_WOW_VDM
Definition: winbase.h:193
#define GetModuleHandle
Definition: winbase.h:3550
#define CREATE_DEFAULT_ERROR_MODE
Definition: winbase.h:216
#define CREATE_SEPARATE_WOW_VDM
Definition: winbase.h:192
#define CREATE_SUSPENDED
Definition: winbase.h:183
#define DEBUG_ONLY_THIS_PROCESS
Definition: winbase.h:182
#define SearchPath
Definition: winbase.h:3623
#define CREATE_PRESERVE_CODE_AUTHZ_LEVEL
Definition: winbase.h:215
#define IDLE_PRIORITY_CLASS
Definition: winbase.h:187
#define STARTF_FORCEONFEEDBACK
Definition: winbase.h:474
#define DEBUG_PROCESS
Definition: winbase.h:181
#define ABOVE_NORMAL_PRIORITY_CLASS
Definition: winbase.h:196
NTSYSAPI NTSTATUS WINAPI DbgUiConnectToDbg(void)
Definition: dbgui.c:25
NTSYSAPI HANDLE WINAPI DbgUiGetThreadDebugObject(void)
Definition: dbgui.c:333
@ ProcessPriorityClass
Definition: winternl.h:1900
@ ProcessDefaultHardErrorMode
Definition: winternl.h:1894
#define ERROR_PATH_NOT_FOUND
Definition: winerror.h:228
#define ERROR_DIRECTORY
Definition: winerror.h:416
#define ERROR_NOT_READY
Definition: winerror.h:246
#define ERROR_BAD_EXE_FORMAT
Definition: winerror.h:373
#define ERROR_CHILD_NOT_COMPLETE
Definition: winerror.h:323
#define ERROR_ACCESS_DISABLED_BY_POLICY
Definition: winerror.h:1092
#define ERROR_CANCELLED
Definition: winerror.h:1055
#define ERROR_EXE_MACHINE_TYPE_MISMATCH
Definition: winerror.h:393
#define ERROR_ACCESS_DISABLED_WEBBLADE_TAMPER
Definition: winerror.h:1105
#define ERROR_ACCESS_DISABLED_WEBBLADE
Definition: winerror.h:1104
#define ERROR_FILE_OFFLINE
Definition: winerror.h:1714
#define ERROR_BAD_DEVICE
Definition: winerror.h:1032
_Out_ PCLIENT_ID ClientId
Definition: kefuncs.h:1151

Referenced by CreateProcessW().

◆ CreateProcessW()

BOOL WINAPI DECLSPEC_HOTPATCH CreateProcessW ( LPCWSTR  lpApplicationName,
LPWSTR  lpCommandLine,
LPSECURITY_ATTRIBUTES  lpProcessAttributes,
LPSECURITY_ATTRIBUTES  lpThreadAttributes,
BOOL  bInheritHandles,
DWORD  dwCreationFlags,
LPVOID  lpEnvironment,
LPCWSTR  lpCurrentDirectory,
LPSTARTUPINFOW  lpStartupInfo,
LPPROCESS_INFORMATION  lpProcessInformation 
)

Definition at line 4493 of file proc.c.

4503{
4504 /* Call the internal (but exported) version */
4506 lpApplicationName,
4507 lpCommandLine,
4508 lpProcessAttributes,
4509 lpThreadAttributes,
4510 bInheritHandles,
4511 dwCreationFlags,
4512 lpEnvironment,
4513 lpCurrentDirectory,
4514 lpStartupInfo,
4515 lpProcessInformation,
4516 NULL);
4517}
BOOL WINAPI CreateProcessInternalW(IN HANDLE hUserToken, IN LPCWSTR lpApplicationName, IN LPWSTR lpCommandLine, IN LPSECURITY_ATTRIBUTES lpProcessAttributes, IN LPSECURITY_ATTRIBUTES lpThreadAttributes, IN BOOL bInheritHandles, IN DWORD dwCreationFlags, IN LPVOID lpEnvironment, IN LPCWSTR lpCurrentDirectory, IN LPSTARTUPINFOW lpStartupInfo, IN LPPROCESS_INFORMATION lpProcessInformation, OUT PHANDLE hNewToken)
Definition: proc.c:2135

Referenced by alloc_console(), AudioDlgProc(), compile_cs(), ConsoleIMERoutine(), CorDebug_CreateProcess(), CProcess::CProcess(), create_pseudo_console(), create_server(), create_surrogate_server(), CreateClientProcess(), CreateProcessAsUserW(), CreateProcessWithTokenW(), do_register_dll(), execute_command(), HotkeyThread(), IDirectInputAImpl_RunControlPanel(), install_wine_gecko(), InstallDevice(), InstallLiveCD(), invoke_appwiz(), ITERATE_RemoveExistingProducts(), CNetConnectionPropertyUi::LANPropertiesUIDlg(), launch_exe(), CNewMenu::NewItemByCommand(), ProcessPage_OnDebug(), PromptAndRunProcessAs(), register_dll(), run_child(), run_rapps(), run_winemenubuilder(), runCmd(), RunCommandAndWait(), RunControlPanelApplet(), RunCurrentJobs(), runscriptfile(), RunSetupThreadProc(), ScmStartUserModeService(), SHELL_ExecuteW(), start_debugger(), START_TEST(), StartChild(), StartLsass(), StartProcess(), StartServicesManager(), TaskManager_OnFileNew(), Test_CommandLine(), test_debug_loop_wow64(), test_loadpaths_execute(), TestStaticDestruct(), UnhandledExceptionFilter(), WshExec_create(), and wWinMain().

◆ ExitProcess()

VOID WINAPI ExitProcess ( IN UINT  uExitCode)

Definition at line 1382 of file proc.c.

1383{
1384 BASE_API_MESSAGE ApiMessage;
1385 PBASE_EXIT_PROCESS ExitProcessRequest = &ApiMessage.Data.ExitProcessRequest;
1386
1388
1389 _SEH2_TRY
1390 {
1391 /* Acquire the PEB lock */
1393
1394 /* Kill all the threads */
1395 NtTerminateProcess(NULL, uExitCode);
1396
1397 /* Unload all DLLs */
1399
1400 /* Notify Base Server of process termination */
1401 ExitProcessRequest->uExitCode = uExitCode;
1403 NULL,
1405 sizeof(*ExitProcessRequest));
1406
1407 /* Now do it again */
1409 }
1411 {
1412 /* Release the PEB lock */
1414 }
1415 _SEH2_END;
1416
1417 /* should never get here */
1418 ASSERT(0);
1419 while(1);
1420}
@ BasepExitProcess
Definition: basemsg.h:24
#define _SEH2_FINALLY
Definition: pseh2_64.h:153
BASE_EXIT_PROCESS ExitProcessRequest
Definition: basemsg.h:286
NTSYSAPI void WINAPI LdrShutdownProcess(void)
Definition: ldrinit.c:954

Referenced by _CorExeMain(), _exit(), _font_assert(), _RunRemoteTest(), alarmThreadMain(), BaseProcessStartup(), BaseThreadStartup(), child_process(), CLRMetaHost_ExitProcess(), ConsoleControlDispatcher(), CtrlCIntercept(), DbgkExitProcess(), DECLARE_INTERFACE_(), DefaultConsoleCtrlHandler(), DevInstallW(), DisplayError(), dll_entry_point(), doChild(), doDebugger(), ErrorExit(), exit(), exit_or_terminate_process(), ExitThread(), FatalAppExitA(), FatalAppExitW(), FatalExit(), fls_exit_deadlock_child(), Host_Quit(), IEWinMain(), init(), LoadProc(), local_server_proc(), LogToFile(), main(), performUninstall(), restart_as_admin_elevated(), RpcRaiseException(), setupDelayHook(), ShellExec_RunDLL_Helper(), ShowUsage(), START_TEST(), StringListAppend(), test__popen_child(), test__popen_read_child(), thread_1(), timeout_thread_proc(), VdmShutdown(), wait_debugger(), WatchDirectory(), WinMain(), wmainCRTStartup(), and wWinMain().

◆ FatalAppExitA()

VOID WINAPI FatalAppExitA ( UINT  uAction,
LPCSTR  lpMessageText 
)

Definition at line 1457 of file proc.c.

1459{
1460 PUNICODE_STRING MessageTextU;
1461 ANSI_STRING MessageText;
1463
1464 /* Initialize the string using the static TEB pointer */
1465 MessageTextU = &NtCurrentTeb()->StaticUnicodeString;
1466 RtlInitAnsiString(&MessageText, (LPSTR)lpMessageText);
1467
1468 /* Convert to unicode, or just exit normally if this failed */
1469 Status = RtlAnsiStringToUnicodeString(MessageTextU, &MessageText, FALSE);
1470 if (!NT_SUCCESS(Status)) ExitProcess(0);
1471
1472 /* Call the Wide function */
1473 FatalAppExitW(uAction, MessageTextU->Buffer);
1474}
VOID WINAPI FatalAppExitW(IN UINT uAction, IN LPCWSTR lpMessageText)
Definition: proc.c:1481
NTSYSAPI VOID NTAPI RtlInitAnsiString(PANSI_STRING DestinationString, PCSZ SourceString)
char * LPSTR
Definition: typedefs.h:51

◆ FatalAppExitW()

VOID WINAPI FatalAppExitW ( IN UINT  uAction,
IN LPCWSTR  lpMessageText 
)

Definition at line 1481 of file proc.c.

1483{
1487
1488 /* Setup the string to print out */
1489 RtlInitUnicodeString(&UnicodeString, lpMessageText);
1490
1491 /* Display the hard error no matter what */
1493 1,
1494 1,
1496#if DBG
1497 /* On Checked builds, Windows allows the user to cancel the operation */
1499#else
1500 OptionOk,
1501#endif
1502 &Response);
1503
1504 /* Give the user a chance to abort */
1506 {
1507 return;
1508 }
1509
1510 /* Otherwise kill the process */
1511 ExitProcess(0);
1512}
#define DBG(x)
Definition: moztest.c:12
#define HARDERROR_OVERRIDE_ERRORMODE
Definition: extypes.h:151
@ OptionOkCancel
Definition: extypes.h:193
@ ResponseCancel
Definition: extypes.h:207
#define STATUS_FATAL_APP_EXIT
Definition: ntstatus.h:210
Definition: ncftp.h:89
uint32_t * PULONG_PTR
Definition: typedefs.h:65
WDF_EXTERN_C_START typedef _Must_inspect_result_ _In_opt_ PCUNICODE_STRING UnicodeString
Definition: wdfstring.h:64

Referenced by FatalAppExitA().

◆ FatalExit()

VOID WINAPI FatalExit ( IN int  ExitCode)

Definition at line 1519 of file proc.c.

1520{
1521#if DBG
1522 /* On Checked builds, Windows gives the user a nice little debugger UI */
1523 CHAR Action[2];
1524 DbgPrint("FatalExit...\n\n");
1525
1526 /* Check for reactos specific flag (set by rosautotest) */
1528 {
1530 }
1531
1532 while (TRUE)
1533 {
1534 DbgPrompt("A (Abort), B (Break), I (Ignore)? ", Action, sizeof(Action));
1535 switch (Action[0])
1536 {
1537 case 'B': case 'b':
1538 DbgBreakPoint();
1539 break;
1540
1541 case 'A': case 'a':
1542 ExitProcess(ExitCode);
1543
1544 case 'I': case 'i':
1545 return;
1546 }
1547 }
1548#endif
1549 /* On other builds, just kill the process */
1550 ExitProcess(ExitCode);
1551}
#define FLG_DISABLE_DEBUG_PROMPTS
Definition: pstypes.h:81
DECLSPEC_NORETURN NTSYSAPI VOID NTAPI RtlRaiseStatus(_In_ NTSTATUS Status)
NTSYSAPI ULONG NTAPI DbgPrompt(_In_z_ PCCH Prompt, _Out_writes_bytes_(MaximumResponseLength) PCH Response, _In_ ULONG MaximumResponseLength)
_In_ WDFIOTARGET _In_ _Strict_type_match_ WDF_IO_TARGET_SENT_IO_ACTION Action
Definition: wdfiotarget.h:510
NTSYSAPI void WINAPI DbgBreakPoint(void)
NTSYSAPI ULONG WINAPI RtlGetNtGlobalFlags(void)
Definition: libsupp.c:106

◆ FlushInstructionCache()

BOOL WINAPI FlushInstructionCache ( IN HANDLE  hProcess,
IN LPCVOID  lpBaseAddress,
IN SIZE_T  nSize 
)

Definition at line 1358 of file proc.c.

1361{
1363
1364 /* Call the native function */
1366 if (!NT_SUCCESS(Status))
1367 {
1368 /* Handle failure case */
1370 return FALSE;
1371 }
1372
1373 /* All good */
1374 return TRUE;
1375}
_In_ BOOL _In_ HANDLE hProcess
Definition: mapping.h:71
NTSTATUS NTAPI NtFlushInstructionCache(_In_ HANDLE ProcessHandle, _In_opt_ PVOID BaseAddress, _In_ SIZE_T FlushSize)
Definition: virtual.c:3009
*nSize LPSTR _Inout_ LPDWORD nSize
Definition: winbase.h:1809

Referenced by test_cross_process_notifications().

◆ GetActiveProcessorCount()

DWORD WINAPI GetActiveProcessorCount ( IN WORD  GroupNumber)

Definition at line 947 of file proc.c.

948{
949 STUB; // FIXME: Real group support
950 return GetProcessorCountInfo(GroupNumber, FALSE);
951}
static DWORD GetProcessorCountInfo(IN WORD GroupNumber, IN BOOL Maximum)
Definition: proc.c:928
#define STUB
Definition: kernel32.h:27

◆ GetActiveProcessorGroupCount()

WORD WINAPI GetActiveProcessorGroupCount ( VOID  )

Definition at line 921 of file proc.c.

922{
923 STUB; // FIXME: Real group support
924 return 1; // TODO: SharedUserData->ActiveGroupCount?
925}

◆ GetCommandLineA()

LPSTR WINAPI GetCommandLineA ( VOID  )

Definition at line 1904 of file proc.c.

1905{
1907}
ANSI_STRING BaseAnsiCommandLine
Definition: proc.c:23

◆ GetCommandLineW()

LPWSTR WINAPI GetCommandLineW ( VOID  )

Definition at line 1914 of file proc.c.

1915{
1917}
UNICODE_STRING BaseUnicodeCommandLine
Definition: proc.c:22

◆ GetCurrentProcess()

HANDLE WINAPI GetCurrentProcess ( VOID  )

Definition at line 1187 of file proc.c.

1188{
1189 return (HANDLE)NtCurrentProcess();
1190}

◆ GetCurrentProcessId()

DWORD WINAPI GetCurrentProcessId ( VOID  )

Definition at line 1207 of file proc.c.

1208{
1210}

Referenced by __security_init_cookie(), _getpid(), _mktemp(), _mktemp_s(), _Success_(), _wmktemp(), _wmktemp_s(), AddPortW(), adns_getpid(), apartment_construct(), child_process(), ClientLoadLibrary(), CloseProcess(), CMP_RegisterNotification(), CommitSpoolData(), ConfigurePortW(), create_test_element_from_hwnd(), CreateNotificationParamAndSend(), CreatePipe(), CreateProcessWithLogonW(), CreateToolhelp32Snapshot(), CURSORICON_CopyImage(), custom_start_server(), default_ctrl_handler(), DirectDrawClipper_Initialize(), dll_entry_point(), DllMain(), do_msidbCustomActionTypeDll(), doChild(), DPLAYX_CreateLobbyApplication(), DPLAYX_IsAppIdLobbied(), DumpNotificationState(), enum_modules64(), EnumWindowsProc(), ExtractAndInstallThread(), ExtractArchiveForExecution(), FreeChangeNotifications(), generate_ipid(), get_cmdline(), get_node_provider_description_string(), get_proc_address64(), GetProcessVersion(), GetSpoolFileHandle(), handle_msi_break(), IDirectPlayLobby3AImpl_SetConnectionSettings(), IDirectPlayLobby3Impl_SetConnectionSettings(), ImmGetImeMenuItemsAW(), Internal_CreatePalette(), Internal_CreateSurface(), ipid_to_ifstub(), IsBlockFromHeap(), LresultFromObject(), main(), mark_task_process(), new_stub_manager(), NotifyLogon(), ole_server(), openlog(), OutputDebugStringA(), ParseSharedPacket(), ProcessIdToSessionId(), RegisterDragDrop(), rpc_execute_call(), rpcrt4_protseq_ncacn_np_open_endpoint(), rpcrt4_protseq_ncalrpc_open_endpoint(), run_in_temp_desktop_thread_func(), ScConnectControlPipe(), CNotifyToolbar::SendNotifyCallback(), ServerThread(), service_main(), SHAllocShared(), SHAppBarMessage(), SHFreeShared(), SHGetAppCompatFlags(), SHHandleUpdateImage(), SHLockShared(), SHMapHandle(), SHUpdateImageW(), start_debugger(), START_TEST(), StartDirectDraw(), TelnetGetConsoleWindow(), test_AddSelfToJob(), test_alloc_shared(), test_alloc_shared_remote(), test_AttachConsole(), test_AttachConsole_child(), test_BreakawayOk(), Test_CloseDuplicatedSocket(), Test_CloseWhileSelectDuplicatedSocket(), test_CoGetCurrentProcess(), test_D3DKMTQueryVideoMemoryInfo(), test_debug_loop(), test_default_clientside_providers(), test_duplicate_handle_access(), test_Element_Find(), test_exception_dispatcher(), test_exit_process_async(), test_GetConsoleProcessList(), test_GetExtendedTcpTable_owner(), test_GetExtendedUdpTable_owner(), test_GetFocusedElement(), test_GetProcessVersion(), test_GetRootElement(), test_handles(), test_hook_cleanup_thread_proc(), Test_InfoClass_Access(), test_init_block(), test_IUIAutomationEventHandler(), test_IUIAutomationFocusChangedEventHandler(), test_jobInheritance(), test_nested_jobs_child(), test_nt_wow64(), test_OpenProcess(), test_parent_process_attribute(), test_peb_teb(), test_process(), test_process_id(), test_process_security_child(), Test_ProcessModules(), test_query_handle(), test_query_handle_ex(), test_query_process(), test_query_process_vm(), test_QueryFullProcessImageNameW(), test_QueryInformationJobObject(), test_readvirtualmemory(), test_RtlQueryProcessDebugInformation(), test_session_info(), test_set_hook(), test_shared_handle_table(), test_SHCreateSessionKey(), test_syscalls(), test_tcp(), test_thread_lookup(), test_Toolhelp(), test_udp(), test_uia_com_focus_change_event_handler_win_event_handling(), test_UiaAddEvent(), test_UiaAddEvent_client_proc(), test_UiaFind(), test_UiaGetRootNode(), test_UiaGetRuntimeId(), test_UiaGetUpdatedCache(), test_UiaNavigate(), test_UiaNodeFromFocus(), test_UiaNodeFromHandle(), test_UiaNodeFromHandle_client_proc(), test_UiaNodeFromProvider(), test_UiaRegisterProviderCallback(), test_WaitForJobObject(), test_Win32_Process(), test_winevents(), test_WithWSAStartup(), test_ws_functions(), test_zero_access(), TestChannelHook_ClientFillBuffer(), TestChannelHook_ClientGetSize(), TestChannelHook_ClientNotify(), TestChannelHook_ServerGetSize(), TestChannelHook_ServerNotify(), ThemeDestroyWndData(), tmpnam_helper(), top_window_cb(), uia_com_event_handler_test_thread(), uia_nested_node_provider_attach_event(), uia_node_from_handle_test_thread(), uia_proxy_provider_win_event_handler_test_thread(), WDML_AddServer(), WinMain(), wmain(), wtmpnam_helper(), and wWinMain().

◆ GetCurrentThread()

HANDLE WINAPI GetCurrentThread ( VOID  )

Definition at line 1197 of file proc.c.

1198{
1199 return (HANDLE)NtCurrentThread();
1200}

Referenced by __threadhandle(), AccpLookupCurrentUser(), AdjustAffinity(), AuthzpInitUnderImpersonation(), CheckTokenMembership(), collect_connections_proc(), ConsoleControlDispatcher(), DirectoryWatcherThreadFuncAPC(), dll_entry_point(), DPWS_ThreadProc(), DwInitializeSdFromThreadToken(), exec_write_handler(), CShellCommandSACL::Execute(), GetProfileType(), GetSystemUserInfo(), GetUserNameW(), ImageView_Main(), io_thread(), IsCallerInteractive(), main(), message_thread_proc(), message_thread_run(), notification_thread_func(), OpenEffectiveToken(), PlaySound_ExpandEnvironmentStrings(), priorityTimeProc(), Privilege(), process_work_items(), RegOpenCurrentUser(), RevertToPrinterSelf(), rpcrt4_http_timer_thread(), RPCRT4_io_thread(), RPCRT4_server_thread(), CFindFolder::SearchThreadProc(), serverThreadMain2(), set_thread_name(), SetThreadToken(), SlideWindow(), SockAsyncThread(), start_address_thread(), start_fiber(), START_TEST(), SystemClockAdviseThread(), test_affinity(), test_alertable(), test_CancelSynchronousIo(), test_cancelsynchronousio(), test_CoWaitForMultipleHandles(), test_CreateDirectoryA(), test_CreatePipe(), test_exec_memory_writes(), test_FileSecurity(), test_GetFileType(), test_GetNamedSecurityInfoA(), test_GetOverlappedResultEx(), test_GetSecurityInfo(), test_GetWindowsAccountDomainSid(), test_HideFromDebugger(), test_ImpersonateNamedPipeClient(), test_impersonation_level(), test_MsgWaitForMultipleObjects(), test_nonalertable(), test_NtGetCurrentProcessorNumber(), test_object_identity(), test_object_permanence(), test_post_completion(), test_pseudo_handle_security(), test_pseudo_tokens(), test_query_architectures(), test_query_object(), test_QueueUserAPC(), test_read_write(), test_selectors(), test_set_io_completion(), Test_SyscallPerformance(), test_thread_description(), test_thread_ideal_processor(), test_thread_info(), test_thread_priority(), test_thread_processor(), test_thread_start_address(), Test_ThreadBasicInformationClass(), test_ThreadEnableAlignmentFaultFixup(), Test_ThreadPriorityClass(), test_token(), test_user_apc(), test_WaitForMultipleObjects(), test_WaitForSingleObject(), TestTokenPrivilege(), ThreadFunc2(), threadFunc3(), TlsFree(), vkd3d_set_thread_name(), WahOpenCurrentThread(), WaveThread(), wined3d_cs_run(), wmain(), and wWinMain().

◆ GetExitCodeProcess()

BOOL WINAPI GetExitCodeProcess ( IN HANDLE  hProcess,
IN LPDWORD  lpExitCode 
)

Definition at line 1217 of file proc.c.

1219{
1220 PROCESS_BASIC_INFORMATION ProcessBasic;
1222
1223 /* Ask the kernel */
1226 &ProcessBasic,
1227 sizeof(ProcessBasic),
1228 NULL);
1229 if (!NT_SUCCESS(Status))
1230 {
1231 /* We failed, was this because this is a VDM process? */
1232 if (BaseCheckForVDM(hProcess, lpExitCode) != FALSE) return TRUE;
1233
1234 /* Not a VDM process, fail the call */
1236 return FALSE;
1237 }
1238
1239 /* Succes case, return the exit code */
1240 *lpExitCode = (DWORD)ProcessBasic.ExitStatus;
1241 return TRUE;
1242}
@ ProcessBasicInformation
Definition: cicbase.cpp:63
BOOL WINAPI BaseCheckForVDM(IN HANDLE ProcessHandle, OUT LPDWORD ExitCode)
Definition: vdm.c:618
#define DWORD
Definition: nt_native.h:44
NTSTATUS NTAPI NtQueryInformationProcess(_In_ HANDLE ProcessHandle, _In_ PROCESSINFOCLASS ProcessInformationClass, _Out_writes_bytes_to_opt_(ProcessInformationLength, *ReturnLength) PVOID ProcessInformation, _In_ ULONG ProcessInformationLength, _Out_opt_ PULONG ReturnLength)
Definition: query.c:211

Referenced by _cwait(), check_child_console_bits(), CloseProcessAndVerify_(), cmd_start(), CommandThreadProc(), crash_and_debug(), crash_and_winedbg(), custom_get_process_return(), DoTestEntry(), Execute(), execute_command(), ExecutePipeline(), LauncherRoutine2(), MonitorChildThread(), ProcessRunning(), read_reg_output_(), restart_as_admin_elevated(), run_child_wait(), run_ex(), run_rapps(), run_reg_exe_(), run_script_file(), runcmd(), runCmd(), RunCommandAndWait(), runscriptfile(), RunSetupThreadProc(), runtime_is_usable(), shell_execute_ex_(), TerminateShell(), test_arm64ec(), test_CreateProcessWithDesktop(), test_CtrlHandlerSubsystem(), test_ddeml_server(), test_debug_loop_wow64(), test_DoInvalidDir(), test_end_to_end_server(), test_exit(), test_ExitProcess(), test_kill_on_exit(), test_loadpaths_execute(), test_msg_server(), test_pe_os_version(), test_quick_exit(), test_UiaAddEvent(), test_UiaNodeFromHandle(), WshExec_get_Status(), and WshShell3_Run().

◆ GetMaximumProcessorCount()

DWORD WINAPI GetMaximumProcessorCount ( IN WORD  GroupNumber)

Definition at line 958 of file proc.c.

959{
960 STUB; // FIXME: Real group support
961 return GetProcessorCountInfo(GroupNumber, TRUE);
962}

◆ GetPriorityClass()

DWORD WINAPI GetPriorityClass ( IN HANDLE  hProcess)

Definition at line 1558 of file proc.c.

1559{
1561 PROCESS_PRIORITY_CLASS DECLSPEC_ALIGN(4) PriorityClass;
1562
1563 /* Query the kernel */
1566 &PriorityClass,
1567 sizeof(PriorityClass),
1568 NULL);
1570 {
1571 /* Handle the conversion from NT to Win32 classes */
1572 switch (PriorityClass.PriorityClass)
1573 {
1580 }
1581 }
1582
1583 /* Failure path */
1585 return 0;
1586}
#define DECLSPEC_ALIGN(x)
Definition: corecrt.h:141
ActualNumberDriverObjects * sizeof(PDRIVER_OBJECT)) PDRIVER_OBJECT *DriverObjectList

Referenced by ProcessPageShowContextMenu(), and test_query_process_priority().

◆ GetProcessAffinityMask()

BOOL WINAPI GetProcessAffinityMask ( IN HANDLE  hProcess,
OUT PDWORD_PTR  lpProcessAffinityMask,
OUT PDWORD_PTR  lpSystemAffinityMask 
)

Definition at line 862 of file proc.c.

865{
866 PROCESS_BASIC_INFORMATION ProcessInfo;
868
869 /* Query information on the process from the kernel */
872 &ProcessInfo,
873 sizeof(ProcessInfo),
874 NULL);
875 if (!NT_SUCCESS(Status))
876 {
877 /* Fail */
879 return FALSE;
880 }
881
882 /* Copy the affinity mask, and get the system one from our shared data */
883 *lpProcessAffinityMask = (DWORD)ProcessInfo.AffinityMask;
885 return TRUE;
886}
unsigned long DWORD
Definition: ntddk_ex.h:95
SYSTEM_BASIC_INFORMATION SysInfo
Definition: base.h:130
KAFFINITY ActiveProcessorsAffinityMask
Definition: ntddk_ex.h:167

Referenced by AffinityDialogWndProc(), START_TEST(), and test_thread_processor().

◆ GetProcessHandleCount()

BOOL WINAPI GetProcessHandleCount ( IN HANDLE  hProcess,
OUT PDWORD  pdwHandleCount 
)

Definition at line 1846 of file proc.c.

1848{
1849 ULONG phc;
1851
1852 /* Query the kernel */
1855 &phc,
1856 sizeof(phc),
1857 NULL);
1858 if (NT_SUCCESS(Status))
1859 {
1860 /* Copy the count and return success */
1861 *pdwHandleCount = phc;
1862 return TRUE;
1863 }
1864
1865 /* Handle error path */
1867 return FALSE;
1868}
@ ProcessHandleCount
Definition: winternl.h:1902

◆ GetProcessId()

DWORD WINAPI GetProcessId ( IN HANDLE  Process)

Definition at line 1249 of file proc.c.

1250{
1251 PROCESS_BASIC_INFORMATION ProcessBasic;
1253
1254 /* Query the kernel */
1257 &ProcessBasic,
1258 sizeof(ProcessBasic),
1259 NULL);
1260 if (!NT_SUCCESS(Status))
1261 {
1262 /* Handle failure */
1264 return 0;
1265 }
1266
1267 /* Return the PID */
1268 return (DWORD)ProcessBasic.UniqueProcessId;
1269}
_Must_inspect_result_ _In_ PLARGE_INTEGER _In_ PLARGE_INTEGER _In_ ULONG _In_ PFILE_OBJECT _In_ PVOID Process
Definition: fsrtlfuncs.h:223

◆ GetProcessIoCounters()

BOOL WINAPI GetProcessIoCounters ( IN HANDLE  hProcess,
OUT PIO_COUNTERS  lpIoCounters 
)

Definition at line 1762 of file proc.c.

1764{
1766
1767 /* Query the kernel. Structures are identical, so let it do the copy too. */
1770 lpIoCounters,
1771 sizeof(IO_COUNTERS),
1772 NULL);
1773 if (!NT_SUCCESS(Status))
1774 {
1775 /* Handle error path */
1777 return FALSE;
1778 }
1779
1780 /* All done */
1781 return TRUE;
1782}
@ ProcessIoCounters
Definition: winternl.h:1884

Referenced by PerfDataRefresh().

◆ GetProcessorCountInfo()

static DWORD GetProcessorCountInfo ( IN WORD  GroupNumber,
IN BOOL  Maximum 
)
static

Definition at line 928 of file proc.c.

929{
931
932 // TODO: SharedUserData->ActiveProcessorCount for ALL_PROCESSOR_GROUPS?
933 if (GroupNumber != ALL_PROCESSOR_GROUPS && GroupNumber != THEONLYGROUP)
934 {
936 return 0;
937 }
939 return info.dwNumberOfProcessors;
940}
#define THEONLYGROUP
Definition: proc.c:914
VOID WINAPI GetNativeSystemInfo(IN LPSYSTEM_INFO lpSystemInfo)
Definition: sysinfo.c:207
#define ALL_PROCESSOR_GROUPS
Definition: ntbasedef.h:656

Referenced by GetActiveProcessorCount(), and GetMaximumProcessorCount().

◆ GetProcessPriorityBoost()

BOOL WINAPI GetProcessPriorityBoost ( IN HANDLE  hProcess,
OUT PBOOL  pDisablePriorityBoost 
)

Definition at line 1789 of file proc.c.

1791{
1794
1795 /* Query the kernel */
1799 sizeof(PriorityBoost),
1800 NULL);
1801 if (NT_SUCCESS(Status))
1802 {
1803 /* Convert from ULONG to a BOOL */
1804 *pDisablePriorityBoost = PriorityBoost ? TRUE : FALSE;
1805 return TRUE;
1806 }
1807
1808 /* Handle error path */
1810 return FALSE;
1811}
_In_ WDFREQUEST _In_ NTSTATUS _In_ CCHAR PriorityBoost
Definition: wdfrequest.h:1016
@ ProcessPriorityBoost
Definition: winternl.h:1904

◆ GetProcessShutdownParameters()

BOOL WINAPI GetProcessShutdownParameters ( OUT LPDWORD  lpdwLevel,
OUT LPDWORD  lpdwFlags 
)

Definition at line 969 of file proc.c.

971{
972 BASE_API_MESSAGE ApiMessage;
973 PBASE_GETSET_PROCESS_SHUTDOWN_PARAMS ShutdownParametersRequest = &ApiMessage.Data.ShutdownParametersRequest;
974
975 /* Ask CSRSS for shutdown information */
977 NULL,
979 sizeof(*ShutdownParametersRequest));
980 if (!NT_SUCCESS(ApiMessage.Status))
981 {
982 /* Return the failure from CSRSS */
983 BaseSetLastNTError(ApiMessage.Status);
984 return FALSE;
985 }
986
987 /* Get the data back */
988 *lpdwLevel = ShutdownParametersRequest->ShutdownLevel;
989 *lpdwFlags = ShutdownParametersRequest->ShutdownFlags;
990 return TRUE;
991}
@ BasepGetProcessShutdownParam
Definition: basemsg.h:34
BASE_GETSET_PROCESS_SHUTDOWN_PARAMS ShutdownParametersRequest
Definition: basemsg.h:294
NTSTATUS Status
Definition: csrmsg.h:110

◆ GetProcessTimes()

BOOL WINAPI GetProcessTimes ( IN HANDLE  hProcess,
IN LPFILETIME  lpCreationTime,
IN LPFILETIME  lpExitTime,
IN LPFILETIME  lpKernelTime,
IN LPFILETIME  lpUserTime 
)

Definition at line 1148 of file proc.c.

1153{
1156
1157 /* Query the times */
1160 &Kut,
1161 sizeof(Kut),
1162 NULL);
1163 if (!NT_SUCCESS(Status))
1164 {
1165 /* Handle failure */
1167 return FALSE;
1168 }
1169
1170 /* Copy all the times and return success */
1171 lpCreationTime->dwLowDateTime = Kut.CreateTime.u.LowPart;
1172 lpCreationTime->dwHighDateTime = Kut.CreateTime.u.HighPart;
1173 lpExitTime->dwLowDateTime = Kut.ExitTime.u.LowPart;
1174 lpExitTime->dwHighDateTime = Kut.ExitTime.u.HighPart;
1175 lpKernelTime->dwLowDateTime = Kut.KernelTime.u.LowPart;
1176 lpKernelTime->dwHighDateTime = Kut.KernelTime.u.HighPart;
1177 lpUserTime->dwLowDateTime = Kut.UserTime.u.LowPart;
1178 lpUserTime->dwHighDateTime = Kut.UserTime.u.HighPart;
1179 return TRUE;
1180}
LARGE_INTEGER UserTime
Definition: winternl.h:2377
LARGE_INTEGER CreateTime
Definition: winternl.h:2374
LARGE_INTEGER KernelTime
Definition: winternl.h:2376
LARGE_INTEGER ExitTime
Definition: winternl.h:2375
struct _LARGE_INTEGER::@2753 u
@ ProcessTimes
Definition: winternl.h:1886

◆ GetProcessVersion()

DWORD WINAPI GetProcessVersion ( IN DWORD  ProcessId)

Definition at line 1661 of file proc.c.

1662{
1663 DWORD Version = 0;
1664 PIMAGE_NT_HEADERS NtHeader;
1665 PIMAGE_DOS_HEADER DosHeader;
1666 PPEB Peb;
1667 PROCESS_BASIC_INFORMATION ProcessBasicInfo;
1672 USHORT VersionData[2];
1674
1675 /* We'll be accessing stuff that can fault, so protect everything with SEH */
1676 _SEH2_TRY
1677 {
1678 /* It this an in-process or out-of-process request? */
1679 if (!(ProcessId) || (GetCurrentProcessId() == ProcessId))
1680 {
1681 /* It's in-process, so just read our own header */
1682 NtHeader = RtlImageNtHeader(NtCurrentPeb()->ImageBaseAddress);
1683 if (!NtHeader)
1684 {
1685 /* Unable to read the NT header, something is wrong here... */
1687 goto Error;
1688 }
1689
1690 /* Get the version straight out of the NT header */
1693 }
1694 else
1695 {
1696 /* Out-of-process, so open it */
1698 FALSE,
1699 ProcessId);
1700 if (!ProcessHandle) _SEH2_YIELD(return 0);
1701
1702 /* Try to find out where its PEB lives */
1705 &ProcessBasicInfo,
1706 sizeof(ProcessBasicInfo),
1707 NULL);
1708
1709 if (!NT_SUCCESS(Status)) goto Error;
1710 Peb = ProcessBasicInfo.PebBaseAddress;
1711
1712 /* Now that we have the PEB, read the image base address out of it */
1715 &BaseAddress,
1716 sizeof(BaseAddress),
1717 NULL);
1718 if (!Result) goto Error;
1719
1720 /* Now read the e_lfanew (offset to NT header) from the base */
1721 DosHeader = BaseAddress;
1723 &DosHeader->e_lfanew,
1724 &e_lfanew,
1725 sizeof(e_lfanew),
1726 NULL);
1727 if (!Result) goto Error;
1728
1729 /* And finally, read the NT header itself by adding the offset */
1730 NtHeader = (PVOID)((ULONG_PTR)BaseAddress + e_lfanew);
1733 &VersionData,
1734 sizeof(VersionData),
1735 NULL);
1736 if (!Result) goto Error;
1737
1738 /* Get the version straight out of the NT header */
1739 Version = MAKELONG(VersionData[0], VersionData[1]);
1740
1741Error:
1742 /* If there was an error anywhere, set the last error */
1744 }
1745 }
1747 {
1748 /* Close the process handle */
1750 }
1751 _SEH2_END;
1752
1753 /* And return the version data */
1754 return Version;
1755}
BOOL Error
Definition: chkdsk.c:66
#define ReadProcessMemory(a, b, c, d, e)
Definition: compat.h:758
HANDLE WINAPI OpenProcess(IN DWORD dwDesiredAccess, IN BOOL bInheritHandle, IN DWORD dwProcessId)
Definition: proc.c:1276
IN PLARGE_INTEGER IN PLARGE_INTEGER PEPROCESS ProcessId
Definition: fatprocs.h:2712
#define PROCESS_VM_READ
Definition: pstypes.h:157
#define PROCESS_QUERY_INFORMATION
Definition: pstypes.h:162
DWORD e_lfanew
Definition: crypt.c:1299
#define STATUS_INVALID_IMAGE_FORMAT
Definition: ntstatus.h:453
#define _SEH2_YIELD(__stmt)
Definition: pseh2_64.h:207
PVOID ImageBaseAddress
Definition: ntddk_ex.h:245
#define MAKELONG(a, b)
Definition: typedefs.h:249
_Must_inspect_result_ _In_ WDFDEVICE _In_ LPCGUID _Out_ PINTERFACE _In_ USHORT _In_ USHORT Version
Definition: wdffdo.h:469
DWORD WINAPI GetCurrentProcessId(void)
Definition: proc.c:1207

Referenced by get_app_version(), GetSystemInfoInternal(), and SHLWAPI_InitAppCompat().

◆ GetProcessWorkingSetSize()

BOOL WINAPI GetProcessWorkingSetSize ( IN HANDLE  hProcess,
OUT PSIZE_T  lpMinimumWorkingSetSize,
OUT PSIZE_T  lpMaximumWorkingSetSize 
)

Definition at line 1060 of file proc.c.

1063{
1064 DWORD Dummy;
1066 lpMinimumWorkingSetSize,
1067 lpMaximumWorkingSetSize,
1068 &Dummy);
1069}
BOOL WINAPI GetProcessWorkingSetSizeEx(IN HANDLE hProcess, OUT PSIZE_T lpMinimumWorkingSetSize, OUT PSIZE_T lpMaximumWorkingSetSize, OUT PDWORD Flags)
Definition: proc.c:1027

◆ GetProcessWorkingSetSizeEx()

BOOL WINAPI GetProcessWorkingSetSizeEx ( IN HANDLE  hProcess,
OUT PSIZE_T  lpMinimumWorkingSetSize,
OUT PSIZE_T  lpMaximumWorkingSetSize,
OUT PDWORD  Flags 
)

Definition at line 1027 of file proc.c.

1031{
1032 QUOTA_LIMITS_EX QuotaLimits;
1034
1035 /* Query the kernel about this */
1038 &QuotaLimits,
1039 sizeof(QuotaLimits),
1040 NULL);
1041 if (!NT_SUCCESS(Status))
1042 {
1043 /* Return error */
1045 return FALSE;
1046 }
1047
1048 /* Copy the quota information out */
1049 *lpMinimumWorkingSetSize = QuotaLimits.MinimumWorkingSetSize;
1050 *lpMaximumWorkingSetSize = QuotaLimits.MaximumWorkingSetSize;
1051 *Flags = QuotaLimits.Flags;
1052 return TRUE;
1053}
SIZE_T MaximumWorkingSetSize
Definition: pstypes.h:71
SIZE_T MinimumWorkingSetSize
Definition: pstypes.h:70
@ ProcessQuotaLimits
Definition: winternl.h:1883

Referenced by GetProcessWorkingSetSize().

◆ GetStartupInfoW()

VOID WINAPI GetStartupInfoW ( IN LPSTARTUPINFOW  lpStartupInfo)

Definition at line 1317 of file proc.c.

1318{
1320
1321 /* Get the process parameters */
1322 Params = NtCurrentPeb()->ProcessParameters;
1323
1324 /* Copy the data out of there */
1325 lpStartupInfo->cb = sizeof(STARTUPINFOW);
1326 lpStartupInfo->lpReserved = Params->ShellInfo.Buffer;
1327 lpStartupInfo->lpDesktop = Params->DesktopInfo.Buffer;
1328 lpStartupInfo->lpTitle = Params->WindowTitle.Buffer;
1329 lpStartupInfo->dwX = Params->StartingX;
1330 lpStartupInfo->dwY = Params->StartingY;
1331 lpStartupInfo->dwXSize = Params->CountX;
1332 lpStartupInfo->dwYSize = Params->CountY;
1333 lpStartupInfo->dwXCountChars = Params->CountCharsX;
1334 lpStartupInfo->dwYCountChars = Params->CountCharsY;
1335 lpStartupInfo->dwFillAttribute = Params->FillAttribute;
1336 lpStartupInfo->dwFlags = Params->WindowFlags;
1337 lpStartupInfo->wShowWindow = (WORD)Params->ShowWindowFlags;
1338 lpStartupInfo->cbReserved2 = Params->RuntimeData.Length;
1339 lpStartupInfo->lpReserved2 = (LPBYTE)Params->RuntimeData.Buffer;
1340
1341 /* Check if the standard handles are being used for other features */
1342 if (lpStartupInfo->dwFlags & (STARTF_USESTDHANDLES |
1344 STARTF_SHELLPRIVATE))
1345 {
1346 /* These are, so copy the standard handles too */
1347 lpStartupInfo->hStdInput = Params->StandardInput;
1348 lpStartupInfo->hStdOutput = Params->StandardOutput;
1349 lpStartupInfo->hStdError = Params->StandardError;
1350 }
1351}
unsigned short WORD
Definition: ntddk_ex.h:93
struct _STARTUPINFOW STARTUPINFOW
unsigned char * LPBYTE
Definition: typedefs.h:53
_In_ WDFIOTARGET _In_ PWDF_REQUEST_COMPLETION_PARAMS Params
Definition: wdfrequest.h:308

Referenced by alloc_console(), AttachConsole(), initialize_inherited_file_handles_nolock(), test_AllocConsole_child(), wmain(), and wWinMain().

◆ InitCommandLines()

VOID WINAPI InitCommandLines ( VOID  )

Definition at line 841 of file proc.c.

842{
844
845 /* Read the UNICODE_STRING from the PEB */
846 BaseUnicodeCommandLine = NtCurrentPeb()->ProcessParameters->CommandLine;
847
848 /* Convert to ANSI_STRING for the *A callers */
851 TRUE);
852 if (!NT_SUCCESS(Status)) RtlInitEmptyAnsiString(&BaseAnsiCommandLine, 0, 0);
853}
NTSYSAPI NTSTATUS NTAPI RtlUnicodeStringToAnsiString(PANSI_STRING DestinationString, PUNICODE_STRING SourceString, BOOLEAN AllocateDestinationString)

Referenced by DllMain().

◆ IsWow64Process()

BOOL WINAPI IsWow64Process ( IN HANDLE  hProcess,
OUT PBOOL  Wow64Process 
)

Definition at line 1875 of file proc.c.

1877{
1878 ULONG_PTR pbi;
1880
1881 /* Query the kernel */
1884 &pbi,
1885 sizeof(pbi),
1886 NULL);
1887 if (!NT_SUCCESS(Status))
1888 {
1889 /* Handle error path */
1891 return FALSE;
1892 }
1893
1894 /* Enforce this is a BOOL, and return success */
1895 *Wow64Process = (pbi != 0);
1896 return TRUE;
1897}
@ ProcessWow64Information
Definition: cicbase.cpp:65
_Inout_ PERBANDINFO * pbi
Definition: winddi.h:3917

◆ OpenProcess()

HANDLE WINAPI OpenProcess ( IN DWORD  dwDesiredAccess,
IN BOOL  bInheritHandle,
IN DWORD  dwProcessId 
)

Definition at line 1276 of file proc.c.

1279{
1284
1285 /* Setup the input client ID structure */
1288
1289 /* This is needed just to define the inheritance flags */
1291 NULL,
1293 NULL,
1294 NULL);
1295
1296 /* Now try to open the process */
1298 dwDesiredAccess,
1300 &ClientId);
1301 if (!NT_SUCCESS(Status))
1302 {
1303 /* Handle failure */
1305 return NULL;
1306 }
1307
1308 /* Otherwise return a handle to the process */
1309 return ProcessHandle;
1310}
#define UlongToHandle(ul)
Definition: basetsd.h:91
static BOOL bInheritHandle
Definition: pipe.c:110
NTSTATUS NTAPI NtOpenProcess(OUT PHANDLE ProcessHandle, IN ACCESS_MASK DesiredAccess, IN POBJECT_ATTRIBUTES ObjectAttributes, IN PCLIENT_ID ClientId)
Definition: process.c:1480
_In_ DWORD dwProcessId
Definition: shlwapi.h:193
#define OBJ_INHERIT
Definition: winternl.h:225

Referenced by _DoDLLInjection(), _RpcCommitSpoolData2(), _RpcGetSpoolFileInfo2(), CIconWatcher::AddIconToWatcher(), child_process(), child_process_exit_process_async(), CloseProcess(), CloseProcessAndVerify_(), DebugActiveProcess(), DebugActiveProcessStop(), debugcontrol_WaitForEvent(), dll_entry_point(), doChild(), DoSetPriority(), enum_modules64(), ExecuteKill(), get_droptarget_local_handle(), get_proc_address64(), get_process_name_from_pid(), GetOwnerModuleFromPidEntry(), GetProcessExecutablePathById(), GetProcessHandleFromHwnd(), GetProcessVersion(), GetThemeServiceProcessHandle(), Ghost_DestroyTarget(), IsProcessRunning(), ObjectFromLresult(), PerfDataGetCommandLine(), PerfDataRefresh(), PNP_ReportLogOn(), ProcessIdToSessionId(), ProcessKeys(), ProcessList_Update(), ProcessPage_OnEndProcess(), ProcessPage_OnEndProcessTree(), ProcessPage_OnSetAffinity(), ProcessPageShowContextMenu(), ProcessRunning(), SeclCreateProcessWithLogonW(), SHELL_GetImageFileNameByWindow(), SHMapHandle(), ShutdownProcessTreeHelper(), START_TEST(), terminate_processes(), test_D3DKMTQueryVideoMemoryInfo(), test_duplicate_handle_access_child(), test_exception_dispatcher(), test_ExitProcess(), test_init_block(), test_nt_wow64(), test_OpenProcess(), test_parent_process_attribute(), test_process_id(), test_process_security_child(), test_query_process_handlecount(), test_query_process_times(), test_query_process_vm(), test_QueryFullProcessImageNameW(), test_readvirtualmemory(), test_syscalls(), test_Toolhelp(), test_ws_functions(), Toolhelp32ReadProcessMemory(), WSPDuplicateSocket(), and wWinMain().

◆ ProcessIdToSessionId()

BOOL WINAPI ProcessIdToSessionId ( IN DWORD  dwProcessId,
OUT PDWORD  pSessionId 
)

Definition at line 2076 of file proc.c.

2078{
2079 PROCESS_SESSION_INFORMATION SessionInformation;
2084
2085 /* Do a quick check if the pointer is not writable */
2086 if (IsBadWritePtr(pSessionId, sizeof(DWORD)))
2087 {
2088 /* Fail fast */
2090 return FALSE;
2091 }
2092
2093 /* Open the process passed in by ID */
2100 &ClientId);
2101 if (NT_SUCCESS(Status))
2102 {
2103 /* Query the session ID from the kernel */
2106 &SessionInformation,
2107 sizeof(SessionInformation),
2108 NULL);
2109
2110 /* Close the handle and check if we succeeded */
2112 if (NT_SUCCESS(Status))
2113 {
2114 /* Return the session ID */
2115 *pSessionId = SessionInformation.SessionId;
2116 return TRUE;
2117 }
2118 }
2119
2120 /* Set error code and fail */
2122 return FALSE;
2123}
BOOL NTAPI IsBadWritePtr(IN LPVOID lp, IN UINT_PTR ucb)
Definition: except.c:883
@ ProcessSessionInformation
Definition: winternl.h:1906

Referenced by AddPortW(), child_process_check_session_id(), ConfigurePortW(), START_TEST(), test_namedpipe_session_id(), and test_SHCreateSessionKey().

◆ ReadProcessMemory()

BOOL NTAPI ReadProcessMemory ( IN HANDLE  hProcess,
IN LPCVOID  lpBaseAddress,
IN LPVOID  lpBuffer,
IN SIZE_T  nSize,
OUT SIZE_T *  lpNumberOfBytesRead 
)

Definition at line 1924 of file proc.c.

1929{
1931
1932 /* Do the read */
1934 (PVOID)lpBaseAddress,
1935 lpBuffer,
1936 nSize,
1937 &nSize);
1938
1939 /* In user-mode, this parameter is optional */
1940 if (lpNumberOfBytesRead) *lpNumberOfBytesRead = nSize;
1941 if (!NT_SUCCESS(Status))
1942 {
1943 /* We failed */
1945 return FALSE;
1946 }
1947
1948 /* Return success */
1949 return TRUE;
1950}
_Out_ LPWSTR lpBuffer
Definition: netsh.h:68

◆ RegisterWaitForInputIdle()

VOID WINAPI RegisterWaitForInputIdle ( WaitForInputIdleType  lpfnRegisterWaitForInputIdle)

◆ SetPriorityClass()

BOOL WINAPI SetPriorityClass ( IN HANDLE  hProcess,
IN DWORD  dwPriorityClass 
)

Definition at line 1593 of file proc.c.

1595{
1597 PVOID State = NULL;
1598 PROCESS_PRIORITY_CLASS PriorityClass;
1599
1600 /* Handle conversion from Win32 to NT priority classes */
1601 switch (dwPriorityClass)
1602 {
1605 break;
1606
1609 break;
1610
1613 break;
1614
1617 break;
1618
1621 break;
1622
1624 /* Try to acquire the privilege. If it fails, just use HIGH */
1627 PriorityClass.PriorityClass += (State != NULL);
1628 break;
1629
1630 default:
1631 /* Unrecognized priority classes don't make it to the kernel */
1633 return FALSE;
1634 }
1635
1636 /* Send the request to the kernel, and don't touch the foreground flag */
1637 PriorityClass.Foreground = FALSE;
1640 &PriorityClass,
1641 sizeof(PROCESS_PRIORITY_CLASS));
1642
1643 /* Release the privilege if we had it */
1645 if (!NT_SUCCESS(Status))
1646 {
1647 /* Handle error path */
1649 return FALSE;
1650 }
1651
1652 /* All done */
1653 return TRUE;
1654}

Referenced by CsrSetPriorityClass(), DoSetPriority(), main(), test_query_process_priority(), UpdatePriority(), and wWinMain().

◆ SetProcessAffinityMask()

BOOL WINAPI SetProcessAffinityMask ( IN HANDLE  hProcess,
IN DWORD_PTR  dwProcessAffinityMask 
)

Definition at line 893 of file proc.c.

895{
897
898 /* Directly set the affinity mask */
901 (PVOID)&dwProcessAffinityMask,
902 sizeof(dwProcessAffinityMask));
903 if (!NT_SUCCESS(Status))
904 {
905 /* Handle failure */
907 return FALSE;
908 }
909
910 /* Everything was ok */
911 return TRUE;
912}
@ ProcessAffinityMask
Definition: winternl.h:1903

Referenced by AffinityDialogWndProc(), and cmd_start().

◆ SetProcessPriorityBoost()

BOOL WINAPI SetProcessPriorityBoost ( IN HANDLE  hProcess,
IN BOOL  bDisablePriorityBoost 
)

Definition at line 1818 of file proc.c.

1820{
1823
1824 /* Enforce that this is a BOOL, and send it to the kernel as a ULONG */
1825 PriorityBoost = (bDisablePriorityBoost ? TRUE : FALSE);
1829 sizeof(ULONG));
1830 if (!NT_SUCCESS(Status))
1831 {
1832 /* Handle error path */
1834 return FALSE;
1835 }
1836
1837 /* All done */
1838 return TRUE;
1839}

◆ SetProcessShutdownParameters()

BOOL WINAPI SetProcessShutdownParameters ( IN DWORD  dwLevel,
IN DWORD  dwFlags 
)

Definition at line 998 of file proc.c.

1000{
1001 BASE_API_MESSAGE ApiMessage;
1002 PBASE_GETSET_PROCESS_SHUTDOWN_PARAMS ShutdownParametersRequest = &ApiMessage.Data.ShutdownParametersRequest;
1003
1004 /* Write the data into the CSRSS request and send it */
1005 ShutdownParametersRequest->ShutdownLevel = dwLevel;
1006 ShutdownParametersRequest->ShutdownFlags = dwFlags;
1008 NULL,
1010 sizeof(*ShutdownParametersRequest));
1011 if (!NT_SUCCESS(ApiMessage.Status))
1012 {
1013 /* Return the failure from CSRSS */
1014 BaseSetLastNTError(ApiMessage.Status);
1015 return FALSE;
1016 }
1017
1018 /* All went well */
1019 return TRUE;
1020}
@ BasepSetProcessShutdownParam
Definition: basemsg.h:33
_In_ LPWSTR _In_ DWORD _In_ DWORD _In_ DWORD dwFlags
Definition: netsh.h:141

Referenced by _tWinMain(), and wWinMain().

◆ SetProcessWorkingSetSize()

BOOL WINAPI SetProcessWorkingSetSize ( IN HANDLE  hProcess,
IN SIZE_T  dwMinimumWorkingSetSize,
IN SIZE_T  dwMaximumWorkingSetSize 
)

Definition at line 1132 of file proc.c.

1135{
1136 /* Call the newer API */
1138 dwMinimumWorkingSetSize,
1139 dwMaximumWorkingSetSize,
1140 0);
1141}
BOOL WINAPI SetProcessWorkingSetSizeEx(IN HANDLE hProcess, IN SIZE_T dwMinimumWorkingSetSize, IN SIZE_T dwMaximumWorkingSetSize, IN DWORD Flags)
Definition: proc.c:1076

◆ SetProcessWorkingSetSizeEx()

BOOL WINAPI SetProcessWorkingSetSizeEx ( IN HANDLE  hProcess,
IN SIZE_T  dwMinimumWorkingSetSize,
IN SIZE_T  dwMaximumWorkingSetSize,
IN DWORD  Flags 
)

Definition at line 1076 of file proc.c.

1080{
1081 QUOTA_LIMITS_EX QuotaLimits;
1082 NTSTATUS Status, ReturnStatus;
1083 BOOL Result;
1084 PVOID State;
1086
1087 /* Zero out the input structure */
1088 RtlZeroMemory(&QuotaLimits, sizeof(QuotaLimits));
1089
1090 /* Check if the caller sent any limits */
1091 if ((dwMinimumWorkingSetSize) && (dwMaximumWorkingSetSize))
1092 {
1093 /* Write the quota information */
1094 QuotaLimits.MinimumWorkingSetSize = dwMinimumWorkingSetSize;
1095 QuotaLimits.MaximumWorkingSetSize = dwMaximumWorkingSetSize;
1096 QuotaLimits.Flags = Flags;
1097
1098 /* Acquire the required privilege */
1100
1101 /* Request the new quotas */
1102 ReturnStatus = NtSetInformationProcess(hProcess,
1104 &QuotaLimits,
1105 sizeof(QuotaLimits));
1106 Result = NT_SUCCESS(ReturnStatus);
1107 if (NT_SUCCESS(Status))
1108 {
1109 /* Release the privilege and set succes code */
1110 ASSERT(State != NULL);
1112 State = NULL;
1113 }
1114 }
1115 else
1116 {
1117 /* No limits, fail the call */
1118 ReturnStatus = STATUS_INVALID_PARAMETER;
1119 Result = FALSE;
1120 }
1121
1122 /* Return result code, set error code if this was a failure */
1123 if (!Result) BaseSetLastNTError(ReturnStatus);
1124 return Result;
1125}
#define SE_INC_BASE_PRIORITY_PRIVILEGE
Definition: security.c:568
#define STATUS_INVALID_PARAMETER
Definition: udferr_usr.h:135
BOOL Privilege(LPTSTR pszPrivilege, BOOL bEnable)
Definition: user_lib.cpp:531

Referenced by EmptyWorkingSet(), and SetProcessWorkingSetSize().

◆ StuffStdHandle()

VOID WINAPI StuffStdHandle ( IN HANDLE  ProcessHandle,
IN HANDLE  StandardHandle,
IN PHANDLE  Address 
)

Definition at line 57 of file proc.c.

60{
62 HANDLE DuplicatedHandle;
63 SIZE_T NumberOfBytesWritten;
64
65 /* If there is no handle to duplicate, return immediately */
66 if (!StandardHandle) return;
67
68 /* Duplicate the handle */
70 StandardHandle,
72 &DuplicatedHandle,
73 0,
74 0,
77 if (!NT_SUCCESS(Status)) return;
78
79 /* Write it */
81 Address,
82 &DuplicatedHandle,
83 sizeof(HANDLE),
84 &NumberOfBytesWritten);
85}
#define DUPLICATE_SAME_ATTRIBUTES
Definition: obtypes.h:127
NTSTATUS NTAPI NtDuplicateObject(IN HANDLE SourceProcessHandle, IN HANDLE SourceHandle, IN HANDLE TargetProcessHandle OPTIONAL, OUT PHANDLE TargetHandle OPTIONAL, IN ACCESS_MASK DesiredAccess, IN ULONG HandleAttributes, IN ULONG Options)
Definition: obhandle.c:3442
static WCHAR Address[46]
Definition: ping.c:68
#define DUPLICATE_SAME_ACCESS

Referenced by CreateProcessInternalW().

◆ TerminateProcess()

BOOL WINAPI TerminateProcess ( IN HANDLE  hProcess,
IN UINT  uExitCode 
)

Definition at line 1427 of file proc.c.

1429{
1431
1432 /* Check if no handle was passed in */
1433 if (!hProcess)
1434 {
1435 /* Set error code */
1437 }
1438 else
1439 {
1440 /* Otherwise, try to terminate the process */
1441 Status = NtTerminateProcess(hProcess, uExitCode);
1442 if (NT_SUCCESS(Status)) return TRUE;
1443
1444 /* It failed, convert error code */
1446 }
1447
1448 /* This is the failure path */
1449 return FALSE;
1450}
#define ERROR_INVALID_HANDLE
Definition: compat.h:98

Referenced by child_process(), Telnet::Close(), CloseProcess(), common_message_window(), ConsoleIMERoutine(), CorDebug_CreateProcess(), cordebugprocess_Terminate(), CPlApplet(), crash_and_debug(), CreateProcessAsUserCommon(), do_register_dll(), DoTestEntry(), ExecuteKill(), ExecutePipeline(), exit_or_terminate_process(), Ghost_DestroyTarget(), ProcessKeys(), ProcessPage_OnEndProcess(), RaiseFailFastException(), read_reg_output_(), run_ex(), run_reg_exe_(), run_regedit_exe_(), runcmd(), RunProcessInJob(), ScreenSaverConfig(), ScreenSaverPageProc(), ScreenSaverPreview(), SetScreenSaverPreviewBox(), ShutdownProcessTreeHelper(), START_TEST(), StartScreenSaver(), SymCryptFatalEnvWindowsUsermodeWin8_1nLater(), terminate_processes(), TerminateShell(), test_apc_deadlock(), test_async_cancel_on_handle_close(), test_BreakawayOk(), test_CompletionPort(), test_CreateRemoteThread(), test_CtrlHandlerSubsystem(), test_debugger(), test_Directory(), TEST_DoTestEntryStruct(), test_EnumProcessModules(), test_ExitProcess(), test_GetProcessVersion(), test_IsProcessInJob(), test_IsWow64Process(), test_IsWow64Process2(), test_job_list_attribute(), test_kill_on_exit(), test_KillOnJobClose(), Test_layers(), test_loadpaths_execute(), test_nested_jobs(), test_nested_jobs_child(), test_NtMapViewOfSection(), test_NtMapViewOfSectionEx(), test_overlapped_transport(), test_peb_teb(), test_process_access(), test_query_architectures(), test_QueryInformationJobObject(), Test_repeatlayer(), test_RunSetupCommand(), test_section_access(), test_TerminateJobObject(), test_TerminateProcess(), test_VirtualAllocEx(), test_WaitForInputIdle(), TestTerminateProcess(), UnhandledExceptionFilter(), WshExec_Terminate(), wWinMain(), and CProcess::~CProcess().

◆ WriteProcessMemory()

BOOL NTAPI WriteProcessMemory ( IN HANDLE  hProcess,
IN LPVOID  lpBaseAddress,
IN LPCVOID  lpBuffer,
IN SIZE_T  nSize,
OUT SIZE_T *  lpNumberOfBytesWritten 
)

Definition at line 1957 of file proc.c.

1962{
1964 ULONG OldValue;
1966 PVOID Base;
1968
1969 /* Set parameters for protect call */
1970 RegionSize = nSize;
1971 Base = lpBaseAddress;
1972
1973 /* Check the current status */
1975 &Base,
1976 &RegionSize,
1978 &OldValue);
1979 if (NT_SUCCESS(Status))
1980 {
1981 /* Check if we are unprotecting */
1982 UnProtect = OldValue & (PAGE_READWRITE |
1986 if (!UnProtect)
1987 {
1988 /* Set the new protection */
1990 &Base,
1991 &RegionSize,
1992 OldValue,
1993 &OldValue);
1994
1995 /* Write the memory */
1997 lpBaseAddress,
1999 nSize,
2000 &nSize);
2001
2002 /* In Win32, the parameter is optional, so handle this case */
2003 if (lpNumberOfBytesWritten) *lpNumberOfBytesWritten = nSize;
2004
2005 if (!NT_SUCCESS(Status))
2006 {
2007 /* We failed */
2009 return FALSE;
2010 }
2011
2012 /* Flush the ITLB */
2013 NtFlushInstructionCache(hProcess, lpBaseAddress, nSize);
2014 return TRUE;
2015 }
2016 else
2017 {
2018 /* Check if we were read only */
2019 if (OldValue & (PAGE_NOACCESS | PAGE_READONLY))
2020 {
2021 /* Restore protection and fail */
2023 &Base,
2024 &RegionSize,
2025 OldValue,
2026 &OldValue);
2028
2029 /* Note: This is what Windows returns and code depends on it */
2031 }
2032
2033 /* Otherwise, do the write */
2035 lpBaseAddress,
2037 nSize,
2038 &nSize);
2039
2040 /* In Win32, the parameter is optional, so handle this case */
2041 if (lpNumberOfBytesWritten) *lpNumberOfBytesWritten = nSize;
2042
2043 /* And restore the protection */
2045 &Base,
2046 &RegionSize,
2047 OldValue,
2048 &OldValue);
2049 if (!NT_SUCCESS(Status))
2050 {
2051 /* We failed */
2053
2054 /* Note: This is what Windows returns and code depends on it */
2056 }
2057
2058 /* Flush the ITLB */
2059 NtFlushInstructionCache(hProcess, lpBaseAddress, nSize);
2060 return TRUE;
2061 }
2062 }
2063 else
2064 {
2065 /* We failed */
2067 return FALSE;
2068 }
2069}
#define PAGE_READONLY
Definition: compat.h:138
#define STATUS_ACCESS_VIOLATION
_In_opt_ ULONG Base
Definition: rtlfuncs.h:2486
#define PAGE_WRITECOPY
Definition: nt_native.h:1308
#define PAGE_EXECUTE_WRITECOPY
Definition: nt_native.h:1312
#define PAGE_NOACCESS
Definition: nt_native.h:1305
NTSTATUS NTAPI NtProtectVirtualMemory(IN HANDLE ProcessHandle, IN OUT PVOID *UnsafeBaseAddress, IN OUT SIZE_T *UnsafeNumberOfBytesToProtect, IN ULONG NewAccessProtection, OUT PULONG UnsafeOldAccessProtection)
Definition: virtual.c:3076

Referenced by _DoDLLInjection(), hook_notification_function(), test_cross_process_notifications(), test_debugger(), test_notifications(), and test_VirtualAllocEx().

Variable Documentation

◆ BaseAnsiCommandLine

ANSI_STRING BaseAnsiCommandLine

Definition at line 23 of file proc.c.

Referenced by GetCommandLineA(), and InitCommandLines().

◆ BasepAppCertDllsList

LIST_ENTRY BasepAppCertDllsList

Definition at line 28 of file proc.c.

Referenced by BasepIsProcessAllowed(), and DllMain().

◆ BasepAppCertTable

RTL_QUERY_REGISTRY_TABLE BasepAppCertTable[2]
Initial value:
=
{
{
1,
L"AppCertDlls",
0,
0
}
}
NTSTATUS NTAPI BasepConfigureAppCertDlls(IN PWSTR ValueName, IN ULONG ValueType, IN PVOID ValueData, IN ULONG ValueLength, IN PVOID Context, IN PVOID EntryContext)
Definition: proc.c:189

Definition at line 32 of file proc.c.

Referenced by BasepIsProcessAllowed().

◆ BasePathVariableName

UNICODE_STRING BasePathVariableName = RTL_CONSTANT_STRING(L"PATH")

Definition at line 24 of file proc.c.

Referenced by BasepComputeProcessPath().

◆ BasepExeLdrEntry

PLDR_DATA_TABLE_ENTRY BasepExeLdrEntry

Definition at line 25 of file proc.c.

Referenced by BasepComputeProcessPath(), BasepLocateExeLdrEntry(), and LoadLibraryExW().

◆ BaseUnicodeCommandLine

UNICODE_STRING BaseUnicodeCommandLine

Definition at line 22 of file proc.c.

Referenced by GetCommandLineW(), and InitCommandLines().

◆ fEmbeddedCertFunc

PBASEP_APPCERT_EMBEDDED_FUNC fEmbeddedCertFunc

Definition at line 30 of file proc.c.

Referenced by BasepIsProcessAllowed().

◆ g_AppCertInitialized

BOOLEAN g_AppCertInitialized

Definition at line 26 of file proc.c.

Referenced by BasepIsProcessAllowed().

◆ g_AppCertStatus

NTSTATUS g_AppCertStatus

Definition at line 31 of file proc.c.

Referenced by BasepIsProcessAllowed().

◆ g_HaveAppCerts

BOOLEAN g_HaveAppCerts

Definition at line 27 of file proc.c.

Referenced by BasepIsProcessAllowed().

◆ g_SaferReplaceProcessThreadTokens

PSAFER_REPLACE_PROCESS_THREAD_TOKENS g_SaferReplaceProcessThreadTokens

Definition at line 45 of file proc.c.

Referenced by BasepReplaceProcessThreadTokens().

◆ gcsAppCert

Definition at line 29 of file proc.c.

Referenced by BasepIsProcessAllowed(), BasepReplaceProcessThreadTokens(), and DllMain().

◆ gSaferHandle

HMODULE gSaferHandle = (HMODULE)-1

Definition at line 46 of file proc.c.

Referenced by BasepReplaceProcessThreadTokens().