ReactOS 0.4.17-dev-1321-g5c122a9
samrpc.c File Reference
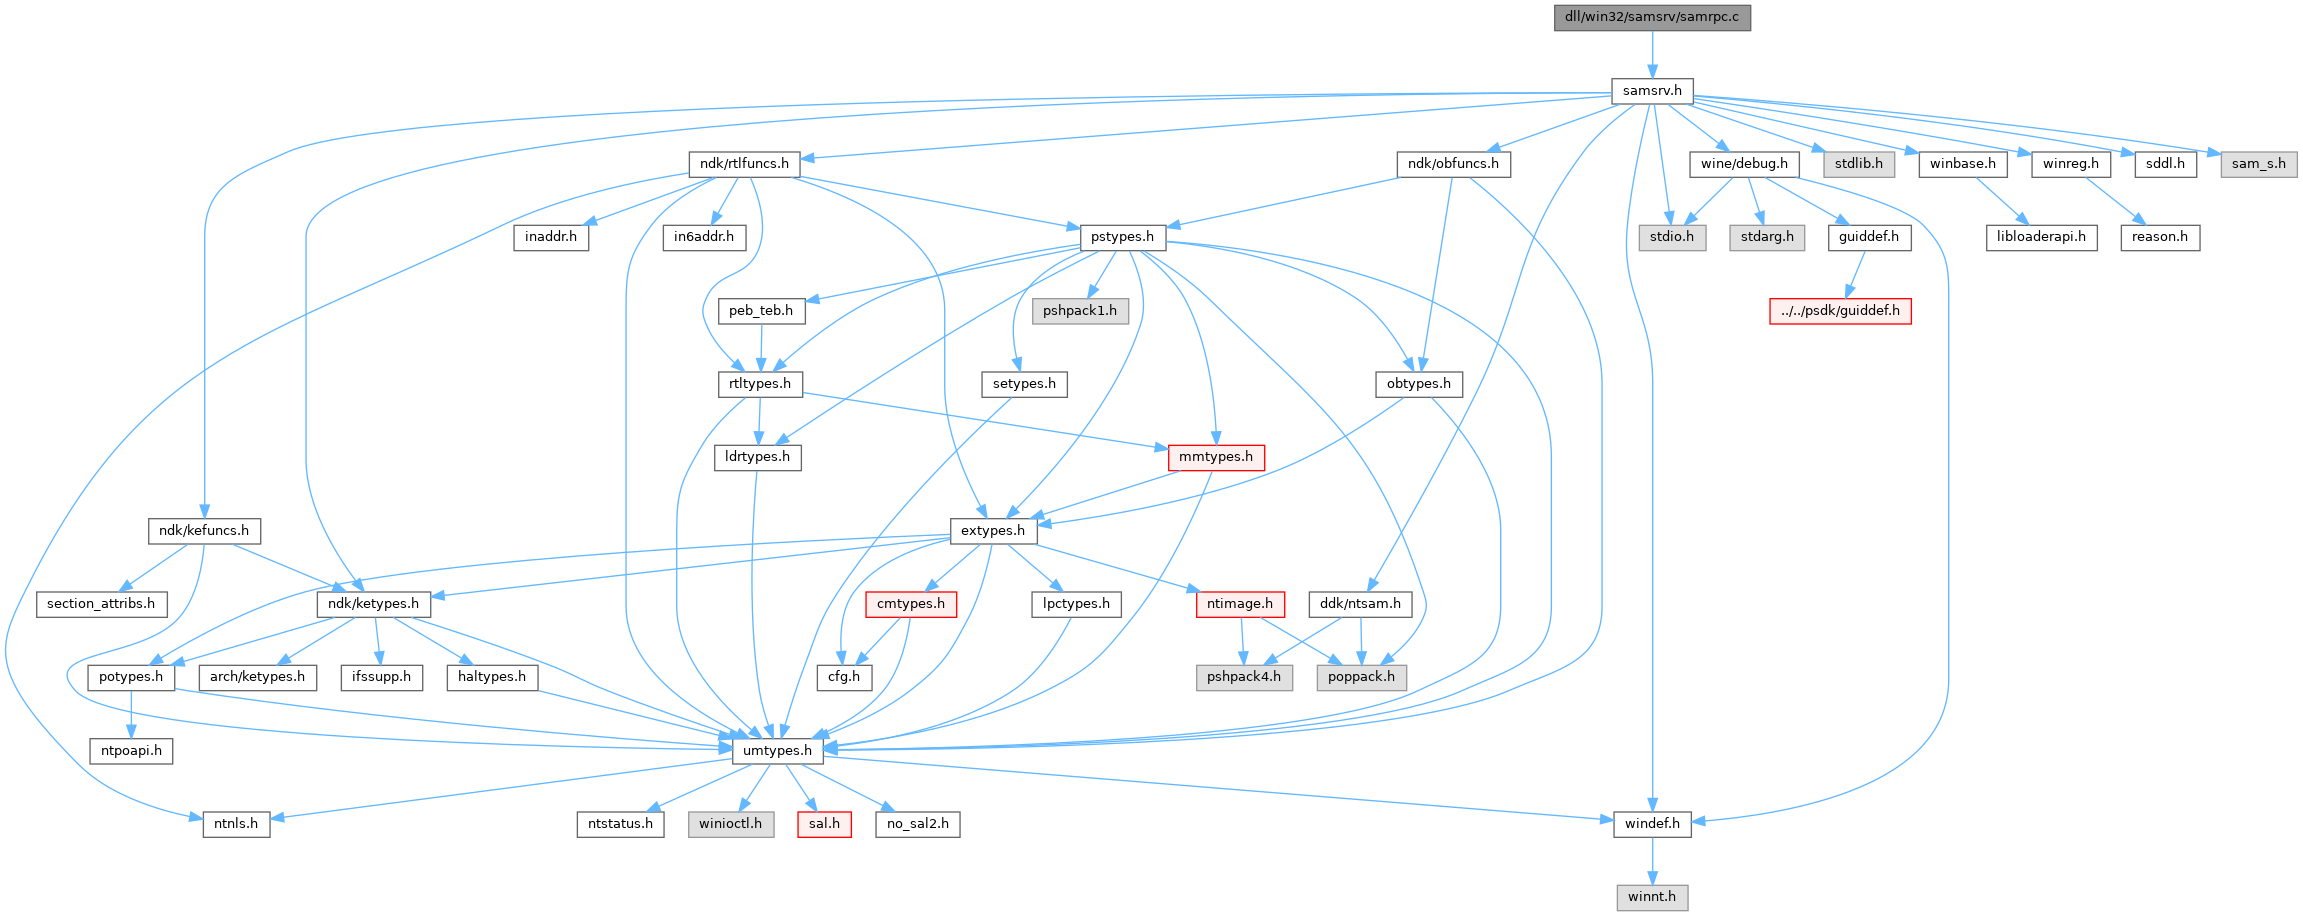
#include "samsrv.h"
Include dependency graph for samrpc.c:

Go to the source code of this file.

Functions

static LARGE_INTEGER SampAddRelativeTimeToTime (IN LARGE_INTEGER AbsoluteTime, IN LARGE_INTEGER RelativeTime)
 
VOID SampStartRpcServer (VOID)
 
void __RPC_FAR *__RPC_USER midl_user_allocate (SIZE_T len)
 
void __RPC_USER midl_user_free (void __RPC_FAR *ptr)
 
void __RPC_USER SAMPR_HANDLE_rundown (SAMPR_HANDLE hHandle)
 
NTSTATUS NTAPI SamrConnect (IN PSAMPR_SERVER_NAME ServerName, OUT SAMPR_HANDLE *ServerHandle, IN ACCESS_MASK DesiredAccess)
 
NTSTATUS NTAPI SamrCloseHandle (IN OUT SAMPR_HANDLE *SamHandle)
 
NTSTATUS NTAPI SamrSetSecurityObject (IN SAMPR_HANDLE ObjectHandle, IN SECURITY_INFORMATION SecurityInformation, IN PSAMPR_SR_SECURITY_DESCRIPTOR SecurityDescriptor)
 
NTSTATUS NTAPI SamrQuerySecurityObject (IN SAMPR_HANDLE ObjectHandle, IN SECURITY_INFORMATION SecurityInformation, OUT PSAMPR_SR_SECURITY_DESCRIPTOR *SecurityDescriptor)
 
NTSTATUS NTAPI SamrShutdownSamServer (IN SAMPR_HANDLE ServerHandle)
 
NTSTATUS NTAPI SamrLookupDomainInSamServer (IN SAMPR_HANDLE ServerHandle, IN PRPC_UNICODE_STRING Name, OUT PRPC_SID *DomainId)
 
NTSTATUS NTAPI SamrEnumerateDomainsInSamServer (IN SAMPR_HANDLE ServerHandle, IN OUT unsigned long *EnumerationContext, OUT PSAMPR_ENUMERATION_BUFFER *Buffer, IN ULONG PreferedMaximumLength, OUT PULONG CountReturned)
 
NTSTATUS NTAPI SamrOpenDomain (IN SAMPR_HANDLE ServerHandle, IN ACCESS_MASK DesiredAccess, IN PRPC_SID DomainId, OUT SAMPR_HANDLE *DomainHandle)
 
static NTSTATUS SampQueryDomainPassword (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
static NTSTATUS SampGetNumberOfAccounts (PSAM_DB_OBJECT DomainObject, LPCWSTR AccountType, PULONG Count)
 
static NTSTATUS SampQueryDomainGeneral (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryDomainLogoff (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryDomainOem (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryDomainName (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryDomainReplication (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryDomainServerRole (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryDomainModified (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryDomainState (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryDomainGeneral2 (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryDomainLockout (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryDomainModified2 (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
NTSTATUS NTAPI SamrQueryInformationDomain (IN SAMPR_HANDLE DomainHandle, IN DOMAIN_INFORMATION_CLASS DomainInformationClass, OUT PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
static NTSTATUS SampSetDomainPassword (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER Buffer)
 
static NTSTATUS SampSetDomainLogoff (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER Buffer)
 
static NTSTATUS SampSetDomainServerRole (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER Buffer)
 
static NTSTATUS SampSetDomainState (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER Buffer)
 
static NTSTATUS SampSetDomainLockout (PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER Buffer)
 
NTSTATUS NTAPI SamrSetInformationDomain (IN SAMPR_HANDLE DomainHandle, IN DOMAIN_INFORMATION_CLASS DomainInformationClass, IN PSAMPR_DOMAIN_INFO_BUFFER DomainInformation)
 
NTSTATUS NTAPI SamrCreateGroupInDomain (IN SAMPR_HANDLE DomainHandle, IN PRPC_UNICODE_STRING Name, IN ACCESS_MASK DesiredAccess, OUT SAMPR_HANDLE *GroupHandle, OUT unsigned long *RelativeId)
 
NTSTATUS NTAPI SamrEnumerateGroupsInDomain (IN SAMPR_HANDLE DomainHandle, IN OUT unsigned long *EnumerationContext, OUT PSAMPR_ENUMERATION_BUFFER *Buffer, IN unsigned long PreferedMaximumLength, OUT unsigned long *CountReturned)
 
NTSTATUS NTAPI SamrCreateUserInDomain (IN SAMPR_HANDLE DomainHandle, IN PRPC_UNICODE_STRING Name, IN ACCESS_MASK DesiredAccess, OUT SAMPR_HANDLE *UserHandle, OUT unsigned long *RelativeId)
 
NTSTATUS NTAPI SamrEnumerateUsersInDomain (IN SAMPR_HANDLE DomainHandle, IN OUT unsigned long *EnumerationContext, IN unsigned long UserAccountControl, OUT PSAMPR_ENUMERATION_BUFFER *Buffer, IN unsigned long PreferedMaximumLength, OUT unsigned long *CountReturned)
 
NTSTATUS NTAPI SamrCreateAliasInDomain (IN SAMPR_HANDLE DomainHandle, IN PRPC_UNICODE_STRING AccountName, IN ACCESS_MASK DesiredAccess, OUT SAMPR_HANDLE *AliasHandle, OUT unsigned long *RelativeId)
 
NTSTATUS NTAPI SamrEnumerateAliasesInDomain (IN SAMPR_HANDLE DomainHandle, IN OUT unsigned long *EnumerationContext, OUT PSAMPR_ENUMERATION_BUFFER *Buffer, IN unsigned long PreferedMaximumLength, OUT unsigned long *CountReturned)
 
NTSTATUS NTAPI SamrGetAliasMembership (IN SAMPR_HANDLE DomainHandle, IN PSAMPR_PSID_ARRAY SidArray, OUT PSAMPR_ULONG_ARRAY Membership)
 
NTSTATUS NTAPI SamrLookupNamesInDomain (IN SAMPR_HANDLE DomainHandle, IN ULONG Count, IN RPC_UNICODE_STRING Names[], OUT PSAMPR_ULONG_ARRAY RelativeIds, OUT PSAMPR_ULONG_ARRAY Use)
 
NTSTATUS NTAPI SamrLookupIdsInDomain (IN SAMPR_HANDLE DomainHandle, IN ULONG Count, IN ULONG *RelativeIds, OUT PSAMPR_RETURNED_USTRING_ARRAY Names, OUT PSAMPR_ULONG_ARRAY Use)
 
NTSTATUS NTAPI SamrOpenGroup (IN SAMPR_HANDLE DomainHandle, IN ACCESS_MASK DesiredAccess, IN unsigned long GroupId, OUT SAMPR_HANDLE *GroupHandle)
 
static NTSTATUS SampQueryGroupGeneral (PSAM_DB_OBJECT GroupObject, PSAMPR_GROUP_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryGroupName (PSAM_DB_OBJECT GroupObject, PSAMPR_GROUP_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryGroupAttribute (PSAM_DB_OBJECT GroupObject, PSAMPR_GROUP_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryGroupAdminComment (PSAM_DB_OBJECT GroupObject, PSAMPR_GROUP_INFO_BUFFER *Buffer)
 
NTSTATUS NTAPI SamrQueryInformationGroup (IN SAMPR_HANDLE GroupHandle, IN GROUP_INFORMATION_CLASS GroupInformationClass, OUT PSAMPR_GROUP_INFO_BUFFER *Buffer)
 
static NTSTATUS SampSetGroupName (PSAM_DB_OBJECT GroupObject, PSAMPR_GROUP_INFO_BUFFER Buffer)
 
static NTSTATUS SampSetGroupAttribute (PSAM_DB_OBJECT GroupObject, PSAMPR_GROUP_INFO_BUFFER Buffer)
 
NTSTATUS NTAPI SamrSetInformationGroup (IN SAMPR_HANDLE GroupHandle, IN GROUP_INFORMATION_CLASS GroupInformationClass, IN PSAMPR_GROUP_INFO_BUFFER Buffer)
 
NTSTATUS NTAPI SamrAddMemberToGroup (IN SAMPR_HANDLE GroupHandle, IN unsigned long MemberId, IN unsigned long Attributes)
 
NTSTATUS NTAPI SamrDeleteGroup (IN OUT SAMPR_HANDLE *GroupHandle)
 
NTSTATUS NTAPI SamrRemoveMemberFromGroup (IN SAMPR_HANDLE GroupHandle, IN unsigned long MemberId)
 
NTSTATUS NTAPI SamrGetMembersInGroup (IN SAMPR_HANDLE GroupHandle, OUT PSAMPR_GET_MEMBERS_BUFFER *Members)
 
NTSTATUS NTAPI SamrSetMemberAttributesOfGroup (IN SAMPR_HANDLE GroupHandle, IN unsigned long MemberId, IN unsigned long Attributes)
 
NTSTATUS NTAPI SamrOpenAlias (IN SAMPR_HANDLE DomainHandle, IN ACCESS_MASK DesiredAccess, IN ULONG AliasId, OUT SAMPR_HANDLE *AliasHandle)
 
static NTSTATUS SampQueryAliasGeneral (PSAM_DB_OBJECT AliasObject, PSAMPR_ALIAS_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryAliasName (PSAM_DB_OBJECT AliasObject, PSAMPR_ALIAS_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryAliasAdminComment (PSAM_DB_OBJECT AliasObject, PSAMPR_ALIAS_INFO_BUFFER *Buffer)
 
NTSTATUS NTAPI SamrQueryInformationAlias (IN SAMPR_HANDLE AliasHandle, IN ALIAS_INFORMATION_CLASS AliasInformationClass, OUT PSAMPR_ALIAS_INFO_BUFFER *Buffer)
 
static NTSTATUS SampSetAliasName (PSAM_DB_OBJECT AliasObject, PSAMPR_ALIAS_INFO_BUFFER Buffer)
 
NTSTATUS NTAPI SamrSetInformationAlias (IN SAMPR_HANDLE AliasHandle, IN ALIAS_INFORMATION_CLASS AliasInformationClass, IN PSAMPR_ALIAS_INFO_BUFFER Buffer)
 
NTSTATUS NTAPI SamrDeleteAlias (IN OUT SAMPR_HANDLE *AliasHandle)
 
NTSTATUS NTAPI SamrAddMemberToAlias (IN SAMPR_HANDLE AliasHandle, IN PRPC_SID MemberId)
 
NTSTATUS NTAPI SamrRemoveMemberFromAlias (IN SAMPR_HANDLE AliasHandle, IN PRPC_SID MemberId)
 
NTSTATUS NTAPI SamrGetMembersInAlias (IN SAMPR_HANDLE AliasHandle, OUT PSAMPR_PSID_ARRAY_OUT Members)
 
NTSTATUS NTAPI SamrOpenUser (IN SAMPR_HANDLE DomainHandle, IN ACCESS_MASK DesiredAccess, IN unsigned long UserId, OUT SAMPR_HANDLE *UserHandle)
 
NTSTATUS NTAPI SamrDeleteUser (IN OUT SAMPR_HANDLE *UserHandle)
 
static NTSTATUS SampQueryUserGeneral (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserPreferences (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserLogon (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserAccount (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserLogonHours (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserName (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserAccountName (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserFullName (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserPrimaryGroup (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserHome (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserScript (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserProfile (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserAdminComment (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserWorkStations (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserControl (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserExpires (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserInternal1 (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserInternal2 (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserParameters (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampQueryUserAll (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
 
NTSTATUS NTAPI SamrQueryInformationUser (IN SAMPR_HANDLE UserHandle, IN USER_INFORMATION_CLASS UserInformationClass, OUT PSAMPR_USER_INFO_BUFFER *Buffer)
 
static NTSTATUS SampSetUserName (PSAM_DB_OBJECT UserObject, PRPC_UNICODE_STRING NewUserName)
 
static NTSTATUS SampSetUserGeneral (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
 
static NTSTATUS SampSetUserPreferences (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
 
static NTSTATUS SampSetUserPrimaryGroup (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
 
static NTSTATUS SampSetUserControl (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
 
static NTSTATUS SampSetUserExpires (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
 
static NTSTATUS SampSetUserInternal1 (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
 
static NTSTATUS SampSetUserInternal2 (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
 
static NTSTATUS SampSetUserAll (PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
 
NTSTATUS NTAPI SamrSetInformationUser (IN SAMPR_HANDLE UserHandle, IN USER_INFORMATION_CLASS UserInformationClass, IN PSAMPR_USER_INFO_BUFFER Buffer)
 
NTSTATUS NTAPI SamrChangePasswordUser (IN SAMPR_HANDLE UserHandle, IN unsigned char LmPresent, IN PENCRYPTED_LM_OWF_PASSWORD OldLmEncryptedWithNewLm, IN PENCRYPTED_LM_OWF_PASSWORD NewLmEncryptedWithOldLm, IN unsigned char NtPresent, IN PENCRYPTED_NT_OWF_PASSWORD OldNtEncryptedWithNewNt, IN PENCRYPTED_NT_OWF_PASSWORD NewNtEncryptedWithOldNt, IN unsigned char NtCrossEncryptionPresent, IN PENCRYPTED_NT_OWF_PASSWORD NewNtEncryptedWithNewLm, IN unsigned char LmCrossEncryptionPresent, IN PENCRYPTED_LM_OWF_PASSWORD NewLmEncryptedWithNewNt)
 
NTSTATUS NTAPI SamrGetGroupsForUser (IN SAMPR_HANDLE UserHandle, OUT PSAMPR_GET_GROUPS_BUFFER *Groups)
 
NTSTATUS NTAPI SamrQueryDisplayInformation (IN SAMPR_HANDLE DomainHandle, IN DOMAIN_DISPLAY_INFORMATION DisplayInformationClass, IN unsigned long Index, IN unsigned long EntryCount, IN unsigned long PreferredMaximumLength, OUT unsigned long *TotalAvailable, OUT unsigned long *TotalReturned, OUT PSAMPR_DISPLAY_INFO_BUFFER Buffer)
 
NTSTATUS NTAPI SamrGetDisplayEnumerationIndex (IN SAMPR_HANDLE DomainHandle, IN DOMAIN_DISPLAY_INFORMATION DisplayInformationClass, IN PRPC_UNICODE_STRING Prefix, OUT unsigned long *Index)
 
NTSTATUS NTAPI SamrTestPrivateFunctionsDomain (IN SAMPR_HANDLE DomainHandle)
 
NTSTATUS NTAPI SamrTestPrivateFunctionsUser (IN SAMPR_HANDLE UserHandle)
 
NTSTATUS NTAPI SamrGetUserDomainPasswordInformation (IN SAMPR_HANDLE UserHandle, OUT PUSER_DOMAIN_PASSWORD_INFORMATION PasswordInformation)
 
NTSTATUS NTAPI SamrRemoveMemberFromForeignDomain (IN SAMPR_HANDLE DomainHandle, IN PRPC_SID MemberSid)
 
NTSTATUS NTAPI SamrQueryInformationDomain2 (IN SAMPR_HANDLE DomainHandle, IN DOMAIN_INFORMATION_CLASS DomainInformationClass, OUT PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
 
NTSTATUS NTAPI SamrQueryInformationUser2 (IN SAMPR_HANDLE UserHandle, IN USER_INFORMATION_CLASS UserInformationClass, OUT PSAMPR_USER_INFO_BUFFER *Buffer)
 
NTSTATUS NTAPI SamrQueryDisplayInformation2 (IN SAMPR_HANDLE DomainHandle, IN DOMAIN_DISPLAY_INFORMATION DisplayInformationClass, IN unsigned long Index, IN unsigned long EntryCount, IN unsigned long PreferredMaximumLength, OUT unsigned long *TotalAvailable, OUT unsigned long *TotalReturned, OUT PSAMPR_DISPLAY_INFO_BUFFER Buffer)
 
NTSTATUS NTAPI SamrGetDisplayEnumerationIndex2 (IN SAMPR_HANDLE DomainHandle, IN DOMAIN_DISPLAY_INFORMATION DisplayInformationClass, IN PRPC_UNICODE_STRING Prefix, OUT unsigned long *Index)
 
NTSTATUS NTAPI SamrCreateUser2InDomain (IN SAMPR_HANDLE DomainHandle, IN PRPC_UNICODE_STRING Name, IN unsigned long AccountType, IN ACCESS_MASK DesiredAccess, OUT SAMPR_HANDLE *UserHandle, OUT unsigned long *GrantedAccess, OUT unsigned long *RelativeId)
 
NTSTATUS NTAPI SamrQueryDisplayInformation3 (IN SAMPR_HANDLE DomainHandle, IN DOMAIN_DISPLAY_INFORMATION DisplayInformationClass, IN unsigned long Index, IN unsigned long EntryCount, IN unsigned long PreferredMaximumLength, OUT unsigned long *TotalAvailable, OUT unsigned long *TotalReturned, OUT PSAMPR_DISPLAY_INFO_BUFFER Buffer)
 
NTSTATUS NTAPI SamrAddMultipleMembersToAlias (IN SAMPR_HANDLE AliasHandle, IN PSAMPR_PSID_ARRAY MembersBuffer)
 
NTSTATUS NTAPI SamrRemoveMultipleMembersFromAlias (IN SAMPR_HANDLE AliasHandle, IN PSAMPR_PSID_ARRAY MembersBuffer)
 
NTSTATUS NTAPI SamrOemChangePasswordUser2 (IN handle_t BindingHandle, IN PRPC_STRING ServerName, IN PRPC_STRING UserName, IN PSAMPR_ENCRYPTED_USER_PASSWORD NewPasswordEncryptedWithOldLm, IN PENCRYPTED_LM_OWF_PASSWORD OldLmOwfPasswordEncryptedWithNewLm)
 
NTSTATUS NTAPI SamrUnicodeChangePasswordUser2 (IN handle_t BindingHandle, IN PRPC_UNICODE_STRING ServerName, IN PRPC_UNICODE_STRING UserName, IN PSAMPR_ENCRYPTED_USER_PASSWORD NewPasswordEncryptedWithOldNt, IN PENCRYPTED_NT_OWF_PASSWORD OldNtOwfPasswordEncryptedWithNewNt, IN unsigned char LmPresent, IN PSAMPR_ENCRYPTED_USER_PASSWORD NewPasswordEncryptedWithOldLm, IN PENCRYPTED_LM_OWF_PASSWORD OldLmOwfPasswordEncryptedWithNewNt)
 
NTSTATUS NTAPI SamrGetDomainPasswordInformation (IN handle_t BindingHandle, IN PRPC_UNICODE_STRING Unused, OUT PUSER_DOMAIN_PASSWORD_INFORMATION PasswordInformation)
 
NTSTATUS NTAPI SamrConnect2 (IN PSAMPR_SERVER_NAME ServerName, OUT SAMPR_HANDLE *ServerHandle, IN ACCESS_MASK DesiredAccess)
 
NTSTATUS NTAPI SamrSetInformationUser2 (IN SAMPR_HANDLE UserHandle, IN USER_INFORMATION_CLASS UserInformationClass, IN PSAMPR_USER_INFO_BUFFER Buffer)
 
NTSTATUS NTAPI SamrSetBootKeyInformation (IN handle_t BindingHandle)
 
NTSTATUS NTAPI SamrGetBootKeyInformation (IN handle_t BindingHandle)
 
NTSTATUS NTAPI SamrConnect3 (IN handle_t BindingHandle)
 
NTSTATUS NTAPI SamrConnect4 (IN PSAMPR_SERVER_NAME ServerName, OUT SAMPR_HANDLE *ServerHandle, IN unsigned long ClientRevision, IN ACCESS_MASK DesiredAccess)
 
NTSTATUS NTAPI SamrUnicodeChangePasswordUser3 (IN handle_t BindingHandle)
 
NTSTATUS NTAPI SamrConnect5 (IN PSAMPR_SERVER_NAME ServerName, IN ACCESS_MASK DesiredAccess, IN unsigned long InVersion, IN SAMPR_REVISION_INFO *InRevisionInfo, OUT unsigned long *OutVersion, OUT SAMPR_REVISION_INFO *OutRevisionInfo, OUT SAMPR_HANDLE *ServerHandle)
 
NTSTATUS NTAPI SamrRidToSid (IN SAMPR_HANDLE ObjectHandle, IN unsigned long Rid, OUT PRPC_SID *Sid)
 
NTSTATUS NTAPI SamrSetDSRMPassword (IN handle_t BindingHandle, IN PRPC_UNICODE_STRING Unused, IN unsigned long UserId, IN PENCRYPTED_NT_OWF_PASSWORD EncryptedNtOwfPassword)
 
NTSTATUS NTAPI SamrValidatePassword (IN handle_t Handle, IN PASSWORD_POLICY_VALIDATION_TYPE ValidationType, IN PSAM_VALIDATE_INPUT_ARG InputArg, OUT PSAM_VALIDATE_OUTPUT_ARG *OutputArg)
 

Variables

static SID_IDENTIFIER_AUTHORITY NtSidAuthority = {SECURITY_NT_AUTHORITY}
 
static GENERIC_MAPPING ServerMapping
 
static GENERIC_MAPPING DomainMapping
 
static GENERIC_MAPPING AliasMapping
 
static GENERIC_MAPPING GroupMapping
 
static GENERIC_MAPPING UserMapping
 
PGENERIC_MAPPING pServerMapping = &ServerMapping
 

Function Documentation

◆ midl_user_allocate()

void __RPC_FAR *__RPC_USER midl_user_allocate ( SIZE_T  len)

Definition at line 114 of file samrpc.c.

115{
117}
#define GetProcessHeap()
Definition: compat.h:736
#define HeapAlloc
Definition: compat.h:733
#define HEAP_ZERO_MEMORY
Definition: compat.h:134
GLenum GLsizei len
Definition: glext.h:6722

◆ midl_user_free()

void __RPC_USER midl_user_free ( void __RPC_FAR *  ptr)

Definition at line 120 of file samrpc.c.

121{
123}
#define HeapFree(x, y, z)
Definition: compat.h:735
static PVOID ptr
Definition: dispmode.c:27

◆ SampAddRelativeTimeToTime()

static LARGE_INTEGER SampAddRelativeTimeToTime ( IN LARGE_INTEGER  AbsoluteTime,
IN LARGE_INTEGER  RelativeTime 
)
static

Definition at line 63 of file samrpc.c.

65{
66 LARGE_INTEGER NewTime;
67
68 NewTime.QuadPart = AbsoluteTime.QuadPart - RelativeTime.QuadPart;
69
70 if (NewTime.QuadPart < 0)
71 NewTime.QuadPart = 0;
72
73 return NewTime;
74}
LONGLONG QuadPart
Definition: typedefs.h:114

Referenced by SampQueryUserAll(), and SampQueryUserLogon().

◆ SampGetNumberOfAccounts()

static NTSTATUS SampGetNumberOfAccounts ( PSAM_DB_OBJECT  DomainObject,
LPCWSTR  AccountType,
PULONG  Count 
)
static

Definition at line 964 of file samrpc.c.

967{
968 HANDLE AccountKeyHandle = NULL;
969 HANDLE NamesKeyHandle = NULL;
971
972 *Count = 0;
973
974 Status = SampRegOpenKey(DomainObject->KeyHandle,
975 AccountType,
976 KEY_READ,
977 &AccountKeyHandle);
978 if (!NT_SUCCESS(Status))
979 return Status;
980
981 Status = SampRegOpenKey(AccountKeyHandle,
982 L"Names",
983 KEY_READ,
984 &NamesKeyHandle);
985 if (!NT_SUCCESS(Status))
986 goto done;
987
988 Status = SampRegQueryKeyInfo(NamesKeyHandle,
989 NULL,
990 Count);
991
992done:
993 SampRegCloseKey(&NamesKeyHandle);
994 SampRegCloseKey(&AccountKeyHandle);
995
996 return Status;
997}
LONG NTSTATUS
Definition: precomp.h:26
#define NULL
Definition: types.h:112
#define NT_SUCCESS(StatCode)
Definition: apphelp.c:33
NTSTATUS SampRegCloseKey(IN OUT PHANDLE KeyHandle)
Definition: registry.c:26
NTSTATUS SampRegQueryKeyInfo(IN HANDLE KeyHandle, OUT PULONG SubKeyCount, OUT PULONG ValueCount)
Definition: registry.c:181
NTSTATUS SampRegOpenKey(IN HANDLE ParentKeyHandle, IN LPCWSTR KeyName, IN ACCESS_MASK DesiredAccess, OUT PHANDLE KeyHandle)
Definition: registry.c:158
#define L(x)
Definition: resources.c:13
Status
Definition: gdiplustypes.h:24
#define KEY_READ
Definition: nt_native.h:1026
HANDLE KeyHandle
Definition: samsrv.h:52
USHORT Count
Definition: userreq.cpp:200

Referenced by SampQueryDomainGeneral(), and SampQueryDomainGeneral2().

◆ SampQueryAliasAdminComment()

static NTSTATUS SampQueryAliasAdminComment ( PSAM_DB_OBJECT  AliasObject,
PSAMPR_ALIAS_INFO_BUFFER *  Buffer 
)
static

Definition at line 5006 of file samrpc.c.

5008{
5009 PSAMPR_ALIAS_INFO_BUFFER InfoBuffer = NULL;
5011
5012 *Buffer = NULL;
5013
5014 InfoBuffer = midl_user_allocate(sizeof(SAMPR_ALIAS_INFO_BUFFER));
5015 if (InfoBuffer == NULL)
5017
5019 L"Description",
5020 &InfoBuffer->AdminComment.AdminComment);
5021 if (!NT_SUCCESS(Status))
5022 {
5023 TRACE("Status 0x%08lx\n", Status);
5024 goto done;
5025 }
5026
5027 *Buffer = InfoBuffer;
5028
5029done:
5030 if (!NT_SUCCESS(Status))
5031 {
5032 if (InfoBuffer != NULL)
5033 {
5034 if (InfoBuffer->AdminComment.AdminComment.Buffer != NULL)
5036
5037 midl_user_free(InfoBuffer);
5038 }
5039 }
5040
5041 return Status;
5042}
Definition: bufpool.h:45
NTSTATUS SampGetObjectAttributeString(PSAM_DB_OBJECT DbObject, LPWSTR AttributeName, PRPC_UNICODE_STRING String)
Definition: database.c:531
#define midl_user_free
Definition: rpc.h:41
#define midl_user_allocate
Definition: rpc.h:40
#define TRACE(s)
Definition: solgame.cpp:4
wchar_t * Buffer
Definition: msv1_0.h:24
RPC_UNICODE_STRING AdminComment
Definition: sam.idl:429
#define STATUS_INSUFFICIENT_RESOURCES
Definition: udferr_usr.h:158
SAMPR_ALIAS_ADM_COMMENT_INFORMATION AdminComment
Definition: sam.idl:445

Referenced by SamrQueryInformationAlias().

◆ SampQueryAliasGeneral()

static NTSTATUS SampQueryAliasGeneral ( PSAM_DB_OBJECT  AliasObject,
PSAMPR_ALIAS_INFO_BUFFER *  Buffer 
)
static

Definition at line 4883 of file samrpc.c.

4885{
4886 PSAMPR_ALIAS_INFO_BUFFER InfoBuffer = NULL;
4887 HANDLE MembersKeyHandle = NULL;
4889
4890 *Buffer = NULL;
4891
4892 InfoBuffer = midl_user_allocate(sizeof(SAMPR_ALIAS_INFO_BUFFER));
4893 if (InfoBuffer == NULL)
4895
4897 L"Name",
4898 &InfoBuffer->General.Name);
4899 if (!NT_SUCCESS(Status))
4900 {
4901 TRACE("Status 0x%08lx\n", Status);
4902 goto done;
4903 }
4904
4906 L"Description",
4907 &InfoBuffer->General.AdminComment);
4908 if (!NT_SUCCESS(Status))
4909 {
4910 TRACE("Status 0x%08lx\n", Status);
4911 goto done;
4912 }
4913
4914 /* Open the Members subkey */
4915 Status = SampRegOpenKey(AliasObject->KeyHandle,
4916 L"Members",
4917 KEY_READ,
4918 &MembersKeyHandle);
4919 if (NT_SUCCESS(Status))
4920 {
4921 /* Retrieve the number of members of the alias */
4922 Status = SampRegQueryKeyInfo(MembersKeyHandle,
4923 NULL,
4924 &InfoBuffer->General.MemberCount);
4925 if (!NT_SUCCESS(Status))
4926 {
4927 TRACE("Status 0x%08lx\n", Status);
4928 goto done;
4929 }
4930 }
4932 {
4933 InfoBuffer->General.MemberCount = 0;
4935 }
4936 else
4937 {
4938 TRACE("Status 0x%08lx\n", Status);
4939 goto done;
4940 }
4941
4942 *Buffer = InfoBuffer;
4943
4944done:
4945 SampRegCloseKey(&MembersKeyHandle);
4946
4947 if (!NT_SUCCESS(Status))
4948 {
4949 if (InfoBuffer != NULL)
4950 {
4951 if (InfoBuffer->General.Name.Buffer != NULL)
4952 midl_user_free(InfoBuffer->General.Name.Buffer);
4953
4954 if (InfoBuffer->General.AdminComment.Buffer != NULL)
4956
4957 midl_user_free(InfoBuffer);
4958 }
4959 }
4960
4961 return Status;
4962}
#define STATUS_SUCCESS
Definition: shellext.h:65
RPC_UNICODE_STRING Name
Definition: sam.idl:417
RPC_UNICODE_STRING AdminComment
Definition: sam.idl:419
#define STATUS_OBJECT_NAME_NOT_FOUND
Definition: udferr_usr.h:149
SAMPR_ALIAS_GENERAL_INFORMATION General
Definition: sam.idl:443

Referenced by SamrQueryInformationAlias().

◆ SampQueryAliasName()

static NTSTATUS SampQueryAliasName ( PSAM_DB_OBJECT  AliasObject,
PSAMPR_ALIAS_INFO_BUFFER *  Buffer 
)
static

Definition at line 4966 of file samrpc.c.

4968{
4969 PSAMPR_ALIAS_INFO_BUFFER InfoBuffer = NULL;
4971
4972 *Buffer = NULL;
4973
4974 InfoBuffer = midl_user_allocate(sizeof(SAMPR_ALIAS_INFO_BUFFER));
4975 if (InfoBuffer == NULL)
4977
4979 L"Name",
4980 &InfoBuffer->Name.Name);
4981 if (!NT_SUCCESS(Status))
4982 {
4983 TRACE("Status 0x%08lx\n", Status);
4984 goto done;
4985 }
4986
4987 *Buffer = InfoBuffer;
4988
4989done:
4990 if (!NT_SUCCESS(Status))
4991 {
4992 if (InfoBuffer != NULL)
4993 {
4994 if (InfoBuffer->Name.Name.Buffer != NULL)
4995 midl_user_free(InfoBuffer->Name.Name.Buffer);
4996
4997 midl_user_free(InfoBuffer);
4998 }
4999 }
5000
5001 return Status;
5002}
RPC_UNICODE_STRING Name
Definition: sam.idl:424
SAMPR_ALIAS_NAME_INFORMATION Name
Definition: sam.idl:444

Referenced by SamrQueryInformationAlias().

◆ SampQueryDomainGeneral()

static NTSTATUS SampQueryDomainGeneral ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)
static

Definition at line 1001 of file samrpc.c.

1003{
1004 PSAMPR_DOMAIN_INFO_BUFFER InfoBuffer = NULL;
1005 SAM_DOMAIN_FIXED_DATA FixedData;
1006 ULONG Length = 0;
1008
1009 *Buffer = NULL;
1010
1011 InfoBuffer = midl_user_allocate(sizeof(SAMPR_DOMAIN_INFO_BUFFER));
1012 if (InfoBuffer == NULL)
1014
1015 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
1016 Status = SampGetObjectAttribute(DomainObject,
1017 L"F",
1018 NULL,
1019 (PVOID)&FixedData,
1020 &Length);
1021 if (!NT_SUCCESS(Status))
1022 goto done;
1023
1024 InfoBuffer->General.ForceLogoff.LowPart = FixedData.ForceLogoff.LowPart;
1025 InfoBuffer->General.ForceLogoff.HighPart = FixedData.ForceLogoff.HighPart;
1028 InfoBuffer->General.DomainServerState = FixedData.DomainServerState;
1029 InfoBuffer->General.DomainServerRole = FixedData.DomainServerRole;
1031
1032 /* Get the OemInformation string */
1033 Status = SampGetObjectAttributeString(DomainObject,
1034 L"OemInformation",
1035 &InfoBuffer->General.OemInformation);
1036 if (!NT_SUCCESS(Status))
1037 {
1038 TRACE("Status 0x%08lx\n", Status);
1039 goto done;
1040 }
1041
1042 /* Get the Name string */
1043 Status = SampGetObjectAttributeString(DomainObject,
1044 L"Name",
1045 &InfoBuffer->General.DomainName);
1046 if (!NT_SUCCESS(Status))
1047 {
1048 TRACE("Status 0x%08lx\n", Status);
1049 goto done;
1050 }
1051
1052 /* Get the ReplicaSourceNodeName string */
1053 Status = SampGetObjectAttributeString(DomainObject,
1054 L"ReplicaSourceNodeName",
1055 &InfoBuffer->General.ReplicaSourceNodeName);
1056 if (!NT_SUCCESS(Status))
1057 {
1058 TRACE("Status 0x%08lx\n", Status);
1059 goto done;
1060 }
1061
1062 /* Get the number of Users in the Domain */
1063 Status = SampGetNumberOfAccounts(DomainObject,
1064 L"Users",
1065 &InfoBuffer->General.UserCount);
1066 if (!NT_SUCCESS(Status))
1067 {
1068 TRACE("Status 0x%08lx\n", Status);
1069 goto done;
1070 }
1071
1072 /* Get the number of Groups in the Domain */
1073 Status = SampGetNumberOfAccounts(DomainObject,
1074 L"Groups",
1075 &InfoBuffer->General.GroupCount);
1076 if (!NT_SUCCESS(Status))
1077 {
1078 TRACE("Status 0x%08lx\n", Status);
1079 goto done;
1080 }
1081
1082 /* Get the number of Aliases in the Domain */
1083 Status = SampGetNumberOfAccounts(DomainObject,
1084 L"Aliases",
1085 &InfoBuffer->General.AliasCount);
1086 if (!NT_SUCCESS(Status))
1087 {
1088 TRACE("Status 0x%08lx\n", Status);
1089 goto done;
1090 }
1091
1092 *Buffer = InfoBuffer;
1093
1094done:
1095 if (!NT_SUCCESS(Status))
1096 {
1097 if (InfoBuffer != NULL)
1098 {
1099 if (InfoBuffer->General.OemInformation.Buffer != NULL)
1101
1102 if (InfoBuffer->General.DomainName.Buffer != NULL)
1104
1105 if (InfoBuffer->General.ReplicaSourceNodeName.Buffer != NULL)
1107
1108 midl_user_free(InfoBuffer);
1109 }
1110 }
1111
1112 return Status;
1113}
NTSTATUS SampGetObjectAttribute(PSAM_DB_OBJECT DbObject, LPWSTR AttributeName, PULONG AttributeType, LPVOID AttributeData, PULONG AttributeSize)
Definition: database.c:516
struct _SAM_DOMAIN_FIXED_DATA SAM_DOMAIN_FIXED_DATA
_In_ ULONG _In_ ULONG _In_ ULONG Length
Definition: ntddpcm.h:102
static NTSTATUS SampGetNumberOfAccounts(PSAM_DB_OBJECT DomainObject, LPCWSTR AccountType, PULONG Count)
Definition: samrpc.c:964
unsigned long LowPart
Definition: msv1_0.h:32
RPC_UNICODE_STRING OemInformation
Definition: sam.idl:204
OLD_LARGE_INTEGER ForceLogoff
Definition: sam.idl:203
unsigned long DomainServerRole
Definition: sam.idl:209
unsigned char UasCompatibilityRequired
Definition: sam.idl:210
RPC_UNICODE_STRING ReplicaSourceNodeName
Definition: sam.idl:206
OLD_LARGE_INTEGER DomainModifiedCount
Definition: sam.idl:207
RPC_UNICODE_STRING DomainName
Definition: sam.idl:205
unsigned long DomainServerState
Definition: sam.idl:208
DOMAIN_SERVER_ENABLE_STATE DomainServerState
Definition: samsrv.h:85
DOMAIN_SERVER_ROLE DomainServerRole
Definition: samsrv.h:86
BOOLEAN UasCompatibilityRequired
Definition: samsrv.h:87
LARGE_INTEGER DomainModifiedCount
Definition: samsrv.h:73
LARGE_INTEGER ForceLogoff
Definition: samsrv.h:76
uint32_t ULONG
Definition: typedefs.h:59
ULONG LowPart
Definition: typedefs.h:106
SAMPR_DOMAIN_GENERAL_INFORMATION General
Definition: sam.idl:268

Referenced by SamrQueryInformationDomain2().

◆ SampQueryDomainGeneral2()

static NTSTATUS SampQueryDomainGeneral2 ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)
static

Definition at line 1408 of file samrpc.c.

1410{
1411 PSAMPR_DOMAIN_INFO_BUFFER InfoBuffer = NULL;
1412 SAM_DOMAIN_FIXED_DATA FixedData;
1413 ULONG Length = 0;
1415
1416 *Buffer = NULL;
1417
1418 InfoBuffer = midl_user_allocate(sizeof(SAMPR_DOMAIN_INFO_BUFFER));
1419 if (InfoBuffer == NULL)
1421
1422 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
1423 Status = SampGetObjectAttribute(DomainObject,
1424 L"F",
1425 NULL,
1426 (PVOID)&FixedData,
1427 &Length);
1428 if (!NT_SUCCESS(Status))
1429 goto done;
1430
1431 InfoBuffer->General2.I1.ForceLogoff.LowPart = FixedData.ForceLogoff.LowPart;
1432 InfoBuffer->General2.I1.ForceLogoff.HighPart = FixedData.ForceLogoff.HighPart;
1435 InfoBuffer->General2.I1.DomainServerState = FixedData.DomainServerState;
1436 InfoBuffer->General2.I1.DomainServerRole = FixedData.DomainServerRole;
1438
1439 InfoBuffer->General2.LockoutDuration = FixedData.LockoutDuration;
1441 InfoBuffer->General2.LockoutThreshold = FixedData.LockoutThreshold;
1442
1443 /* Get the OemInformation string */
1444 Status = SampGetObjectAttributeString(DomainObject,
1445 L"OemInformation",
1446 &InfoBuffer->General2.I1.OemInformation);
1447 if (!NT_SUCCESS(Status))
1448 {
1449 TRACE("Status 0x%08lx\n", Status);
1450 goto done;
1451 }
1452
1453 /* Get the Name string */
1454 Status = SampGetObjectAttributeString(DomainObject,
1455 L"Name",
1456 &InfoBuffer->General2.I1.DomainName);
1457 if (!NT_SUCCESS(Status))
1458 {
1459 TRACE("Status 0x%08lx\n", Status);
1460 goto done;
1461 }
1462
1463 /* Get the ReplicaSourceNodeName string */
1464 Status = SampGetObjectAttributeString(DomainObject,
1465 L"ReplicaSourceNodeName",
1466 &InfoBuffer->General2.I1.ReplicaSourceNodeName);
1467 if (!NT_SUCCESS(Status))
1468 {
1469 TRACE("Status 0x%08lx\n", Status);
1470 goto done;
1471 }
1472
1473 /* Get the number of Users in the Domain */
1474 Status = SampGetNumberOfAccounts(DomainObject,
1475 L"Users",
1476 &InfoBuffer->General2.I1.UserCount);
1477 if (!NT_SUCCESS(Status))
1478 {
1479 TRACE("Status 0x%08lx\n", Status);
1480 goto done;
1481 }
1482
1483 /* Get the number of Groups in the Domain */
1484 Status = SampGetNumberOfAccounts(DomainObject,
1485 L"Groups",
1486 &InfoBuffer->General2.I1.GroupCount);
1487 if (!NT_SUCCESS(Status))
1488 {
1489 TRACE("Status 0x%08lx\n", Status);
1490 goto done;
1491 }
1492
1493 /* Get the number of Aliases in the Domain */
1494 Status = SampGetNumberOfAccounts(DomainObject,
1495 L"Aliases",
1496 &InfoBuffer->General2.I1.AliasCount);
1497 if (!NT_SUCCESS(Status))
1498 {
1499 TRACE("Status 0x%08lx\n", Status);
1500 goto done;
1501 }
1502
1503 *Buffer = InfoBuffer;
1504
1505done:
1506 if (!NT_SUCCESS(Status))
1507 {
1508 if (InfoBuffer != NULL)
1509 {
1510 if (InfoBuffer->General2.I1.OemInformation.Buffer != NULL)
1512
1513 if (InfoBuffer->General2.I1.DomainName.Buffer != NULL)
1515
1516 if (InfoBuffer->General2.I1.ReplicaSourceNodeName.Buffer != NULL)
1518
1519 midl_user_free(InfoBuffer);
1520 }
1521 }
1522
1523 return Status;
1524}
LARGE_INTEGER LockoutObservationWindow
Definition: sam.idl:220
SAMPR_DOMAIN_GENERAL_INFORMATION I1
Definition: sam.idl:218
unsigned short LockoutThreshold
Definition: sam.idl:221
LARGE_INTEGER LockoutObservationWindow
Definition: samsrv.h:78
LARGE_INTEGER LockoutDuration
Definition: samsrv.h:77
USHORT LockoutThreshold
Definition: samsrv.h:84
SAMPR_DOMAIN_GENERAL_INFORMATION2 General2
Definition: sam.idl:276

Referenced by SamrQueryInformationDomain2().

◆ SampQueryDomainLockout()

static NTSTATUS SampQueryDomainLockout ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)
static

Definition at line 1528 of file samrpc.c.

1530{
1531 PSAMPR_DOMAIN_INFO_BUFFER InfoBuffer = NULL;
1532 SAM_DOMAIN_FIXED_DATA FixedData;
1533 ULONG Length = 0;
1535
1536 *Buffer = NULL;
1537
1538 InfoBuffer = midl_user_allocate(sizeof(SAMPR_DOMAIN_INFO_BUFFER));
1539 if (InfoBuffer == NULL)
1541
1542 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
1543 Status = SampGetObjectAttribute(DomainObject,
1544 L"F",
1545 NULL,
1546 (PVOID)&FixedData,
1547 &Length);
1548 if (!NT_SUCCESS(Status))
1549 goto done;
1550
1551 InfoBuffer->Lockout.LockoutDuration = FixedData.LockoutDuration;
1553 InfoBuffer->Lockout.LockoutThreshold = FixedData.LockoutThreshold;
1554
1555 *Buffer = InfoBuffer;
1556
1557done:
1558 if (!NT_SUCCESS(Status))
1559 {
1560 if (InfoBuffer != NULL)
1561 {
1562 midl_user_free(InfoBuffer);
1563 }
1564 }
1565
1566 return Status;
1567}
LARGE_INTEGER LockoutDuration
Definition: sam.idl:242
unsigned short LockoutThreshold
Definition: sam.idl:244
LARGE_INTEGER LockoutObservationWindow
Definition: sam.idl:243
SAMPR_DOMAIN_LOCKOUT_INFORMATION Lockout
Definition: sam.idl:277

Referenced by SamrQueryInformationDomain2().

◆ SampQueryDomainLogoff()

static NTSTATUS SampQueryDomainLogoff ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)
static

Definition at line 1117 of file samrpc.c.

1119{
1120 PSAMPR_DOMAIN_INFO_BUFFER InfoBuffer = NULL;
1121 SAM_DOMAIN_FIXED_DATA FixedData;
1122 ULONG Length = 0;
1124
1125 *Buffer = NULL;
1126
1127 InfoBuffer = midl_user_allocate(sizeof(SAMPR_DOMAIN_INFO_BUFFER));
1128 if (InfoBuffer == NULL)
1130
1131 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
1132 Status = SampGetObjectAttribute(DomainObject,
1133 L"F",
1134 NULL,
1135 (PVOID)&FixedData,
1136 &Length);
1137 if (!NT_SUCCESS(Status))
1138 goto done;
1139
1140 InfoBuffer->Logoff.ForceLogoff.LowPart = FixedData.ForceLogoff.LowPart;
1141 InfoBuffer->Logoff.ForceLogoff.HighPart = FixedData.ForceLogoff.HighPart;
1142
1143 *Buffer = InfoBuffer;
1144
1145done:
1146 if (!NT_SUCCESS(Status))
1147 {
1148 if (InfoBuffer != NULL)
1149 {
1150 midl_user_free(InfoBuffer);
1151 }
1152 }
1153
1154 return Status;
1155}
LARGE_INTEGER ForceLogoff
Definition: ntsam.h:399
DOMAIN_LOGOFF_INFORMATION Logoff
Definition: sam.idl:269

Referenced by SamrQueryInformationDomain2().

◆ SampQueryDomainModified()

static NTSTATUS SampQueryDomainModified ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)
static

Definition at line 1323 of file samrpc.c.

1325{
1326 PSAMPR_DOMAIN_INFO_BUFFER InfoBuffer = NULL;
1327 SAM_DOMAIN_FIXED_DATA FixedData;
1328 ULONG Length = 0;
1330
1331 *Buffer = NULL;
1332
1333 InfoBuffer = midl_user_allocate(sizeof(SAMPR_DOMAIN_INFO_BUFFER));
1334 if (InfoBuffer == NULL)
1336
1337 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
1338 Status = SampGetObjectAttribute(DomainObject,
1339 L"F",
1340 NULL,
1341 (PVOID)&FixedData,
1342 &Length);
1343 if (!NT_SUCCESS(Status))
1344 goto done;
1345
1348 InfoBuffer->Modified.CreationTime.LowPart = FixedData.CreationTime.LowPart;
1349 InfoBuffer->Modified.CreationTime.HighPart = FixedData.CreationTime.HighPart;
1350
1351 *Buffer = InfoBuffer;
1352
1353done:
1354 if (!NT_SUCCESS(Status))
1355 {
1356 if (InfoBuffer != NULL)
1357 {
1358 midl_user_free(InfoBuffer);
1359 }
1360 }
1361
1362 return Status;
1363}
LARGE_INTEGER DomainModifiedCount
Definition: ntsam.h:424
LARGE_INTEGER CreationTime
Definition: ntsam.h:425
LARGE_INTEGER CreationTime
Definition: samsrv.h:72
DOMAIN_MODIFIED_INFORMATION Modified
Definition: sam.idl:274

Referenced by SamrQueryInformationDomain2().

◆ SampQueryDomainModified2()

static NTSTATUS SampQueryDomainModified2 ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)
static

Definition at line 1571 of file samrpc.c.

1573{
1574 PSAMPR_DOMAIN_INFO_BUFFER InfoBuffer = NULL;
1575 SAM_DOMAIN_FIXED_DATA FixedData;
1576 ULONG Length = 0;
1578
1579 *Buffer = NULL;
1580
1581 InfoBuffer = midl_user_allocate(sizeof(SAMPR_DOMAIN_INFO_BUFFER));
1582 if (InfoBuffer == NULL)
1584
1585 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
1586 Status = SampGetObjectAttribute(DomainObject,
1587 L"F",
1588 NULL,
1589 (PVOID)&FixedData,
1590 &Length);
1591 if (!NT_SUCCESS(Status))
1592 goto done;
1593
1596 InfoBuffer->Modified2.CreationTime.LowPart = FixedData.CreationTime.LowPart;
1597 InfoBuffer->Modified2.CreationTime.HighPart = FixedData.CreationTime.HighPart;
1600
1601 *Buffer = InfoBuffer;
1602
1603done:
1604 if (!NT_SUCCESS(Status))
1605 {
1606 if (InfoBuffer != NULL)
1607 {
1608 midl_user_free(InfoBuffer);
1609 }
1610 }
1611
1612 return Status;
1613}
LARGE_INTEGER DomainModifiedCount
Definition: ntsam.h:457
LARGE_INTEGER ModifiedCountAtLastPromotion
Definition: ntsam.h:459
LARGE_INTEGER CreationTime
Definition: ntsam.h:458
LARGE_INTEGER ModifiedCountAtLastPromotion
Definition: samsrv.h:79
DOMAIN_MODIFIED_INFORMATION2 Modified2
Definition: sam.idl:278

Referenced by SamrQueryInformationDomain2().

◆ SampQueryDomainName()

static NTSTATUS SampQueryDomainName ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)
static

Definition at line 1200 of file samrpc.c.

1202{
1203 PSAMPR_DOMAIN_INFO_BUFFER InfoBuffer = NULL;
1205
1206 *Buffer = NULL;
1207
1208 InfoBuffer = midl_user_allocate(sizeof(SAMPR_DOMAIN_INFO_BUFFER));
1209 if (InfoBuffer == NULL)
1211
1212 /* Get the Name string */
1213 Status = SampGetObjectAttributeString(DomainObject,
1214 L"Name",
1215 &InfoBuffer->Name.DomainName);
1216 if (!NT_SUCCESS(Status))
1217 {
1218 TRACE("Status 0x%08lx\n", Status);
1219 goto done;
1220 }
1221
1222 *Buffer = InfoBuffer;
1223
1224done:
1225 if (!NT_SUCCESS(Status))
1226 {
1227 if (InfoBuffer != NULL)
1228 {
1229 if (InfoBuffer->Name.DomainName.Buffer != NULL)
1230 midl_user_free(InfoBuffer->Name.DomainName.Buffer);
1231
1232 midl_user_free(InfoBuffer);
1233 }
1234 }
1235
1236 return Status;
1237}
RPC_UNICODE_STRING DomainName
Definition: sam.idl:232
SAMPR_DOMAIN_NAME_INFORMATION Name
Definition: sam.idl:271

Referenced by SamrQueryInformationDomain2().

◆ SampQueryDomainOem()

static NTSTATUS SampQueryDomainOem ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)
static

Definition at line 1159 of file samrpc.c.

1161{
1162 PSAMPR_DOMAIN_INFO_BUFFER InfoBuffer = NULL;
1164
1165 *Buffer = NULL;
1166
1167 InfoBuffer = midl_user_allocate(sizeof(SAMPR_DOMAIN_INFO_BUFFER));
1168 if (InfoBuffer == NULL)
1170
1171 /* Get the OemInformation string */
1172 Status = SampGetObjectAttributeString(DomainObject,
1173 L"OemInformation",
1174 &InfoBuffer->Oem.OemInformation);
1175 if (!NT_SUCCESS(Status))
1176 {
1177 TRACE("Status 0x%08lx\n", Status);
1178 goto done;
1179 }
1180
1181 *Buffer = InfoBuffer;
1182
1183done:
1184 if (!NT_SUCCESS(Status))
1185 {
1186 if (InfoBuffer != NULL)
1187 {
1188 if (InfoBuffer->Oem.OemInformation.Buffer != NULL)
1190
1191 midl_user_free(InfoBuffer);
1192 }
1193 }
1194
1195 return Status;
1196}
RPC_UNICODE_STRING OemInformation
Definition: sam.idl:227
SAMPR_DOMAIN_OEM_INFORMATION Oem
Definition: sam.idl:270

Referenced by SamrQueryInformationDomain2().

◆ SampQueryDomainPassword()

static NTSTATUS SampQueryDomainPassword ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)
static

Definition at line 917 of file samrpc.c.

919{
920 PSAMPR_DOMAIN_INFO_BUFFER InfoBuffer = NULL;
921 SAM_DOMAIN_FIXED_DATA FixedData;
922 ULONG Length = 0;
924
925 *Buffer = NULL;
926
927 InfoBuffer = midl_user_allocate(sizeof(SAMPR_DOMAIN_INFO_BUFFER));
928 if (InfoBuffer == NULL)
930
932 Status = SampGetObjectAttribute(DomainObject,
933 L"F",
934 NULL,
935 (PVOID)&FixedData,
936 &Length);
937 if (!NT_SUCCESS(Status))
938 goto done;
939
940 InfoBuffer->Password.MinPasswordLength = FixedData.MinPasswordLength;
942 InfoBuffer->Password.PasswordProperties = FixedData.PasswordProperties;
943 InfoBuffer->Password.MaxPasswordAge.LowPart = FixedData.MaxPasswordAge.LowPart;
945 InfoBuffer->Password.MinPasswordAge.LowPart = FixedData.MinPasswordAge.LowPart;
947
948 *Buffer = InfoBuffer;
949
950done:
951 if (!NT_SUCCESS(Status))
952 {
953 if (InfoBuffer != NULL)
954 {
955 midl_user_free(InfoBuffer);
956 }
957 }
958
959 return Status;
960}
LARGE_INTEGER MinPasswordAge
Definition: ntsam.h:376
LARGE_INTEGER MaxPasswordAge
Definition: ntsam.h:375
USHORT PasswordHistoryLength
Definition: samsrv.h:83
LARGE_INTEGER MaxPasswordAge
Definition: samsrv.h:74
USHORT MinPasswordLength
Definition: samsrv.h:82
LARGE_INTEGER MinPasswordAge
Definition: samsrv.h:75
ULONG PasswordProperties
Definition: samsrv.h:81
DOMAIN_PASSWORD_INFORMATION Password
Definition: sam.idl:267

Referenced by SamrQueryInformationDomain2().

◆ SampQueryDomainReplication()

static NTSTATUS SampQueryDomainReplication ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)
static

Definition at line 1241 of file samrpc.c.

1243{
1244 PSAMPR_DOMAIN_INFO_BUFFER InfoBuffer = NULL;
1246
1247 *Buffer = NULL;
1248
1249 InfoBuffer = midl_user_allocate(sizeof(SAMPR_DOMAIN_INFO_BUFFER));
1250 if (InfoBuffer == NULL)
1252
1253 /* Get the ReplicaSourceNodeName string */
1254 Status = SampGetObjectAttributeString(DomainObject,
1255 L"ReplicaSourceNodeName",
1256 &InfoBuffer->Replication.ReplicaSourceNodeName);
1257 if (!NT_SUCCESS(Status))
1258 {
1259 TRACE("Status 0x%08lx\n", Status);
1260 goto done;
1261 }
1262
1263 *Buffer = InfoBuffer;
1264
1265done:
1266 if (!NT_SUCCESS(Status))
1267 {
1268 if (InfoBuffer != NULL)
1269 {
1270 if (InfoBuffer->Replication.ReplicaSourceNodeName.Buffer != NULL)
1272
1273 midl_user_free(InfoBuffer);
1274 }
1275 }
1276
1277 return Status;
1278}
RPC_UNICODE_STRING ReplicaSourceNodeName
Definition: sam.idl:237
SAMPR_DOMAIN_REPLICATION_INFORMATION Replication
Definition: sam.idl:273

Referenced by SamrQueryInformationDomain2().

◆ SampQueryDomainServerRole()

static NTSTATUS SampQueryDomainServerRole ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)
static

Definition at line 1282 of file samrpc.c.

1284{
1285 PSAMPR_DOMAIN_INFO_BUFFER InfoBuffer = NULL;
1286 SAM_DOMAIN_FIXED_DATA FixedData;
1287 ULONG Length = 0;
1289
1290 *Buffer = NULL;
1291
1292 InfoBuffer = midl_user_allocate(sizeof(SAMPR_DOMAIN_INFO_BUFFER));
1293 if (InfoBuffer == NULL)
1295
1296 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
1297 Status = SampGetObjectAttribute(DomainObject,
1298 L"F",
1299 NULL,
1300 (PVOID)&FixedData,
1301 &Length);
1302 if (!NT_SUCCESS(Status))
1303 goto done;
1304
1305 InfoBuffer->Role.DomainServerRole = FixedData.DomainServerRole;
1306
1307 *Buffer = InfoBuffer;
1308
1309done:
1310 if (!NT_SUCCESS(Status))
1311 {
1312 if (InfoBuffer != NULL)
1313 {
1314 midl_user_free(InfoBuffer);
1315 }
1316 }
1317
1318 return Status;
1319}
DOMAIN_SERVER_ROLE DomainServerRole
Definition: ntsam.h:419
DOMAIN_SERVER_ROLE_INFORMATION Role
Definition: sam.idl:272

Referenced by SamrQueryInformationDomain2().

◆ SampQueryDomainState()

static NTSTATUS SampQueryDomainState ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)
static

Definition at line 1367 of file samrpc.c.

1369{
1370 PSAMPR_DOMAIN_INFO_BUFFER InfoBuffer = NULL;
1371 SAM_DOMAIN_FIXED_DATA FixedData;
1372 ULONG Length = 0;
1374
1375 *Buffer = NULL;
1376
1377 InfoBuffer = midl_user_allocate(sizeof(SAMPR_DOMAIN_INFO_BUFFER));
1378 if (InfoBuffer == NULL)
1380
1381 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
1382 Status = SampGetObjectAttribute(DomainObject,
1383 L"F",
1384 NULL,
1385 (PVOID)&FixedData,
1386 &Length);
1387 if (!NT_SUCCESS(Status))
1388 goto done;
1389
1390 InfoBuffer->State.DomainServerState = FixedData.DomainServerState;
1391
1392 *Buffer = InfoBuffer;
1393
1394done:
1395 if (!NT_SUCCESS(Status))
1396 {
1397 if (InfoBuffer != NULL)
1398 {
1399 midl_user_free(InfoBuffer);
1400 }
1401 }
1402
1403 return Status;
1404}
DOMAIN_SERVER_ENABLE_STATE DomainServerState
Definition: ntsam.h:430
DOMAIN_STATE_INFORMATION State
Definition: sam.idl:275

Referenced by SamrQueryInformationDomain2().

◆ SampQueryGroupAdminComment()

static NTSTATUS SampQueryGroupAdminComment ( PSAM_DB_OBJECT  GroupObject,
PSAMPR_GROUP_INFO_BUFFER *  Buffer 
)
static

Definition at line 4214 of file samrpc.c.

4216{
4217 PSAMPR_GROUP_INFO_BUFFER InfoBuffer = NULL;
4219
4220 *Buffer = NULL;
4221
4222 InfoBuffer = midl_user_allocate(sizeof(SAMPR_GROUP_INFO_BUFFER));
4223 if (InfoBuffer == NULL)
4225
4227 L"AdminComment",
4228 &InfoBuffer->AdminComment.AdminComment);
4229 if (!NT_SUCCESS(Status))
4230 {
4231 TRACE("Status 0x%08lx\n", Status);
4232 goto done;
4233 }
4234
4235 *Buffer = InfoBuffer;
4236
4237done:
4238 if (!NT_SUCCESS(Status))
4239 {
4240 if (InfoBuffer != NULL)
4241 {
4242 if (InfoBuffer->AdminComment.AdminComment.Buffer != NULL)
4244
4245 midl_user_free(InfoBuffer);
4246 }
4247 }
4248
4249 return Status;
4250}
RPC_UNICODE_STRING AdminComment
Definition: sam.idl:392
SAMPR_GROUP_ADM_COMMENT_INFORMATION AdminComment
Definition: sam.idl:411

Referenced by SamrQueryInformationGroup().

◆ SampQueryGroupAttribute()

static NTSTATUS SampQueryGroupAttribute ( PSAM_DB_OBJECT  GroupObject,
PSAMPR_GROUP_INFO_BUFFER *  Buffer 
)
static

Definition at line 4170 of file samrpc.c.

4172{
4173 PSAMPR_GROUP_INFO_BUFFER InfoBuffer = NULL;
4174 SAM_GROUP_FIXED_DATA FixedData;
4175 ULONG Length = 0;
4177
4178 *Buffer = NULL;
4179
4180 InfoBuffer = midl_user_allocate(sizeof(SAMPR_GROUP_INFO_BUFFER));
4181 if (InfoBuffer == NULL)
4183
4184 Length = sizeof(SAM_GROUP_FIXED_DATA);
4185 Status = SampGetObjectAttribute(GroupObject,
4186 L"F",
4187 NULL,
4188 (PVOID)&FixedData,
4189 &Length);
4190 if (!NT_SUCCESS(Status))
4191 {
4192 TRACE("Status 0x%08lx\n", Status);
4193 goto done;
4194 }
4195
4196 InfoBuffer->Attribute.Attributes = FixedData.Attributes;
4197
4198 *Buffer = InfoBuffer;
4199
4200done:
4201 if (!NT_SUCCESS(Status))
4202 {
4203 if (InfoBuffer != NULL)
4204 {
4205 midl_user_free(InfoBuffer);
4206 }
4207 }
4208
4209 return Status;
4210}
struct _SAM_GROUP_FIXED_DATA SAM_GROUP_FIXED_DATA
SAMPR_GROUP_ATTRIBUTE_INFORMATION Attribute
Definition: sam.idl:410

Referenced by SamrQueryInformationGroup().

◆ SampQueryGroupGeneral()

static NTSTATUS SampQueryGroupGeneral ( PSAM_DB_OBJECT  GroupObject,
PSAMPR_GROUP_INFO_BUFFER *  Buffer 
)
static

Definition at line 4040 of file samrpc.c.

4042{
4043 PSAMPR_GROUP_INFO_BUFFER InfoBuffer = NULL;
4044 SAM_GROUP_FIXED_DATA FixedData;
4045 ULONG MembersLength = 0;
4046 ULONG Length = 0;
4048
4049 *Buffer = NULL;
4050
4051 InfoBuffer = midl_user_allocate(sizeof(SAMPR_GROUP_INFO_BUFFER));
4052 if (InfoBuffer == NULL)
4054
4056 L"Name",
4057 &InfoBuffer->General.Name);
4058 if (!NT_SUCCESS(Status))
4059 {
4060 TRACE("Status 0x%08lx\n", Status);
4061 goto done;
4062 }
4063
4065 L"AdminComment",
4066 &InfoBuffer->General.AdminComment);
4067 if (!NT_SUCCESS(Status))
4068 {
4069 TRACE("Status 0x%08lx\n", Status);
4070 goto done;
4071 }
4072
4073 Length = sizeof(SAM_GROUP_FIXED_DATA);
4074 Status = SampGetObjectAttribute(GroupObject,
4075 L"F",
4076 NULL,
4077 (PVOID)&FixedData,
4078 &Length);
4079 if (!NT_SUCCESS(Status))
4080 {
4081 TRACE("Status 0x%08lx\n", Status);
4082 goto done;
4083 }
4084
4085 InfoBuffer->General.Attributes = FixedData.Attributes;
4086
4087 Status = SampGetObjectAttribute(GroupObject,
4088 L"Members",
4089 NULL,
4090 NULL,
4091 &MembersLength);
4093 {
4094 TRACE("Status 0x%08lx\n", Status);
4095 goto done;
4096 }
4097
4099 {
4100 InfoBuffer->General.MemberCount = 0;
4102 }
4103 else
4104 {
4105 InfoBuffer->General.MemberCount = MembersLength / sizeof(ULONG);
4106 }
4107
4108 *Buffer = InfoBuffer;
4109
4110done:
4111 if (!NT_SUCCESS(Status))
4112 {
4113 if (InfoBuffer != NULL)
4114 {
4115 if (InfoBuffer->General.Name.Buffer != NULL)
4116 midl_user_free(InfoBuffer->General.Name.Buffer);
4117
4118 if (InfoBuffer->General.AdminComment.Buffer != NULL)
4120
4121 midl_user_free(InfoBuffer);
4122 }
4123 }
4124
4125 return Status;
4126}
RPC_UNICODE_STRING Name
Definition: sam.idl:379
RPC_UNICODE_STRING AdminComment
Definition: sam.idl:382
SAMPR_GROUP_GENERAL_INFORMATION General
Definition: sam.idl:408

Referenced by SamrQueryInformationGroup().

◆ SampQueryGroupName()

static NTSTATUS SampQueryGroupName ( PSAM_DB_OBJECT  GroupObject,
PSAMPR_GROUP_INFO_BUFFER *  Buffer 
)
static

Definition at line 4130 of file samrpc.c.

4132{
4133 PSAMPR_GROUP_INFO_BUFFER InfoBuffer = NULL;
4135
4136 *Buffer = NULL;
4137
4138 InfoBuffer = midl_user_allocate(sizeof(SAMPR_GROUP_INFO_BUFFER));
4139 if (InfoBuffer == NULL)
4141
4143 L"Name",
4144 &InfoBuffer->Name.Name);
4145 if (!NT_SUCCESS(Status))
4146 {
4147 TRACE("Status 0x%08lx\n", Status);
4148 goto done;
4149 }
4150
4151 *Buffer = InfoBuffer;
4152
4153done:
4154 if (!NT_SUCCESS(Status))
4155 {
4156 if (InfoBuffer != NULL)
4157 {
4158 if (InfoBuffer->Name.Name.Buffer != NULL)
4159 midl_user_free(InfoBuffer->Name.Name.Buffer);
4160
4161 midl_user_free(InfoBuffer);
4162 }
4163 }
4164
4165 return Status;
4166}
RPC_UNICODE_STRING Name
Definition: sam.idl:387
SAMPR_GROUP_NAME_INFORMATION Name
Definition: sam.idl:409

Referenced by SamrQueryInformationGroup().

◆ SampQueryUserAccount()

static NTSTATUS SampQueryUserAccount ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 5880 of file samrpc.c.

5882{
5883 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
5884 SAM_USER_FIXED_DATA FixedData;
5885 ULONG Length = 0;
5887
5888 *Buffer = NULL;
5889
5890 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
5891 if (InfoBuffer == NULL)
5893
5894 Length = sizeof(SAM_USER_FIXED_DATA);
5895 Status = SampGetObjectAttribute(UserObject,
5896 L"F",
5897 NULL,
5898 (PVOID)&FixedData,
5899 &Length);
5900 if (!NT_SUCCESS(Status))
5901 goto done;
5902
5903 InfoBuffer->Account.UserId = FixedData.UserId;
5904 InfoBuffer->Account.PrimaryGroupId = FixedData.PrimaryGroupId;
5905 InfoBuffer->Account.LastLogon.LowPart = FixedData.LastLogon.LowPart;
5906 InfoBuffer->Account.LastLogon.HighPart = FixedData.LastLogon.HighPart;
5907 InfoBuffer->Account.LastLogoff.LowPart = FixedData.LastLogoff.LowPart;
5908 InfoBuffer->Account.LastLogoff.HighPart = FixedData.LastLogoff.HighPart;
5909 InfoBuffer->Account.PasswordLastSet.LowPart = FixedData.PasswordLastSet.LowPart;
5911 InfoBuffer->Account.AccountExpires.LowPart = FixedData.AccountExpires.LowPart;
5912 InfoBuffer->Account.AccountExpires.HighPart = FixedData.AccountExpires.HighPart;
5913 InfoBuffer->Account.BadPasswordCount = FixedData.BadPasswordCount;
5914 InfoBuffer->Account.LogonCount = FixedData.LogonCount;
5915 InfoBuffer->Account.UserAccountControl = FixedData.UserAccountControl;
5916
5917 /* Get the Name string */
5919 L"Name",
5920 &InfoBuffer->Account.UserName);
5921 if (!NT_SUCCESS(Status))
5922 {
5923 TRACE("Status 0x%08lx\n", Status);
5924 goto done;
5925 }
5926
5927 /* Get the FullName string */
5929 L"FullName",
5930 &InfoBuffer->Account.FullName);
5931 if (!NT_SUCCESS(Status))
5932 {
5933 TRACE("Status 0x%08lx\n", Status);
5934 goto done;
5935 }
5936
5937 /* Get the HomeDirectory string */
5939 L"HomeDirectory",
5940 &InfoBuffer->Account.HomeDirectory);
5941 if (!NT_SUCCESS(Status))
5942 {
5943 TRACE("Status 0x%08lx\n", Status);
5944 goto done;
5945 }
5946
5947 /* Get the HomeDirectoryDrive string */
5949 L"HomeDirectoryDrive",
5950 &InfoBuffer->Account.HomeDirectoryDrive);
5951 if (!NT_SUCCESS(Status))
5952 {
5953 TRACE("Status 0x%08lx\n", Status);
5954 goto done;
5955 }
5956
5957 /* Get the ScriptPath string */
5959 L"ScriptPath",
5960 &InfoBuffer->Account.ScriptPath);
5961 if (!NT_SUCCESS(Status))
5962 {
5963 TRACE("Status 0x%08lx\n", Status);
5964 goto done;
5965 }
5966
5967 /* Get the ProfilePath string */
5969 L"ProfilePath",
5970 &InfoBuffer->Account.ProfilePath);
5971 if (!NT_SUCCESS(Status))
5972 {
5973 TRACE("Status 0x%08lx\n", Status);
5974 goto done;
5975 }
5976
5977 /* Get the AdminComment string */
5979 L"AdminComment",
5980 &InfoBuffer->Account.AdminComment);
5981 if (!NT_SUCCESS(Status))
5982 {
5983 TRACE("Status 0x%08lx\n", Status);
5984 goto done;
5985 }
5986
5987 /* Get the WorkStations string */
5989 L"WorkStations",
5990 &InfoBuffer->Account.WorkStations);
5991 if (!NT_SUCCESS(Status))
5992 {
5993 TRACE("Status 0x%08lx\n", Status);
5994 goto done;
5995 }
5996
5997 /* Get the LogonHours attribute */
5999 &InfoBuffer->Account.LogonHours);
6000 if (!NT_SUCCESS(Status))
6001 {
6002 TRACE("Status 0x%08lx\n", Status);
6003 goto done;
6004 }
6005
6006 *Buffer = InfoBuffer;
6007
6008done:
6009 if (!NT_SUCCESS(Status))
6010 {
6011 if (InfoBuffer != NULL)
6012 {
6013 if (InfoBuffer->Account.UserName.Buffer != NULL)
6015
6016 if (InfoBuffer->Account.FullName.Buffer != NULL)
6018
6019 if (InfoBuffer->Account.HomeDirectory.Buffer != NULL)
6021
6022 if (InfoBuffer->Account.HomeDirectoryDrive.Buffer != NULL)
6024
6025 if (InfoBuffer->Account.ScriptPath.Buffer != NULL)
6027
6028 if (InfoBuffer->Account.ProfilePath.Buffer != NULL)
6030
6031 if (InfoBuffer->Account.AdminComment.Buffer != NULL)
6033
6034 if (InfoBuffer->Account.WorkStations.Buffer != NULL)
6036
6037 if (InfoBuffer->Account.LogonHours.LogonHours != NULL)
6039
6040 midl_user_free(InfoBuffer);
6041 }
6042 }
6043
6044 return Status;
6045}
NTSTATUS SampGetLogonHoursAttribute(IN PSAM_DB_OBJECT UserObject, IN OUT PSAMPR_LOGON_HOURS LogonHours)
Definition: user.c:810
struct _SAM_USER_FIXED_DATA SAM_USER_FIXED_DATA
unsigned char * LogonHours
Definition: msv1_0.h:63
RPC_UNICODE_STRING FullName
Definition: sam.idl:565
SAMPR_LOGON_HOURS LogonHours
Definition: sam.idl:576
OLD_LARGE_INTEGER LastLogoff
Definition: sam.idl:575
RPC_UNICODE_STRING HomeDirectoryDrive
Definition: sam.idl:569
RPC_UNICODE_STRING ScriptPath
Definition: sam.idl:570
unsigned long UserAccountControl
Definition: sam.idl:581
OLD_LARGE_INTEGER PasswordLastSet
Definition: sam.idl:579
unsigned short BadPasswordCount
Definition: sam.idl:577
RPC_UNICODE_STRING ProfilePath
Definition: sam.idl:571
RPC_UNICODE_STRING HomeDirectory
Definition: sam.idl:568
RPC_UNICODE_STRING AdminComment
Definition: sam.idl:572
OLD_LARGE_INTEGER AccountExpires
Definition: sam.idl:580
RPC_UNICODE_STRING UserName
Definition: sam.idl:564
unsigned short LogonCount
Definition: sam.idl:578
unsigned long PrimaryGroupId
Definition: sam.idl:567
RPC_UNICODE_STRING WorkStations
Definition: sam.idl:573
OLD_LARGE_INTEGER LastLogon
Definition: sam.idl:574
LARGE_INTEGER AccountExpires
Definition: samsrv.h:105
ULONG UserAccountControl
Definition: samsrv.h:109
LARGE_INTEGER LastLogon
Definition: samsrv.h:102
ULONG PrimaryGroupId
Definition: samsrv.h:108
LARGE_INTEGER PasswordLastSet
Definition: samsrv.h:104
USHORT BadPasswordCount
Definition: samsrv.h:112
LARGE_INTEGER LastLogoff
Definition: samsrv.h:103
SAMPR_USER_ACCOUNT_INFORMATION Account
Definition: sam.idl:725

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserAccountName()

static NTSTATUS SampQueryUserAccountName ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6149 of file samrpc.c.

6151{
6152 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6154
6155 *Buffer = NULL;
6156
6157 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6158 if (InfoBuffer == NULL)
6160
6161 /* Get the Name string */
6163 L"Name",
6164 &InfoBuffer->AccountName.UserName);
6165 if (!NT_SUCCESS(Status))
6166 {
6167 TRACE("Status 0x%08lx\n", Status);
6168 goto done;
6169 }
6170
6171 *Buffer = InfoBuffer;
6172
6173done:
6174 if (!NT_SUCCESS(Status))
6175 {
6176 if (InfoBuffer != NULL)
6177 {
6178 if (InfoBuffer->AccountName.UserName.Buffer != NULL)
6180
6181 midl_user_free(InfoBuffer);
6182 }
6183 }
6184
6185 return Status;
6186}
RPC_UNICODE_STRING UserName
Definition: sam.idl:586
SAMPR_USER_A_NAME_INFORMATION AccountName
Definition: sam.idl:727

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserAdminComment()

static NTSTATUS SampQueryUserAdminComment ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6409 of file samrpc.c.

6411{
6412 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6414
6415 *Buffer = NULL;
6416
6417 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6418 if (InfoBuffer == NULL)
6420
6421 /* Get the AdminComment string */
6423 L"AdminComment",
6424 &InfoBuffer->AdminComment.AdminComment);
6425 if (!NT_SUCCESS(Status))
6426 {
6427 TRACE("Status 0x%08lx\n", Status);
6428 goto done;
6429 }
6430
6431 *Buffer = InfoBuffer;
6432
6433done:
6434 if (!NT_SUCCESS(Status))
6435 {
6436 if (InfoBuffer != NULL)
6437 {
6438 if (InfoBuffer->AdminComment.AdminComment.Buffer != NULL)
6440
6441 midl_user_free(InfoBuffer);
6442 }
6443 }
6444
6445 return Status;
6446}
RPC_UNICODE_STRING AdminComment
Definition: sam.idl:618
SAMPR_USER_ADMIN_COMMENT_INFORMATION AdminComment
Definition: sam.idl:733

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserAll()

static NTSTATUS SampQueryUserAll ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6753 of file samrpc.c.

6755{
6756 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6757 SAM_DOMAIN_FIXED_DATA DomainFixedData;
6758 SAM_USER_FIXED_DATA FixedData;
6759 LARGE_INTEGER PasswordCanChange;
6760 LARGE_INTEGER PasswordMustChange;
6761 ULONG Length = 0;
6763
6764 *Buffer = NULL;
6765
6766 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6767 if (InfoBuffer == NULL)
6769
6770 /* Get the fixed size domain data */
6771 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
6773 L"F",
6774 NULL,
6775 (PVOID)&DomainFixedData,
6776 &Length);
6777 if (!NT_SUCCESS(Status))
6778 goto done;
6779
6780 /* Get the fixed size user data */
6781 Length = sizeof(SAM_USER_FIXED_DATA);
6782 Status = SampGetObjectAttribute(UserObject,
6783 L"F",
6784 NULL,
6785 (PVOID)&FixedData,
6786 &Length);
6787 if (!NT_SUCCESS(Status))
6788 goto done;
6789
6790 /* Set the fields to be returned */
6791 if (UserObject->Trusted)
6792 {
6798 }
6799 else
6800 {
6801 InfoBuffer->All.WhichFields = 0;
6802
6803 if (UserObject->Access & USER_READ_GENERAL)
6805
6806 if (UserObject->Access & USER_READ_LOGON)
6808
6809 if (UserObject->Access & USER_READ_ACCOUNT)
6811
6812 if (UserObject->Access & USER_READ_PREFERENCES)
6814 }
6815
6816 /* Fail, if no fields are to be returned */
6817 if (InfoBuffer->All.WhichFields == 0)
6818 {
6820 goto done;
6821 }
6822
6823 /* Get the UserName attribute */
6824 if (InfoBuffer->All.WhichFields & USER_ALL_USERNAME)
6825 {
6827 L"Name",
6828 &InfoBuffer->All.UserName);
6829 if (!NT_SUCCESS(Status))
6830 {
6831 TRACE("Status 0x%08lx\n", Status);
6832 goto done;
6833 }
6834 }
6835
6836 /* Get the FullName attribute */
6837 if (InfoBuffer->All.WhichFields & USER_ALL_FULLNAME)
6838 {
6840 L"FullName",
6841 &InfoBuffer->All.FullName);
6842 if (!NT_SUCCESS(Status))
6843 {
6844 TRACE("Status 0x%08lx\n", Status);
6845 goto done;
6846 }
6847 }
6848
6849 /* Get the UserId attribute */
6850 if (InfoBuffer->All.WhichFields & USER_ALL_USERID)
6851 {
6852 InfoBuffer->All.UserId = FixedData.UserId;
6853 }
6854
6855 /* Get the PrimaryGroupId attribute */
6856 if (InfoBuffer->All.WhichFields & USER_ALL_PRIMARYGROUPID)
6857 {
6858 InfoBuffer->All.PrimaryGroupId = FixedData.PrimaryGroupId;
6859 }
6860
6861 /* Get the AdminComment attribute */
6862 if (InfoBuffer->All.WhichFields & USER_ALL_ADMINCOMMENT)
6863 {
6865 L"AdminComment",
6866 &InfoBuffer->All.AdminComment);
6867 if (!NT_SUCCESS(Status))
6868 {
6869 TRACE("Status 0x%08lx\n", Status);
6870 goto done;
6871 }
6872 }
6873
6874 /* Get the UserComment attribute */
6875 if (InfoBuffer->All.WhichFields & USER_ALL_USERCOMMENT)
6876 {
6878 L"UserComment",
6879 &InfoBuffer->All.UserComment);
6880 if (!NT_SUCCESS(Status))
6881 {
6882 TRACE("Status 0x%08lx\n", Status);
6883 goto done;
6884 }
6885 }
6886
6887 /* Get the HomeDirectory attribute */
6888 if (InfoBuffer->All.WhichFields & USER_ALL_HOMEDIRECTORY)
6889 {
6891 L"HomeDirectory",
6892 &InfoBuffer->All.HomeDirectory);
6893 if (!NT_SUCCESS(Status))
6894 {
6895 TRACE("Status 0x%08lx\n", Status);
6896 goto done;
6897 }
6898 }
6899
6900 /* Get the HomeDirectoryDrive attribute */
6902 {
6904 L"HomeDirectoryDrive",
6905 &InfoBuffer->Home.HomeDirectoryDrive);
6906 if (!NT_SUCCESS(Status))
6907 {
6908 TRACE("Status 0x%08lx\n", Status);
6909 goto done;
6910 }
6911 }
6912
6913 /* Get the ScriptPath attribute */
6914 if (InfoBuffer->All.WhichFields & USER_ALL_SCRIPTPATH)
6915 {
6917 L"ScriptPath",
6918 &InfoBuffer->All.ScriptPath);
6919 if (!NT_SUCCESS(Status))
6920 {
6921 TRACE("Status 0x%08lx\n", Status);
6922 goto done;
6923 }
6924 }
6925
6926 /* Get the ProfilePath attribute */
6927 if (InfoBuffer->All.WhichFields & USER_ALL_PROFILEPATH)
6928 {
6930 L"ProfilePath",
6931 &InfoBuffer->All.ProfilePath);
6932 if (!NT_SUCCESS(Status))
6933 {
6934 TRACE("Status 0x%08lx\n", Status);
6935 goto done;
6936 }
6937 }
6938
6939 /* Get the WorkStations attribute */
6940 if (InfoBuffer->All.WhichFields & USER_ALL_WORKSTATIONS)
6941 {
6943 L"WorkStations",
6944 &InfoBuffer->All.WorkStations);
6945 if (!NT_SUCCESS(Status))
6946 {
6947 TRACE("Status 0x%08lx\n", Status);
6948 goto done;
6949 }
6950 }
6951
6952 /* Get the LastLogon attribute */
6953 if (InfoBuffer->All.WhichFields & USER_ALL_LASTLOGON)
6954 {
6955 InfoBuffer->All.LastLogon.LowPart = FixedData.LastLogon.LowPart;
6956 InfoBuffer->All.LastLogon.HighPart = FixedData.LastLogon.HighPart;
6957 }
6958
6959 /* Get the LastLogoff attribute */
6960 if (InfoBuffer->All.WhichFields & USER_ALL_LASTLOGOFF)
6961 {
6962 InfoBuffer->All.LastLogoff.LowPart = FixedData.LastLogoff.LowPart;
6963 InfoBuffer->All.LastLogoff.HighPart = FixedData.LastLogoff.HighPart;
6964 }
6965
6966 /* Get the LogonHours attribute */
6967 if (InfoBuffer->All.WhichFields & USER_ALL_LOGONHOURS)
6968 {
6970 &InfoBuffer->All.LogonHours);
6971 if (!NT_SUCCESS(Status))
6972 {
6973 TRACE("Status 0x%08lx\n", Status);
6974 goto done;
6975 }
6976 }
6977
6978 /* Get the BadPasswordCount attribute */
6979 if (InfoBuffer->All.WhichFields & USER_ALL_BADPASSWORDCOUNT)
6980 {
6981 InfoBuffer->All.BadPasswordCount = FixedData.BadPasswordCount;
6982 }
6983
6984 /* Get the LogonCount attribute */
6985 if (InfoBuffer->All.WhichFields & USER_ALL_LOGONCOUNT)
6986 {
6987 InfoBuffer->All.LogonCount = FixedData.LogonCount;
6988 }
6989
6990 /* Get the PasswordCanChange attribute */
6991 if (InfoBuffer->All.WhichFields & USER_ALL_PASSWORDCANCHANGE)
6992 {
6993 PasswordCanChange = SampAddRelativeTimeToTime(FixedData.PasswordLastSet,
6994 DomainFixedData.MinPasswordAge);
6995 InfoBuffer->All.PasswordCanChange.LowPart = PasswordCanChange.LowPart;
6996 InfoBuffer->All.PasswordCanChange.HighPart = PasswordCanChange.HighPart;
6997 }
6998
6999 /* Get the PasswordMustChange attribute */
7001 {
7002 PasswordMustChange = SampAddRelativeTimeToTime(FixedData.PasswordLastSet,
7003 DomainFixedData.MaxPasswordAge);
7004 InfoBuffer->All.PasswordMustChange.LowPart = PasswordMustChange.LowPart;
7005 InfoBuffer->All.PasswordMustChange.HighPart = PasswordMustChange.HighPart;
7006 }
7007
7008 /* Get the PasswordLastSet attribute */
7009 if (InfoBuffer->All.WhichFields & USER_ALL_PASSWORDLASTSET)
7010 {
7011 InfoBuffer->All.PasswordLastSet.LowPart = FixedData.PasswordLastSet.LowPart;
7012 InfoBuffer->All.PasswordLastSet.HighPart = FixedData.PasswordLastSet.HighPart;
7013 }
7014
7015 /* Get the AccountExpires attribute */
7016 if (InfoBuffer->All.WhichFields & USER_ALL_ACCOUNTEXPIRES)
7017 {
7018 InfoBuffer->All.AccountExpires.LowPart = FixedData.AccountExpires.LowPart;
7019 InfoBuffer->All.AccountExpires.HighPart = FixedData.AccountExpires.HighPart;
7020 }
7021
7022 /* Get the UserAccountControl attribute */
7024 {
7025 InfoBuffer->All.UserAccountControl = FixedData.UserAccountControl;
7026 }
7027
7028 /* Get the Parameters attribute */
7029 if (InfoBuffer->All.WhichFields & USER_ALL_PARAMETERS)
7030 {
7032 L"Parameters",
7033 &InfoBuffer->All.Parameters);
7034 if (!NT_SUCCESS(Status))
7035 {
7036 TRACE("Status 0x%08lx\n", Status);
7037 goto done;
7038 }
7039 }
7040
7041 /* Get the CountryCode attribute */
7042 if (InfoBuffer->All.WhichFields & USER_ALL_COUNTRYCODE)
7043 {
7044 InfoBuffer->All.CountryCode = FixedData.CountryCode;
7045 }
7046
7047 /* Get the CodePage attribute */
7048 if (InfoBuffer->All.WhichFields & USER_ALL_CODEPAGE)
7049 {
7050 InfoBuffer->All.CodePage = FixedData.CodePage;
7051 }
7052
7053 /* Get the LmPassword and NtPassword attributes */
7055 {
7056 InfoBuffer->All.LmPasswordPresent = FALSE;
7057 InfoBuffer->All.NtPasswordPresent = FALSE;
7058
7059 /* Get the NT password */
7060 Length = 0;
7061 SampGetObjectAttribute(UserObject,
7062 L"NTPwd",
7063 NULL,
7064 NULL,
7065 &Length);
7066
7067 if (Length == sizeof(ENCRYPTED_NT_OWF_PASSWORD))
7068 {
7070 if (InfoBuffer->All.NtOwfPassword.Buffer == NULL)
7071 {
7073 goto done;
7074 }
7075
7076 InfoBuffer->All.NtOwfPassword.Length = sizeof(ENCRYPTED_NT_OWF_PASSWORD);
7078
7079 Status = SampGetObjectAttribute(UserObject,
7080 L"NTPwd",
7081 NULL,
7082 (PVOID)InfoBuffer->All.NtOwfPassword.Buffer,
7083 &Length);
7084 if (!NT_SUCCESS(Status))
7085 goto done;
7086
7087 if (memcmp(InfoBuffer->All.NtOwfPassword.Buffer,
7088 &EmptyNtHash,
7090 InfoBuffer->All.NtPasswordPresent = TRUE;
7091 }
7092
7093 /* Get the LM password */
7094 Length = 0;
7095 SampGetObjectAttribute(UserObject,
7096 L"LMPwd",
7097 NULL,
7098 NULL,
7099 &Length);
7100
7101 if (Length == sizeof(ENCRYPTED_LM_OWF_PASSWORD))
7102 {
7104 if (InfoBuffer->All.LmOwfPassword.Buffer == NULL)
7105 {
7107 goto done;
7108 }
7109
7110 InfoBuffer->All.LmOwfPassword.Length = sizeof(ENCRYPTED_LM_OWF_PASSWORD);
7112
7113 Status = SampGetObjectAttribute(UserObject,
7114 L"LMPwd",
7115 NULL,
7116 (PVOID)InfoBuffer->All.LmOwfPassword.Buffer,
7117 &Length);
7118 if (!NT_SUCCESS(Status))
7119 goto done;
7120
7121 if (memcmp(InfoBuffer->All.LmOwfPassword.Buffer,
7122 &EmptyLmHash,
7124 InfoBuffer->All.LmPasswordPresent = TRUE;
7125 }
7126 }
7127
7128 if (InfoBuffer->All.WhichFields & USER_ALL_PRIVATEDATA)
7129 {
7131 L"PrivateData",
7132 &InfoBuffer->All.PrivateData);
7133 if (!NT_SUCCESS(Status))
7134 {
7135 TRACE("Status 0x%08lx\n", Status);
7136 goto done;
7137 }
7138 }
7139
7140 if (InfoBuffer->All.WhichFields & USER_ALL_PASSWORDEXPIRED)
7141 {
7142 /* FIXME */
7143 }
7144
7146 {
7147 Length = 0;
7148 SampGetObjectAttribute(UserObject,
7149 L"SecDesc",
7150 NULL,
7151 NULL,
7152 &Length);
7153
7154 if (Length > 0)
7155 {
7157 if (InfoBuffer->All.SecurityDescriptor.SecurityDescriptor == NULL)
7158 {
7160 goto done;
7161 }
7162
7163 InfoBuffer->All.SecurityDescriptor.Length = Length;
7164
7165 Status = SampGetObjectAttribute(UserObject,
7166 L"SecDesc",
7167 NULL,
7169 &Length);
7170 if (!NT_SUCCESS(Status))
7171 goto done;
7172 }
7173 }
7174
7175 *Buffer = InfoBuffer;
7176
7177done:
7178 if (!NT_SUCCESS(Status))
7179 {
7180 if (InfoBuffer != NULL)
7181 {
7182 if (InfoBuffer->All.UserName.Buffer != NULL)
7183 midl_user_free(InfoBuffer->All.UserName.Buffer);
7184
7185 if (InfoBuffer->All.FullName.Buffer != NULL)
7186 midl_user_free(InfoBuffer->All.FullName.Buffer);
7187
7188 if (InfoBuffer->All.AdminComment.Buffer != NULL)
7190
7191 if (InfoBuffer->All.UserComment.Buffer != NULL)
7192 midl_user_free(InfoBuffer->All.UserComment.Buffer);
7193
7194 if (InfoBuffer->All.HomeDirectory.Buffer != NULL)
7196
7197 if (InfoBuffer->All.HomeDirectoryDrive.Buffer != NULL)
7199
7200 if (InfoBuffer->All.ScriptPath.Buffer != NULL)
7201 midl_user_free(InfoBuffer->All.ScriptPath.Buffer);
7202
7203 if (InfoBuffer->All.ProfilePath.Buffer != NULL)
7204 midl_user_free(InfoBuffer->All.ProfilePath.Buffer);
7205
7206 if (InfoBuffer->All.WorkStations.Buffer != NULL)
7208
7209 if (InfoBuffer->All.LogonHours.LogonHours != NULL)
7211
7212 if (InfoBuffer->All.Parameters.Buffer != NULL)
7213 midl_user_free(InfoBuffer->All.Parameters.Buffer);
7214
7215 if (InfoBuffer->All.LmOwfPassword.Buffer != NULL)
7217
7218 if (InfoBuffer->All.NtOwfPassword.Buffer != NULL)
7220
7221 if (InfoBuffer->All.PrivateData.Buffer != NULL)
7222 midl_user_free(InfoBuffer->All.PrivateData.Buffer);
7223
7224 if (InfoBuffer->All.SecurityDescriptor.SecurityDescriptor != NULL)
7226
7227 midl_user_free(InfoBuffer);
7228 }
7229 }
7230
7231 return Status;
7232}
#define TRUE
Definition: types.h:120
#define FALSE
Definition: types.h:117
_ACRTIMP int __cdecl memcmp(const void *, const void *, size_t)
Definition: string.c:2807
struct _ENCRYPTED_LM_OWF_PASSWORD ENCRYPTED_NT_OWF_PASSWORD
struct _ENCRYPTED_LM_OWF_PASSWORD ENCRYPTED_LM_OWF_PASSWORD
#define USER_READ_GENERAL
Definition: ntsam.h:126
#define USER_ALL_READ_GENERAL_MASK
Definition: ntsam.h:228
#define USER_READ_LOGON
Definition: ntsam.h:129
#define USER_ALL_SCRIPTPATH
Definition: ntsam.h:204
#define USER_ALL_COUNTRYCODE
Definition: ntsam.h:218
#define USER_ALL_ADMINCOMMENT
Definition: ntsam.h:200
#define USER_ALL_PARAMETERS
Definition: ntsam.h:217
#define USER_ALL_WORKSTATIONS
Definition: ntsam.h:206
#define USER_READ_PREFERENCES
Definition: ntsam.h:127
#define USER_ALL_READ_LOGON_MASK
Definition: ntsam.h:229
#define USER_ALL_USERID
Definition: ntsam.h:198
#define USER_READ_ACCOUNT
Definition: ntsam.h:130
#define USER_ALL_HOMEDIRECTORY
Definition: ntsam.h:202
#define USER_ALL_USERNAME
Definition: ntsam.h:196
#define USER_ALL_PASSWORDCANCHANGE
Definition: ntsam.h:212
#define USER_ALL_PRIVATEDATA
Definition: ntsam.h:222
#define USER_ALL_LMPASSWORDPRESENT
Definition: ntsam.h:221
#define USER_ALL_HOMEDIRECTORYDRIVE
Definition: ntsam.h:203
#define USER_ALL_PASSWORDEXPIRED
Definition: ntsam.h:223
#define USER_ALL_USERCOMMENT
Definition: ntsam.h:201
#define USER_ALL_ACCOUNTEXPIRES
Definition: ntsam.h:215
#define USER_ALL_READ_PREFERENCES_MASK
Definition: ntsam.h:231
#define USER_ALL_READ_ACCOUNT_MASK
Definition: ntsam.h:230
#define USER_ALL_LASTLOGON
Definition: ntsam.h:207
#define USER_ALL_LOGONHOURS
Definition: ntsam.h:209
#define USER_ALL_PASSWORDLASTSET
Definition: ntsam.h:214
#define USER_ALL_PASSWORDMUSTCHANGE
Definition: ntsam.h:213
#define USER_ALL_PRIMARYGROUPID
Definition: ntsam.h:199
#define USER_ALL_USERACCOUNTCONTROL
Definition: ntsam.h:216
#define USER_ALL_FULLNAME
Definition: ntsam.h:197
#define USER_ALL_LASTLOGOFF
Definition: ntsam.h:208
#define USER_ALL_CODEPAGE
Definition: ntsam.h:219
#define USER_ALL_BADPASSWORDCOUNT
Definition: ntsam.h:210
#define USER_ALL_SECURITYDESCRIPTOR
Definition: ntsam.h:224
#define USER_ALL_LOGONCOUNT
Definition: ntsam.h:211
#define USER_ALL_PROFILEPATH
Definition: ntsam.h:205
#define USER_ALL_NTPASSWORDPRESENT
Definition: ntsam.h:220
#define USER_ALL_READ_TRUSTED_MASK
Definition: ntsam.h:232
static LARGE_INTEGER SampAddRelativeTimeToTime(IN LARGE_INTEGER AbsoluteTime, IN LARGE_INTEGER RelativeTime)
Definition: samrpc.c:63
ENCRYPTED_LM_OWF_PASSWORD EmptyLmHash
Definition: samsrv.c:27
ENCRYPTED_NT_OWF_PASSWORD EmptyNtHash
Definition: samsrv.c:26
unsigned short * Buffer
Definition: msv1_0.h:40
unsigned short MaximumLength
Definition: msv1_0.h:39
unsigned short Length
Definition: msv1_0.h:38
unsigned long Length
Definition: msv1_0.h:45
unsigned char * SecurityDescriptor
Definition: msv1_0.h:46
unsigned short BadPasswordCount
Definition: msv1_0.h:105
unsigned short LogonCount
Definition: msv1_0.h:106
OLD_LARGE_INTEGER PasswordMustChange
Definition: msv1_0.h:85
unsigned long PrimaryGroupId
Definition: msv1_0.h:101
OLD_LARGE_INTEGER PasswordLastSet
Definition: msv1_0.h:82
unsigned short CodePage
Definition: msv1_0.h:108
RPC_SHORT_BLOB NtOwfPassword
Definition: msv1_0.h:97
RPC_UNICODE_STRING UserName
Definition: msv1_0.h:86
OLD_LARGE_INTEGER PasswordCanChange
Definition: msv1_0.h:84
unsigned long WhichFields
Definition: msv1_0.h:103
OLD_LARGE_INTEGER LastLogon
Definition: msv1_0.h:80
RPC_UNICODE_STRING Parameters
Definition: msv1_0.h:95
RPC_UNICODE_STRING ProfilePath
Definition: msv1_0.h:91
RPC_UNICODE_STRING PrivateData
Definition: msv1_0.h:98
RPC_UNICODE_STRING FullName
Definition: msv1_0.h:87
RPC_UNICODE_STRING HomeDirectoryDrive
Definition: msv1_0.h:89
SAMPR_LOGON_HOURS LogonHours
Definition: msv1_0.h:104
unsigned short CountryCode
Definition: msv1_0.h:107
RPC_UNICODE_STRING UserComment
Definition: msv1_0.h:94
OLD_LARGE_INTEGER LastLogoff
Definition: msv1_0.h:81
RPC_UNICODE_STRING ScriptPath
Definition: msv1_0.h:90
RPC_UNICODE_STRING AdminComment
Definition: msv1_0.h:92
RPC_UNICODE_STRING HomeDirectory
Definition: msv1_0.h:88
unsigned long UserId
Definition: msv1_0.h:100
unsigned char LmPasswordPresent
Definition: msv1_0.h:109
SAMPR_SR_SECURITY_DESCRIPTOR SecurityDescriptor
Definition: msv1_0.h:99
OLD_LARGE_INTEGER AccountExpires
Definition: msv1_0.h:83
unsigned long UserAccountControl
Definition: msv1_0.h:102
RPC_SHORT_BLOB LmOwfPassword
Definition: msv1_0.h:96
unsigned char NtPasswordPresent
Definition: msv1_0.h:110
RPC_UNICODE_STRING WorkStations
Definition: msv1_0.h:93
RPC_UNICODE_STRING HomeDirectoryDrive
Definition: sam.idl:603
BOOLEAN Trusted
Definition: samsrv.h:55
ACCESS_MASK Access
Definition: samsrv.h:50
struct _SAM_DB_OBJECT * ParentObject
Definition: samsrv.h:56
USHORT CountryCode
Definition: samsrv.h:110
#define STATUS_ACCESS_DENIED
Definition: udferr_usr.h:145
SAMPR_USER_HOME_INFORMATION Home
Definition: sam.idl:730
SAMPR_USER_ALL_INFORMATION All
Definition: msv1_0.h:141

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserControl()

static NTSTATUS SampQueryUserControl ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6492 of file samrpc.c.

6494{
6495 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6496 SAM_USER_FIXED_DATA FixedData;
6497 ULONG Length = 0;
6499
6500 *Buffer = NULL;
6501
6502 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6503 if (InfoBuffer == NULL)
6505
6506 Length = sizeof(SAM_USER_FIXED_DATA);
6507 Status = SampGetObjectAttribute(UserObject,
6508 L"F",
6509 NULL,
6510 (PVOID)&FixedData,
6511 &Length);
6512 if (!NT_SUCCESS(Status))
6513 goto done;
6514
6515 InfoBuffer->Control.UserAccountControl = FixedData.UserAccountControl;
6516
6517 *Buffer = InfoBuffer;
6518
6519done:
6520 if (!NT_SUCCESS(Status))
6521 {
6522 if (InfoBuffer != NULL)
6523 {
6524 midl_user_free(InfoBuffer);
6525 }
6526 }
6527
6528 return Status;
6529}
USER_CONTROL_INFORMATION Control
Definition: sam.idl:736

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserExpires()

static NTSTATUS SampQueryUserExpires ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6534 of file samrpc.c.

6536{
6537 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6538 SAM_USER_FIXED_DATA FixedData;
6539 ULONG Length = 0;
6541
6542 *Buffer = NULL;
6543
6544 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6545 if (InfoBuffer == NULL)
6547
6548 Length = sizeof(SAM_USER_FIXED_DATA);
6549 Status = SampGetObjectAttribute(UserObject,
6550 L"F",
6551 NULL,
6552 (PVOID)&FixedData,
6553 &Length);
6554 if (!NT_SUCCESS(Status))
6555 goto done;
6556
6557 InfoBuffer->Expires.AccountExpires.LowPart = FixedData.AccountExpires.LowPart;
6558 InfoBuffer->Expires.AccountExpires.HighPart = FixedData.AccountExpires.HighPart;
6559
6560 *Buffer = InfoBuffer;
6561
6562done:
6563 if (!NT_SUCCESS(Status))
6564 {
6565 if (InfoBuffer != NULL)
6566 {
6567 midl_user_free(InfoBuffer);
6568 }
6569 }
6570
6571 return Status;
6572}
LARGE_INTEGER AccountExpires
Definition: ntsam.h:675
USER_EXPIRES_INFORMATION Expires
Definition: sam.idl:737

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserFullName()

static NTSTATUS SampQueryUserFullName ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6190 of file samrpc.c.

6192{
6193 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6195
6196 *Buffer = NULL;
6197
6198 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6199 if (InfoBuffer == NULL)
6201
6202 /* Get the FullName string */
6204 L"FullName",
6205 &InfoBuffer->FullName.FullName);
6206 if (!NT_SUCCESS(Status))
6207 {
6208 TRACE("Status 0x%08lx\n", Status);
6209 goto done;
6210 }
6211
6212 *Buffer = InfoBuffer;
6213
6214done:
6215 if (!NT_SUCCESS(Status))
6216 {
6217 if (InfoBuffer != NULL)
6218 {
6219 if (InfoBuffer->FullName.FullName.Buffer != NULL)
6221
6222 midl_user_free(InfoBuffer);
6223 }
6224 }
6225
6226 return Status;
6227}
RPC_UNICODE_STRING FullName
Definition: sam.idl:591
SAMPR_USER_F_NAME_INFORMATION FullName
Definition: sam.idl:728

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserGeneral()

static NTSTATUS SampQueryUserGeneral ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 5551 of file samrpc.c.

5553{
5554 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
5555 SAM_USER_FIXED_DATA FixedData;
5556 ULONG Length = 0;
5558
5559 *Buffer = NULL;
5560
5561 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
5562 if (InfoBuffer == NULL)
5564
5565 Length = sizeof(SAM_USER_FIXED_DATA);
5566 Status = SampGetObjectAttribute(UserObject,
5567 L"F",
5568 NULL,
5569 (PVOID)&FixedData,
5570 &Length);
5571 if (!NT_SUCCESS(Status))
5572 goto done;
5573
5574 InfoBuffer->General.PrimaryGroupId = FixedData.PrimaryGroupId;
5575
5576 /* Get the Name string */
5578 L"Name",
5579 &InfoBuffer->General.UserName);
5580 if (!NT_SUCCESS(Status))
5581 {
5582 TRACE("Status 0x%08lx\n", Status);
5583 goto done;
5584 }
5585
5586 /* Get the FullName string */
5588 L"FullName",
5589 &InfoBuffer->General.FullName);
5590 if (!NT_SUCCESS(Status))
5591 {
5592 TRACE("Status 0x%08lx\n", Status);
5593 goto done;
5594 }
5595
5596 /* Get the AdminComment string */
5598 L"AdminComment",
5599 &InfoBuffer->General.AdminComment);
5600 if (!NT_SUCCESS(Status))
5601 {
5602 TRACE("Status 0x%08lx\n", Status);
5603 goto done;
5604 }
5605
5606 /* Get the UserComment string */
5608 L"UserComment",
5609 &InfoBuffer->General.UserComment);
5610 if (!NT_SUCCESS(Status))
5611 {
5612 TRACE("Status 0x%08lx\n", Status);
5613 goto done;
5614 }
5615
5616 *Buffer = InfoBuffer;
5617
5618done:
5619 if (!NT_SUCCESS(Status))
5620 {
5621 if (InfoBuffer != NULL)
5622 {
5623 if (InfoBuffer->General.UserName.Buffer != NULL)
5625
5626 if (InfoBuffer->General.FullName.Buffer != NULL)
5628
5629 if (InfoBuffer->General.AdminComment.Buffer != NULL)
5631
5632 if (InfoBuffer->General.UserComment.Buffer != NULL)
5634
5635 midl_user_free(InfoBuffer);
5636 }
5637 }
5638
5639 return Status;
5640}
RPC_UNICODE_STRING UserName
Definition: sam.idl:520
RPC_UNICODE_STRING AdminComment
Definition: sam.idl:523
unsigned long PrimaryGroupId
Definition: sam.idl:522
RPC_UNICODE_STRING UserComment
Definition: sam.idl:524
RPC_UNICODE_STRING FullName
Definition: sam.idl:521
SAMPR_USER_GENERAL_INFORMATION General
Definition: sam.idl:721

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserHome()

static NTSTATUS SampQueryUserHome ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6273 of file samrpc.c.

6275{
6276 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6278
6279 *Buffer = NULL;
6280
6281 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6282 if (InfoBuffer == NULL)
6284
6285 /* Get the HomeDirectory string */
6287 L"HomeDirectory",
6288 &InfoBuffer->Home.HomeDirectory);
6289 if (!NT_SUCCESS(Status))
6290 {
6291 TRACE("Status 0x%08lx\n", Status);
6292 goto done;
6293 }
6294
6295 /* Get the HomeDirectoryDrive string */
6297 L"HomeDirectoryDrive",
6298 &InfoBuffer->Home.HomeDirectoryDrive);
6299 if (!NT_SUCCESS(Status))
6300 {
6301 TRACE("Status 0x%08lx\n", Status);
6302 goto done;
6303 }
6304
6305 *Buffer = InfoBuffer;
6306
6307done:
6308 if (!NT_SUCCESS(Status))
6309 {
6310 if (InfoBuffer != NULL)
6311 {
6312 if (InfoBuffer->Home.HomeDirectory.Buffer != NULL)
6314
6315 if (InfoBuffer->Home.HomeDirectoryDrive.Buffer != NULL)
6317
6318 midl_user_free(InfoBuffer);
6319 }
6320 }
6321
6322 return Status;
6323}
RPC_UNICODE_STRING HomeDirectory
Definition: sam.idl:602

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserInternal1()

static NTSTATUS SampQueryUserInternal1 ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6577 of file samrpc.c.

6579{
6580 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6581 ULONG Length = 0;
6583
6584 /* Fail, if the caller is not a trusted caller */
6585 if (UserObject->Trusted == FALSE)
6587
6588 *Buffer = NULL;
6589
6590 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6591 if (InfoBuffer == NULL)
6593
6594 InfoBuffer->Internal1.LmPasswordPresent = FALSE;
6595 InfoBuffer->Internal1.NtPasswordPresent = FALSE;
6596
6597 /* Get the NT password */
6598 Length = 0;
6599 SampGetObjectAttribute(UserObject,
6600 L"NTPwd",
6601 NULL,
6602 NULL,
6603 &Length);
6604
6605 if (Length == sizeof(ENCRYPTED_NT_OWF_PASSWORD))
6606 {
6607 Status = SampGetObjectAttribute(UserObject,
6608 L"NTPwd",
6609 NULL,
6611 &Length);
6612 if (!NT_SUCCESS(Status))
6613 goto done;
6614
6615 if (memcmp(&InfoBuffer->Internal1.EncryptedNtOwfPassword,
6616 &EmptyNtHash,
6618 InfoBuffer->Internal1.NtPasswordPresent = TRUE;
6619 }
6620
6621
6622 /* Get the LM password */
6623 Length = 0;
6624 SampGetObjectAttribute(UserObject,
6625 L"LMPwd",
6626 NULL,
6627 NULL,
6628 &Length);
6629
6630 if (Length == sizeof(ENCRYPTED_LM_OWF_PASSWORD))
6631 {
6632 Status = SampGetObjectAttribute(UserObject,
6633 L"LMPwd",
6634 NULL,
6636 &Length);
6637 if (!NT_SUCCESS(Status))
6638 goto done;
6639
6640 if (memcmp(&InfoBuffer->Internal1.EncryptedLmOwfPassword,
6641 &EmptyLmHash,
6643 InfoBuffer->Internal1.LmPasswordPresent = TRUE;
6644 }
6645
6646 InfoBuffer->Internal1.PasswordExpired = FALSE;
6647
6648 *Buffer = InfoBuffer;
6649
6650done:
6651 if (!NT_SUCCESS(Status))
6652 {
6653 if (InfoBuffer != NULL)
6654 {
6655 midl_user_free(InfoBuffer);
6656 }
6657 }
6658
6659 return Status;
6660}
#define STATUS_INVALID_INFO_CLASS
Definition: ntstatus.h:333
ENCRYPTED_NT_OWF_PASSWORD EncryptedNtOwfPassword
Definition: sam.idl:640
ENCRYPTED_LM_OWF_PASSWORD EncryptedLmOwfPassword
Definition: sam.idl:641
SAMPR_USER_INTERNAL1_INFORMATION Internal1
Definition: sam.idl:738

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserInternal2()

static NTSTATUS SampQueryUserInternal2 ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6665 of file samrpc.c.

6667{
6668 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6669 SAM_USER_FIXED_DATA FixedData;
6670 ULONG Length = 0;
6672
6673 *Buffer = NULL;
6674
6675 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6676 if (InfoBuffer == NULL)
6678
6679 Length = sizeof(SAM_USER_FIXED_DATA);
6680 Status = SampGetObjectAttribute(UserObject,
6681 L"F",
6682 NULL,
6683 (PVOID)&FixedData,
6684 &Length);
6685 if (!NT_SUCCESS(Status))
6686 goto done;
6687
6688 InfoBuffer->Internal2.Flags = 0;
6689 InfoBuffer->Internal2.LastLogon.LowPart = FixedData.LastLogon.LowPart;
6690 InfoBuffer->Internal2.LastLogon.HighPart = FixedData.LastLogon.HighPart;
6691 InfoBuffer->Internal2.LastLogoff.LowPart = FixedData.LastLogoff.LowPart;
6692 InfoBuffer->Internal2.LastLogoff.HighPart = FixedData.LastLogoff.HighPart;
6693 InfoBuffer->Internal2.BadPasswordCount = FixedData.BadPasswordCount;
6694 InfoBuffer->Internal2.LogonCount = FixedData.LogonCount;
6695
6696 *Buffer = InfoBuffer;
6697
6698done:
6699 if (!NT_SUCCESS(Status))
6700 {
6701 if (InfoBuffer != NULL)
6702 {
6703 midl_user_free(InfoBuffer);
6704 }
6705 }
6706
6707 return Status;
6708}
OLD_LARGE_INTEGER LastLogon
Definition: msv1_0.h:72
unsigned short BadPasswordCount
Definition: msv1_0.h:74
OLD_LARGE_INTEGER LastLogoff
Definition: msv1_0.h:73
SAMPR_USER_INTERNAL2_INFORMATION Internal2
Definition: msv1_0.h:137

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserLogon()

static NTSTATUS SampQueryUserLogon ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 5701 of file samrpc.c.

5703{
5704 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
5705 SAM_DOMAIN_FIXED_DATA DomainFixedData;
5706 SAM_USER_FIXED_DATA FixedData;
5707 LARGE_INTEGER PasswordCanChange;
5708 LARGE_INTEGER PasswordMustChange;
5709 ULONG Length = 0;
5711
5712 *Buffer = NULL;
5713
5714 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
5715 if (InfoBuffer == NULL)
5717
5718 /* Get the fixed size domain data */
5719 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
5721 L"F",
5722 NULL,
5723 (PVOID)&DomainFixedData,
5724 &Length);
5725 if (!NT_SUCCESS(Status))
5726 goto done;
5727
5728 /* Get the fixed size user data */
5729 Length = sizeof(SAM_USER_FIXED_DATA);
5730 Status = SampGetObjectAttribute(UserObject,
5731 L"F",
5732 NULL,
5733 (PVOID)&FixedData,
5734 &Length);
5735 if (!NT_SUCCESS(Status))
5736 goto done;
5737
5738 InfoBuffer->Logon.UserId = FixedData.UserId;
5739 InfoBuffer->Logon.PrimaryGroupId = FixedData.PrimaryGroupId;
5740 InfoBuffer->Logon.LastLogon.LowPart = FixedData.LastLogon.LowPart;
5741 InfoBuffer->Logon.LastLogon.HighPart = FixedData.LastLogon.HighPart;
5742 InfoBuffer->Logon.LastLogoff.LowPart = FixedData.LastLogoff.LowPart;
5743 InfoBuffer->Logon.LastLogoff.HighPart = FixedData.LastLogoff.HighPart;
5744 InfoBuffer->Logon.PasswordLastSet.LowPart = FixedData.PasswordLastSet.LowPart;
5745 InfoBuffer->Logon.PasswordLastSet.HighPart = FixedData.PasswordLastSet.HighPart;
5746 InfoBuffer->Logon.BadPasswordCount = FixedData.BadPasswordCount;
5747 InfoBuffer->Logon.LogonCount = FixedData.LogonCount;
5748 InfoBuffer->Logon.UserAccountControl = FixedData.UserAccountControl;
5749
5750 PasswordCanChange = SampAddRelativeTimeToTime(FixedData.PasswordLastSet,
5751 DomainFixedData.MinPasswordAge);
5752 InfoBuffer->Logon.PasswordCanChange.LowPart = PasswordCanChange.LowPart;
5753 InfoBuffer->Logon.PasswordCanChange.HighPart = PasswordCanChange.HighPart;
5754
5755 PasswordMustChange = SampAddRelativeTimeToTime(FixedData.PasswordLastSet,
5756 DomainFixedData.MaxPasswordAge);
5757 InfoBuffer->Logon.PasswordMustChange.LowPart = PasswordMustChange.LowPart;
5758 InfoBuffer->Logon.PasswordMustChange.HighPart = PasswordMustChange.HighPart;
5759
5760 /* Get the Name string */
5762 L"Name",
5763 &InfoBuffer->Logon.UserName);
5764 if (!NT_SUCCESS(Status))
5765 {
5766 TRACE("Status 0x%08lx\n", Status);
5767 goto done;
5768 }
5769
5770 /* Get the FullName string */
5772 L"FullName",
5773 &InfoBuffer->Logon.FullName);
5774 if (!NT_SUCCESS(Status))
5775 {
5776 TRACE("Status 0x%08lx\n", Status);
5777 goto done;
5778 }
5779
5780 /* Get the HomeDirectory string */
5782 L"HomeDirectory",
5783 &InfoBuffer->Logon.HomeDirectory);
5784 if (!NT_SUCCESS(Status))
5785 {
5786 TRACE("Status 0x%08lx\n", Status);
5787 goto done;
5788 }
5789
5790 /* Get the HomeDirectoryDrive string */
5792 L"HomeDirectoryDrive",
5793 &InfoBuffer->Logon.HomeDirectoryDrive);
5794 if (!NT_SUCCESS(Status))
5795 {
5796 TRACE("Status 0x%08lx\n", Status);
5797 goto done;
5798 }
5799
5800 /* Get the ScriptPath string */
5802 L"ScriptPath",
5803 &InfoBuffer->Logon.ScriptPath);
5804 if (!NT_SUCCESS(Status))
5805 {
5806 TRACE("Status 0x%08lx\n", Status);
5807 goto done;
5808 }
5809
5810 /* Get the ProfilePath string */
5812 L"ProfilePath",
5813 &InfoBuffer->Logon.ProfilePath);
5814 if (!NT_SUCCESS(Status))
5815 {
5816 TRACE("Status 0x%08lx\n", Status);
5817 goto done;
5818 }
5819
5820 /* Get the WorkStations string */
5822 L"WorkStations",
5823 &InfoBuffer->Logon.WorkStations);
5824 if (!NT_SUCCESS(Status))
5825 {
5826 TRACE("Status 0x%08lx\n", Status);
5827 goto done;
5828 }
5829
5830 /* Get the LogonHours attribute */
5832 &InfoBuffer->Logon.LogonHours);
5833 if (!NT_SUCCESS(Status))
5834 {
5835 TRACE("Status 0x%08lx\n", Status);
5836 goto done;
5837 }
5838
5839 *Buffer = InfoBuffer;
5840
5841done:
5842 if (!NT_SUCCESS(Status))
5843 {
5844 if (InfoBuffer != NULL)
5845 {
5846 if (InfoBuffer->Logon.UserName.Buffer != NULL)
5847 midl_user_free(InfoBuffer->Logon.UserName.Buffer);
5848
5849 if (InfoBuffer->Logon.FullName.Buffer != NULL)
5850 midl_user_free(InfoBuffer->Logon.FullName.Buffer);
5851
5852 if (InfoBuffer->Logon.HomeDirectory.Buffer != NULL)
5854
5855 if (InfoBuffer->Logon.HomeDirectoryDrive.Buffer != NULL)
5857
5858 if (InfoBuffer->Logon.ScriptPath.Buffer != NULL)
5860
5861 if (InfoBuffer->Logon.ProfilePath.Buffer != NULL)
5863
5864 if (InfoBuffer->Logon.WorkStations.Buffer != NULL)
5866
5867 if (InfoBuffer->Logon.LogonHours.LogonHours != NULL)
5869
5870 midl_user_free(InfoBuffer);
5871 }
5872 }
5873
5874 return Status;
5875}
RPC_UNICODE_STRING HomeDirectory
Definition: sam.idl:546
unsigned long PrimaryGroupId
Definition: sam.idl:545
RPC_UNICODE_STRING ProfilePath
Definition: sam.idl:549
unsigned long UserAccountControl
Definition: sam.idl:559
OLD_LARGE_INTEGER PasswordLastSet
Definition: sam.idl:553
unsigned short BadPasswordCount
Definition: sam.idl:557
OLD_LARGE_INTEGER LastLogon
Definition: sam.idl:551
SAMPR_LOGON_HOURS LogonHours
Definition: sam.idl:556
RPC_UNICODE_STRING UserName
Definition: sam.idl:542
RPC_UNICODE_STRING ScriptPath
Definition: sam.idl:548
OLD_LARGE_INTEGER PasswordMustChange
Definition: sam.idl:555
OLD_LARGE_INTEGER PasswordCanChange
Definition: sam.idl:554
unsigned short LogonCount
Definition: sam.idl:558
RPC_UNICODE_STRING FullName
Definition: sam.idl:543
OLD_LARGE_INTEGER LastLogoff
Definition: sam.idl:552
RPC_UNICODE_STRING WorkStations
Definition: sam.idl:550
unsigned long UserId
Definition: sam.idl:544
RPC_UNICODE_STRING HomeDirectoryDrive
Definition: sam.idl:547
SAMPR_USER_LOGON_INFORMATION Logon
Definition: sam.idl:723

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserLogonHours()

static NTSTATUS SampQueryUserLogonHours ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6050 of file samrpc.c.

6052{
6053 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6055
6056 TRACE("(%p %p)\n", UserObject, Buffer);
6057
6058 *Buffer = NULL;
6059
6060 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6061 if (InfoBuffer == NULL)
6062 {
6063 TRACE("Failed to allocate InfoBuffer!\n");
6065 }
6066
6068 &InfoBuffer->LogonHours.LogonHours);
6069 if (!NT_SUCCESS(Status))
6070 {
6071 TRACE("SampGetLogonHoursAttribute failed (Status 0x%08lx)\n", Status);
6072 goto done;
6073 }
6074
6075 *Buffer = InfoBuffer;
6076
6077done:
6078 if (!NT_SUCCESS(Status))
6079 {
6080 if (InfoBuffer != NULL)
6081 {
6082 if (InfoBuffer->LogonHours.LogonHours.LogonHours != NULL)
6084
6085 midl_user_free(InfoBuffer);
6086 }
6087 }
6088
6089 return Status;
6090}
SAMPR_LOGON_HOURS LogonHours
Definition: sam.idl:635
SAMPR_USER_LOGON_HOURS_INFORMATION LogonHours
Definition: sam.idl:724

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserName()

static NTSTATUS SampQueryUserName ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6095 of file samrpc.c.

6097{
6098 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6100
6101 *Buffer = NULL;
6102
6103 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6104 if (InfoBuffer == NULL)
6106
6107 /* Get the Name string */
6109 L"Name",
6110 &InfoBuffer->Name.UserName);
6111 if (!NT_SUCCESS(Status))
6112 {
6113 TRACE("Status 0x%08lx\n", Status);
6114 goto done;
6115 }
6116
6117 /* Get the FullName string */
6119 L"FullName",
6120 &InfoBuffer->Name.FullName);
6121 if (!NT_SUCCESS(Status))
6122 {
6123 TRACE("Status 0x%08lx\n", Status);
6124 goto done;
6125 }
6126
6127 *Buffer = InfoBuffer;
6128
6129done:
6130 if (!NT_SUCCESS(Status))
6131 {
6132 if (InfoBuffer != NULL)
6133 {
6134 if (InfoBuffer->Name.UserName.Buffer != NULL)
6135 midl_user_free(InfoBuffer->Name.UserName.Buffer);
6136
6137 if (InfoBuffer->Name.FullName.Buffer != NULL)
6138 midl_user_free(InfoBuffer->Name.FullName.Buffer);
6139
6140 midl_user_free(InfoBuffer);
6141 }
6142 }
6143
6144 return Status;
6145}
RPC_UNICODE_STRING FullName
Definition: sam.idl:597
RPC_UNICODE_STRING UserName
Definition: sam.idl:596
SAMPR_USER_NAME_INFORMATION Name
Definition: sam.idl:726

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserParameters()

static NTSTATUS SampQueryUserParameters ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6712 of file samrpc.c.

6714{
6715 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6717
6718 *Buffer = NULL;
6719
6720 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6721 if (InfoBuffer == NULL)
6723
6724 /* Get the Parameters string */
6726 L"Parameters",
6727 &InfoBuffer->Parameters.Parameters);
6728 if (!NT_SUCCESS(Status))
6729 {
6730 TRACE("Status 0x%08lx\n", Status);
6731 goto done;
6732 }
6733
6734 *Buffer = InfoBuffer;
6735
6736done:
6737 if (!NT_SUCCESS(Status))
6738 {
6739 if (InfoBuffer != NULL)
6740 {
6741 if (InfoBuffer->Parameters.Parameters.Buffer != NULL)
6743
6744 midl_user_free(InfoBuffer);
6745 }
6746 }
6747
6748 return Status;
6749}
RPC_UNICODE_STRING Parameters
Definition: sam.idl:537
SAMPR_USER_PARAMETERS_INFORMATION Parameters
Definition: sam.idl:740

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserPreferences()

static NTSTATUS SampQueryUserPreferences ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 5645 of file samrpc.c.

5647{
5648 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
5649 SAM_USER_FIXED_DATA FixedData;
5650 ULONG Length = 0;
5652
5653 *Buffer = NULL;
5654
5655 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
5656 if (InfoBuffer == NULL)
5658
5659 Length = sizeof(SAM_USER_FIXED_DATA);
5660 Status = SampGetObjectAttribute(UserObject,
5661 L"F",
5662 NULL,
5663 (PVOID)&FixedData,
5664 &Length);
5665 if (!NT_SUCCESS(Status))
5666 goto done;
5667
5668 InfoBuffer->Preferences.CountryCode = FixedData.CountryCode;
5669 InfoBuffer->Preferences.CodePage = FixedData.CodePage;
5670
5671 /* Get the UserComment string */
5673 L"UserComment",
5674 &InfoBuffer->Preferences.UserComment);
5675 if (!NT_SUCCESS(Status))
5676 {
5677 TRACE("Status 0x%08lx\n", Status);
5678 goto done;
5679 }
5680
5681 *Buffer = InfoBuffer;
5682
5683done:
5684 if (!NT_SUCCESS(Status))
5685 {
5686 if (InfoBuffer != NULL)
5687 {
5688 if (InfoBuffer->Preferences.UserComment.Buffer != NULL)
5690
5691 midl_user_free(InfoBuffer);
5692 }
5693 }
5694
5695 return Status;
5696}
RPC_UNICODE_STRING UserComment
Definition: sam.idl:529
SAMPR_USER_PREFERENCES_INFORMATION Preferences
Definition: sam.idl:722

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserPrimaryGroup()

static NTSTATUS SampQueryUserPrimaryGroup ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6232 of file samrpc.c.

6234{
6235 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6236 SAM_USER_FIXED_DATA FixedData;
6237 ULONG Length = 0;
6239
6240 *Buffer = NULL;
6241
6242 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6243 if (InfoBuffer == NULL)
6245
6246 Length = sizeof(SAM_USER_FIXED_DATA);
6247 Status = SampGetObjectAttribute(UserObject,
6248 L"F",
6249 NULL,
6250 (PVOID)&FixedData,
6251 &Length);
6252 if (!NT_SUCCESS(Status))
6253 goto done;
6254
6255 InfoBuffer->PrimaryGroup.PrimaryGroupId = FixedData.PrimaryGroupId;
6256
6257 *Buffer = InfoBuffer;
6258
6259done:
6260 if (!NT_SUCCESS(Status))
6261 {
6262 if (InfoBuffer != NULL)
6263 {
6264 midl_user_free(InfoBuffer);
6265 }
6266 }
6267
6268 return Status;
6269}
USER_PRIMARY_GROUP_INFORMATION PrimaryGroup
Definition: sam.idl:729

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserProfile()

static NTSTATUS SampQueryUserProfile ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6368 of file samrpc.c.

6370{
6371 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6373
6374 *Buffer = NULL;
6375
6376 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6377 if (InfoBuffer == NULL)
6379
6380 /* Get the ProfilePath string */
6382 L"ProfilePath",
6383 &InfoBuffer->Profile.ProfilePath);
6384 if (!NT_SUCCESS(Status))
6385 {
6386 TRACE("Status 0x%08lx\n", Status);
6387 goto done;
6388 }
6389
6390 *Buffer = InfoBuffer;
6391
6392done:
6393 if (!NT_SUCCESS(Status))
6394 {
6395 if (InfoBuffer != NULL)
6396 {
6397 if (InfoBuffer->Profile.ProfilePath.Buffer != NULL)
6399
6400 midl_user_free(InfoBuffer);
6401 }
6402 }
6403
6404 return Status;
6405}
RPC_UNICODE_STRING ProfilePath
Definition: sam.idl:613
SAMPR_USER_PROFILE_INFORMATION Profile
Definition: sam.idl:732

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserScript()

static NTSTATUS SampQueryUserScript ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6327 of file samrpc.c.

6329{
6330 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6332
6333 *Buffer = NULL;
6334
6335 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6336 if (InfoBuffer == NULL)
6338
6339 /* Get the ScriptPath string */
6341 L"ScriptPath",
6342 &InfoBuffer->Script.ScriptPath);
6343 if (!NT_SUCCESS(Status))
6344 {
6345 TRACE("Status 0x%08lx\n", Status);
6346 goto done;
6347 }
6348
6349 *Buffer = InfoBuffer;
6350
6351done:
6352 if (!NT_SUCCESS(Status))
6353 {
6354 if (InfoBuffer != NULL)
6355 {
6356 if (InfoBuffer->Script.ScriptPath.Buffer != NULL)
6358
6359 midl_user_free(InfoBuffer);
6360 }
6361 }
6362
6363 return Status;
6364}
RPC_UNICODE_STRING ScriptPath
Definition: sam.idl:608
SAMPR_USER_SCRIPT_INFORMATION Script
Definition: sam.idl:731

Referenced by SamrQueryInformationUser2().

◆ SampQueryUserWorkStations()

static NTSTATUS SampQueryUserWorkStations ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER *  Buffer 
)
static

Definition at line 6450 of file samrpc.c.

6452{
6453 PSAMPR_USER_INFO_BUFFER InfoBuffer = NULL;
6455
6456 *Buffer = NULL;
6457
6458 InfoBuffer = midl_user_allocate(sizeof(SAMPR_USER_INFO_BUFFER));
6459 if (InfoBuffer == NULL)
6461
6462 /* Get the WorkStations string */
6464 L"WorkStations",
6465 &InfoBuffer->WorkStations.WorkStations);
6466 if (!NT_SUCCESS(Status))
6467 {
6468 TRACE("Status 0x%08lx\n", Status);
6469 goto done;
6470 }
6471
6472 *Buffer = InfoBuffer;
6473
6474done:
6475 if (!NT_SUCCESS(Status))
6476 {
6477 if (InfoBuffer != NULL)
6478 {
6479 if (InfoBuffer->WorkStations.WorkStations.Buffer != NULL)
6481
6482 midl_user_free(InfoBuffer);
6483 }
6484 }
6485
6486 return Status;
6487}
RPC_UNICODE_STRING WorkStations
Definition: sam.idl:623
SAMPR_USER_WORKSTATIONS_INFORMATION WorkStations
Definition: sam.idl:734

Referenced by SamrQueryInformationUser2().

◆ SAMPR_HANDLE_rundown()

void __RPC_USER SAMPR_HANDLE_rundown ( SAMPR_HANDLE  hHandle)

Definition at line 126 of file samrpc.c.

127{
128 FIXME("SAMPR_HANDLE_rundown(%p)\n", hHandle);
129}
#define FIXME(fmt,...)
Definition: precomp.h:53

◆ SampSetAliasName()

static NTSTATUS SampSetAliasName ( PSAM_DB_OBJECT  AliasObject,
PSAMPR_ALIAS_INFO_BUFFER  Buffer 
)
static

Definition at line 5099 of file samrpc.c.

5101{
5102 UNICODE_STRING OldAliasName = {0, 0, NULL};
5103 UNICODE_STRING NewAliasName;
5105
5107 L"Name",
5108 (PRPC_UNICODE_STRING)&OldAliasName);
5109 if (!NT_SUCCESS(Status))
5110 {
5111 TRACE("SampGetObjectAttributeString failed (Status 0x%08lx)\n", Status);
5112 goto done;
5113 }
5114
5115 /* Check the new account name */
5116 Status = SampCheckAccountName(&Buffer->Name.Name, 256);
5117 if (!NT_SUCCESS(Status))
5118 {
5119 TRACE("SampCheckAccountName failed (Status 0x%08lx)\n", Status);
5120 return Status;
5121 }
5122
5123 NewAliasName.Length = Buffer->Name.Name.Length;
5124 NewAliasName.MaximumLength = Buffer->Name.Name.MaximumLength;
5125 NewAliasName.Buffer = Buffer->Name.Name.Buffer;
5126
5127 if (!RtlEqualUnicodeString(&OldAliasName, &NewAliasName, TRUE))
5128 {
5130 NewAliasName.Buffer);
5131 if (!NT_SUCCESS(Status))
5132 {
5133 TRACE("Alias name \'%S\' already exists in domain (Status 0x%08lx)\n",
5134 NewAliasName.Buffer, Status);
5135 goto done;
5136 }
5137 }
5138
5140 L"Aliases",
5141 NewAliasName.Buffer,
5142 AliasObject->RelativeId);
5143 if (!NT_SUCCESS(Status))
5144 {
5145 TRACE("SampSetAccountNameInDomain failed (Status 0x%08lx)\n", Status);
5146 goto done;
5147 }
5148
5150 L"Aliases",
5151 OldAliasName.Buffer);
5152 if (!NT_SUCCESS(Status))
5153 {
5154 TRACE("SampRemoveAccountNameFromDomain failed (Status 0x%08lx)\n", Status);
5155 goto done;
5156 }
5157
5159 L"Name",
5160 (PRPC_UNICODE_STRING)&NewAliasName);
5161 if (!NT_SUCCESS(Status))
5162 {
5163 TRACE("SampSetObjectAttribute failed (Status 0x%08lx)\n", Status);
5164 }
5165
5166done:
5167 if (OldAliasName.Buffer != NULL)
5168 midl_user_free(OldAliasName.Buffer);
5169
5170 return Status;
5171}
NTSTATUS SampSetObjectAttributeString(PSAM_DB_OBJECT DbObject, LPWSTR AttributeName, PRPC_UNICODE_STRING String)
Definition: database.c:595
NTSTATUS SampSetAccountNameInDomain(IN PSAM_DB_OBJECT DomainObject, IN LPCWSTR lpContainerName, IN LPCWSTR lpAccountName, IN ULONG ulRelativeId)
Definition: domain.c:14
NTSTATUS SampRemoveAccountNameFromDomain(IN PSAM_DB_OBJECT DomainObject, IN LPCWSTR lpContainerName, IN LPCWSTR lpAccountName)
Definition: domain.c:57
NTSTATUS SampCheckAccountNameInDomain(IN PSAM_DB_OBJECT DomainObject, IN LPCWSTR lpAccountName)
Definition: domain.c:96
NTSTATUS SampCheckAccountName(IN PRPC_UNICODE_STRING AccountName, IN USHORT MaxLength)
Definition: utils.c:154
NTSYSAPI BOOLEAN NTAPI RtlEqualUnicodeString(PUNICODE_STRING String1, PUNICODE_STRING String2, BOOLEAN CaseInSensitive)
ULONG RelativeId
Definition: samsrv.h:54
USHORT MaximumLength
Definition: env_spec_w32.h:370

Referenced by SamrSetInformationAlias().

◆ SampSetDomainLockout()

static NTSTATUS SampSetDomainLockout ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER  Buffer 
)
static

Definition at line 1760 of file samrpc.c.

1762{
1763 SAM_DOMAIN_FIXED_DATA FixedData;
1764 ULONG Length = 0;
1766
1767 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
1768 Status = SampGetObjectAttribute(DomainObject,
1769 L"F",
1770 NULL,
1771 (PVOID)&FixedData,
1772 &Length);
1773 if (!NT_SUCCESS(Status))
1774 goto done;
1775
1776 FixedData.LockoutDuration = Buffer->Lockout.LockoutDuration;
1777 FixedData.LockoutObservationWindow = Buffer->Lockout.LockoutObservationWindow;
1778 FixedData.LockoutThreshold = Buffer->Lockout.LockoutThreshold;
1779
1780 Status = SampSetObjectAttribute(DomainObject,
1781 L"F",
1782 REG_BINARY,
1783 &FixedData,
1784 Length);
1785
1786done:
1787 return Status;
1788}
NTSTATUS SampSetObjectAttribute(PSAM_DB_OBJECT DbObject, LPWSTR AttributeName, ULONG AttributeType, LPVOID AttributeData, ULONG AttributeSize)
Definition: database.c:501
#define REG_BINARY
Definition: nt_native.h:1499

Referenced by SamrSetInformationDomain().

◆ SampSetDomainLogoff()

static NTSTATUS SampSetDomainLogoff ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER  Buffer 
)
static

Definition at line 1669 of file samrpc.c.

1671{
1672 SAM_DOMAIN_FIXED_DATA FixedData;
1673 ULONG Length = 0;
1675
1676 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
1677 Status = SampGetObjectAttribute(DomainObject,
1678 L"F",
1679 NULL,
1680 (PVOID)&FixedData,
1681 &Length);
1682 if (!NT_SUCCESS(Status))
1683 goto done;
1684
1685 FixedData.ForceLogoff.LowPart = Buffer->Logoff.ForceLogoff.LowPart;
1686 FixedData.ForceLogoff.HighPart = Buffer->Logoff.ForceLogoff.HighPart;
1687
1688 Status = SampSetObjectAttribute(DomainObject,
1689 L"F",
1690 REG_BINARY,
1691 &FixedData,
1692 Length);
1693
1694done:
1695 return Status;
1696}

Referenced by SamrSetInformationDomain().

◆ SampSetDomainPassword()

static NTSTATUS SampSetDomainPassword ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER  Buffer 
)
static

Definition at line 1633 of file samrpc.c.

1635{
1636 SAM_DOMAIN_FIXED_DATA FixedData;
1637 ULONG Length = 0;
1639
1640 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
1641 Status = SampGetObjectAttribute(DomainObject,
1642 L"F",
1643 NULL,
1644 (PVOID)&FixedData,
1645 &Length);
1646 if (!NT_SUCCESS(Status))
1647 goto done;
1648
1649 FixedData.MinPasswordLength = Buffer->Password.MinPasswordLength;
1650 FixedData.PasswordHistoryLength = Buffer->Password.PasswordHistoryLength;
1651 FixedData.PasswordProperties = Buffer->Password.PasswordProperties;
1652 FixedData.MaxPasswordAge.LowPart = Buffer->Password.MaxPasswordAge.LowPart;
1653 FixedData.MaxPasswordAge.HighPart = Buffer->Password.MaxPasswordAge.HighPart;
1654 FixedData.MinPasswordAge.LowPart = Buffer->Password.MinPasswordAge.LowPart;
1655 FixedData.MinPasswordAge.HighPart = Buffer->Password.MinPasswordAge.HighPart;
1656
1657 Status = SampSetObjectAttribute(DomainObject,
1658 L"F",
1659 REG_BINARY,
1660 &FixedData,
1661 Length);
1662
1663done:
1664 return Status;
1665}

Referenced by SamrSetInformationDomain().

◆ SampSetDomainServerRole()

static NTSTATUS SampSetDomainServerRole ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER  Buffer 
)
static

Definition at line 1700 of file samrpc.c.

1702{
1703 SAM_DOMAIN_FIXED_DATA FixedData;
1704 ULONG Length = 0;
1706
1707 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
1708 Status = SampGetObjectAttribute(DomainObject,
1709 L"F",
1710 NULL,
1711 (PVOID)&FixedData,
1712 &Length);
1713 if (!NT_SUCCESS(Status))
1714 goto done;
1715
1716 FixedData.DomainServerRole = Buffer->Role.DomainServerRole;
1717
1718 Status = SampSetObjectAttribute(DomainObject,
1719 L"F",
1720 REG_BINARY,
1721 &FixedData,
1722 Length);
1723
1724done:
1725 return Status;
1726}

Referenced by SamrSetInformationDomain().

◆ SampSetDomainState()

static NTSTATUS SampSetDomainState ( PSAM_DB_OBJECT  DomainObject,
PSAMPR_DOMAIN_INFO_BUFFER  Buffer 
)
static

Definition at line 1730 of file samrpc.c.

1732{
1733 SAM_DOMAIN_FIXED_DATA FixedData;
1734 ULONG Length = 0;
1736
1737 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
1738 Status = SampGetObjectAttribute(DomainObject,
1739 L"F",
1740 NULL,
1741 (PVOID)&FixedData,
1742 &Length);
1743 if (!NT_SUCCESS(Status))
1744 goto done;
1745
1746 FixedData.DomainServerState = Buffer->State.DomainServerState;
1747
1748 Status = SampSetObjectAttribute(DomainObject,
1749 L"F",
1750 REG_BINARY,
1751 &FixedData,
1752 Length);
1753
1754done:
1755 return Status;
1756}

Referenced by SamrSetInformationDomain().

◆ SampSetGroupAttribute()

static NTSTATUS SampSetGroupAttribute ( PSAM_DB_OBJECT  GroupObject,
PSAMPR_GROUP_INFO_BUFFER  Buffer 
)
static

Definition at line 4388 of file samrpc.c.

4390{
4391 SAM_GROUP_FIXED_DATA FixedData;
4392 ULONG Length = 0;
4394
4395 Length = sizeof(SAM_GROUP_FIXED_DATA);
4396 Status = SampGetObjectAttribute(GroupObject,
4397 L"F",
4398 NULL,
4399 (PVOID)&FixedData,
4400 &Length);
4401 if (!NT_SUCCESS(Status))
4402 goto done;
4403
4404 FixedData.Attributes = Buffer->Attribute.Attributes;
4405
4406 Status = SampSetObjectAttribute(GroupObject,
4407 L"F",
4408 REG_BINARY,
4409 &FixedData,
4410 Length);
4411
4412done:
4413 return Status;
4414}

Referenced by SamrSetInformationGroup().

◆ SampSetGroupName()

static NTSTATUS SampSetGroupName ( PSAM_DB_OBJECT  GroupObject,
PSAMPR_GROUP_INFO_BUFFER  Buffer 
)
static

Definition at line 4312 of file samrpc.c.

4314{
4315 UNICODE_STRING OldGroupName = {0, 0, NULL};
4316 UNICODE_STRING NewGroupName;
4318
4320 L"Name",
4321 (PRPC_UNICODE_STRING)&OldGroupName);
4322 if (!NT_SUCCESS(Status))
4323 {
4324 TRACE("SampGetObjectAttributeString failed (Status 0x%08lx)\n", Status);
4325 goto done;
4326 }
4327
4328 /* Check the new account name */
4329 Status = SampCheckAccountName(&Buffer->Name.Name, 256);
4330 if (!NT_SUCCESS(Status))
4331 {
4332 TRACE("SampCheckAccountName failed (Status 0x%08lx)\n", Status);
4333 return Status;
4334 }
4335
4336 NewGroupName.Length = Buffer->Name.Name.Length;
4337 NewGroupName.MaximumLength = Buffer->Name.Name.MaximumLength;
4338 NewGroupName.Buffer = Buffer->Name.Name.Buffer;
4339
4340 if (!RtlEqualUnicodeString(&OldGroupName, &NewGroupName, TRUE))
4341 {
4343 NewGroupName.Buffer);
4344 if (!NT_SUCCESS(Status))
4345 {
4346 TRACE("Group name \'%S\' already exists in domain (Status 0x%08lx)\n",
4347 NewGroupName.Buffer, Status);
4348 goto done;
4349 }
4350 }
4351
4353 L"Groups",
4354 NewGroupName.Buffer,
4355 GroupObject->RelativeId);
4356 if (!NT_SUCCESS(Status))
4357 {
4358 TRACE("SampSetAccountNameInDomain failed (Status 0x%08lx)\n", Status);
4359 goto done;
4360 }
4361
4363 L"Groups",
4364 OldGroupName.Buffer);
4365 if (!NT_SUCCESS(Status))
4366 {
4367 TRACE("SampRemoveAccountNameFromDomain failed (Status 0x%08lx)\n", Status);
4368 goto done;
4369 }
4370
4372 L"Name",
4373 (PRPC_UNICODE_STRING)&NewGroupName);
4374 if (!NT_SUCCESS(Status))
4375 {
4376 TRACE("SampSetObjectAttribute failed (Status 0x%08lx)\n", Status);
4377 }
4378
4379done:
4380 if (OldGroupName.Buffer != NULL)
4381 midl_user_free(OldGroupName.Buffer);
4382
4383 return Status;
4384}

Referenced by SamrSetInformationGroup().

◆ SampSetUserAll()

static NTSTATUS SampSetUserAll ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER  Buffer 
)
static

Definition at line 7612 of file samrpc.c.

7614{
7615 SAM_USER_FIXED_DATA FixedData;
7616 ULONG Length = 0;
7617 ULONG WhichFields;
7618 PENCRYPTED_NT_OWF_PASSWORD NtPassword = NULL;
7619 PENCRYPTED_LM_OWF_PASSWORD LmPassword = NULL;
7620 BOOLEAN NtPasswordPresent = FALSE;
7621 BOOLEAN LmPasswordPresent = FALSE;
7622 BOOLEAN WriteFixedData = FALSE;
7624
7625 WhichFields = Buffer->All.WhichFields;
7626
7627 /* Get the fixed size attributes */
7628 Length = sizeof(SAM_USER_FIXED_DATA);
7629 Status = SampGetObjectAttribute(UserObject,
7630 L"F",
7631 NULL,
7632 (PVOID)&FixedData,
7633 &Length);
7634 if (!NT_SUCCESS(Status))
7635 goto done;
7636
7637 if (WhichFields & USER_ALL_USERNAME)
7638 {
7639 Status = SampSetUserName(UserObject,
7640 &Buffer->All.UserName);
7641 if (!NT_SUCCESS(Status))
7642 goto done;
7643 }
7644
7645 if (WhichFields & USER_ALL_FULLNAME)
7646 {
7648 L"FullName",
7649 &Buffer->All.FullName);
7650 if (!NT_SUCCESS(Status))
7651 goto done;
7652 }
7653
7654 if (WhichFields & USER_ALL_ADMINCOMMENT)
7655 {
7657 L"AdminComment",
7658 &Buffer->All.AdminComment);
7659 if (!NT_SUCCESS(Status))
7660 goto done;
7661 }
7662
7663 if (WhichFields & USER_ALL_USERCOMMENT)
7664 {
7666 L"UserComment",
7667 &Buffer->All.UserComment);
7668 if (!NT_SUCCESS(Status))
7669 goto done;
7670 }
7671
7672 if (WhichFields & USER_ALL_HOMEDIRECTORY)
7673 {
7675 L"HomeDirectory",
7676 &Buffer->All.HomeDirectory);
7677 if (!NT_SUCCESS(Status))
7678 goto done;
7679 }
7680
7681 if (WhichFields & USER_ALL_HOMEDIRECTORYDRIVE)
7682 {
7684 L"HomeDirectoryDrive",
7685 &Buffer->All.HomeDirectoryDrive);
7686 if (!NT_SUCCESS(Status))
7687 goto done;
7688 }
7689
7690 if (WhichFields & USER_ALL_SCRIPTPATH)
7691 {
7693 L"ScriptPath",
7694 &Buffer->All.ScriptPath);
7695 if (!NT_SUCCESS(Status))
7696 goto done;
7697 }
7698
7699 if (WhichFields & USER_ALL_PROFILEPATH)
7700 {
7702 L"ProfilePath",
7703 &Buffer->All.ProfilePath);
7704 if (!NT_SUCCESS(Status))
7705 goto done;
7706 }
7707
7708 if (WhichFields & USER_ALL_WORKSTATIONS)
7709 {
7711 L"WorkStations",
7712 &Buffer->All.WorkStations);
7713 if (!NT_SUCCESS(Status))
7714 goto done;
7715 }
7716
7717 if (WhichFields & USER_ALL_PARAMETERS)
7718 {
7720 L"Parameters",
7721 &Buffer->All.Parameters);
7722 if (!NT_SUCCESS(Status))
7723 goto done;
7724 }
7725
7726 if (WhichFields & USER_ALL_LOGONHOURS)
7727 {
7729 &Buffer->All.LogonHours);
7730 if (!NT_SUCCESS(Status))
7731 goto done;
7732 }
7733
7734 if (WhichFields & USER_ALL_PRIMARYGROUPID)
7735 {
7736 FixedData.PrimaryGroupId = Buffer->All.PrimaryGroupId;
7737 WriteFixedData = TRUE;
7738 }
7739
7740 if (WhichFields & USER_ALL_ACCOUNTEXPIRES)
7741 {
7742 FixedData.AccountExpires.LowPart = Buffer->All.AccountExpires.LowPart;
7743 FixedData.AccountExpires.HighPart = Buffer->All.AccountExpires.HighPart;
7744 WriteFixedData = TRUE;
7745 }
7746
7747 if (WhichFields & USER_ALL_USERACCOUNTCONTROL)
7748 {
7749 FixedData.UserAccountControl = Buffer->All.UserAccountControl;
7750 WriteFixedData = TRUE;
7751 }
7752
7753 if (WhichFields & USER_ALL_COUNTRYCODE)
7754 {
7755 FixedData.CountryCode = Buffer->All.CountryCode;
7756 WriteFixedData = TRUE;
7757 }
7758
7759 if (WhichFields & USER_ALL_CODEPAGE)
7760 {
7761 FixedData.CodePage = Buffer->All.CodePage;
7762 WriteFixedData = TRUE;
7763 }
7764
7765 if (WhichFields & (USER_ALL_NTPASSWORDPRESENT |
7767 {
7768 if (WhichFields & USER_ALL_NTPASSWORDPRESENT)
7769 {
7770 NtPassword = (PENCRYPTED_NT_OWF_PASSWORD)Buffer->All.NtOwfPassword.Buffer;
7771 NtPasswordPresent = Buffer->All.NtPasswordPresent;
7772 }
7773
7774 if (WhichFields & USER_ALL_LMPASSWORDPRESENT)
7775 {
7776 LmPassword = (PENCRYPTED_LM_OWF_PASSWORD)Buffer->All.LmOwfPassword.Buffer;
7777 LmPasswordPresent = Buffer->All.LmPasswordPresent;
7778 }
7779
7780 Status = SampSetUserPassword(UserObject,
7781 NtPassword,
7782 NtPasswordPresent,
7783 LmPassword,
7784 LmPasswordPresent);
7785 if (!NT_SUCCESS(Status))
7786 goto done;
7787
7788 /* The password has just been set */
7790 if (!NT_SUCCESS(Status))
7791 goto done;
7792
7793 WriteFixedData = TRUE;
7794 }
7795
7796 if (WhichFields & USER_ALL_PRIVATEDATA)
7797 {
7799 L"PrivateData",
7800 &Buffer->All.PrivateData);
7801 if (!NT_SUCCESS(Status))
7802 goto done;
7803 }
7804
7805 if (WhichFields & USER_ALL_PASSWORDEXPIRED)
7806 {
7807 if (Buffer->All.PasswordExpired)
7808 {
7809 /* The password was last set ages ago */
7810 FixedData.PasswordLastSet.LowPart = 0;
7811 FixedData.PasswordLastSet.HighPart = 0;
7812 }
7813 else
7814 {
7815 /* The password was last set right now */
7817 if (!NT_SUCCESS(Status))
7818 goto done;
7819 }
7820
7821 WriteFixedData = TRUE;
7822 }
7823
7824 if (WhichFields & USER_ALL_SECURITYDESCRIPTOR)
7825 {
7826 Status = SampSetObjectAttribute(UserObject,
7827 L"SecDesc",
7828 REG_BINARY,
7829 Buffer->All.SecurityDescriptor.SecurityDescriptor,
7830 Buffer->All.SecurityDescriptor.Length);
7831 }
7832
7833 if (WriteFixedData != FALSE)
7834 {
7835 Status = SampSetObjectAttribute(UserObject,
7836 L"F",
7837 REG_BINARY,
7838 &FixedData,
7839 Length);
7840 if (!NT_SUCCESS(Status))
7841 goto done;
7842 }
7843
7844done:
7845 return Status;
7846}
unsigned char BOOLEAN
Definition: actypes.h:127
NTSTATUS SampSetLogonHoursAttribute(IN PSAM_DB_OBJECT UserObject, IN PSAMPR_LOGON_HOURS LogonHours)
Definition: user.c:880
NTSTATUS SampSetUserPassword(IN PSAM_DB_OBJECT UserObject, IN PENCRYPTED_NT_OWF_PASSWORD NtPassword, IN BOOLEAN NtPasswordPresent, IN PENCRYPTED_LM_OWF_PASSWORD LmPassword, IN BOOLEAN LmPasswordPresent)
Definition: user.c:590
struct _ENCRYPTED_LM_OWF_PASSWORD * PENCRYPTED_NT_OWF_PASSWORD
struct _ENCRYPTED_LM_OWF_PASSWORD * PENCRYPTED_LM_OWF_PASSWORD
NTSTATUS NTAPI NtQuerySystemTime(OUT PLARGE_INTEGER SystemTime)
Definition: time.c:563
static NTSTATUS SampSetUserName(PSAM_DB_OBJECT UserObject, PRPC_UNICODE_STRING NewUserName)
Definition: samrpc.c:7252

Referenced by SamrSetInformationUser2().

◆ SampSetUserControl()

static NTSTATUS SampSetUserControl ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER  Buffer 
)
static

Definition at line 7443 of file samrpc.c.

7445{
7446 SAM_USER_FIXED_DATA FixedData;
7447 ULONG Length = 0;
7449
7450 Length = sizeof(SAM_USER_FIXED_DATA);
7451 Status = SampGetObjectAttribute(UserObject,
7452 L"F",
7453 NULL,
7454 (PVOID)&FixedData,
7455 &Length);
7456 if (!NT_SUCCESS(Status))
7457 goto done;
7458
7459 FixedData.UserAccountControl = Buffer->Control.UserAccountControl;
7460
7461 Status = SampSetObjectAttribute(UserObject,
7462 L"F",
7463 REG_BINARY,
7464 &FixedData,
7465 Length);
7466
7467done:
7468 return Status;
7469}

Referenced by SamrSetInformationUser2().

◆ SampSetUserExpires()

static NTSTATUS SampSetUserExpires ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER  Buffer 
)
static

Definition at line 7473 of file samrpc.c.

7475{
7476 SAM_USER_FIXED_DATA FixedData;
7477 ULONG Length = 0;
7479
7480 Length = sizeof(SAM_USER_FIXED_DATA);
7481 Status = SampGetObjectAttribute(UserObject,
7482 L"F",
7483 NULL,
7484 (PVOID)&FixedData,
7485 &Length);
7486 if (!NT_SUCCESS(Status))
7487 goto done;
7488
7489 FixedData.AccountExpires.LowPart = Buffer->Expires.AccountExpires.LowPart;
7490 FixedData.AccountExpires.HighPart = Buffer->Expires.AccountExpires.HighPart;
7491
7492 Status = SampSetObjectAttribute(UserObject,
7493 L"F",
7494 REG_BINARY,
7495 &FixedData,
7496 Length);
7497
7498done:
7499 return Status;
7500}

Referenced by SamrSetInformationUser2().

◆ SampSetUserGeneral()

static NTSTATUS SampSetUserGeneral ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER  Buffer 
)
static

Definition at line 7323 of file samrpc.c.

7325{
7326 SAM_USER_FIXED_DATA FixedData;
7327 ULONG Length = 0;
7329
7330 Length = sizeof(SAM_USER_FIXED_DATA);
7331 Status = SampGetObjectAttribute(UserObject,
7332 L"F",
7333 NULL,
7334 (PVOID)&FixedData,
7335 &Length);
7336 if (!NT_SUCCESS(Status))
7337 goto done;
7338
7339 FixedData.PrimaryGroupId = Buffer->General.PrimaryGroupId;
7340
7341 Status = SampSetObjectAttribute(UserObject,
7342 L"F",
7343 REG_BINARY,
7344 &FixedData,
7345 Length);
7346 if (!NT_SUCCESS(Status))
7347 goto done;
7348
7349 Status = SampSetUserName(UserObject,
7350 &Buffer->General.UserName);
7351 if (!NT_SUCCESS(Status))
7352 goto done;
7353
7355 L"FullName",
7356 &Buffer->General.FullName);
7357 if (!NT_SUCCESS(Status))
7358 goto done;
7359
7361 L"AdminComment",
7362 &Buffer->General.AdminComment);
7363 if (!NT_SUCCESS(Status))
7364 goto done;
7365
7367 L"UserComment",
7368 &Buffer->General.UserComment);
7369
7370done:
7371 return Status;
7372}

Referenced by SamrSetInformationUser2().

◆ SampSetUserInternal1()

static NTSTATUS SampSetUserInternal1 ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER  Buffer 
)
static

Definition at line 7504 of file samrpc.c.

7506{
7507 SAM_USER_FIXED_DATA FixedData;
7508 ULONG Length = 0;
7510
7511 /* FIXME: Decrypt NT password */
7512 /* FIXME: Decrypt LM password */
7513
7514 Status = SampSetUserPassword(UserObject,
7515 &Buffer->Internal1.EncryptedNtOwfPassword,
7516 Buffer->Internal1.NtPasswordPresent,
7517 &Buffer->Internal1.EncryptedLmOwfPassword,
7518 Buffer->Internal1.LmPasswordPresent);
7519 if (!NT_SUCCESS(Status))
7520 goto done;
7521
7522 /* Get the fixed user attributes */
7523 Length = sizeof(SAM_USER_FIXED_DATA);
7524 Status = SampGetObjectAttribute(UserObject,
7525 L"F",
7526 NULL,
7527 (PVOID)&FixedData,
7528 &Length);
7529 if (!NT_SUCCESS(Status))
7530 goto done;
7531
7532 if (Buffer->Internal1.PasswordExpired)
7533 {
7534 /* The password was last set ages ago */
7535 FixedData.PasswordLastSet.LowPart = 0;
7536 FixedData.PasswordLastSet.HighPart = 0;
7537 }
7538 else
7539 {
7540 /* The password was last set right now */
7542 if (!NT_SUCCESS(Status))
7543 goto done;
7544 }
7545
7546 /* Set the fixed user attributes */
7547 Status = SampSetObjectAttribute(UserObject,
7548 L"F",
7549 REG_BINARY,
7550 &FixedData,
7551 Length);
7552
7553done:
7554 return Status;
7555}

Referenced by SamrSetInformationUser2().

◆ SampSetUserInternal2()

static NTSTATUS SampSetUserInternal2 ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER  Buffer 
)
static

Definition at line 7559 of file samrpc.c.

7561{
7562 SAM_USER_FIXED_DATA FixedData;
7563 ULONG Length = 0;
7565
7566 /* Get the fixed user attributes */
7567 Length = sizeof(SAM_USER_FIXED_DATA);
7568 Status = SampGetObjectAttribute(UserObject,
7569 L"F",
7570 NULL,
7571 (PVOID)&FixedData,
7572 &Length);
7573 if (!NT_SUCCESS(Status))
7574 goto done;
7575
7576 if ((Buffer->Internal2.Flags & USER_LOGON_SUCCESS) &&
7577 ((Buffer->Internal2.Flags & ~USER_LOGON_SUCCESS) == 0))
7578 {
7579 /* Update the LastLogon time */
7580 Status = NtQuerySystemTime(&FixedData.LastLogon);
7581 if (!NT_SUCCESS(Status))
7582 goto done;
7583
7584 FixedData.LogonCount++;
7585 FixedData.BadPasswordCount = 0;
7586 }
7587
7588 if ((Buffer->Internal2.Flags & USER_LOGON_BAD_PASSWORD) &&
7589 ((Buffer->Internal2.Flags & ~USER_LOGON_BAD_PASSWORD) == 0))
7590 {
7591 /* Update the LastBadPasswordTime */
7593 if (!NT_SUCCESS(Status))
7594 goto done;
7595
7596 FixedData.BadPasswordCount++;
7597 }
7598
7599 /* Set the fixed user attributes */
7600 Status = SampSetObjectAttribute(UserObject,
7601 L"F",
7602 REG_BINARY,
7603 &FixedData,
7604 Length);
7605
7606done:
7607 return Status;
7608}
#define USER_LOGON_SUCCESS
Definition: sam.idl:649
#define USER_LOGON_BAD_PASSWORD
Definition: sam.idl:648
LARGE_INTEGER LastBadPasswordTime
Definition: samsrv.h:106

Referenced by SamrSetInformationUser2().

◆ SampSetUserName()

static NTSTATUS SampSetUserName ( PSAM_DB_OBJECT  UserObject,
PRPC_UNICODE_STRING  NewUserName 
)
static

Definition at line 7252 of file samrpc.c.

7254{
7255 UNICODE_STRING OldUserName = {0, 0, NULL};
7257
7258 /* Check the account name */
7259 Status = SampCheckAccountName(NewUserName, 20);
7260 if (!NT_SUCCESS(Status))
7261 {
7262 TRACE("SampCheckAccountName failed (Status 0x%08lx)\n", Status);
7263 return Status;
7264 }
7265
7267 L"Name",
7268 (PRPC_UNICODE_STRING)&OldUserName);
7269 if (!NT_SUCCESS(Status))
7270 {
7271 TRACE("SampGetObjectAttributeString failed (Status 0x%08lx)\n", Status);
7272 goto done;
7273 }
7274
7275 if (!RtlEqualUnicodeString(&OldUserName, (PCUNICODE_STRING)NewUserName, TRUE))
7276 {
7278 NewUserName->Buffer);
7279 if (!NT_SUCCESS(Status))
7280 {
7281 TRACE("User name \'%S\' already exists in domain (Status 0x%08lx)\n",
7282 NewUserName->Buffer, Status);
7283 goto done;
7284 }
7285 }
7286
7288 L"Users",
7289 NewUserName->Buffer,
7290 UserObject->RelativeId);
7291 if (!NT_SUCCESS(Status))
7292 {
7293 TRACE("SampSetAccountNameInDomain failed (Status 0x%08lx)\n", Status);
7294 goto done;
7295 }
7296
7298 L"Users",
7299 OldUserName.Buffer);
7300 if (!NT_SUCCESS(Status))
7301 {
7302 TRACE("SampRemoveAccountNameFromDomain failed (Status 0x%08lx)\n", Status);
7303 goto done;
7304 }
7305
7307 L"Name",
7308 NewUserName);
7309 if (!NT_SUCCESS(Status))
7310 {
7311 TRACE("SampSetObjectAttribute failed (Status 0x%08lx)\n", Status);
7312 }
7313
7314done:
7315 if (OldUserName.Buffer != NULL)
7316 midl_user_free(OldUserName.Buffer);
7317
7318 return Status;
7319}

Referenced by SampSetUserAll(), SampSetUserGeneral(), and SamrSetInformationUser2().

◆ SampSetUserPreferences()

static NTSTATUS SampSetUserPreferences ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER  Buffer 
)
static

Definition at line 7376 of file samrpc.c.

7378{
7379 SAM_USER_FIXED_DATA FixedData;
7380 ULONG Length = 0;
7382
7383 Length = sizeof(SAM_USER_FIXED_DATA);
7384 Status = SampGetObjectAttribute(UserObject,
7385 L"F",
7386 NULL,
7387 (PVOID)&FixedData,
7388 &Length);
7389 if (!NT_SUCCESS(Status))
7390 goto done;
7391
7392 FixedData.CountryCode = Buffer->Preferences.CountryCode;
7393 FixedData.CodePage = Buffer->Preferences.CodePage;
7394
7395 Status = SampSetObjectAttribute(UserObject,
7396 L"F",
7397 REG_BINARY,
7398 &FixedData,
7399 Length);
7400 if (!NT_SUCCESS(Status))
7401 goto done;
7402
7404 L"UserComment",
7405 &Buffer->Preferences.UserComment);
7406
7407done:
7408 return Status;
7409}

Referenced by SamrSetInformationUser2().

◆ SampSetUserPrimaryGroup()

static NTSTATUS SampSetUserPrimaryGroup ( PSAM_DB_OBJECT  UserObject,
PSAMPR_USER_INFO_BUFFER  Buffer 
)
static

Definition at line 7413 of file samrpc.c.

7415{
7416 SAM_USER_FIXED_DATA FixedData;
7417 ULONG Length = 0;
7419
7420 Length = sizeof(SAM_USER_FIXED_DATA);
7421 Status = SampGetObjectAttribute(UserObject,
7422 L"F",
7423 NULL,
7424 (PVOID)&FixedData,
7425 &Length);
7426 if (!NT_SUCCESS(Status))
7427 goto done;
7428
7429 FixedData.PrimaryGroupId = Buffer->PrimaryGroup.PrimaryGroupId;
7430
7431 Status = SampSetObjectAttribute(UserObject,
7432 L"F",
7433 REG_BINARY,
7434 &FixedData,
7435 Length);
7436
7437done:
7438 return Status;
7439}

Referenced by SamrSetInformationUser2().

◆ SampStartRpcServer()

VOID SampStartRpcServer ( VOID  )

Definition at line 78 of file samrpc.c.

79{
81
82 TRACE("SampStartRpcServer() called\n");
83
86 L"\\pipe\\samr",
87 NULL);
88 if (Status != RPC_S_OK)
89 {
90 WARN("RpcServerUseProtseqEpW() failed (Status %lx)\n", Status);
91 return;
92 }
93
94 Status = RpcServerRegisterIf(samr_v1_0_s_ifspec,
95 NULL,
96 NULL);
97 if (Status != RPC_S_OK)
98 {
99 WARN("RpcServerRegisterIf() failed (Status %lx)\n", Status);
100 return;
101 }
102
103 Status = RpcServerListen(1, 20, TRUE);
104 if (Status != RPC_S_OK)
105 {
106 WARN("RpcServerListen() failed (Status %lx)\n", Status);
107 return;
108 }
109
110 TRACE("SampStartRpcServer() done\n");
111}
#define WARN(fmt,...)
Definition: precomp.h:61
RPC_STATUS WINAPI RpcServerListen(UINT MinimumCallThreads, UINT MaxCalls, UINT DontWait)
Definition: rpc_server.c:1520
RPC_STATUS WINAPI RpcServerRegisterIf(RPC_IF_HANDLE IfSpec, UUID *MgrTypeUuid, RPC_MGR_EPV *MgrEpv)
Definition: rpc_server.c:1116
RPC_STATUS WINAPI RpcServerUseProtseqEpW(RPC_WSTR Protseq, UINT MaxCalls, RPC_WSTR Endpoint, LPVOID SecurityDescriptor)
Definition: rpc_server.c:927
#define RPC_C_PROTSEQ_MAX_REQS_DEFAULT
Definition: rpcdce.h:123
#define RPC_S_OK
Definition: rpcnterr.h:22
long RPC_STATUS
Definition: rpc.h:48

Referenced by SamIInitialize().

◆ SamrAddMemberToAlias()

NTSTATUS NTAPI SamrAddMemberToAlias ( IN SAMPR_HANDLE  AliasHandle,
IN PRPC_SID  MemberId 
)

Definition at line 5284 of file samrpc.c.

5286{
5287 PSAM_DB_OBJECT AliasObject;
5289
5290 TRACE("SamrAddMemberToAlias(%p %p)\n",
5291 AliasHandle, MemberId);
5292
5294 TRUE);
5295
5296 /* Validate the alias handle */
5297 Status = SampValidateDbObject(AliasHandle,
5300 &AliasObject);
5301 if (!NT_SUCCESS(Status))
5302 {
5303 TRACE("failed with status 0x%08lx\n", Status);
5304 goto done;
5305 }
5306
5307 Status = SampAddMemberToAlias(AliasObject,
5308 MemberId);
5309 if (!NT_SUCCESS(Status))
5310 {
5311 TRACE("failed with status 0x%08lx\n", Status);
5312 }
5313
5314done:
5316
5317 return Status;
5318}
NTSTATUS SampAddMemberToAlias(IN PSAM_DB_OBJECT AliasObject, IN PRPC_SID MemberId)
Definition: alias.c:39
NTSTATUS SampValidateDbObject(SAMPR_HANDLE Handle, SAM_DB_OBJECT_TYPE ObjectType, ACCESS_MASK DesiredAccess, PSAM_DB_OBJECT *DbObject)
Definition: database.c:301
@ SamDbAliasObject
Definition: samsrv.h:40
NTSYSAPI BOOLEAN NTAPI RtlAcquireResourceExclusive(_In_ PRTL_RESOURCE Resource, _In_ BOOLEAN Wait)
NTSYSAPI VOID NTAPI RtlReleaseResource(_In_ PRTL_RESOURCE Resource)
#define ALIAS_ADD_MEMBER
Definition: ntsam.h:9
RTL_RESOURCE SampResource
Definition: samsrv.c:28

Referenced by SamAddMemberToAlias(), and SamrAddMultipleMembersToAlias().

◆ SamrAddMemberToGroup()

NTSTATUS NTAPI SamrAddMemberToGroup ( IN SAMPR_HANDLE  GroupHandle,
IN unsigned long  MemberId,
IN unsigned long  Attributes 
)

Definition at line 4474 of file samrpc.c.

4477{
4478 PSAM_DB_OBJECT GroupObject;
4479 PSAM_DB_OBJECT UserObject = NULL;
4481
4482 TRACE("SamrAddMemberToGroup(%p %lu %lx)\n",
4483 GroupHandle, MemberId, Attributes);
4484
4486 TRUE);
4487
4488 /* Validate the group handle */
4489 Status = SampValidateDbObject(GroupHandle,
4492 &GroupObject);
4493 if (!NT_SUCCESS(Status))
4494 goto done;
4495
4496 /* Open the user object in the same domain */
4497 Status = SampOpenUserObject(GroupObject->ParentObject,
4498 MemberId,
4499 0,
4500 &UserObject);
4501 if (!NT_SUCCESS(Status))
4502 {
4503 TRACE("SampOpenUserObject() failed (Status 0x%08lx)\n", Status);
4504 goto done;
4505 }
4506
4507 /* Add group membership to the user object */
4509 GroupObject->RelativeId,
4510 Attributes);
4511 if (!NT_SUCCESS(Status))
4512 {
4513 TRACE("SampAddGroupMembershipToUser() failed (Status 0x%08lx)\n", Status);
4514 goto done;
4515 }
4516
4517 /* Add the member to the group object */
4518 Status = SampAddMemberToGroup(GroupObject,
4519 MemberId);
4520 if (!NT_SUCCESS(Status))
4521 {
4522 TRACE("SampAddMemberToGroup() failed (Status 0x%08lx)\n", Status);
4523 }
4524
4525done:
4526 if (UserObject)
4527 SampCloseDbObject(UserObject);
4528
4530
4531 return Status;
4532}
_In_ ULONG Attributes
Definition: dispmprt.h:1077
NTSTATUS SampCloseDbObject(PSAM_DB_OBJECT DbObject)
Definition: database.c:346
NTSTATUS SampAddMemberToGroup(IN PSAM_DB_OBJECT GroupObject, IN ULONG MemberId)
Definition: group.c:39
NTSTATUS SampAddGroupMembershipToUser(IN PSAM_DB_OBJECT UserObject, IN ULONG GroupId, IN ULONG Attributes)
Definition: user.c:39
NTSTATUS SampOpenUserObject(IN PSAM_DB_OBJECT DomainObject, IN ULONG UserId, IN ACCESS_MASK DesiredAccess, OUT PSAM_DB_OBJECT *UserObject)
Definition: user.c:14
@ SamDbGroupObject
Definition: samsrv.h:41
#define GROUP_ADD_MEMBER
Definition: ntsam.h:77

Referenced by SamAddMemberToGroup().

◆ SamrAddMultipleMembersToAlias()

NTSTATUS NTAPI SamrAddMultipleMembersToAlias ( IN SAMPR_HANDLE  AliasHandle,
IN PSAMPR_PSID_ARRAY  MembersBuffer 
)

Definition at line 9296 of file samrpc.c.

9298{
9299 ULONG i;
9301
9302 TRACE("SamrAddMultipleMembersToAlias(%p %p)\n",
9303 AliasHandle, MembersBuffer);
9304
9305 for (i = 0; i < MembersBuffer->Count; i++)
9306 {
9307 Status = SamrAddMemberToAlias(AliasHandle,
9308 ((PSID *)MembersBuffer->Sids)[i]);
9309
9312
9313 if (!NT_SUCCESS(Status))
9314 break;
9315 }
9316
9317 return Status;
9318}
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble const GLfloat const GLdouble const GLfloat GLint i
Definition: glfuncs.h:248
#define STATUS_MEMBER_IN_ALIAS
Definition: ntstatus.h:669
NTSTATUS NTAPI SamrAddMemberToAlias(IN SAMPR_HANDLE AliasHandle, IN PRPC_SID MemberId)
Definition: samrpc.c:5284

Referenced by SamAddMultipleMembersToAlias().

◆ SamrChangePasswordUser()

NTSTATUS NTAPI SamrChangePasswordUser ( IN SAMPR_HANDLE  UserHandle,
IN unsigned char  LmPresent,
IN PENCRYPTED_LM_OWF_PASSWORD  OldLmEncryptedWithNewLm,
IN PENCRYPTED_LM_OWF_PASSWORD  NewLmEncryptedWithOldLm,
IN unsigned char  NtPresent,
IN PENCRYPTED_NT_OWF_PASSWORD  OldNtEncryptedWithNewNt,
IN PENCRYPTED_NT_OWF_PASSWORD  NewNtEncryptedWithOldNt,
IN unsigned char  NtCrossEncryptionPresent,
IN PENCRYPTED_NT_OWF_PASSWORD  NewNtEncryptedWithNewLm,
IN unsigned char  LmCrossEncryptionPresent,
IN PENCRYPTED_LM_OWF_PASSWORD  NewLmEncryptedWithNewNt 
)

Definition at line 7868 of file samrpc.c.

7879{
7880 ENCRYPTED_LM_OWF_PASSWORD StoredLmPassword;
7881 ENCRYPTED_NT_OWF_PASSWORD StoredNtPassword;
7882 LM_OWF_PASSWORD OldLmPassword;
7883 LM_OWF_PASSWORD NewLmPassword;
7884 NT_OWF_PASSWORD OldNtPassword;
7885 NT_OWF_PASSWORD NewNtPassword;
7886 BOOLEAN StoredLmPresent = FALSE;
7887 BOOLEAN StoredNtPresent = FALSE;
7888 BOOLEAN StoredLmEmpty = TRUE;
7889 BOOLEAN StoredNtEmpty = TRUE;
7890 PSAM_DB_OBJECT UserObject;
7891 ULONG Length;
7892 SAM_USER_FIXED_DATA UserFixedData;
7893 SAM_DOMAIN_FIXED_DATA DomainFixedData;
7894 LARGE_INTEGER SystemTime;
7896
7897 DBG_UNREFERENCED_LOCAL_VARIABLE(StoredLmPresent);
7898 DBG_UNREFERENCED_LOCAL_VARIABLE(StoredNtPresent);
7899 DBG_UNREFERENCED_LOCAL_VARIABLE(StoredLmEmpty);
7900
7901 TRACE("SamrChangePasswordUser(%p %u %p %p %u %p %p %u %p %u %p)\n",
7902 UserHandle, LmPresent, OldLmEncryptedWithNewLm, NewLmEncryptedWithOldLm,
7903 NtPresent, OldNtEncryptedWithNewNt, NewNtEncryptedWithOldNt, NtCrossEncryptionPresent,
7904 NewNtEncryptedWithNewLm, LmCrossEncryptionPresent, NewLmEncryptedWithNewNt);
7905
7907 TRUE);
7908
7909 /* Validate the user handle */
7910 Status = SampValidateDbObject(UserHandle,
7913 &UserObject);
7914 if (!NT_SUCCESS(Status))
7915 {
7916 TRACE("SampValidateDbObject failed with status 0x%08lx\n", Status);
7917 goto done;
7918 }
7919
7920 /* Get the current time */
7921 Status = NtQuerySystemTime(&SystemTime);
7922 if (!NT_SUCCESS(Status))
7923 {
7924 TRACE("NtQuerySystemTime failed (Status 0x%08lx)\n", Status);
7925 goto done;
7926 }
7927
7928 /* Retrieve the LM password */
7930 Status = SampGetObjectAttribute(UserObject,
7931 L"LMPwd",
7932 NULL,
7933 &StoredLmPassword,
7934 &Length);
7935 if (NT_SUCCESS(Status))
7936 {
7937 if (Length == sizeof(ENCRYPTED_LM_OWF_PASSWORD))
7938 {
7939 StoredLmPresent = TRUE;
7940 if (!RtlEqualMemory(&StoredLmPassword,
7941 &EmptyLmHash,
7943 StoredLmEmpty = FALSE;
7944 }
7945 }
7946
7947 /* Retrieve the NT password */
7949 Status = SampGetObjectAttribute(UserObject,
7950 L"NTPwd",
7951 NULL,
7952 &StoredNtPassword,
7953 &Length);
7954 if (NT_SUCCESS(Status))
7955 {
7956 if (Length == sizeof(ENCRYPTED_NT_OWF_PASSWORD))
7957 {
7958 StoredNtPresent = TRUE;
7959 if (!RtlEqualMemory(&StoredNtPassword,
7960 &EmptyNtHash,
7962 StoredNtEmpty = FALSE;
7963 }
7964 }
7965
7966 /* Retrieve the fixed size user data */
7967 Length = sizeof(SAM_USER_FIXED_DATA);
7968 Status = SampGetObjectAttribute(UserObject,
7969 L"F",
7970 NULL,
7971 &UserFixedData,
7972 &Length);
7973 if (!NT_SUCCESS(Status))
7974 {
7975 TRACE("SampGetObjectAttribute failed to retrieve the fixed user data (Status 0x%08lx)\n", Status);
7976 goto done;
7977 }
7978
7979 /* Check if we can change the password at this time */
7980 if ((StoredLmEmpty == FALSE) || (StoredNtEmpty == FALSE))
7981 {
7982 /* Get fixed domain data */
7983 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
7985 L"F",
7986 NULL,
7987 &DomainFixedData,
7988 &Length);
7989 if (!NT_SUCCESS(Status))
7990 {
7991 TRACE("SampGetObjectAttribute failed to retrieve the fixed domain data (Status 0x%08lx)\n", Status);
7992 goto done;
7993 }
7994
7995 if (DomainFixedData.MinPasswordAge.QuadPart > 0)
7996 {
7997 if (SystemTime.QuadPart < (UserFixedData.PasswordLastSet.QuadPart + DomainFixedData.MinPasswordAge.QuadPart))
7998 {
8000 goto done;
8001 }
8002 }
8003 }
8004
8005 /* Decrypt the LM passwords, if present */
8006 if (LmPresent)
8007 {
8008 Status = SystemFunction013((const BYTE *)NewLmEncryptedWithOldLm,
8009 (const BYTE *)&StoredLmPassword,
8010 (LPBYTE)&NewLmPassword);
8011 if (!NT_SUCCESS(Status))
8012 {
8013 TRACE("SystemFunction013 failed (Status 0x%08lx)\n", Status);
8014 goto done;
8015 }
8016
8017 Status = SystemFunction013((const BYTE *)OldLmEncryptedWithNewLm,
8018 (const BYTE *)&NewLmPassword,
8019 (LPBYTE)&OldLmPassword);
8020 if (!NT_SUCCESS(Status))
8021 {
8022 TRACE("SystemFunction013 failed (Status 0x%08lx)\n", Status);
8023 goto done;
8024 }
8025 }
8026
8027 /* Decrypt the NT passwords, if present */
8028 if (NtPresent)
8029 {
8030 Status = SystemFunction013((const BYTE *)NewNtEncryptedWithOldNt,
8031 (const BYTE *)&StoredNtPassword,
8032 (LPBYTE)&NewNtPassword);
8033 if (!NT_SUCCESS(Status))
8034 {
8035 TRACE("SystemFunction013 failed (Status 0x%08lx)\n", Status);
8036 goto done;
8037 }
8038
8039 Status = SystemFunction013((const BYTE *)OldNtEncryptedWithNewNt,
8040 (const BYTE *)&NewNtPassword,
8041 (LPBYTE)&OldNtPassword);
8042 if (!NT_SUCCESS(Status))
8043 {
8044 TRACE("SystemFunction013 failed (Status 0x%08lx)\n", Status);
8045 goto done;
8046 }
8047 }
8048
8049 /* Check if the old passwords match the stored ones */
8050 if (NtPresent)
8051 {
8052 if (LmPresent)
8053 {
8054 if (!RtlEqualMemory(&StoredLmPassword,
8055 &OldLmPassword,
8057 {
8058 TRACE("Old LM Password does not match!\n");
8060 }
8061 else
8062 {
8063 if (!RtlEqualMemory(&StoredNtPassword,
8064 &OldNtPassword,
8066 {
8067 TRACE("Old NT Password does not match!\n");
8069 }
8070 }
8071 }
8072 else
8073 {
8074 if (!RtlEqualMemory(&StoredNtPassword,
8075 &OldNtPassword,
8077 {
8078 TRACE("Old NT Password does not match!\n");
8080 }
8081 }
8082 }
8083 else
8084 {
8085 if (LmPresent)
8086 {
8087 if (!RtlEqualMemory(&StoredLmPassword,
8088 &OldLmPassword,
8090 {
8091 TRACE("Old LM Password does not match!\n");
8093 }
8094 }
8095 else
8096 {
8098 }
8099 }
8100
8101 /* Store the new password hashes */
8102 if (NT_SUCCESS(Status))
8103 {
8104 Status = SampSetUserPassword(UserObject,
8105 &NewNtPassword,
8106 NtPresent,
8107 &NewLmPassword,
8108 LmPresent);
8109 if (NT_SUCCESS(Status))
8110 {
8111 /* Update PasswordLastSet */
8112 UserFixedData.PasswordLastSet.QuadPart = SystemTime.QuadPart;
8113
8114 /* Set the fixed size user data */
8115 Length = sizeof(SAM_USER_FIXED_DATA);
8116 Status = SampSetObjectAttribute(UserObject,
8117 L"F",
8118 REG_BINARY,
8119 &UserFixedData,
8120 Length);
8121 }
8122 }
8123
8125 {
8126 /* Update BadPasswordCount and LastBadPasswordTime */
8127 UserFixedData.BadPasswordCount++;
8128 UserFixedData.LastBadPasswordTime.QuadPart = SystemTime.QuadPart;
8129
8130 /* Set the fixed size user data */
8131 Length = sizeof(SAM_USER_FIXED_DATA);
8132 Status = SampSetObjectAttribute(UserObject,
8133 L"F",
8134 REG_BINARY,
8135 &UserFixedData,
8136 Length);
8137 }
8138
8139done:
8141
8142 return Status;
8143}
@ SamDbUserObject
Definition: samsrv.h:42
#define RtlEqualMemory(dst, src, len)
Definition: kdvm.h:18
#define DBG_UNREFERENCED_LOCAL_VARIABLE(L)
Definition: ntbasedef.h:331
#define USER_CHANGE_PASSWORD
Definition: ntsam.h:132
#define STATUS_WRONG_PASSWORD
Definition: ntstatus.h:436
#define STATUS_ACCOUNT_RESTRICTION
Definition: ntstatus.h:440
NTSTATUS WINAPI SystemFunction013(const BYTE *in, const BYTE *key, LPBYTE out)
Definition: sysfunc.c:383
unsigned char * LPBYTE
Definition: typedefs.h:53
#define STATUS_INVALID_PARAMETER
Definition: udferr_usr.h:135
unsigned char BYTE
Definition: xxhash.c:193

Referenced by MsvpChangePassword(), and SamChangePasswordUser().

◆ SamrCloseHandle()

NTSTATUS NTAPI SamrCloseHandle ( IN OUT SAMPR_HANDLE *  SamHandle)

Definition at line 161 of file samrpc.c.

162{
163 PSAM_DB_OBJECT DbObject;
165
166 TRACE("SamrCloseHandle(%p)\n", SamHandle);
167
169 TRUE);
170
171 Status = SampValidateDbObject(*SamHandle,
173 0,
174 &DbObject);
175 if (Status == STATUS_SUCCESS)
176 {
177 Status = SampCloseDbObject(DbObject);
178 *SamHandle = NULL;
179 }
180
182
183 TRACE("SamrCloseHandle done (Status 0x%08lx)\n", Status);
184
185 return Status;
186}
@ SamDbIgnoreObject
Definition: samsrv.h:37
NTSYSAPI BOOLEAN NTAPI RtlAcquireResourceShared(_In_ PRTL_RESOURCE Resource, _In_ BOOLEAN Wait)

Referenced by LsapLookupAccountDomainSids(), LsapLookupAccountNames(), LsapLookupBuiltinDomainSids(), LsapLookupBuiltinNames(), LsapLookupIsolatedAccountNames(), LsapLookupIsolatedBuiltinNames(), and SamrGetDomainPasswordInformation().

◆ SamrConnect()

NTSTATUS NTAPI SamrConnect ( IN PSAMPR_SERVER_NAME  ServerName,
OUT SAMPR_HANDLE *  ServerHandle,
IN ACCESS_MASK  DesiredAccess 
)

Definition at line 135 of file samrpc.c.

138{
139 SAMPR_REVISION_INFO InRevisionInfo, OutRevisionInfo;
140 ULONG OutVersion;
141
142 TRACE("SamrConnect(%p %p %lx)\n",
143 ServerName, ServerHandle, DesiredAccess);
144
145 InRevisionInfo.V1.Revision = 0;
146 InRevisionInfo.V1.SupportedFeatures = 0;
147
148 return SamrConnect5(ServerName,
150 1,
151 &InRevisionInfo,
152 &OutVersion,
153 &OutRevisionInfo,
154 ServerHandle);
155}
union @4363 SAMPR_REVISION_INFO
NTSTATUS NTAPI SamrConnect5(IN PSAMPR_SERVER_NAME ServerName, IN ACCESS_MASK DesiredAccess, IN unsigned long InVersion, IN SAMPR_REVISION_INFO *InRevisionInfo, OUT unsigned long *OutVersion, OUT SAMPR_REVISION_INFO *OutRevisionInfo, OUT SAMPR_HANDLE *ServerHandle)
Definition: samrpc.c:9742
_Must_inspect_result_ _In_ WDFDEVICE _In_ ULONG _In_ ACCESS_MASK DesiredAccess
Definition: wdfdevice.h:2664

Referenced by LsapLookupAccountDomainSids(), LsapLookupAccountNames(), LsapLookupBuiltinDomainSids(), LsapLookupBuiltinNames(), LsapLookupIsolatedAccountNames(), LsapLookupIsolatedBuiltinNames(), SamConnect(), and SamrGetDomainPasswordInformation().

◆ SamrConnect2()

NTSTATUS NTAPI SamrConnect2 ( IN PSAMPR_SERVER_NAME  ServerName,
OUT SAMPR_HANDLE *  ServerHandle,
IN ACCESS_MASK  DesiredAccess 
)

Definition at line 9446 of file samrpc.c.

9449{
9450 SAMPR_REVISION_INFO InRevisionInfo, OutRevisionInfo;
9451 ULONG OutVersion;
9452
9453 TRACE("SamrConnect2(%p %p %lx)\n",
9454 ServerName, ServerHandle, DesiredAccess);
9455
9456 InRevisionInfo.V1.Revision = 1;
9457 InRevisionInfo.V1.SupportedFeatures = 0;
9458
9459 return SamrConnect5(ServerName,
9461 1,
9462 &InRevisionInfo,
9463 &OutVersion,
9464 &OutRevisionInfo,
9465 ServerHandle);
9466}

◆ SamrConnect3()

NTSTATUS NTAPI SamrConnect3 ( IN handle_t  BindingHandle)

Definition at line 9695 of file samrpc.c.

9696{
9699}
#define UNIMPLEMENTED
Definition: ntoskrnl.c:15
#define STATUS_NOT_IMPLEMENTED
Definition: d3dkmdt.h:42

◆ SamrConnect4()

NTSTATUS NTAPI SamrConnect4 ( IN PSAMPR_SERVER_NAME  ServerName,
OUT SAMPR_HANDLE *  ServerHandle,
IN unsigned long  ClientRevision,
IN ACCESS_MASK  DesiredAccess 
)

Definition at line 9705 of file samrpc.c.

9709{
9710 SAMPR_REVISION_INFO InRevisionInfo, OutRevisionInfo;
9711 ULONG OutVersion;
9712
9713 TRACE("SamrConnect4(%p %p %lu 0x%lx)\n",
9714 ServerName, ServerHandle, ClientRevision, DesiredAccess);
9715
9716 InRevisionInfo.V1.Revision = 2;
9717 InRevisionInfo.V1.SupportedFeatures = 0;
9718
9719 return SamrConnect5(ServerName,
9721 1,
9722 &InRevisionInfo,
9723 &OutVersion,
9724 &OutRevisionInfo,
9725 ServerHandle);
9726}

◆ SamrConnect5()

NTSTATUS NTAPI SamrConnect5 ( IN PSAMPR_SERVER_NAME  ServerName,
IN ACCESS_MASK  DesiredAccess,
IN unsigned long  InVersion,
IN SAMPR_REVISION_INFO *  InRevisionInfo,
OUT unsigned long *  OutVersion,
OUT SAMPR_REVISION_INFO *  OutRevisionInfo,
OUT SAMPR_HANDLE *  ServerHandle 
)

Definition at line 9742 of file samrpc.c.

9749{
9750 PSAM_DB_OBJECT ServerObject;
9752
9753 TRACE("SamrConnect5(%p 0x%lx %lu %p %p %p %p)\n",
9754 ServerName, DesiredAccess, InVersion, InRevisionInfo,
9755 OutVersion, OutRevisionInfo, ServerHandle);
9756
9757 if (InVersion != 1)
9758 return STATUS_NOT_SUPPORTED;
9759
9761 TRUE);
9762
9763 /* Map generic access rights */
9765 &ServerMapping);
9766
9767 /* Open the Server Object */
9769 NULL,
9770 L"SAM",
9771 0,
9774 &ServerObject);
9775 if (NT_SUCCESS(Status))
9776 {
9777 *OutVersion = 1;
9778
9779 OutRevisionInfo->V1.Revision = 3;
9780 OutRevisionInfo->V1.SupportedFeatures = 0;
9781
9782 *ServerHandle = (SAMPR_HANDLE)ServerObject;
9783 }
9784
9786
9787 TRACE("SamrConnect5 done (Status 0x%08lx)\n", Status);
9788
9789 return Status;
9790}
void * SAMPR_HANDLE
Definition: authpackage.c:113
#define STATUS_NOT_SUPPORTED
Definition: d3dkmdt.h:48
NTSTATUS SampOpenDbObject(IN PSAM_DB_OBJECT ParentObject, IN LPWSTR ContainerName, IN LPWSTR ObjectName, IN ULONG RelativeId, IN SAM_DB_OBJECT_TYPE ObjectType, IN ACCESS_MASK DesiredAccess, OUT PSAM_DB_OBJECT *DbObject)
Definition: database.c:173
@ SamDbServerObject
Definition: samsrv.h:38
NTSYSAPI VOID NTAPI RtlMapGenericMask(PACCESS_MASK AccessMask, PGENERIC_MAPPING GenericMapping)
static GENERIC_MAPPING ServerMapping
Definition: samrpc.c:16

Referenced by SamrConnect(), SamrConnect2(), and SamrConnect4().

◆ SamrCreateAliasInDomain()

NTSTATUS NTAPI SamrCreateAliasInDomain ( IN SAMPR_HANDLE  DomainHandle,
IN PRPC_UNICODE_STRING  AccountName,
IN ACCESS_MASK  DesiredAccess,
OUT SAMPR_HANDLE *  AliasHandle,
OUT unsigned long *  RelativeId 
)

Definition at line 2913 of file samrpc.c.

2918{
2919 SAM_DOMAIN_FIXED_DATA FixedDomainData;
2920 PSAM_DB_OBJECT DomainObject;
2921 PSAM_DB_OBJECT AliasObject;
2923 ULONG SdSize = 0;
2924 ULONG ulSize;
2925 ULONG ulRid;
2926 WCHAR szRid[9];
2928
2929 TRACE("SamrCreateAliasInDomain(%p %p %lx %p %p)\n",
2930 DomainHandle, AccountName, DesiredAccess, AliasHandle, RelativeId);
2931
2932 /* Map generic access rights */
2934 &AliasMapping);
2935
2937 TRUE);
2938
2939 /* Validate the domain handle */
2940 Status = SampValidateDbObject(DomainHandle,
2943 &DomainObject);
2944 if (!NT_SUCCESS(Status))
2945 {
2946 TRACE("failed with status 0x%08lx\n", Status);
2947 goto done;
2948 }
2949
2950 /* Check the alias account name */
2951 Status = SampCheckAccountName(AccountName, 256);
2952 if (!NT_SUCCESS(Status))
2953 {
2954 TRACE("SampCheckAccountName failed (Status 0x%08lx)\n", Status);
2955 goto done;
2956 }
2957
2958 /* Check if the alias name already exists in the domain */
2959 Status = SampCheckAccountNameInDomain(DomainObject,
2960 AccountName->Buffer);
2961 if (!NT_SUCCESS(Status))
2962 {
2963 TRACE("Alias name \'%S\' already exists in domain (Status 0x%08lx)\n",
2964 AccountName->Buffer, Status);
2965 goto done;
2966 }
2967
2968 /* Create the security descriptor */
2970 &SdSize);
2971 if (!NT_SUCCESS(Status))
2972 {
2973 TRACE("SampCreateAliasSD failed (Status 0x%08lx)\n", Status);
2974 goto done;
2975 }
2976
2977 /* Get the fixed domain attributes */
2978 ulSize = sizeof(SAM_DOMAIN_FIXED_DATA);
2979 Status = SampGetObjectAttribute(DomainObject,
2980 L"F",
2981 NULL,
2982 (PVOID)&FixedDomainData,
2983 &ulSize);
2984 if (!NT_SUCCESS(Status))
2985 {
2986 TRACE("failed with status 0x%08lx\n", Status);
2987 goto done;
2988 }
2989
2990 /* Increment the NextRid attribute */
2991 ulRid = FixedDomainData.NextRid;
2992 FixedDomainData.NextRid++;
2993
2994 /* Store the fixed domain attributes */
2995 Status = SampSetObjectAttribute(DomainObject,
2996 L"F",
2997 REG_BINARY,
2998 &FixedDomainData,
2999 ulSize);
3000 if (!NT_SUCCESS(Status))
3001 {
3002 TRACE("failed with status 0x%08lx\n", Status);
3003 goto done;
3004 }
3005
3006 TRACE("RID: %lx\n", ulRid);
3007
3008 /* Convert the RID into a string (hex) */
3009 _swprintf(szRid, L"%08lX", ulRid);
3010
3011 /* Create the alias object */
3012 Status = SampCreateDbObject(DomainObject,
3013 L"Aliases",
3014 szRid,
3015 ulRid,
3018 &AliasObject);
3019 if (!NT_SUCCESS(Status))
3020 {
3021 TRACE("failed with status 0x%08lx\n", Status);
3022 goto done;
3023 }
3024
3025 /* Add the account name for the alias object */
3026 Status = SampSetAccountNameInDomain(DomainObject,
3027 L"Aliases",
3028 AccountName->Buffer,
3029 ulRid);
3030 if (!NT_SUCCESS(Status))
3031 {
3032 TRACE("failed with status 0x%08lx\n", Status);
3033 goto done;
3034 }
3035
3036 /* Set the Name attribute */
3038 L"Name",
3039 AccountName);
3040 if (!NT_SUCCESS(Status))
3041 {
3042 TRACE("failed with status 0x%08lx\n", Status);
3043 goto done;
3044 }
3045
3046 /* Set the Description attribute */
3048 L"Description",
3049 NULL);
3050 if (!NT_SUCCESS(Status))
3051 {
3052 TRACE("failed with status 0x%08lx\n", Status);
3053 goto done;
3054 }
3055
3056 /* Set the SecDesc attribute*/
3057 Status = SampSetObjectAttribute(AliasObject,
3058 L"SecDesc",
3059 REG_BINARY,
3060 Sd,
3061 SdSize);
3062 if (!NT_SUCCESS(Status))
3063 {
3064 TRACE("failed with status 0x%08lx\n", Status);
3065 goto done;
3066 }
3067
3068 if (NT_SUCCESS(Status))
3069 {
3070 *AliasHandle = (SAMPR_HANDLE)AliasObject;
3071 *RelativeId = ulRid;
3072 }
3073
3074done:
3075 if (Sd != NULL)
3076 RtlFreeHeap(RtlGetProcessHeap(), 0, Sd);
3077
3079
3080 TRACE("returns with status 0x%08lx\n", Status);
3081
3082 return Status;
3083}
BOOLEAN NTAPI RtlFreeHeap(IN PVOID HeapHandle, IN ULONG Flags, IN PVOID HeapBase)
Definition: heap.c:634
NTSTATUS SampCreateDbObject(IN PSAM_DB_OBJECT ParentObject, IN LPWSTR ContainerName, IN LPWSTR ObjectName, IN ULONG RelativeId, IN SAM_DB_OBJECT_TYPE ObjectType, IN ACCESS_MASK DesiredAccess, OUT PSAM_DB_OBJECT *DbObject)
Definition: database.c:44
NTSTATUS SampCreateAliasSD(OUT PSECURITY_DESCRIPTOR *AliasSd, OUT PULONG Size)
Definition: security.c:859
@ SamDbDomainObject
Definition: samsrv.h:39
#define _swprintf(buf, format,...)
Definition: sprintf.c:56
#define DOMAIN_CREATE_ALIAS
Definition: ntsam.h:39
short WCHAR
Definition: pedump.c:58
static GENERIC_MAPPING AliasMapping
Definition: samrpc.c:32

Referenced by SamCreateAliasInDomain().

◆ SamrCreateGroupInDomain()

NTSTATUS NTAPI SamrCreateGroupInDomain ( IN SAMPR_HANDLE  DomainHandle,
IN PRPC_UNICODE_STRING  Name,
IN ACCESS_MASK  DesiredAccess,
OUT SAMPR_HANDLE *  GroupHandle,
OUT unsigned long *  RelativeId 
)

Definition at line 1898 of file samrpc.c.

1903{
1904 SAM_DOMAIN_FIXED_DATA FixedDomainData;
1905 SAM_GROUP_FIXED_DATA FixedGroupData;
1906 PSAM_DB_OBJECT DomainObject;
1907 PSAM_DB_OBJECT GroupObject;
1909 ULONG SdSize = 0;
1910 ULONG ulSize;
1911 ULONG ulRid;
1912 WCHAR szRid[9];
1914
1915 TRACE("SamrCreateGroupInDomain(%p %p %lx %p %p)\n",
1916 DomainHandle, Name, DesiredAccess, GroupHandle, RelativeId);
1917
1918 /* Map generic access rights */
1920 &GroupMapping);
1921
1923 TRUE);
1924
1925 /* Validate the domain handle */
1926 Status = SampValidateDbObject(DomainHandle,
1929 &DomainObject);
1930 if (!NT_SUCCESS(Status))
1931 {
1932 TRACE("failed with status 0x%08lx\n", Status);
1933 goto done;
1934 }
1935
1936 /* Check the group account name */
1938 if (!NT_SUCCESS(Status))
1939 {
1940 TRACE("SampCheckAccountName failed (Status 0x%08lx)\n", Status);
1941 goto done;
1942 }
1943
1944 /* Check if the group name already exists in the domain */
1945 Status = SampCheckAccountNameInDomain(DomainObject,
1946 Name->Buffer);
1947 if (!NT_SUCCESS(Status))
1948 {
1949 TRACE("Group name \'%S\' already exists in domain (Status 0x%08lx)\n",
1950 Name->Buffer, Status);
1951 goto done;
1952 }
1953
1954 /* Create the security descriptor */
1956 &SdSize);
1957 if (!NT_SUCCESS(Status))
1958 {
1959 TRACE("SampCreateGroupSD failed (Status 0x%08lx)\n", Status);
1960 goto done;
1961 }
1962
1963 /* Get the fixed domain attributes */
1964 ulSize = sizeof(SAM_DOMAIN_FIXED_DATA);
1965 Status = SampGetObjectAttribute(DomainObject,
1966 L"F",
1967 NULL,
1968 (PVOID)&FixedDomainData,
1969 &ulSize);
1970 if (!NT_SUCCESS(Status))
1971 {
1972 TRACE("failed with status 0x%08lx\n", Status);
1973 goto done;
1974 }
1975
1976 /* Increment the NextRid attribute */
1977 ulRid = FixedDomainData.NextRid;
1978 FixedDomainData.NextRid++;
1979
1980 /* Store the fixed domain attributes */
1981 Status = SampSetObjectAttribute(DomainObject,
1982 L"F",
1983 REG_BINARY,
1984 &FixedDomainData,
1985 ulSize);
1986 if (!NT_SUCCESS(Status))
1987 {
1988 TRACE("failed with status 0x%08lx\n", Status);
1989 goto done;
1990 }
1991
1992 TRACE("RID: %lx\n", ulRid);
1993
1994 /* Convert the RID into a string (hex) */
1995 _swprintf(szRid, L"%08lX", ulRid);
1996
1997 /* Create the group object */
1998 Status = SampCreateDbObject(DomainObject,
1999 L"Groups",
2000 szRid,
2001 ulRid,
2004 &GroupObject);
2005 if (!NT_SUCCESS(Status))
2006 {
2007 TRACE("failed with status 0x%08lx\n", Status);
2008 goto done;
2009 }
2010
2011 /* Add the account name of the user object */
2012 Status = SampSetAccountNameInDomain(DomainObject,
2013 L"Groups",
2014 Name->Buffer,
2015 ulRid);
2016 if (!NT_SUCCESS(Status))
2017 {
2018 TRACE("failed with status 0x%08lx\n", Status);
2019 goto done;
2020 }
2021
2022 /* Initialize fixed user data */
2023 memset(&FixedGroupData, 0, sizeof(SAM_GROUP_FIXED_DATA));
2024 FixedGroupData.Version = 1;
2025 FixedGroupData.GroupId = ulRid;
2026
2027 /* Set fixed user data attribute */
2028 Status = SampSetObjectAttribute(GroupObject,
2029 L"F",
2030 REG_BINARY,
2031 (LPVOID)&FixedGroupData,
2032 sizeof(SAM_GROUP_FIXED_DATA));
2033 if (!NT_SUCCESS(Status))
2034 {
2035 TRACE("failed with status 0x%08lx\n", Status);
2036 goto done;
2037 }
2038
2039 /* Set the Name attribute */
2041 L"Name",
2042 Name);
2043 if (!NT_SUCCESS(Status))
2044 {
2045 TRACE("failed with status 0x%08lx\n", Status);
2046 goto done;
2047 }
2048
2049 /* Set the AdminComment attribute */
2051 L"AdminComment",
2052 NULL);
2053 if (!NT_SUCCESS(Status))
2054 {
2055 TRACE("failed with status 0x%08lx\n", Status);
2056 goto done;
2057 }
2058
2059 /* Set the SecDesc attribute*/
2060 Status = SampSetObjectAttribute(GroupObject,
2061 L"SecDesc",
2062 REG_BINARY,
2063 Sd,
2064 SdSize);
2065 if (!NT_SUCCESS(Status))
2066 {
2067 TRACE("failed with status 0x%08lx\n", Status);
2068 goto done;
2069 }
2070
2071 if (NT_SUCCESS(Status))
2072 {
2073 *GroupHandle = (SAMPR_HANDLE)GroupObject;
2074 *RelativeId = ulRid;
2075 }
2076
2077done:
2078 if (Sd != NULL)
2079 RtlFreeHeap(RtlGetProcessHeap(), 0, Sd);
2080
2082
2083 TRACE("returns with status 0x%08lx\n", Status);
2084
2085 return Status;
2086}
LPWSTR Name
Definition: desk.c:124
NTSTATUS SampCreateGroupSD(OUT PSECURITY_DESCRIPTOR *GroupSd, OUT PULONG Size)
Definition: security.c:1146
#define DOMAIN_CREATE_GROUP
Definition: ntsam.h:38
static GENERIC_MAPPING GroupMapping
Definition: samrpc.c:40
#define memset(x, y, z)
Definition: compat.h:39

Referenced by SamCreateGroupInDomain().

◆ SamrCreateUser2InDomain()

NTSTATUS NTAPI SamrCreateUser2InDomain ( IN SAMPR_HANDLE  DomainHandle,
IN PRPC_UNICODE_STRING  Name,
IN unsigned long  AccountType,
IN ACCESS_MASK  DesiredAccess,
OUT SAMPR_HANDLE *  UserHandle,
OUT unsigned long *  GrantedAccess,
OUT unsigned long *  RelativeId 
)

Definition at line 8829 of file samrpc.c.

8836{
8837 SAM_DOMAIN_FIXED_DATA FixedDomainData;
8838 SAM_USER_FIXED_DATA FixedUserData;
8839 PSAM_DB_OBJECT DomainObject;
8840 PSAM_DB_OBJECT UserObject;
8841 GROUP_MEMBERSHIP GroupMembership;
8842 UCHAR LogonHours[23];
8843 ULONG ulSize;
8844 ULONG ulRid;
8845 WCHAR szRid[9];
8847 ULONG SdSize = 0;
8848 PSID UserSid = NULL;
8850
8851 TRACE("SamrCreateUserInDomain(%p %p %lx %p %p)\n",
8852 DomainHandle, Name, DesiredAccess, UserHandle, RelativeId);
8853
8854 if (Name == NULL ||
8855 Name->Length == 0 ||
8856 Name->Buffer == NULL ||
8857 UserHandle == NULL ||
8858 RelativeId == NULL)
8860
8861 /* Check for valid account type */
8862 if (AccountType != USER_NORMAL_ACCOUNT &&
8863 AccountType != USER_WORKSTATION_TRUST_ACCOUNT &&
8864 AccountType != USER_INTERDOMAIN_TRUST_ACCOUNT &&
8865 AccountType != USER_SERVER_TRUST_ACCOUNT &&
8866 AccountType != USER_TEMP_DUPLICATE_ACCOUNT)
8868
8869 /* Map generic access rights */
8871 &UserMapping);
8872
8874 TRUE);
8875
8876 /* Validate the domain handle */
8877 Status = SampValidateDbObject(DomainHandle,
8880 &DomainObject);
8881 if (!NT_SUCCESS(Status))
8882 {
8883 TRACE("failed with status 0x%08lx\n", Status);
8884 goto done;
8885 }
8886
8887 /* Check the user account name */
8889 if (!NT_SUCCESS(Status))
8890 {
8891 TRACE("SampCheckAccountName failed (Status 0x%08lx)\n", Status);
8892 goto done;
8893 }
8894
8895 /* Check if the user name already exists in the domain */
8896 Status = SampCheckAccountNameInDomain(DomainObject,
8897 Name->Buffer);
8898 if (!NT_SUCCESS(Status))
8899 {
8900 TRACE("User name \'%S\' already exists in domain (Status 0x%08lx)\n",
8901 Name->Buffer, Status);
8902 goto done;
8903 }
8904
8905 /* Get the fixed domain attributes */
8906 ulSize = sizeof(SAM_DOMAIN_FIXED_DATA);
8907 Status = SampGetObjectAttribute(DomainObject,
8908 L"F",
8909 NULL,
8910 (PVOID)&FixedDomainData,
8911 &ulSize);
8912 if (!NT_SUCCESS(Status))
8913 {
8914 TRACE("failed with status 0x%08lx\n", Status);
8915 goto done;
8916 }
8917
8918 /* Increment the NextRid attribute */
8919 ulRid = FixedDomainData.NextRid;
8920 FixedDomainData.NextRid++;
8921
8922 TRACE("RID: %lx\n", ulRid);
8923
8924 /* Create the user SID */
8925 Status = SampCreateAccountSid(DomainObject,
8926 ulRid,
8927 &UserSid);
8928 if (!NT_SUCCESS(Status))
8929 {
8930 TRACE("SampCreateAccountSid failed (Status 0x%08lx)\n", Status);
8931 goto done;
8932 }
8933
8934 /* Create the security descriptor */
8935 Status = SampCreateUserSD(UserSid,
8936 &Sd,
8937 &SdSize);
8938 if (!NT_SUCCESS(Status))
8939 {
8940 TRACE("SampCreateUserSD failed (Status 0x%08lx)\n", Status);
8941 goto done;
8942 }
8943
8944 /* Store the fixed domain attributes */
8945 Status = SampSetObjectAttribute(DomainObject,
8946 L"F",
8947 REG_BINARY,
8948 &FixedDomainData,
8949 ulSize);
8950 if (!NT_SUCCESS(Status))
8951 {
8952 TRACE("failed with status 0x%08lx\n", Status);
8953 goto done;
8954 }
8955
8956 /* Convert the RID into a string (hex) */
8957 _swprintf(szRid, L"%08lX", ulRid);
8958
8959 /* Create the user object */
8960 Status = SampCreateDbObject(DomainObject,
8961 L"Users",
8962 szRid,
8963 ulRid,
8966 &UserObject);
8967 if (!NT_SUCCESS(Status))
8968 {
8969 TRACE("failed with status 0x%08lx\n", Status);
8970 goto done;
8971 }
8972
8973 /* Add the account name for the user object */
8974 Status = SampSetAccountNameInDomain(DomainObject,
8975 L"Users",
8976 Name->Buffer,
8977 ulRid);
8978 if (!NT_SUCCESS(Status))
8979 {
8980 TRACE("failed with status 0x%08lx\n", Status);
8981 goto done;
8982 }
8983
8984 /* Initialize fixed user data */
8985 FixedUserData.Version = 1;
8986 FixedUserData.Reserved = 0;
8987 FixedUserData.LastLogon.QuadPart = 0;
8988 FixedUserData.LastLogoff.QuadPart = 0;
8989 FixedUserData.PasswordLastSet.QuadPart = 0;
8990 FixedUserData.AccountExpires.LowPart = MAXULONG;
8991 FixedUserData.AccountExpires.HighPart = MAXLONG;
8992 FixedUserData.LastBadPasswordTime.QuadPart = 0;
8993 FixedUserData.UserId = ulRid;
8994 FixedUserData.PrimaryGroupId = DOMAIN_GROUP_RID_USERS;
8997 AccountType;
8998 FixedUserData.CountryCode = 0;
8999 FixedUserData.CodePage = 0;
9000 FixedUserData.BadPasswordCount = 0;
9001 FixedUserData.LogonCount = 0;
9002 FixedUserData.AdminCount = 0;
9003 FixedUserData.OperatorCount = 0;
9004
9005 /* Set fixed user data attribute */
9006 Status = SampSetObjectAttribute(UserObject,
9007 L"F",
9008 REG_BINARY,
9009 (LPVOID)&FixedUserData,
9010 sizeof(SAM_USER_FIXED_DATA));
9011 if (!NT_SUCCESS(Status))
9012 {
9013 TRACE("failed with status 0x%08lx\n", Status);
9014 goto done;
9015 }
9016
9017 /* Set the Name attribute */
9019 L"Name",
9020 Name);
9021 if (!NT_SUCCESS(Status))
9022 {
9023 TRACE("failed with status 0x%08lx\n", Status);
9024 goto done;
9025 }
9026
9027 /* Set the FullName attribute */
9029 L"FullName",
9030 NULL);
9031 if (!NT_SUCCESS(Status))
9032 {
9033 TRACE("failed with status 0x%08lx\n", Status);
9034 goto done;
9035 }
9036
9037 /* Set the HomeDirectory attribute */
9039 L"HomeDirectory",
9040 NULL);
9041 if (!NT_SUCCESS(Status))
9042 {
9043 TRACE("failed with status 0x%08lx\n", Status);
9044 goto done;
9045 }
9046
9047 /* Set the HomeDirectoryDrive attribute */
9049 L"HomeDirectoryDrive",
9050 NULL);
9051 if (!NT_SUCCESS(Status))
9052 {
9053 TRACE("failed with status 0x%08lx\n", Status);
9054 goto done;
9055 }
9056
9057 /* Set the ScriptPath attribute */
9059 L"ScriptPath",
9060 NULL);
9061 if (!NT_SUCCESS(Status))
9062 {
9063 TRACE("failed with status 0x%08lx\n", Status);
9064 goto done;
9065 }
9066
9067 /* Set the ProfilePath attribute */
9069 L"ProfilePath",
9070 NULL);
9071 if (!NT_SUCCESS(Status))
9072 {
9073 TRACE("failed with status 0x%08lx\n", Status);
9074 goto done;
9075 }
9076
9077 /* Set the AdminComment attribute */
9079 L"AdminComment",
9080 NULL);
9081 if (!NT_SUCCESS(Status))
9082 {
9083 TRACE("failed with status 0x%08lx\n", Status);
9084 goto done;
9085 }
9086
9087 /* Set the UserComment attribute */
9089 L"UserComment",
9090 NULL);
9091 if (!NT_SUCCESS(Status))
9092 {
9093 TRACE("failed with status 0x%08lx\n", Status);
9094 goto done;
9095 }
9096
9097 /* Set the WorkStations attribute */
9099 L"WorkStations",
9100 NULL);
9101 if (!NT_SUCCESS(Status))
9102 {
9103 TRACE("failed with status 0x%08lx\n", Status);
9104 goto done;
9105 }
9106
9107 /* Set the Parameters attribute */
9109 L"Parameters",
9110 NULL);
9111 if (!NT_SUCCESS(Status))
9112 {
9113 TRACE("failed with status 0x%08lx\n", Status);
9114 goto done;
9115 }
9116
9117 /* Set LogonHours attribute*/
9118 *((PUSHORT)LogonHours) = 168;
9119 memset(&(LogonHours[2]), 0xff, 21);
9120
9121 Status = SampSetObjectAttribute(UserObject,
9122 L"LogonHours",
9123 REG_BINARY,
9124 &LogonHours,
9125 sizeof(LogonHours));
9126 if (!NT_SUCCESS(Status))
9127 {
9128 TRACE("failed with status 0x%08lx\n", Status);
9129 goto done;
9130 }
9131
9132 /* Set Groups attribute*/
9133 GroupMembership.RelativeId = DOMAIN_GROUP_RID_USERS;
9134 GroupMembership.Attributes = SE_GROUP_MANDATORY |
9137
9138 Status = SampSetObjectAttribute(UserObject,
9139 L"Groups",
9140 REG_BINARY,
9141 &GroupMembership,
9142 sizeof(GROUP_MEMBERSHIP));
9143 if (!NT_SUCCESS(Status))
9144 {
9145 TRACE("failed with status 0x%08lx\n", Status);
9146 goto done;
9147 }
9148
9149 /* Set LMPwd attribute*/
9150 Status = SampSetObjectAttribute(UserObject,
9151 L"LMPwd",
9152 REG_BINARY,
9153 NULL,
9154 0);
9155 if (!NT_SUCCESS(Status))
9156 {
9157 TRACE("failed with status 0x%08lx\n", Status);
9158 goto done;
9159 }
9160
9161 /* Set NTPwd attribute*/
9162 Status = SampSetObjectAttribute(UserObject,
9163 L"NTPwd",
9164 REG_BINARY,
9165 NULL,
9166 0);
9167 if (!NT_SUCCESS(Status))
9168 {
9169 TRACE("failed with status 0x%08lx\n", Status);
9170 goto done;
9171 }
9172
9173 /* Set LMPwdHistory attribute*/
9174 Status = SampSetObjectAttribute(UserObject,
9175 L"LMPwdHistory",
9176 REG_BINARY,
9177 NULL,
9178 0);
9179 if (!NT_SUCCESS(Status))
9180 {
9181 TRACE("failed with status 0x%08lx\n", Status);
9182 goto done;
9183 }
9184
9185 /* Set NTPwdHistory attribute*/
9186 Status = SampSetObjectAttribute(UserObject,
9187 L"NTPwdHistory",
9188 REG_BINARY,
9189 NULL,
9190 0);
9191 if (!NT_SUCCESS(Status))
9192 {
9193 TRACE("failed with status 0x%08lx\n", Status);
9194 goto done;
9195 }
9196
9197 /* Set the PrivateData attribute */
9199 L"PrivateData",
9200 NULL);
9201 if (!NT_SUCCESS(Status))
9202 {
9203 TRACE("failed with status 0x%08lx\n", Status);
9204 goto done;
9205 }
9206
9207 /* Set the SecDesc attribute*/
9208 Status = SampSetObjectAttribute(UserObject,
9209 L"SecDesc",
9210 REG_BINARY,
9211 Sd,
9212 SdSize);
9213 if (!NT_SUCCESS(Status))
9214 {
9215 TRACE("failed with status 0x%08lx\n", Status);
9216 goto done;
9217 }
9218
9219 if (NT_SUCCESS(Status))
9220 {
9221 *UserHandle = (SAMPR_HANDLE)UserObject;
9222 *RelativeId = ulRid;
9223 *GrantedAccess = UserObject->Access;
9224 }
9225
9226done:
9227 if (Sd != NULL)
9228 RtlFreeHeap(RtlGetProcessHeap(), 0, Sd);
9229
9230 if (UserSid != NULL)
9231 RtlFreeHeap(RtlGetProcessHeap(), 0, UserSid);
9232
9234
9235 TRACE("returns with status 0x%08lx\n", Status);
9236
9237 return Status;
9238}
NTSTATUS SampCreateAccountSid(IN PSAM_DB_OBJECT DomainObject, IN ULONG ulRelativeId, IN OUT PSID *AccountSid)
Definition: domain.c:303
NTSTATUS SampCreateUserSD(IN PSID UserSid, OUT PSECURITY_DESCRIPTOR *UserSd, OUT PULONG Size)
Definition: security.c:1433
#define SE_GROUP_MANDATORY
Definition: setypes.h:90
#define SE_GROUP_ENABLED_BY_DEFAULT
Definition: setypes.h:91
#define SE_GROUP_ENABLED
Definition: setypes.h:92
#define USER_NORMAL_ACCOUNT
Definition: ntsam.h:171
#define USER_PASSWORD_NOT_REQUIRED
Definition: ntsam.h:169
#define USER_WORKSTATION_TRUST_ACCOUNT
Definition: ntsam.h:174
#define USER_TEMP_DUPLICATE_ACCOUNT
Definition: ntsam.h:170
#define DOMAIN_CREATE_USER
Definition: ntsam.h:37
#define USER_SERVER_TRUST_ACCOUNT
Definition: ntsam.h:175
#define USER_INTERDOMAIN_TRUST_ACCOUNT
Definition: ntsam.h:173
#define USER_ACCOUNT_DISABLED
Definition: ntsam.h:167
static GENERIC_MAPPING UserMapping
Definition: samrpc.c:48
ULONG RelativeId
Definition: ntsam.h:496
ULONG Attributes
Definition: ntsam.h:497
USHORT OperatorCount
Definition: samsrv.h:115
#define MAXULONG
Definition: typedefs.h:251
unsigned char UCHAR
Definition: typedefs.h:53
uint16_t * PUSHORT
Definition: typedefs.h:56
#define MAXLONG
Definition: umtypes.h:116
_In_ PSECURITY_SUBJECT_CONTEXT _In_ BOOLEAN _In_ ACCESS_MASK _In_ ACCESS_MASK _Outptr_opt_ PPRIVILEGE_SET _In_ PGENERIC_MAPPING _In_ KPROCESSOR_MODE _Out_ PACCESS_MASK GrantedAccess
Definition: sefuncs.h:20
#define DOMAIN_GROUP_RID_USERS
Definition: setypes.h:640

Referenced by SamCreateUser2InDomain().

◆ SamrCreateUserInDomain()

NTSTATUS NTAPI SamrCreateUserInDomain ( IN SAMPR_HANDLE  DomainHandle,
IN PRPC_UNICODE_STRING  Name,
IN ACCESS_MASK  DesiredAccess,
OUT SAMPR_HANDLE *  UserHandle,
OUT unsigned long *  RelativeId 
)

Definition at line 2300 of file samrpc.c.

2305{
2306 SAM_DOMAIN_FIXED_DATA FixedDomainData;
2307 SAM_USER_FIXED_DATA FixedUserData;
2308 PSAM_DB_OBJECT DomainObject;
2309 PSAM_DB_OBJECT UserObject;
2310 GROUP_MEMBERSHIP GroupMembership;
2311 UCHAR LogonHours[23];
2312 ULONG ulSize;
2313 ULONG ulRid;
2314 WCHAR szRid[9];
2316 ULONG SdSize = 0;
2317 PSID UserSid = NULL;
2319
2320 TRACE("SamrCreateUserInDomain(%p %p %lx %p %p)\n",
2321 DomainHandle, Name, DesiredAccess, UserHandle, RelativeId);
2322
2323 if (Name == NULL ||
2324 Name->Length == 0 ||
2325 Name->Buffer == NULL ||
2326 UserHandle == NULL ||
2327 RelativeId == NULL)
2329
2330 /* Map generic access rights */
2332 &UserMapping);
2333
2335 TRUE);
2336
2337 /* Validate the domain handle */
2338 Status = SampValidateDbObject(DomainHandle,
2341 &DomainObject);
2342 if (!NT_SUCCESS(Status))
2343 {
2344 TRACE("failed with status 0x%08lx\n", Status);
2345 goto done;
2346 }
2347
2348 /* Check the user account name */
2350 if (!NT_SUCCESS(Status))
2351 {
2352 TRACE("SampCheckAccountName failed (Status 0x%08lx)\n", Status);
2353 goto done;
2354 }
2355
2356 /* Check if the user name already exists in the domain */
2357 Status = SampCheckAccountNameInDomain(DomainObject,
2358 Name->Buffer);
2359 if (!NT_SUCCESS(Status))
2360 {
2361 TRACE("User name \'%S\' already exists in domain (Status 0x%08lx)\n",
2362 Name->Buffer, Status);
2363 goto done;
2364 }
2365
2366 /* Get the fixed domain attributes */
2367 ulSize = sizeof(SAM_DOMAIN_FIXED_DATA);
2368 Status = SampGetObjectAttribute(DomainObject,
2369 L"F",
2370 NULL,
2371 (PVOID)&FixedDomainData,
2372 &ulSize);
2373 if (!NT_SUCCESS(Status))
2374 {
2375 TRACE("failed with status 0x%08lx\n", Status);
2376 goto done;
2377 }
2378
2379 /* Increment the NextRid attribute */
2380 ulRid = FixedDomainData.NextRid;
2381 FixedDomainData.NextRid++;
2382
2383 TRACE("RID: %lx\n", ulRid);
2384
2385 /* Create the user SID */
2386 Status = SampCreateAccountSid(DomainObject,
2387 ulRid,
2388 &UserSid);
2389 if (!NT_SUCCESS(Status))
2390 {
2391 TRACE("SampCreateAccountSid failed (Status 0x%08lx)\n", Status);
2392 goto done;
2393 }
2394
2395 /* Create the security descriptor */
2396 Status = SampCreateUserSD(UserSid,
2397 &Sd,
2398 &SdSize);
2399 if (!NT_SUCCESS(Status))
2400 {
2401 TRACE("SampCreateUserSD failed (Status 0x%08lx)\n", Status);
2402 goto done;
2403 }
2404
2405 /* Store the fixed domain attributes */
2406 Status = SampSetObjectAttribute(DomainObject,
2407 L"F",
2408 REG_BINARY,
2409 &FixedDomainData,
2410 ulSize);
2411 if (!NT_SUCCESS(Status))
2412 {
2413 TRACE("failed with status 0x%08lx\n", Status);
2414 goto done;
2415 }
2416
2417 /* Convert the RID into a string (hex) */
2418 _swprintf(szRid, L"%08lX", ulRid);
2419
2420 /* Create the user object */
2421 Status = SampCreateDbObject(DomainObject,
2422 L"Users",
2423 szRid,
2424 ulRid,
2427 &UserObject);
2428 if (!NT_SUCCESS(Status))
2429 {
2430 TRACE("failed with status 0x%08lx\n", Status);
2431 goto done;
2432 }
2433
2434 /* Add the account name for the user object */
2435 Status = SampSetAccountNameInDomain(DomainObject,
2436 L"Users",
2437 Name->Buffer,
2438 ulRid);
2439 if (!NT_SUCCESS(Status))
2440 {
2441 TRACE("failed with status 0x%08lx\n", Status);
2442 goto done;
2443 }
2444
2445 /* Initialize fixed user data */
2446 memset(&FixedUserData, 0, sizeof(SAM_USER_FIXED_DATA));
2447 FixedUserData.Version = 1;
2448 FixedUserData.Reserved = 0;
2449 FixedUserData.LastLogon.QuadPart = 0;
2450 FixedUserData.LastLogoff.QuadPart = 0;
2451 FixedUserData.PasswordLastSet.QuadPart = 0;
2452 FixedUserData.AccountExpires.QuadPart = MAXLONGLONG;
2453 FixedUserData.LastBadPasswordTime.QuadPart = 0;
2454 FixedUserData.UserId = ulRid;
2455 FixedUserData.PrimaryGroupId = DOMAIN_GROUP_RID_USERS;
2459 FixedUserData.CountryCode = 0;
2460 FixedUserData.CodePage = 0;
2461 FixedUserData.BadPasswordCount = 0;
2462 FixedUserData.LogonCount = 0;
2463 FixedUserData.AdminCount = 0;
2464 FixedUserData.OperatorCount = 0;
2465
2466 /* Set fixed user data attribute */
2467 Status = SampSetObjectAttribute(UserObject,
2468 L"F",
2469 REG_BINARY,
2470 (LPVOID)&FixedUserData,
2471 sizeof(SAM_USER_FIXED_DATA));
2472 if (!NT_SUCCESS(Status))
2473 {
2474 TRACE("failed with status 0x%08lx\n", Status);
2475 goto done;
2476 }
2477
2478 /* Set the Name attribute */
2480 L"Name",
2481 Name);
2482 if (!NT_SUCCESS(Status))
2483 {
2484 TRACE("failed with status 0x%08lx\n", Status);
2485 goto done;
2486 }
2487
2488 /* Set the FullName attribute */
2490 L"FullName",
2491 NULL);
2492 if (!NT_SUCCESS(Status))
2493 {
2494 TRACE("failed with status 0x%08lx\n", Status);
2495 goto done;
2496 }
2497
2498 /* Set the HomeDirectory attribute */
2500 L"HomeDirectory",
2501 NULL);
2502 if (!NT_SUCCESS(Status))
2503 {
2504 TRACE("failed with status 0x%08lx\n", Status);
2505 goto done;
2506 }
2507
2508 /* Set the HomeDirectoryDrive attribute */
2510 L"HomeDirectoryDrive",
2511 NULL);
2512 if (!NT_SUCCESS(Status))
2513 {
2514 TRACE("failed with status 0x%08lx\n", Status);
2515 goto done;
2516 }
2517
2518 /* Set the ScriptPath attribute */
2520 L"ScriptPath",
2521 NULL);
2522 if (!NT_SUCCESS(Status))
2523 {
2524 TRACE("failed with status 0x%08lx\n", Status);
2525 goto done;
2526 }
2527
2528 /* Set the ProfilePath attribute */
2530 L"ProfilePath",
2531 NULL);
2532 if (!NT_SUCCESS(Status))
2533 {
2534 TRACE("failed with status 0x%08lx\n", Status);
2535 goto done;
2536 }
2537
2538 /* Set the AdminComment attribute */
2540 L"AdminComment",
2541 NULL);
2542 if (!NT_SUCCESS(Status))
2543 {
2544 TRACE("failed with status 0x%08lx\n", Status);
2545 goto done;
2546 }
2547
2548 /* Set the UserComment attribute */
2550 L"UserComment",
2551 NULL);
2552 if (!NT_SUCCESS(Status))
2553 {
2554 TRACE("failed with status 0x%08lx\n", Status);
2555 goto done;
2556 }
2557
2558 /* Set the WorkStations attribute */
2560 L"WorkStations",
2561 NULL);
2562 if (!NT_SUCCESS(Status))
2563 {
2564 TRACE("failed with status 0x%08lx\n", Status);
2565 goto done;
2566 }
2567
2568 /* Set the Parameters attribute */
2570 L"Parameters",
2571 NULL);
2572 if (!NT_SUCCESS(Status))
2573 {
2574 TRACE("failed with status 0x%08lx\n", Status);
2575 goto done;
2576 }
2577
2578 /* Set LogonHours attribute*/
2579 *((PUSHORT)LogonHours) = 168;
2580 memset(&(LogonHours[2]), 0xff, 21);
2581
2582 Status = SampSetObjectAttribute(UserObject,
2583 L"LogonHours",
2584 REG_BINARY,
2585 &LogonHours,
2586 sizeof(LogonHours));
2587 if (!NT_SUCCESS(Status))
2588 {
2589 TRACE("failed with status 0x%08lx\n", Status);
2590 goto done;
2591 }
2592
2593 /* Set Groups attribute*/
2594 GroupMembership.RelativeId = DOMAIN_GROUP_RID_USERS;
2595 GroupMembership.Attributes = SE_GROUP_MANDATORY |
2598
2599 Status = SampSetObjectAttribute(UserObject,
2600 L"Groups",
2601 REG_BINARY,
2602 &GroupMembership,
2603 sizeof(GROUP_MEMBERSHIP));
2604 if (!NT_SUCCESS(Status))
2605 {
2606 TRACE("failed with status 0x%08lx\n", Status);
2607 goto done;
2608 }
2609
2610 /* Set LMPwd attribute*/
2611 Status = SampSetObjectAttribute(UserObject,
2612 L"LMPwd",
2613 REG_BINARY,
2614 &EmptyLmHash,
2616 if (!NT_SUCCESS(Status))
2617 {
2618 TRACE("failed with status 0x%08lx\n", Status);
2619 goto done;
2620 }
2621
2622 /* Set NTPwd attribute*/
2623 Status = SampSetObjectAttribute(UserObject,
2624 L"NTPwd",
2625 REG_BINARY,
2626 &EmptyNtHash,
2628 if (!NT_SUCCESS(Status))
2629 {
2630 TRACE("failed with status 0x%08lx\n", Status);
2631 goto done;
2632 }
2633
2634 /* Set LMPwdHistory attribute*/
2635 Status = SampSetObjectAttribute(UserObject,
2636 L"LMPwdHistory",
2637 REG_BINARY,
2638 NULL,
2639 0);
2640 if (!NT_SUCCESS(Status))
2641 {
2642 TRACE("failed with status 0x%08lx\n", Status);
2643 goto done;
2644 }
2645
2646 /* Set NTPwdHistory attribute*/
2647 Status = SampSetObjectAttribute(UserObject,
2648 L"NTPwdHistory",
2649 REG_BINARY,
2650 NULL,
2651 0);
2652 if (!NT_SUCCESS(Status))
2653 {
2654 TRACE("failed with status 0x%08lx\n", Status);
2655 goto done;
2656 }
2657
2658 /* Set the PrivateData attribute */
2660 L"PrivateData",
2661 NULL);
2662 if (!NT_SUCCESS(Status))
2663 {
2664 TRACE("failed with status 0x%08lx\n", Status);
2665 goto done;
2666 }
2667
2668 /* Set the SecDesc attribute*/
2669 Status = SampSetObjectAttribute(UserObject,
2670 L"SecDesc",
2671 REG_BINARY,
2672 Sd,
2673 SdSize);
2674 if (!NT_SUCCESS(Status))
2675 {
2676 TRACE("failed with status 0x%08lx\n", Status);
2677 goto done;
2678 }
2679
2680 if (NT_SUCCESS(Status))
2681 {
2682 *UserHandle = (SAMPR_HANDLE)UserObject;
2683 *RelativeId = ulRid;
2684 }
2685
2686done:
2687 if (Sd != NULL)
2688 RtlFreeHeap(RtlGetProcessHeap(), 0, Sd);
2689
2690 if (UserSid != NULL)
2691 RtlFreeHeap(RtlGetProcessHeap(), 0, UserSid);
2692
2694
2695 TRACE("returns with status 0x%08lx\n", Status);
2696
2697 return Status;
2698}
#define MAXLONGLONG

Referenced by SamCreateUserInDomain().

◆ SamrDeleteAlias()

NTSTATUS NTAPI SamrDeleteAlias ( IN OUT SAMPR_HANDLE *  AliasHandle)

Definition at line 5226 of file samrpc.c.

5227{
5228 PSAM_DB_OBJECT AliasObject;
5230
5231 TRACE("SamrDeleteAlias(%p)\n", AliasHandle);
5232
5234 TRUE);
5235
5236 /* Validate the alias handle */
5237 Status = SampValidateDbObject(*AliasHandle,
5239 DELETE,
5240 &AliasObject);
5241 if (!NT_SUCCESS(Status))
5242 {
5243 TRACE("SampValidateDbObject failed (Status 0x%08lx)\n", Status);
5244 goto done;
5245 }
5246
5247 /* Fail, if the alias is built-in */
5248 if (AliasObject->RelativeId < 1000)
5249 {
5250 TRACE("You can not delete a special account!\n");
5252 goto done;
5253 }
5254
5255 /* Remove all members from the alias */
5257 if (!NT_SUCCESS(Status))
5258 {
5259 TRACE("SampRemoveAllMembersFromAlias() failed (Status 0x%08lx)\n", Status);
5260 goto done;
5261 }
5262
5263 /* Delete the alias from the database */
5264 Status = SampDeleteAccountDbObject(AliasObject);
5265 if (!NT_SUCCESS(Status))
5266 {
5267 TRACE("SampDeleteAccountDbObject() failed (Status 0x%08lx)\n", Status);
5268 goto done;
5269 }
5270
5271 /* Invalidate the handle */
5272 *AliasHandle = NULL;
5273
5274done:
5276
5277 return Status;
5278}
NTSTATUS SampRemoveAllMembersFromAlias(IN PSAM_DB_OBJECT AliasObject)
Definition: alias.c:314
NTSTATUS SampDeleteAccountDbObject(PSAM_DB_OBJECT DbObject)
Definition: database.c:368
#define DELETE
Definition: nt_native.h:57
#define STATUS_SPECIAL_ACCOUNT
Definition: ntstatus.h:622

Referenced by SamDeleteAlias().

◆ SamrDeleteGroup()

NTSTATUS NTAPI SamrDeleteGroup ( IN OUT SAMPR_HANDLE *  GroupHandle)

Definition at line 4538 of file samrpc.c.

4539{
4540 PSAM_DB_OBJECT GroupObject;
4541 ULONG Length = 0;
4543
4544 TRACE("SamrDeleteGroup(%p)\n", GroupHandle);
4545
4547 TRUE);
4548
4549 /* Validate the group handle */
4550 Status = SampValidateDbObject(*GroupHandle,
4552 DELETE,
4553 &GroupObject);
4554 if (!NT_SUCCESS(Status))
4555 {
4556 TRACE("SampValidateDbObject() failed (Status 0x%08lx)\n", Status);
4557 goto done;
4558 }
4559
4560 /* Fail, if the group is built-in */
4561 if (GroupObject->RelativeId < 1000)
4562 {
4563 TRACE("You can not delete a special account!\n");
4565 goto done;
4566 }
4567
4568 /* Get the length of the Members attribute */
4569 SampGetObjectAttribute(GroupObject,
4570 L"Members",
4571 NULL,
4572 NULL,
4573 &Length);
4574
4575 /* Fail, if the group has members */
4576 if (Length != 0)
4577 {
4578 TRACE("There are still members in the group!\n");
4580 goto done;
4581 }
4582
4583 /* FIXME: Remove the group from all aliases */
4584
4585 /* Delete the group from the database */
4586 Status = SampDeleteAccountDbObject(GroupObject);
4587 if (!NT_SUCCESS(Status))
4588 {
4589 TRACE("SampDeleteAccountDbObject() failed (Status 0x%08lx)\n", Status);
4590 goto done;
4591 }
4592
4593 /* Invalidate the handle */
4594 *GroupHandle = NULL;
4595
4596done:
4598
4599 return Status;
4600}
#define STATUS_MEMBER_IN_GROUP
Definition: ntstatus.h:433

Referenced by SamDeleteGroup().

◆ SamrDeleteUser()

NTSTATUS NTAPI SamrDeleteUser ( IN OUT SAMPR_HANDLE *  UserHandle)

Definition at line 5486 of file samrpc.c.

5487{
5488 PSAM_DB_OBJECT UserObject;
5490
5491 TRACE("SamrDeleteUser(%p)\n", UserHandle);
5492
5494 TRUE);
5495
5496 /* Validate the user handle */
5497 Status = SampValidateDbObject(*UserHandle,
5499 DELETE,
5500 &UserObject);
5501 if (!NT_SUCCESS(Status))
5502 {
5503 TRACE("SampValidateDbObject() failed (Status 0x%08lx)\n", Status);
5504 goto done;
5505 }
5506
5507 /* Fail, if the user is built-in */
5508 if (UserObject->RelativeId < 1000)
5509 {
5510 TRACE("You can not delete a special account!\n");
5512 goto done;
5513 }
5514
5515 /* Remove the user from all groups */
5516 Status = SampRemoveUserFromAllGroups(UserObject);
5517 if (!NT_SUCCESS(Status))
5518 {
5519 TRACE("SampRemoveUserFromAllGroups() failed (Status 0x%08lx)\n", Status);
5520 goto done;
5521 }
5522
5523 /* Remove the user from all aliases */
5525 if (!NT_SUCCESS(Status))
5526 {
5527 TRACE("SampRemoveUserFromAllAliases() failed (Status 0x%08lx)\n", Status);
5528 goto done;
5529 }
5530
5531 /* Delete the user from the database */
5532 Status = SampDeleteAccountDbObject(UserObject);
5533 if (!NT_SUCCESS(Status))
5534 {
5535 TRACE("SampDeleteAccountDbObject() failed (Status 0x%08lx)\n", Status);
5536 goto done;
5537 }
5538
5539 /* Invalidate the handle */
5540 *UserHandle = NULL;
5541
5542done:
5544
5545 return Status;
5546}
NTSTATUS SampRemoveUserFromAllGroups(IN PSAM_DB_OBJECT UserObject)
Definition: user.c:319
NTSTATUS SampRemoveUserFromAllAliases(IN PSAM_DB_OBJECT UserObject)

Referenced by SamDeleteUser().

◆ SamrEnumerateAliasesInDomain()

NTSTATUS NTAPI SamrEnumerateAliasesInDomain ( IN SAMPR_HANDLE  DomainHandle,
IN OUT unsigned long *  EnumerationContext,
OUT PSAMPR_ENUMERATION_BUFFER *  Buffer,
IN unsigned long  PreferedMaximumLength,
OUT unsigned long *  CountReturned 
)

Definition at line 3089 of file samrpc.c.

3094{
3095 PSAMPR_ENUMERATION_BUFFER EnumBuffer = NULL;
3096 PSAM_DB_OBJECT DomainObject;
3097 HANDLE AliasesKeyHandle = NULL;
3098 HANDLE NamesKeyHandle = NULL;
3099 WCHAR AliasName[64];
3100 ULONG EnumIndex;
3101 ULONG EnumCount = 0;
3105 ULONG Rid;
3106 ULONG i;
3107 BOOLEAN MoreEntries = FALSE;
3109
3110 TRACE("SamrEnumerateAliasesInDomain(%p %p %p %lu %p)\n",
3111 DomainHandle, EnumerationContext, Buffer,
3112 PreferedMaximumLength, CountReturned);
3113
3115 TRUE);
3116
3117 /* Validate the domain handle */
3118 Status = SampValidateDbObject(DomainHandle,
3121 &DomainObject);
3122 if (!NT_SUCCESS(Status))
3123 goto done;
3124
3125 Status = SampRegOpenKey(DomainObject->KeyHandle,
3126 L"Aliases",
3127 KEY_READ,
3128 &AliasesKeyHandle);
3129 if (!NT_SUCCESS(Status))
3130 goto done;
3131
3132 Status = SampRegOpenKey(AliasesKeyHandle,
3133 L"Names",
3134 KEY_READ,
3135 &NamesKeyHandle);
3136 if (!NT_SUCCESS(Status))
3137 goto done;
3138
3139 TRACE("Part 1\n");
3140
3141 EnumIndex = *EnumerationContext;
3142
3143 while (TRUE)
3144 {
3145 NameLength = 64 * sizeof(WCHAR);
3146 Status = SampRegEnumerateValue(NamesKeyHandle,
3147 EnumIndex,
3148 AliasName,
3149 &NameLength,
3150 NULL,
3151 NULL,
3152 NULL);
3153 if (!NT_SUCCESS(Status))
3154 {
3157 break;
3158 }
3159
3160 TRACE("EnumIndex: %lu\n", EnumIndex);
3161 TRACE("Alias name: %S\n", AliasName);
3162 TRACE("Name length: %lu\n", NameLength);
3163
3164 if ((RequiredLength + NameLength + sizeof(UNICODE_NULL) + sizeof(SAMPR_RID_ENUMERATION)) > PreferedMaximumLength)
3165 {
3166 MoreEntries = TRUE;
3167 break;
3168 }
3169
3171 EnumCount++;
3172
3173 EnumIndex++;
3174 }
3175
3176 TRACE("EnumCount: %lu\n", EnumCount);
3177 TRACE("RequiredLength: %lu\n", RequiredLength);
3178
3179 if (!NT_SUCCESS(Status))
3180 goto done;
3181
3182 EnumBuffer = midl_user_allocate(sizeof(SAMPR_ENUMERATION_BUFFER));
3183 if (EnumBuffer == NULL)
3184 {
3186 goto done;
3187 }
3188
3189 EnumBuffer->EntriesRead = EnumCount;
3190 if (EnumCount == 0)
3191 {
3193 goto done;
3194 }
3195
3196 EnumBuffer->Buffer = midl_user_allocate(EnumCount * sizeof(SAMPR_RID_ENUMERATION));
3197 if (EnumBuffer->Buffer == NULL)
3198 {
3200 goto done;
3201 }
3202
3203 TRACE("Part 2\n");
3204
3205 EnumIndex = *EnumerationContext;
3206 for (i = 0; i < EnumCount; i++, EnumIndex++)
3207 {
3208 NameLength = 64 * sizeof(WCHAR);
3209 DataLength = sizeof(ULONG);
3210 Status = SampRegEnumerateValue(NamesKeyHandle,
3211 EnumIndex,
3212 AliasName,
3213 &NameLength,
3214 NULL,
3215 &Rid,
3216 &DataLength);
3217 if (!NT_SUCCESS(Status))
3218 {
3221 break;
3222 }
3223
3224 TRACE("EnumIndex: %lu\n", EnumIndex);
3225 TRACE("Alias name: %S\n", AliasName);
3226 TRACE("Name length: %lu\n", NameLength);
3227 TRACE("RID: %lu\n", Rid);
3228
3229 EnumBuffer->Buffer[i].RelativeId = Rid;
3230
3231 EnumBuffer->Buffer[i].Name.Length = (USHORT)NameLength;
3232 EnumBuffer->Buffer[i].Name.MaximumLength = (USHORT)(NameLength + sizeof(UNICODE_NULL));
3233
3234/* FIXME: Disabled because of bugs in widl and rpcrt4 */
3235#if 0
3236 EnumBuffer->Buffer[i].Name.Buffer = midl_user_allocate(EnumBuffer->Buffer[i].Name.MaximumLength);
3237 if (EnumBuffer->Buffer[i].Name.Buffer == NULL)
3238 {
3240 goto done;
3241 }
3242
3243 memcpy(EnumBuffer->Buffer[i].Name.Buffer,
3244 AliasName,
3245 EnumBuffer->Buffer[i].Name.Length);
3246#endif
3247 }
3248
3249done:
3250 if (NT_SUCCESS(Status))
3251 {
3252 *EnumerationContext += EnumCount;
3253 *Buffer = EnumBuffer;
3254 *CountReturned = EnumCount;
3255 }
3256 else
3257 {
3258 *EnumerationContext = 0;
3259 *Buffer = NULL;
3260 *CountReturned = 0;
3261
3262 if (EnumBuffer != NULL)
3263 {
3264 if (EnumBuffer->Buffer != NULL)
3265 {
3266 if (EnumBuffer->EntriesRead != 0)
3267 {
3268 for (i = 0; i < EnumBuffer->EntriesRead; i++)
3269 {
3270 if (EnumBuffer->Buffer[i].Name.Buffer != NULL)
3271 midl_user_free(EnumBuffer->Buffer[i].Name.Buffer);
3272 }
3273 }
3274
3275 midl_user_free(EnumBuffer->Buffer);
3276 }
3277
3278 midl_user_free(EnumBuffer);
3279 }
3280 }
3281
3282 SampRegCloseKey(&NamesKeyHandle);
3283 SampRegCloseKey(&AliasesKeyHandle);
3284
3285 if ((Status == STATUS_SUCCESS) && (MoreEntries != FALSE))
3287
3289
3290 return Status;
3291}
_In_ D3DDDI_VIDEO_PRESENT_TARGET_ID _In_ ULONG _In_ ULONG DataLength
Definition: dispmprt.h:233
NTSTATUS SampRegEnumerateValue(IN HANDLE KeyHandle, IN ULONG Index, OUT LPWSTR Name, IN OUT PULONG NameLength, OUT PULONG Type OPTIONAL, OUT PVOID Data OPTIONAL, IN OUT PULONG DataLength OPTIONAL)
Definition: registry.c:226
#define memcpy(s1, s2, n)
Definition: mkisofs.h:878
#define UNICODE_NULL
#define DOMAIN_LIST_ACCOUNTS
Definition: ntsam.h:41
#define STATUS_NO_MORE_ENTRIES
Definition: ntstatus.h:285
unsigned short USHORT
Definition: pedump.c:61
Input NameLength
Definition: portacpi.cpp:298
unsigned short Length
Definition: msv1_0.h:22
unsigned short MaximumLength
Definition: msv1_0.h:23
PSAMPR_RID_ENUMERATION Buffer
Definition: sam.idl:96
unsigned long EntriesRead
Definition: sam.idl:95
unsigned long RelativeId
Definition: sam.idl:89
RPC_UNICODE_STRING Name
Definition: sam.idl:90
#define STATUS_MORE_ENTRIES
Definition: udferr_usr.h:124
_In_ ULONG _Out_opt_ PULONG RequiredLength
Definition: wmifuncs.h:30

Referenced by SamEnumerateAliasesInDomain().

◆ SamrEnumerateDomainsInSamServer()

NTSTATUS NTAPI SamrEnumerateDomainsInSamServer ( IN SAMPR_HANDLE  ServerHandle,
IN OUT unsigned long *  EnumerationContext,
OUT PSAMPR_ENUMERATION_BUFFER *  Buffer,
IN ULONG  PreferedMaximumLength,
OUT PULONG  CountReturned 
)

Definition at line 621 of file samrpc.c.

626{
627 PSAM_DB_OBJECT ServerObject;
628 WCHAR DomainKeyName[64];
629 HANDLE DomainsKeyHandle = NULL;
630 HANDLE DomainKeyHandle = NULL;
631 ULONG EnumIndex;
632 ULONG EnumCount;
635 ULONG i;
636 PSAMPR_ENUMERATION_BUFFER EnumBuffer = NULL;
638
639 TRACE("SamrEnumerateDomainsInSamServer(%p %p %p %lu %p)\n",
640 ServerHandle, EnumerationContext, Buffer, PreferedMaximumLength,
641 CountReturned);
642
644 TRUE);
645
646 /* Validate the server handle */
647 Status = SampValidateDbObject(ServerHandle,
650 &ServerObject);
651 if (!NT_SUCCESS(Status))
652 goto done;
653
654 Status = SampRegOpenKey(ServerObject->KeyHandle,
655 L"Domains",
656 KEY_READ,
657 &DomainsKeyHandle);
658 if (!NT_SUCCESS(Status))
659 goto done;
660
661 EnumIndex = *EnumerationContext;
662 EnumCount = 0;
663 RequiredLength = 0;
664
665 while (TRUE)
666 {
667 Status = SampRegEnumerateSubKey(DomainsKeyHandle,
668 EnumIndex,
669 64 * sizeof(WCHAR),
670 DomainKeyName);
671 if (!NT_SUCCESS(Status))
672 break;
673
674 TRACE("EnumIndex: %lu\n", EnumIndex);
675 TRACE("Domain key name: %S\n", DomainKeyName);
676
677 Status = SampRegOpenKey(DomainsKeyHandle,
678 DomainKeyName,
679 KEY_READ,
680 &DomainKeyHandle);
681 TRACE("SampRegOpenKey returned %08lX\n", Status);
682 if (NT_SUCCESS(Status))
683 {
684 DataLength = 0;
685 Status = SampRegQueryValue(DomainKeyHandle,
686 L"Name",
687 NULL,
688 NULL,
689 &DataLength);
690 TRACE("SampRegQueryValue returned %08lX\n", Status);
691 if (NT_SUCCESS(Status))
692 {
693 TRACE("Data length: %lu\n", DataLength);
694
695 if ((RequiredLength + DataLength + sizeof(UNICODE_STRING)) > PreferedMaximumLength)
696 break;
697
699 EnumCount++;
700 }
701
702 SampRegCloseKey(&DomainKeyHandle);
703 }
704
705 EnumIndex++;
706 }
707
708 TRACE("EnumCount: %lu\n", EnumCount);
709 TRACE("RequiredLength: %lu\n", RequiredLength);
710
711 EnumBuffer = midl_user_allocate(sizeof(SAMPR_ENUMERATION_BUFFER));
712 if (EnumBuffer == NULL)
713 {
715 goto done;
716 }
717
718 EnumBuffer->EntriesRead = EnumCount;
719 EnumBuffer->Buffer = midl_user_allocate(EnumCount * sizeof(SAMPR_RID_ENUMERATION));
720 if (EnumBuffer->Buffer == NULL)
721 {
723 goto done;
724 }
725
726 EnumIndex = *EnumerationContext;
727 for (i = 0; i < EnumCount; i++, EnumIndex++)
728 {
729 Status = SampRegEnumerateSubKey(DomainsKeyHandle,
730 EnumIndex,
731 64 * sizeof(WCHAR),
732 DomainKeyName);
733 if (!NT_SUCCESS(Status))
734 break;
735
736 TRACE("EnumIndex: %lu\n", EnumIndex);
737 TRACE("Domain key name: %S\n", DomainKeyName);
738
739 Status = SampRegOpenKey(DomainsKeyHandle,
740 DomainKeyName,
741 KEY_READ,
742 &DomainKeyHandle);
743 TRACE("SampRegOpenKey returned %08lX\n", Status);
744 if (NT_SUCCESS(Status))
745 {
746 DataLength = 0;
747 Status = SampRegQueryValue(DomainKeyHandle,
748 L"Name",
749 NULL,
750 NULL,
751 &DataLength);
752 TRACE("SampRegQueryValue returned %08lX\n", Status);
753 if (NT_SUCCESS(Status))
754 {
755 EnumBuffer->Buffer[i].RelativeId = 0;
756 EnumBuffer->Buffer[i].Name.Length = (USHORT)DataLength - sizeof(WCHAR);
757 EnumBuffer->Buffer[i].Name.MaximumLength = (USHORT)DataLength;
759 if (EnumBuffer->Buffer[i].Name.Buffer == NULL)
760 {
761 SampRegCloseKey(&DomainKeyHandle);
763 goto done;
764 }
765
766 Status = SampRegQueryValue(DomainKeyHandle,
767 L"Name",
768 NULL,
769 EnumBuffer->Buffer[i].Name.Buffer,
770 &DataLength);
771 TRACE("SampRegQueryValue returned %08lX\n", Status);
772 if (NT_SUCCESS(Status))
773 {
774 TRACE("Domain name: %S\n", EnumBuffer->Buffer[i].Name.Buffer);
775 }
776 }
777
778 SampRegCloseKey(&DomainKeyHandle);
779
780 if (!NT_SUCCESS(Status))
781 goto done;
782 }
783 }
784
785 if (NT_SUCCESS(Status))
786 {
787 *EnumerationContext += EnumCount;
788 *Buffer = EnumBuffer;
789 *CountReturned = EnumCount;
790 }
791
792done:
793 SampRegCloseKey(&DomainKeyHandle);
794 SampRegCloseKey(&DomainsKeyHandle);
795
796 if (!NT_SUCCESS(Status))
797 {
798 *EnumerationContext = 0;
799 *Buffer = NULL;
800 *CountReturned = 0;
801
802 if (EnumBuffer != NULL)
803 {
804 if (EnumBuffer->Buffer != NULL)
805 {
806 if (EnumBuffer->EntriesRead != 0)
807 {
808 for (i = 0; i < EnumBuffer->EntriesRead; i++)
809 {
810 if (EnumBuffer->Buffer[i].Name.Buffer != NULL)
811 midl_user_free(EnumBuffer->Buffer[i].Name.Buffer);
812 }
813 }
814
815 midl_user_free(EnumBuffer->Buffer);
816 }
817
818 midl_user_free(EnumBuffer);
819 }
820 }
821
823
824 return Status;
825}
NTSTATUS SampRegQueryValue(IN HANDLE KeyHandle, IN LPCWSTR ValueName, OUT PULONG Type OPTIONAL, OUT PVOID Data OPTIONAL, IN OUT PULONG DataLength OPTIONAL)
Definition: registry.c:332
NTSTATUS SampRegEnumerateSubKey(IN HANDLE KeyHandle, IN ULONG Index, IN ULONG Length, OUT LPWSTR Buffer)
Definition: registry.c:101
struct _UNICODE_STRING UNICODE_STRING
#define SAM_SERVER_ENUMERATE_DOMAINS
Definition: ntsam.h:103

Referenced by SamEnumerateDomainsInSamServer().

◆ SamrEnumerateGroupsInDomain()

NTSTATUS NTAPI SamrEnumerateGroupsInDomain ( IN SAMPR_HANDLE  DomainHandle,
IN OUT unsigned long *  EnumerationContext,
OUT PSAMPR_ENUMERATION_BUFFER *  Buffer,
IN unsigned long  PreferedMaximumLength,
OUT unsigned long *  CountReturned 
)

Definition at line 2092 of file samrpc.c.

2097{
2098 PSAMPR_ENUMERATION_BUFFER EnumBuffer = NULL;
2099 PSAM_DB_OBJECT DomainObject;
2100 HANDLE GroupsKeyHandle = NULL;
2101 HANDLE NamesKeyHandle = NULL;
2102 WCHAR GroupName[64];
2103 ULONG EnumIndex;
2104 ULONG EnumCount = 0;
2108 ULONG Rid;
2109 ULONG i;
2110 BOOLEAN MoreEntries = FALSE;
2112
2113 TRACE("SamrEnumerateUsersInDomain(%p %p %p %lu %p)\n",
2114 DomainHandle, EnumerationContext, Buffer,
2115 PreferedMaximumLength, CountReturned);
2116
2118 TRUE);
2119
2120 /* Validate the domain handle */
2121 Status = SampValidateDbObject(DomainHandle,
2124 &DomainObject);
2125 if (!NT_SUCCESS(Status))
2126 goto done;
2127
2128 Status = SampRegOpenKey(DomainObject->KeyHandle,
2129 L"Groups",
2130 KEY_READ,
2131 &GroupsKeyHandle);
2132 if (!NT_SUCCESS(Status))
2133 goto done;
2134
2135 Status = SampRegOpenKey(GroupsKeyHandle,
2136 L"Names",
2137 KEY_READ,
2138 &NamesKeyHandle);
2139 if (!NT_SUCCESS(Status))
2140 goto done;
2141
2142 TRACE("Part 1\n");
2143
2144 EnumIndex = *EnumerationContext;
2145
2146 while (TRUE)
2147 {
2148 NameLength = 64 * sizeof(WCHAR);
2149 Status = SampRegEnumerateValue(NamesKeyHandle,
2150 EnumIndex,
2151 GroupName,
2152 &NameLength,
2153 NULL,
2154 NULL,
2155 NULL);
2156 if (!NT_SUCCESS(Status))
2157 {
2160 break;
2161 }
2162
2163 TRACE("EnumIndex: %lu\n", EnumIndex);
2164 TRACE("Group name: %S\n", GroupName);
2165 TRACE("Name length: %lu\n", NameLength);
2166
2167 if ((RequiredLength + NameLength + sizeof(UNICODE_NULL) + sizeof(SAMPR_RID_ENUMERATION)) > PreferedMaximumLength)
2168 {
2169 MoreEntries = TRUE;
2170 break;
2171 }
2172
2174 EnumCount++;
2175
2176 EnumIndex++;
2177 }
2178
2179 TRACE("EnumCount: %lu\n", EnumCount);
2180 TRACE("RequiredLength: %lu\n", RequiredLength);
2181
2182 if (!NT_SUCCESS(Status))
2183 goto done;
2184
2185 EnumBuffer = midl_user_allocate(sizeof(SAMPR_ENUMERATION_BUFFER));
2186 if (EnumBuffer == NULL)
2187 {
2189 goto done;
2190 }
2191
2192 EnumBuffer->EntriesRead = EnumCount;
2193 if (EnumCount == 0)
2194 {
2196 goto done;
2197 }
2198
2199 EnumBuffer->Buffer = midl_user_allocate(EnumCount * sizeof(SAMPR_RID_ENUMERATION));
2200 if (EnumBuffer->Buffer == NULL)
2201 {
2203 goto done;
2204 }
2205
2206 TRACE("Part 2\n");
2207
2208 EnumIndex = *EnumerationContext;
2209 for (i = 0; i < EnumCount; i++, EnumIndex++)
2210 {
2211 NameLength = 64 * sizeof(WCHAR);
2212 DataLength = sizeof(ULONG);
2213 Status = SampRegEnumerateValue(NamesKeyHandle,
2214 EnumIndex,
2215 GroupName,
2216 &NameLength,
2217 NULL,
2218 &Rid,
2219 &DataLength);
2220 if (!NT_SUCCESS(Status))
2221 {
2224 break;
2225 }
2226
2227 TRACE("EnumIndex: %lu\n", EnumIndex);
2228 TRACE("Group name: %S\n", GroupName);
2229 TRACE("Name length: %lu\n", NameLength);
2230 TRACE("RID: %lu\n", Rid);
2231
2232 EnumBuffer->Buffer[i].RelativeId = Rid;
2233
2234 EnumBuffer->Buffer[i].Name.Length = (USHORT)NameLength;
2235 EnumBuffer->Buffer[i].Name.MaximumLength = (USHORT)(NameLength + sizeof(UNICODE_NULL));
2236
2237/* FIXME: Disabled because of bugs in widl and rpcrt4 */
2238#if 0
2239 EnumBuffer->Buffer[i].Name.Buffer = midl_user_allocate(EnumBuffer->Buffer[i].Name.MaximumLength);
2240 if (EnumBuffer->Buffer[i].Name.Buffer == NULL)
2241 {
2243 goto done;
2244 }
2245
2246 memcpy(EnumBuffer->Buffer[i].Name.Buffer,
2247 GroupName,
2248 EnumBuffer->Buffer[i].Name.Length);
2249#endif
2250 }
2251
2252done:
2253 if (NT_SUCCESS(Status))
2254 {
2255 *EnumerationContext += EnumCount;
2256 *Buffer = EnumBuffer;
2257 *CountReturned = EnumCount;
2258 }
2259 else
2260 {
2261 *EnumerationContext = 0;
2262 *Buffer = NULL;
2263 *CountReturned = 0;
2264
2265 if (EnumBuffer != NULL)
2266 {
2267 if (EnumBuffer->Buffer != NULL)
2268 {
2269 if (EnumBuffer->EntriesRead != 0)
2270 {
2271 for (i = 0; i < EnumBuffer->EntriesRead; i++)
2272 {
2273 if (EnumBuffer->Buffer[i].Name.Buffer != NULL)
2274 midl_user_free(EnumBuffer->Buffer[i].Name.Buffer);
2275 }
2276 }
2277
2278 midl_user_free(EnumBuffer->Buffer);
2279 }
2280
2281 midl_user_free(EnumBuffer);
2282 }
2283 }
2284
2285 SampRegCloseKey(&NamesKeyHandle);
2286 SampRegCloseKey(&GroupsKeyHandle);
2287
2288 if ((Status == STATUS_SUCCESS) && (MoreEntries != FALSE))
2290
2292
2293 return Status;
2294}

Referenced by SamEnumerateGroupsInDomain().

◆ SamrEnumerateUsersInDomain()

NTSTATUS NTAPI SamrEnumerateUsersInDomain ( IN SAMPR_HANDLE  DomainHandle,
IN OUT unsigned long *  EnumerationContext,
IN unsigned long  UserAccountControl,
OUT PSAMPR_ENUMERATION_BUFFER *  Buffer,
IN unsigned long  PreferedMaximumLength,
OUT unsigned long *  CountReturned 
)

Definition at line 2704 of file samrpc.c.

2710{
2711 PSAMPR_ENUMERATION_BUFFER EnumBuffer = NULL;
2712 PSAM_DB_OBJECT DomainObject;
2713 HANDLE UsersKeyHandle = NULL;
2714 HANDLE NamesKeyHandle = NULL;
2715 WCHAR UserName[64];
2716 ULONG EnumIndex;
2717 ULONG EnumCount = 0;
2721 ULONG Rid;
2722 ULONG i;
2723 BOOLEAN MoreEntries = FALSE;
2725
2726 TRACE("SamrEnumerateUsersInDomain(%p %p %lx %p %lu %p)\n",
2727 DomainHandle, EnumerationContext, UserAccountControl, Buffer,
2728 PreferedMaximumLength, CountReturned);
2729
2731 TRUE);
2732
2733 /* Validate the domain handle */
2734 Status = SampValidateDbObject(DomainHandle,
2737 &DomainObject);
2738 if (!NT_SUCCESS(Status))
2739 goto done;
2740
2741 Status = SampRegOpenKey(DomainObject->KeyHandle,
2742 L"Users",
2743 KEY_READ,
2744 &UsersKeyHandle);
2745 if (!NT_SUCCESS(Status))
2746 goto done;
2747
2748 Status = SampRegOpenKey(UsersKeyHandle,
2749 L"Names",
2750 KEY_READ,
2751 &NamesKeyHandle);
2752 if (!NT_SUCCESS(Status))
2753 goto done;
2754
2755 TRACE("Part 1\n");
2756
2757 EnumIndex = *EnumerationContext;
2758
2759 while (TRUE)
2760 {
2761 NameLength = 64 * sizeof(WCHAR);
2762 Status = SampRegEnumerateValue(NamesKeyHandle,
2763 EnumIndex,
2764 UserName,
2765 &NameLength,
2766 NULL,
2767 NULL,
2768 NULL);
2769 if (!NT_SUCCESS(Status))
2770 {
2773 break;
2774 }
2775
2776 TRACE("EnumIndex: %lu\n", EnumIndex);
2777 TRACE("User name: %S\n", UserName);
2778 TRACE("Name length: %lu\n", NameLength);
2779
2780 if ((RequiredLength + NameLength + sizeof(UNICODE_NULL) + sizeof(SAMPR_RID_ENUMERATION)) > PreferedMaximumLength)
2781 {
2782 MoreEntries = TRUE;
2783 break;
2784 }
2785
2787 EnumCount++;
2788
2789 EnumIndex++;
2790 }
2791
2792 TRACE("EnumCount: %lu\n", EnumCount);
2793 TRACE("RequiredLength: %lu\n", RequiredLength);
2794
2795 if (!NT_SUCCESS(Status))
2796 goto done;
2797
2798 EnumBuffer = midl_user_allocate(sizeof(SAMPR_ENUMERATION_BUFFER));
2799 if (EnumBuffer == NULL)
2800 {
2802 goto done;
2803 }
2804
2805 EnumBuffer->EntriesRead = EnumCount;
2806 if (EnumCount == 0)
2807 {
2809 goto done;
2810 }
2811
2812 EnumBuffer->Buffer = midl_user_allocate(EnumCount * sizeof(SAMPR_RID_ENUMERATION));
2813 if (EnumBuffer->Buffer == NULL)
2814 {
2816 goto done;
2817 }
2818
2819 TRACE("Part 2\n");
2820
2821 EnumIndex = *EnumerationContext;
2822 for (i = 0; i < EnumCount; i++, EnumIndex++)
2823 {
2824 NameLength = 64 * sizeof(WCHAR);
2825 DataLength = sizeof(ULONG);
2826 Status = SampRegEnumerateValue(NamesKeyHandle,
2827 EnumIndex,
2828 UserName,
2829 &NameLength,
2830 NULL,
2831 &Rid,
2832 &DataLength);
2833 if (!NT_SUCCESS(Status))
2834 {
2837 break;
2838 }
2839
2840 TRACE("EnumIndex: %lu\n", EnumIndex);
2841 TRACE("User name: %S\n", UserName);
2842 TRACE("Name length: %lu\n", NameLength);
2843 TRACE("RID: %lu\n", Rid);
2844
2845 EnumBuffer->Buffer[i].RelativeId = Rid;
2846
2847 EnumBuffer->Buffer[i].Name.Length = (USHORT)NameLength;
2848 EnumBuffer->Buffer[i].Name.MaximumLength = (USHORT)(NameLength + sizeof(UNICODE_NULL));
2849
2850/* FIXME: Disabled because of bugs in widl and rpcrt4 */
2851#if 0
2852 EnumBuffer->Buffer[i].Name.Buffer = midl_user_allocate(EnumBuffer->Buffer[i].Name.MaximumLength);
2853 if (EnumBuffer->Buffer[i].Name.Buffer == NULL)
2854 {
2856 goto done;
2857 }
2858
2859 memcpy(EnumBuffer->Buffer[i].Name.Buffer,
2860 UserName,
2861 EnumBuffer->Buffer[i].Name.Length);
2862#endif
2863 }
2864
2865done:
2866 if (NT_SUCCESS(Status))
2867 {
2868 *EnumerationContext += EnumCount;
2869 *Buffer = EnumBuffer;
2870 *CountReturned = EnumCount;
2871 }
2872 else
2873 {
2874 *EnumerationContext = 0;
2875 *Buffer = NULL;
2876 *CountReturned = 0;
2877
2878 if (EnumBuffer != NULL)
2879 {
2880 if (EnumBuffer->Buffer != NULL)
2881 {
2882 if (EnumBuffer->EntriesRead != 0)
2883 {
2884 for (i = 0; i < EnumBuffer->EntriesRead; i++)
2885 {
2886 if (EnumBuffer->Buffer[i].Name.Buffer != NULL)
2887 midl_user_free(EnumBuffer->Buffer[i].Name.Buffer);
2888 }
2889 }
2890
2891 midl_user_free(EnumBuffer->Buffer);
2892 }
2893
2894 midl_user_free(EnumBuffer);
2895 }
2896 }
2897
2898 SampRegCloseKey(&NamesKeyHandle);
2899 SampRegCloseKey(&UsersKeyHandle);
2900
2901 if ((Status == STATUS_SUCCESS) && (MoreEntries != FALSE))
2903
2905
2906 return Status;
2907}

Referenced by SamEnumerateUsersInDomain().

◆ SamrGetAliasMembership()

NTSTATUS NTAPI SamrGetAliasMembership ( IN SAMPR_HANDLE  DomainHandle,
IN PSAMPR_PSID_ARRAY  SidArray,
OUT PSAMPR_ULONG_ARRAY  Membership 
)

Definition at line 3297 of file samrpc.c.

3300{
3301 PSAM_DB_OBJECT DomainObject;
3302 HANDLE AliasesKeyHandle = NULL;
3303 HANDLE MembersKeyHandle = NULL;
3304 HANDLE MemberKeyHandle = NULL;
3305 LPWSTR MemberSidString = NULL;
3306 PULONG RidArray = NULL;
3307 ULONG MaxSidCount = 0;
3308 ULONG ValueCount;
3310 ULONG i, j;
3311 ULONG RidIndex;
3313 WCHAR NameBuffer[9];
3314
3315 TRACE("SamrGetAliasMembership(%p %p %p)\n",
3316 DomainHandle, SidArray, Membership);
3317
3319 TRUE);
3320
3321 /* Validate the domain handle */
3322 Status = SampValidateDbObject(DomainHandle,
3325 &DomainObject);
3326 if (!NT_SUCCESS(Status))
3327 goto done;
3328
3329 Status = SampRegOpenKey(DomainObject->KeyHandle,
3330 L"Aliases",
3331 KEY_READ,
3332 &AliasesKeyHandle);
3333 TRACE("SampRegOpenKey returned %08lX\n", Status);
3334 if (!NT_SUCCESS(Status))
3335 goto done;
3336
3337 Status = SampRegOpenKey(AliasesKeyHandle,
3338 L"Members",
3339 KEY_READ,
3340 &MembersKeyHandle);
3341 TRACE("SampRegOpenKey returned %08lX\n", Status);
3342
3344 {
3346 goto done;
3347 }
3348
3349 if (!NT_SUCCESS(Status))
3350 goto done;
3351
3352 for (i = 0; i < SidArray->Count; i++)
3353 {
3354 ConvertSidToStringSid(SidArray->Sids[i].SidPointer, &MemberSidString);
3355TRACE("Open %S\n", MemberSidString);
3356
3357 Status = SampRegOpenKey(MembersKeyHandle,
3358 MemberSidString,
3359 KEY_READ,
3360 &MemberKeyHandle);
3361 TRACE("SampRegOpenKey returned %08lX\n", Status);
3362 if (NT_SUCCESS(Status))
3363 {
3364 Status = SampRegQueryKeyInfo(MemberKeyHandle,
3365 NULL,
3366 &ValueCount);
3367 if (NT_SUCCESS(Status))
3368 {
3369 TRACE("Found %lu values\n", ValueCount);
3370 MaxSidCount += ValueCount;
3371 }
3372
3373 SampRegCloseKey(&MemberKeyHandle);
3374 }
3375
3378
3379 LocalFree(MemberSidString);
3380 }
3381
3382 if (MaxSidCount == 0)
3383 {
3385 goto done;
3386 }
3387
3388 TRACE("Maximum sid count: %lu\n", MaxSidCount);
3389 RidArray = midl_user_allocate(MaxSidCount * sizeof(ULONG));
3390 if (RidArray == NULL)
3391 {
3393 goto done;
3394 }
3395
3396 RidIndex = 0;
3397 for (i = 0; i < SidArray->Count; i++)
3398 {
3399 ConvertSidToStringSid(SidArray->Sids[i].SidPointer, &MemberSidString);
3400TRACE("Open %S\n", MemberSidString);
3401
3402 Status = SampRegOpenKey(MembersKeyHandle,
3403 MemberSidString,
3404 KEY_READ,
3405 &MemberKeyHandle);
3406 TRACE("SampRegOpenKey returned %08lX\n", Status);
3407 if (NT_SUCCESS(Status))
3408 {
3409 Status = SampRegQueryKeyInfo(MemberKeyHandle,
3410 NULL,
3411 &ValueCount);
3412 if (NT_SUCCESS(Status))
3413 {
3414 TRACE("Found %lu values\n", ValueCount);
3415
3416 for (j = 0; j < ValueCount; j++)
3417 {
3418 DataLength = 9 * sizeof(WCHAR);
3419 Status = SampRegEnumerateValue(MemberKeyHandle,
3420 j,
3421 NameBuffer,
3422 &DataLength,
3423 NULL,
3424 NULL,
3425 NULL);
3426 if (NT_SUCCESS(Status))
3427 {
3428 /* FIXME: Do not return each RID more than once. */
3429 RidArray[RidIndex] = wcstoul(NameBuffer, NULL, 16);
3430 RidIndex++;
3431 }
3432 }
3433 }
3434
3435 SampRegCloseKey(&MemberKeyHandle);
3436 }
3437
3440
3441 LocalFree(MemberSidString);
3442 }
3443
3444done:
3445 SampRegCloseKey(&MembersKeyHandle);
3446 SampRegCloseKey(&AliasesKeyHandle);
3447
3448 if (NT_SUCCESS(Status))
3449 {
3450 Membership->Count = MaxSidCount;
3451 Membership->Element = RidArray;
3452 }
3453 else
3454 {
3455 if (RidArray != NULL)
3456 midl_user_free(RidArray);
3457 }
3458
3460
3461 return Status;
3462}
_ACRTIMP __msvcrt_ulong __cdecl wcstoul(const wchar_t *, wchar_t **, int)
Definition: wcs.c:2917
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble const GLfloat const GLdouble const GLfloat GLint GLint GLint j
Definition: glfuncs.h:250
HLOCAL NTAPI LocalFree(HLOCAL hMem)
Definition: heapmem.c:1594
#define DOMAIN_GET_ALIAS_MEMBERSHIP
Definition: ntsam.h:40
#define ConvertSidToStringSid
Definition: sddl.h:160
uint32_t * PULONG
Definition: typedefs.h:59
uint16_t * LPWSTR
Definition: typedefs.h:56

◆ SamrGetBootKeyInformation()

NTSTATUS NTAPI SamrGetBootKeyInformation ( IN handle_t  BindingHandle)

Definition at line 9686 of file samrpc.c.

9687{
9690}

◆ SamrGetDisplayEnumerationIndex()

NTSTATUS NTAPI SamrGetDisplayEnumerationIndex ( IN SAMPR_HANDLE  DomainHandle,
IN DOMAIN_DISPLAY_INFORMATION  DisplayInformationClass,
IN PRPC_UNICODE_STRING  Prefix,
OUT unsigned long *  Index 
)

Definition at line 8280 of file samrpc.c.

8284{
8285 TRACE("SamrGetDisplayEnumerationIndex(%p %lu %p %p)\n",
8286 DomainHandle, DisplayInformationClass, Prefix, Index);
8287
8288 return SamrGetDisplayEnumerationIndex2(DomainHandle,
8289 DisplayInformationClass,
8290 Prefix,
8291 Index);
8292}
NTSTATUS NTAPI SamrGetDisplayEnumerationIndex2(IN SAMPR_HANDLE DomainHandle, IN DOMAIN_DISPLAY_INFORMATION DisplayInformationClass, IN PRPC_UNICODE_STRING Prefix, OUT unsigned long *Index)
Definition: samrpc.c:8813
_In_ WDFCOLLECTION _In_ ULONG Index
_In_ __drv_aliasesMem PSTRING Prefix
Definition: rtlfuncs.h:1647

◆ SamrGetDisplayEnumerationIndex2()

NTSTATUS NTAPI SamrGetDisplayEnumerationIndex2 ( IN SAMPR_HANDLE  DomainHandle,
IN DOMAIN_DISPLAY_INFORMATION  DisplayInformationClass,
IN PRPC_UNICODE_STRING  Prefix,
OUT unsigned long *  Index 
)

Definition at line 8813 of file samrpc.c.

8817{
8818 TRACE("SamrGetDisplayEnumerationIndex2(%p %lu %p %p)\n",
8819 DomainHandle, DisplayInformationClass, Prefix, Index);
8820
8823}

Referenced by SamGetDisplayEnumerationIndex(), and SamrGetDisplayEnumerationIndex().

◆ SamrGetDomainPasswordInformation()

NTSTATUS NTAPI SamrGetDomainPasswordInformation ( IN handle_t  BindingHandle,
IN PRPC_UNICODE_STRING  Unused,
OUT PUSER_DOMAIN_PASSWORD_INFORMATION  PasswordInformation 
)

Definition at line 9382 of file samrpc.c.

9385{
9386 SAMPR_HANDLE ServerHandle = NULL;
9387 PSAM_DB_OBJECT DomainObject = NULL;
9388 SAM_DOMAIN_FIXED_DATA FixedData;
9389 ULONG Length;
9391
9392 TRACE("SamrGetDomainPasswordInformation(%p %p %p)\n",
9393 BindingHandle, Unused, PasswordInformation);
9394
9396 &ServerHandle,
9398 if (!NT_SUCCESS(Status))
9399 {
9400 TRACE("SamrConnect() failed (Status 0x%08lx)\n", Status);
9401 goto done;
9402 }
9403
9404 Status = SampOpenDbObject((PSAM_DB_OBJECT)ServerHandle,
9405 L"Domains",
9406 L"Account",
9407 0,
9410 &DomainObject);
9411 if (!NT_SUCCESS(Status))
9412 {
9413 TRACE("SampOpenDbObject() failed (Status 0x%08lx)\n", Status);
9414 goto done;
9415 }
9416
9417 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
9418 Status = SampGetObjectAttribute(DomainObject,
9419 L"F",
9420 NULL,
9421 &FixedData,
9422 &Length);
9423 if (!NT_SUCCESS(Status))
9424 {
9425 TRACE("SampGetObjectAttribute() failed (Status 0x%08lx)\n", Status);
9426 goto done;
9427 }
9428
9429 PasswordInformation->MinPasswordLength = FixedData.MinPasswordLength;
9430 PasswordInformation->PasswordProperties = FixedData.PasswordProperties;
9431
9432done:
9433 if (DomainObject != NULL)
9434 SampCloseDbObject(DomainObject);
9435
9436 if (ServerHandle != NULL)
9437 SamrCloseHandle(&ServerHandle);
9438
9439 return Status;
9440}
#define Unused(x)
Definition: atlwin.h:28
#define SAM_SERVER_LOOKUP_DOMAIN
Definition: ntsam.h:104
#define DOMAIN_READ_PASSWORD_PARAMETERS
Definition: ntsam.h:33
NTSTATUS NTAPI SamrCloseHandle(IN OUT SAMPR_HANDLE *SamHandle)
Definition: samrpc.c:161
NTSTATUS NTAPI SamrConnect(IN PSAMPR_SERVER_NAME ServerName, OUT SAMPR_HANDLE *ServerHandle, IN ACCESS_MASK DesiredAccess)
Definition: samrpc.c:135
_In_ ULONG _Out_ HANDLE * BindingHandle
Definition: tdikrnl.h:1147

◆ SamrGetGroupsForUser()

NTSTATUS NTAPI SamrGetGroupsForUser ( IN SAMPR_HANDLE  UserHandle,
OUT PSAMPR_GET_GROUPS_BUFFER *  Groups 
)

Definition at line 8149 of file samrpc.c.

8151{
8152 PSAMPR_GET_GROUPS_BUFFER GroupsBuffer = NULL;
8153 PSAM_DB_OBJECT UserObject;
8154 ULONG Length = 0;
8156
8157 TRACE("SamrGetGroupsForUser(%p %p)\n",
8158 UserHandle, Groups);
8159
8161 TRUE);
8162
8163 /* Validate the user handle */
8164 Status = SampValidateDbObject(UserHandle,
8167 &UserObject);
8168 if (!NT_SUCCESS(Status))
8169 {
8170 TRACE("SampValidateDbObject failed with status 0x%08lx\n", Status);
8171 goto done;
8172 }
8173
8174 /* Allocate the groups buffer */
8175 GroupsBuffer = midl_user_allocate(sizeof(SAMPR_GET_GROUPS_BUFFER));
8176 if (GroupsBuffer == NULL)
8177 {
8179 goto done;
8180 }
8181
8182 /*
8183 * Get the size of the Groups attribute.
8184 * Do not check the status code because in case of an error
8185 * Length will be 0. And that is all we need.
8186 */
8187 SampGetObjectAttribute(UserObject,
8188 L"Groups",
8189 NULL,
8190 NULL,
8191 &Length);
8192
8193 /* If there is no Groups attribute, return a groups buffer without an array */
8194 if (Length == 0)
8195 {
8196 GroupsBuffer->MembershipCount = 0;
8197 GroupsBuffer->Groups = NULL;
8198
8199 *Groups = GroupsBuffer;
8200
8202 goto done;
8203 }
8204
8205 /* Allocate a buffer for the Groups attribute */
8206 GroupsBuffer->Groups = midl_user_allocate(Length);
8207 if (GroupsBuffer->Groups == NULL)
8208 {
8210 goto done;
8211 }
8212
8213 /* Retrieve the Grous attribute */
8214 Status = SampGetObjectAttribute(UserObject,
8215 L"Groups",
8216 NULL,
8217 GroupsBuffer->Groups,
8218 &Length);
8219 if (!NT_SUCCESS(Status))
8220 {
8221 TRACE("SampGetObjectAttribute failed with status 0x%08lx\n", Status);
8222 goto done;
8223 }
8224
8225 /* Calculate the membership count */
8226 GroupsBuffer->MembershipCount = Length / sizeof(GROUP_MEMBERSHIP);
8227
8228 /* Return the groups buffer to the caller */
8229 *Groups = GroupsBuffer;
8230
8231done:
8232 if (!NT_SUCCESS(Status))
8233 {
8234 if (GroupsBuffer != NULL)
8235 {
8236 if (GroupsBuffer->Groups != NULL)
8237 midl_user_free(GroupsBuffer->Groups);
8238
8239 midl_user_free(GroupsBuffer);
8240 }
8241 }
8242
8244
8245 return Status;
8246}
#define USER_LIST_GROUPS
Definition: ntsam.h:134
struct _GROUP_MEMBERSHIP GROUP_MEMBERSHIP
unsigned long MembershipCount
Definition: sam.idl:115
PGROUP_MEMBERSHIP Groups
Definition: sam.idl:116

Referenced by SamGetGroupsForUser().

◆ SamrGetMembersInAlias()

NTSTATUS NTAPI SamrGetMembersInAlias ( IN SAMPR_HANDLE  AliasHandle,
OUT PSAMPR_PSID_ARRAY_OUT  Members 
)

Definition at line 5364 of file samrpc.c.

5366{
5367 PSAM_DB_OBJECT AliasObject;
5368 PSAMPR_SID_INFORMATION MemberArray = NULL;
5369 ULONG MemberCount = 0;
5370 ULONG Index;
5372
5373 TRACE("SamrGetMembersInAlias(%p %p %p)\n",
5374 AliasHandle, Members);
5375
5377 TRUE);
5378
5379 /* Validate the alias handle */
5380 Status = SampValidateDbObject(AliasHandle,
5383 &AliasObject);
5384 if (!NT_SUCCESS(Status))
5385 {
5386 ERR("failed with status 0x%08lx\n", Status);
5387 goto done;
5388 }
5389
5390 Status = SampGetMembersInAlias(AliasObject,
5391 &MemberCount,
5392 &MemberArray);
5393
5394 /* Return the number of members and the member array */
5395 if (NT_SUCCESS(Status))
5396 {
5397 Members->Count = MemberCount;
5398 Members->Sids = MemberArray;
5399 }
5400
5401done:
5402 /* Clean up the members array and the SID buffers if something failed */
5403 if (!NT_SUCCESS(Status))
5404 {
5405 if (MemberArray != NULL)
5406 {
5407 for (Index = 0; Index < MemberCount; Index++)
5408 {
5409 if (MemberArray[Index].SidPointer != NULL)
5410 midl_user_free(MemberArray[Index].SidPointer);
5411 }
5412
5413 midl_user_free(MemberArray);
5414 }
5415 }
5416
5418
5419 return Status;
5420}
#define ERR(fmt,...)
Definition: precomp.h:57
NTSTATUS SampGetMembersInAlias(IN PSAM_DB_OBJECT AliasObject, OUT PULONG MemberCount, OUT PSAMPR_SID_INFORMATION *MemberArray)
Definition: alias.c:218
#define ALIAS_LIST_MEMBERS
Definition: ntsam.h:11

Referenced by SamGetMembersInAlias().

◆ SamrGetMembersInGroup()

NTSTATUS NTAPI SamrGetMembersInGroup ( IN SAMPR_HANDLE  GroupHandle,
OUT PSAMPR_GET_MEMBERS_BUFFER *  Members 
)

Definition at line 4668 of file samrpc.c.

4670{
4671 PSAMPR_GET_MEMBERS_BUFFER MembersBuffer = NULL;
4672 PSAM_DB_OBJECT GroupObject;
4673 ULONG Length = 0;
4674 ULONG i;
4676
4677 TRACE("SamrGetMembersInGroup(%p %p)\n",
4678 GroupHandle, Members);
4679
4681 TRUE);
4682
4683 /* Validate the group handle */
4684 Status = SampValidateDbObject(GroupHandle,
4687 &GroupObject);
4688 if (!NT_SUCCESS(Status))
4689 goto done;
4690
4691 MembersBuffer = midl_user_allocate(sizeof(SAMPR_GET_MEMBERS_BUFFER));
4692 if (MembersBuffer == NULL)
4693 {
4695 goto done;
4696 }
4697
4698 SampGetObjectAttribute(GroupObject,
4699 L"Members",
4700 NULL,
4701 NULL,
4702 &Length);
4703
4704 if (Length == 0)
4705 {
4706 MembersBuffer->MemberCount = 0;
4707 MembersBuffer->Members = NULL;
4708 MembersBuffer->Attributes = NULL;
4709
4710 *Members = MembersBuffer;
4711
4713 goto done;
4714 }
4715
4716 MembersBuffer->Members = midl_user_allocate(Length);
4717 if (MembersBuffer->Members == NULL)
4718 {
4720 goto done;
4721 }
4722
4723 MembersBuffer->Attributes = midl_user_allocate(Length);
4724 if (MembersBuffer->Attributes == NULL)
4725 {
4727 goto done;
4728 }
4729
4730 Status = SampGetObjectAttribute(GroupObject,
4731 L"Members",
4732 NULL,
4733 MembersBuffer->Members,
4734 &Length);
4735 if (!NT_SUCCESS(Status))
4736 {
4737 TRACE("SampGetObjectAttributes() failed (Status 0x%08lx)\n", Status);
4738 goto done;
4739 }
4740
4741 MembersBuffer->MemberCount = Length / sizeof(ULONG);
4742
4743 for (i = 0; i < MembersBuffer->MemberCount; i++)
4744 {
4746 MembersBuffer->Members[i],
4747 GroupObject->RelativeId,
4748 &(MembersBuffer->Attributes[i]));
4749 if (!NT_SUCCESS(Status))
4750 {
4751 TRACE("SampGetUserGroupAttributes() failed (Status 0x%08lx)\n", Status);
4752 goto done;
4753 }
4754 }
4755
4756 *Members = MembersBuffer;
4757
4758done:
4759 if (!NT_SUCCESS(Status))
4760 {
4761 if (MembersBuffer != NULL)
4762 {
4763 if (MembersBuffer->Members != NULL)
4764 midl_user_free(MembersBuffer->Members);
4765
4766 if (MembersBuffer->Attributes != NULL)
4767 midl_user_free(MembersBuffer->Attributes);
4768
4769 midl_user_free(MembersBuffer);
4770 }
4771 }
4772
4774
4775 return Status;
4776}
NTSTATUS SampGetUserGroupAttributes(IN PSAM_DB_OBJECT DomainObject, IN ULONG UserId, IN ULONG GroupId, OUT PULONG GroupAttributes)
Definition: user.c:183
#define GROUP_LIST_MEMBERS
Definition: ntsam.h:79
unsigned long * Members
Definition: sam.idl:122
unsigned long MemberCount
Definition: sam.idl:121
unsigned long * Attributes
Definition: sam.idl:123

Referenced by SamGetMembersInGroup().

◆ SamrGetUserDomainPasswordInformation()

NTSTATUS NTAPI SamrGetUserDomainPasswordInformation ( IN SAMPR_HANDLE  UserHandle,
OUT PUSER_DOMAIN_PASSWORD_INFORMATION  PasswordInformation 
)

Definition at line 8318 of file samrpc.c.

8320{
8321 SAM_DOMAIN_FIXED_DATA DomainFixedData;
8322 SAM_USER_FIXED_DATA UserFixedData;
8323 PSAM_DB_OBJECT DomainObject;
8324 PSAM_DB_OBJECT UserObject;
8325 ULONG Length = 0;
8327
8328 TRACE("SamrGetUserDomainPasswordInformation(%p %p)\n",
8329 UserHandle, PasswordInformation);
8330
8332 TRUE);
8333
8334 /* Validate the user handle */
8335 Status = SampValidateDbObject(UserHandle,
8337 0,
8338 &UserObject);
8339 if (!NT_SUCCESS(Status))
8340 {
8341 TRACE("SampValidateDbObject failed with status 0x%08lx\n", Status);
8342 goto done;
8343 }
8344
8345 /* Validate the domain object */
8349 &DomainObject);
8350 if (!NT_SUCCESS(Status))
8351 {
8352 TRACE("SampValidateDbObject failed with status 0x%08lx\n", Status);
8353 goto done;
8354 }
8355
8356 /* Get fixed user data */
8357 Length = sizeof(SAM_USER_FIXED_DATA);
8358 Status = SampGetObjectAttribute(UserObject,
8359 L"F",
8360 NULL,
8361 (PVOID)&UserFixedData,
8362 &Length);
8363 if (!NT_SUCCESS(Status))
8364 {
8365 TRACE("SampGetObjectAttribute failed with status 0x%08lx\n", Status);
8366 goto done;
8367 }
8368
8369 if ((UserObject->RelativeId == DOMAIN_USER_RID_KRBTGT) ||
8373 {
8374 PasswordInformation->MinPasswordLength = 0;
8375 PasswordInformation->PasswordProperties = 0;
8376 }
8377 else
8378 {
8379 /* Get fixed domain data */
8380 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
8381 Status = SampGetObjectAttribute(DomainObject,
8382 L"F",
8383 NULL,
8384 (PVOID)&DomainFixedData,
8385 &Length);
8386 if (!NT_SUCCESS(Status))
8387 {
8388 TRACE("SampGetObjectAttribute failed with status 0x%08lx\n", Status);
8389 goto done;
8390 }
8391
8392 PasswordInformation->MinPasswordLength = DomainFixedData.MinPasswordLength;
8393 PasswordInformation->PasswordProperties = DomainFixedData.PasswordProperties;
8394 }
8395
8396done:
8398
8399 return STATUS_SUCCESS;
8400}
#define DOMAIN_USER_RID_KRBTGT
Definition: setypes.h:633

Referenced by SampCheckPassword().

◆ SamrLookupDomainInSamServer()

NTSTATUS NTAPI SamrLookupDomainInSamServer ( IN SAMPR_HANDLE  ServerHandle,
IN PRPC_UNICODE_STRING  Name,
OUT PRPC_SID *  DomainId 
)

Definition at line 504 of file samrpc.c.

507{
508 PSAM_DB_OBJECT ServerObject;
509 HANDLE DomainsKeyHandle = NULL;
510 HANDLE DomainKeyHandle = NULL;
511 WCHAR DomainKeyName[64];
512 ULONG Index;
513 WCHAR DomainNameString[MAX_COMPUTERNAME_LENGTH + 1];
514 UNICODE_STRING DomainName;
516 BOOL Found = FALSE;
518
519 TRACE("SamrLookupDomainInSamServer(%p %p %p)\n",
520 ServerHandle, Name, DomainId);
521
523 TRUE);
524
525 /* Validate the server handle */
526 Status = SampValidateDbObject(ServerHandle,
529 &ServerObject);
530 if (!NT_SUCCESS(Status))
531 goto done;
532
533 *DomainId = NULL;
534
535 Status = SampRegOpenKey(ServerObject->KeyHandle,
536 L"Domains",
537 KEY_READ,
538 &DomainsKeyHandle);
539 if (!NT_SUCCESS(Status))
540 goto done;
541
542 Index = 0;
543 while (Found == FALSE)
544 {
545 Status = SampRegEnumerateSubKey(DomainsKeyHandle,
546 Index,
547 64,
548 DomainKeyName);
549 if (!NT_SUCCESS(Status))
550 {
553 break;
554 }
555
556 TRACE("Domain key name: %S\n", DomainKeyName);
557
558 Status = SampRegOpenKey(DomainsKeyHandle,
559 DomainKeyName,
560 KEY_READ,
561 &DomainKeyHandle);
562 if (NT_SUCCESS(Status))
563 {
564 Length = (MAX_COMPUTERNAME_LENGTH + 1) * sizeof(WCHAR);
565 Status = SampRegQueryValue(DomainKeyHandle,
566 L"Name",
567 NULL,
568 (PVOID)&DomainNameString,
569 &Length);
570 if (NT_SUCCESS(Status))
571 {
572 TRACE("Domain name: %S\n", DomainNameString);
573
574 RtlInitUnicodeString(&DomainName,
575 DomainNameString);
577 {
578 TRACE("Found it!\n");
579 Found = TRUE;
580
581 Status = SampRegQueryValue(DomainKeyHandle,
582 L"SID",
583 NULL,
584 NULL,
585 &Length);
586 if (NT_SUCCESS(Status))
587 {
588 *DomainId = midl_user_allocate(Length);
589
590 SampRegQueryValue(DomainKeyHandle,
591 L"SID",
592 NULL,
593 (PVOID)*DomainId,
594 &Length);
595
597 break;
598 }
599 }
600 }
601
602 SampRegCloseKey(&DomainKeyHandle);
603 }
604
605 Index++;
606 }
607
608done:
609 SampRegCloseKey(&DomainKeyHandle);
610 SampRegCloseKey(&DomainsKeyHandle);
611
613
614 return Status;
615}
return Found
Definition: dirsup.c:1270
unsigned int BOOL
Definition: ntddk_ex.h:94
NTSYSAPI VOID NTAPI RtlInitUnicodeString(PUNICODE_STRING DestinationString, PCWSTR SourceString)
#define STATUS_NO_SUCH_DOMAIN
Definition: ntstatus.h:553
#define MAX_COMPUTERNAME_LENGTH
Definition: winbase.h:268

Referenced by MsvpChangePassword(), and SamLookupDomainInSamServer().

◆ SamrLookupIdsInDomain()

NTSTATUS NTAPI SamrLookupIdsInDomain ( IN SAMPR_HANDLE  DomainHandle,
IN ULONG  Count,
IN ULONG *  RelativeIds,
OUT PSAMPR_RETURNED_USTRING_ARRAY  Names,
OUT PSAMPR_ULONG_ARRAY  Use 
)

Definition at line 3697 of file samrpc.c.

3702{
3703 PSAM_DB_OBJECT DomainObject;
3704 WCHAR RidString[9];
3705 HANDLE AccountsKeyHandle = NULL;
3706 HANDLE AccountKeyHandle = NULL;
3707 ULONG MappedCount = 0;
3709 ULONG i;
3711
3712 TRACE("SamrLookupIdsInDomain(%p %lu %p %p %p)\n",
3713 DomainHandle, Count, RelativeIds, Names, Use);
3714
3716 TRUE);
3717
3718 /* Validate the domain handle */
3719 Status = SampValidateDbObject(DomainHandle,
3722 &DomainObject);
3723 if (!NT_SUCCESS(Status))
3724 {
3725 TRACE("failed with status 0x%08lx\n", Status);
3726 goto done;
3727 }
3728
3729 Names->Count = 0;
3730 Use->Count = 0;
3731
3732 if (Count == 0)
3733 {
3735 goto done;
3736 }
3737
3738 /* Allocate the names array */
3739 Names->Element = midl_user_allocate(Count * sizeof(*Names->Element));
3740 if (Names->Element == NULL)
3741 {
3743 goto done;
3744 }
3745
3746 /* Allocate the use array */
3747 Use->Element = midl_user_allocate(Count * sizeof(*Use->Element));
3748 if (Use->Element == NULL)
3749 {
3751 goto done;
3752 }
3753
3754 Names->Count = Count;
3755 Use->Count = Count;
3756
3757 for (i = 0; i < Count; i++)
3758 {
3759 TRACE("RID: %lu\n", RelativeIds[i]);
3760
3761 _swprintf(RidString, L"%08lx", RelativeIds[i]);
3762
3763 /* Lookup aliases */
3764 Status = SampRegOpenKey(DomainObject->KeyHandle,
3765 L"Aliases",
3766 KEY_READ,
3767 &AccountsKeyHandle);
3768 if (NT_SUCCESS(Status))
3769 {
3770 Status = SampRegOpenKey(AccountsKeyHandle,
3771 RidString,
3772 KEY_READ,
3773 &AccountKeyHandle);
3774 if (NT_SUCCESS(Status))
3775 {
3776 DataLength = 0;
3777 Status = SampRegQueryValue(AccountKeyHandle,
3778 L"Name",
3779 NULL,
3780 NULL,
3781 &DataLength);
3782 if (NT_SUCCESS(Status))
3783 {
3784 Names->Element[i].Buffer = midl_user_allocate(DataLength);
3785 if (Names->Element[i].Buffer == NULL)
3787
3788 if (NT_SUCCESS(Status))
3789 {
3790 Names->Element[i].MaximumLength = (USHORT)DataLength;
3791 Names->Element[i].Length = (USHORT)(DataLength - sizeof(WCHAR));
3792
3793 Status = SampRegQueryValue(AccountKeyHandle,
3794 L"Name",
3795 NULL,
3796 Names->Element[i].Buffer,
3797 &DataLength);
3798 }
3799 }
3800
3801 SampRegCloseKey(&AccountKeyHandle);
3802 }
3803
3804 SampRegCloseKey(&AccountsKeyHandle);
3805 }
3806
3808 break;
3809
3810 /* Return alias account */
3811 if (NT_SUCCESS(Status) && Names->Element[i].Buffer != NULL)
3812 {
3813 TRACE("Name: %S\n", Names->Element[i].Buffer);
3814 Use->Element[i] = SidTypeAlias;
3815 MappedCount++;
3816 continue;
3817 }
3818
3819 /* Lookup groups */
3820 Status = SampRegOpenKey(DomainObject->KeyHandle,
3821 L"Groups",
3822 KEY_READ,
3823 &AccountsKeyHandle);
3824 if (NT_SUCCESS(Status))
3825 {
3826 Status = SampRegOpenKey(AccountsKeyHandle,
3827 RidString,
3828 KEY_READ,
3829 &AccountKeyHandle);
3830 if (NT_SUCCESS(Status))
3831 {
3832 DataLength = 0;
3833 Status = SampRegQueryValue(AccountKeyHandle,
3834 L"Name",
3835 NULL,
3836 NULL,
3837 &DataLength);
3838 if (NT_SUCCESS(Status))
3839 {
3840 Names->Element[i].Buffer = midl_user_allocate(DataLength);
3841 if (Names->Element[i].Buffer == NULL)
3843
3844 if (NT_SUCCESS(Status))
3845 {
3846 Names->Element[i].MaximumLength = (USHORT)DataLength;
3847 Names->Element[i].Length = (USHORT)(DataLength - sizeof(WCHAR));
3848
3849 Status = SampRegQueryValue(AccountKeyHandle,
3850 L"Name",
3851 NULL,
3852 Names->Element[i].Buffer,
3853 &DataLength);
3854 }
3855 }
3856
3857 SampRegCloseKey(&AccountKeyHandle);
3858 }
3859
3860 SampRegCloseKey(&AccountsKeyHandle);
3861 }
3862
3864 break;
3865
3866 /* Return group account */
3867 if (NT_SUCCESS(Status) && Names->Element[i].Buffer != NULL)
3868 {
3869 TRACE("Name: %S\n", Names->Element[i].Buffer);
3870 Use->Element[i] = SidTypeGroup;
3871 MappedCount++;
3872 continue;
3873 }
3874
3875 /* Lookup users */
3876 Status = SampRegOpenKey(DomainObject->KeyHandle,
3877 L"Users",
3878 KEY_READ,
3879 &AccountsKeyHandle);
3880 if (NT_SUCCESS(Status))
3881 {
3882 Status = SampRegOpenKey(AccountsKeyHandle,
3883 RidString,
3884 KEY_READ,
3885 &AccountKeyHandle);
3886 if (NT_SUCCESS(Status))
3887 {
3888 DataLength = 0;
3889 Status = SampRegQueryValue(AccountKeyHandle,
3890 L"Name",
3891 NULL,
3892 NULL,
3893 &DataLength);
3894 if (NT_SUCCESS(Status))
3895 {
3896 TRACE("DataLength: %lu\n", DataLength);
3897
3898 Names->Element[i].Buffer = midl_user_allocate(DataLength);
3899 if (Names->Element[i].Buffer == NULL)
3901
3902 if (NT_SUCCESS(Status))
3903 {
3904 Names->Element[i].MaximumLength = (USHORT)DataLength;
3905 Names->Element[i].Length = (USHORT)(DataLength - sizeof(WCHAR));
3906
3907 Status = SampRegQueryValue(AccountKeyHandle,
3908 L"Name",
3909 NULL,
3910 Names->Element[i].Buffer,
3911 &DataLength);
3912 }
3913 }
3914
3915 SampRegCloseKey(&AccountKeyHandle);
3916 }
3917
3918 SampRegCloseKey(&AccountsKeyHandle);
3919 }
3920
3922 break;
3923
3924 /* Return user account */
3925 if (NT_SUCCESS(Status) && Names->Element[i].Buffer != NULL)
3926 {
3927 TRACE("Name: %S\n", Names->Element[i].Buffer);
3928 Use->Element[i] = SidTypeUser;
3929 MappedCount++;
3930 continue;
3931 }
3932
3933 /* Return unknown account */
3934 Use->Element[i] = SidTypeUnknown;
3935 }
3936
3937done:
3940
3941 if (NT_SUCCESS(Status))
3942 {
3943 if (MappedCount == 0)
3945 else if (MappedCount < Count)
3947 }
3948 else
3949 {
3950 if (Names->Element != NULL)
3951 {
3952 for (i = 0; i < Count; i++)
3953 {
3954 if (Names->Element[i].Buffer != NULL)
3955 midl_user_free(Names->Element[i].Buffer);
3956 }
3957
3958 midl_user_free(Names->Element);
3959 Names->Element = NULL;
3960 }
3961
3962 Names->Count = 0;
3963
3964 if (Use->Element != NULL)
3965 {
3966 midl_user_free(Use->Element);
3967 Use->Element = NULL;
3968 }
3969
3970 Use->Count = 0;
3971 }
3972
3974
3975 return Status;
3976}
PWSTR Names[]
@ SidTypeUnknown
Definition: lsa.idl:125
@ SidTypeAlias
Definition: lsa.idl:121
@ SidTypeGroup
Definition: lsa.idl:119
@ SidTypeUser
Definition: lsa.idl:118
#define DOMAIN_LOOKUP
Definition: ntsam.h:42
#define STATUS_NONE_MAPPED
Definition: ntstatus.h:445
#define STATUS_SOME_NOT_MAPPED
Definition: ntstatus.h:139

Referenced by LsapLookupAccountDomainSids(), LsapLookupBuiltinDomainSids(), and SamLookupIdsInDomain().

◆ SamrLookupNamesInDomain()

NTSTATUS NTAPI SamrLookupNamesInDomain ( IN SAMPR_HANDLE  DomainHandle,
IN ULONG  Count,
IN RPC_UNICODE_STRING  Names[],
OUT PSAMPR_ULONG_ARRAY  RelativeIds,
OUT PSAMPR_ULONG_ARRAY  Use 
)

Definition at line 3468 of file samrpc.c.

3473{
3474 PSAM_DB_OBJECT DomainObject;
3475 HANDLE AccountsKeyHandle = NULL;
3476 HANDLE NamesKeyHandle = NULL;
3477 ULONG MappedCount = 0;
3479 ULONG i;
3480 ULONG RelativeId;
3482
3483 TRACE("SamrLookupNamesInDomain(%p %lu %p %p %p)\n",
3484 DomainHandle, Count, Names, RelativeIds, Use);
3485
3487 TRUE);
3488
3489 /* Validate the domain handle */
3490 Status = SampValidateDbObject(DomainHandle,
3493 &DomainObject);
3494 if (!NT_SUCCESS(Status))
3495 {
3496 TRACE("failed with status 0x%08lx\n", Status);
3497 goto done;
3498 }
3499
3500 RelativeIds->Count = 0;
3501 Use->Count = 0;
3502
3503 if (Count == 0)
3504 {
3506 goto done;
3507 }
3508
3509 /* Allocate the relative IDs array */
3510 RelativeIds->Element = midl_user_allocate(Count * sizeof(ULONG));
3511 if (RelativeIds->Element == NULL)
3512 {
3514 goto done;
3515 }
3516
3517 /* Allocate the use array */
3518 Use->Element = midl_user_allocate(Count * sizeof(ULONG));
3519 if (Use->Element == NULL)
3520 {
3522 goto done;
3523 }
3524
3525 RelativeIds->Count = Count;
3526 Use->Count = Count;
3527
3528 for (i = 0; i < Count; i++)
3529 {
3530 TRACE("Name: %S\n", Names[i].Buffer);
3531
3532 RelativeId = 0;
3533
3534 /* Lookup aliases */
3535 Status = SampRegOpenKey(DomainObject->KeyHandle,
3536 L"Aliases",
3537 KEY_READ,
3538 &AccountsKeyHandle);
3539 if (NT_SUCCESS(Status))
3540 {
3541 Status = SampRegOpenKey(AccountsKeyHandle,
3542 L"Names",
3543 KEY_READ,
3544 &NamesKeyHandle);
3545 if (NT_SUCCESS(Status))
3546 {
3547 DataLength = sizeof(ULONG);
3548 Status = SampRegQueryValue(NamesKeyHandle,
3549 Names[i].Buffer,
3550 NULL,
3551 &RelativeId,
3552 &DataLength);
3553
3554 SampRegCloseKey(&NamesKeyHandle);
3555 }
3556
3557 SampRegCloseKey(&AccountsKeyHandle);
3558 }
3559
3561 break;
3562
3563 /* Return alias account */
3564 if (NT_SUCCESS(Status) && RelativeId != 0)
3565 {
3566 TRACE("Rid: %lu\n", RelativeId);
3567 RelativeIds->Element[i] = RelativeId;
3568 Use->Element[i] = SidTypeAlias;
3569 MappedCount++;
3570 continue;
3571 }
3572
3573 /* Lookup groups */
3574 Status = SampRegOpenKey(DomainObject->KeyHandle,
3575 L"Groups",
3576 KEY_READ,
3577 &AccountsKeyHandle);
3578 if (NT_SUCCESS(Status))
3579 {
3580 Status = SampRegOpenKey(AccountsKeyHandle,
3581 L"Names",
3582 KEY_READ,
3583 &NamesKeyHandle);
3584 if (NT_SUCCESS(Status))
3585 {
3586 DataLength = sizeof(ULONG);
3587 Status = SampRegQueryValue(NamesKeyHandle,
3588 Names[i].Buffer,
3589 NULL,
3590 &RelativeId,
3591 &DataLength);
3592
3593 SampRegCloseKey(&NamesKeyHandle);
3594 }
3595
3596 SampRegCloseKey(&AccountsKeyHandle);
3597 }
3598
3600 break;
3601
3602 /* Return group account */
3603 if (NT_SUCCESS(Status) && RelativeId != 0)
3604 {
3605 TRACE("Rid: %lu\n", RelativeId);
3606 RelativeIds->Element[i] = RelativeId;
3607 Use->Element[i] = SidTypeGroup;
3608 MappedCount++;
3609 continue;
3610 }
3611
3612 /* Lookup users */
3613 Status = SampRegOpenKey(DomainObject->KeyHandle,
3614 L"Users",
3615 KEY_READ,
3616 &AccountsKeyHandle);
3617 if (NT_SUCCESS(Status))
3618 {
3619 Status = SampRegOpenKey(AccountsKeyHandle,
3620 L"Names",
3621 KEY_READ,
3622 &NamesKeyHandle);
3623 if (NT_SUCCESS(Status))
3624 {
3625 DataLength = sizeof(ULONG);
3626 Status = SampRegQueryValue(NamesKeyHandle,
3627 Names[i].Buffer,
3628 NULL,
3629 &RelativeId,
3630 &DataLength);
3631
3632 SampRegCloseKey(&NamesKeyHandle);
3633 }
3634
3635 SampRegCloseKey(&AccountsKeyHandle);
3636 }
3637
3639 break;
3640
3641 /* Return user account */
3642 if (NT_SUCCESS(Status) && RelativeId != 0)
3643 {
3644 TRACE("Rid: %lu\n", RelativeId);
3645 RelativeIds->Element[i] = RelativeId;
3646 Use->Element[i] = SidTypeUser;
3647 MappedCount++;
3648 continue;
3649 }
3650
3651 /* Return unknown account */
3652 RelativeIds->Element[i] = 0;
3653 Use->Element[i] = SidTypeUnknown;
3654 }
3655
3656done:
3659
3660 if (NT_SUCCESS(Status))
3661 {
3662 if (MappedCount == 0)
3664 else if (MappedCount < Count)
3666 }
3667 else
3668 {
3669 if (RelativeIds->Element != NULL)
3670 {
3671 midl_user_free(RelativeIds->Element);
3672 RelativeIds->Element = NULL;
3673 }
3674
3675 RelativeIds->Count = 0;
3676
3677 if (Use->Element != NULL)
3678 {
3679 midl_user_free(Use->Element);
3680 Use->Element = NULL;
3681 }
3682
3683 Use->Count = 0;
3684 }
3685
3687
3688 TRACE("Returned Status %lx\n", Status);
3689
3690 return Status;
3691}

Referenced by LsapLookupAccountNames(), LsapLookupBuiltinNames(), LsapLookupIsolatedAccountNames(), LsapLookupIsolatedBuiltinNames(), MsvpChangePassword(), SamLookupNamesInDomain(), and SamValidateNormalUser().

◆ SamrOemChangePasswordUser2()

NTSTATUS NTAPI SamrOemChangePasswordUser2 ( IN handle_t  BindingHandle,
IN PRPC_STRING  ServerName,
IN PRPC_STRING  UserName,
IN PSAMPR_ENCRYPTED_USER_PASSWORD  NewPasswordEncryptedWithOldLm,
IN PENCRYPTED_LM_OWF_PASSWORD  OldLmOwfPasswordEncryptedWithNewLm 
)

Definition at line 9352 of file samrpc.c.

9357{
9360}

◆ SamrOpenAlias()

NTSTATUS NTAPI SamrOpenAlias ( IN SAMPR_HANDLE  DomainHandle,
IN ACCESS_MASK  DesiredAccess,
IN ULONG  AliasId,
OUT SAMPR_HANDLE *  AliasHandle 
)

Definition at line 4825 of file samrpc.c.

4829{
4830 PSAM_DB_OBJECT DomainObject;
4831 PSAM_DB_OBJECT AliasObject;
4832 WCHAR szRid[9];
4834
4835 TRACE("SamrOpenAlias(%p %lx %lx %p)\n",
4836 DomainHandle, DesiredAccess, AliasId, AliasHandle);
4837
4838 /* Map generic access rights */
4840 &AliasMapping);
4841
4843 TRUE);
4844
4845 /* Validate the domain handle */
4846 Status = SampValidateDbObject(DomainHandle,
4849 &DomainObject);
4850 if (!NT_SUCCESS(Status))
4851 {
4852 TRACE("failed with status 0x%08lx\n", Status);
4853 goto done;
4854 }
4855
4856 /* Convert the RID into a string (hex) */
4857 _swprintf(szRid, L"%08lX", AliasId);
4858
4859 /* Create the alias object */
4860 Status = SampOpenDbObject(DomainObject,
4861 L"Aliases",
4862 szRid,
4863 AliasId,
4866 &AliasObject);
4867 if (!NT_SUCCESS(Status))
4868 {
4869 TRACE("failed with status 0x%08lx\n", Status);
4870 goto done;
4871 }
4872
4873 *AliasHandle = (SAMPR_HANDLE)AliasObject;
4874
4875done:
4877
4878 return Status;
4879}

Referenced by SamOpenAlias().

◆ SamrOpenDomain()

NTSTATUS NTAPI SamrOpenDomain ( IN SAMPR_HANDLE  ServerHandle,
IN ACCESS_MASK  DesiredAccess,
IN PRPC_SID  DomainId,
OUT SAMPR_HANDLE *  DomainHandle 
)

Definition at line 831 of file samrpc.c.

835{
836 PSAM_DB_OBJECT ServerObject;
837 PSAM_DB_OBJECT DomainObject;
839
840 TRACE("SamrOpenDomain(%p %lx %p %p)\n",
841 ServerHandle, DesiredAccess, DomainId, DomainHandle);
842
843 /* Map generic access rights */
846
848 TRUE);
849
850 /* Validate the server handle */
851 Status = SampValidateDbObject(ServerHandle,
854 &ServerObject);
855 if (!NT_SUCCESS(Status))
856 goto done;
857
858 /* Validate the Domain SID */
859 if ((DomainId->Revision != SID_REVISION) ||
860 (DomainId->SubAuthorityCount > SID_MAX_SUB_AUTHORITIES) ||
861 (memcmp(&DomainId->IdentifierAuthority, &NtSidAuthority, sizeof(SID_IDENTIFIER_AUTHORITY)) != 0))
862 {
864 goto done;
865 }
866
867 /* Open the domain object */
868 if ((DomainId->SubAuthorityCount == 1) &&
869 (DomainId->SubAuthority[0] == SECURITY_BUILTIN_DOMAIN_RID))
870 {
871 /* Builtin domain object */
872 TRACE("Opening the builtin domain object.\n");
873
874 Status = SampOpenDbObject(ServerObject,
875 L"Domains",
876 L"Builtin",
877 0,
880 &DomainObject);
881 }
882 else if ((DomainId->SubAuthorityCount == 4) &&
883 (DomainId->SubAuthority[0] == SECURITY_NT_NON_UNIQUE))
884 {
885 /* Account domain object */
886 TRACE("Opening the account domain object.\n");
887
888 /* FIXME: Check the account domain sub authorities!!! */
889
890 Status = SampOpenDbObject(ServerObject,
891 L"Domains",
892 L"Account",
893 0,
896 &DomainObject);
897 }
898 else
899 {
900 /* No valid domain SID */
902 }
903
904 if (NT_SUCCESS(Status))
905 *DomainHandle = (SAMPR_HANDLE)DomainObject;
906
907done:
909
910 TRACE("SamrOpenDomain done (Status 0x%08lx)\n", Status);
911
912 return Status;
913}
static SID_IDENTIFIER_AUTHORITY NtSidAuthority
Definition: samrpc.c:14
static GENERIC_MAPPING DomainMapping
Definition: samrpc.c:24
#define SECURITY_BUILTIN_DOMAIN_RID
Definition: setypes.h:581
#define SID_MAX_SUB_AUTHORITIES
Definition: setypes.h:482
#define SID_REVISION
Definition: setypes.h:481
#define SECURITY_NT_NON_UNIQUE
Definition: setypes.h:577

Referenced by LsapLookupAccountDomainSids(), LsapLookupAccountNames(), LsapLookupBuiltinDomainSids(), LsapLookupBuiltinNames(), LsapLookupIsolatedAccountNames(), and LsapLookupIsolatedBuiltinNames().

◆ SamrOpenGroup()

NTSTATUS NTAPI SamrOpenGroup ( IN SAMPR_HANDLE  DomainHandle,
IN ACCESS_MASK  DesiredAccess,
IN unsigned long  GroupId,
OUT SAMPR_HANDLE *  GroupHandle 
)

Definition at line 3982 of file samrpc.c.

3986{
3987 PSAM_DB_OBJECT DomainObject;
3988 PSAM_DB_OBJECT GroupObject;
3989 WCHAR szRid[9];
3991
3992 TRACE("SamrOpenGroup(%p %lx %lx %p)\n",
3993 DomainHandle, DesiredAccess, GroupId, GroupHandle);
3994
3995 /* Map generic access rights */
3997 &GroupMapping);
3998
4000 TRUE);
4001
4002 /* Validate the domain handle */
4003 Status = SampValidateDbObject(DomainHandle,
4006 &DomainObject);
4007 if (!NT_SUCCESS(Status))
4008 {
4009 TRACE("failed with status 0x%08lx\n", Status);
4010 goto done;
4011 }
4012
4013 /* Convert the RID into a string (hex) */
4014 _swprintf(szRid, L"%08lX", GroupId);
4015
4016 /* Create the group object */
4017 Status = SampOpenDbObject(DomainObject,
4018 L"Groups",
4019 szRid,
4020 GroupId,
4023 &GroupObject);
4024 if (!NT_SUCCESS(Status))
4025 {
4026 TRACE("failed with status 0x%08lx\n", Status);
4027 goto done;
4028 }
4029
4030 *GroupHandle = (SAMPR_HANDLE)GroupObject;
4031
4032done:
4034
4035 return Status;
4036}

Referenced by SamOpenGroup().

◆ SamrOpenUser()

NTSTATUS NTAPI SamrOpenUser ( IN SAMPR_HANDLE  DomainHandle,
IN ACCESS_MASK  DesiredAccess,
IN unsigned long  UserId,
OUT SAMPR_HANDLE *  UserHandle 
)

Definition at line 5426 of file samrpc.c.

5430{
5431 PSAM_DB_OBJECT DomainObject;
5432 PSAM_DB_OBJECT UserObject;
5433 WCHAR szRid[9];
5435
5436 TRACE("SamrOpenUser(%p %lx %lx %p)\n",
5437 DomainHandle, DesiredAccess, UserId, UserHandle);
5438
5439 /* Map generic access rights */
5441 &UserMapping);
5442
5444 TRUE);
5445
5446 /* Validate the domain handle */
5447 Status = SampValidateDbObject(DomainHandle,
5450 &DomainObject);
5451 if (!NT_SUCCESS(Status))
5452 {
5453 TRACE("failed with status 0x%08lx\n", Status);
5454 goto done;
5455 }
5456
5457 /* Convert the RID into a string (hex) */
5458 _swprintf(szRid, L"%08lX", UserId);
5459
5460 /* Create the user object */
5461 Status = SampOpenDbObject(DomainObject,
5462 L"Users",
5463 szRid,
5464 UserId,
5467 &UserObject);
5468 if (!NT_SUCCESS(Status))
5469 {
5470 TRACE("failed with status 0x%08lx\n", Status);
5471 goto done;
5472 }
5473
5474 *UserHandle = (SAMPR_HANDLE)UserObject;
5475
5476done:
5478
5479 return Status;
5480}

◆ SamrQueryDisplayInformation()

NTSTATUS NTAPI SamrQueryDisplayInformation ( IN SAMPR_HANDLE  DomainHandle,
IN DOMAIN_DISPLAY_INFORMATION  DisplayInformationClass,
IN unsigned long  Index,
IN unsigned long  EntryCount,
IN unsigned long  PreferredMaximumLength,
OUT unsigned long *  TotalAvailable,
OUT unsigned long *  TotalReturned,
OUT PSAMPR_DISPLAY_INFO_BUFFER  Buffer 
)

Definition at line 8252 of file samrpc.c.

8260{
8261 TRACE("SamrQueryDisplayInformation(%p %lu %lu %lu %lu %p %p %p)\n",
8262 DomainHandle, DisplayInformationClass, Index,
8263 EntryCount, PreferredMaximumLength, TotalAvailable,
8264 TotalReturned, Buffer);
8265
8266 return SamrQueryDisplayInformation3(DomainHandle,
8267 DisplayInformationClass,
8268 Index,
8269 EntryCount,
8270 PreferredMaximumLength,
8271 TotalAvailable,
8272 TotalReturned,
8273 Buffer);
8274}
NTSTATUS NTAPI SamrQueryDisplayInformation3(IN SAMPR_HANDLE DomainHandle, IN DOMAIN_DISPLAY_INFORMATION DisplayInformationClass, IN unsigned long Index, IN unsigned long EntryCount, IN unsigned long PreferredMaximumLength, OUT unsigned long *TotalAvailable, OUT unsigned long *TotalReturned, OUT PSAMPR_DISPLAY_INFO_BUFFER Buffer)
Definition: samrpc.c:9244

◆ SamrQueryDisplayInformation2()

NTSTATUS NTAPI SamrQueryDisplayInformation2 ( IN SAMPR_HANDLE  DomainHandle,
IN DOMAIN_DISPLAY_INFORMATION  DisplayInformationClass,
IN unsigned long  Index,
IN unsigned long  EntryCount,
IN unsigned long  PreferredMaximumLength,
OUT unsigned long *  TotalAvailable,
OUT unsigned long *  TotalReturned,
OUT PSAMPR_DISPLAY_INFO_BUFFER  Buffer 
)

Definition at line 8785 of file samrpc.c.

8793{
8794 TRACE("SamrQueryDisplayInformation2(%p %lu %lu %lu %lu %p %p %p)\n",
8795 DomainHandle, DisplayInformationClass, Index,
8796 EntryCount, PreferredMaximumLength, TotalAvailable,
8797 TotalReturned, Buffer);
8798
8799 return SamrQueryDisplayInformation3(DomainHandle,
8800 DisplayInformationClass,
8801 Index,
8802 EntryCount,
8803 PreferredMaximumLength,
8804 TotalAvailable,
8805 TotalReturned,
8806 Buffer);
8807}

◆ SamrQueryDisplayInformation3()

NTSTATUS NTAPI SamrQueryDisplayInformation3 ( IN SAMPR_HANDLE  DomainHandle,
IN DOMAIN_DISPLAY_INFORMATION  DisplayInformationClass,
IN unsigned long  Index,
IN unsigned long  EntryCount,
IN unsigned long  PreferredMaximumLength,
OUT unsigned long *  TotalAvailable,
OUT unsigned long *  TotalReturned,
OUT PSAMPR_DISPLAY_INFO_BUFFER  Buffer 
)

Definition at line 9244 of file samrpc.c.

9252{
9253 PSAM_DB_OBJECT DomainObject;
9255
9256 FIXME("SamrQueryDisplayInformation3(%p %lu %lu %lu %lu %p %p %p)\n",
9257 DomainHandle, DisplayInformationClass, Index,
9258 EntryCount, PreferredMaximumLength, TotalAvailable,
9259 TotalReturned, Buffer);
9260
9262 TRUE);
9263
9264 /* Validate the domain handle */
9265 Status = SampValidateDbObject(DomainHandle,
9268 &DomainObject);
9269 if (!NT_SUCCESS(Status))
9270 {
9271 ERR("SampValidateDbObject() failed (Status 0x%08lx)\n", Status);
9272 goto done;
9273 }
9274
9275 Status = SampFillDisplayCache(DomainObject,
9276 DisplayInformationClass);
9277 if (!NT_SUCCESS(Status))
9278 {
9279 ERR("SampFillDisplayCache() failed (Status 0x%08lx)\n", Status);
9280 goto done;
9281 }
9282
9283done:
9284 TRACE("returns with status 0x%08lx\n", Status);
9285
9287
9288// return Status;
9290}
NTSTATUS SampFillDisplayCache(_In_ PSAM_DB_OBJECT DomainObject, _In_ DOMAIN_DISPLAY_INFORMATION DisplayInformationClass)
Definition: display.c:172

Referenced by SamQueryDisplayInformation(), SamrQueryDisplayInformation(), and SamrQueryDisplayInformation2().

◆ SamrQueryInformationAlias()

NTSTATUS NTAPI SamrQueryInformationAlias ( IN SAMPR_HANDLE  AliasHandle,
IN ALIAS_INFORMATION_CLASS  AliasInformationClass,
OUT PSAMPR_ALIAS_INFO_BUFFER *  Buffer 
)

Definition at line 5048 of file samrpc.c.

5051{
5052 PSAM_DB_OBJECT AliasObject;
5054
5055 TRACE("SamrQueryInformationAlias(%p %lu %p)\n",
5056 AliasHandle, AliasInformationClass, Buffer);
5057
5059 TRUE);
5060
5061 /* Validate the alias handle */
5062 Status = SampValidateDbObject(AliasHandle,
5065 &AliasObject);
5066 if (!NT_SUCCESS(Status))
5067 goto done;
5068
5069 switch (AliasInformationClass)
5070 {
5072 Status = SampQueryAliasGeneral(AliasObject,
5073 Buffer);
5074 break;
5075
5077 Status = SampQueryAliasName(AliasObject,
5078 Buffer);
5079 break;
5080
5082 Status = SampQueryAliasAdminComment(AliasObject,
5083 Buffer);
5084 break;
5085
5086 default:
5088 break;
5089 }
5090
5091done:
5093
5094 return Status;
5095}
@ AliasGeneralInformation
Definition: ntsam.h:279
@ AliasAdminCommentInformation
Definition: ntsam.h:281
@ AliasNameInformation
Definition: ntsam.h:280
#define ALIAS_READ_INFORMATION
Definition: ntsam.h:12
static NTSTATUS SampQueryAliasGeneral(PSAM_DB_OBJECT AliasObject, PSAMPR_ALIAS_INFO_BUFFER *Buffer)
Definition: samrpc.c:4883
static NTSTATUS SampQueryAliasName(PSAM_DB_OBJECT AliasObject, PSAMPR_ALIAS_INFO_BUFFER *Buffer)
Definition: samrpc.c:4966
static NTSTATUS SampQueryAliasAdminComment(PSAM_DB_OBJECT AliasObject, PSAMPR_ALIAS_INFO_BUFFER *Buffer)
Definition: samrpc.c:5006

Referenced by SamQueryInformationAlias().

◆ SamrQueryInformationDomain()

NTSTATUS NTAPI SamrQueryInformationDomain ( IN SAMPR_HANDLE  DomainHandle,
IN DOMAIN_INFORMATION_CLASS  DomainInformationClass,
OUT PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)

Definition at line 1619 of file samrpc.c.

1622{
1623 TRACE("SamrQueryInformationDomain(%p %lu %p)\n",
1624 DomainHandle, DomainInformationClass, Buffer);
1625
1626 return SamrQueryInformationDomain2(DomainHandle,
1627 DomainInformationClass,
1628 Buffer);
1629}
NTSTATUS NTAPI SamrQueryInformationDomain2(IN SAMPR_HANDLE DomainHandle, IN DOMAIN_INFORMATION_CLASS DomainInformationClass, OUT PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
Definition: samrpc.c:8465

Referenced by SamQueryInformationDomain().

◆ SamrQueryInformationDomain2()

NTSTATUS NTAPI SamrQueryInformationDomain2 ( IN SAMPR_HANDLE  DomainHandle,
IN DOMAIN_INFORMATION_CLASS  DomainInformationClass,
OUT PSAMPR_DOMAIN_INFO_BUFFER *  Buffer 
)

Definition at line 8465 of file samrpc.c.

8468{
8469 PSAM_DB_OBJECT DomainObject;
8472
8473 TRACE("SamrQueryInformationDomain2(%p %lu %p)\n",
8474 DomainHandle, DomainInformationClass, Buffer);
8475
8476 switch (DomainInformationClass)
8477 {
8481 break;
8482
8493 break;
8494
8498 break;
8499
8500 default:
8502 }
8503
8505 TRUE);
8506
8507 /* Validate the server handle */
8508 Status = SampValidateDbObject(DomainHandle,
8511 &DomainObject);
8512 if (!NT_SUCCESS(Status))
8513 goto done;
8514
8515 switch (DomainInformationClass)
8516 {
8518 Status = SampQueryDomainPassword(DomainObject,
8519 Buffer);
8520 break;
8521
8523 Status = SampQueryDomainGeneral(DomainObject,
8524 Buffer);
8525 break;
8526
8528 Status = SampQueryDomainLogoff(DomainObject,
8529 Buffer);
8530 break;
8531
8533 Status = SampQueryDomainOem(DomainObject,
8534 Buffer);
8535 break;
8536
8538 Status = SampQueryDomainName(DomainObject,
8539 Buffer);
8540 break;
8541
8543 Status = SampQueryDomainReplication(DomainObject,
8544 Buffer);
8545 break;
8546
8548 Status = SampQueryDomainServerRole(DomainObject,
8549 Buffer);
8550 break;
8551
8553 Status = SampQueryDomainModified(DomainObject,
8554 Buffer);
8555 break;
8556
8558 Status = SampQueryDomainState(DomainObject,
8559 Buffer);
8560 break;
8561
8563 Status = SampQueryDomainGeneral2(DomainObject,
8564 Buffer);
8565 break;
8566
8568 Status = SampQueryDomainLockout(DomainObject,
8569 Buffer);
8570 break;
8571
8573 Status = SampQueryDomainModified2(DomainObject,
8574 Buffer);
8575 break;
8576
8577 default:
8579 }
8580
8581done:
8583
8584 return Status;
8585}
ULONG ACCESS_MASK
Definition: nt_native.h:40
@ DomainLogoffInformation
Definition: ntsam.h:343
@ DomainReplicationInformation
Definition: ntsam.h:346
@ DomainOemInformation
Definition: ntsam.h:344
@ DomainNameInformation
Definition: ntsam.h:345
@ DomainServerRoleInformation
Definition: ntsam.h:347
@ DomainPasswordInformation
Definition: ntsam.h:341
@ DomainLockoutInformation
Definition: ntsam.h:352
@ DomainModifiedInformation2
Definition: ntsam.h:353
@ DomainGeneralInformation
Definition: ntsam.h:342
@ DomainGeneralInformation2
Definition: ntsam.h:351
@ DomainStateInformation
Definition: ntsam.h:349
@ DomainModifiedInformation
Definition: ntsam.h:348
#define DOMAIN_READ_OTHER_PARAMETERS
Definition: ntsam.h:35
static NTSTATUS SampQueryDomainReplication(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
Definition: samrpc.c:1241
static NTSTATUS SampQueryDomainLockout(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
Definition: samrpc.c:1528
static NTSTATUS SampQueryDomainModified(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
Definition: samrpc.c:1323
static NTSTATUS SampQueryDomainOem(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
Definition: samrpc.c:1159
static NTSTATUS SampQueryDomainName(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
Definition: samrpc.c:1200
static NTSTATUS SampQueryDomainLogoff(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
Definition: samrpc.c:1117
static NTSTATUS SampQueryDomainPassword(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
Definition: samrpc.c:917
static NTSTATUS SampQueryDomainModified2(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
Definition: samrpc.c:1571
static NTSTATUS SampQueryDomainState(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
Definition: samrpc.c:1367
static NTSTATUS SampQueryDomainServerRole(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
Definition: samrpc.c:1282
static NTSTATUS SampQueryDomainGeneral(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
Definition: samrpc.c:1001
static NTSTATUS SampQueryDomainGeneral2(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER *Buffer)
Definition: samrpc.c:1408

Referenced by SamrQueryInformationDomain().

◆ SamrQueryInformationGroup()

NTSTATUS NTAPI SamrQueryInformationGroup ( IN SAMPR_HANDLE  GroupHandle,
IN GROUP_INFORMATION_CLASS  GroupInformationClass,
OUT PSAMPR_GROUP_INFO_BUFFER *  Buffer 
)

Definition at line 4256 of file samrpc.c.

4259{
4260 PSAM_DB_OBJECT GroupObject;
4262
4263 TRACE("SamrQueryInformationGroup(%p %lu %p)\n",
4264 GroupHandle, GroupInformationClass, Buffer);
4265
4267 TRUE);
4268
4269 /* Validate the group handle */
4270 Status = SampValidateDbObject(GroupHandle,
4273 &GroupObject);
4274 if (!NT_SUCCESS(Status))
4275 goto done;
4276
4277 switch (GroupInformationClass)
4278 {
4280 Status = SampQueryGroupGeneral(GroupObject,
4281 Buffer);
4282 break;
4283
4285 Status = SampQueryGroupName(GroupObject,
4286 Buffer);
4287 break;
4288
4290 Status = SampQueryGroupAttribute(GroupObject,
4291 Buffer);
4292 break;
4293
4295 Status = SampQueryGroupAdminComment(GroupObject,
4296 Buffer);
4297 break;
4298
4299 default:
4301 break;
4302 }
4303
4304done:
4306
4307 return Status;
4308}
#define GROUP_READ_INFORMATION
Definition: ntsam.h:75
@ GroupAttributeInformation
Definition: ntsam.h:466
@ GroupGeneralInformation
Definition: ntsam.h:464
@ GroupNameInformation
Definition: ntsam.h:465
@ GroupAdminCommentInformation
Definition: ntsam.h:467
static NTSTATUS SampQueryGroupGeneral(PSAM_DB_OBJECT GroupObject, PSAMPR_GROUP_INFO_BUFFER *Buffer)
Definition: samrpc.c:4040
static NTSTATUS SampQueryGroupName(PSAM_DB_OBJECT GroupObject, PSAMPR_GROUP_INFO_BUFFER *Buffer)
Definition: samrpc.c:4130
static NTSTATUS SampQueryGroupAttribute(PSAM_DB_OBJECT GroupObject, PSAMPR_GROUP_INFO_BUFFER *Buffer)
Definition: samrpc.c:4170
static NTSTATUS SampQueryGroupAdminComment(PSAM_DB_OBJECT GroupObject, PSAMPR_GROUP_INFO_BUFFER *Buffer)
Definition: samrpc.c:4214

Referenced by SamQueryInformationGroup().

◆ SamrQueryInformationUser()

NTSTATUS NTAPI SamrQueryInformationUser ( IN SAMPR_HANDLE  UserHandle,
IN USER_INFORMATION_CLASS  UserInformationClass,
OUT PSAMPR_USER_INFO_BUFFER *  Buffer 
)

Definition at line 7238 of file samrpc.c.

7241{
7242 TRACE("SamrQueryInformationUser(%p %lu %p)\n",
7243 UserHandle, UserInformationClass, Buffer);
7244
7245 return SamrQueryInformationUser2(UserHandle,
7246 UserInformationClass,
7247 Buffer);
7248}
NTSTATUS NTAPI SamrQueryInformationUser2(IN SAMPR_HANDLE UserHandle, IN USER_INFORMATION_CLASS UserInformationClass, OUT PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:8591

Referenced by SamQueryInformationUser(), and SamValidateNormalUser().

◆ SamrQueryInformationUser2()

NTSTATUS NTAPI SamrQueryInformationUser2 ( IN SAMPR_HANDLE  UserHandle,
IN USER_INFORMATION_CLASS  UserInformationClass,
OUT PSAMPR_USER_INFO_BUFFER *  Buffer 
)

Definition at line 8591 of file samrpc.c.

8594{
8595 PSAM_DB_OBJECT UserObject;
8598
8599 TRACE("SamrQueryInformationUser2(%p %lu %p)\n",
8600 UserHandle, UserInformationClass, Buffer);
8601
8602 switch (UserInformationClass)
8603 {
8611 break;
8612
8619 break;
8620
8625 break;
8626
8630 break;
8631
8638 break;
8639
8642 case UserAllInformation:
8643 DesiredAccess = 0;
8644 break;
8645
8646 default:
8648 }
8649
8651 TRUE);
8652
8653 /* Validate the domain handle */
8654 Status = SampValidateDbObject(UserHandle,
8657 &UserObject);
8658 if (!NT_SUCCESS(Status))
8659 {
8660 TRACE("failed with status 0x%08lx\n", Status);
8661 goto done;
8662 }
8663
8664 switch (UserInformationClass)
8665 {
8667 Status = SampQueryUserGeneral(UserObject,
8668 Buffer);
8669 break;
8670
8672 Status = SampQueryUserPreferences(UserObject,
8673 Buffer);
8674 break;
8675
8677 Status = SampQueryUserLogon(UserObject,
8678 Buffer);
8679 break;
8680
8682 Status = SampQueryUserLogonHours(UserObject,
8683 Buffer);
8684 break;
8685
8687 Status = SampQueryUserAccount(UserObject,
8688 Buffer);
8689 break;
8690
8692 Status = SampQueryUserName(UserObject,
8693 Buffer);
8694 break;
8695
8697 Status = SampQueryUserAccountName(UserObject,
8698 Buffer);
8699 break;
8700
8702 Status = SampQueryUserFullName(UserObject,
8703 Buffer);
8704 break;
8705
8707 Status = SampQueryUserPrimaryGroup(UserObject,
8708 Buffer);
8709 break;
8710
8712 Status = SampQueryUserHome(UserObject,
8713 Buffer);
8714 break;
8715
8717 Status = SampQueryUserScript(UserObject,
8718 Buffer);
8719 break;
8720
8722 Status = SampQueryUserProfile(UserObject,
8723 Buffer);
8724 break;
8725
8727 Status = SampQueryUserAdminComment(UserObject,
8728 Buffer);
8729 break;
8730
8732 Status = SampQueryUserWorkStations(UserObject,
8733 Buffer);
8734 break;
8735
8737 Status = SampQueryUserControl(UserObject,
8738 Buffer);
8739 break;
8740
8742 Status = SampQueryUserExpires(UserObject,
8743 Buffer);
8744 break;
8745
8747 Status = SampQueryUserInternal1(UserObject,
8748 Buffer);
8749 break;
8750
8752 Status = SampQueryUserInternal2(UserObject,
8753 Buffer);
8754 break;
8755
8757 Status = SampQueryUserParameters(UserObject,
8758 Buffer);
8759 break;
8760
8761 case UserAllInformation:
8762 Status = SampQueryUserAll(UserObject,
8763 Buffer);
8764 break;
8765
8766// case UserInternal4Information:
8767// case UserInternal5Information:
8768// case UserInternal4InformationNew:
8769// case UserInternal5InformationNew:
8770
8771 default:
8773 }
8774
8775done:
8777
8778 return Status;
8779}
@ UserScriptInformation
Definition: ntsam.h:524
@ UserAccountNameInformation
Definition: ntsam.h:520
@ UserPrimaryGroupInformation
Definition: ntsam.h:522
@ UserAccountInformation
Definition: ntsam.h:518
@ UserInternal1Information
Definition: ntsam.h:531
@ UserParametersInformation
Definition: ntsam.h:533
@ UserWorkStationsInformation
Definition: ntsam.h:527
@ UserNameInformation
Definition: ntsam.h:519
@ UserLogonHoursInformation
Definition: ntsam.h:517
@ UserLogonInformation
Definition: ntsam.h:516
@ UserGeneralInformation
Definition: ntsam.h:514
@ UserFullNameInformation
Definition: ntsam.h:521
@ UserInternal2Information
Definition: ntsam.h:532
@ UserControlInformation
Definition: ntsam.h:529
@ UserAdminCommentInformation
Definition: ntsam.h:526
@ UserProfileInformation
Definition: ntsam.h:525
@ UserAllInformation
Definition: ntsam.h:534
@ UserExpiresInformation
Definition: ntsam.h:530
@ UserPreferencesInformation
Definition: ntsam.h:515
@ UserHomeInformation
Definition: ntsam.h:523
static NTSTATUS SampQueryUserLogon(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:5701
static NTSTATUS SampQueryUserAdminComment(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6409
static NTSTATUS SampQueryUserWorkStations(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6450
static NTSTATUS SampQueryUserInternal2(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6665
static NTSTATUS SampQueryUserAll(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6753
static NTSTATUS SampQueryUserExpires(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6534
static NTSTATUS SampQueryUserGeneral(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:5551
static NTSTATUS SampQueryUserPreferences(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:5645
static NTSTATUS SampQueryUserLogonHours(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6050
static NTSTATUS SampQueryUserControl(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6492
static NTSTATUS SampQueryUserHome(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6273
static NTSTATUS SampQueryUserInternal1(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6577
static NTSTATUS SampQueryUserParameters(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6712
static NTSTATUS SampQueryUserFullName(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6190
static NTSTATUS SampQueryUserPrimaryGroup(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6232
static NTSTATUS SampQueryUserName(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6095
static NTSTATUS SampQueryUserAccount(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:5880
static NTSTATUS SampQueryUserProfile(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6368
static NTSTATUS SampQueryUserScript(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6327
static NTSTATUS SampQueryUserAccountName(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:6149

Referenced by SamrQueryInformationUser().

◆ SamrQuerySecurityObject()

NTSTATUS NTAPI SamrQuerySecurityObject ( IN SAMPR_HANDLE  ObjectHandle,
IN SECURITY_INFORMATION  SecurityInformation,
OUT PSAMPR_SR_SECURITY_DESCRIPTOR *  SecurityDescriptor 
)

Definition at line 329 of file samrpc.c.

332{
333 PSAM_DB_OBJECT SamObject;
336 PSECURITY_DESCRIPTOR ResultSd = NULL;
338 ULONG RelativeSdSize = 0;
339 ULONG ResultSdSize = 0;
341
342 TRACE("SamrQuerySecurityObject(%p %lx %p)\n",
344
346
348 TRUE);
349
354
357
358 /* Validate the server handle */
359 Status = SampValidateDbObject(ObjectHandle,
362 &SamObject);
363 if (!NT_SUCCESS(Status))
364 goto done;
365
366 /* Get the size of the SD */
367 Status = SampGetObjectAttribute(SamObject,
368 L"SecDesc",
369 NULL,
370 NULL,
371 &RelativeSdSize);
373 {
374 TRACE("Status 0x%08lx\n", Status);
375 goto done;
376 }
377
378 /* Allocate a buffer for the SD */
379 RelativeSd = midl_user_allocate(RelativeSdSize);
380 if (RelativeSd == NULL)
381 {
383 goto done;
384 }
385
386 /* Get the SD */
387 Status = SampGetObjectAttribute(SamObject,
388 L"SecDesc",
389 NULL,
390 RelativeSd,
391 &RelativeSdSize);
392 if (!NT_SUCCESS(Status))
393 {
394 TRACE("Status 0x%08lx\n", Status);
395 goto done;
396 }
397
398 /* Invalidate the SD information that was not requested */
400 RelativeSd->Owner = 0;
401
403 RelativeSd->Group = 0;
404
406 RelativeSd->Control &= ~SE_DACL_PRESENT;
407
409 RelativeSd->Control &= ~SE_SACL_PRESENT;
410
411 /* Calculate the required SD size */
412 Status = RtlMakeSelfRelativeSD(RelativeSd,
413 NULL,
414 &ResultSdSize);
416 goto done;
417
418 /* Allocate a buffer for the new SD */
419 ResultSd = MIDL_user_allocate(ResultSdSize);
420 if (ResultSd == NULL)
421 {
423 goto done;
424 }
425
426 /* Build the new SD */
427 Status = RtlMakeSelfRelativeSD(RelativeSd,
428 ResultSd,
429 &ResultSdSize);
430 if (!NT_SUCCESS(Status))
431 goto done;
432
433 /* Allocate the SD data buffer */
435 if (SdData == NULL)
436 {
438 goto done;
439 }
440
441 /* Fill the SD data buffer and return it to the caller */
442 SdData->Length = ResultSdSize;
443 SdData->SecurityDescriptor = (PBYTE)ResultSd;
444
445 *SecurityDescriptor = SdData;
446
447done:
449
450 if (!NT_SUCCESS(Status))
451 {
452 if (ResultSd != NULL)
453 MIDL_user_free(ResultSd);
454 }
455
456 if (RelativeSd != NULL)
457 MIDL_user_free(RelativeSd);
458
459 return Status;
460}
void __RPC_USER MIDL_user_free(void __RPC_FAR *ptr)
Definition: dhcpcsvc.c:31
void __RPC_FAR *__RPC_USER MIDL_user_allocate(SIZE_T len)
Definition: dhcpcsvc.c:26
_Must_inspect_result_ _In_ PFILE_OBJECT _In_ SECURITY_INFORMATION SecurityInformation
Definition: fltkernel.h:1340
NTSYSAPI NTSTATUS NTAPI RtlMakeSelfRelativeSD(_In_ PSECURITY_DESCRIPTOR AbsoluteSD, _Out_ PSECURITY_DESCRIPTOR SelfRelativeSD, _Inout_ PULONG BufferLength)
#define ACCESS_SYSTEM_SECURITY
Definition: nt_native.h:77
#define READ_CONTROL
Definition: nt_native.h:58
BYTE * PBYTE
Definition: pedump.c:66
#define STATUS_BUFFER_TOO_SMALL
Definition: shellext.h:69
#define STATUS_BUFFER_OVERFLOW
Definition: shellext.h:66
SECURITY_DESCRIPTOR_CONTROL Control
Definition: setypes.h:851
_In_ USHORT _In_ ULONG _In_ PSOCKADDR _In_ PSOCKADDR _Reserved_ ULONG _In_opt_ PVOID _In_opt_ const WSK_CLIENT_CONNECTION_DISPATCH _In_opt_ PEPROCESS _In_opt_ PETHREAD _In_opt_ PSECURITY_DESCRIPTOR SecurityDescriptor
Definition: wsk.h:191
#define DACL_SECURITY_INFORMATION
Definition: setypes.h:125
#define OWNER_SECURITY_INFORMATION
Definition: setypes.h:123
#define GROUP_SECURITY_INFORMATION
Definition: setypes.h:124
#define SACL_SECURITY_INFORMATION
Definition: setypes.h:126

Referenced by SamQuerySecurityObject().

◆ SamrRemoveMemberFromAlias()

NTSTATUS NTAPI SamrRemoveMemberFromAlias ( IN SAMPR_HANDLE  AliasHandle,
IN PRPC_SID  MemberId 
)

Definition at line 5324 of file samrpc.c.

5326{
5327 PSAM_DB_OBJECT AliasObject;
5329
5330 TRACE("SamrRemoveMemberFromAlias(%p %p)\n",
5331 AliasHandle, MemberId);
5332
5334 TRUE);
5335
5336 /* Validate the alias handle */
5337 Status = SampValidateDbObject(AliasHandle,
5340 &AliasObject);
5341 if (!NT_SUCCESS(Status))
5342 {
5343 TRACE("failed with status 0x%08lx\n", Status);
5344 goto done;
5345 }
5346
5347 Status = SampRemoveMemberFromAlias(AliasObject,
5348 MemberId);
5349 if (!NT_SUCCESS(Status))
5350 {
5351 TRACE("failed with status 0x%08lx\n", Status);
5352 }
5353
5354done:
5356
5357 return Status;
5358}
NTSTATUS NTAPI SampRemoveMemberFromAlias(IN PSAM_DB_OBJECT AliasObject, IN PRPC_SID MemberId)
Definition: alias.c:111
#define ALIAS_REMOVE_MEMBER
Definition: ntsam.h:10

Referenced by SamRemoveMemberFromAlias(), and SamrRemoveMultipleMembersFromAlias().

◆ SamrRemoveMemberFromForeignDomain()

NTSTATUS NTAPI SamrRemoveMemberFromForeignDomain ( IN SAMPR_HANDLE  DomainHandle,
IN PRPC_SID  MemberSid 
)

Definition at line 8406 of file samrpc.c.

8408{
8409 PSAM_DB_OBJECT DomainObject;
8410 ULONG Rid = 0;
8412
8413 TRACE("SamrRemoveMemberFromForeignDomain(%p %p)\n",
8414 DomainHandle, MemberSid);
8415
8417 TRUE);
8418
8419 /* Validate the domain object */
8420 Status = SampValidateDbObject(DomainHandle,
8423 &DomainObject);
8424 if (!NT_SUCCESS(Status))
8425 {
8426 TRACE("SampValidateDbObject failed with status 0x%08lx\n", Status);
8427 goto done;
8428 }
8429
8430 /* Retrieve the RID from the MemberSID */
8431 Status = SampGetRidFromSid((PSID)MemberSid,
8432 &Rid);
8433 if (!NT_SUCCESS(Status))
8434 {
8435 TRACE("SampGetRidFromSid failed with status 0x%08lx\n", Status);
8436 goto done;
8437 }
8438
8439 /* Fail, if the RID represents a special account */
8440 if (Rid < 1000)
8441 {
8442 TRACE("Cannot remove a special account (RID: %lu)\n", Rid);
8444 goto done;
8445 }
8446
8447 /* Remove the member from all aliases in the domain */
8449 MemberSid);
8450 if (!NT_SUCCESS(Status))
8451 {
8452 TRACE("SampRemoveMemberFromAllAliases failed with status 0x%08lx\n", Status);
8453 }
8454
8455done:
8457
8458 return Status;
8459}
NTSTATUS SampRemoveMemberFromAllAliases(IN PSAM_DB_OBJECT DomainObject, IN PRPC_SID MemberSid)
Definition: domain.c:214
NTSTATUS SampGetRidFromSid(IN PSID Sid, OUT PULONG Rid)
Definition: utils.c:138

Referenced by SamRemoveMemberFromForeignDomain().

◆ SamrRemoveMemberFromGroup()

NTSTATUS NTAPI SamrRemoveMemberFromGroup ( IN SAMPR_HANDLE  GroupHandle,
IN unsigned long  MemberId 
)

Definition at line 4606 of file samrpc.c.

4608{
4609 PSAM_DB_OBJECT GroupObject;
4610 PSAM_DB_OBJECT UserObject = NULL;
4612
4613 TRACE("SamrRemoveMemberFromGroup(%p %lu)\n",
4614 GroupHandle, MemberId);
4615
4617 TRUE);
4618
4619 /* Validate the group handle */
4620 Status = SampValidateDbObject(GroupHandle,
4623 &GroupObject);
4624 if (!NT_SUCCESS(Status))
4625 goto done;
4626
4627 /* Open the user object in the same domain */
4628 Status = SampOpenUserObject(GroupObject->ParentObject,
4629 MemberId,
4630 0,
4631 &UserObject);
4632 if (!NT_SUCCESS(Status))
4633 {
4634 ERR("SampOpenUserObject() failed (Status 0x%08lx)\n", Status);
4635 goto done;
4636 }
4637
4638 /* Remove group membership from the user object */
4640 GroupObject->RelativeId);
4641 if (!NT_SUCCESS(Status))
4642 {
4643 ERR("SampAddGroupMembershipToUser() failed (Status 0x%08lx)\n", Status);
4644 goto done;
4645 }
4646
4647 /* Remove the member from the group object */
4648 Status = SampRemoveMemberFromGroup(GroupObject,
4649 MemberId);
4650 if (!NT_SUCCESS(Status))
4651 {
4652 ERR("SampRemoveMemberFromGroup() failed (Status 0x%08lx)\n", Status);
4653 }
4654
4655done:
4656 if (UserObject)
4657 SampCloseDbObject(UserObject);
4658
4660
4661 return Status;
4662}
NTSTATUS SampRemoveMemberFromGroup(IN PSAM_DB_OBJECT GroupObject, IN ULONG MemberId)
Definition: group.c:103
NTSTATUS SampRemoveGroupMembershipFromUser(IN PSAM_DB_OBJECT UserObject, IN ULONG GroupId)
Definition: user.c:108
#define GROUP_REMOVE_MEMBER
Definition: ntsam.h:78

Referenced by SamRemoveMemberFromGroup().

◆ SamrRemoveMultipleMembersFromAlias()

NTSTATUS NTAPI SamrRemoveMultipleMembersFromAlias ( IN SAMPR_HANDLE  AliasHandle,
IN PSAMPR_PSID_ARRAY  MembersBuffer 
)

Definition at line 9324 of file samrpc.c.

9326{
9327 ULONG i;
9329
9330 TRACE("SamrRemoveMultipleMembersFromAlias(%p %p)\n",
9331 AliasHandle, MembersBuffer);
9332
9333 for (i = 0; i < MembersBuffer->Count; i++)
9334 {
9335 Status = SamrRemoveMemberFromAlias(AliasHandle,
9336 ((PSID *)MembersBuffer->Sids)[i]);
9337
9340
9341 if (!NT_SUCCESS(Status))
9342 break;
9343 }
9344
9345 return Status;
9346}
NTSTATUS NTAPI SamrRemoveMemberFromAlias(IN SAMPR_HANDLE AliasHandle, IN PRPC_SID MemberId)
Definition: samrpc.c:5324

Referenced by SamRemoveMultipleMembersFromAlias().

◆ SamrRidToSid()

NTSTATUS NTAPI SamrRidToSid ( IN SAMPR_HANDLE  ObjectHandle,
IN unsigned long  Rid,
OUT PRPC_SID *  Sid 
)

Definition at line 9796 of file samrpc.c.

9799{
9802}

◆ SamrSetBootKeyInformation()

NTSTATUS NTAPI SamrSetBootKeyInformation ( IN handle_t  BindingHandle)

Definition at line 9677 of file samrpc.c.

9678{
9681}

◆ SamrSetDSRMPassword()

NTSTATUS NTAPI SamrSetDSRMPassword ( IN handle_t  BindingHandle,
IN PRPC_UNICODE_STRING  Unused,
IN unsigned long  UserId,
IN PENCRYPTED_NT_OWF_PASSWORD  EncryptedNtOwfPassword 
)

Definition at line 9807 of file samrpc.c.

9811{
9814}

◆ SamrSetInformationAlias()

NTSTATUS NTAPI SamrSetInformationAlias ( IN SAMPR_HANDLE  AliasHandle,
IN ALIAS_INFORMATION_CLASS  AliasInformationClass,
IN PSAMPR_ALIAS_INFO_BUFFER  Buffer 
)

Definition at line 5177 of file samrpc.c.

5180{
5181 PSAM_DB_OBJECT AliasObject;
5183
5184 TRACE("SamrSetInformationAlias(%p %lu %p)\n",
5185 AliasHandle, AliasInformationClass, Buffer);
5186
5188 TRUE);
5189
5190 /* Validate the alias handle */
5191 Status = SampValidateDbObject(AliasHandle,
5194 &AliasObject);
5195 if (!NT_SUCCESS(Status))
5196 goto done;
5197
5198 switch (AliasInformationClass)
5199 {
5201 Status = SampSetAliasName(AliasObject,
5202 Buffer);
5203 break;
5204
5207 L"Description",
5208 &Buffer->AdminComment.AdminComment);
5209 break;
5210
5211 default:
5213 break;
5214 }
5215
5216done:
5218
5219 return Status;
5220}
#define ALIAS_WRITE_ACCOUNT
Definition: ntsam.h:13
static NTSTATUS SampSetAliasName(PSAM_DB_OBJECT AliasObject, PSAMPR_ALIAS_INFO_BUFFER Buffer)
Definition: samrpc.c:5099

Referenced by SamSetInformationAlias().

◆ SamrSetInformationDomain()

NTSTATUS NTAPI SamrSetInformationDomain ( IN SAMPR_HANDLE  DomainHandle,
IN DOMAIN_INFORMATION_CLASS  DomainInformationClass,
IN PSAMPR_DOMAIN_INFO_BUFFER  DomainInformation 
)

Definition at line 1794 of file samrpc.c.

1797{
1798 PSAM_DB_OBJECT DomainObject;
1801
1802 TRACE("SamrSetInformationDomain(%p %lu %p)\n",
1803 DomainHandle, DomainInformationClass, DomainInformation);
1804
1805 switch (DomainInformationClass)
1806 {
1810 break;
1811
1816 break;
1817
1822 break;
1823
1824 default:
1826 }
1827
1829 TRUE);
1830
1831 /* Validate the server handle */
1832 Status = SampValidateDbObject(DomainHandle,
1835 &DomainObject);
1836 if (!NT_SUCCESS(Status))
1837 goto done;
1838
1839 switch (DomainInformationClass)
1840 {
1842 Status = SampSetDomainPassword(DomainObject,
1843 DomainInformation);
1844 break;
1845
1847 Status = SampSetDomainLogoff(DomainObject,
1848 DomainInformation);
1849 break;
1850
1852 Status = SampSetObjectAttributeString(DomainObject,
1853 L"OemInformation",
1854 &DomainInformation->Oem.OemInformation);
1855 break;
1856
1858 Status = SampSetObjectAttributeString(DomainObject,
1859 L"Name",
1860 &DomainInformation->Name.DomainName);
1861 break;
1862
1864 Status = SampSetObjectAttributeString(DomainObject,
1865 L"ReplicaSourceNodeName",
1866 &DomainInformation->Replication.ReplicaSourceNodeName);
1867 break;
1868
1870 Status = SampSetDomainServerRole(DomainObject,
1871 DomainInformation);
1872 break;
1873
1875 Status = SampSetDomainState(DomainObject,
1876 DomainInformation);
1877 break;
1878
1880 Status = SampSetDomainLockout(DomainObject,
1881 DomainInformation);
1882 break;
1883
1884 default:
1886 }
1887
1888done:
1890
1891 return Status;
1892}
#define DOMAIN_WRITE_OTHER_PARAMETERS
Definition: ntsam.h:36
#define DOMAIN_WRITE_PASSWORD_PARAMS
Definition: ntsam.h:34
#define DOMAIN_ADMINISTER_SERVER
Definition: ntsam.h:43
static NTSTATUS SampSetDomainState(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER Buffer)
Definition: samrpc.c:1730
static NTSTATUS SampSetDomainServerRole(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER Buffer)
Definition: samrpc.c:1700
static NTSTATUS SampSetDomainLogoff(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER Buffer)
Definition: samrpc.c:1669
static NTSTATUS SampSetDomainPassword(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER Buffer)
Definition: samrpc.c:1633
static NTSTATUS SampSetDomainLockout(PSAM_DB_OBJECT DomainObject, PSAMPR_DOMAIN_INFO_BUFFER Buffer)
Definition: samrpc.c:1760

Referenced by SamSetInformationDomain().

◆ SamrSetInformationGroup()

NTSTATUS NTAPI SamrSetInformationGroup ( IN SAMPR_HANDLE  GroupHandle,
IN GROUP_INFORMATION_CLASS  GroupInformationClass,
IN PSAMPR_GROUP_INFO_BUFFER  Buffer 
)

Definition at line 4420 of file samrpc.c.

4423{
4424 PSAM_DB_OBJECT GroupObject;
4426
4427 TRACE("SamrSetInformationGroup(%p %lu %p)\n",
4428 GroupHandle, GroupInformationClass, Buffer);
4429
4431 TRUE);
4432
4433 /* Validate the group handle */
4434 Status = SampValidateDbObject(GroupHandle,
4437 &GroupObject);
4438 if (!NT_SUCCESS(Status))
4439 goto done;
4440
4441 switch (GroupInformationClass)
4442 {
4444 Status = SampSetGroupName(GroupObject,
4445 Buffer);
4446 break;
4447
4449 Status = SampSetGroupAttribute(GroupObject,
4450 Buffer);
4451 break;
4452
4455 L"AdminComment",
4456 &Buffer->AdminComment.AdminComment);
4457 break;
4458
4459 default:
4461 break;
4462 }
4463
4464done:
4466
4467 return Status;
4468}
#define GROUP_WRITE_ACCOUNT
Definition: ntsam.h:76
static NTSTATUS SampSetGroupAttribute(PSAM_DB_OBJECT GroupObject, PSAMPR_GROUP_INFO_BUFFER Buffer)
Definition: samrpc.c:4388
static NTSTATUS SampSetGroupName(PSAM_DB_OBJECT GroupObject, PSAMPR_GROUP_INFO_BUFFER Buffer)
Definition: samrpc.c:4312

Referenced by SamSetInformationGroup().

◆ SamrSetInformationUser()

NTSTATUS NTAPI SamrSetInformationUser ( IN SAMPR_HANDLE  UserHandle,
IN USER_INFORMATION_CLASS  UserInformationClass,
IN PSAMPR_USER_INFO_BUFFER  Buffer 
)

Definition at line 7852 of file samrpc.c.

7855{
7856 TRACE("SamrSetInformationUser(%p %lu %p)\n",
7857 UserHandle, UserInformationClass, Buffer);
7858
7859 return SamrSetInformationUser2(UserHandle,
7860 UserInformationClass,
7861 Buffer);
7862}
NTSTATUS NTAPI SamrSetInformationUser2(IN SAMPR_HANDLE UserHandle, IN USER_INFORMATION_CLASS UserInformationClass, IN PSAMPR_USER_INFO_BUFFER Buffer)
Definition: samrpc.c:9472

Referenced by LsaApLogonUserEx2(), and SamSetInformationUser().

◆ SamrSetInformationUser2()

NTSTATUS NTAPI SamrSetInformationUser2 ( IN SAMPR_HANDLE  UserHandle,
IN USER_INFORMATION_CLASS  UserInformationClass,
IN PSAMPR_USER_INFO_BUFFER  Buffer 
)

Definition at line 9472 of file samrpc.c.

9475{
9476 PSAM_DB_OBJECT UserObject;
9479
9480 TRACE("SamrSetInformationUser2(%p %lu %p)\n",
9481 UserHandle, UserInformationClass, Buffer);
9482
9483 switch (UserInformationClass)
9484 {
9499 break;
9500
9504 break;
9505
9508 break;
9509
9513 break;
9514
9515 case UserAllInformation:
9517 DesiredAccess = 0; /* FIXME */
9518 break;
9519
9520 default:
9522 }
9523
9525 TRUE);
9526
9527 /* Validate the domain handle */
9528 Status = SampValidateDbObject(UserHandle,
9531 &UserObject);
9532 if (!NT_SUCCESS(Status))
9533 {
9534 TRACE("failed with status 0x%08lx\n", Status);
9535 goto done;
9536 }
9537
9538 switch (UserInformationClass)
9539 {
9541 Status = SampSetUserGeneral(UserObject,
9542 Buffer);
9543 break;
9544
9546 Status = SampSetUserPreferences(UserObject,
9547 Buffer);
9548 break;
9549
9552 &Buffer->LogonHours.LogonHours);
9553 break;
9554
9556 Status = SampSetUserName(UserObject,
9557 &Buffer->Name.UserName);
9558 if (!NT_SUCCESS(Status))
9559 break;
9560
9562 L"FullName",
9563 &Buffer->Name.FullName);
9564 break;
9565
9567 Status = SampSetUserName(UserObject,
9568 &Buffer->AccountName.UserName);
9569 break;
9570
9573 L"FullName",
9574 &Buffer->FullName.FullName);
9575 break;
9576
9578 Status = SampSetUserPrimaryGroup(UserObject,
9579 Buffer);
9580 break;
9581
9584 L"HomeDirectory",
9585 &Buffer->Home.HomeDirectory);
9586 if (!NT_SUCCESS(Status))
9587 break;
9588
9590 L"HomeDirectoryDrive",
9591 &Buffer->Home.HomeDirectoryDrive);
9592 break;
9593
9596 L"ScriptPath",
9597 &Buffer->Script.ScriptPath);
9598 break;
9599
9602 L"ProfilePath",
9603 &Buffer->Profile.ProfilePath);
9604 break;
9605
9608 L"AdminComment",
9609 &Buffer->AdminComment.AdminComment);
9610 break;
9611
9614 L"WorkStations",
9615 &Buffer->WorkStations.WorkStations);
9616 break;
9617
9619 TRACE("Password: %S\n", Buffer->SetPassword.Password.Buffer);
9620 TRACE("PasswordExpired: %d\n", Buffer->SetPassword.PasswordExpired);
9621
9623 L"Password",
9624 &Buffer->SetPassword.Password);
9625 break;
9626
9628 Status = SampSetUserControl(UserObject,
9629 Buffer);
9630 break;
9631
9633 Status = SampSetUserExpires(UserObject,
9634 Buffer);
9635 break;
9636
9638 Status = SampSetUserInternal1(UserObject,
9639 Buffer);
9640 break;
9641
9643 Status = SampSetUserInternal2(UserObject,
9644 Buffer);
9645 break;
9646
9649 L"Parameters",
9650 &Buffer->Parameters.Parameters);
9651 break;
9652
9653 case UserAllInformation:
9654 Status = SampSetUserAll(UserObject,
9655 Buffer);
9656 break;
9657
9658// case UserInternal4Information:
9659// case UserInternal5Information:
9660// case UserInternal4InformationNew:
9661// case UserInternal5InformationNew:
9662
9663 default:
9665 }
9666
9667done:
9669
9670 return Status;
9671}
#define USER_FORCE_PASSWORD_CHANGE
Definition: ntsam.h:133
#define USER_WRITE_ACCOUNT
Definition: ntsam.h:131
@ UserSetPasswordInformation
Definition: ntsam.h:528
#define USER_WRITE_PREFERENCES
Definition: ntsam.h:128
static NTSTATUS SampSetUserPreferences(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
Definition: samrpc.c:7376
static NTSTATUS SampSetUserAll(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
Definition: samrpc.c:7612
static NTSTATUS SampSetUserInternal2(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
Definition: samrpc.c:7559
static NTSTATUS SampSetUserExpires(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
Definition: samrpc.c:7473
static NTSTATUS SampSetUserGeneral(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
Definition: samrpc.c:7323
static NTSTATUS SampSetUserInternal1(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
Definition: samrpc.c:7504
static NTSTATUS SampSetUserPrimaryGroup(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
Definition: samrpc.c:7413
static NTSTATUS SampSetUserControl(PSAM_DB_OBJECT UserObject, PSAMPR_USER_INFO_BUFFER Buffer)
Definition: samrpc.c:7443

Referenced by SamrSetInformationUser().

◆ SamrSetMemberAttributesOfGroup()

NTSTATUS NTAPI SamrSetMemberAttributesOfGroup ( IN SAMPR_HANDLE  GroupHandle,
IN unsigned long  MemberId,
IN unsigned long  Attributes 
)

Definition at line 4782 of file samrpc.c.

4785{
4786 PSAM_DB_OBJECT GroupObject;
4788
4789 TRACE("SamrSetMemberAttributesOfGroup(%p %lu %lx)\n",
4790 GroupHandle, MemberId, Attributes);
4791
4793 TRUE);
4794
4795 /* Validate the group handle */
4796 Status = SampValidateDbObject(GroupHandle,
4799 &GroupObject);
4800 if (!NT_SUCCESS(Status))
4801 {
4802 TRACE("SampValidateDbObject failed with status 0x%08lx\n", Status);
4803 goto done;
4804 }
4805
4807 MemberId,
4808 GroupObject->RelativeId,
4809 Attributes);
4810 if (!NT_SUCCESS(Status))
4811 {
4812 TRACE("SampSetUserGroupAttributes failed with status 0x%08lx\n", Status);
4813 }
4814
4815done:
4817
4818 return Status;
4819}
NTSTATUS SampSetUserGroupAttributes(IN PSAM_DB_OBJECT DomainObject, IN ULONG UserId, IN ULONG GroupId, IN ULONG GroupAttributes)
Definition: user.c:248

Referenced by SamSetMemberAttributesOfGroup().

◆ SamrSetSecurityObject()

NTSTATUS NTAPI SamrSetSecurityObject ( IN SAMPR_HANDLE  ObjectHandle,
IN SECURITY_INFORMATION  SecurityInformation,
IN PSAMPR_SR_SECURITY_DESCRIPTOR  SecurityDescriptor 
)

Definition at line 192 of file samrpc.c.

195{
196 PSAM_DB_OBJECT DbObject = NULL;
198 PSECURITY_DESCRIPTOR RelativeSd = NULL;
199 ULONG RelativeSdSize = 0;
203
204 TRACE("SamrSetSecurityObject(%p %lx %p)\n",
206
207 if ((SecurityDescriptor == NULL) ||
208 (SecurityDescriptor->SecurityDescriptor == NULL) ||
211
212 if (SecurityInformation == 0 ||
216
219
222
225
229
233
234 /* Validate the server handle */
235 Status = SampValidateDbObject(ObjectHandle,
238 &DbObject);
239 if (!NT_SUCCESS(Status))
240 goto done;
241
242 /* Get the mapping for the object type */
243 switch (DbObject->ObjectType)
244 {
247 break;
248
251 break;
252
253 case SamDbAliasObject:
255 break;
256
257 case SamDbGroupObject:
259 break;
260
261 case SamDbUserObject:
263 break;
264
265 default:
267 }
268
269 /* Get the size of the SD */
271 L"SecDesc",
272 NULL,
273 NULL,
274 &RelativeSdSize);
275 if (!NT_SUCCESS(Status))
276 return Status;
277
278 /* Allocate a buffer for the SD */
279 RelativeSd = RtlAllocateHeap(RtlGetProcessHeap(), 0, RelativeSdSize);
280 if (RelativeSd == NULL)
282
283 /* Get the SD */
285 L"SecDesc",
286 NULL,
287 RelativeSd,
288 &RelativeSdSize);
289 if (!NT_SUCCESS(Status))
290 goto done;
291
292 /* Build the new security descriptor */
294 (PSECURITY_DESCRIPTOR)SecurityDescriptor->SecurityDescriptor,
295 &RelativeSd,
296 Mapping,
298 if (!NT_SUCCESS(Status))
299 {
300 ERR("RtlSetSecurityObject failed (Status 0x%08lx)\n", Status);
301 goto done;
302 }
303
304 /* Set the modified SD */
306 L"SecDesc",
308 RelativeSd,
309 RtlLengthSecurityDescriptor(RelativeSd));
310 if (!NT_SUCCESS(Status))
311 {
312 ERR("SampSetObjectAttribute failed (Status 0x%08lx)\n", Status);
313 }
314
315done:
316 if (TokenHandle != NULL)
318
319 if (RelativeSd != NULL)
320 RtlFreeHeap(RtlGetProcessHeap(), 0, RelativeSd);
321
322 return Status;
323}
@ Group
Definition: help.c:22
PVOID NTAPI RtlAllocateHeap(IN PVOID HeapHandle, IN ULONG Flags, IN SIZE_T Size)
Definition: heap.c:616
#define STATUS_INVALID_HANDLE
Definition: d3dkmdt.h:40
#define ERROR_INVALID_PARAMETER
Definition: compat.h:101
static PVOID Mapping[EMS_PHYSICAL_PAGES]
Definition: emsdrv.c:41
_In_ ACCESS_MASK _In_ ULONG _Out_ PHANDLE TokenHandle
Definition: psfuncs.h:772
NTSYSAPI NTSTATUS NTAPI RtlSetSecurityObject(_In_ SECURITY_INFORMATION SecurityInformation, _In_ PSECURITY_DESCRIPTOR ModificationDescriptor, _Out_ PSECURITY_DESCRIPTOR *ObjectsSecurityDescriptor, _In_ PGENERIC_MAPPING GenericMapping, _In_ HANDLE Token)
_Out_writes_bytes_to_opt_ AbsoluteSecurityDescriptorSize PSECURITY_DESCRIPTOR _Inout_ PULONG _Out_writes_bytes_to_opt_ DaclSize PACL _Inout_ PULONG _Out_writes_bytes_to_opt_ SaclSize PACL _Inout_ PULONG _Out_writes_bytes_to_opt_ OwnerSize PSID Owner
Definition: rtlfuncs.h:1629
NTSYSAPI BOOLEAN NTAPI RtlValidSecurityDescriptor(IN PSECURITY_DESCRIPTOR SecurityDescriptor)
Definition: sd.c:1054
#define WRITE_DAC
Definition: nt_native.h:59
NTSTATUS NTAPI NtClose(IN HANDLE Handle)
Definition: obhandle.c:3434
#define WRITE_OWNER
Definition: nt_native.h:60
SAM_DB_OBJECT_TYPE ObjectType
Definition: samsrv.h:48
NTSYSAPI ULONG WINAPI RtlLengthSecurityDescriptor(PSECURITY_DESCRIPTOR)

Referenced by SamSetSecurityObject().

◆ SamrShutdownSamServer()

NTSTATUS NTAPI SamrShutdownSamServer ( IN SAMPR_HANDLE  ServerHandle)

Definition at line 466 of file samrpc.c.

467{
468 PSAM_DB_OBJECT ServerObject;
470
471 TRACE("SamrShutdownSamServer(%p)\n",
472 ServerHandle);
473
475 TRUE);
476
477 /* Validate the server handle */
478 Status = SampValidateDbObject(ServerHandle,
481 &ServerObject);
482
484
485 if (!NT_SUCCESS(Status))
486 return Status;
487
488 /* Shut the server down */
490
492 if (!NT_SUCCESS(Status))
493 {
494 ERR("SampShutdownDisplayCache() failed (Status 0x%08lx)\n", Status);
495 }
496
497 return STATUS_SUCCESS;
498}
NTSTATUS SampShutdownDisplayCache(VOID)
Definition: display.c:164
#define SAM_SERVER_SHUTDOWN
Definition: ntsam.h:100
RPC_STATUS WINAPI RpcMgmtStopServerListening(RPC_BINDING_HANDLE Binding)
Definition: rpc_server.c:1596

Referenced by SamShutdownSamServer().

◆ SamrTestPrivateFunctionsDomain()

NTSTATUS NTAPI SamrTestPrivateFunctionsDomain ( IN SAMPR_HANDLE  DomainHandle)

Definition at line 8298 of file samrpc.c.

8299{
8302}

◆ SamrTestPrivateFunctionsUser()

NTSTATUS NTAPI SamrTestPrivateFunctionsUser ( IN SAMPR_HANDLE  UserHandle)

Definition at line 8308 of file samrpc.c.

8309{
8312}

◆ SamrUnicodeChangePasswordUser2()

NTSTATUS NTAPI SamrUnicodeChangePasswordUser2 ( IN handle_t  BindingHandle,
IN PRPC_UNICODE_STRING  ServerName,
IN PRPC_UNICODE_STRING  UserName,
IN PSAMPR_ENCRYPTED_USER_PASSWORD  NewPasswordEncryptedWithOldNt,
IN PENCRYPTED_NT_OWF_PASSWORD  OldNtOwfPasswordEncryptedWithNewNt,
IN unsigned char  LmPresent,
IN PSAMPR_ENCRYPTED_USER_PASSWORD  NewPasswordEncryptedWithOldLm,
IN PENCRYPTED_LM_OWF_PASSWORD  OldLmOwfPasswordEncryptedWithNewNt 
)

Definition at line 9365 of file samrpc.c.

9373{
9376}

◆ SamrUnicodeChangePasswordUser3()

NTSTATUS NTAPI SamrUnicodeChangePasswordUser3 ( IN handle_t  BindingHandle)

Definition at line 9732 of file samrpc.c.

9733{
9736}

◆ SamrValidatePassword()

NTSTATUS NTAPI SamrValidatePassword ( IN handle_t  Handle,
IN PASSWORD_POLICY_VALIDATION_TYPE  ValidationType,
IN PSAM_VALIDATE_INPUT_ARG  InputArg,
OUT PSAM_VALIDATE_OUTPUT_ARG *  OutputArg 
)

Definition at line 9819 of file samrpc.c.

9823{
9826}

Variable Documentation

◆ AliasMapping

GENERIC_MAPPING AliasMapping
static
Initial value:
=
{
}
#define ALIAS_EXECUTE
Definition: ntsam.h:23
#define ALIAS_READ
Definition: ntsam.h:15
#define ALIAS_WRITE
Definition: ntsam.h:18
#define ALIAS_ALL_ACCESS
Definition: ntsam.h:26

Definition at line 32 of file samrpc.c.

Referenced by SamrCreateAliasInDomain(), SamrOpenAlias(), and SamrSetSecurityObject().

◆ DomainMapping

GENERIC_MAPPING DomainMapping
static
Initial value:
=
{
}
#define DOMAIN_ALL_ACCESS
Definition: ntsam.h:62
#define DOMAIN_EXECUTE
Definition: ntsam.h:57
#define DOMAIN_WRITE
Definition: ntsam.h:49
#define DOMAIN_READ
Definition: ntsam.h:45

Definition at line 24 of file samrpc.c.

Referenced by SamrOpenDomain(), and SamrSetSecurityObject().

◆ GroupMapping

GENERIC_MAPPING GroupMapping
static
Initial value:
=
{
}
#define GROUP_ALL_ACCESS
Definition: ntsam.h:92
#define GROUP_EXECUTE
Definition: ntsam.h:89
#define GROUP_WRITE
Definition: ntsam.h:84
#define GROUP_READ
Definition: ntsam.h:81

Definition at line 40 of file samrpc.c.

Referenced by SamrCreateGroupInDomain(), SamrOpenGroup(), and SamrSetSecurityObject().

◆ NtSidAuthority

◆ pServerMapping

PGENERIC_MAPPING pServerMapping = &ServerMapping

Definition at line 56 of file samrpc.c.

Referenced by SamIConnect().

◆ ServerMapping

GENERIC_MAPPING ServerMapping
static
Initial value:
=
{
}
#define SAM_SERVER_READ
Definition: ntsam.h:106
#define SAM_SERVER_EXECUTE
Definition: ntsam.h:114
#define SAM_SERVER_ALL_ACCESS
Definition: ntsam.h:118
#define SAM_SERVER_WRITE
Definition: ntsam.h:109

Definition at line 16 of file samrpc.c.

Referenced by SamrConnect5(), and SamrSetSecurityObject().

◆ UserMapping

GENERIC_MAPPING UserMapping
static
Initial value:
=
{
}
#define USER_READ
Definition: ntsam.h:138
#define USER_WRITE
Definition: ntsam.h:145
#define USER_EXECUTE
Definition: ntsam.h:149
#define USER_ALL_ACCESS
Definition: ntsam.h:153

Definition at line 48 of file samrpc.c.

Referenced by InitProcessCallback(), MapGlobalUserHeap(), SamrCreateUser2InDomain(), SamrCreateUserInDomain(), SamrOpenUser(), and SamrSetSecurityObject().