ReactOS 0.4.17-dev-1321-g5c122a9
msv1_0.h File Reference
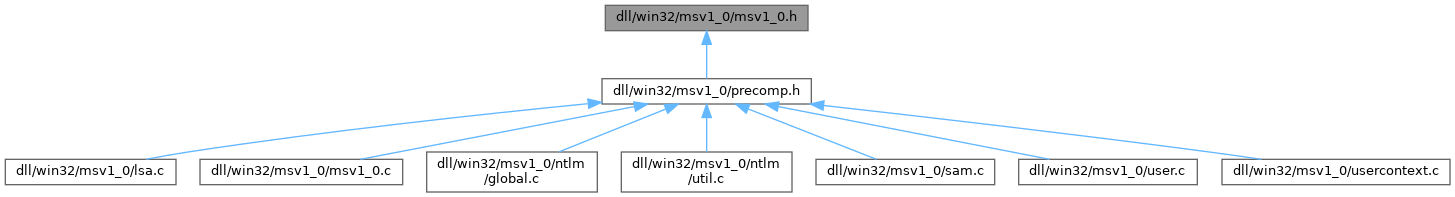
This graph shows which files directly or indirectly include this file:

Go to the source code of this file.

Classes

struct  _RPC_SID
 
struct  _RPC_UNICODE_STRING
 
struct  _OLD_LARGE_INTEGER
 
struct  RPC_SHORT_BLOB
 
struct  _SAMPR_SR_SECURITY_DESCRIPTOR
 
struct  _ENCRYPTED_LM_OWF_PASSWORD
 
struct  _SAMPR_ULONG_ARRAY
 
struct  _SAMPR_LOGON_HOURS
 
struct  _SAMPR_USER_INTERNAL2_INFORMATION
 
struct  _SAMPR_USER_ALL_INFORMATION
 
union  _SAMPR_USER_INFO_BUFFER
 
struct  _LSAPR_POLICY_AUDIT_EVENTS_INFO
 
struct  _LSAPR_POLICY_PRIMARY_DOM_INFO
 
struct  _LSAPR_POLICY_ACCOUNT_DOM_INFO
 
struct  _LSAPR_POLICY_PD_ACCOUNT_INFO
 
struct  _POLICY_LSA_REPLICA_SRCE_INFO
 
struct  _LSAPR_POLICY_DNS_DOMAIN_INFO
 
union  _LSAPR_POLICY_INFORMATION
 

Macros

#define FIXUP_POINTER(Pointer, Offset)   ((Pointer != NULL) ? ((PWSTR)((ULONG_PTR)Pointer + Offset)) : NULL)
 
#define USER_LOGON_BAD_PASSWORD   0x08000000
 
#define USER_LOGON_SUCCESS   0x10000000
 

Typedefs

typedef struct _RPC_SID RPC_SID
 
typedef struct _RPC_SID * PRPC_SID
 
typedef struct _RPC_UNICODE_STRING RPC_UNICODE_STRING
 
typedef struct _RPC_UNICODE_STRING * PRPC_UNICODE_STRING
 
typedef wchar_t * PSAMPR_SERVER_NAME
 
typedef void * SAMPR_HANDLE
 
typedef struct _OLD_LARGE_INTEGER OLD_LARGE_INTEGER
 
typedef struct _OLD_LARGE_INTEGER * POLD_LARGE_INTEGER
 
typedef struct RPC_SHORT_BLOB RPC_SHORT_BLOB
 
typedef struct RPC_SHORT_BLOB * PRPC_SHORT_BLOB
 
typedef struct _SAMPR_SR_SECURITY_DESCRIPTOR SAMPR_SR_SECURITY_DESCRIPTOR
 
typedef struct _SAMPR_SR_SECURITY_DESCRIPTOR * PSAMPR_SR_SECURITY_DESCRIPTOR
 
typedef struct _ENCRYPTED_LM_OWF_PASSWORD ENCRYPTED_LM_OWF_PASSWORD
 
typedef struct _ENCRYPTED_LM_OWF_PASSWORD * PENCRYPTED_LM_OWF_PASSWORD
 
typedef struct _ENCRYPTED_LM_OWF_PASSWORD ENCRYPTED_NT_OWF_PASSWORD
 
typedef struct _ENCRYPTED_LM_OWF_PASSWORD * PENCRYPTED_NT_OWF_PASSWORD
 
typedef struct _SAMPR_ULONG_ARRAY SAMPR_ULONG_ARRAY
 
typedef struct _SAMPR_ULONG_ARRAY * PSAMPR_ULONG_ARRAY
 
typedef struct _SAMPR_LOGON_HOURS SAMPR_LOGON_HOURS
 
typedef struct _SAMPR_LOGON_HOURS * PSAMPR_LOGON_HOURS
 
typedef struct _SAMPR_USER_INTERNAL2_INFORMATION SAMPR_USER_INTERNAL2_INFORMATION
 
typedef struct _SAMPR_USER_INTERNAL2_INFORMATION * PSAMPR_USER_INTERNAL2_INFORMATION
 
typedef struct _SAMPR_USER_ALL_INFORMATION SAMPR_USER_ALL_INFORMATION
 
typedef struct _SAMPR_USER_ALL_INFORMATION * PSAMPR_USER_ALL_INFORMATION
 
typedef union _SAMPR_USER_INFO_BUFFER SAMPR_USER_INFO_BUFFER
 
typedef union _SAMPR_USER_INFO_BUFFER * PSAMPR_USER_INFO_BUFFER
 
typedef PVOID LSAPR_HANDLE
 
typedef struct _LSAPR_POLICY_AUDIT_EVENTS_INFO LSAPR_POLICY_AUDIT_EVENTS_INFO
 
typedef struct _LSAPR_POLICY_AUDIT_EVENTS_INFO * PLSAPR_POLICY_AUDIT_EVENTS_INFO
 
typedef struct _LSAPR_POLICY_PRIMARY_DOM_INFO LSAPR_POLICY_PRIMARY_DOM_INFO
 
typedef struct _LSAPR_POLICY_PRIMARY_DOM_INFO * PLSAPR_POLICY_PRIMARY_DOM_INFO
 
typedef struct _LSAPR_POLICY_ACCOUNT_DOM_INFO LSAPR_POLICY_ACCOUNT_DOM_INFO
 
typedef struct _LSAPR_POLICY_ACCOUNT_DOM_INFO * PLSAPR_POLICY_ACCOUNT_DOM_INFO
 
typedef struct _LSAPR_POLICY_PD_ACCOUNT_INFO LSAPR_POLICY_PD_ACCOUNT_INFO
 
typedef struct _LSAPR_POLICY_PD_ACCOUNT_INFO * PLSAPR_POLICY_PD_ACCOUNT_INFO
 
typedef struct _POLICY_LSA_REPLICA_SRCE_INFO POLICY_LSA_REPLICA_SRCE_INFO
 
typedef struct _POLICY_LSA_REPLICA_SRCE_INFO * PPOLICY_LSA_REPLICA_SRCE_INFO
 
typedef struct _LSAPR_POLICY_DNS_DOMAIN_INFO LSAPR_POLICY_DNS_DOMAIN_INFO
 
typedef struct _LSAPR_POLICY_DNS_DOMAIN_INFO * PLSAPR_POLICY_DNS_DOMAIN_INFO
 
typedef union _LSAPR_POLICY_INFORMATION LSAPR_POLICY_INFORMATION
 
typedef union _LSAPR_POLICY_INFORMATION * PLSAPR_POLICY_INFORMATION
 

Functions

NTSTATUS NTAPI SamIConnect (IN PSAMPR_SERVER_NAME ServerName, OUT SAMPR_HANDLE *ServerHandle, IN ACCESS_MASK DesiredAccess, IN BOOLEAN Trusted)
 
VOID NTAPI SamIFreeVoid (PVOID Ptr)
 
VOID NTAPI SamIFree_SAMPR_ULONG_ARRAY (PSAMPR_ULONG_ARRAY Ptr)
 
VOID NTAPI SamIFree_SAMPR_USER_INFO_BUFFER (PSAMPR_USER_INFO_BUFFER Ptr, USER_INFORMATION_CLASS InformationClass)
 
NTSTATUS NTAPI SamrChangePasswordUser (IN SAMPR_HANDLE UserHandle, IN unsigned char LmPresent, IN PENCRYPTED_LM_OWF_PASSWORD OldLmEncryptedWithNewLm, IN PENCRYPTED_LM_OWF_PASSWORD NewLmEncryptedWithOldLm, IN unsigned char NtPresent, IN PENCRYPTED_NT_OWF_PASSWORD OldNtEncryptedWithNewNt, IN PENCRYPTED_NT_OWF_PASSWORD NewNtEncryptedWithOldNt, IN unsigned char NtCrossEncryptionPresent, IN PENCRYPTED_NT_OWF_PASSWORD NewNtEncryptedWithNewLm, IN unsigned char LmCrossEncryptionPresent, IN PENCRYPTED_LM_OWF_PASSWORD NewLmEncryptedWithNewNt)
 
NTSTATUS NTAPI SamrCloseHandle (IN OUT SAMPR_HANDLE *SamHandle)
 
NTSTATUS NTAPI SamrLookupDomainInSamServer (IN SAMPR_HANDLE ServerHandle, IN PRPC_UNICODE_STRING Name, OUT PRPC_SID *DomainId)
 
NTSTATUS NTAPI SamrLookupNamesInDomain (IN SAMPR_HANDLE DomainHandle, IN ULONG Count, IN RPC_UNICODE_STRING Names[], OUT PSAMPR_ULONG_ARRAY RelativeIds, OUT PSAMPR_ULONG_ARRAY Use)
 
NTSTATUS NTAPI SamrOpenDomain (IN SAMPR_HANDLE ServerHandle, IN ACCESS_MASK DesiredAccess, IN PRPC_SID DomainId, OUT SAMPR_HANDLE *DomainHandle)
 
NTSTATUS NTAPI SamrOpenUser (IN SAMPR_HANDLE DomainHandle, IN ACCESS_MASK DesiredAccess, IN ULONG UserId, OUT SAMPR_HANDLE *UserHandle)
 
NTSTATUS NTAPI SamrQueryInformationUser (IN SAMPR_HANDLE UserHandle, IN USER_INFORMATION_CLASS UserInformationClass, OUT PSAMPR_USER_INFO_BUFFER *Buffer)
 
NTSTATUS NTAPI SamrSetInformationUser (IN SAMPR_HANDLE UserHandle, IN USER_INFORMATION_CLASS UserInformationClass, IN PSAMPR_USER_INFO_BUFFER Buffer)
 
VOID NTAPI LsaIFree_LSAPR_POLICY_INFORMATION (IN POLICY_INFORMATION_CLASS InformationClass, IN PLSAPR_POLICY_INFORMATION PolicyInformation)
 
NTSTATUS WINAPI LsaIOpenPolicyTrusted (OUT LSAPR_HANDLE *PolicyHandle)
 
NTSTATUS WINAPI LsarClose (IN OUT LSAPR_HANDLE *ObjectHandle)
 
NTSTATUS WINAPI LsarLookupPrivilegeValue (IN LSAPR_HANDLE PolicyHandle, IN PRPC_UNICODE_STRING Name, OUT PLUID Value)
 
NTSTATUS WINAPI LsarQueryInformationPolicy (IN LSAPR_HANDLE PolicyHandle, IN POLICY_INFORMATION_CLASS InformationClass, OUT PLSAPR_POLICY_INFORMATION *PolicyInformation)
 
NTSTATUS WINAPI SystemFunction006 (LPCSTR password, LPSTR hash)
 
NTSTATUS WINAPI SystemFunction007 (PUNICODE_STRING string, LPBYTE hash)
 
NTSTATUS WINAPI SystemFunction012 (const BYTE *in, const BYTE *key, LPBYTE out)
 
NTSTATUS NTAPI LsaApCallPackage (_In_ PLSA_CLIENT_REQUEST ClientRequest, _In_ PVOID ProtocolSubmitBuffer, _In_ PVOID ClientBufferBase, _In_ ULONG SubmitBufferLength, _Out_ PVOID *ProtocolReturnBuffer, _Out_ PULONG ReturnBufferLength, _Out_ PNTSTATUS ProtocolStatus)
 
NTSTATUS NTAPI LsaApCallPackagePassthrough (_In_ PLSA_CLIENT_REQUEST ClientRequest, _In_ PVOID ProtocolSubmitBuffer, _In_ PVOID ClientBufferBase, _In_ ULONG SubmitBufferLength, _Out_ PVOID *ProtocolReturnBuffer, _Out_ PULONG ReturnBufferLength, _Out_ PNTSTATUS ProtocolStatus)
 
NTSTATUS NTAPI LsaApCallPackageUntrusted (_In_ PLSA_CLIENT_REQUEST ClientRequest, _In_ PVOID ProtocolSubmitBuffer, _In_ PVOID ClientBufferBase, _In_ ULONG SubmitBufferLength, _Out_ PVOID *ProtocolReturnBuffer, _Out_ PULONG ReturnBufferLength, _Out_ PNTSTATUS ProtocolStatus)
 
VOID NTAPI LsaApLogonTerminated (_In_ PLUID LogonId)
 
NTSTATUS NTAPI LsaApLogonUserEx2 (_In_ PLSA_CLIENT_REQUEST ClientRequest, _In_ SECURITY_LOGON_TYPE LogonType, _In_ PVOID ProtocolSubmitBuffer, _In_ PVOID ClientBufferBase, _In_ ULONG SubmitBufferSize, _Out_ PVOID *ProfileBuffer, _Out_ PULONG ProfileBufferSize, _Out_ PLUID LogonId, _Out_ PNTSTATUS SubStatus, _Out_ PLSA_TOKEN_INFORMATION_TYPE TokenInformationType, _Out_ PVOID *TokenInformation, _Out_ PUNICODE_STRING *AccountName, _Out_ PUNICODE_STRING *AuthenticatingAuthority, _Out_ PUNICODE_STRING *MachineName, _Out_ PSECPKG_PRIMARY_CRED PrimaryCredentials, _Out_ PSECPKG_SUPPLEMENTAL_CRED_ARRAY *SupplementalCredentials)
 

Macro Definition Documentation

◆ FIXUP_POINTER

#define FIXUP_POINTER (   Pointer,
  Offset 
)    ((Pointer != NULL) ? ((PWSTR)((ULONG_PTR)Pointer + Offset)) : NULL)

Definition at line 9 of file msv1_0.h.

◆ USER_LOGON_BAD_PASSWORD

#define USER_LOGON_BAD_PASSWORD   0x08000000

Definition at line 648 of file sam.idl.

◆ USER_LOGON_SUCCESS

#define USER_LOGON_SUCCESS   0x10000000

Definition at line 649 of file sam.idl.

Typedef Documentation

◆ ENCRYPTED_LM_OWF_PASSWORD

◆ ENCRYPTED_NT_OWF_PASSWORD

◆ LSAPR_HANDLE

Definition at line 229 of file msv1_0.h.

◆ LSAPR_POLICY_ACCOUNT_DOM_INFO

◆ LSAPR_POLICY_AUDIT_EVENTS_INFO

◆ LSAPR_POLICY_DNS_DOMAIN_INFO

◆ LSAPR_POLICY_INFORMATION

◆ LSAPR_POLICY_PD_ACCOUNT_INFO

◆ LSAPR_POLICY_PRIMARY_DOM_INFO

◆ OLD_LARGE_INTEGER

◆ PENCRYPTED_LM_OWF_PASSWORD

◆ PENCRYPTED_NT_OWF_PASSWORD

◆ PLSAPR_POLICY_ACCOUNT_DOM_INFO

◆ PLSAPR_POLICY_AUDIT_EVENTS_INFO

◆ PLSAPR_POLICY_DNS_DOMAIN_INFO

◆ PLSAPR_POLICY_INFORMATION

◆ PLSAPR_POLICY_PD_ACCOUNT_INFO

◆ PLSAPR_POLICY_PRIMARY_DOM_INFO

◆ POLD_LARGE_INTEGER

◆ POLICY_LSA_REPLICA_SRCE_INFO

◆ PPOLICY_LSA_REPLICA_SRCE_INFO

◆ PRPC_SHORT_BLOB

◆ PRPC_SID

◆ PRPC_UNICODE_STRING

◆ PSAMPR_LOGON_HOURS

◆ PSAMPR_SERVER_NAME

Definition at line 27 of file msv1_0.h.

◆ PSAMPR_SR_SECURITY_DESCRIPTOR

◆ PSAMPR_ULONG_ARRAY

◆ PSAMPR_USER_ALL_INFORMATION

◆ PSAMPR_USER_INFO_BUFFER

◆ PSAMPR_USER_INTERNAL2_INFORMATION

◆ RPC_SHORT_BLOB

◆ RPC_SID

◆ RPC_UNICODE_STRING

◆ SAMPR_HANDLE

typedef void* SAMPR_HANDLE

Definition at line 28 of file msv1_0.h.

◆ SAMPR_LOGON_HOURS

◆ SAMPR_SR_SECURITY_DESCRIPTOR

◆ SAMPR_ULONG_ARRAY

◆ SAMPR_USER_ALL_INFORMATION

◆ SAMPR_USER_INFO_BUFFER

◆ SAMPR_USER_INTERNAL2_INFORMATION

Function Documentation

◆ LsaApCallPackage()

NTSTATUS NTAPI LsaApCallPackage ( _In_ PLSA_CLIENT_REQUEST  ClientRequest,
_In_ PVOID  ProtocolSubmitBuffer,
_In_ PVOID  ClientBufferBase,
_In_ ULONG  SubmitBufferLength,
_Out_ PVOID *  ProtocolReturnBuffer,
_Out_ PULONG  ReturnBufferLength,
_Out_ PNTSTATUS  ProtocolStatus 
)

◆ LsaApCallPackagePassthrough()

NTSTATUS NTAPI LsaApCallPackagePassthrough ( _In_ PLSA_CLIENT_REQUEST  ClientRequest,
_In_ PVOID  ProtocolSubmitBuffer,
_In_ PVOID  ClientBufferBase,
_In_ ULONG  SubmitBufferLength,
_Out_ PVOID *  ProtocolReturnBuffer,
_Out_ PULONG  ReturnBufferLength,
_Out_ PNTSTATUS  ProtocolStatus 
)

◆ LsaApCallPackageUntrusted()

NTSTATUS NTAPI LsaApCallPackageUntrusted ( _In_ PLSA_CLIENT_REQUEST  ClientRequest,
_In_ PVOID  ProtocolSubmitBuffer,
_In_ PVOID  ClientBufferBase,
_In_ ULONG  SubmitBufferLength,
_Out_ PVOID *  ProtocolReturnBuffer,
_Out_ PULONG  ReturnBufferLength,
_Out_ PNTSTATUS  ProtocolStatus 
)

◆ LsaApLogonTerminated()

VOID NTAPI LsaApLogonTerminated ( _In_ PLUID  LogonId)

Definition at line 1437 of file msv1_0.c.

1439{
1440 PLOGON_LIST_ENTRY LogonEntry;
1441
1442 TRACE("LsaApLogonTerminated()\n");
1443
1444 /* Remove the given logon entry from the list */
1445 LogonEntry = GetLogonByLogonId(LogonId);
1446 if (LogonEntry != NULL)
1447 {
1449 RemoveEntryList(&LogonEntry->ListEntry);
1451
1452 if (LogonEntry->UserName.Buffer)
1453 RtlFreeHeap(RtlGetProcessHeap(), 0, LogonEntry->UserName.Buffer);
1454
1455 if (LogonEntry->LogonDomainName.Buffer)
1456 RtlFreeHeap(RtlGetProcessHeap(), 0, LogonEntry->LogonDomainName.Buffer);
1457
1458 if (LogonEntry->LogonServer.Buffer)
1459 RtlFreeHeap(RtlGetProcessHeap(), 0, LogonEntry->LogonServer.Buffer);
1460
1461 RtlFreeHeap(RtlGetProcessHeap(), 0, LogonEntry);
1462 }
1463}
BOOLEAN NTAPI RtlFreeHeap(IN PVOID HeapHandle, IN ULONG Flags, IN PVOID HeapBase)
Definition: heap.c:634
#define NULL
Definition: types.h:112
#define TRUE
Definition: types.h:120
#define RemoveEntryList(Entry)
Definition: env_spec_w32.h:986
RTL_RESOURCE LogonListResource
Definition: msv1_0.c:30
static PLOGON_LIST_ENTRY GetLogonByLogonId(_In_ PLUID LogonId)
Definition: msv1_0.c:37
NTSYSAPI BOOLEAN NTAPI RtlAcquireResourceExclusive(_In_ PRTL_RESOURCE Resource, _In_ BOOLEAN Wait)
NTSYSAPI VOID NTAPI RtlReleaseResource(_In_ PRTL_RESOURCE Resource)
_IRQL_requires_same_ _In_ PLSA_STRING _In_ SECURITY_LOGON_TYPE _In_ ULONG _In_ ULONG _In_opt_ PTOKEN_GROUPS _In_ PTOKEN_SOURCE _Out_ PVOID _Out_ PULONG _Inout_ PLUID LogonId
#define TRACE(s)
Definition: solgame.cpp:4
Definition: msv1_0.c:16
UNICODE_STRING UserName
Definition: msv1_0.c:20
LIST_ENTRY ListEntry
Definition: msv1_0.c:17
UNICODE_STRING LogonServer
Definition: msv1_0.c:22
UNICODE_STRING LogonDomainName
Definition: msv1_0.c:21

◆ LsaApLogonUserEx2()

NTSTATUS NTAPI LsaApLogonUserEx2 ( _In_ PLSA_CLIENT_REQUEST  ClientRequest,
_In_ SECURITY_LOGON_TYPE  LogonType,
_In_ PVOID  ProtocolSubmitBuffer,
_In_ PVOID  ClientBufferBase,
_In_ ULONG  SubmitBufferSize,
_Out_ PVOID *  ProfileBuffer,
_Out_ PULONG  ProfileBufferSize,
_Out_ PLUID  LogonId,
_Out_ PNTSTATUS  SubStatus,
_Out_ PLSA_TOKEN_INFORMATION_TYPE  TokenInformationType,
_Out_ PVOID *  TokenInformation,
_Out_ PUNICODE_STRING *  AccountName,
_Out_ PUNICODE_STRING *  AuthenticatingAuthority,
_Out_ PUNICODE_STRING *  MachineName,
_Out_ PSECPKG_PRIMARY_CRED  PrimaryCredentials,
_Out_ PSECPKG_SUPPLEMENTAL_CRED_ARRAY *  SupplementalCredentials 
)

◆ LsaIFree_LSAPR_POLICY_INFORMATION()

VOID NTAPI LsaIFree_LSAPR_POLICY_INFORMATION ( IN POLICY_INFORMATION_CLASS  InformationClass,
IN PLSAPR_POLICY_INFORMATION  PolicyInformation 
)

Definition at line 51 of file lsasrv.c.

53{
54 if (PolicyInformation != NULL)
55 {
56 switch (InformationClass)
57 {
58 case PolicyAuditLogInformation: /* 1 */
59 break;
60
62 if (PolicyInformation->PolicyAuditEventsInfo.EventAuditingOptions != NULL)
63 midl_user_free(PolicyInformation->PolicyAuditEventsInfo.EventAuditingOptions);
64 break;
65
67 if (PolicyInformation->PolicyPrimaryDomInfo.Name.Buffer != NULL)
68 midl_user_free(PolicyInformation->PolicyPrimaryDomInfo.Name.Buffer);
69
70 if (PolicyInformation->PolicyPrimaryDomInfo.Sid != NULL)
71 midl_user_free(PolicyInformation->PolicyPrimaryDomInfo.Sid);
72 break;
73
74 case PolicyPdAccountInformation: /* 4 */
75 if (PolicyInformation->PolicyPdAccountInfo.Name.Buffer != NULL)
76 midl_user_free(PolicyInformation->PolicyPdAccountInfo.Name.Buffer);
77 break;
78
80 if (PolicyInformation->PolicyAccountDomainInfo.DomainName.Buffer != NULL)
81 midl_user_free(PolicyInformation->PolicyAccountDomainInfo.DomainName.Buffer);
82
83 if (PolicyInformation->PolicyAccountDomainInfo.Sid != NULL)
84 midl_user_free(PolicyInformation->PolicyAccountDomainInfo.Sid);
85 break;
86
88 break;
89
91 if (PolicyInformation->PolicyReplicaSourceInfo.ReplicaSource.Buffer != NULL)
92 midl_user_free(PolicyInformation->PolicyReplicaSourceInfo.ReplicaSource.Buffer);
93
94 if (PolicyInformation->PolicyReplicaSourceInfo.ReplicaAccountName.Buffer != NULL)
95 midl_user_free(PolicyInformation->PolicyReplicaSourceInfo.ReplicaAccountName.Buffer);
96 break;
97
99 break;
100
102 break;
103
104 case PolicyAuditFullSetInformation: /* 10 (0xA) */
105 break;
106
107 case PolicyAuditFullQueryInformation: /* 11 (0xB) */
108 break;
109
110 case PolicyDnsDomainInformation: /* 12 (0xC) */
111 if (PolicyInformation->PolicyDnsDomainInfo.Name.Buffer != NULL)
112 midl_user_free(PolicyInformation->PolicyDnsDomainInfo.Name.Buffer);
113
114 if (PolicyInformation->PolicyDnsDomainInfo.DnsDomainName.Buffer != NULL)
115 midl_user_free(PolicyInformation->PolicyDnsDomainInfo.DnsDomainName.Buffer);
116
117 if (PolicyInformation->PolicyDnsDomainInfo.DnsForestName.Buffer != NULL)
118 midl_user_free(PolicyInformation->PolicyDnsDomainInfo.DnsForestName.Buffer);
119
120 if (PolicyInformation->PolicyDnsDomainInfo.Sid != NULL)
121 midl_user_free(PolicyInformation->PolicyDnsDomainInfo.Sid);
122 break;
123
124 case PolicyDnsDomainInformationInt: /* 13 (0xD) */
125 if (PolicyInformation->PolicyDnsDomainInfoInt.Name.Buffer != NULL)
126 midl_user_free(PolicyInformation->PolicyDnsDomainInfoInt.Name.Buffer);
127
128 if (PolicyInformation->PolicyDnsDomainInfoInt.DnsDomainName.Buffer != NULL)
129 midl_user_free(PolicyInformation->PolicyDnsDomainInfoInt.DnsDomainName.Buffer);
130
131 if (PolicyInformation->PolicyDnsDomainInfoInt.DnsForestName.Buffer != NULL)
132 midl_user_free(PolicyInformation->PolicyDnsDomainInfoInt.DnsForestName.Buffer);
133
134 if (PolicyInformation->PolicyDnsDomainInfoInt.Sid != NULL)
135 midl_user_free(PolicyInformation->PolicyDnsDomainInfoInt.Sid);
136 break;
137
138 case PolicyLocalAccountDomainInformation: /* 14 (0xE) */
139 if (PolicyInformation->PolicyLocalAccountDomainInfo.DomainName.Buffer != NULL)
140 midl_user_free(PolicyInformation->PolicyLocalAccountDomainInfo.DomainName.Buffer);
141
142 if (PolicyInformation->PolicyLocalAccountDomainInfo.Sid != NULL)
143 midl_user_free(PolicyInformation->PolicyLocalAccountDomainInfo.Sid);
144 break;
145
146 default:
147 ERR("Invalid InformationClass: %lu\n", InformationClass);
148 break;
149 }
150
151 midl_user_free(PolicyInformation);
152 }
153}
#define ERR(fmt,...)
Definition: precomp.h:57
_In_ FILTER_INFORMATION_CLASS InformationClass
Definition: fltkernel.h:1713
@ PolicyModificationInformation
Definition: ntsecapi.h:251
@ PolicyAuditEventsInformation
Definition: ntsecapi.h:244
@ PolicyDnsDomainInformationInt
Definition: ntsecapi.h:255
@ PolicyDefaultQuotaInformation
Definition: ntsecapi.h:250
@ PolicyReplicaSourceInformation
Definition: ntsecapi.h:249
@ PolicyLsaServerRoleInformation
Definition: ntsecapi.h:248
@ PolicyAuditFullSetInformation
Definition: ntsecapi.h:252
@ PolicyDnsDomainInformation
Definition: ntsecapi.h:254
@ PolicyPrimaryDomainInformation
Definition: ntsecapi.h:245
@ PolicyAuditLogInformation
Definition: ntsecapi.h:243
@ PolicyAuditFullQueryInformation
Definition: ntsecapi.h:253
@ PolicyLocalAccountDomainInformation
Definition: ntsecapi.h:256
@ PolicyPdAccountInformation
Definition: ntsecapi.h:246
@ PolicyAccountDomainInformation
Definition: ntsecapi.h:247
#define midl_user_free
Definition: rpc.h:41

◆ LsaIOpenPolicyTrusted()

NTSTATUS WINAPI LsaIOpenPolicyTrusted ( OUT LSAPR_HANDLE *  PolicyHandle)

Definition at line 15 of file policy.c.

16{
17 PLSA_DB_OBJECT PolicyObject;
19
20 TRACE("(%p)\n", PolicyHandle);
21
23 NULL,
24 L"Policy",
27 TRUE,
28 &PolicyObject);
29
30 if (NT_SUCCESS(Status))
31 *PolicyHandle = (LSAPR_HANDLE)PolicyObject;
32
33 return Status;
34}
LONG NTSTATUS
Definition: precomp.h:26
#define NT_SUCCESS(StatCode)
Definition: apphelp.c:33
NTSTATUS LsapOpenDbObject(IN PLSA_DB_OBJECT ParentObject, IN LPWSTR ContainerName, IN LPWSTR ObjectName, IN LSA_DB_OBJECT_TYPE ObjectType, IN ACCESS_MASK DesiredAccess, IN BOOLEAN Trusted, OUT PLSA_DB_OBJECT *DbObject)
Definition: database.c:712
@ LsaDbPolicyObject
Definition: lsasrv.h:50
#define L(x)
Definition: resources.c:13
Status
Definition: gdiplustypes.h:24
PVOID LSAPR_HANDLE
Definition: msv1_0.h:229
#define POLICY_ALL_ACCESS
Definition: ntsecapi.h:77

Referenced by GetAccountDomainSid().

◆ LsarClose()

NTSTATUS WINAPI LsarClose ( IN OUT LSAPR_HANDLE *  ObjectHandle)

◆ LsarLookupPrivilegeValue()

NTSTATUS WINAPI LsarLookupPrivilegeValue ( IN LSAPR_HANDLE  PolicyHandle,
IN PRPC_UNICODE_STRING  Name,
OUT PLUID  Value 
)

◆ LsarQueryInformationPolicy()

NTSTATUS WINAPI LsarQueryInformationPolicy ( IN LSAPR_HANDLE  PolicyHandle,
IN POLICY_INFORMATION_CLASS  InformationClass,
OUT PLSAPR_POLICY_INFORMATION *  PolicyInformation 
)

◆ SamIConnect()

NTSTATUS NTAPI SamIConnect ( IN PSAMPR_SERVER_NAME  ServerName,
OUT SAMPR_HANDLE *  ServerHandle,
IN ACCESS_MASK  DesiredAccess,
IN BOOLEAN  Trusted 
)

Definition at line 65 of file samsrv.c.

69{
70 PSAM_DB_OBJECT ServerObject;
72
73 TRACE("SamIConnect(%p %p %lx %ld)\n",
74 ServerName, ServerHandle, DesiredAccess, Trusted);
75
76 /* Map generic access rights */
79
80 /* Open the Server Object */
82 NULL,
83 L"SAM",
84 0,
87 &ServerObject);
88 if (NT_SUCCESS(Status))
89 {
90 ServerObject->Trusted = Trusted;
91 *ServerHandle = (SAMPR_HANDLE)ServerObject;
92 }
93
94 TRACE("SamIConnect done (Status 0x%08lx)\n", Status);
95
96 return Status;
97}
void * SAMPR_HANDLE
Definition: authpackage.c:113
NTSTATUS SampOpenDbObject(IN PSAM_DB_OBJECT ParentObject, IN LPWSTR ContainerName, IN LPWSTR ObjectName, IN ULONG RelativeId, IN SAM_DB_OBJECT_TYPE ObjectType, IN ACCESS_MASK DesiredAccess, OUT PSAM_DB_OBJECT *DbObject)
Definition: database.c:173
@ SamDbServerObject
Definition: samsrv.h:38
NTSYSAPI VOID NTAPI RtlMapGenericMask(PACCESS_MASK AccessMask, PGENERIC_MAPPING GenericMapping)
PGENERIC_MAPPING pServerMapping
Definition: samrpc.c:56
BOOLEAN Trusted
Definition: samsrv.h:55
_Must_inspect_result_ _In_ WDFDEVICE _In_ ULONG _In_ ACCESS_MASK DesiredAccess
Definition: wdfdevice.h:2664

◆ SamIFree_SAMPR_ULONG_ARRAY()

VOID NTAPI SamIFree_SAMPR_ULONG_ARRAY ( PSAMPR_ULONG_ARRAY  Ptr)

Definition at line 524 of file samsrv.c.

525{
526 if (Ptr == NULL)
527 return;
528
529 if (Ptr->Element != NULL)
530 {
531 MIDL_user_free(Ptr->Element);
532 Ptr->Element = NULL;
533 Ptr->Count = 0;
534 }
535}
void __RPC_USER MIDL_user_free(void __RPC_FAR *ptr)
Definition: dhcpcsvc.c:31
_Must_inspect_result_ _In_ PFSRTL_PER_STREAM_CONTEXT Ptr
Definition: fsrtlfuncs.h:898

◆ SamIFree_SAMPR_USER_INFO_BUFFER()

VOID NTAPI SamIFree_SAMPR_USER_INFO_BUFFER ( PSAMPR_USER_INFO_BUFFER  Ptr,
USER_INFORMATION_CLASS  InformationClass 
)

Definition at line 540 of file samsrv.c.

542{
543 if (Ptr == NULL)
544 return;
545
546 switch (InformationClass)
547 {
549 if (Ptr->General.UserName.Buffer != NULL)
550 MIDL_user_free(Ptr->General.UserName.Buffer);
551
552 if (Ptr->General.FullName.Buffer != NULL)
553 MIDL_user_free(Ptr->General.FullName.Buffer);
554
555 if (Ptr->General.AdminComment.Buffer != NULL)
556 MIDL_user_free(Ptr->General.AdminComment.Buffer);
557
558 if (Ptr->General.UserComment.Buffer != NULL)
559 MIDL_user_free(Ptr->General.UserComment.Buffer);
560 break;
561
563 if (Ptr->Preferences.UserComment.Buffer != NULL)
564 MIDL_user_free(Ptr->Preferences.UserComment.Buffer);
565
566 if (Ptr->Preferences.Reserved1.Buffer != NULL)
567 MIDL_user_free(Ptr->Preferences.Reserved1.Buffer);
568 break;
569
571 if (Ptr->Logon.UserName.Buffer != NULL)
572 MIDL_user_free(Ptr->Logon.UserName.Buffer);
573
574 if (Ptr->Logon.FullName.Buffer != NULL)
575 MIDL_user_free(Ptr->Logon.FullName.Buffer);
576
577 if (Ptr->Logon.HomeDirectory.Buffer != NULL)
578 MIDL_user_free(Ptr->Logon.HomeDirectory.Buffer);
579
580 if (Ptr->Logon.HomeDirectoryDrive.Buffer != NULL)
581 MIDL_user_free(Ptr->Logon.HomeDirectoryDrive.Buffer);
582
583 if (Ptr->Logon.ScriptPath.Buffer != NULL)
584 MIDL_user_free(Ptr->Logon.ScriptPath.Buffer);
585
586 if (Ptr->Logon.ProfilePath.Buffer != NULL)
587 MIDL_user_free(Ptr->Logon.ProfilePath.Buffer);
588
589 if (Ptr->Logon.WorkStations.Buffer != NULL)
590 MIDL_user_free(Ptr->Logon.WorkStations.Buffer);
591
592 if (Ptr->Logon.LogonHours.LogonHours != NULL)
593 MIDL_user_free(Ptr->Logon.LogonHours.LogonHours);
594 break;
595
597 if (Ptr->LogonHours.LogonHours.LogonHours != NULL)
598 MIDL_user_free(Ptr->LogonHours.LogonHours.LogonHours);
599 break;
600
602 if (Ptr->Account.UserName.Buffer != NULL)
603 MIDL_user_free(Ptr->Account.UserName.Buffer);
604
605 if (Ptr->Account.FullName.Buffer != NULL)
606 MIDL_user_free(Ptr->Account.FullName.Buffer);
607
608 if (Ptr->Account.HomeDirectory.Buffer != NULL)
609 MIDL_user_free(Ptr->Account.HomeDirectory.Buffer);
610
611 if (Ptr->Account.HomeDirectoryDrive.Buffer != NULL)
612 MIDL_user_free(Ptr->Account.HomeDirectoryDrive.Buffer);
613
614 if (Ptr->Account.ScriptPath.Buffer != NULL)
615 MIDL_user_free(Ptr->Account.ScriptPath.Buffer);
616
617 if (Ptr->Account.ProfilePath.Buffer != NULL)
618 MIDL_user_free(Ptr->Account.ProfilePath.Buffer);
619
620 if (Ptr->Account.AdminComment.Buffer != NULL)
621 MIDL_user_free(Ptr->Account.AdminComment.Buffer);
622
623 if (Ptr->Account.WorkStations.Buffer != NULL)
624 MIDL_user_free(Ptr->Account.WorkStations.Buffer);
625
626 if (Ptr->Account.LogonHours.LogonHours != NULL)
627 MIDL_user_free(Ptr->Account.LogonHours.LogonHours);
628 break;
629
631 if (Ptr->Name.UserName.Buffer != NULL)
632 MIDL_user_free(Ptr->Name.UserName.Buffer);
633
634 if (Ptr->Name.FullName.Buffer != NULL)
635 MIDL_user_free(Ptr->Name.FullName.Buffer);
636 break;
637
639 if (Ptr->AccountName.UserName.Buffer != NULL)
640 MIDL_user_free(Ptr->AccountName.UserName.Buffer);
641 break;
642
644 if (Ptr->FullName.FullName.Buffer != NULL)
645 MIDL_user_free(Ptr->FullName.FullName.Buffer);
646 break;
647
649 break;
650
652 if (Ptr->Home.HomeDirectory.Buffer != NULL)
653 MIDL_user_free(Ptr->Home.HomeDirectory.Buffer);
654
655 if (Ptr->Home.HomeDirectoryDrive.Buffer != NULL)
656 MIDL_user_free(Ptr->Home.HomeDirectoryDrive.Buffer);
657 break;
658
660 if (Ptr->Script.ScriptPath.Buffer != NULL)
661 MIDL_user_free(Ptr->Script.ScriptPath.Buffer);
662 break;
663
665 if (Ptr->Profile.ProfilePath.Buffer != NULL)
666 MIDL_user_free(Ptr->Profile.ProfilePath.Buffer);
667 break;
668
670 if (Ptr->AdminComment.AdminComment.Buffer != NULL)
671 MIDL_user_free(Ptr->AdminComment.AdminComment.Buffer);
672 break;
673
675 if (Ptr->WorkStations.WorkStations.Buffer != NULL)
676 MIDL_user_free(Ptr->WorkStations.WorkStations.Buffer);
677 break;
678
680 ERR("Information class UserSetPasswordInformation cannot be queried!\n");
681 break;
682
684 break;
685
687 break;
688
690 break;
691
693 break;
694
696 if (Ptr->Parameters.Parameters.Buffer != NULL)
697 MIDL_user_free(Ptr->Parameters.Parameters.Buffer);
698 break;
699
701 if (Ptr->All.UserName.Buffer != NULL)
702 MIDL_user_free(Ptr->All.UserName.Buffer);
703
704 if (Ptr->All.FullName.Buffer != NULL)
705 MIDL_user_free(Ptr->All.FullName.Buffer);
706
707 if (Ptr->All.HomeDirectory.Buffer != NULL)
708 MIDL_user_free(Ptr->All.HomeDirectory.Buffer);
709
710 if (Ptr->All.HomeDirectoryDrive.Buffer != NULL)
711 MIDL_user_free(Ptr->All.HomeDirectoryDrive.Buffer);
712
713 if (Ptr->All.ScriptPath.Buffer != NULL)
714 MIDL_user_free(Ptr->All.ScriptPath.Buffer);
715
716 if (Ptr->All.ProfilePath.Buffer != NULL)
717 MIDL_user_free(Ptr->All.ProfilePath.Buffer);
718
719 if (Ptr->All.AdminComment.Buffer != NULL)
720 MIDL_user_free(Ptr->All.AdminComment.Buffer);
721
722 if (Ptr->All.WorkStations.Buffer != NULL)
723 MIDL_user_free(Ptr->All.WorkStations.Buffer);
724
725 if (Ptr->All.UserComment.Buffer != NULL)
726 MIDL_user_free(Ptr->All.UserComment.Buffer);
727
728 if (Ptr->All.Parameters.Buffer != NULL)
729 MIDL_user_free(Ptr->All.Parameters.Buffer);
730
731 if (Ptr->All.LmOwfPassword.Buffer != NULL)
732 MIDL_user_free(Ptr->All.LmOwfPassword.Buffer);
733
734 if (Ptr->All.NtOwfPassword.Buffer != NULL)
735 MIDL_user_free(Ptr->All.NtOwfPassword.Buffer);
736
737 if (Ptr->All.PrivateData.Buffer != NULL)
738 MIDL_user_free(Ptr->All.PrivateData.Buffer);
739
740 if (Ptr->All.SecurityDescriptor.SecurityDescriptor != NULL)
741 MIDL_user_free(Ptr->All.SecurityDescriptor.SecurityDescriptor);
742
743 if (Ptr->All.LogonHours.LogonHours != NULL)
744 MIDL_user_free(Ptr->All.LogonHours.LogonHours);
745 break;
746
747 default:
748 FIXME("Unsupported information class: %lu\n", InformationClass);
749 break;
750 }
751
753}
#define FIXME(fmt,...)
Definition: precomp.h:53
@ UserScriptInformation
Definition: ntsam.h:524
@ UserAccountNameInformation
Definition: ntsam.h:520
@ UserPrimaryGroupInformation
Definition: ntsam.h:522
@ UserAccountInformation
Definition: ntsam.h:518
@ UserInternal1Information
Definition: ntsam.h:531
@ UserParametersInformation
Definition: ntsam.h:533
@ UserWorkStationsInformation
Definition: ntsam.h:527
@ UserNameInformation
Definition: ntsam.h:519
@ UserLogonHoursInformation
Definition: ntsam.h:517
@ UserLogonInformation
Definition: ntsam.h:516
@ UserSetPasswordInformation
Definition: ntsam.h:528
@ UserGeneralInformation
Definition: ntsam.h:514
@ UserFullNameInformation
Definition: ntsam.h:521
@ UserInternal2Information
Definition: ntsam.h:532
@ UserControlInformation
Definition: ntsam.h:529
@ UserAdminCommentInformation
Definition: ntsam.h:526
@ UserProfileInformation
Definition: ntsam.h:525
@ UserAllInformation
Definition: ntsam.h:534
@ UserExpiresInformation
Definition: ntsam.h:530
@ UserPreferencesInformation
Definition: ntsam.h:515
@ UserHomeInformation
Definition: ntsam.h:523

Referenced by LsaApLogonUserEx2(), and SamValidateNormalUser().

◆ SamIFreeVoid()

VOID NTAPI SamIFreeVoid ( PVOID  Ptr)

Definition at line 155 of file samsrv.c.

156{
158}

Referenced by MsvpChangePassword().

◆ SamrChangePasswordUser()

NTSTATUS NTAPI SamrChangePasswordUser ( IN SAMPR_HANDLE  UserHandle,
IN unsigned char  LmPresent,
IN PENCRYPTED_LM_OWF_PASSWORD  OldLmEncryptedWithNewLm,
IN PENCRYPTED_LM_OWF_PASSWORD  NewLmEncryptedWithOldLm,
IN unsigned char  NtPresent,
IN PENCRYPTED_NT_OWF_PASSWORD  OldNtEncryptedWithNewNt,
IN PENCRYPTED_NT_OWF_PASSWORD  NewNtEncryptedWithOldNt,
IN unsigned char  NtCrossEncryptionPresent,
IN PENCRYPTED_NT_OWF_PASSWORD  NewNtEncryptedWithNewLm,
IN unsigned char  LmCrossEncryptionPresent,
IN PENCRYPTED_LM_OWF_PASSWORD  NewLmEncryptedWithNewNt 
)

Definition at line 7868 of file samrpc.c.

7879{
7880 ENCRYPTED_LM_OWF_PASSWORD StoredLmPassword;
7881 ENCRYPTED_NT_OWF_PASSWORD StoredNtPassword;
7882 LM_OWF_PASSWORD OldLmPassword;
7883 LM_OWF_PASSWORD NewLmPassword;
7884 NT_OWF_PASSWORD OldNtPassword;
7885 NT_OWF_PASSWORD NewNtPassword;
7886 BOOLEAN StoredLmPresent = FALSE;
7887 BOOLEAN StoredNtPresent = FALSE;
7888 BOOLEAN StoredLmEmpty = TRUE;
7889 BOOLEAN StoredNtEmpty = TRUE;
7890 PSAM_DB_OBJECT UserObject;
7891 ULONG Length;
7892 SAM_USER_FIXED_DATA UserFixedData;
7893 SAM_DOMAIN_FIXED_DATA DomainFixedData;
7894 LARGE_INTEGER SystemTime;
7896
7897 DBG_UNREFERENCED_LOCAL_VARIABLE(StoredLmPresent);
7898 DBG_UNREFERENCED_LOCAL_VARIABLE(StoredNtPresent);
7899 DBG_UNREFERENCED_LOCAL_VARIABLE(StoredLmEmpty);
7900
7901 TRACE("SamrChangePasswordUser(%p %u %p %p %u %p %p %u %p %u %p)\n",
7902 UserHandle, LmPresent, OldLmEncryptedWithNewLm, NewLmEncryptedWithOldLm,
7903 NtPresent, OldNtEncryptedWithNewNt, NewNtEncryptedWithOldNt, NtCrossEncryptionPresent,
7904 NewNtEncryptedWithNewLm, LmCrossEncryptionPresent, NewLmEncryptedWithNewNt);
7905
7907 TRUE);
7908
7909 /* Validate the user handle */
7910 Status = SampValidateDbObject(UserHandle,
7913 &UserObject);
7914 if (!NT_SUCCESS(Status))
7915 {
7916 TRACE("SampValidateDbObject failed with status 0x%08lx\n", Status);
7917 goto done;
7918 }
7919
7920 /* Get the current time */
7921 Status = NtQuerySystemTime(&SystemTime);
7922 if (!NT_SUCCESS(Status))
7923 {
7924 TRACE("NtQuerySystemTime failed (Status 0x%08lx)\n", Status);
7925 goto done;
7926 }
7927
7928 /* Retrieve the LM password */
7930 Status = SampGetObjectAttribute(UserObject,
7931 L"LMPwd",
7932 NULL,
7933 &StoredLmPassword,
7934 &Length);
7935 if (NT_SUCCESS(Status))
7936 {
7937 if (Length == sizeof(ENCRYPTED_LM_OWF_PASSWORD))
7938 {
7939 StoredLmPresent = TRUE;
7940 if (!RtlEqualMemory(&StoredLmPassword,
7941 &EmptyLmHash,
7943 StoredLmEmpty = FALSE;
7944 }
7945 }
7946
7947 /* Retrieve the NT password */
7949 Status = SampGetObjectAttribute(UserObject,
7950 L"NTPwd",
7951 NULL,
7952 &StoredNtPassword,
7953 &Length);
7954 if (NT_SUCCESS(Status))
7955 {
7956 if (Length == sizeof(ENCRYPTED_NT_OWF_PASSWORD))
7957 {
7958 StoredNtPresent = TRUE;
7959 if (!RtlEqualMemory(&StoredNtPassword,
7960 &EmptyNtHash,
7962 StoredNtEmpty = FALSE;
7963 }
7964 }
7965
7966 /* Retrieve the fixed size user data */
7967 Length = sizeof(SAM_USER_FIXED_DATA);
7968 Status = SampGetObjectAttribute(UserObject,
7969 L"F",
7970 NULL,
7971 &UserFixedData,
7972 &Length);
7973 if (!NT_SUCCESS(Status))
7974 {
7975 TRACE("SampGetObjectAttribute failed to retrieve the fixed user data (Status 0x%08lx)\n", Status);
7976 goto done;
7977 }
7978
7979 /* Check if we can change the password at this time */
7980 if ((StoredLmEmpty == FALSE) || (StoredNtEmpty == FALSE))
7981 {
7982 /* Get fixed domain data */
7983 Length = sizeof(SAM_DOMAIN_FIXED_DATA);
7985 L"F",
7986 NULL,
7987 &DomainFixedData,
7988 &Length);
7989 if (!NT_SUCCESS(Status))
7990 {
7991 TRACE("SampGetObjectAttribute failed to retrieve the fixed domain data (Status 0x%08lx)\n", Status);
7992 goto done;
7993 }
7994
7995 if (DomainFixedData.MinPasswordAge.QuadPart > 0)
7996 {
7997 if (SystemTime.QuadPart < (UserFixedData.PasswordLastSet.QuadPart + DomainFixedData.MinPasswordAge.QuadPart))
7998 {
8000 goto done;
8001 }
8002 }
8003 }
8004
8005 /* Decrypt the LM passwords, if present */
8006 if (LmPresent)
8007 {
8008 Status = SystemFunction013((const BYTE *)NewLmEncryptedWithOldLm,
8009 (const BYTE *)&StoredLmPassword,
8010 (LPBYTE)&NewLmPassword);
8011 if (!NT_SUCCESS(Status))
8012 {
8013 TRACE("SystemFunction013 failed (Status 0x%08lx)\n", Status);
8014 goto done;
8015 }
8016
8017 Status = SystemFunction013((const BYTE *)OldLmEncryptedWithNewLm,
8018 (const BYTE *)&NewLmPassword,
8019 (LPBYTE)&OldLmPassword);
8020 if (!NT_SUCCESS(Status))
8021 {
8022 TRACE("SystemFunction013 failed (Status 0x%08lx)\n", Status);
8023 goto done;
8024 }
8025 }
8026
8027 /* Decrypt the NT passwords, if present */
8028 if (NtPresent)
8029 {
8030 Status = SystemFunction013((const BYTE *)NewNtEncryptedWithOldNt,
8031 (const BYTE *)&StoredNtPassword,
8032 (LPBYTE)&NewNtPassword);
8033 if (!NT_SUCCESS(Status))
8034 {
8035 TRACE("SystemFunction013 failed (Status 0x%08lx)\n", Status);
8036 goto done;
8037 }
8038
8039 Status = SystemFunction013((const BYTE *)OldNtEncryptedWithNewNt,
8040 (const BYTE *)&NewNtPassword,
8041 (LPBYTE)&OldNtPassword);
8042 if (!NT_SUCCESS(Status))
8043 {
8044 TRACE("SystemFunction013 failed (Status 0x%08lx)\n", Status);
8045 goto done;
8046 }
8047 }
8048
8049 /* Check if the old passwords match the stored ones */
8050 if (NtPresent)
8051 {
8052 if (LmPresent)
8053 {
8054 if (!RtlEqualMemory(&StoredLmPassword,
8055 &OldLmPassword,
8057 {
8058 TRACE("Old LM Password does not match!\n");
8060 }
8061 else
8062 {
8063 if (!RtlEqualMemory(&StoredNtPassword,
8064 &OldNtPassword,
8066 {
8067 TRACE("Old NT Password does not match!\n");
8069 }
8070 }
8071 }
8072 else
8073 {
8074 if (!RtlEqualMemory(&StoredNtPassword,
8075 &OldNtPassword,
8077 {
8078 TRACE("Old NT Password does not match!\n");
8080 }
8081 }
8082 }
8083 else
8084 {
8085 if (LmPresent)
8086 {
8087 if (!RtlEqualMemory(&StoredLmPassword,
8088 &OldLmPassword,
8090 {
8091 TRACE("Old LM Password does not match!\n");
8093 }
8094 }
8095 else
8096 {
8098 }
8099 }
8100
8101 /* Store the new password hashes */
8102 if (NT_SUCCESS(Status))
8103 {
8104 Status = SampSetUserPassword(UserObject,
8105 &NewNtPassword,
8106 NtPresent,
8107 &NewLmPassword,
8108 LmPresent);
8109 if (NT_SUCCESS(Status))
8110 {
8111 /* Update PasswordLastSet */
8112 UserFixedData.PasswordLastSet.QuadPart = SystemTime.QuadPart;
8113
8114 /* Set the fixed size user data */
8115 Length = sizeof(SAM_USER_FIXED_DATA);
8116 Status = SampSetObjectAttribute(UserObject,
8117 L"F",
8118 REG_BINARY,
8119 &UserFixedData,
8120 Length);
8121 }
8122 }
8123
8125 {
8126 /* Update BadPasswordCount and LastBadPasswordTime */
8127 UserFixedData.BadPasswordCount++;
8128 UserFixedData.LastBadPasswordTime.QuadPart = SystemTime.QuadPart;
8129
8130 /* Set the fixed size user data */
8131 Length = sizeof(SAM_USER_FIXED_DATA);
8132 Status = SampSetObjectAttribute(UserObject,
8133 L"F",
8134 REG_BINARY,
8135 &UserFixedData,
8136 Length);
8137 }
8138
8139done:
8141
8142 return Status;
8143}
unsigned char BOOLEAN
Definition: actypes.h:127
#define FALSE
Definition: types.h:117
NTSTATUS SampGetObjectAttribute(PSAM_DB_OBJECT DbObject, LPWSTR AttributeName, PULONG AttributeType, LPVOID AttributeData, PULONG AttributeSize)
Definition: database.c:516
NTSTATUS SampSetObjectAttribute(PSAM_DB_OBJECT DbObject, LPWSTR AttributeName, ULONG AttributeType, LPVOID AttributeData, ULONG AttributeSize)
Definition: database.c:501
NTSTATUS SampValidateDbObject(SAMPR_HANDLE Handle, SAM_DB_OBJECT_TYPE ObjectType, ACCESS_MASK DesiredAccess, PSAM_DB_OBJECT *DbObject)
Definition: database.c:301
struct _SAM_DOMAIN_FIXED_DATA SAM_DOMAIN_FIXED_DATA
struct _SAM_USER_FIXED_DATA SAM_USER_FIXED_DATA
NTSTATUS SampSetUserPassword(IN PSAM_DB_OBJECT UserObject, IN PENCRYPTED_NT_OWF_PASSWORD NtPassword, IN BOOLEAN NtPasswordPresent, IN PENCRYPTED_LM_OWF_PASSWORD LmPassword, IN BOOLEAN LmPasswordPresent)
Definition: user.c:590
@ SamDbUserObject
Definition: samsrv.h:42
#define RtlEqualMemory(dst, src, len)
Definition: kdvm.h:18
struct _ENCRYPTED_LM_OWF_PASSWORD ENCRYPTED_NT_OWF_PASSWORD
struct _ENCRYPTED_LM_OWF_PASSWORD ENCRYPTED_LM_OWF_PASSWORD
#define REG_BINARY
Definition: nt_native.h:1499
#define DBG_UNREFERENCED_LOCAL_VARIABLE(L)
Definition: ntbasedef.h:331
_In_ ULONG _In_ ULONG _In_ ULONG Length
Definition: ntddpcm.h:102
NTSTATUS NTAPI NtQuerySystemTime(OUT PLARGE_INTEGER SystemTime)
Definition: time.c:563
#define USER_CHANGE_PASSWORD
Definition: ntsam.h:132
#define STATUS_WRONG_PASSWORD
Definition: ntstatus.h:436
#define STATUS_ACCOUNT_RESTRICTION
Definition: ntstatus.h:440
RTL_RESOURCE SampResource
Definition: samsrv.c:28
ENCRYPTED_LM_OWF_PASSWORD EmptyLmHash
Definition: samsrv.c:27
ENCRYPTED_NT_OWF_PASSWORD EmptyNtHash
Definition: samsrv.c:26
struct _SAM_DB_OBJECT * ParentObject
Definition: samsrv.h:56
LARGE_INTEGER MinPasswordAge
Definition: samsrv.h:75
LARGE_INTEGER LastBadPasswordTime
Definition: samsrv.h:106
LARGE_INTEGER PasswordLastSet
Definition: samsrv.h:104
USHORT BadPasswordCount
Definition: samsrv.h:112
NTSTATUS WINAPI SystemFunction013(const BYTE *in, const BYTE *key, LPBYTE out)
Definition: sysfunc.c:383
unsigned char * LPBYTE
Definition: typedefs.h:53
uint32_t ULONG
Definition: typedefs.h:59
#define STATUS_INVALID_PARAMETER
Definition: udferr_usr.h:135
LONGLONG QuadPart
Definition: typedefs.h:114
unsigned char BYTE
Definition: xxhash.c:193

Referenced by MsvpChangePassword(), and SamChangePasswordUser().

◆ SamrCloseHandle()

NTSTATUS NTAPI SamrCloseHandle ( IN OUT SAMPR_HANDLE *  SamHandle)

Definition at line 161 of file samrpc.c.

162{
163 PSAM_DB_OBJECT DbObject;
165
166 TRACE("SamrCloseHandle(%p)\n", SamHandle);
167
169 TRUE);
170
171 Status = SampValidateDbObject(*SamHandle,
173 0,
174 &DbObject);
175 if (Status == STATUS_SUCCESS)
176 {
177 Status = SampCloseDbObject(DbObject);
178 *SamHandle = NULL;
179 }
180
182
183 TRACE("SamrCloseHandle done (Status 0x%08lx)\n", Status);
184
185 return Status;
186}
NTSTATUS SampCloseDbObject(PSAM_DB_OBJECT DbObject)
Definition: database.c:346
@ SamDbIgnoreObject
Definition: samsrv.h:37
NTSYSAPI BOOLEAN NTAPI RtlAcquireResourceShared(_In_ PRTL_RESOURCE Resource, _In_ BOOLEAN Wait)
#define STATUS_SUCCESS
Definition: shellext.h:65

Referenced by SamrGetDomainPasswordInformation().

◆ SamrLookupDomainInSamServer()

NTSTATUS NTAPI SamrLookupDomainInSamServer ( IN SAMPR_HANDLE  ServerHandle,
IN PRPC_UNICODE_STRING  Name,
OUT PRPC_SID *  DomainId 
)

Definition at line 504 of file samrpc.c.

507{
508 PSAM_DB_OBJECT ServerObject;
509 HANDLE DomainsKeyHandle = NULL;
510 HANDLE DomainKeyHandle = NULL;
511 WCHAR DomainKeyName[64];
512 ULONG Index;
513 WCHAR DomainNameString[MAX_COMPUTERNAME_LENGTH + 1];
514 UNICODE_STRING DomainName;
516 BOOL Found = FALSE;
518
519 TRACE("SamrLookupDomainInSamServer(%p %p %p)\n",
520 ServerHandle, Name, DomainId);
521
523 TRUE);
524
525 /* Validate the server handle */
526 Status = SampValidateDbObject(ServerHandle,
529 &ServerObject);
530 if (!NT_SUCCESS(Status))
531 goto done;
532
533 *DomainId = NULL;
534
535 Status = SampRegOpenKey(ServerObject->KeyHandle,
536 L"Domains",
537 KEY_READ,
538 &DomainsKeyHandle);
539 if (!NT_SUCCESS(Status))
540 goto done;
541
542 Index = 0;
543 while (Found == FALSE)
544 {
545 Status = SampRegEnumerateSubKey(DomainsKeyHandle,
546 Index,
547 64,
548 DomainKeyName);
549 if (!NT_SUCCESS(Status))
550 {
553 break;
554 }
555
556 TRACE("Domain key name: %S\n", DomainKeyName);
557
558 Status = SampRegOpenKey(DomainsKeyHandle,
559 DomainKeyName,
560 KEY_READ,
561 &DomainKeyHandle);
562 if (NT_SUCCESS(Status))
563 {
564 Length = (MAX_COMPUTERNAME_LENGTH + 1) * sizeof(WCHAR);
565 Status = SampRegQueryValue(DomainKeyHandle,
566 L"Name",
567 NULL,
568 (PVOID)&DomainNameString,
569 &Length);
570 if (NT_SUCCESS(Status))
571 {
572 TRACE("Domain name: %S\n", DomainNameString);
573
574 RtlInitUnicodeString(&DomainName,
575 DomainNameString);
577 {
578 TRACE("Found it!\n");
579 Found = TRUE;
580
581 Status = SampRegQueryValue(DomainKeyHandle,
582 L"SID",
583 NULL,
584 NULL,
585 &Length);
586 if (NT_SUCCESS(Status))
587 {
588 *DomainId = midl_user_allocate(Length);
589
590 SampRegQueryValue(DomainKeyHandle,
591 L"SID",
592 NULL,
593 (PVOID)*DomainId,
594 &Length);
595
597 break;
598 }
599 }
600 }
601
602 SampRegCloseKey(&DomainKeyHandle);
603 }
604
605 Index++;
606 }
607
608done:
609 SampRegCloseKey(&DomainKeyHandle);
610 SampRegCloseKey(&DomainsKeyHandle);
611
613
614 return Status;
615}
return Found
Definition: dirsup.c:1270
LPWSTR Name
Definition: desk.c:124
NTSTATUS SampRegQueryValue(IN HANDLE KeyHandle, IN LPCWSTR ValueName, OUT PULONG Type OPTIONAL, OUT PVOID Data OPTIONAL, IN OUT PULONG DataLength OPTIONAL)
Definition: registry.c:332
NTSTATUS SampRegCloseKey(IN OUT PHANDLE KeyHandle)
Definition: registry.c:26
NTSTATUS SampRegOpenKey(IN HANDLE ParentKeyHandle, IN LPCWSTR KeyName, IN ACCESS_MASK DesiredAccess, OUT PHANDLE KeyHandle)
Definition: registry.c:158
NTSTATUS SampRegEnumerateSubKey(IN HANDLE KeyHandle, IN ULONG Index, IN ULONG Length, OUT LPWSTR Buffer)
Definition: registry.c:101
unsigned int BOOL
Definition: ntddk_ex.h:94
#define KEY_READ
Definition: nt_native.h:1026
NTSYSAPI VOID NTAPI RtlInitUnicodeString(PUNICODE_STRING DestinationString, PCWSTR SourceString)
NTSYSAPI BOOLEAN NTAPI RtlEqualUnicodeString(PUNICODE_STRING String1, PUNICODE_STRING String2, BOOLEAN CaseInSensitive)
#define SAM_SERVER_LOOKUP_DOMAIN
Definition: ntsam.h:104
#define STATUS_NO_SUCH_DOMAIN
Definition: ntstatus.h:553
#define STATUS_NO_MORE_ENTRIES
Definition: ntstatus.h:285
short WCHAR
Definition: pedump.c:58
#define midl_user_allocate
Definition: rpc.h:40
HANDLE KeyHandle
Definition: samsrv.h:52
_In_ WDFCOLLECTION _In_ ULONG Index
#define MAX_COMPUTERNAME_LENGTH
Definition: winbase.h:268

Referenced by MsvpChangePassword(), and SamLookupDomainInSamServer().

◆ SamrLookupNamesInDomain()

NTSTATUS NTAPI SamrLookupNamesInDomain ( IN SAMPR_HANDLE  DomainHandle,
IN ULONG  Count,
IN RPC_UNICODE_STRING  Names[],
OUT PSAMPR_ULONG_ARRAY  RelativeIds,
OUT PSAMPR_ULONG_ARRAY  Use 
)

Definition at line 3468 of file samrpc.c.

3473{
3474 PSAM_DB_OBJECT DomainObject;
3475 HANDLE AccountsKeyHandle = NULL;
3476 HANDLE NamesKeyHandle = NULL;
3477 ULONG MappedCount = 0;
3479 ULONG i;
3480 ULONG RelativeId;
3482
3483 TRACE("SamrLookupNamesInDomain(%p %lu %p %p %p)\n",
3484 DomainHandle, Count, Names, RelativeIds, Use);
3485
3487 TRUE);
3488
3489 /* Validate the domain handle */
3490 Status = SampValidateDbObject(DomainHandle,
3493 &DomainObject);
3494 if (!NT_SUCCESS(Status))
3495 {
3496 TRACE("failed with status 0x%08lx\n", Status);
3497 goto done;
3498 }
3499
3500 RelativeIds->Count = 0;
3501 Use->Count = 0;
3502
3503 if (Count == 0)
3504 {
3506 goto done;
3507 }
3508
3509 /* Allocate the relative IDs array */
3510 RelativeIds->Element = midl_user_allocate(Count * sizeof(ULONG));
3511 if (RelativeIds->Element == NULL)
3512 {
3514 goto done;
3515 }
3516
3517 /* Allocate the use array */
3518 Use->Element = midl_user_allocate(Count * sizeof(ULONG));
3519 if (Use->Element == NULL)
3520 {
3522 goto done;
3523 }
3524
3525 RelativeIds->Count = Count;
3526 Use->Count = Count;
3527
3528 for (i = 0; i < Count; i++)
3529 {
3530 TRACE("Name: %S\n", Names[i].Buffer);
3531
3532 RelativeId = 0;
3533
3534 /* Lookup aliases */
3535 Status = SampRegOpenKey(DomainObject->KeyHandle,
3536 L"Aliases",
3537 KEY_READ,
3538 &AccountsKeyHandle);
3539 if (NT_SUCCESS(Status))
3540 {
3541 Status = SampRegOpenKey(AccountsKeyHandle,
3542 L"Names",
3543 KEY_READ,
3544 &NamesKeyHandle);
3545 if (NT_SUCCESS(Status))
3546 {
3547 DataLength = sizeof(ULONG);
3548 Status = SampRegQueryValue(NamesKeyHandle,
3549 Names[i].Buffer,
3550 NULL,
3551 &RelativeId,
3552 &DataLength);
3553
3554 SampRegCloseKey(&NamesKeyHandle);
3555 }
3556
3557 SampRegCloseKey(&AccountsKeyHandle);
3558 }
3559
3561 break;
3562
3563 /* Return alias account */
3564 if (NT_SUCCESS(Status) && RelativeId != 0)
3565 {
3566 TRACE("Rid: %lu\n", RelativeId);
3567 RelativeIds->Element[i] = RelativeId;
3568 Use->Element[i] = SidTypeAlias;
3569 MappedCount++;
3570 continue;
3571 }
3572
3573 /* Lookup groups */
3574 Status = SampRegOpenKey(DomainObject->KeyHandle,
3575 L"Groups",
3576 KEY_READ,
3577 &AccountsKeyHandle);
3578 if (NT_SUCCESS(Status))
3579 {
3580 Status = SampRegOpenKey(AccountsKeyHandle,
3581 L"Names",
3582 KEY_READ,
3583 &NamesKeyHandle);
3584 if (NT_SUCCESS(Status))
3585 {
3586 DataLength = sizeof(ULONG);
3587 Status = SampRegQueryValue(NamesKeyHandle,
3588 Names[i].Buffer,
3589 NULL,
3590 &RelativeId,
3591 &DataLength);
3592
3593 SampRegCloseKey(&NamesKeyHandle);
3594 }
3595
3596 SampRegCloseKey(&AccountsKeyHandle);
3597 }
3598
3600 break;
3601
3602 /* Return group account */
3603 if (NT_SUCCESS(Status) && RelativeId != 0)
3604 {
3605 TRACE("Rid: %lu\n", RelativeId);
3606 RelativeIds->Element[i] = RelativeId;
3607 Use->Element[i] = SidTypeGroup;
3608 MappedCount++;
3609 continue;
3610 }
3611
3612 /* Lookup users */
3613 Status = SampRegOpenKey(DomainObject->KeyHandle,
3614 L"Users",
3615 KEY_READ,
3616 &AccountsKeyHandle);
3617 if (NT_SUCCESS(Status))
3618 {
3619 Status = SampRegOpenKey(AccountsKeyHandle,
3620 L"Names",
3621 KEY_READ,
3622 &NamesKeyHandle);
3623 if (NT_SUCCESS(Status))
3624 {
3625 DataLength = sizeof(ULONG);
3626 Status = SampRegQueryValue(NamesKeyHandle,
3627 Names[i].Buffer,
3628 NULL,
3629 &RelativeId,
3630 &DataLength);
3631
3632 SampRegCloseKey(&NamesKeyHandle);
3633 }
3634
3635 SampRegCloseKey(&AccountsKeyHandle);
3636 }
3637
3639 break;
3640
3641 /* Return user account */
3642 if (NT_SUCCESS(Status) && RelativeId != 0)
3643 {
3644 TRACE("Rid: %lu\n", RelativeId);
3645 RelativeIds->Element[i] = RelativeId;
3646 Use->Element[i] = SidTypeUser;
3647 MappedCount++;
3648 continue;
3649 }
3650
3651 /* Return unknown account */
3652 RelativeIds->Element[i] = 0;
3653 Use->Element[i] = SidTypeUnknown;
3654 }
3655
3656done:
3659
3660 if (NT_SUCCESS(Status))
3661 {
3662 if (MappedCount == 0)
3664 else if (MappedCount < Count)
3666 }
3667 else
3668 {
3669 if (RelativeIds->Element != NULL)
3670 {
3671 midl_user_free(RelativeIds->Element);
3672 RelativeIds->Element = NULL;
3673 }
3674
3675 RelativeIds->Count = 0;
3676
3677 if (Use->Element != NULL)
3678 {
3679 midl_user_free(Use->Element);
3680 Use->Element = NULL;
3681 }
3682
3683 Use->Count = 0;
3684 }
3685
3687
3688 TRACE("Returned Status %lx\n", Status);
3689
3690 return Status;
3691}
PWSTR Names[]
Definition: bufpool.h:45
_In_ D3DDDI_VIDEO_PRESENT_TARGET_ID _In_ ULONG _In_ ULONG DataLength
Definition: dispmprt.h:233
@ SamDbDomainObject
Definition: samsrv.h:39
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble const GLfloat const GLdouble const GLfloat GLint i
Definition: glfuncs.h:248
@ SidTypeUnknown
Definition: lsa.idl:125
@ SidTypeAlias
Definition: lsa.idl:121
@ SidTypeGroup
Definition: lsa.idl:119
@ SidTypeUser
Definition: lsa.idl:118
#define DOMAIN_LOOKUP
Definition: ntsam.h:42
#define STATUS_NONE_MAPPED
Definition: ntstatus.h:445
#define STATUS_SOME_NOT_MAPPED
Definition: ntstatus.h:139
#define STATUS_INSUFFICIENT_RESOURCES
Definition: udferr_usr.h:158
#define STATUS_OBJECT_NAME_NOT_FOUND
Definition: udferr_usr.h:149
USHORT Count
Definition: userreq.cpp:200

◆ SamrOpenDomain()

NTSTATUS NTAPI SamrOpenDomain ( IN SAMPR_HANDLE  ServerHandle,
IN ACCESS_MASK  DesiredAccess,
IN PRPC_SID  DomainId,
OUT SAMPR_HANDLE *  DomainHandle 
)

Definition at line 831 of file samrpc.c.

835{
836 PSAM_DB_OBJECT ServerObject;
837 PSAM_DB_OBJECT DomainObject;
839
840 TRACE("SamrOpenDomain(%p %lx %p %p)\n",
841 ServerHandle, DesiredAccess, DomainId, DomainHandle);
842
843 /* Map generic access rights */
846
848 TRUE);
849
850 /* Validate the server handle */
851 Status = SampValidateDbObject(ServerHandle,
854 &ServerObject);
855 if (!NT_SUCCESS(Status))
856 goto done;
857
858 /* Validate the Domain SID */
859 if ((DomainId->Revision != SID_REVISION) ||
860 (DomainId->SubAuthorityCount > SID_MAX_SUB_AUTHORITIES) ||
861 (memcmp(&DomainId->IdentifierAuthority, &NtSidAuthority, sizeof(SID_IDENTIFIER_AUTHORITY)) != 0))
862 {
864 goto done;
865 }
866
867 /* Open the domain object */
868 if ((DomainId->SubAuthorityCount == 1) &&
869 (DomainId->SubAuthority[0] == SECURITY_BUILTIN_DOMAIN_RID))
870 {
871 /* Builtin domain object */
872 TRACE("Opening the builtin domain object.\n");
873
874 Status = SampOpenDbObject(ServerObject,
875 L"Domains",
876 L"Builtin",
877 0,
880 &DomainObject);
881 }
882 else if ((DomainId->SubAuthorityCount == 4) &&
883 (DomainId->SubAuthority[0] == SECURITY_NT_NON_UNIQUE))
884 {
885 /* Account domain object */
886 TRACE("Opening the account domain object.\n");
887
888 /* FIXME: Check the account domain sub authorities!!! */
889
890 Status = SampOpenDbObject(ServerObject,
891 L"Domains",
892 L"Account",
893 0,
896 &DomainObject);
897 }
898 else
899 {
900 /* No valid domain SID */
902 }
903
904 if (NT_SUCCESS(Status))
905 *DomainHandle = (SAMPR_HANDLE)DomainObject;
906
907done:
909
910 TRACE("SamrOpenDomain done (Status 0x%08lx)\n", Status);
911
912 return Status;
913}
_ACRTIMP int __cdecl memcmp(const void *, const void *, size_t)
Definition: string.c:2807
static SID_IDENTIFIER_AUTHORITY NtSidAuthority
Definition: samrpc.c:14
static GENERIC_MAPPING DomainMapping
Definition: samrpc.c:24
#define SECURITY_BUILTIN_DOMAIN_RID
Definition: setypes.h:581
#define SID_MAX_SUB_AUTHORITIES
Definition: setypes.h:482
#define SID_REVISION
Definition: setypes.h:481
#define SECURITY_NT_NON_UNIQUE
Definition: setypes.h:577

◆ SamrOpenUser()

NTSTATUS NTAPI SamrOpenUser ( IN SAMPR_HANDLE  DomainHandle,
IN ACCESS_MASK  DesiredAccess,
IN ULONG  UserId,
OUT SAMPR_HANDLE *  UserHandle 
)

◆ SamrQueryInformationUser()

NTSTATUS NTAPI SamrQueryInformationUser ( IN SAMPR_HANDLE  UserHandle,
IN USER_INFORMATION_CLASS  UserInformationClass,
OUT PSAMPR_USER_INFO_BUFFER *  Buffer 
)

Definition at line 7238 of file samrpc.c.

7241{
7242 TRACE("SamrQueryInformationUser(%p %lu %p)\n",
7243 UserHandle, UserInformationClass, Buffer);
7244
7245 return SamrQueryInformationUser2(UserHandle,
7246 UserInformationClass,
7247 Buffer);
7248}
NTSTATUS NTAPI SamrQueryInformationUser2(IN SAMPR_HANDLE UserHandle, IN USER_INFORMATION_CLASS UserInformationClass, OUT PSAMPR_USER_INFO_BUFFER *Buffer)
Definition: samrpc.c:8591

Referenced by SamQueryInformationUser(), and SamValidateNormalUser().

◆ SamrSetInformationUser()

NTSTATUS NTAPI SamrSetInformationUser ( IN SAMPR_HANDLE  UserHandle,
IN USER_INFORMATION_CLASS  UserInformationClass,
IN PSAMPR_USER_INFO_BUFFER  Buffer 
)

Definition at line 7852 of file samrpc.c.

7855{
7856 TRACE("SamrSetInformationUser(%p %lu %p)\n",
7857 UserHandle, UserInformationClass, Buffer);
7858
7859 return SamrSetInformationUser2(UserHandle,
7860 UserInformationClass,
7861 Buffer);
7862}
NTSTATUS NTAPI SamrSetInformationUser2(IN SAMPR_HANDLE UserHandle, IN USER_INFORMATION_CLASS UserInformationClass, IN PSAMPR_USER_INFO_BUFFER Buffer)
Definition: samrpc.c:9472

Referenced by LsaApLogonUserEx2(), and SamSetInformationUser().

◆ SystemFunction006()

NTSTATUS WINAPI SystemFunction006 ( LPCSTR  password,
LPSTR  hash 
)

Definition at line 53 of file crypt_lmhash.c.

54{
55 CRYPT_LMhash( (unsigned char*)hash, (const unsigned char*)password, strlen(password) );
56
57 return STATUS_SUCCESS;
58}
static UCHAR password[]
Definition: bcrypt.c:494
static void CRYPT_LMhash(unsigned char *dst, const unsigned char *pwd, const int len)
Definition: crypt_lmhash.c:39
_ACRTIMP size_t __cdecl strlen(const char *)
Definition: string.c:1597

◆ SystemFunction007()

NTSTATUS WINAPI SystemFunction007 ( PUNICODE_STRING  string,
LPBYTE  hash 
)

◆ SystemFunction012()

NTSTATUS WINAPI SystemFunction012 ( const BYTE *  in,
const BYTE *  key,
LPBYTE  out 
)

Definition at line 353 of file sysfunc.c.

354{
355 if (!in || !out)
356 return STATUS_UNSUCCESSFUL;
357
359 CRYPT_DEShash(out+8, key+7, in+8);
360 return STATUS_SUCCESS;
361}
unsigned char * CRYPT_DEShash(unsigned char *dst, const unsigned char *key, const unsigned char *src) DECLSPEC_HIDDEN
Definition: crypt_des.c:259
GLuint in
Definition: glext.h:9616
Definition: copy.c:22
#define STATUS_UNSUCCESSFUL
Definition: udferr_usr.h:132
wchar_t tm const _CrtWcstime_Writes_and_advances_ptr_ count wchar_t ** out
Definition: wcsftime.cpp:383