ReactOS 0.4.17-dev-1133-gc25e4fd
tomcrypt.h File Reference
#include <stdio.h>
#include <string.h>
#include <stdlib.h>
#include <basetsd.h>
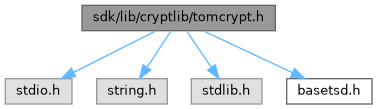
Include dependency graph for tomcrypt.h:
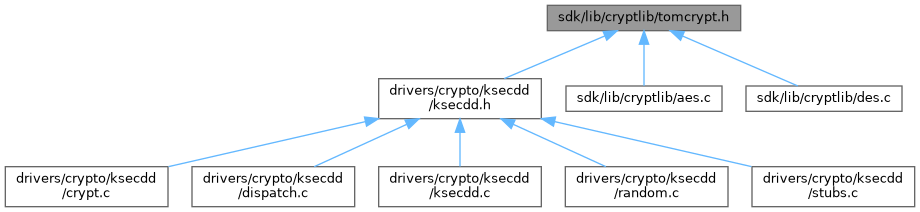
This graph shows which files directly or indirectly include this file:

Go to the source code of this file.

Classes

struct  tag_rc2_key
 
struct  tag_des_key
 
struct  tag_des3_key
 
struct  tag_aes_key
 
struct  tag_md2_state
 
struct  rc4_prng
 
union  Prng_state
 
struct  mp_int
 
struct  Rsa_key
 

Macros

#define CONST64(a, b)   ((((ULONG64)(a)) << 32) | (b))
 
#define STORE32H(x, y)
 
#define LOAD32H(x, y)
 
#define ROR(x, y)
 
#define MIN(x, y)   ( ((x)<(y))?(x):(y) )
 
#define byte(x, n)   (((x) >> (8 * (n))) & 255)
 
#define DIGIT_BIT   28
 
#define MP_DIGIT_BIT   DIGIT_BIT
 
#define MP_MASK   ((((mp_digit)1)<<((mp_digit)DIGIT_BIT))-((mp_digit)1))
 
#define MP_DIGIT_MAX   MP_MASK
 
#define MP_LT   -1 /* less than */
 
#define MP_EQ   0 /* equal to */
 
#define MP_GT   1 /* greater than */
 
#define MP_ZPOS   0 /* positive integer */
 
#define MP_NEG   1 /* negative */
 
#define MP_OKAY   0 /* ok result */
 
#define MP_MEM   -2 /* out of mem */
 
#define MP_VAL   -3 /* invalid input */
 
#define MP_RANGE   MP_VAL
 
#define MP_YES   1 /* yes response */
 
#define MP_NO   0 /* no response */
 
#define LTM_PRIME_BBS   0x0001 /* BBS style prime */
 
#define LTM_PRIME_SAFE   0x0002 /* Safe prime (p-1)/2 == prime */
 
#define LTM_PRIME_2MSB_OFF   0x0004 /* force 2nd MSB to 0 */
 
#define LTM_PRIME_2MSB_ON   0x0008 /* force 2nd MSB to 1 */
 
#define MP_PREC   64 /* default digits of precision */
 
#define MP_WARRAY   (1 << (sizeof(mp_word) * CHAR_BIT - 2 * DIGIT_BIT + 1))
 
#define DIGIT(m, k)   ((m)->dp[(k)])
 
#define mp_iszero(a)   (((a)->used == 0) ? MP_YES : MP_NO)
 
#define mp_iseven(a)   (((a)->used > 0 && (((a)->dp[0] & 1) == 0)) ? MP_YES : MP_NO)
 
#define mp_isodd(a)   (((a)->used > 0 && (((a)->dp[0] & 1) == 1)) ? MP_YES : MP_NO)
 
#define PRIME_SIZE   256
 
#define mp_prime_random(a, t, size, bbs, cb, dat)   mp_prime_random_ex(a, t, ((size) * 8) + 1, (bbs==1)?LTM_PRIME_BBS:0, cb, dat)
 
#define mp_read_raw(mp, str, len)   mp_read_signed_bin((mp), (str), (len))
 
#define mp_raw_size(mp)   mp_signed_bin_size(mp)
 
#define mp_toraw(mp, str)   mp_to_signed_bin((mp), (str))
 
#define mp_read_mag(mp, str, len)   mp_read_unsigned_bin((mp), (str), (len))
 
#define mp_mag_size(mp)   mp_unsigned_bin_size(mp)
 
#define mp_tomag(mp, str)   mp_to_unsigned_bin((mp), (str))
 
#define mp_tobinary(M, S)   mp_toradix((M), (S), 2)
 
#define mp_tooctal(M, S)   mp_toradix((M), (S), 8)
 
#define mp_todecimal(M, S)   mp_toradix((M), (S), 10)
 
#define mp_tohex(M, S)   mp_toradix((M), (S), 16)
 
#define PK_PRIVATE   0 /* PK private keys */
 
#define PK_PUBLIC   1 /* PK public keys */
 
#define MIN_RSA_SIZE   384
 
#define MAX_RSA_SIZE   16384
 

Typedefs

typedef ULONG64 ulong64
 
typedef ULONG32 ulong32
 
typedef struct tag_rc2_key rc2_key
 
typedef struct tag_des_key des_key
 
typedef struct tag_des3_key des3_key
 
typedef struct tag_aes_key aes_key
 
typedef struct tag_md2_state md2_state
 
typedef union Prng_state prng_state
 
typedef unsigned long mp_digit
 
typedef ulong64 mp_word
 
typedef int mp_err
 
typedef int ltm_prime_callback(unsigned char *dst, int len, void *dat)
 
typedef struct Rsa_key rsa_key
 

Enumerations

enum  {
  CRYPT_OK =0 , CRYPT_ERROR , CRYPT_NOP , CRYPT_INVALID_KEYSIZE ,
  CRYPT_INVALID_ROUNDS , CRYPT_FAIL_TESTVECTOR , CRYPT_BUFFER_OVERFLOW , CRYPT_INVALID_PACKET ,
  CRYPT_INVALID_PRNGSIZE , CRYPT_ERROR_READPRNG , CRYPT_INVALID_CIPHER , CRYPT_INVALID_HASH ,
  CRYPT_INVALID_PRNG , CRYPT_MEM , CRYPT_PK_TYPE_MISMATCH , CRYPT_PK_NOT_PRIVATE ,
  CRYPT_INVALID_ARG , CRYPT_FILE_NOTFOUND , CRYPT_PK_INVALID_TYPE , CRYPT_PK_INVALID_SYSTEM ,
  CRYPT_PK_DUP , CRYPT_PK_NOT_FOUND , CRYPT_PK_INVALID_SIZE , CRYPT_INVALID_PRIME_SIZE
}
 

Functions

int rc2_setup (const unsigned char *key, int keylen, int bits, int num_rounds, rc2_key *skey)
 
void rc2_ecb_encrypt (const unsigned char *pt, unsigned char *ct, rc2_key *key)
 
void rc2_ecb_decrypt (const unsigned char *ct, unsigned char *pt, rc2_key *key)
 
int des_setup (const unsigned char *key, int keylen, int num_rounds, des_key *skey)
 
void des_ecb_encrypt (const unsigned char *pt, unsigned char *ct, const des_key *key)
 
void des_ecb_decrypt (const unsigned char *ct, unsigned char *pt, const des_key *key)
 
int des3_setup (const unsigned char *key, int keylen, int num_rounds, des3_key *skey)
 
void des3_ecb_encrypt (const unsigned char *pt, unsigned char *ct, const des3_key *key)
 
void des3_ecb_decrypt (const unsigned char *ct, unsigned char *pt, const des3_key *key)
 
int aes_setup (const unsigned char *key, int keylen, int rounds, aes_key *skey)
 
void aes_ecb_encrypt (const unsigned char *pt, unsigned char *ct, aes_key *skey)
 
void aes_ecb_decrypt (const unsigned char *ct, unsigned char *pt, aes_key *skey)
 
int md2_init (md2_state *md)
 
int md2_process (md2_state *md, const unsigned char *buf, unsigned long len)
 
int md2_done (md2_state *md, unsigned char *hash)
 
int rc4_start (prng_state *prng)
 
int rc4_add_entropy (const unsigned char *buf, unsigned long len, prng_state *prng)
 
int rc4_ready (prng_state *prng)
 
unsigned long rc4_read (unsigned char *buf, unsigned long len, prng_state *prng)
 
char * mp_error_to_string (int code)
 
int mp_init_multi (mp_int *mp,...)
 
void mp_clear_multi (mp_int *mp,...)
 
int mp_shrink (mp_int *a)
 
int mp_set_int (mp_int *a, unsigned long b)
 
unsigned long mp_get_int (const mp_int *a)
 
int mp_init_set (mp_int *a, mp_digit b)
 
int mp_init_set_int (mp_int *a, unsigned long b)
 
int mp_copy (const mp_int *a, mp_int *b)
 
int mp_init_copy (mp_int *a, const mp_int *b)
 
int mp_rand (mp_int *a, int digits)
 
int mp_xor (mp_int *a, mp_int *b, mp_int *c)
 
int mp_or (mp_int *a, mp_int *b, mp_int *c)
 
int mp_and (mp_int *a, mp_int *b, mp_int *c)
 
int mp_neg (mp_int *a, mp_int *b)
 
int mp_cmp (const mp_int *a, const mp_int *b)
 
int mp_add (mp_int *a, mp_int *b, mp_int *c)
 
int mp_sub (mp_int *a, mp_int *b, mp_int *c)
 
int mp_mul (const mp_int *a, const mp_int *b, mp_int *c)
 
int mp_mod (const mp_int *a, mp_int *b, mp_int *c)
 
int mp_cmp_d (const mp_int *a, mp_digit b)
 
int mp_sub_d (mp_int *a, mp_digit b, mp_int *c)
 
int mp_div_3 (mp_int *a, mp_int *c, mp_digit *d)
 
int mp_expt_d (mp_int *a, mp_digit b, mp_int *c)
 
int mp_addmod (mp_int *a, mp_int *b, mp_int *c, mp_int *d)
 
int mp_submod (mp_int *a, mp_int *b, mp_int *c, mp_int *d)
 
int mp_mulmod (const mp_int *a, const mp_int *b, mp_int *c, mp_int *d)
 
int mp_invmod (const mp_int *a, mp_int *b, mp_int *c)
 
int mp_gcd (const mp_int *a, const mp_int *b, mp_int *c)
 
int mp_exteuclid (mp_int *a, mp_int *b, mp_int *U1, mp_int *U2, mp_int *U3)
 
int mp_lcm (const mp_int *a, const mp_int *b, mp_int *c)
 
int mp_n_root (mp_int *a, mp_digit b, mp_int *c)
 
int mp_sqrt (mp_int *arg, mp_int *ret)
 
int mp_is_square (mp_int *arg, int *ret)
 
int mp_jacobi (mp_int *a, mp_int *n, int *c)
 
int mp_dr_is_modulus (mp_int *a)
 
int mp_reduce_is_2k (mp_int *a)
 
int mp_exptmod (const mp_int *a, const mp_int *b, mp_int *c, mp_int *d)
 
int mp_prime_fermat (mp_int *a, mp_int *b, int *result)
 
int mp_prime_rabin_miller_trials (int size)
 
int mp_prime_next_prime (mp_int *a, int t, int bbs_style)
 
int mp_prime_random_ex (mp_int *a, int t, int size, int flags, ltm_prime_callback cb, void *dat)
 
int mp_count_bits (const mp_int *a)
 
int mp_unsigned_bin_size (const mp_int *a)
 
int mp_read_unsigned_bin (mp_int *a, const unsigned char *b, int c)
 
int mp_to_unsigned_bin (const mp_int *a, unsigned char *b)
 
int mp_read_signed_bin (mp_int *a, unsigned char *b, int c)
 
int mp_to_signed_bin (mp_int *a, unsigned char *b)
 
int mp_read_radix (mp_int *a, char *str, int radix)
 
int mp_toradix (mp_int *a, char *str, int radix)
 
int mp_toradix_n (mp_int *a, char *str, int radix, int maxlen)
 
int mp_radix_size (mp_int *a, int radix, int *size)
 
int mp_fread (mp_int *a, int radix, FILE *stream)
 
int mp_fwrite (mp_int *a, int radix, FILE *stream)
 
int rsa_make_key (int size, long e, rsa_key *key)
 
int rsa_exptmod (const unsigned char *in, unsigned long inlen, unsigned char *out, unsigned long *outlen, int which, rsa_key *key)
 
void rsa_free (rsa_key *key)
 

Variables

const char * mp_s_rmap
 

Macro Definition Documentation

◆ byte

#define byte (   x,
  n 
)    (((x) >> (8 * (n))) & 255)

Definition at line 118 of file tomcrypt.h.

◆ CONST64

#define CONST64 (   a,
  b 
)    ((((ULONG64)(a)) << 32) | (b))

Definition at line 78 of file tomcrypt.h.

◆ DIGIT

#define DIGIT (   m,
  k 
)    ((m)->dp[(k)])

Definition at line 233 of file tomcrypt.h.

◆ DIGIT_BIT

#define DIGIT_BIT   28

Definition at line 186 of file tomcrypt.h.

◆ LOAD32H

#define LOAD32H (   x,
  y 
)
Value:
{ x = ((unsigned long)((y)[0] & 255)<<24) | \
((unsigned long)((y)[1] & 255)<<16) | \
((unsigned long)((y)[2] & 255)<<8) | \
((unsigned long)((y)[3] & 255)); }
GLint GLint GLint GLint GLint x
Definition: gl.h:1548
GLint GLint GLint GLint GLint GLint y
Definition: gl.h:1548
#define long
Definition: qsort.c:33

Definition at line 91 of file tomcrypt.h.

◆ LTM_PRIME_2MSB_OFF

#define LTM_PRIME_2MSB_OFF   0x0004 /* force 2nd MSB to 0 */

Definition at line 211 of file tomcrypt.h.

◆ LTM_PRIME_2MSB_ON

#define LTM_PRIME_2MSB_ON   0x0008 /* force 2nd MSB to 1 */

Definition at line 212 of file tomcrypt.h.

◆ LTM_PRIME_BBS

#define LTM_PRIME_BBS   0x0001 /* BBS style prime */

Definition at line 209 of file tomcrypt.h.

◆ LTM_PRIME_SAFE

#define LTM_PRIME_SAFE   0x0002 /* Safe prime (p-1)/2 == prime */

Definition at line 210 of file tomcrypt.h.

◆ MAX_RSA_SIZE

#define MAX_RSA_SIZE   16384

Definition at line 454 of file tomcrypt.h.

◆ MIN

#define MIN (   x,
  y 
)    ( ((x)<(y))?(x):(y) )

Definition at line 116 of file tomcrypt.h.

◆ MIN_RSA_SIZE

#define MIN_RSA_SIZE   384

Definition at line 453 of file tomcrypt.h.

◆ MP_DIGIT_BIT

#define MP_DIGIT_BIT   DIGIT_BIT

Definition at line 188 of file tomcrypt.h.

◆ MP_DIGIT_MAX

#define MP_DIGIT_MAX   MP_MASK

Definition at line 190 of file tomcrypt.h.

◆ MP_EQ

#define MP_EQ   0 /* equal to */

Definition at line 194 of file tomcrypt.h.

◆ MP_GT

#define MP_GT   1 /* greater than */

Definition at line 195 of file tomcrypt.h.

◆ mp_iseven

#define mp_iseven (   a)    (((a)->used > 0 && (((a)->dp[0] & 1) == 0)) ? MP_YES : MP_NO)

Definition at line 249 of file tomcrypt.h.

◆ mp_isodd

#define mp_isodd (   a)    (((a)->used > 0 && (((a)->dp[0] & 1) == 1)) ? MP_YES : MP_NO)

Definition at line 250 of file tomcrypt.h.

◆ mp_iszero

#define mp_iszero (   a)    (((a)->used == 0) ? MP_YES : MP_NO)

Definition at line 248 of file tomcrypt.h.

◆ MP_LT

#define MP_LT   -1 /* less than */

Definition at line 193 of file tomcrypt.h.

◆ mp_mag_size

#define mp_mag_size (   mp)    mp_unsigned_bin_size(mp)

Definition at line 439 of file tomcrypt.h.

◆ MP_MASK

#define MP_MASK   ((((mp_digit)1)<<((mp_digit)DIGIT_BIT))-((mp_digit)1))

Definition at line 189 of file tomcrypt.h.

◆ MP_MEM

#define MP_MEM   -2 /* out of mem */

Definition at line 201 of file tomcrypt.h.

◆ MP_NEG

#define MP_NEG   1 /* negative */

Definition at line 198 of file tomcrypt.h.

◆ MP_NO

#define MP_NO   0 /* no response */

Definition at line 206 of file tomcrypt.h.

◆ MP_OKAY

#define MP_OKAY   0 /* ok result */

Definition at line 200 of file tomcrypt.h.

◆ MP_PREC

#define MP_PREC   64 /* default digits of precision */

Definition at line 219 of file tomcrypt.h.

◆ mp_prime_random

#define mp_prime_random (   a,
  t,
  size,
  bbs,
  cb,
  dat 
)    mp_prime_random_ex(a, t, ((size) * 8) + 1, (bbs==1)?LTM_PRIME_BBS:0, cb, dat)

Definition at line 399 of file tomcrypt.h.

◆ MP_RANGE

#define MP_RANGE   MP_VAL

Definition at line 203 of file tomcrypt.h.

◆ mp_raw_size

#define mp_raw_size (   mp)    mp_signed_bin_size(mp)

Definition at line 436 of file tomcrypt.h.

◆ mp_read_mag

#define mp_read_mag (   mp,
  str,
  len 
)    mp_read_unsigned_bin((mp), (str), (len))

Definition at line 438 of file tomcrypt.h.

◆ mp_read_raw

#define mp_read_raw (   mp,
  str,
  len 
)    mp_read_signed_bin((mp), (str), (len))

Definition at line 435 of file tomcrypt.h.

◆ mp_tobinary

#define mp_tobinary (   M,
  S 
)    mp_toradix((M), (S), 2)

Definition at line 442 of file tomcrypt.h.

◆ mp_todecimal

#define mp_todecimal (   M,
  S 
)    mp_toradix((M), (S), 10)

Definition at line 444 of file tomcrypt.h.

◆ mp_tohex

#define mp_tohex (   M,
  S 
)    mp_toradix((M), (S), 16)

Definition at line 445 of file tomcrypt.h.

◆ mp_tomag

#define mp_tomag (   mp,
  str 
)    mp_to_unsigned_bin((mp), (str))

Definition at line 440 of file tomcrypt.h.

◆ mp_tooctal

#define mp_tooctal (   M,
  S 
)    mp_toradix((M), (S), 8)

Definition at line 443 of file tomcrypt.h.

◆ mp_toraw

#define mp_toraw (   mp,
  str 
)    mp_to_signed_bin((mp), (str))

Definition at line 437 of file tomcrypt.h.

◆ MP_VAL

#define MP_VAL   -3 /* invalid input */

Definition at line 202 of file tomcrypt.h.

◆ MP_WARRAY

#define MP_WARRAY   (1 << (sizeof(mp_word) * CHAR_BIT - 2 * DIGIT_BIT + 1))

Definition at line 222 of file tomcrypt.h.

◆ MP_YES

#define MP_YES   1 /* yes response */

Definition at line 205 of file tomcrypt.h.

◆ MP_ZPOS

#define MP_ZPOS   0 /* positive integer */

Definition at line 197 of file tomcrypt.h.

◆ PK_PRIVATE

#define PK_PRIVATE   0 /* PK private keys */

Definition at line 449 of file tomcrypt.h.

◆ PK_PUBLIC

#define PK_PUBLIC   1 /* PK public keys */

Definition at line 450 of file tomcrypt.h.

◆ PRIME_SIZE

#define PRIME_SIZE   256

Definition at line 371 of file tomcrypt.h.

◆ ROR

#define ROR (   x,
  y 
)
Value:
( ((((unsigned long)(x)&0xFFFFFFFFUL)>>(unsigned long)((y)&31)) | \
((unsigned long)(x)<<(unsigned long)(32-((y)&31)))) & 0xFFFFFFFFUL)

Definition at line 110 of file tomcrypt.h.

◆ STORE32H

#define STORE32H (   x,
  y 
)
Value:
{ (y)[0] = (unsigned char)(((x)>>24)&255); (y)[1] = (unsigned char)(((x)>>16)&255); \
(y)[2] = (unsigned char)(((x)>>8)&255); (y)[3] = (unsigned char)((x)&255); }

Definition at line 87 of file tomcrypt.h.

Typedef Documentation

◆ aes_key

◆ des3_key

◆ des_key

◆ ltm_prime_callback

typedef int ltm_prime_callback(unsigned char *dst, int len, void *dat)

Definition at line 231 of file tomcrypt.h.

◆ md2_state

◆ mp_digit

Definition at line 184 of file tomcrypt.h.

◆ mp_err

typedef int mp_err

Definition at line 214 of file tomcrypt.h.

◆ mp_word

typedef ulong64 mp_word

Definition at line 185 of file tomcrypt.h.

◆ prng_state

typedef union Prng_state prng_state

◆ rc2_key

◆ rsa_key

◆ ulong32

typedef ULONG32 ulong32

Definition at line 84 of file tomcrypt.h.

◆ ulong64

typedef ULONG64 ulong64

Definition at line 79 of file tomcrypt.h.

Enumeration Type Documentation

◆ anonymous enum

anonymous enum
Enumerator
CRYPT_OK 
CRYPT_ERROR 
CRYPT_NOP 
CRYPT_INVALID_KEYSIZE 
CRYPT_INVALID_ROUNDS 
CRYPT_FAIL_TESTVECTOR 
CRYPT_BUFFER_OVERFLOW 
CRYPT_INVALID_PACKET 
CRYPT_INVALID_PRNGSIZE 
CRYPT_ERROR_READPRNG 
CRYPT_INVALID_CIPHER 
CRYPT_INVALID_HASH 
CRYPT_INVALID_PRNG 
CRYPT_MEM 
CRYPT_PK_TYPE_MISMATCH 
CRYPT_PK_NOT_PRIVATE 
CRYPT_INVALID_ARG 
CRYPT_FILE_NOTFOUND 
CRYPT_PK_INVALID_TYPE 
CRYPT_PK_INVALID_SYSTEM 
CRYPT_PK_DUP 
CRYPT_PK_NOT_FOUND 
CRYPT_PK_INVALID_SIZE 
CRYPT_INVALID_PRIME_SIZE 

Definition at line 42 of file tomcrypt.h.

42 {
43 CRYPT_OK=0, /* Result OK */
44 CRYPT_ERROR, /* Generic Error */
45 CRYPT_NOP, /* Not a failure but no operation was performed */
46
47 CRYPT_INVALID_KEYSIZE, /* Invalid key size given */
48 CRYPT_INVALID_ROUNDS, /* Invalid number of rounds */
49 CRYPT_FAIL_TESTVECTOR, /* Algorithm failed test vectors */
50
51 CRYPT_BUFFER_OVERFLOW, /* Not enough space for output */
52 CRYPT_INVALID_PACKET, /* Invalid input packet given */
53
54 CRYPT_INVALID_PRNGSIZE, /* Invalid number of bits for a PRNG */
55 CRYPT_ERROR_READPRNG, /* Could not read enough from PRNG */
56
57 CRYPT_INVALID_CIPHER, /* Invalid cipher specified */
58 CRYPT_INVALID_HASH, /* Invalid hash specified */
59 CRYPT_INVALID_PRNG, /* Invalid PRNG specified */
60
61 CRYPT_MEM, /* Out of memory */
62
63 CRYPT_PK_TYPE_MISMATCH, /* Not equivalent types of PK keys */
64 CRYPT_PK_NOT_PRIVATE, /* Requires a private PK key */
65
66 CRYPT_INVALID_ARG, /* Generic invalid argument */
67 CRYPT_FILE_NOTFOUND, /* File Not Found */
68
69 CRYPT_PK_INVALID_TYPE, /* Invalid type of PK key */
70 CRYPT_PK_INVALID_SYSTEM,/* Invalid PK system specified */
71 CRYPT_PK_DUP, /* Duplicate key already in key ring */
72 CRYPT_PK_NOT_FOUND, /* Key not found in keyring */
73 CRYPT_PK_INVALID_SIZE, /* Invalid size input for PK parameters */
74
75 CRYPT_INVALID_PRIME_SIZE/* Invalid size of prime requested */
76};
@ CRYPT_ERROR
Definition: tomcrypt.h:44
@ CRYPT_MEM
Definition: tomcrypt.h:61
@ CRYPT_PK_INVALID_TYPE
Definition: tomcrypt.h:69
@ CRYPT_INVALID_CIPHER
Definition: tomcrypt.h:57
@ CRYPT_PK_TYPE_MISMATCH
Definition: tomcrypt.h:63
@ CRYPT_INVALID_PRIME_SIZE
Definition: tomcrypt.h:75
@ CRYPT_PK_INVALID_SYSTEM
Definition: tomcrypt.h:70
@ CRYPT_INVALID_PRNG
Definition: tomcrypt.h:59
@ CRYPT_ERROR_READPRNG
Definition: tomcrypt.h:55
@ CRYPT_INVALID_ROUNDS
Definition: tomcrypt.h:48
@ CRYPT_PK_NOT_FOUND
Definition: tomcrypt.h:72
@ CRYPT_INVALID_ARG
Definition: tomcrypt.h:66
@ CRYPT_INVALID_PACKET
Definition: tomcrypt.h:52
@ CRYPT_FILE_NOTFOUND
Definition: tomcrypt.h:67
@ CRYPT_INVALID_KEYSIZE
Definition: tomcrypt.h:47
@ CRYPT_PK_NOT_PRIVATE
Definition: tomcrypt.h:64
@ CRYPT_INVALID_PRNGSIZE
Definition: tomcrypt.h:54
@ CRYPT_NOP
Definition: tomcrypt.h:45
@ CRYPT_BUFFER_OVERFLOW
Definition: tomcrypt.h:51
@ CRYPT_OK
Definition: tomcrypt.h:43
@ CRYPT_PK_INVALID_SIZE
Definition: tomcrypt.h:73
@ CRYPT_PK_DUP
Definition: tomcrypt.h:71
@ CRYPT_INVALID_HASH
Definition: tomcrypt.h:58
@ CRYPT_FAIL_TESTVECTOR
Definition: tomcrypt.h:49

Function Documentation

◆ aes_ecb_decrypt()

void aes_ecb_decrypt ( const unsigned char *  ct,
unsigned char *  pt,
aes_key *  skey 
)

Definition at line 1165 of file aes.c.

1166{
1167 ulong32 s0, s1, s2, s3, t0, t1, t2, t3, *rk;
1168 int Nr, r;
1169
1170 Nr = skey->Nr;
1171 rk = skey->dK;
1172
1173 LOAD32H(s0, ct ); s0 ^= rk[0];
1174 LOAD32H(s1, ct + 4); s1 ^= rk[1];
1175 LOAD32H(s2, ct + 8); s2 ^= rk[2];
1176 LOAD32H(s3, ct + 12); s3 ^= rk[3];
1177
1178 r = Nr >> 1;
1179 for (;;) {
1180
1181 t0 =
1182 Td0(byte(s0, 3)) ^
1183 Td1(byte(s3, 2)) ^
1184 Td2(byte(s2, 1)) ^
1185 Td3(byte(s1, 0)) ^
1186 rk[4];
1187 t1 =
1188 Td0(byte(s1, 3)) ^
1189 Td1(byte(s0, 2)) ^
1190 Td2(byte(s3, 1)) ^
1191 Td3(byte(s2, 0)) ^
1192 rk[5];
1193 t2 =
1194 Td0(byte(s2, 3)) ^
1195 Td1(byte(s1, 2)) ^
1196 Td2(byte(s0, 1)) ^
1197 Td3(byte(s3, 0)) ^
1198 rk[6];
1199 t3 =
1200 Td0(byte(s3, 3)) ^
1201 Td1(byte(s2, 2)) ^
1202 Td2(byte(s1, 1)) ^
1203 Td3(byte(s0, 0)) ^
1204 rk[7];
1205
1206 rk += 8;
1207 if (--r == 0) {
1208 break;
1209 }
1210
1211
1212 s0 =
1213 Td0(byte(t0, 3)) ^
1214 Td1(byte(t3, 2)) ^
1215 Td2(byte(t2, 1)) ^
1216 Td3(byte(t1, 0)) ^
1217 rk[0];
1218 s1 =
1219 Td0(byte(t1, 3)) ^
1220 Td1(byte(t0, 2)) ^
1221 Td2(byte(t3, 1)) ^
1222 Td3(byte(t2, 0)) ^
1223 rk[1];
1224 s2 =
1225 Td0(byte(t2, 3)) ^
1226 Td1(byte(t1, 2)) ^
1227 Td2(byte(t0, 1)) ^
1228 Td3(byte(t3, 0)) ^
1229 rk[2];
1230 s3 =
1231 Td0(byte(t3, 3)) ^
1232 Td1(byte(t2, 2)) ^
1233 Td2(byte(t1, 1)) ^
1234 Td3(byte(t0, 0)) ^
1235 rk[3];
1236 }
1237
1238 s0 =
1239 (Td4[byte(t0, 3)] & 0xff000000) ^
1240 (Td4[byte(t3, 2)] & 0x00ff0000) ^
1241 (Td4[byte(t2, 1)] & 0x0000ff00) ^
1242 (Td4[byte(t1, 0)] & 0x000000ff) ^
1243 rk[0];
1244 STORE32H(s0, pt);
1245 s1 =
1246 (Td4[byte(t1, 3)] & 0xff000000) ^
1247 (Td4[byte(t0, 2)] & 0x00ff0000) ^
1248 (Td4[byte(t3, 1)] & 0x0000ff00) ^
1249 (Td4[byte(t2, 0)] & 0x000000ff) ^
1250 rk[1];
1251 STORE32H(s1, pt+4);
1252 s2 =
1253 (Td4[byte(t2, 3)] & 0xff000000) ^
1254 (Td4[byte(t1, 2)] & 0x00ff0000) ^
1255 (Td4[byte(t0, 1)] & 0x0000ff00) ^
1256 (Td4[byte(t3, 0)] & 0x000000ff) ^
1257 rk[2];
1258 STORE32H(s2, pt+8);
1259 s3 =
1260 (Td4[byte(t3, 3)] & 0xff000000) ^
1261 (Td4[byte(t2, 2)] & 0x00ff0000) ^
1262 (Td4[byte(t1, 1)] & 0x0000ff00) ^
1263 (Td4[byte(t0, 0)] & 0x000000ff) ^
1264 rk[3];
1265 STORE32H(s3, pt+12);
1266}
#define pt(x, y)
Definition: drawing.c:79
GLdouble GLdouble GLdouble r
Definition: gl.h:2055
struct S1 s1
#define Td1(x)
Definition: aes.c:240
#define Td2(x)
Definition: aes.c:241
#define Td3(x)
Definition: aes.c:242
static const ulong32 Td4[256]
Definition: aes.c:167
#define Td0(x)
Definition: aes.c:239
PCWSTR s2
Definition: shell32_main.h:38
#define STORE32H(x, y)
Definition: tomcrypt.h:87
ULONG32 ulong32
Definition: tomcrypt.h:84
#define byte(x, n)
Definition: tomcrypt.h:118
#define LOAD32H(x, y)
Definition: tomcrypt.h:91

Referenced by KsecDecryptMemoryAes().

◆ aes_ecb_encrypt()

void aes_ecb_encrypt ( const unsigned char *  pt,
unsigned char *  ct,
aes_key *  skey 
)

Definition at line 1064 of file aes.c.

1065{
1066 ulong32 s0, s1, s2, s3, t0, t1, t2, t3, *rk;
1067 int Nr, r;
1068
1069 Nr = skey->Nr;
1070 rk = skey->eK;
1071
1072 LOAD32H(s0, pt ); s0 ^= rk[0];
1073 LOAD32H(s1, pt + 4); s1 ^= rk[1];
1074 LOAD32H(s2, pt + 8); s2 ^= rk[2];
1075 LOAD32H(s3, pt + 12); s3 ^= rk[3];
1076
1077 r = Nr >> 1;
1078 for (;;) {
1079 t0 =
1080 Te0(byte(s0, 3)) ^
1081 Te1(byte(s1, 2)) ^
1082 Te2(byte(s2, 1)) ^
1083 Te3(byte(s3, 0)) ^
1084 rk[4];
1085 t1 =
1086 Te0(byte(s1, 3)) ^
1087 Te1(byte(s2, 2)) ^
1088 Te2(byte(s3, 1)) ^
1089 Te3(byte(s0, 0)) ^
1090 rk[5];
1091 t2 =
1092 Te0(byte(s2, 3)) ^
1093 Te1(byte(s3, 2)) ^
1094 Te2(byte(s0, 1)) ^
1095 Te3(byte(s1, 0)) ^
1096 rk[6];
1097 t3 =
1098 Te0(byte(s3, 3)) ^
1099 Te1(byte(s0, 2)) ^
1100 Te2(byte(s1, 1)) ^
1101 Te3(byte(s2, 0)) ^
1102 rk[7];
1103
1104 rk += 8;
1105 if (--r == 0) {
1106 break;
1107 }
1108
1109 s0 =
1110 Te0(byte(t0, 3)) ^
1111 Te1(byte(t1, 2)) ^
1112 Te2(byte(t2, 1)) ^
1113 Te3(byte(t3, 0)) ^
1114 rk[0];
1115 s1 =
1116 Te0(byte(t1, 3)) ^
1117 Te1(byte(t2, 2)) ^
1118 Te2(byte(t3, 1)) ^
1119 Te3(byte(t0, 0)) ^
1120 rk[1];
1121 s2 =
1122 Te0(byte(t2, 3)) ^
1123 Te1(byte(t3, 2)) ^
1124 Te2(byte(t0, 1)) ^
1125 Te3(byte(t1, 0)) ^
1126 rk[2];
1127 s3 =
1128 Te0(byte(t3, 3)) ^
1129 Te1(byte(t0, 2)) ^
1130 Te2(byte(t1, 1)) ^
1131 Te3(byte(t2, 0)) ^
1132 rk[3];
1133 }
1134
1135 s0 =
1136 (Te4_3[byte(t0, 3)]) ^
1137 (Te4_2[byte(t1, 2)]) ^
1138 (Te4_1[byte(t2, 1)]) ^
1139 (Te4_0[byte(t3, 0)]) ^
1140 rk[0];
1141 STORE32H(s0, ct);
1142 s1 =
1143 (Te4_3[byte(t1, 3)]) ^
1144 (Te4_2[byte(t2, 2)]) ^
1145 (Te4_1[byte(t3, 1)]) ^
1146 (Te4_0[byte(t0, 0)]) ^
1147 rk[1];
1148 STORE32H(s1, ct+4);
1149 s2 =
1150 (Te4_3[byte(t2, 3)]) ^
1151 (Te4_2[byte(t3, 2)]) ^
1152 (Te4_1[byte(t0, 1)]) ^
1153 (Te4_0[byte(t1, 0)]) ^
1154 rk[2];
1155 STORE32H(s2, ct+8);
1156 s3 =
1157 (Te4_3[byte(t3, 3)]) ^
1158 (Te4_2[byte(t0, 2)]) ^
1159 (Te4_1[byte(t1, 1)]) ^
1160 (Te4_0[byte(t2, 0)]) ^
1161 rk[3];
1162 STORE32H(s3, ct+12);
1163}
static const ulong32 Te4_2[]
Definition: aes.c:514
static const ulong32 Te4_0[]
Definition: aes.c:444
#define Te2(x)
Definition: aes.c:236
static const ulong32 Te4_1[]
Definition: aes.c:479
static const ulong32 Te4_3[]
Definition: aes.c:549
#define Te0(x)
Definition: aes.c:234
#define Te3(x)
Definition: aes.c:237
#define Te1(x)
Definition: aes.c:235

Referenced by KsecEncryptMemoryAes().

◆ aes_setup()

int aes_setup ( const unsigned char *  key,
int  keylen,
int  rounds,
aes_key *  skey 
)

Definition at line 937 of file aes.c.

938{
939 int i, j;
940 ulong32 temp, *rk;
941 ulong32 *rrk;
942
943 if (keylen != 16 && keylen != 24 && keylen != 32) {
945 }
946
947 if (rounds != 0 && rounds != (10 + ((keylen/8)-2)*2)) {
949 }
950
951 skey->Nr = 10 + ((keylen/8)-2)*2;
952
953 /* setup the forward key */
954 i = 0;
955 rk = skey->eK;
956 LOAD32H(rk[0], key );
957 LOAD32H(rk[1], key + 4);
958 LOAD32H(rk[2], key + 8);
959 LOAD32H(rk[3], key + 12);
960 if (keylen == 16) {
961 j = 44;
962 for (;;) {
963 temp = rk[3];
964 rk[4] = rk[0] ^ setup_mix(temp) ^ rcon[i];
965 rk[5] = rk[1] ^ rk[4];
966 rk[6] = rk[2] ^ rk[5];
967 rk[7] = rk[3] ^ rk[6];
968 if (++i == 10) {
969 break;
970 }
971 rk += 4;
972 }
973 } else if (keylen == 24) {
974 j = 52;
975 LOAD32H(rk[4], key + 16);
976 LOAD32H(rk[5], key + 20);
977 for (;;) {
978 temp = rk[5];
979 rk[ 6] = rk[ 0] ^ setup_mix(temp) ^ rcon[i];
980 rk[ 7] = rk[ 1] ^ rk[ 6];
981 rk[ 8] = rk[ 2] ^ rk[ 7];
982 rk[ 9] = rk[ 3] ^ rk[ 8];
983 if (++i == 8) {
984 break;
985 }
986 rk[10] = rk[ 4] ^ rk[ 9];
987 rk[11] = rk[ 5] ^ rk[10];
988 rk += 6;
989 }
990 } else if (keylen == 32) {
991 j = 60;
992 LOAD32H(rk[4], key + 16);
993 LOAD32H(rk[5], key + 20);
994 LOAD32H(rk[6], key + 24);
995 LOAD32H(rk[7], key + 28);
996 for (;;) {
997 temp = rk[7];
998 rk[ 8] = rk[ 0] ^ setup_mix(temp) ^ rcon[i];
999 rk[ 9] = rk[ 1] ^ rk[ 8];
1000 rk[10] = rk[ 2] ^ rk[ 9];
1001 rk[11] = rk[ 3] ^ rk[10];
1002 if (++i == 7) {
1003 break;
1004 }
1005 temp = rk[11];
1006 rk[12] = rk[ 4] ^ setup_mix(ROR(temp, 8));
1007 rk[13] = rk[ 5] ^ rk[12];
1008 rk[14] = rk[ 6] ^ rk[13];
1009 rk[15] = rk[ 7] ^ rk[14];
1010 rk += 8;
1011 }
1012 } else {
1013 j = 4;
1014 }
1015
1016 rk = skey->dK;
1017 rrk = skey->eK + j - 4;
1018
1019 *rk++ = *rrk++;
1020 *rk++ = *rrk++;
1021 *rk++ = *rrk++;
1022 *rk = *rrk;
1023 rk -= 3; rrk -= 3;
1024
1025 for (i = 1; i < skey->Nr; i++) {
1026 rrk -= 4;
1027 rk += 4;
1028 temp = rrk[0];
1029 rk[0] =
1030 Tks0[byte(temp, 3)] ^
1031 Tks1[byte(temp, 2)] ^
1032 Tks2[byte(temp, 1)] ^
1033 Tks3[byte(temp, 0)];
1034 temp = rrk[1];
1035 rk[1] =
1036 Tks0[byte(temp, 3)] ^
1037 Tks1[byte(temp, 2)] ^
1038 Tks2[byte(temp, 1)] ^
1039 Tks3[byte(temp, 0)];
1040 temp = rrk[2];
1041 rk[2] =
1042 Tks0[byte(temp, 3)] ^
1043 Tks1[byte(temp, 2)] ^
1044 Tks2[byte(temp, 1)] ^
1045 Tks3[byte(temp, 0)];
1046 temp = rrk[3];
1047 rk[3] =
1048 Tks0[byte(temp, 3)] ^
1049 Tks1[byte(temp, 2)] ^
1050 Tks2[byte(temp, 1)] ^
1051 Tks3[byte(temp, 0)];
1052 }
1053
1054 rrk -= 4;
1055 rk += 4;
1056 *rk++ = *rrk++;
1057 *rk++ = *rrk++;
1058 *rk++ = *rrk++;
1059 *rk = *rrk;
1060
1061 return CRYPT_OK;
1062}
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble const GLfloat const GLdouble const GLfloat GLint i
Definition: glfuncs.h:248
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble const GLfloat const GLdouble const GLfloat GLint GLint GLint j
Definition: glfuncs.h:250
static calc_node_t temp
Definition: rpn_ieee.c:38
static ulong32 setup_mix(ulong32 temp)
Definition: aes.c:929
static const ulong32 Tks1[]
Definition: aes.c:818
static const ulong32 Tks0[]
Definition: aes.c:783
static const ulong32 Tks2[]
Definition: aes.c:853
static const ulong32 Tks3[]
Definition: aes.c:888
static const ulong32 rcon[]
Definition: aes.c:923
Definition: copy.c:22
#define ROR(x, y)
Definition: tomcrypt.h:110

Referenced by KsecGetAesKey(), and KsecInitializeEncryptionSupport().

◆ des3_ecb_decrypt()

void des3_ecb_decrypt ( const unsigned char *  ct,
unsigned char *  pt,
const des3_key *  key 
)

Definition at line 1485 of file des.c.

1486{
1487 ulong32 work[2];
1488 LOAD32H(work[0], ct+0);
1489 LOAD32H(work[1], ct+4);
1490 desfunc(work, des3->dk[0]);
1491 desfunc(work, des3->dk[1]);
1492 desfunc(work, des3->dk[2]);
1493 STORE32H(work[0],pt+0);
1494 STORE32H(work[1],pt+4);
1495}
static void desfunc(ulong32 *block, const ulong32 *keys)
Definition: des.c:1357

Referenced by KsecDecryptMemoryDes3().

◆ des3_ecb_encrypt()

void des3_ecb_encrypt ( const unsigned char *  pt,
unsigned char *  ct,
const des3_key *  key 
)

Definition at line 1473 of file des.c.

1474{
1475 ulong32 work[2];
1476 LOAD32H(work[0], pt+0);
1477 LOAD32H(work[1], pt+4);
1478 desfunc(work, des3->ek[0]);
1479 desfunc(work, des3->ek[1]);
1480 desfunc(work, des3->ek[2]);
1481 STORE32H(work[0],ct+0);
1482 STORE32H(work[1],ct+4);
1483}

Referenced by KsecEncryptMemoryDes3().

◆ des3_setup()

int des3_setup ( const unsigned char *  key,
int  keylen,
int  num_rounds,
des3_key *  skey 
)

Definition at line 1432 of file des.c.

1433{
1434 if(num_rounds != 0 && num_rounds != 16) {
1435 return CRYPT_INVALID_ROUNDS;
1436 }
1437
1438 if (keylen != 24) {
1439 return CRYPT_INVALID_KEYSIZE;
1440 }
1441
1442 deskey(key, EN0, des3->ek[0]);
1443 deskey(key+8, DE1, des3->ek[1]);
1444 deskey(key+16, EN0, des3->ek[2]);
1445
1446 deskey(key, DE1, des3->dk[2]);
1447 deskey(key+8, EN0, des3->dk[1]);
1448 deskey(key+16, DE1, des3->dk[0]);
1449
1450 return CRYPT_OK;
1451}
static void deskey(const unsigned char *key, short edf, ulong32 *keyout)
Definition: des.c:1285
#define DE1
Definition: des.c:35
#define EN0
Definition: des.c:34

Referenced by KsecGetDes3Key(), and KsecInitializeEncryptionSupport().

◆ des_ecb_decrypt()

void des_ecb_decrypt ( const unsigned char *  ct,
unsigned char *  pt,
const des_key *  key 
)

Definition at line 1463 of file des.c.

1464{
1465 ulong32 work[2];
1466 LOAD32H(work[0], ct+0);
1467 LOAD32H(work[1], ct+4);
1468 desfunc(work, des->dk);
1469 STORE32H(work[0],pt+0);
1470 STORE32H(work[1],pt+4);
1471}

◆ des_ecb_encrypt()

void des_ecb_encrypt ( const unsigned char *  pt,
unsigned char *  ct,
const des_key *  key 
)

Definition at line 1453 of file des.c.

1454{
1455 ulong32 work[2];
1456 LOAD32H(work[0], pt+0);
1457 LOAD32H(work[1], pt+4);
1458 desfunc(work, des->ek);
1459 STORE32H(work[0],ct+0);
1460 STORE32H(work[1],ct+4);
1461}

◆ des_setup()

int des_setup ( const unsigned char *  key,
int  keylen,
int  num_rounds,
des_key *  skey 
)

Definition at line 1416 of file des.c.

1417{
1418 if (num_rounds != 0 && num_rounds != 16) {
1419 return CRYPT_INVALID_ROUNDS;
1420 }
1421
1422 if (keylen != 8) {
1423 return CRYPT_INVALID_KEYSIZE;
1424 }
1425
1426 deskey(key, EN0, des->ek);
1427 deskey(key, DE1, des->dk);
1428
1429 return CRYPT_OK;
1430}

◆ md2_done()

int md2_done ( md2_state *  md,
unsigned char *  hash 
)

◆ md2_init()

int md2_init ( md2_state *  md)

◆ md2_process()

int md2_process ( md2_state *  md,
const unsigned char *  buf,
unsigned long  len 
)

◆ mp_add()

int mp_add ( mp_int *  a,
mp_int *  b,
mp_int *  c 
)

◆ mp_addmod()

int mp_addmod ( mp_int *  a,
mp_int *  b,
mp_int *  c,
mp_int *  d 
)

◆ mp_and()

int mp_and ( mp_int *  a,
mp_int *  b,
mp_int *  c 
)

◆ mp_clear_multi()

void mp_clear_multi ( mp_int *  mp,
  ... 
)

◆ mp_cmp()

int mp_cmp ( const mp_int *  a,
const mp_int *  b 
)

◆ mp_cmp_d()

int mp_cmp_d ( const mp_int *  a,
mp_digit  b 
)

◆ mp_copy()

int mp_copy ( const mp_int *  a,
mp_int *  b 
)

◆ mp_count_bits()

int mp_count_bits ( const mp_int *  a)

◆ mp_div_3()

int mp_div_3 ( mp_int *  a,
mp_int *  c,
mp_digit *  d 
)

◆ mp_dr_is_modulus()

int mp_dr_is_modulus ( mp_int *  a)

◆ mp_error_to_string()

char * mp_error_to_string ( int  code)

◆ mp_expt_d()

int mp_expt_d ( mp_int *  a,
mp_digit  b,
mp_int *  c 
)

◆ mp_exptmod()

int mp_exptmod ( const mp_int *  a,
const mp_int *  b,
mp_int *  c,
mp_int *  d 
)

◆ mp_exteuclid()

int mp_exteuclid ( mp_int *  a,
mp_int *  b,
mp_int *  U1,
mp_int *  U2,
mp_int *  U3 
)

◆ mp_fread()

int mp_fread ( mp_int *  a,
int  radix,
FILE *  stream 
)

◆ mp_fwrite()

int mp_fwrite ( mp_int *  a,
int  radix,
FILE *  stream 
)

◆ mp_gcd()

int mp_gcd ( const mp_int *  a,
const mp_int *  b,
mp_int *  c 
)

◆ mp_get_int()

unsigned long mp_get_int ( const mp_int *  a)

◆ mp_init_copy()

int mp_init_copy ( mp_int *  a,
const mp_int *  b 
)

◆ mp_init_multi()

int mp_init_multi ( mp_int *  mp,
  ... 
)

◆ mp_init_set()

int mp_init_set ( mp_int *  a,
mp_digit  b 
)

◆ mp_init_set_int()

int mp_init_set_int ( mp_int *  a,
unsigned long  b 
)

◆ mp_invmod()

int mp_invmod ( const mp_int *  a,
mp_int *  b,
mp_int *  c 
)

◆ mp_is_square()

int mp_is_square ( mp_int *  arg,
int *  ret 
)

◆ mp_jacobi()

int mp_jacobi ( mp_int *  a,
mp_int *  n,
int *  c 
)

◆ mp_lcm()

int mp_lcm ( const mp_int *  a,
const mp_int *  b,
mp_int *  c 
)

◆ mp_mod()

int mp_mod ( const mp_int *  a,
mp_int *  b,
mp_int *  c 
)

◆ mp_mul()

int mp_mul ( const mp_int *  a,
const mp_int *  b,
mp_int *  c 
)

◆ mp_mulmod()

int mp_mulmod ( const mp_int *  a,
const mp_int *  b,
mp_int *  c,
mp_int *  d 
)

◆ mp_n_root()

int mp_n_root ( mp_int *  a,
mp_digit  b,
mp_int *  c 
)

◆ mp_neg()

int mp_neg ( mp_int *  a,
mp_int *  b 
)

◆ mp_or()

int mp_or ( mp_int *  a,
mp_int *  b,
mp_int *  c 
)

◆ mp_prime_fermat()

int mp_prime_fermat ( mp_int *  a,
mp_int *  b,
int *  result 
)

◆ mp_prime_next_prime()

int mp_prime_next_prime ( mp_int *  a,
int  t,
int  bbs_style 
)

◆ mp_prime_rabin_miller_trials()

int mp_prime_rabin_miller_trials ( int  size)

◆ mp_prime_random_ex()

int mp_prime_random_ex ( mp_int *  a,
int  t,
int  size,
int  flags,
ltm_prime_callback  cb,
void *  dat 
)

◆ mp_radix_size()

int mp_radix_size ( mp_int *  a,
int  radix,
int *  size 
)

◆ mp_rand()

int mp_rand ( mp_int *  a,
int  digits 
)

◆ mp_read_radix()

int mp_read_radix ( mp_int *  a,
char *  str,
int  radix 
)

◆ mp_read_signed_bin()

int mp_read_signed_bin ( mp_int *  a,
unsigned char *  b,
int  c 
)

◆ mp_read_unsigned_bin()

int mp_read_unsigned_bin ( mp_int *  a,
const unsigned char *  b,
int  c 
)

◆ mp_reduce_is_2k()

int mp_reduce_is_2k ( mp_int *  a)

◆ mp_set_int()

int mp_set_int ( mp_int *  a,
unsigned long  b 
)

◆ mp_shrink()

int mp_shrink ( mp_int *  a)

◆ mp_sqrt()

int mp_sqrt ( mp_int *  arg,
mp_int *  ret 
)

◆ mp_sub()

int mp_sub ( mp_int *  a,
mp_int *  b,
mp_int *  c 
)

◆ mp_sub_d()

int mp_sub_d ( mp_int *  a,
mp_digit  b,
mp_int *  c 
)

◆ mp_submod()

int mp_submod ( mp_int *  a,
mp_int *  b,
mp_int *  c,
mp_int *  d 
)

◆ mp_to_signed_bin()

int mp_to_signed_bin ( mp_int *  a,
unsigned char *  b 
)

◆ mp_to_unsigned_bin()

int mp_to_unsigned_bin ( const mp_int *  a,
unsigned char *  b 
)

◆ mp_toradix()

int mp_toradix ( mp_int *  a,
char *  str,
int  radix 
)

◆ mp_toradix_n()

int mp_toradix_n ( mp_int *  a,
char *  str,
int  radix,
int  maxlen 
)

◆ mp_unsigned_bin_size()

int mp_unsigned_bin_size ( const mp_int *  a)

◆ mp_xor()

int mp_xor ( mp_int *  a,
mp_int *  b,
mp_int *  c 
)

◆ rc2_ecb_decrypt()

void rc2_ecb_decrypt ( const unsigned char *  ct,
unsigned char *  pt,
rc2_key *  key 
)

◆ rc2_ecb_encrypt()

void rc2_ecb_encrypt ( const unsigned char *  pt,
unsigned char *  ct,
rc2_key *  key 
)

◆ rc2_setup()

int rc2_setup ( const unsigned char *  key,
int  keylen,
int  bits,
int  num_rounds,
rc2_key *  skey 
)

◆ rc4_add_entropy()

int rc4_add_entropy ( const unsigned char *  buf,
unsigned long  len,
prng_state *  prng 
)

◆ rc4_read()

unsigned long rc4_read ( unsigned char *  buf,
unsigned long  len,
prng_state *  prng 
)

◆ rc4_ready()

int rc4_ready ( prng_state *  prng)

◆ rc4_start()

int rc4_start ( prng_state *  prng)

◆ rsa_exptmod()

int rsa_exptmod ( const unsigned char *  in,
unsigned long  inlen,
unsigned char *  out,
unsigned long *  outlen,
int  which,
rsa_key *  key 
)

◆ rsa_free()

void rsa_free ( rsa_key *  key)

◆ rsa_make_key()

int rsa_make_key ( int  size,
long  e,
rsa_key *  key 
)

Variable Documentation

◆ mp_s_rmap

const char* mp_s_rmap
extern