#include "precomp.h"
Include dependency graph for rc2.c:
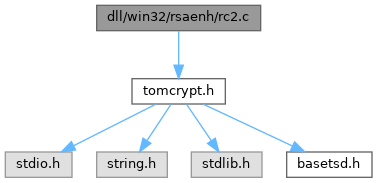
Go to the source code of this file.
Macros | |
| #define | MIXROUND(n) |
| #define | MASHROUND() |
| #define | RMIXROUND(n) |
| #define | RMASHROUND() |
Variables | |
| const SYMCRYPT_BLOCKCIPHER | SymCryptRc2BlockCipher_default |
| const PCSYMCRYPT_BLOCKCIPHER | SymCryptRc2BlockCipher = &SymCryptRc2BlockCipher_default |
| static const BYTE | PITABLE [] |
| static const BYTE | testPlaintext [8] = { 'P', 'l', 'a', 'i', 'n', 't', 'x', 't', } |
| static const BYTE | testCiphertext [8] |
Macro Definition Documentation
◆ MASHROUND
| #define MASHROUND | ( | ) |
Value:
{ \
}
◆ MIXROUND
Value:
{\
}
◆ RMASHROUND
| #define RMASHROUND | ( | ) |
◆ RMIXROUND
Value:
{\
}
Function Documentation
◆ SymCryptRc2Decrypt()
| VOID SYMCRYPT_CALL SymCryptRc2Decrypt | ( | _In_ PCSYMCRYPT_RC2_EXPANDED_KEY | pExpandedKey, |
| _In_reads_(SYMCRYPT_RC2_BLOCK_SIZE) PCBYTE | pbSrc, | ||
| _Out_writes_(SYMCRYPT_RC2_BLOCK_SIZE) PBYTE | pbDst | ||
| ) |
Definition at line 330 of file rc2.c.
334{
336 PCUINT16 K;
337
339
340 //
341 // 1. Initialize words R[0], ..., R[3] to contain the 64-bit plaintext value.
342 //
347
348 //
349 // 2. Expand the key, so that words K[0], ..., K[63] become defined.
350 // (In our case the key was previously expanded, so we just grab the pointer to it.)
351 //
352 K = pExpandedKey->K;
353
354 //
355 // 3. Initialize j to 63.
356 //
357
358 //
359 // 4. Perform five r-mixing rounds.
360 //
361 RMIXROUND(15);
362 RMIXROUND(14);
363 RMIXROUND(13);
364 RMIXROUND(12);
365 RMIXROUND(11);
366
367 //
368 // 5. Perform one r-mashing round.
369 //
370 RMASHROUND();
371
372 //
373 // 6. Perform six r-mixing rounds.
374 //
375 RMIXROUND(10);
376 RMIXROUND(9);
377 RMIXROUND(8);
378 RMIXROUND(7);
379 RMIXROUND(6);
380 RMIXROUND(5);
381
382 //
383 // 7. Perform one r-mashing round.
384 //
385 RMASHROUND();
386
387 //
388 // 8. Perform five r-mixing rounds.
389 //
390 RMIXROUND(4);
391 RMIXROUND(3);
392 RMIXROUND(2);
393 RMIXROUND(1);
394 RMIXROUND(0);
395
400
401}
Referenced by decrypt_block_impl(), and SymCryptRc2Selftest().
◆ SymCryptRc2Encrypt()
| VOID SYMCRYPT_CALL SymCryptRc2Encrypt | ( | _In_ PCSYMCRYPT_RC2_EXPANDED_KEY | pExpandedKey, |
| _In_reads_(SYMCRYPT_RC2_BLOCK_SIZE) PCBYTE | pbSrc, | ||
| _Out_writes_(SYMCRYPT_RC2_BLOCK_SIZE) PBYTE | pbDst | ||
| ) |
Definition at line 234 of file rc2.c.
238{
240 PCUINT16 K;
241
243
244 //
245 // 1. Initialize words R[0], ..., R[3] to contain the 64-bit plaintext value.
246 //
251
252 //
253 // 2. Expand the key, so that words K[0], ..., K[63] become defined.
254 // (In our case the key was previously expanded, so we just grab the pointer to it.)
255 //
256 K = pExpandedKey->K;
257
258 //
259 // 3. Initialize j to zero.
260 //
261
262 //
263 // 4. Perform five mixing rounds.
264 //
265 MIXROUND(0);
266 MIXROUND(1);
267 MIXROUND(2);
268 MIXROUND(3);
269 MIXROUND(4);
270
271 //
272 // 5. Perform one mashing round.
273 //
274 MASHROUND();
275
276 //
277 // 6. Perform six mixing rounds.
278 //
279 MIXROUND(5);
280 MIXROUND(6);
281 MIXROUND(7);
282 MIXROUND(8);
283 MIXROUND(9);
284 MIXROUND(10);
285
286 //
287 // 7. Perform one mashing round.
288 //
289 MASHROUND();
290
291 //
292 // 8. Perform five mixing rounds.
293 //
294 MIXROUND(11);
295 MIXROUND(12);
296 MIXROUND(13);
297 MIXROUND(14);
298 MIXROUND(15);
299
304
305}
Referenced by encrypt_block_impl(), and SymCryptRc2Selftest().
◆ SymCryptRc2ExpandKey()
| SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptRc2ExpandKey | ( | _Out_ PSYMCRYPT_RC2_EXPANDED_KEY | pExpandedKey, |
| _In_reads_(cbKey) PCBYTE | pbKey, | ||
| SIZE_T | cbKey | ||
| ) |
◆ SymCryptRc2ExpandKeyEx()
| SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptRc2ExpandKeyEx | ( | _Out_ PSYMCRYPT_RC2_EXPANDED_KEY | pExpandedKey, |
| _In_reads_(cbKey) PCBYTE | pbKey, | ||
| SIZE_T | cbKey, | ||
| UINT32 | effectiveKeySizeInBits | ||
| ) |
Definition at line 129 of file rc2.c.
134{
137 UINT32 T1;
138 UINT32 T8;
139 UINT32 TM;
141
143
144 //
145 // According to RFC 2268 any key size in 1..128 is allowed.
146 //
147 // The effective key size cannot be 0 as the RFC specs would lead to a buffer overflow
148 // in the key expansion.
149 //
150 // If the effective key size <= 8 then T8=1 and the key expansion backward recursion
151 // drops into a fixed point because L[i+1] xor L[i+T8] is zero.
152 // Therefore, we require an effective key size of at least 9.
153 //
154 if( cbKey < 1 || cbKey > 128 || effectiveKeySizeInBits < 9 || effectiveKeySizeInBits > 8*128 )
155 {
156 return SYMCRYPT_WRONG_KEY_SIZE;
157 }
158
160
161 T1 = effectiveKeySizeInBits; // 9 <= T1 <= 1024
162 T8 = (T1+7)/8; // 2 <= T8 <= 128
163
164 TM = 255 & ((1 << (8 + (UINT32)T1 - 8*T8))-1);
165
166 //
167 // To be endian-agnostic our expanded key is stored as an array of UINT16s. We do the key
168 // expansion in a local buffer and copy the values into the expanded key using the proper conversion.
169 //
171
173 {
175 //
176 // If the key size T=1 then we lose one bit of key space in the key expansion because
177 // L[i-1] == L[i-T] which makes the index to PITABLE even. So L[1..128] depend only on
178 // 7 bits.
179 //
180 }
181
183
185 {
187 }
188
189 //
190 // Now we copy the result into the UINT16 array in our expanded key.
191 // This is a memcpy for little-endian platforms, but this code works on all CPUs.
192 //
194 {
196 }
197
199
200 return SYMCRYPT_NO_ERROR;
201}
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble const GLfloat const GLdouble const GLfloat GLint i
Definition: glfuncs.h:248
FORCEINLINE VOID SYMCRYPT_CALL SymCryptWipeKnownSize(_Out_writes_bytes_(cbData) PVOID pbData, SIZE_T cbData)
Definition: symcrypt_internal.h:3411
Referenced by setup_key_impl(), SymCryptRc2ExpandKey(), and SymCryptRc2Selftest().
◆ SymCryptRc2Selftest()
| VOID SYMCRYPT_CALL SymCryptRc2Selftest | ( | void | ) |
Definition at line 410 of file rc2.c.
411{
414
416 {
418 }
419
421
423
425 {
427 }
428
430
432
434 {
436 }
437
438}
VOID SYMCRYPT_CALL SymCryptRc2Decrypt(_In_ PCSYMCRYPT_RC2_EXPANDED_KEY pExpandedKey, _In_reads_(SYMCRYPT_RC2_BLOCK_SIZE) PCBYTE pbSrc, _Out_writes_(SYMCRYPT_RC2_BLOCK_SIZE) PBYTE pbDst)
Definition: rc2.c:330
VOID SYMCRYPT_CALL SymCryptRc2Encrypt(_In_ PCSYMCRYPT_RC2_EXPANDED_KEY pExpandedKey, _In_reads_(SYMCRYPT_RC2_BLOCK_SIZE) PCBYTE pbSrc, _Out_writes_(SYMCRYPT_RC2_BLOCK_SIZE) PBYTE pbDst)
Definition: rc2.c:234
VOID SYMCRYPT_CALL SymCryptInjectError(PBYTE pbData, SIZE_T cbData)
_Analysis_noreturn_ VOID SYMCRYPT_CALL SymCryptFatal(UINT32 fatalCode)
SYMCRYPT_MAGIC_FIELD SYMCRYPT_RC2_EXPANDED_KEY
Definition: symcrypt_internal.h:1815
Variable Documentation
◆ PITABLE
Initial value:
=
{
0xd9, 0x78, 0xf9, 0xc4, 0x19, 0xdd, 0xb5, 0xed, 0x28, 0xe9, 0xfd, 0x79, 0x4a, 0xa0, 0xd8, 0x9d,
0xc6, 0x7e, 0x37, 0x83, 0x2b, 0x76, 0x53, 0x8e, 0x62, 0x4c, 0x64, 0x88, 0x44, 0x8b, 0xfb, 0xa2,
0x17, 0x9a, 0x59, 0xf5, 0x87, 0xb3, 0x4f, 0x13, 0x61, 0x45, 0x6d, 0x8d, 0x09, 0x81, 0x7d, 0x32,
0xbd, 0x8f, 0x40, 0xeb, 0x86, 0xb7, 0x7b, 0x0b, 0xf0, 0x95, 0x21, 0x22, 0x5c, 0x6b, 0x4e, 0x82,
0x54, 0xd6, 0x65, 0x93, 0xce, 0x60, 0xb2, 0x1c, 0x73, 0x56, 0xc0, 0x14, 0xa7, 0x8c, 0xf1, 0xdc,
0x12, 0x75, 0xca, 0x1f, 0x3b, 0xbe, 0xe4, 0xd1, 0x42, 0x3d, 0xd4, 0x30, 0xa3, 0x3c, 0xb6, 0x26,
0x6f, 0xbf, 0x0e, 0xda, 0x46, 0x69, 0x07, 0x57, 0x27, 0xf2, 0x1d, 0x9b, 0xbc, 0x94, 0x43, 0x03,
0xf8, 0x11, 0xc7, 0xf6, 0x90, 0xef, 0x3e, 0xe7, 0x06, 0xc3, 0xd5, 0x2f, 0xc8, 0x66, 0x1e, 0xd7,
0x08, 0xe8, 0xea, 0xde, 0x80, 0x52, 0xee, 0xf7, 0x84, 0xaa, 0x72, 0xac, 0x35, 0x4d, 0x6a, 0x2a,
0x96, 0x1a, 0xd2, 0x71, 0x5a, 0x15, 0x49, 0x74, 0x4b, 0x9f, 0xd0, 0x5e, 0x04, 0x18, 0xa4, 0xec,
0xc2, 0xe0, 0x41, 0x6e, 0x0f, 0x51, 0xcb, 0xcc, 0x24, 0x91, 0xaf, 0x50, 0xa1, 0xf4, 0x70, 0x39,
0x99, 0x7c, 0x3a, 0x85, 0x23, 0xb8, 0xb4, 0x7a, 0xfc, 0x02, 0x36, 0x5b, 0x25, 0x55, 0x97, 0x31,
0x2d, 0x5d, 0xfa, 0x98, 0xe3, 0x8a, 0x92, 0xae, 0x05, 0xdf, 0x29, 0x10, 0x67, 0x6c, 0xba, 0xc9,
0xd3, 0x00, 0xe6, 0xcf, 0xe1, 0x9e, 0xa8, 0x2c, 0x63, 0x16, 0x01, 0x3f, 0x58, 0xe2, 0x89, 0xa9,
0x0d, 0x38, 0x34, 0x1b, 0xab, 0x33, 0xff, 0xb0, 0xbb, 0x48, 0x0c, 0x5f, 0xb9, 0xb1, 0xcd, 0x2e,
0xc5, 0xf3, 0xdb, 0x47, 0xe5, 0xa5, 0x9c, 0x77, 0x0a, 0xa6, 0x20, 0x68, 0xfe, 0x7f, 0xc1, 0xad
}
Definition at line 40 of file rc2.c.
Referenced by SymCryptRc2ExpandKeyEx().
◆ SymCryptRc2BlockCipher
| const PCSYMCRYPT_BLOCKCIPHER SymCryptRc2BlockCipher = &SymCryptRc2BlockCipher_default |
◆ SymCryptRc2BlockCipher_default
| const SYMCRYPT_BLOCKCIPHER SymCryptRc2BlockCipher_default |
◆ testCiphertext
Initial value:
= {
0x89, 0xe8, 0x5d, 0x1a, 0x98, 0xcd, 0xe5, 0x52,
}
Definition at line 404 of file rc2.c.
Referenced by SymCryptRc2Selftest().
