#include "precomp.h"
Include dependency graph for aes-key.c:
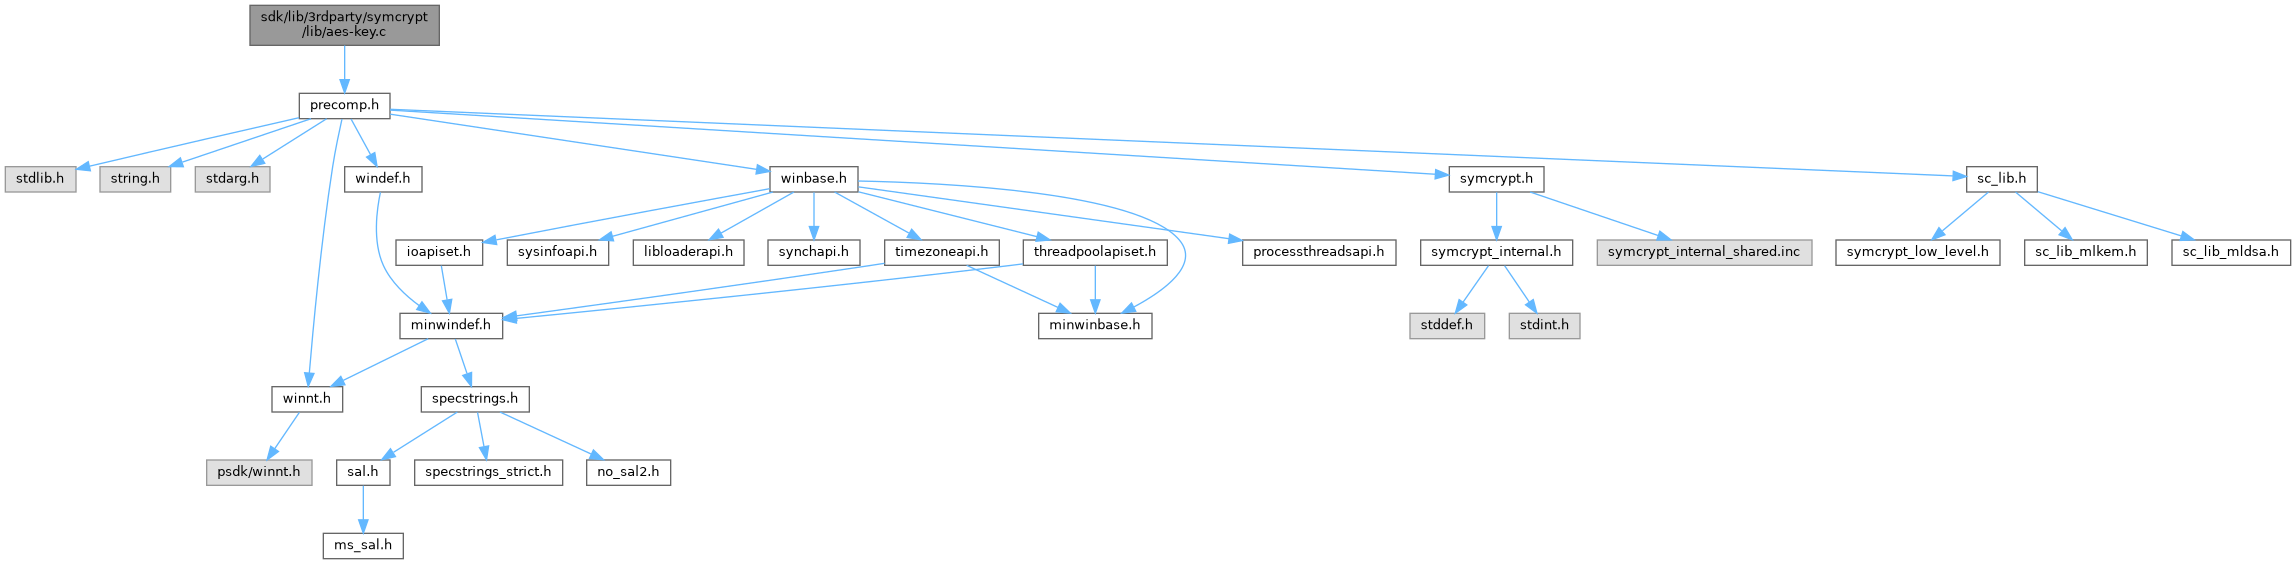
Go to the source code of this file.
Variables | |
| static BYTE | g_SymCryptAesRoundConstant [11] |
| const BYTE | SymCryptAesNistTestVector128Ciphertext [16] |
Function Documentation
◆ SymCryptAesExpandKey()
| SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesExpandKey | ( | _Out_ PSYMCRYPT_AES_EXPANDED_KEY | pExpandedKey, |
| _In_reads_(cbKey) PCBYTE | pbKey, | ||
| SIZE_T | cbKey | ||
| ) |
Definition at line 219 of file aes-key.c.
224{
226}
SYMCRYPT_NOINLINE SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesExpandKeyInternal(_Out_ PSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _In_reads_(cbKey) PCBYTE pbKey, SIZE_T cbKey, BOOLEAN fCreateDecryptionKeys)
Definition: aes-key.c:35
Referenced by setup_key_impl(), SymCryptAesCmacExpandKey(), SymCryptCcmSelftest(), and SymCryptXtsAesExpandKey().
◆ SymCryptAesExpandKeyEncryptOnly()
| SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesExpandKeyEncryptOnly | ( | _Out_ PSYMCRYPT_AES_EXPANDED_KEY | pExpandedKey, |
| _In_reads_(cbKey) PCBYTE | pbKey, | ||
| SIZE_T | cbKey | ||
| ) |
Definition at line 230 of file aes-key.c.
234{
236}
Referenced by SymCryptRngAesDf(), SymCryptRngAesGenerateSmall(), SymCryptRngAesUpdate(), SymCryptSrtpKdfExpandKey(), and SymCryptXtsAesExpandKey().
◆ SymCryptAesExpandKeyInternal()
| SYMCRYPT_NOINLINE SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesExpandKeyInternal | ( | _Out_ PSYMCRYPT_AES_EXPANDED_KEY | pExpandedKey, |
| _In_reads_(cbKey) PCBYTE | pbKey, | ||
| SIZE_T | cbKey, | ||
| BOOLEAN | fCreateDecryptionKeys | ||
| ) |
Definition at line 35 of file aes-key.c.
40{
41 UINT32 nRounds;
46
49
50#if SYMCRYPT_CPU_X86
51 SYMCRYPT_EXTENDED_SAVE_DATA SaveData;
52
54 {
56 {
57 UseSimd = TRUE;
58 }
59 }
60#elif SYMCRYPT_CPU_AMD64
62 {
63 UseSimd = TRUE;
64 }
65#elif SYMCRYPT_CPU_ARM64
67 {
68 UseSimd = TRUE;
69 }
70#endif
71
73
74 //
75 // Separate code for each key size, this is significantly faster.
76 // We have a number of applications that do frequent key expansions.
77 //
79 {
80 case 16:
81 nRounds = 10;
84
86
88
90 {
92 t = ROR32(SYMCRYPT_LOAD_LSBFIRST32(p), 8) ^ SYMCRYPT_LOAD_LSBFIRST32(p - 16) ^ g_SymCryptAesRoundConstant[i];
94
98
99 p += 16;
100 }
101
102 break;
103
104 case 24:
105 nRounds = 12;
108
110
112
113 //
114 // We have 12 rounds, 13 round keys, and 13*16 = 208 bytes of encryption key to generate.
115 // We have 24 already, so we need 184 more.
116 // Each iteration produces 24 bytes, so we need to loop 8 times.
117 //
119 {
121 t = ROR32(SYMCRYPT_LOAD_LSBFIRST32(p), 8) ^ SYMCRYPT_LOAD_LSBFIRST32(p - 24) ^ g_SymCryptAesRoundConstant[i];
123
129
130 p += 24;
131 }
132
133 break;
134
135 case 32:
136 nRounds = 14;
139
141
143
144 //
145 // We have 14 rounds, 15 round keys, and 15*16 = 240 bytes of encryption key to generate.
146 // We have 32 already, so we need 208 more.
147 // Each iteration produces 32 bytes, so we need to loop 6.5 times.
148 //
150 {
152 t = ROR32(SYMCRYPT_LOAD_LSBFIRST32(p), 8) ^ SYMCRYPT_LOAD_LSBFIRST32(p - 32) ^ g_SymCryptAesRoundConstant[i];
154
158
161
165
166 p += 32;
167 }
168
169 // We looped 6 times, so here is the half-loop
170
172 t = ROR32(SYMCRYPT_LOAD_LSBFIRST32(p), 8) ^ SYMCRYPT_LOAD_LSBFIRST32(p - 32) ^ g_SymCryptAesRoundConstant[i];
174
178
179 break;
180
181 default:
182 status = SYMCRYPT_WRONG_KEY_SIZE;
184 }
185
186
187 if( fCreateDecryptionKeys )
188 {
191
192 // The first encryption round key is the last decryption round key
194 p += 16;
195 q -= 16;
196
198 {
200 q -= 16;
201 p += 16;
202 }
203 }
204
205cleanup:
206
207#if SYMCRYPT_CPU_X86
208 if( UseSimd )
209 {
210 SymCryptRestoreXmm( &SaveData );
211 }
212#endif
213
215}
VOID SYMCRYPT_CALL SymCryptAesCreateDecryptionRoundKey(_In_reads_(16) PCBYTE pEncryptionRoundKey, _Out_writes_(16) PBYTE pDecryptionRoundKey, BOOL UseSimd)
Definition: aes-default.c:68
VOID SYMCRYPT_CALL SymCryptAes4Sbox(_In_reads_(4) PCBYTE pIn, _Out_writes_(4) PBYTE pOut, BOOL UseSimd)
Definition: aes-default.c:44
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble const GLfloat const GLdouble const GLfloat GLint i
Definition: glfuncs.h:248
#define SYMCRYPT_CPU_FEATURES_FOR_AESNI_CODE
Definition: sc_lib.h:307
#define SYMCRYPT_CPU_FEATURES_PRESENT(x)
Definition: symcrypt_internal.h:423
Referenced by SymCryptAesExpandKey(), and SymCryptAesExpandKeyEncryptOnly().
◆ SymCryptAesKeyCopy()
| VOID SYMCRYPT_CALL SymCryptAesKeyCopy | ( | _In_ PCSYMCRYPT_AES_EXPANDED_KEY | pSrc, |
| _Out_ PSYMCRYPT_AES_EXPANDED_KEY | pDst | ||
| ) |
Definition at line 240 of file aes-key.c.
242{
243 SYMCRYPT_CHECK_MAGIC( pSrc );
244
245 *pDst = *pSrc;
246 pDst->lastEncRoundKey = &pDst->RoundKey[0] + (pSrc->lastEncRoundKey - &pSrc->RoundKey[0]);
247 pDst->lastDecRoundKey = &pDst->RoundKey[0] + (pSrc->lastDecRoundKey - &pSrc->RoundKey[0]);
248
249 SYMCRYPT_SET_MAGIC( pDst );
250}
Referenced by duplicate_key_impl(), SymCryptAesCmacKeyCopy(), and SymCryptXtsAesKeyCopy().
Variable Documentation
◆ g_SymCryptAesRoundConstant
|
static |
Initial value:
=
{
0, 0x01, 0x02, 0x04, 0x08, 0x10, 0x20, 0x40, 0x80, 0x1b, 0x36,
}
Definition at line 27 of file aes-key.c.
Referenced by SymCryptAesExpandKeyInternal().
