#include "precomp.h"
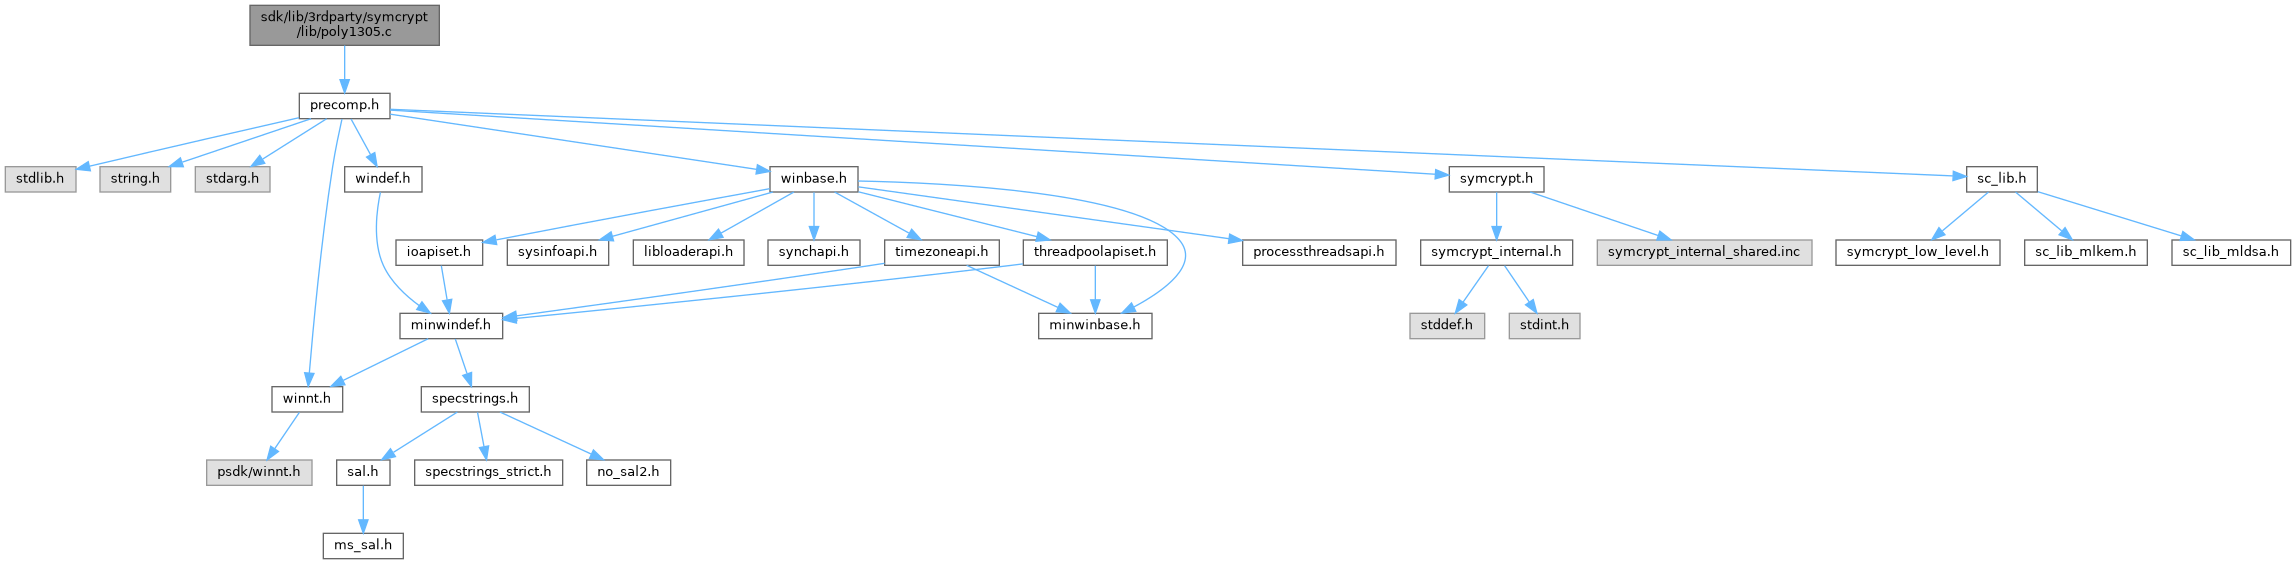
Include dependency graph for poly1305.c:
Go to the source code of this file.
Variables | |
| static const BYTE | poly1305Kat [16] |
Function Documentation
◆ SymCryptPoly1305()
| VOID SYMCRYPT_CALL SymCryptPoly1305 | ( | _In_reads_(SYMCRYPT_POLY1305_KEY_SIZE) PCBYTE | pbKey, |
| _In_reads_(cbData) PCBYTE | pbData, | ||
| SIZE_T | cbData, | ||
| _Out_writes_(SYMCRYPT_POLY1305_RESULT_SIZE) PBYTE | pbResult | ||
| ) |
Definition at line 18 of file poly1305.c.
23{
25
29}
VOID SYMCRYPT_CALL SymCryptPoly1305Result(_Inout_ PSYMCRYPT_POLY1305_STATE pState, _Out_writes_(SYMCRYPT_POLY1305_RESULT_SIZE) PBYTE pbResult)
Definition: poly1305.c:109
VOID SYMCRYPT_CALL SymCryptPoly1305Init(_Out_ PSYMCRYPT_POLY1305_STATE pState, _In_reads_(SYMCRYPT_POLY1305_KEY_SIZE) PCBYTE pbKey)
Definition: poly1305.c:33
VOID SYMCRYPT_CALL SymCryptPoly1305Append(_Inout_ PSYMCRYPT_POLY1305_STATE pState, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData)
Definition: poly1305.c:55
SYMCRYPT_MAGIC_FIELD SYMCRYPT_POLY1305_STATE
Definition: symcrypt_internal.h:1697
Referenced by SymCryptPoly1305Selftest().
◆ SymCryptPoly1305Append()
| VOID SYMCRYPT_CALL SymCryptPoly1305Append | ( | _Inout_ PSYMCRYPT_POLY1305_STATE | pState, |
| _In_reads_(cbData) PCBYTE | pbData, | ||
| SIZE_T | cbData | ||
| ) |
Definition at line 55 of file poly1305.c.
59{
60 SIZE_T nBytes;
62
65 {
66 // We have a partial block in the buffer, keep filling the block
67
69 nBytes = 16 - bytesInBuffer;
71 {
72 nBytes = cbData;
73 }
74
76 pbData += nBytes;
77 cbData -= nBytes;
78 bytesInBuffer += nBytes;
79
81 {
82 // Buffer is full, process it and empty the buffer
84 bytesInBuffer = 0;
85 }
87 }
88
90 {
91 // There are whole blocks to process
94 cbData &= 0xf;
96 }
97
99 {
100 // Copy remaining data to buffer
104 }
105}
VOID SYMCRYPT_CALL SymCryptPoly1305ProcessBlocks(_Inout_ PSYMCRYPT_POLY1305_STATE pState, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData)
Definition: poly1305.c:323
Referenced by SymCryptChaCha20Poly1305ComputeTag(), and SymCryptPoly1305().
◆ SymCryptPoly1305Init()
| VOID SYMCRYPT_CALL SymCryptPoly1305Init | ( | _Out_ PSYMCRYPT_POLY1305_STATE | pState, |
| _In_reads_(SYMCRYPT_POLY1305_KEY_SIZE) PCBYTE | pbKey | ||
| ) |
Definition at line 33 of file poly1305.c.
36{
41
46
47 // Set accumulator to zero
49
50 pState->bytesInBuffer = 0;
51}
FORCEINLINE VOID SYMCRYPT_CALL SymCryptWipeKnownSize(_Out_writes_bytes_(cbData) PVOID pbData, SIZE_T cbData)
Definition: symcrypt_internal.h:3411
Referenced by SymCryptChaCha20Poly1305Decrypt(), SymCryptChaCha20Poly1305Encrypt(), and SymCryptPoly1305().
◆ SymCryptPoly1305ProcessBlocks()
| VOID SYMCRYPT_CALL SymCryptPoly1305ProcessBlocks | ( | _Inout_ PSYMCRYPT_POLY1305_STATE | pState, |
| _In_reads_(cbData) PCBYTE | pbData, | ||
| SIZE_T | cbData | ||
| ) |
Definition at line 323 of file poly1305.c.
329{
332 UINT64 t64;
333 UINT32 T3;
337 UINT32 t32;
338
339 r0 = pState->r[0];
343
344 a0 = pState->a[0];
349
350 // Here we have a4 < 6, but we sometimes decrement a4 to compensate for the
351 // 2^128 this function always adds. So we test a4 + 1 < 7
353
355 {
356 // Acc += data[0..15] + 2^128
358 a0 = (UINT32) t64;
359 t64 >>= 32;
360
363 t64 >>= 32;
364
367 t64 >>= 32;
368
371 t64 >>= 32;
372
375
376 pbData += 16;
377 cbData -=16;
378
379 // Compute S3
380 t64 = SYMCRYPT_MUL32x32TO64( a3, r0 )
383 + SYMCRYPT_MUL32x32TO64( a0, r3 );
384
385 SYMCRYPT_ASSERT( t64 < (1ULL << 62) );
386
387 T3 = (UINT32) t64;
388 t64 >>= 32;
389
390 // Compute T = S4 + floor(S3/2^32). We have the floor part in t64 already
391 // now add S4 to it
396
398 t64 &= ~3; // t64 = T4 here
399
400 // Compute S0 + T4 + T4/4, and V0
401 t64 += (t64 >> 2) + SYMCRYPT_MUL32x32TO64( a0, r0 );
404
405 // Compute S5
407 t64 += t64 >> 2; // = S5 + S5/4
408
410 // t64 = S1 + S5 + S5/4
411
412 t64 += cy;
415
416 // Compute S6
418 t64 += t64 >> 2; // S6 + S6/4
419
420 // now add S2
421 t64 += SYMCRYPT_MUL32x32TO64( a2, r0 ) + SYMCRYPT_MUL32x32TO64( a1, r1 ) + SYMCRYPT_MUL32x32TO64( a0, r2 );
422 t64 += cy;
423 V2 = (UINT32) t64;
425
426 // Finally T3 + S7 + S7/4
428 t32 += t32/4;
429 t64 = (UINT64) T3 + t32;
430 t64 += cy;
431
432 a0 = V0;
434 a2 = V2;
437
439 }
440
441 pState->a[0] = a0;
446}
Referenced by SymCryptPoly1305Append(), and SymCryptPoly1305Result().
◆ SymCryptPoly1305Result()
| VOID SYMCRYPT_CALL SymCryptPoly1305Result | ( | _Inout_ PSYMCRYPT_POLY1305_STATE | pState, |
| _Out_writes_(SYMCRYPT_POLY1305_RESULT_SIZE) PBYTE | pbResult | ||
| ) |
Definition at line 109 of file poly1305.c.
112{
116 UINT32 maskOld, maskNew;
117
120 {
121 // Add trailing '1' byte and pad with zeroes
122 // Wipe function deals with 0-length wipes properly
125
126 // Now we have to process the block, but the block function adds a trailing
127 // 1 byte to each 16-byte block. We compensate for that by decrementing
128 // the highest word of the accumulator first; the 1 byte added by the block
129 // processing function has the effect of incrementing the highest accumulator
130 // word so those two operations cancel each other out.
131 pState->a[4] -= 1;
133 }
134
135 // We have to fully reduce the accumulator first
136 // We have a[4]<6 at this point
137 a0 = pState->a[0];
142
144 // Because a4 < 6, we have to subtract either 0*P or 1*P
145 // we subtract P and them mux-choose between the new and old value
146 // Subtracting P is the same as subtracting 2^130 and adding 5
147 t = 5;
148
149 t += a0;
151 t >>= 32;
152
155 t >>= 32;
156
159 t >>= 32;
160
163 t >>= 32;
164
166 t -= 4;
168 t >>= 32;
169
170 // If this subtraction produced a carry, then t = 0xffffffff, otherwise it is 0
172 maskNew = ~maskOld; // ffffffff if the new value is correct, 0 otherwise
173
174 a0 = (maskNew & a0) | (maskOld & pState->a[0]);
178 // a4 = (maskNew & a4) | (maskOld & pState->a[4]); // We don't need a4...
179
180 // Now we add S and return the data
181 t = a0;
184 t >>= 32;
185
189 t >>= 32;
190
194 t >>= 32;
195
199
201}
VOID SYMCRYPT_CALL SymCryptWipe(_Out_writes_bytes_(cbData) PVOID pbData, SIZE_T cbData)
Definition: libmain.c:137
Referenced by SymCryptChaCha20Poly1305ComputeTag(), and SymCryptPoly1305().
◆ SymCryptPoly1305Selftest()
| VOID SYMCRYPT_CALL SymCryptPoly1305Selftest | ( | void | ) |
Definition at line 456 of file poly1305.c.
457{
459
461
463
465 {
467 }
468}
VOID SYMCRYPT_CALL SymCryptInjectError(PBYTE pbData, SIZE_T cbData)
VOID SYMCRYPT_CALL SymCryptPoly1305(_In_reads_(SYMCRYPT_POLY1305_KEY_SIZE) PCBYTE pbKey, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData, _Out_writes_(SYMCRYPT_POLY1305_RESULT_SIZE) PBYTE pbResult)
Definition: poly1305.c:18
_Analysis_noreturn_ VOID SYMCRYPT_CALL SymCryptFatal(UINT32 fatalCode)
Variable Documentation
◆ poly1305Kat
Initial value:
= {
0xef, 0x9e, 0x73, 0x2a, 0x7f, 0x2d, 0xf1, 0x85, 0xa7, 0x11, 0x80, 0xae, 0x58, 0x3a, 0x0f, 0x93,
}
Definition at line 449 of file poly1305.c.
Referenced by SymCryptPoly1305Selftest().
