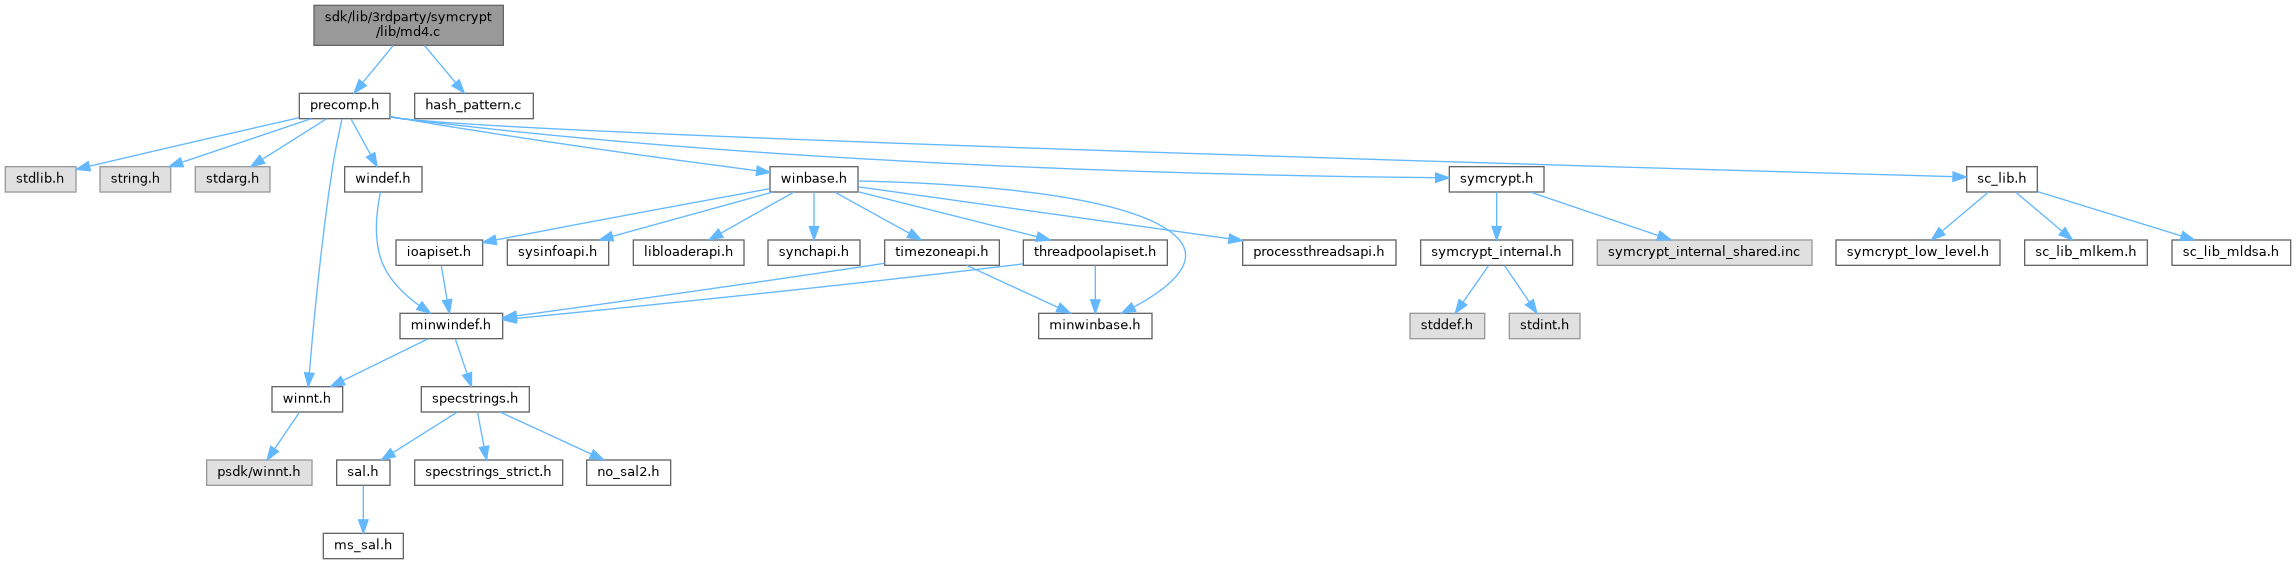
Include dependency graph for md4.c:
Go to the source code of this file.
Macros | |
| #define | ALG MD4 |
| #define | Alg Md4 |
| #define | F(x, y, z) ((((z) ^ (y)) & (x)) ^ (z)) |
| #define | G(x, y, z) ((((x) | (y)) & (z) ) | ((x) & (y))) |
| #define | H(x, y, z) ((x) ^ (y) ^ (z) ) |
| #define | CROUND(r, Func) |
| #define | IROUND(r, Func) |
| #define | FROUND(r, Func) |
Variables | |
| const SYMCRYPT_HASH | SymCryptMd4Algorithm_default |
| const PCSYMCRYPT_HASH | SymCryptMd4Algorithm = &SymCryptMd4Algorithm_default |
| static const UINT32 | md4Const [3] |
| static const int | md4Rotate [48] |
| static const int | md4MsgIndex [48] |
| static const UINT32 | md4InitialState [4] |
| static const BYTE | md4KATAnswer [16] |
Macro Definition Documentation
◆ ALG
◆ Alg
◆ CROUND
◆ F
◆ FROUND
Value:
◆ G
◆ H
◆ IROUND
Value:
{ \
}
Function Documentation
◆ SymCryptMd4Append()
| VOID SYMCRYPT_CALL SymCryptMd4Append | ( | _Inout_ PSYMCRYPT_MD4_STATE | pState, |
| _In_reads_(cbData) PCBYTE | pbData, | ||
| SIZE_T | cbData | ||
| ) |
Definition at line 139 of file md4.c.
142{
143 SymCryptHashAppendInternal( SymCryptMd4Algorithm, (PSYMCRYPT_COMMON_HASH_STATE)pState, pbData, cbData );
144}
VOID SYMCRYPT_CALL SymCryptHashAppendInternal(_In_ PCSYMCRYPT_HASH pHash, _Inout_ PSYMCRYPT_COMMON_HASH_STATE pState, _In_reads_bytes_(cbData) PCBYTE pbData, SIZE_T cbData)
Definition: hash.c:10
◆ SymCryptMd4AppendBlocks()
| VOID SYMCRYPT_CALL SymCryptMd4AppendBlocks | ( | _Inout_ PSYMCRYPT_MD4_CHAINING_STATE | pChain, |
| _In_reads_(cbData) PCBYTE | pbData, | ||
| SIZE_T | cbData, | ||
| _Out_ SIZE_T * | pcbRemaining | ||
| ) |
Definition at line 234 of file md4.c.
239{
240
243 UINT32 Wt;
244
245 ad[0] = pChain->H[0];
246 ad[1] = pChain->H[3];
247 ad[2] = pChain->H[2];
248 ad[3] = pChain->H[1];
249
251 {
252 //
253 // initial rounds 1 to 16
254 //
255
272
289
306
307 pChain->H[0] = ad[0] = ad[0] + pChain->H[0];
308 pChain->H[3] = ad[1] = ad[1] + pChain->H[3];
309 pChain->H[2] = ad[2] = ad[2] + pChain->H[2];
310 pChain->H[1] = ad[3] = ad[3] + pChain->H[1];
311
312 pbData += 64;
313 cbData -= 64;
314 }
315
316 *pcbRemaining = cbData;
317 //
318 // Wipe the variables;
319 //
322 SYMCRYPT_FORCE_WRITE32( &Wt, 0 );
323}
FORCEINLINE VOID SYMCRYPT_CALL SymCryptWipeKnownSize(_Out_writes_bytes_(cbData) PVOID pbData, SIZE_T cbData)
Definition: symcrypt_internal.h:3411
◆ SymCryptMd4Init()
| VOID SYMCRYPT_CALL SymCryptMd4Init | ( | _Out_ PSYMCRYPT_MD4_STATE | pState | ) |
Definition at line 117 of file md4.c.
118{
120
121 pState->dataLengthL = 0;
122 pState->dataLengthH = 0;
123 pState->bytesInBuffer = 0;
124
126
127 //
128 // There is no need to initialize the buffer part of the state as that will be
129 // filled before it is used.
130 //
131}
Referenced by SymCryptMd4Result().
◆ SymCryptMd4Result()
| VOID SYMCRYPT_CALL SymCryptMd4Result | ( | _Inout_ PSYMCRYPT_MD4_STATE | pState, |
| _Out_writes_(SYMCRYPT_MD4_RESULT_SIZE) PBYTE | pbResult | ||
| ) |
Definition at line 152 of file md4.c.
155{
157
158 //
159 // Write the output in the correct byte order
160 //
162
163 //
164 // Wipe & re-initialize
165 // We have to wipe the whole state as the initialization might be optimized away.
166 //
169 }
FORCEINLINE VOID SYMCRYPT_CALL SymCryptUint32ToLsbFirst(_In_reads_(cuData) PCUINT32 puData, _Out_writes_(4 *cuData) PBYTE pbResult, SIZE_T cuData)
Definition: sc_lib.h:471
VOID SYMCRYPT_CALL SymCryptHashCommonPaddingMd4Style(_In_ PCSYMCRYPT_HASH pHash, _Inout_ PSYMCRYPT_COMMON_HASH_STATE pState)
Definition: hash.c:85
VOID SYMCRYPT_CALL SymCryptMd4Init(_Out_ PSYMCRYPT_MD4_STATE pState)
Definition: md4.c:117
◆ SymCryptMd4Selftest()
| VOID SYMCRYPT_CALL SymCryptMd4Selftest | ( | void | ) |
Definition at line 414 of file md4.c.
415{
417
419
421
424 }
425}
VOID SYMCRYPT_CALL SymCryptInjectError(PBYTE pbData, SIZE_T cbData)
_Analysis_noreturn_ VOID SYMCRYPT_CALL SymCryptFatal(UINT32 fatalCode)
VOID SYMCRYPT_CALL SymCryptMd4(_In_reads_(cbData) PCBYTE pbData, SIZE_T cbData, _Out_writes_(SYMCRYPT_MD4_RESULT_SIZE) PBYTE pbResult)
◆ SymCryptMd4StateExport()
| VOID SYMCRYPT_CALL SymCryptMd4StateExport | ( | _In_ PCSYMCRYPT_MD4_STATE | pState, |
| _Out_writes_bytes_(SYMCRYPT_MD4_STATE_EXPORT_SIZE) PBYTE | pbBlob | ||
| ) |
Definition at line 327 of file md4.c.
330{
333
335
337
341
342 //
343 // Copy the relevant data. Buffer will be 0-padded.
344 //
345
349
350 SYMCRYPT_ASSERT( (PCBYTE) &blob + sizeof( blob ) - sizeof( SYMCRYPT_BLOB_TRAILER ) == (PCBYTE) &blob.trailer );
351 SymCryptMarvin32( SymCryptMarvin32DefaultSeed, (PCBYTE) &blob, sizeof( blob ) - sizeof( SYMCRYPT_BLOB_TRAILER ), &blob.trailer.checksum[0] );
352
354
355//cleanup:
357 return;
358}
Definition: sc_lib.h:1090
Definition: sc_lib.h:1107
Definition: image.c:229
VOID SYMCRYPT_CALL SymCryptMarvin32(_In_ PCSYMCRYPT_MARVIN32_EXPANDED_SEED pExpandedSeed, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData, _Out_writes_(SYMCRYPT_MARVIN32_RESULT_SIZE) PBYTE pbResult)
Definition: marvin32.c:239
PCSYMCRYPT_MARVIN32_EXPANDED_SEED const SymCryptMarvin32DefaultSeed
Definition: marvin32.c:29
#define SYMCRYPT_MD4_STATE_EXPORT_SIZE
Definition: symcrypt_internal.h:2180
◆ SymCryptMd4StateImport()
| SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptMd4StateImport | ( | _Out_ PSYMCRYPT_MD4_STATE | pState, |
| _In_reads_bytes_(SYMCRYPT_MD4_STATE_EXPORT_SIZE) PCBYTE | pbBlob | ||
| ) |
Definition at line 362 of file md4.c.
365{
366 SYMCRYPT_ERROR scError = SYMCRYPT_NO_ERROR;
369
372
376 {
377 scError = SYMCRYPT_INVALID_BLOB;
379 }
380
381 SymCryptMarvin32( SymCryptMarvin32DefaultSeed, (PCBYTE) &blob, sizeof( blob ) - sizeof( SYMCRYPT_BLOB_TRAILER ), checksum );
383 {
384 scError = SYMCRYPT_INVALID_BLOB;
386 }
387
390 pState->dataLengthH = 0;
393
395
396cleanup:
398 return scError;
399}
static cab_ULONG checksum(const cab_UBYTE *data, cab_UWORD bytes, cab_ULONG csum)
Definition: fdi.c:353
FORCEINLINE VOID SYMCRYPT_CALL SymCryptLsbFirstToUint32(_In_reads_(4 *cuResult) PCBYTE pbData, _Out_writes_(cuResult) PUINT32 puResult, SIZE_T cuResult)
Definition: sc_lib.h:487
Variable Documentation
◆ md4Const
◆ md4InitialState
Initial value:
= {
0x67452301UL,
0xefcdab89UL,
0x98badcfeUL,
0x10325476UL,
}
Definition at line 93 of file md4.c.
Referenced by SymCryptMd4Init().
◆ md4KATAnswer
Initial value:
= {
0xa4, 0x48, 0x01, 0x7a, 0xaf, 0x21, 0xd8, 0x52,
0x5f, 0xc1, 0x0a, 0xe8, 0x7a, 0xa6, 0x72, 0x9d,
}
Definition at line 407 of file md4.c.
Referenced by SymCryptMd4Selftest().
◆ md4MsgIndex
◆ md4Rotate
◆ SymCryptMd4Algorithm
| const PCSYMCRYPT_HASH SymCryptMd4Algorithm = &SymCryptMd4Algorithm_default |
Definition at line 46 of file md4.c.
Referenced by init_hash_impl(), SymCryptMd4Append(), and SymCryptMd4Result().
◆ SymCryptMd4Algorithm_default
| const SYMCRYPT_HASH SymCryptMd4Algorithm_default |
Initial value:
= {
sizeof( SYMCRYPT_MD4_STATE ),
}
VOID SYMCRYPT_CALL SymCryptMd4Result(_Inout_ PSYMCRYPT_MD4_STATE pState, _Out_writes_(SYMCRYPT_MD4_RESULT_SIZE) PBYTE pbResult)
Definition: md4.c:152
VOID SYMCRYPT_CALL SymCryptMd4AppendBlocks(_Inout_ PSYMCRYPT_MD4_CHAINING_STATE pChain, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData, _Out_ SIZE_T *pcbRemaining)
Definition: md4.c:234
VOID SYMCRYPT_CALL SymCryptMd4Append(_Inout_ PSYMCRYPT_MD4_STATE pState, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData)
Definition: md4.c:139
VOID SYMCRYPT_CALL SymCryptMd4StateCopy(_In_ PCSYMCRYPT_MD4_STATE pSrc, _Out_ PSYMCRYPT_MD4_STATE pDst)
