#include "precomp.h"
Include dependency graph for tlsCbcVerify.c:
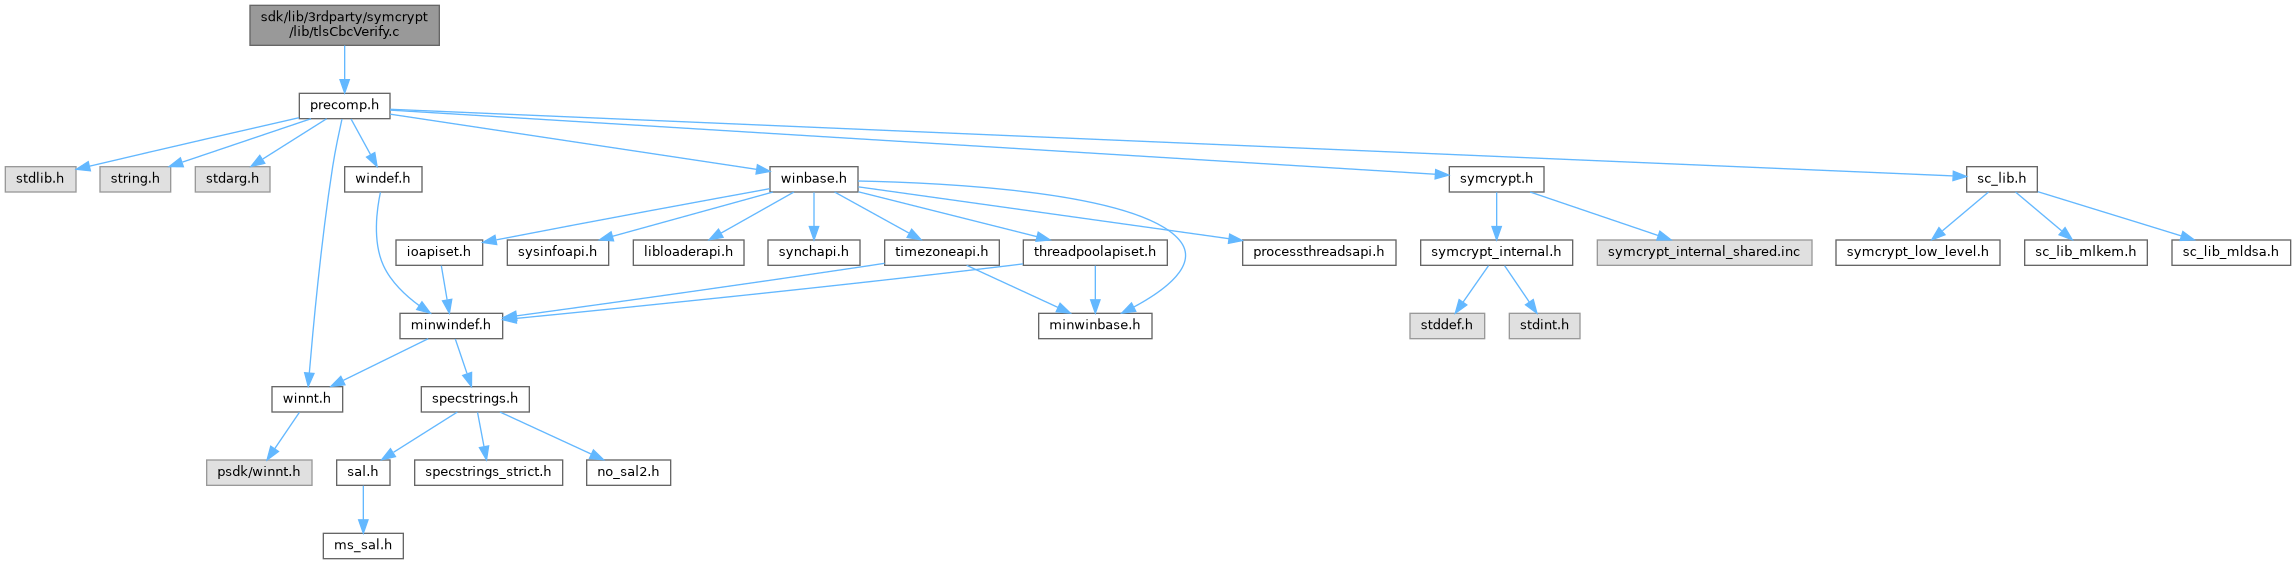
Go to the source code of this file.
Macros | |
| #define | NATIVE_01 (0x01010101) |
| #define | MASK32_LT(_a, _b) ((UINT32)( ( (INT32)((_a)-(_b)) ) >> 31 ) ) |
| #define | MASK32_EQ(_a, _b) (~(UINT32)(-(INT32)((_a) ^ (_b)) >> 31)) |
| #define | MASKNB_INWORD_RELEVANTBITS (~(NATIVE_BYTES - 1) & 0x0fffffff) |
| #define | MASKNB_BROADCAST(_b) ((NATIVE_UINT)(_b) * NATIVE_01) |
Functions | |
| FORCEINLINE NATIVE_UINT | SymCryptNMaskGe (UINT32 wordStart, UINT32 boundary) |
| FORCEINLINE NATIVE_UINT | SymCryptNMaskEq (UINT32 wordStart, UINT32 boundary) |
| FORCEINLINE NATIVE_UINT | SymCryptNMaskEq80 (UINT32 wordStart, UINT32 boundary) |
| SYMCRYPT_ERROR SYMCRYPT_CALL | SymCryptTlsCbcHmacVerifyCore (_In_ PCSYMCRYPT_HASH pHash, _Inout_ PSYMCRYPT_COMMON_HASH_STATE pState, _In_reads_bytes_(cbData) PCBYTE pbData, SIZE_T cbData, _Inout_updates_(pHash->inputBlockSize/2) PBYTE pbMacValue, _Inout_updates_(pHash->resultSize) PBYTE pbHashResult, _Out_ PUINT32 pu32PaddingError) |
| SYMCRYPT_ERROR SYMCRYPT_CALL | SymCryptTlsCbcHmacVerify (_In_ PCSYMCRYPT_MAC pMacAlgorithm, _In_ PVOID pExpandedKey, _Inout_ PVOID pState, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData) |
Macro Definition Documentation
◆ MASK32_EQ
Definition at line 34 of file tlsCbcVerify.c.
◆ MASK32_LT
Definition at line 31 of file tlsCbcVerify.c.
◆ MASKNB_BROADCAST
| #define MASKNB_BROADCAST | ( | _b | ) | ((NATIVE_UINT)(_b) * NATIVE_01) |
Definition at line 49 of file tlsCbcVerify.c.
◆ MASKNB_INWORD_RELEVANTBITS
| #define MASKNB_INWORD_RELEVANTBITS (~(NATIVE_BYTES - 1) & 0x0fffffff) |
Definition at line 47 of file tlsCbcVerify.c.
◆ NATIVE_01
| #define NATIVE_01 (0x01010101) |
Definition at line 21 of file tlsCbcVerify.c.
Function Documentation
◆ SymCryptNMaskEq()
| FORCEINLINE NATIVE_UINT SymCryptNMaskEq | ( | UINT32 | wordStart, |
| UINT32 | boundary | ||
| ) |
Definition at line 76 of file tlsCbcVerify.c.
78{
79 INT32 diff32;
80 NATIVE_UINT inWord;
81
82 // 32-bit signed difference
84
85 // inWord = (-1) if boundary is within the word, 0 otherwise
86 // Cast to NATIVE_UINT is free on AMD64, as is subsequent cast to NATIVE_INT
87 // A direct cast from INT32 to NATIVE_INT requires a sign extension instruction, so this is faster.
88 inWord = ~ ((-(NATIVE_INT)(NATIVE_UINT)(diff32 & MASKNB_INWORD_RELEVANTBITS)) >> (NATIVE_BITS -1));
89
91}
◆ SymCryptNMaskEq80()
| FORCEINLINE NATIVE_UINT SymCryptNMaskEq80 | ( | UINT32 | wordStart, |
| UINT32 | boundary | ||
| ) |
Definition at line 95 of file tlsCbcVerify.c.
97{
98 INT32 diff32;
99 NATIVE_UINT inWord;
100
101 // 32-bit signed difference
103
104 // inWord = (-1) if boundary is within the word, 0 otherwise
105 inWord = ~ ((-(NATIVE_INT)(NATIVE_UINT)(diff32 & MASKNB_INWORD_RELEVANTBITS)) >> (NATIVE_BITS -1));
106
108}
Referenced by SymCryptTlsCbcHmacVerifyCore().
◆ SymCryptNMaskGe()
| FORCEINLINE NATIVE_UINT SymCryptNMaskGe | ( | UINT32 | wordStart, |
| UINT32 | boundary | ||
| ) |
Definition at line 53 of file tlsCbcVerify.c.
55{
56 INT32 diff32;
57 NATIVE_INT anySet;
59
60 // Mask that is -1 if boundary < wordStart + 8
62
63 // Compute the index of boundary into the word, possibly negative
65 // Compute the necessary shift when the result will be partially set
67
68 // Mask the shift to 0 if the word is to be all set as boundary < wordStart
70
72}
Referenced by SymCryptTlsCbcHmacVerifyCore().
◆ SymCryptTlsCbcHmacVerify()
| SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptTlsCbcHmacVerify | ( | _In_ PCSYMCRYPT_MAC | pMacAlgorithm, |
| _In_ PVOID | pExpandedKey, | ||
| _Inout_ PVOID | pState, | ||
| _In_reads_(cbData) PCBYTE | pbData, | ||
| SIZE_T | cbData | ||
| ) |
Definition at line 403 of file tlsCbcVerify.c.
409{
410 BYTE abMacValue[64];
411 BYTE abHashResult[48];
412 UINT32 u32PaddingError;
416
418 pMacAlgorithm == SymCryptHmacSha256Algorithm ||
419 pMacAlgorithm == SymCryptHmacSha384Algorithm );
420 SYMCRYPT_ASSERT(((*(pMacAlgorithm->ppHashAlgorithm))->inputBlockSize)/2 <= 64);
421 SYMCRYPT_ASSERT((*(pMacAlgorithm->ppHashAlgorithm))->resultSize <= 48);
422
424 pHashAlgorithm,
425 pHashState,
426 pbData,
427 cbData,
428 abMacValue,
429 abHashResult,
430 &u32PaddingError );
431
432 // We have the hash value, convert it to a MAC value
433 // First we set up the chaining value
436 pHashAlgorithm->chainSize );
437 // Then copy the data & set the length
438 // The hash result wasn't BSWAPPED yet...
439 if( pMacAlgorithm->resultSize <= 32 )
440 {
441 SymCryptUint32ToMsbFirst( (UINT32 *) abHashResult, pHashState->buffer, pHashAlgorithm->resultSize / 4 );
442 } else {
443 SymCryptUint64ToMsbFirst( (UINT64 *) abHashResult, pHashState->buffer, pHashAlgorithm->resultSize / 8 );
444 }
445 pHashState->bytesInBuffer = pHashAlgorithm->resultSize;
447
448 (*pHashAlgorithm->resultFunc)( pHashState, abHashResult );
449
450 // Verify in 32-bit chunks to support SHA-1 without further problems
452 {
454 }
455
456 // We may reveal the final error-or-no-error as that will be visible anyway
457 return u32PaddingError == 0 ? SYMCRYPT_NO_ERROR : SYMCRYPT_AUTHENTICATION_FAILURE;
458}
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble const GLfloat const GLdouble const GLfloat GLint i
Definition: glfuncs.h:248
FORCEINLINE VOID SYMCRYPT_CALL SymCryptUint32ToMsbFirst(_In_reads_(cuData) PCUINT32 puData, _Out_writes_(4 *cuData) PBYTE pbResult, SIZE_T cuData)
Definition: sc_lib.h:405
FORCEINLINE VOID SYMCRYPT_CALL SymCryptUint64ToMsbFirst(_In_reads_(cuData) PCUINT64 puData, _Out_writes_(8 *cuData) PBYTE pbResult, SIZE_T cuData)
Definition: sc_lib.h:576
const PCSYMCRYPT_MAC SymCryptHmacSha256Algorithm
Definition: hmacsha256.c:29
const PCSYMCRYPT_MAC SymCryptHmacSha384Algorithm
Definition: hmacsha384.c:31
SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptTlsCbcHmacVerifyCore(_In_ PCSYMCRYPT_HASH pHash, _Inout_ PSYMCRYPT_COMMON_HASH_STATE pState, _In_reads_bytes_(cbData) PCBYTE pbData, SIZE_T cbData, _Inout_updates_(pHash->inputBlockSize/2) PBYTE pbMacValue, _Inout_updates_(pHash->resultSize) PBYTE pbHashResult, _Out_ PUINT32 pu32PaddingError)
Definition: tlsCbcVerify.c:113
◆ SymCryptTlsCbcHmacVerifyCore()
| SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptTlsCbcHmacVerifyCore | ( | _In_ PCSYMCRYPT_HASH | pHash, |
| _Inout_ PSYMCRYPT_COMMON_HASH_STATE | pState, | ||
| _In_reads_bytes_(cbData) PCBYTE | pbData, | ||
| SIZE_T | cbData, | ||
| _Inout_updates_(pHash->inputBlockSize/2) PBYTE | pbMacValue, | ||
| _Inout_updates_(pHash->resultSize) PBYTE | pbHashResult, | ||
| _Out_ PUINT32 | pu32PaddingError | ||
| ) |
Definition at line 113 of file tlsCbcVerify.c.
126{
127 SYMCRYPT_ERROR scError = SYMCRYPT_NO_ERROR;
128
129 UINT32 cbPad;
130 UINT32 maxPadLength;
134 UINT32 iMacStart;
135 NATIVE_UINT mInData;
136 NATIVE_UINT mInMac;
137 NATIVE_UINT mInPadding;
141 UINT32 cbHashPrefix;
142 UINT32 cbExtendedData;
143 UINT32 totalBytesHashed;
144 UINT32 hashPaddingFinal;
145 UINT32 resultHashBlockIndex;
146 UINT32 lastHashBlockIndex;
149 UINT32 backOffset;
150 NATIVE_UINT * bufferLocation;
151 NATIVE_UINT padBytes;
152 UINT32 m32ResultBlock;
153 NATIVE_UINT mResultBlock;
154 SIZE_T tmp;
156
158
159 // Process all the data up to the part where the MAC value might appear
160 // The if() is safe as both cbData and u32 are public values.
161 u32 = pHash->resultSize + 256;
163 {
167 }
168
169 // Check that we have enough data for a valid record.
170 // We need one MAC value plus one padding_length byte
172 {
173 scError = SYMCRYPT_BUFFER_TOO_SMALL;
175 }
176
177 // We OR our results into the result buffers, so we must init them to zero
178 SymCryptWipe( pbMacValue, cbMacValue );
179 SymCryptWipe( pbHashResult, pHash->resultSize );
180
181 // Pick up the padding_length. Note that this is the value we have to keep secret from
182 // side-channel attacks.
184
185 // We reduce cbData so that the padding_length byte is no longer under consideration.
186 cbData -= 1;
187
188 // Bound the padding length to cbData - mac_length
189 // This doesn't reveal data as we treat all cbPad values the same, but it makes our
190 // further computations easier
193 cbPad = cbPad + ((maxPadLength - cbPad) & u32);
195
196 // From here on out we maintain indices into a conceptual extended buffer with length cbExtendedData,
197 // and index 0 at the start of the hash computation.
198 // This aligns us with the hash input block, and simplifies hash padding computations and word
199 // accesses.
200 // However, we must always subtract cbHashPrefix from indices before using them to access bytes
201 // in pbData, as the HashPrefix was already hashed into the MAC state.
202
204 cbExtendedData = (UINT32)cbData + cbHashPrefix; // total # bytes that the conceptual extended buffer has
206
207 totalBytesHashed = cbExtendedData - pHash->resultSize - cbPad;
208 SYMCRYPT_STORE_MSBFIRST32( &hashPaddingFinal, totalBytesHashed * 8 ); // Length padding for result hash block
209
210 // We need to figure out what the index is of the last hash input block in the computation
211 // (including any phantom blocks after the actual hash is done) and the index of the result
212 // hash block of the actual hash computation.
213 // We've limited the max input for simplicity (everything fits in 32 bits)
214 // We also avoid 64-bit operations as their implementation on 32-bit architectures might not
215 // always be constant-time.
216 // This computation works for SHA-1, SHA-256, and SHA-384 which is all we care about
217 // We avoid using % as the runtime isn't constant and our inputs are secret.
218
219 // First the actual # bytes in the real and phantom computation
220 resultHashBlockIndex = totalBytesHashed + 1 + pHash->inputBlockSize / 8; // 1 byte 0x80 + length padding in last block
221 lastHashBlockIndex = resultHashBlockIndex + cbPad; // The furthest any hash could go
222
223 // round up to a whole # blocks
224 resultHashBlockIndex = (resultHashBlockIndex + pHash->inputBlockSize - 1) & ~(pHash->inputBlockSize - 1);
225 lastHashBlockIndex = (lastHashBlockIndex + pHash->inputBlockSize - 1) & ~(pHash->inputBlockSize - 1);
226
227 // Compute the indices where the MAC and padding start
228 iPaddingStart = cbExtendedData - cbPad;
229 iMacStart = iPaddingStart - pHash->resultSize;
230
232
233 // Align our handling to the native word size so that we can safely use native words
235 {
237
238 // Process a partial word
240
241 // Read a word; as the MAC value is > 8 bytes this won't overflow the buffer
244 mInData = ~m;
245 mInMac = m;
246
249
250 // Now we put the data into the hash buffer
252 *bufferLocation = (*bufferLocation & (((NATIVE_UINT)1 << 8*backOffset) - 1)) | (data << 8*backOffset);
254
255 // And the MAC data in the mac buffer
256 *(NATIVE_UINT *)&pbMacValue[(next - backOffset) & (cbMacValue - 1)] |= (w & mInMac) << 8*backOffset;
257
259 {
260 // Block is full. This can't be the result block as we didn't have room for the padding yet.
261 (*pHash->appendBlockFunc)( (PBYTE)pState + pHash->chainOffset, &pState->buffer[0], pHash->inputBlockSize, &tmp );
262 pState->bytesInBuffer = 0;
263 }
264
266 }
267
268 padBytes = MASKNB_BROADCAST( cbPad );
269
270 // Now we can loop over the data in whole words
272 {
274
276 mInMac = m;
277 mInData = ~m;
278
280 mInPadding = m;
281 mInMac &= ~m;
282
285
288
290 {
291 // Insert the length component of the hash padding (only in result block)
294
295 (*pHash->appendBlockFunc)( (PBYTE)pState + pHash->chainOffset, &pState->buffer[0], pHash->inputBlockSize, &tmp );
296 SYMCRYPT_ASSERT( tmp == 0 );
297
298 mResultBlock = (NATIVE_UINT)(NATIVE_INT)(INT32) m32ResultBlock; // Convert 32-bit mask to native mask
299
300 // Masked copy of result to result buffer
301 // We do whole words, and then an optional UINT32 to handle the 20-byte SHA-1 result on AMD64.
302 // The for() and if() are side-channel safe as the resultSize and NATIVE_BYTES values are public.
304 {
305 ((NATIVE_UINT *)pbHashResult)[i] |= ((NATIVE_UINT *)((PBYTE)pState + pHash->chainOffset))[i] & mResultBlock;
306 }
308 {
309 *(UINT32 *) (&pbHashResult[ pHash->resultSize - 4 ]) |= *(UINT32 *) ((PBYTE) pState + pHash->chainOffset + pHash->resultSize - 4) & (UINT32) mResultBlock;
310 }
311 pState->bytesInBuffer = 0;
312 }
313
315
316 nPaddingError |= (w ^ padBytes) & mInPadding;
317
319 }
320
322 {
323 // Process the remaining bytes. This can't be data so we only do the MAC and padding...
324 // The main difference is that we read the last full word in pbData and then align it
325 // as if we read the next word starting at pbData[next - cbHashPrefix]
329
331 mInPadding = m;
332 mInMac = ~m;
333
335
336 nPaddingError |= (w ^ padBytes) & mInPadding;
337 next = cbExtendedData;
338 }
339
340 // At this point we still have to potentially do one more hash block.
341 // The data is all copied into the hash input buffer, as is the 0x80 padding byte.
342
344 {
345 // there is still one more hash block to compute. This could either be the actual last block of the hash
346 // computation, or a phantom block for side-channel hiding.
347 // This IF depends only on the cbData, the # bytes hashed before this final pbData buffer, and the hash algorithm
348 // properties.
349 // We never need to compute more than 1 additional hash block as we are at least pHash->resultSize bytes beyond the
350 // actual data.
351 SymCryptWipe( &pState->buffer[ pState->bytesInBuffer], pHash->inputBlockSize - pState->bytesInBuffer );
352
353 // Just put in the padding, no need to mask this
355
356 (*pHash->appendBlockFunc)( (PBYTE)pState + pHash->chainOffset, &pState->buffer[0], pHash->inputBlockSize, &tmp );
357 SYMCRYPT_ASSERT( tmp == 0 );
358
359 // Masked copy of the result
360 mResultBlock = (NATIVE_UINT)(NATIVE_INT)(INT32) MASK32_EQ( lastHashBlockIndex, resultHashBlockIndex );
361
362 // Masked copy of result to result buffer
363 // We do whole words, and then an optional UINT32 to handle the 20-byte SHA-1 result on AMD64.
365 {
366 ((NATIVE_UINT *)pbHashResult)[i] |= ((NATIVE_UINT *)((PBYTE)pState + pHash->chainOffset))[i] & mResultBlock;
367 }
369 {
370 *(UINT32 *) (&pbHashResult[ pHash->resultSize - 4 ]) |= *(UINT32 *) ((PBYTE) pState + pHash->chainOffset + pHash->resultSize - 4) & (UINT32) mResultBlock;
371 }
372 pState->bytesInBuffer = 0;
373 }
374
375 // Now we have the hash result, and the Mac value buffer is filled with a rotated copy of the Mac value.
376 // We have to un-rotate the Mac value.
377
378 // Check that we have the right hash result
379 //for( SIZE_T t=0; t < cbMacValue; t++ )
380 //{
381 // SYMCRYPT_ASSERT( pbMacValue[ (iMacStart + t) & (cbMacValue - 1 ) ] == (t >= pHash->resultSize ? 0 : pbData[iMacStart - cbHashPrefix + t] ));
382 //}
383
384 SymCryptScsRotateBuffer( pbMacValue, cbMacValue, iMacStart & (cbMacValue - 1) );
385
386 //for( SIZE_T t=0; t < cbMacValue; t++ )
387 //{
388 // SYMCRYPT_ASSERT( pbMacValue[ t ] == (t >= pHash->resultSize ? 0 : pbData[iMacStart - cbHashPrefix + t] ));
389 //}
390
391cleanup:
392
394
395 *pu32PaddingError = (UINT32) nPaddingError;
396
397 return scError;
398}
VOID SYMCRYPT_CALL SymCryptWipe(_Out_writes_bytes_(cbData) PVOID pbData, SIZE_T cbData)
Definition: libmain.c:137
VOID SYMCRYPT_CALL SymCryptScsRotateBuffer(_Inout_updates_(cbBuffer) PBYTE pbBuffer, SIZE_T cbBuffer, SIZE_T lshift)
Definition: scsTools.c:179
SIZE_T SYMCRYPT_CALL SymCryptRoundUpPow2Sizet(SIZE_T v)
Definition: scsTools.c:76
FORCEINLINE NATIVE_UINT SymCryptNMaskEq80(UINT32 wordStart, UINT32 boundary)
Definition: tlsCbcVerify.c:95
FORCEINLINE NATIVE_UINT SymCryptNMaskGe(UINT32 wordStart, UINT32 boundary)
Definition: tlsCbcVerify.c:53
Referenced by SymCryptTlsCbcHmacVerify().
