ReactOS 0.4.17-dev-1005-g171e1de
3des.c File Reference
#include "precomp.h"
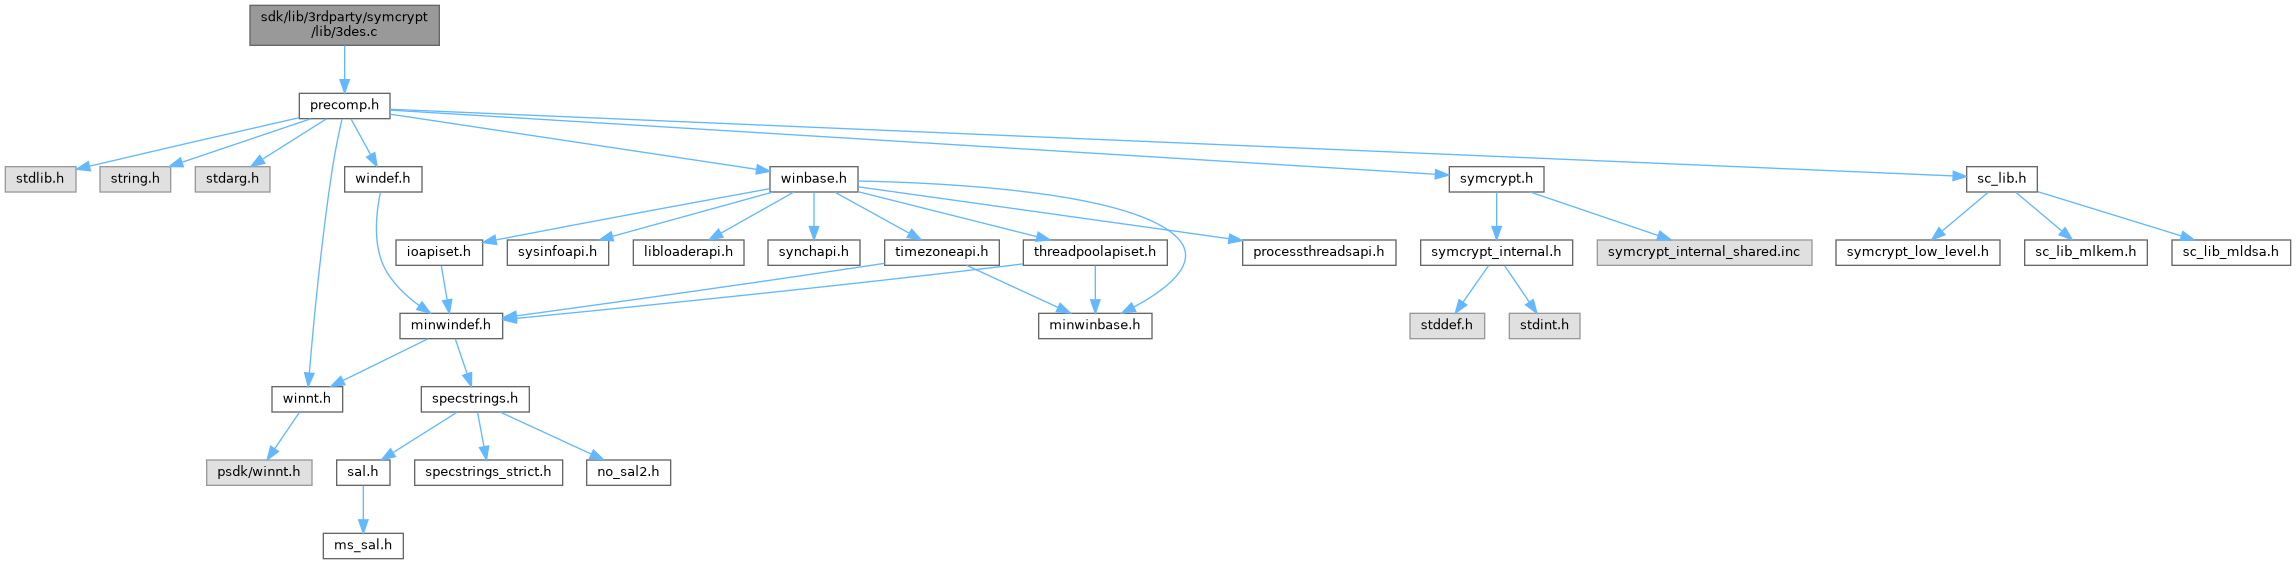
Include dependency graph for 3des.c:

Go to the source code of this file.

Macros

#define SWAP_BITS_WITHIN_UINT32(_value, _shift, _mask)
 
#define SWAP_BITS_BETWEEN_UINT32(_v1, _v2, _shift, _mask)
 
#define F(L, R, keyptr)
 

Functions

 SYMCRYPT_ALIGN_AT (256) const
 
SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptDesExpandKey (_Out_ PSYMCRYPT_DES_EXPANDED_KEY pExpandedKey, _In_reads_(cbKey) PCBYTE pbKey, SIZE_T cbKey)
 
VOID SYMCRYPT_CALL SymCryptDesEncrypt (_In_ PCSYMCRYPT_DES_EXPANDED_KEY pExpandedKey, _In_reads_(SYMCRYPT_DES_BLOCK_SIZE) PCBYTE pbSrc, _Out_writes_(SYMCRYPT_DES_BLOCK_SIZE) PBYTE pbDst)
 
VOID SYMCRYPT_CALL SymCryptDesDecrypt (_In_ PCSYMCRYPT_DES_EXPANDED_KEY pExpandedKey, _In_reads_(SYMCRYPT_DES_BLOCK_SIZE) PCBYTE pbSrc, _Out_writes_(SYMCRYPT_DES_BLOCK_SIZE) PBYTE pbDst)
 
VOID SYMCRYPT_CALL SymCrypt3DesCbcEncrypt (_In_ PCSYMCRYPT_3DES_EXPANDED_KEY pExpandedKey, _Inout_updates_(SYMCRYPT_3DES_BLOCK_SIZE) PBYTE pbChainingValue, _In_reads_(cbData) PCBYTE pbSrc, _Out_writes_(cbData) PBYTE pbDst, SIZE_T cbData)
 
VOID SYMCRYPT_CALL SymCrypt3DesCbcDecrypt (_In_ PCSYMCRYPT_3DES_EXPANDED_KEY pExpandedKey, _Inout_updates_(SYMCRYPT_3DES_BLOCK_SIZE) PBYTE pbChainingValue, _In_reads_(cbData) PCBYTE pbSrc, _Out_writes_(cbData) PBYTE pbDst, SIZE_T cbData)
 
VOID SYMCRYPT_CALL SymCryptDesExpandSingleKey (_Out_writes_bytes_(128) UINT32 expandedKeyTable[16][2], _In_reads_(8) PCBYTE pKey)
 
SYMCRYPT_NOINLINE SYMCRYPT_ERROR SYMCRYPT_CALL SymCrypt3DesExpandKey (_Out_ PSYMCRYPT_3DES_EXPANDED_KEY pExpandedKey, _In_reads_(cbKey) PCBYTE pbKey, SIZE_T cbKey)
 
SYMCRYPT_NOINLINE VOID SYMCRYPT_CALL SymCrypt3DesEncrypt (_In_ PCSYMCRYPT_3DES_EXPANDED_KEY pExpandedKey, _In_reads_(SYMCRYPT_3DES_BLOCK_SIZE) PCBYTE pbSrc, _Out_writes_(SYMCRYPT_3DES_BLOCK_SIZE) PBYTE pbDst)
 
SYMCRYPT_NOINLINE VOID SYMCRYPT_CALL SymCrypt3DesDecrypt (_In_ PCSYMCRYPT_3DES_EXPANDED_KEY pExpandedKey, _In_reads_(SYMCRYPT_3DES_BLOCK_SIZE) PCBYTE pbSrc, _Out_writes_(SYMCRYPT_3DES_BLOCK_SIZE) PBYTE pbDst)
 
VOID SYMCRYPT_CALL SymCryptDesSetOddParity (_Inout_updates_(cbData) PBYTE pbData, _In_ SIZE_T cbData)
 
VOID SYMCRYPT_CALL SymCryptDesSelftest (void)
 
VOID SYMCRYPT_CALL SymCrypt3DesSelftest (void)
 

Variables

const SYMCRYPT_BLOCKCIPHER SymCrypt3DesBlockCipher_default
 
const SYMCRYPT_BLOCKCIPHER SymCryptDesBlockCipher_default
 
const PCSYMCRYPT_BLOCKCIPHER SymCrypt3DesBlockCipher = &SymCrypt3DesBlockCipher_default
 
const PCSYMCRYPT_BLOCKCIPHER SymCryptDesBlockCipher = &SymCryptDesBlockCipher_default
 
static const BYTE SP800_67Key [24]
 
static const BYTE des3KnownPlaintext [8]
 
static const BYTE des3KnownCiphertext [8]
 
static const BYTE desKnownCiphertext [8]
 

Macro Definition Documentation

◆ F

#define F (   L,
  R,
  keyptr 
)
Value:
{ \
Ta = keyptr[0] ^ R; \
Tb = keyptr[1] ^ R; \
Tb = ROR32(Tb, 4); \
L ^= *(UINT32 *)((PBYTE)SymCryptDesSpbox[0] + ( Ta & 0xfc)); \
L ^= *(UINT32 *)((PBYTE)SymCryptDesSpbox[1] + ( Tb & 0xfc)); \
L ^= *(UINT32 *)((PBYTE)SymCryptDesSpbox[2] + ((Ta>> 8)& 0xfc)); \
L ^= *(UINT32 *)((PBYTE)SymCryptDesSpbox[3] + ((Tb>> 8)& 0xfc)); \
L ^= *(UINT32 *)((PBYTE)SymCryptDesSpbox[4] + ((Ta>>16)& 0xfc)); \
L ^= *(UINT32 *)((PBYTE)SymCryptDesSpbox[5] + ((Tb>>16)& 0xfc)); \
L ^= *(UINT32 *)((PBYTE)SymCryptDesSpbox[6] + ((Ta>>24)& 0xfc)); \
L ^= *(UINT32 *)((PBYTE)SymCryptDesSpbox[7] + ((Tb>>24)& 0xfc)); }
static PTUNNEL Tb
Definition: FsRtlTunnel.c:26
@ R
Definition: bidi.c:79
#define L(x)
Definition: resources.c:13
BYTE * PBYTE
Definition: pedump.c:66
uint32_t UINT32
Definition: typedefs.h:59

Definition at line 335 of file 3des.c.

◆ SWAP_BITS_BETWEEN_UINT32

#define SWAP_BITS_BETWEEN_UINT32 (   _v1,
  _v2,
  _shift,
  _mask 
)
Value:
{ \
UINT32 _tmp; \
_tmp = ((_v1) ^ ((_v2) >> (_shift))) & (_mask); \
_v1 ^= _tmp; \
_v2 ^= (_tmp << (_shift )); \
}

◆ SWAP_BITS_WITHIN_UINT32

#define SWAP_BITS_WITHIN_UINT32 (   _value,
  _shift,
  _mask 
)
Value:
{ \
UINT32 _tmp; \
_tmp = ((_value) ^ ((_value) >> (_shift))) & (_mask ); \
_value = (_value) ^ _tmp ^ (_tmp << (_shift)); \
}

Function Documentation

◆ SymCrypt3DesCbcDecrypt()

VOID SYMCRYPT_CALL SymCrypt3DesCbcDecrypt ( _In_ PCSYMCRYPT_3DES_EXPANDED_KEY  pExpandedKey,
_Inout_updates_(SYMCRYPT_3DES_BLOCK_SIZE) PBYTE  pbChainingValue,
_In_reads_(cbData) PCBYTE  pbSrc,
_Out_writes_(cbData) PBYTE  pbDst,
SIZE_T  cbData 
)

Definition at line 180 of file 3des.c.

186{
189}
const PCSYMCRYPT_BLOCKCIPHER SymCrypt3DesBlockCipher
Definition: 3des.c:75
#define SYMCRYPT_ASSERT(_x)
Definition: symcrypt.h:10807
#define SYMCRYPT_3DES_BLOCK_SIZE
Definition: symcrypt.h:4440
VOID SYMCRYPT_CALL SymCryptCbcDecrypt(_In_ PCSYMCRYPT_BLOCKCIPHER pBlockCipher, _In_ PCVOID pExpandedKey, _Inout_updates_(pBlockCipher->blockSize) PBYTE pbChainingValue, _In_reads_(cbData) PCBYTE pbSrc, _Out_writes_(cbData) PBYTE pbDst, SIZE_T cbData)
PBYTE pbChainingValue
PCBYTE pbSrc
PCBYTE PBYTE SIZE_T cbData
PCBYTE PBYTE pbDst
PCVOID pExpandedKey

◆ SymCrypt3DesCbcEncrypt()

VOID SYMCRYPT_CALL SymCrypt3DesCbcEncrypt ( _In_ PCSYMCRYPT_3DES_EXPANDED_KEY  pExpandedKey,
_Inout_updates_(SYMCRYPT_3DES_BLOCK_SIZE) PBYTE  pbChainingValue,
_In_reads_(cbData) PCBYTE  pbSrc,
_Out_writes_(cbData) PBYTE  pbDst,
SIZE_T  cbData 
)

Definition at line 167 of file 3des.c.

173{
176}
VOID SYMCRYPT_CALL SymCryptCbcEncrypt(_In_ PCSYMCRYPT_BLOCKCIPHER pBlockCipher, _In_ PCVOID pExpandedKey, _Inout_updates_(pBlockCipher->blockSize) PBYTE pbChainingValue, _In_reads_(cbData) PCBYTE pbSrc, _Out_writes_(cbData) PBYTE pbDst, SIZE_T cbData)

◆ SymCrypt3DesDecrypt()

SYMCRYPT_NOINLINE VOID SYMCRYPT_CALL SymCrypt3DesDecrypt ( _In_ PCSYMCRYPT_3DES_EXPANDED_KEY  pExpandedKey,
_In_reads_(SYMCRYPT_3DES_BLOCK_SIZE) PCBYTE  pbSrc,
_Out_writes_(SYMCRYPT_3DES_BLOCK_SIZE) PBYTE  pbDst 
)

Definition at line 478 of file 3des.c.

482{
483 UINT32 L, R, Ta, Tb;
484 int r;
485
487
490
491 R = ROL32(R, 4);
492 Ta = (L ^ R) & 0xf0f0f0f0;
493 L ^= Ta;
494 R ^= Ta;
495
496 L = ROL32(L, 20);
497 Ta = (L ^ R) & 0xfff0000f;
498 L ^= Ta;
499 R ^= Ta;
500
501 L = ROL32(L, 14);
502 Ta = (L ^ R) & 0x33333333;
503 L ^= Ta;
504 R ^= Ta;
505
506 R = ROL32(R, 22);
507 Ta = (L ^ R) & 0x03fc03fc;
508 L ^= Ta;
509 R ^= Ta;
510
511 R = ROL32(R, 9);
512 Ta = (L ^ R) & 0xaaaaaaaa;
513 L ^= Ta;
514 R ^= Ta;
515
516 L = ROL32(L, 1);
517
518
519 // Decrypt with key 2
520 for( r=14; r>=0; r -= 2 )
521 {
522 F( L, R, pExpandedKey->roundKey[2][r+1] );
523 F( R, L, pExpandedKey->roundKey[2][r ] );
524 }
525
526 // Encrypt with key 1
527 for( r=0; r<16; r += 2 )
528 {
529 F( R, L, pExpandedKey->roundKey[1][r ] );
530 F( L, R, pExpandedKey->roundKey[1][r+1] );
531 }
532
533 // Decrypt with key 0
534 for( r=14; r>=0; r -= 2 )
535 {
536 F( L, R, pExpandedKey->roundKey[0][r+1] );
537 F( R, L, pExpandedKey->roundKey[0][r ] );
538 }
539
540 /* Inverse permutation, also from Hoey via Outerbridge and Schneier */
541
542 R = ROR32(R, 1);
543 Ta = (L ^ R) & 0xaaaaaaaa;
544 L ^= Ta;
545 R ^= Ta;
546
547 L = ROR32(L, 9);
548 Ta = (L ^ R) & 0x03fc03fc;
549 L ^= Ta;
550 R ^= Ta;
551
552 L = ROR32(L, 22);
553 Ta = (L ^ R) & 0x33333333;
554 L ^= Ta;
555 R ^= Ta;
556
557 R = ROR32(R, 14);
558 Ta = (L ^ R) & 0xfff0000f;
559 L ^= Ta;
560 R ^= Ta;
561
562 R = ROR32(R, 20);
563 Ta = (L ^ R) & 0xf0f0f0f0;
564 L ^= Ta;
565 R ^= Ta;
566
567 L = ROR32(L, 4);
568
571}
#define F(L, R, keyptr)
Definition: 3des.c:335
GLdouble GLdouble GLdouble r
Definition: gl.h:2055
#define SYMCRYPT_LOAD_LSBFIRST32(p)
Definition: symcrypt.h:299
#define SYMCRYPT_STORE_LSBFIRST32(p, v)
Definition: symcrypt.h:307
#define SYMCRYPT_CHECK_MAGIC(p)

Referenced by decrypt_block_impl(), SymCrypt3DesSelftest(), and SymCryptDesDecrypt().

◆ SymCrypt3DesEncrypt()

SYMCRYPT_NOINLINE VOID SYMCRYPT_CALL SymCrypt3DesEncrypt ( _In_ PCSYMCRYPT_3DES_EXPANDED_KEY  pExpandedKey,
_In_reads_(SYMCRYPT_3DES_BLOCK_SIZE) PCBYTE  pbSrc,
_Out_writes_(SYMCRYPT_3DES_BLOCK_SIZE) PBYTE  pbDst 
)

Definition at line 358 of file 3des.c.

362{
363 UINT32 L, R, Ta, Tb;
364 int r;
365
367
370
371 //
372 // Hoey's wonderful initial permutation algorithm, from Outerbridge
373 // (see Schneier p 478)
374 //
375 // The algorithm we use is derived (through several intermediate forms) from the mentioned source.
376 // But the algorithm cannot be copyrighted, only patented, and if there were any patents
377 // they have expired by now.
378 // The expression of the algorithm in code is purely MS generated,
379 // within the confines of implementing the algorithm in the best way such that even a simple
380 // compiler will create good code.
381 //
382
383 R = ROL32(R, 4);
384 Ta = (L ^ R) & 0xf0f0f0f0;
385 L ^= Ta;
386 R ^= Ta;
387
388 L = ROL32(L, 20);
389 Ta = (L ^ R) & 0xfff0000f;
390 R ^= Ta;
391 L ^= Ta;
392
393 L = ROL32(L,14);
394 Ta = (L ^ R) & 0x33333333;
395 R ^= Ta;
396 L ^= Ta;
397
398 R = ROL32(R, 22);
399 Ta = (L ^ R) & 0x03fc03fc;
400 R ^= Ta;
401 L ^= Ta;
402
403 R = ROL32(R, 9);
404 Ta = (L ^ R) & 0xaaaaaaaa;
405 R ^= Ta;
406 L ^= Ta;
407
408 L = ROL32(L, 1);
409
410 //
411 // First: encryption
412 //
413 for( r=0; r<16; r += 2 )
414 {
415 F( L, R, pExpandedKey->roundKey[0][r ] );
416 F( R, L, pExpandedKey->roundKey[0][r+1] );
417 }
418
419 //
420 // Second: decryption
421 // Note that L and R are swapped here, and the round counter counts down.
422 //
423 for( r=14; r>=0; r -= 2 )
424 {
425 F( R, L, pExpandedKey->roundKey[1][r+1] );
426 F( L, R, pExpandedKey->roundKey[1][r ] );
427 }
428
429 //
430 // Third: encryption
431 //
432 for( r=0; r<16; r += 2 )
433 {
434 F( L, R, pExpandedKey->roundKey[2][r ] );
435 F( R, L, pExpandedKey->roundKey[2][r+1] );
436 }
437
438 R = ROR32(R, 1);
439 Ta = (L ^ R) & 0xaaaaaaaa;
440 R ^= Ta;
441 L ^= Ta;
442
443 L = ROR32(L, 9);
444 Ta = (L ^ R) & 0x03fc03fc;
445 R ^= Ta;
446 L ^= Ta;
447
448 L = ROR32(L, 22);
449 Ta = (L ^ R) & 0x33333333;
450 R ^= Ta;
451 L ^= Ta;
452
453 R = ROR32(R, 14);
454 Ta = (L ^ R) & 0xfff0000f;
455 R ^= Ta;
456 L ^= Ta;
457
458 R = ROR32(R, 20);
459 Ta = (L ^ R) & 0xf0f0f0f0;
460 R ^= Ta;
461 L ^= Ta;
462
463 L = ROR32(L, 4);
464
467}

Referenced by encrypt_block_impl(), SymCrypt3DesSelftest(), and SymCryptDesEncrypt().

◆ SymCrypt3DesExpandKey()

SYMCRYPT_NOINLINE SYMCRYPT_ERROR SYMCRYPT_CALL SymCrypt3DesExpandKey ( _Out_ PSYMCRYPT_3DES_EXPANDED_KEY  pExpandedKey,
_In_reads_(cbKey) PCBYTE  pbKey,
SIZE_T  cbKey 
)

Definition at line 295 of file 3des.c.

299{
300 SIZE_T keyIndex = 0;
301 int i;
302
303 if( cbKey != 8 && cbKey != 16 && cbKey != 24 )
304 {
305 return SYMCRYPT_WRONG_KEY_SIZE;
306 }
307
308 //
309 // A loop that goes over the provided key as a circular buffer provides
310 // the right result with the least complexity.
311 // This is inefficient for the cases cbKey=8 and cbKey=16, but those should
312 // not be used anyway.
313 //
314 for( i=0; i<3; i++ )
315 {
316 SYMCRYPT_ASSERT( keyIndex <= cbKey - 8 ); // help PreFast
317 SymCryptDesExpandSingleKey( pExpandedKey->roundKey[i], pbKey + keyIndex );
318 keyIndex = (keyIndex + 8) % cbKey;
319 }
320
322
323 return SYMCRYPT_NO_ERROR;
324}
VOID SYMCRYPT_CALL SymCryptDesExpandSingleKey(_Out_writes_bytes_(128) UINT32 expandedKeyTable[16][2], _In_reads_(8) PCBYTE pKey)
Definition: 3des.c:195
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble const GLfloat const GLdouble const GLfloat GLint i
Definition: glfuncs.h:248
PCBYTE pbKey
PCBYTE SIZE_T cbKey
#define SYMCRYPT_SET_MAGIC(p)
ULONG_PTR SIZE_T
Definition: typedefs.h:80

Referenced by setup_key_impl(), SymCrypt3DesSelftest(), and SymCryptDesExpandKey().

◆ SymCrypt3DesSelftest()

VOID SYMCRYPT_CALL SymCrypt3DesSelftest ( void  )

Definition at line 656 of file 3des.c.

657{
660
661 if( SymCrypt3DesExpandKey( &key, SP800_67Key, 24 ) != SYMCRYPT_NO_ERROR )
662 {
663 SymCryptFatal( 'des3' );
664 }
665
667
669
671 {
672 SymCryptFatal( 'des4' );
673 }
674
676
678
680 {
681 SymCryptFatal( 'des5' );
682 }
683}
static const BYTE des3KnownCiphertext[8]
Definition: 3des.c:613
static const BYTE SP800_67Key[24]
Definition: 3des.c:603
SYMCRYPT_NOINLINE VOID SYMCRYPT_CALL SymCrypt3DesEncrypt(_In_ PCSYMCRYPT_3DES_EXPANDED_KEY pExpandedKey, _In_reads_(SYMCRYPT_3DES_BLOCK_SIZE) PCBYTE pbSrc, _Out_writes_(SYMCRYPT_3DES_BLOCK_SIZE) PBYTE pbDst)
Definition: 3des.c:358
SYMCRYPT_NOINLINE SYMCRYPT_ERROR SYMCRYPT_CALL SymCrypt3DesExpandKey(_Out_ PSYMCRYPT_3DES_EXPANDED_KEY pExpandedKey, _In_reads_(cbKey) PCBYTE pbKey, SIZE_T cbKey)
Definition: 3des.c:295
static const BYTE des3KnownPlaintext[8]
Definition: 3des.c:609
SYMCRYPT_NOINLINE VOID SYMCRYPT_CALL SymCrypt3DesDecrypt(_In_ PCSYMCRYPT_3DES_EXPANDED_KEY pExpandedKey, _In_reads_(SYMCRYPT_3DES_BLOCK_SIZE) PCBYTE pbSrc, _Out_writes_(SYMCRYPT_3DES_BLOCK_SIZE) PBYTE pbDst)
Definition: 3des.c:478
_ACRTIMP int __cdecl memcmp(const void *, const void *, size_t)
Definition: string.c:2807
GLenum GLuint GLenum GLsizei const GLchar * buf
Definition: glext.h:7751
VOID SYMCRYPT_CALL SymCryptInjectError(PBYTE pbData, SIZE_T cbData)
Definition: copy.c:22
_Analysis_noreturn_ VOID SYMCRYPT_CALL SymCryptFatal(UINT32 fatalCode)
SYMCRYPT_MAGIC_FIELD SYMCRYPT_3DES_EXPANDED_KEY
unsigned char BYTE
Definition: xxhash.c:193

◆ SYMCRYPT_ALIGN_AT()

SYMCRYPT_ALIGN_AT ( 256  ) const

Definition at line 78 of file 3des.c.

90{ \
91 UINT32 _tmp; \
92 _tmp = ((_value) ^ ((_value) >> (_shift))) & (_mask ); \
93 _value = (_value) ^ _tmp ^ (_tmp << (_shift)); \
94}
95
96//
97// The SWAP_BITS_BETWEEN_UINT32 macro swaps bits between two UINT32 values
98// SWAP_BITS_BETWEEN_UINT32( _v1, _v2, _shift, _mask )
99// swaps bits in _v1 selected by _mask with bits in _v2 selected by _mask << _shift
100//
101
102#define SWAP_BITS_BETWEEN_UINT32( _v1, _v2, _shift, _mask ) \
103{ \
104 UINT32 _tmp; \
105 _tmp = ((_v1) ^ ((_v2) >> (_shift))) & (_mask); \
106 _v1 ^= _tmp; \
107 _v2 ^= (_tmp << (_shift )); \
108}
109
110//
111// For each round, a bit that states whether the key schedule shift registers are clocked twice
112// The data is straight from the standard.
113//
114static const BYTE SymCryptDesDoubleShift[16]={0,0,1,1,1,1,1,1,0,1,1,1,1,1,1,0};

◆ SymCryptDesDecrypt()

Definition at line 152 of file 3des.c.

156{
158}

Referenced by decrypt_block_impl(), SymCryptDesSelftest(), and SymCryptDesxDecrypt().

◆ SymCryptDesEncrypt()

Definition at line 142 of file 3des.c.

146{
148}

Referenced by encrypt_block_impl(), SymCryptDesSelftest(), and SymCryptDesxEncrypt().

◆ SymCryptDesExpandKey()

SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptDesExpandKey ( _Out_ PSYMCRYPT_DES_EXPANDED_KEY  pExpandedKey,
_In_reads_(cbKey) PCBYTE  pbKey,
SIZE_T  cbKey 
)

Definition at line 124 of file 3des.c.

128{
129 if( cbKey != 8 )
130 {
131 //
132 // cbKey should be a compile-time constant in most cases,
133 // so this should be optimized away
134 //
135 return SYMCRYPT_WRONG_KEY_SIZE;
136 }
137 return SymCrypt3DesExpandKey( &pExpandedKey->threeDes, pbKey, cbKey );
138}

Referenced by setup_key_impl(), SymCryptDesSelftest(), and SymCryptDesxExpandKey().

◆ SymCryptDesExpandSingleKey()

VOID SYMCRYPT_CALL SymCryptDesExpandSingleKey ( _Out_writes_bytes_(128) UINT32  expandedKeyTable[16][2],
_In_reads_(8) PCBYTE  pKey 
)

Definition at line 195 of file 3des.c.

198{
199 UINT32 Cr, Dr; // The C_r D_r values of FIPS 43 for round value r
200 UINT32 r; // round
201 UINT32 K1, K2; // round keys after the permuted choice 2
202 UINT32 tmp;
203
204 //
205 // We follow the FIPS 43 flow quite closely and have not optimized the key expansion much.
206 // Key expansion is not performance-critical.
207 //
208
209 // Load the key
211 Dr = SYMCRYPT_LOAD_LSBFIRST32( pKey + 4 );
212
213 //
214 // The Permuted Choice 1 can be done mostly with a sequence of bit swaps.
215 // The algorithm we use is derived from our earlier implementation and might potentially
216 // derive from an external source.
217 // But the algorithm cannot be copyrighted, only patented, and if there were any patents
218 // they have expired by now.
219 // The expression of the algorithm in code is purely MS generated, and so not encumbered
220 // by external copyrights.
221 // This algorithm is really just a transposition of the bits when viewed as an 8x8 matrix
222 // with an additional permutation on the output side.
223 //
224 SWAP_BITS_BETWEEN_UINT32( Cr, Dr, 4, 0x0f0f0f0f );
225 SWAP_BITS_WITHIN_UINT32( Dr, 18, 0x00003333 );
226 SWAP_BITS_WITHIN_UINT32( Cr, 18, 0x00003333 );
227 SWAP_BITS_BETWEEN_UINT32( Cr, Dr, 1, 0x55555555 );
228 SWAP_BITS_BETWEEN_UINT32( Dr, Cr, 8, 0x00ff00ff );
229 SWAP_BITS_BETWEEN_UINT32( Cr, Dr, 1, 0x55555555 );
230 SWAP_BITS_WITHIN_UINT32( Dr, 16, 0xff );
231
232 // Have to re-arrange C and D a tiny bit so that each contains 28 bits and we throw away 8 bits
233 Dr = (Dr & 0x00ffffff) | ((Cr & 0xf0000000 ) >> 4 );
234 Cr = (Cr & 0x0fffffff);
235
236 for( r = 0; r < 16; r++)
237 {
238 //
239 // Cr and Dr are the two key shift registers, they are rotated once or twice for each round.
240 //
241
242 if( SymCryptDesDoubleShift[ r ] ) {
243 Cr = ((Cr >> 2) | (Cr << 26));
244 Dr = ((Dr >> 2) | (Dr << 26));
245 } else {
246 Cr = ((Cr >> 1) | (Cr << 27));
247 Dr = ((Dr >> 1) | (Dr << 27));
248 }
249
250 Cr &= 0x0fffffff;
251 Dr &= 0x0fffffff;
252
253 //
254 // The Permuted Choice 2 is done using table lookups
255 // Not all bits of C and D are used, so we cut those out using shifts and masks,
256 // and then index 6 bits at a time into lookup tables that implement the bit relocation.
257 //
258
259 K1 = SymCryptDesKeySelect[0][ (Cr )&0x3f ] |
260 SymCryptDesKeySelect[1][((Cr >> 6)&0x03) | ((Cr >> 7)&0x3c)] |
261 SymCryptDesKeySelect[2][((Cr >> 13)&0x0f) | ((Cr >> 14)&0x30)] |
262 SymCryptDesKeySelect[3][((Cr >> 20)&0x01) | ((Cr >> 21)&0x06) | ((Cr >> 22)&0x38)];
263
264 K2 = SymCryptDesKeySelect[4][ (Dr )&0x3f ] |
265 SymCryptDesKeySelect[5][((Dr >> 7)&0x03) | ((Dr >> 8)&0x3c)] |
266 SymCryptDesKeySelect[6][ (Dr >> 15)&0x3f ] |
267 SymCryptDesKeySelect[7][((Dr >> 21)&0x0f) | ((Dr >> 22)&0x30)];
268
269 //
270 // After this we still have to swap the halves of K1 and K2, that is done below
271 // as part of the formatting of the round key
272 //
273
274 //
275 // So far we have recreated the round keys per the standard.
276 // The round keys are stored rotated by 2 as the encrypt/decrypt code finds that easier.
277 // We could update the tables to do this, but key expansion is not used that frequently,
278 // and it is not worth the effort to update the tables.
279 //
280 // We don't worry about extraneous bits in unused positions as the F function masks out unused bits.
281 //
282
283 tmp = ((K2 << 16) | (K1 & 0x0000ffff)) ;
284 expandedKeyTable[r][0] = ROL32(tmp, 2);
285
286 tmp = ((K1 >> 16) | (K2 & 0xffff0000));
287 expandedKeyTable[r][1] = ROL32(tmp, 6);
288 }
289}
#define SWAP_BITS_WITHIN_UINT32(_value, _shift, _mask)
#define SWAP_BITS_BETWEEN_UINT32(_v1, _v2, _shift, _mask)
BYTE K2[16]
PCSYMCRYPT_HMAC_MD5_EXPANDED_KEY pKey
BYTE K1[16]

Referenced by SymCrypt3DesExpandKey().

◆ SymCryptDesSelftest()

VOID SYMCRYPT_CALL SymCryptDesSelftest ( void  )

Definition at line 624 of file 3des.c.

625{
628
629 if( SymCryptDesExpandKey( &key, SP800_67Key, 8 ) != SYMCRYPT_NO_ERROR )
630 {
631 SymCryptFatal( 'desa' );
632 }
633
635
637
639 {
640 SymCryptFatal( 'desb' );
641 }
642
644
646
648 {
649 SymCryptFatal( 'desc' );
650 }
651}
VOID SYMCRYPT_CALL SymCryptDesEncrypt(_In_ PCSYMCRYPT_DES_EXPANDED_KEY pExpandedKey, _In_reads_(SYMCRYPT_DES_BLOCK_SIZE) PCBYTE pbSrc, _Out_writes_(SYMCRYPT_DES_BLOCK_SIZE) PBYTE pbDst)
Definition: 3des.c:142
SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptDesExpandKey(_Out_ PSYMCRYPT_DES_EXPANDED_KEY pExpandedKey, _In_reads_(cbKey) PCBYTE pbKey, SIZE_T cbKey)
Definition: 3des.c:124
static const BYTE desKnownCiphertext[8]
Definition: 3des.c:617
VOID SYMCRYPT_CALL SymCryptDesDecrypt(_In_ PCSYMCRYPT_DES_EXPANDED_KEY pExpandedKey, _In_reads_(SYMCRYPT_DES_BLOCK_SIZE) PCBYTE pbSrc, _Out_writes_(SYMCRYPT_DES_BLOCK_SIZE) PBYTE pbDst)
Definition: 3des.c:152
#define SYMCRYPT_DES_BLOCK_SIZE
Definition: symcrypt.h:4385
SYMCRYPT_DES_EXPANDED_KEY

◆ SymCryptDesSetOddParity()

VOID SYMCRYPT_CALL SymCryptDesSetOddParity ( _Inout_updates_(cbData) PBYTE  pbData,
_In_ SIZE_T  cbData 
)

Definition at line 577 of file 3des.c.

584{
585 SIZE_T i;
586 BYTE b, t;
587 for( i=0; i<cbData; i++ )
588 {
589 // We obey the read-once write-once rule
590 b = *pbData;
591
592 t = b ^ (b>>4); // parity(b) = parity( t & 0xf )
593 t ^= t>>2; // = parity( t & 0x3 )
594 t ^= t>>1; // = parity( t & 0x1 )
595 *pbData++ = b ^ (t&1) ^ 1;
596 }
597}
GLdouble GLdouble t
Definition: gl.h:2047
GLboolean GLboolean GLboolean b
Definition: glext.h:6204
#define b
Definition: ke_i.h:79
PCBYTE pbData

Variable Documentation

◆ des3KnownCiphertext

const BYTE des3KnownCiphertext[8]
static
Initial value:
= {
0x31, 0x4F, 0x83, 0x27, 0xFA, 0x7A, 0x09, 0xA8,
}

Definition at line 613 of file 3des.c.

Referenced by SymCrypt3DesSelftest().

◆ des3KnownPlaintext

const BYTE des3KnownPlaintext[8]
static
Initial value:
= {
0x4E, 0x6F, 0x77, 0x20, 0x69, 0x73, 0x20, 0x74,
}

Definition at line 609 of file 3des.c.

Referenced by SymCrypt3DesSelftest(), and SymCryptDesSelftest().

◆ desKnownCiphertext

const BYTE desKnownCiphertext[8]
static
Initial value:
= {
0x3F, 0xA4, 0x0E, 0x8A, 0x98, 0x4D, 0x48, 0x15,
}

Definition at line 617 of file 3des.c.

Referenced by SymCryptDesSelftest().

◆ SP800_67Key

const BYTE SP800_67Key[24]
static
Initial value:
= {
0x01, 0x23, 0x45, 0x67, 0x89, 0xAB, 0xCD, 0xEF,
0x23, 0x45, 0x67, 0x89, 0xAB, 0xCD, 0xEF, 0x01,
0x45, 0x67, 0x89, 0xAB, 0xCD, 0xEF, 0x01, 0x23,
}

Definition at line 603 of file 3des.c.

Referenced by SymCrypt3DesSelftest(), and SymCryptDesSelftest().

◆ SymCrypt3DesBlockCipher

Definition at line 75 of file 3des.c.

Referenced by SymCrypt3DesCbcDecrypt(), and SymCrypt3DesCbcEncrypt().

◆ SymCrypt3DesBlockCipher_default

const SYMCRYPT_BLOCKCIPHER SymCrypt3DesBlockCipher_default
Initial value:

Definition at line 43 of file 3des.c.

◆ SymCryptDesBlockCipher

Definition at line 76 of file 3des.c.

◆ SymCryptDesBlockCipher_default

const SYMCRYPT_BLOCKCIPHER SymCryptDesBlockCipher_default
Initial value:

Definition at line 59 of file 3des.c.