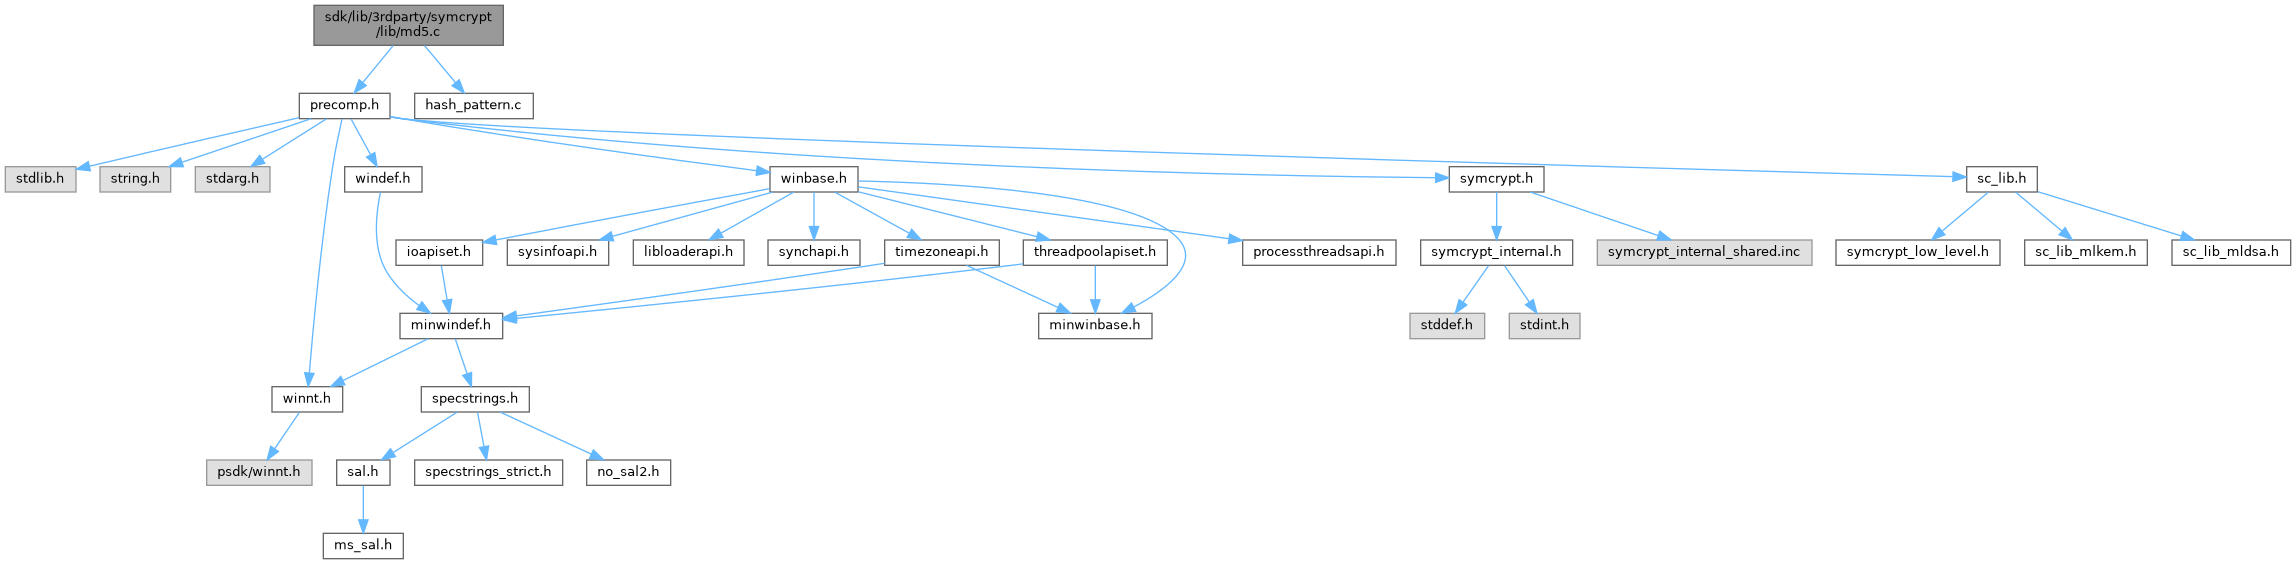
Include dependency graph for md5.c:
Go to the source code of this file.
Macros | |
| #define | ALG MD5 |
| #define | Alg Md5 |
| #define | F(x, y, z) ((((z) ^ (y)) & (x)) ^ (z)) |
| #define | G(x, y, z) F( (z), (x), (y) ) |
| #define | H(x, y, z) ((x) ^ (y) ^ (z) ) |
| #define | I(x, y, z) ((y) ^ ((x) | ~(z))) |
| #define | CROUND(r, Func) |
| #define | IROUND(r, Func) |
| #define | FROUND(r, Func) |
Variables | |
| const SYMCRYPT_HASH | SymCryptMd5Algorithm_default |
| const PCSYMCRYPT_HASH | SymCryptMd5Algorithm = &SymCryptMd5Algorithm_default |
| static const UINT32 | md5Const [64] |
| static const int | md5Rotate [64] |
| static const int | md5MsgIndex [64] |
| static const UINT32 | md5InitialState [4] |
| static const BYTE | md5KATAnswer [16] |
Macro Definition Documentation
◆ ALG
◆ Alg
◆ CROUND
◆ F
◆ FROUND
Value:
◆ G
◆ H
◆ I
◆ IROUND
Value:
{ \
}
Function Documentation
◆ SymCryptMd5Append()
| VOID SYMCRYPT_CALL SymCryptMd5Append | ( | _Inout_ PSYMCRYPT_MD5_STATE | pState, |
| _In_reads_(cbData) PCBYTE | pbData, | ||
| SIZE_T | cbData | ||
| ) |
Definition at line 204 of file md5.c.
208{
209 SymCryptHashAppendInternal( SymCryptMd5Algorithm, (PSYMCRYPT_COMMON_HASH_STATE)pState, pbData, cbData );
210}
VOID SYMCRYPT_CALL SymCryptHashAppendInternal(_In_ PCSYMCRYPT_HASH pHash, _Inout_ PSYMCRYPT_COMMON_HASH_STATE pState, _In_reads_bytes_(cbData) PCBYTE pbData, SIZE_T cbData)
Definition: hash.c:10
◆ SymCryptMd5AppendBlocks()
| VOID SYMCRYPT_CALL SymCryptMd5AppendBlocks | ( | _Inout_ SYMCRYPT_MD5_CHAINING_STATE * | pChain, |
| _In_reads_(cbData) PCBYTE | pbData, | ||
| SIZE_T | cbData, | ||
| _Out_ SIZE_T * | pcbRemaining | ||
| ) |
Definition at line 295 of file md5.c.
300{
301
303 UINT32 ad[4];
304 UINT32 Wt;
305
306 ad[0] = pChain->H[0];
307 ad[1] = pChain->H[3];
308 ad[2] = pChain->H[2];
309 ad[3] = pChain->H[1];
310
312 {
313 //
314 // initial rounds 1 to 16
315 //
316
333
350
367
384
385 pChain->H[0] = ad[0] = ad[0] + pChain->H[0];
386 pChain->H[3] = ad[1] = ad[1] + pChain->H[3];
387 pChain->H[2] = ad[2] = ad[2] + pChain->H[2];
388 pChain->H[1] = ad[3] = ad[3] + pChain->H[1];
389
390 pbData += 64;
391 cbData -= 64;
392 }
393
394 *pcbRemaining = cbData;
395
396 //
397 // Wipe the variables;
398 //
402}
FORCEINLINE VOID SYMCRYPT_CALL SymCryptWipeKnownSize(_Out_writes_bytes_(cbData) PVOID pbData, SIZE_T cbData)
Definition: symcrypt_internal.h:3411
◆ SymCryptMd5Init()
| VOID SYMCRYPT_CALL SymCryptMd5Init | ( | _Out_ PSYMCRYPT_MD5_STATE | pState | ) |
Definition at line 182 of file md5.c.
183{
185
186 pState->dataLengthL = 0;
187 pState->dataLengthH = 0;
188 pState->bytesInBuffer = 0;
189
191
192 //
193 // There is no need to initialize the buffer part of the state as that will be
194 // filled before it is used.
195 //
196}
Referenced by SymCryptMd5Result().
◆ SymCryptMd5Result()
| VOID SYMCRYPT_CALL SymCryptMd5Result | ( | _Inout_ PSYMCRYPT_MD5_STATE | pState, |
| _Out_writes_(SYMCRYPT_MD5_RESULT_SIZE) PBYTE | pbResult | ||
| ) |
Definition at line 217 of file md5.c.
220{
221 SymCryptHashCommonPaddingMd4Style( SymCryptMd5Algorithm, (PSYMCRYPT_COMMON_HASH_STATE) pState );
222
223 //
224 // Write the output in the correct byte order
225 //
227
228 //
229 // Wipe & re-initialize
230 // We have to wipe the whole state because the Init call
231 // might be optimized away by a smart compiler.
232 // And we need to wipe old data.
233 //
236}
FORCEINLINE VOID SYMCRYPT_CALL SymCryptUint32ToLsbFirst(_In_reads_(cuData) PCUINT32 puData, _Out_writes_(4 *cuData) PBYTE pbResult, SIZE_T cuData)
Definition: sc_lib.h:471
VOID SYMCRYPT_CALL SymCryptHashCommonPaddingMd4Style(_In_ PCSYMCRYPT_HASH pHash, _Inout_ PSYMCRYPT_COMMON_HASH_STATE pState)
Definition: hash.c:85
VOID SYMCRYPT_CALL SymCryptMd5Init(_Out_ PSYMCRYPT_MD5_STATE pState)
Definition: md5.c:182
◆ SymCryptMd5Selftest()
| VOID SYMCRYPT_CALL SymCryptMd5Selftest | ( | void | ) |
Definition at line 492 of file md5.c.
493{
495
497
499
502 }
503}
VOID SYMCRYPT_CALL SymCryptInjectError(PBYTE pbData, SIZE_T cbData)
_Analysis_noreturn_ VOID SYMCRYPT_CALL SymCryptFatal(UINT32 fatalCode)
VOID SYMCRYPT_CALL SymCryptMd5(_In_reads_(cbData) PCBYTE pbData, SIZE_T cbData, _Out_writes_(SYMCRYPT_MD5_RESULT_SIZE) PBYTE pbResult)
◆ SymCryptMd5StateExport()
| VOID SYMCRYPT_CALL SymCryptMd5StateExport | ( | _In_ PCSYMCRYPT_MD5_STATE | pState, |
| _Out_writes_bytes_(SYMCRYPT_MD5_STATE_EXPORT_SIZE) PBYTE | pbBlob | ||
| ) |
Definition at line 406 of file md5.c.
409{
412
414
416
420
421 //
422 // Copy the relevant data. Buffer will be 0-padded.
423 //
424
428
429 SYMCRYPT_ASSERT( (PCBYTE) &blob + sizeof( blob ) - sizeof( SYMCRYPT_BLOB_TRAILER ) == (PCBYTE) &blob.trailer );
430 SymCryptMarvin32( SymCryptMarvin32DefaultSeed, (PCBYTE) &blob, sizeof( blob ) - sizeof( SYMCRYPT_BLOB_TRAILER ), &blob.trailer.checksum[0] );
431
433
434//cleanup:
436 return;
437}
Definition: sc_lib.h:1090
Definition: sc_lib.h:1119
Definition: image.c:229
VOID SYMCRYPT_CALL SymCryptMarvin32(_In_ PCSYMCRYPT_MARVIN32_EXPANDED_SEED pExpandedSeed, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData, _Out_writes_(SYMCRYPT_MARVIN32_RESULT_SIZE) PBYTE pbResult)
Definition: marvin32.c:239
PCSYMCRYPT_MARVIN32_EXPANDED_SEED const SymCryptMarvin32DefaultSeed
Definition: marvin32.c:29
#define SYMCRYPT_MD5_STATE_EXPORT_SIZE
Definition: symcrypt_internal.h:2181
◆ SymCryptMd5StateImport()
| SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptMd5StateImport | ( | _Out_ PSYMCRYPT_MD5_STATE | pState, |
| _In_reads_bytes_(SYMCRYPT_MD5_STATE_EXPORT_SIZE) PCBYTE | pbBlob | ||
| ) |
Definition at line 441 of file md5.c.
444{
445 SYMCRYPT_ERROR scError = SYMCRYPT_NO_ERROR;
448
451
455 {
456 scError = SYMCRYPT_INVALID_BLOB;
458 }
459
460 SymCryptMarvin32( SymCryptMarvin32DefaultSeed, (PCBYTE) &blob, sizeof( blob ) - sizeof( SYMCRYPT_BLOB_TRAILER ), checksum );
462 {
463 scError = SYMCRYPT_INVALID_BLOB;
465 }
466
469 pState->dataLengthH = 0;
472
474
475cleanup:
477 return scError;
478}
static cab_ULONG checksum(const cab_UBYTE *data, cab_UWORD bytes, cab_ULONG csum)
Definition: fdi.c:353
FORCEINLINE VOID SYMCRYPT_CALL SymCryptLsbFirstToUint32(_In_reads_(4 *cuResult) PCBYTE pbData, _Out_writes_(cuResult) PUINT32 puResult, SIZE_T cuResult)
Definition: sc_lib.h:487
Variable Documentation
◆ md5Const
◆ md5InitialState
Initial value:
= {
0x67452301UL,
0xefcdab89UL,
0x98badcfeUL,
0x10325476UL,
}
Definition at line 158 of file md5.c.
Referenced by SymCryptMd5Init().
◆ md5KATAnswer
Initial value:
= {
0x90, 0x01, 0x50, 0x98, 0x3c, 0xd2, 0x4f, 0xb0,
0xd6, 0x96, 0x3f, 0x7d, 0x28, 0xe1, 0x7f, 0x72,
}
Definition at line 485 of file md5.c.
Referenced by SymCryptMd5Selftest().
◆ md5MsgIndex
◆ md5Rotate
◆ SymCryptMd5Algorithm
| const PCSYMCRYPT_HASH SymCryptMd5Algorithm = &SymCryptMd5Algorithm_default |
Definition at line 43 of file md5.c.
Referenced by init_hash_impl(), SymCryptMd5Append(), and SymCryptMd5Result().
◆ SymCryptMd5Algorithm_default
| const SYMCRYPT_HASH SymCryptMd5Algorithm_default |
Initial value:
= {
sizeof( SYMCRYPT_MD5_STATE ),
}
VOID SYMCRYPT_CALL SymCryptMd5AppendBlocks(_Inout_ SYMCRYPT_MD5_CHAINING_STATE *pChain, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData, _Out_ SIZE_T *pcbRemaining)
Definition: md5.c:295
VOID SYMCRYPT_CALL SymCryptMd5Append(_Inout_ PSYMCRYPT_MD5_STATE pState, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData)
Definition: md5.c:204
VOID SYMCRYPT_CALL SymCryptMd5Result(_Inout_ PSYMCRYPT_MD5_STATE pState, _Out_writes_(SYMCRYPT_MD5_RESULT_SIZE) PBYTE pbResult)
Definition: md5.c:217
VOID SYMCRYPT_CALL SymCryptMd5StateCopy(_In_ PCSYMCRYPT_MD5_STATE pSrc, _Out_ PSYMCRYPT_MD5_STATE pDst)
