#include "precomp.h"
Include dependency graph for aescmac.c:
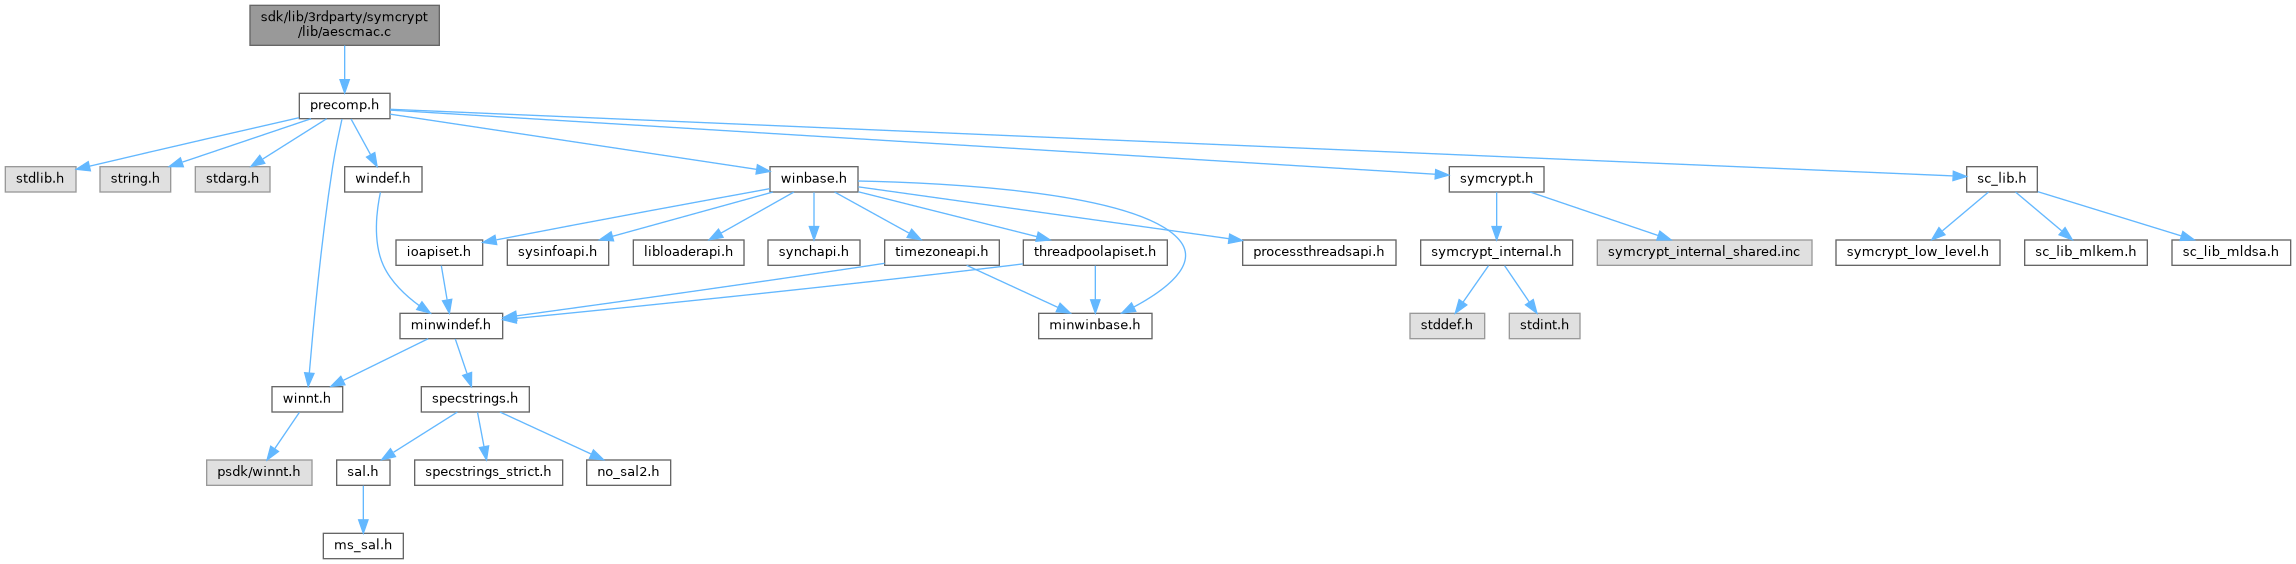
Go to the source code of this file.
Variables | |
| const SYMCRYPT_MAC | SymCryptAesCmacAlgorithm_fast |
| const PCSYMCRYPT_MAC | SymCryptAesCmacAlgorithm = &SymCryptAesCmacAlgorithm_fast |
| static const BYTE | aesCmacKat [SYMCRYPT_AES_CMAC_RESULT_SIZE] |
Function Documentation
◆ SymCryptAesCmac()
| VOID SYMCRYPT_CALL SymCryptAesCmac | ( | _In_ PSYMCRYPT_AES_CMAC_EXPANDED_KEY | pExpandedKey, |
| _In_reads_(cbData) PCBYTE | pbData, | ||
| SIZE_T | cbData, | ||
| _Out_writes_(SYMCRYPT_AES_CMAC_RESULT_SIZE) PBYTE | pbResult | ||
| ) |
Definition at line 93 of file aescmac.c.
98{
100
104
106}
VOID SYMCRYPT_CALL SymCryptAesCmacInit(_Out_ PSYMCRYPT_AES_CMAC_STATE pState, _In_ PCSYMCRYPT_AES_CMAC_EXPANDED_KEY pExpandedKey)
Definition: aescmac.c:135
VOID SYMCRYPT_CALL SymCryptAesCmacAppend(_Inout_ PSYMCRYPT_AES_CMAC_STATE pState, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData)
Definition: aescmac.c:150
VOID SYMCRYPT_CALL SymCryptAesCmacResult(_Inout_ PSYMCRYPT_AES_CMAC_STATE pState, _Out_writes_(SYMCRYPT_AES_CMAC_RESULT_SIZE) PBYTE pbResult)
Definition: aescmac.c:202
FORCEINLINE VOID SYMCRYPT_CALL SymCryptWipeKnownSize(_Out_writes_bytes_(cbData) PVOID pbData, SIZE_T cbData)
Definition: symcrypt_internal.h:3411
SYMCRYPT_MAGIC_FIELD SYMCRYPT_AES_CMAC_STATE
Definition: symcrypt_internal.h:1681
Referenced by SymCryptAesCmacSelftest().
◆ SymCryptAesCmacAppend()
| VOID SYMCRYPT_CALL SymCryptAesCmacAppend | ( | _Inout_ PSYMCRYPT_AES_CMAC_STATE | pState, |
| _In_reads_(cbData) PCBYTE | pbData, | ||
| SIZE_T | cbData | ||
| ) |
Definition at line 150 of file aescmac.c.
154{
155
157
159 {
162
164 {
165 // Do nothing.
166 // the data will be copied into the buf at the end of this function
167 //
168 }
169 else
170 {
172 pbData += freeInBuf;
173 cbData -= freeInBuf;
174 SymCryptAesCbcMac( &pState->pKey->aesKey, &pState->chain[0], &pState->buf[0], SYMCRYPT_AES_BLOCK_SIZE );
175 pState->bytesInBuf = 0;
176 }
177 }
178
179 //
180 // At this point, either pState->bytesInBuf == 0, or it is !=0 but cbData is small enough that all the
181 // data will still fit in the buffer without further processing.
182 //
183
185 {
188 pbData += bytesToDo;
189 cbData -= bytesToDo;
190 }
191
193 {
196 }
197}
VOID SYMCRYPT_CALL SymCryptAesCbcMac(_In_ PCSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _Inout_updates_(SYMCRYPT_AES_BLOCK_SIZE) PBYTE pbChainingValue, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData)
Definition: aes-default.c:317
Referenced by SymCryptAesCmac().
◆ SymCryptAesCmacExpandKey()
| SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesCmacExpandKey | ( | _Out_ PSYMCRYPT_AES_CMAC_EXPANDED_KEY | pExpandedKey, |
| _In_reads_(cbKey) PCBYTE | pbKey, | ||
| SIZE_T | cbKey | ||
| ) |
Definition at line 44 of file aescmac.c.
48{
49 SYMCRYPT_ERROR scError = SYMCRYPT_NO_ERROR;
51
53 if( scError != SYMCRYPT_NO_ERROR )
54 {
56 }
57
59
61
66
68
70
71cleanup:
72
73 return scError;
74}
VOID SYMCRYPT_CALL SymCryptCmacMunge(_Inout_updates_bytes_(SYMCRYPT_AES_BLOCK_SIZE) BYTE buf[SYMCRYPT_AES_BLOCK_SIZE])
Definition: aescmac.c:25
SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesExpandKey(_Out_ PSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _In_reads_(cbKey) PCBYTE pbKey, SIZE_T cbKey)
Definition: aes-key.c:219
VOID SYMCRYPT_CALL SymCryptAesEncrypt(_In_ PCSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _In_reads_(SYMCRYPT_AES_BLOCK_SIZE) PCBYTE pbSrc, _Out_writes_(SYMCRYPT_AES_BLOCK_SIZE) PBYTE pbDst)
Definition: aes-default.c:95
Referenced by SymCryptAesCmacSelftest().
◆ SymCryptAesCmacInit()
| VOID SYMCRYPT_CALL SymCryptAesCmacInit | ( | _Out_ PSYMCRYPT_AES_CMAC_STATE | pState, |
| _In_ PCSYMCRYPT_AES_CMAC_EXPANDED_KEY | pExpandedKey | ||
| ) |
Definition at line 135 of file aescmac.c.
Referenced by SymCryptAesCmac().
◆ SymCryptAesCmacKeyCopy()
| VOID SYMCRYPT_CALL SymCryptAesCmacKeyCopy | ( | _In_ PCSYMCRYPT_AES_CMAC_EXPANDED_KEY | pSrc, |
| _Out_ PSYMCRYPT_AES_CMAC_EXPANDED_KEY | pDst | ||
| ) |
Definition at line 79 of file aescmac.c.
82{
83 SYMCRYPT_CHECK_MAGIC( pSrc );
84 SymCryptAesKeyCopy( &pSrc->aesKey, &pDst->aesKey );
87 SYMCRYPT_SET_MAGIC( pDst );
88}
VOID SYMCRYPT_CALL SymCryptAesKeyCopy(_In_ PCSYMCRYPT_AES_EXPANDED_KEY pSrc, _Out_ PSYMCRYPT_AES_EXPANDED_KEY pDst)
Definition: aes-key.c:240
◆ SymCryptAesCmacResult()
| VOID SYMCRYPT_CALL SymCryptAesCmacResult | ( | _Inout_ PSYMCRYPT_AES_CMAC_STATE | pState, |
| _Out_writes_(SYMCRYPT_AES_CMAC_RESULT_SIZE) PBYTE | pbResult | ||
| ) |
Definition at line 202 of file aescmac.c.
205{
207
209 {
210 SymCryptWipe( &pState->buf[pState->bytesInBuf + 1], SYMCRYPT_AES_BLOCK_SIZE - pState->bytesInBuf - 1 );
212 SymCryptXorBytes( &pState->buf[0], &pState->pKey->K2[0], &pState->buf[0], SYMCRYPT_AES_BLOCK_SIZE );
213 }
214 else
215 {
216 SymCryptXorBytes( &pState->buf[0], &pState->pKey->K1[0], &pState->buf[0], SYMCRYPT_AES_BLOCK_SIZE );
217 }
218
219 SymCryptAesCbcMac( &pState->pKey->aesKey, &pState->chain[0], &pState->buf[0], SYMCRYPT_AES_BLOCK_SIZE );
221
222 //
223 // Put the state back in the original starting state,
224 // and wipe any traces of the data.
225 //
226 pState->bytesInBuf = 0;
229}
VOID SYMCRYPT_CALL SymCryptWipe(_Out_writes_bytes_(cbData) PVOID pbData, SIZE_T cbData)
Definition: libmain.c:137
VOID SYMCRYPT_CALL SymCryptXorBytes(_In_reads_(cbBytes) PCBYTE pbSrc1, _In_reads_(cbBytes) PCBYTE pbSrc2, _Out_writes_(cbBytes) PBYTE pbResult, SIZE_T cbBytes)
Definition: libmain.c:236
Referenced by SymCryptAesCmac().
◆ SymCryptAesCmacSelftest()
| VOID SYMCRYPT_CALL SymCryptAesCmacSelftest | ( | void | ) |
Definition at line 240 of file aescmac.c.
241{
242 SYMCRYPT_AES_CMAC_EXPANDED_KEY xKey;
244
247
250 {
252 }
253
254 //
255 // Normally we would wipe the expanded key structure here,
256 // but as this is a selftest with known data this is not needed.
257 //
258}
VOID SYMCRYPT_CALL SymCryptAesCmac(_In_ PSYMCRYPT_AES_CMAC_EXPANDED_KEY pExpandedKey, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData, _Out_writes_(SYMCRYPT_AES_CMAC_RESULT_SIZE) PBYTE pbResult)
Definition: aescmac.c:93
SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesCmacExpandKey(_Out_ PSYMCRYPT_AES_CMAC_EXPANDED_KEY pExpandedKey, _In_reads_(cbKey) PCBYTE pbKey, SIZE_T cbKey)
Definition: aescmac.c:44
VOID SYMCRYPT_CALL SymCryptInjectError(PBYTE pbData, SIZE_T cbData)
_Analysis_noreturn_ VOID SYMCRYPT_CALL SymCryptFatal(UINT32 fatalCode)
SYMCRYPT_MAGIC_FIELD SYMCRYPT_AES_CMAC_EXPANDED_KEY
Definition: symcrypt_internal.h:1670
◆ SymCryptAesCmacStateCopy()
| VOID SYMCRYPT_CALL SymCryptAesCmacStateCopy | ( | _In_ PCSYMCRYPT_AES_CMAC_STATE | pSrc, |
| _In_opt_ PCSYMCRYPT_AES_CMAC_EXPANDED_KEY | pExpandedKey, | ||
| _Out_ PSYMCRYPT_AES_CMAC_STATE | pDst | ||
| ) |
Definition at line 111 of file aescmac.c.
115{
116 SYMCRYPT_CHECK_MAGIC( pSrc );
117 *pDst = *pSrc;
118
120 {
121 SYMCRYPT_CHECK_MAGIC( pSrc->pKey );
122 pDst->pKey = pSrc->pKey;
123 }
124 else
125 {
127 pDst->pKey = pExpandedKey;
128 }
129
130 SYMCRYPT_SET_MAGIC( pDst );
131}
◆ SymCryptCmacMunge()
| VOID SYMCRYPT_CALL SymCryptCmacMunge | ( | _Inout_updates_bytes_(SYMCRYPT_AES_BLOCK_SIZE) BYTE | buf[SYMCRYPT_AES_BLOCK_SIZE] | ) |
Definition at line 25 of file aescmac.c.
27{
28 SIZE_T carry = 0;
29 SIZE_T tmp;
31
33 {
36 carry = tmp >> 7;
37 }
38
40}
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble const GLfloat const GLdouble const GLfloat GLint i
Definition: glfuncs.h:248
Referenced by SymCryptAesCmacExpandKey().
Variable Documentation
◆ aesCmacKat
|
static |
Initial value:
= {
0x0a, 0x54, 0xa6, 0xa4, 0x25, 0xd4, 0x84, 0x38, 0xc3, 0xf8, 0xbb, 0xe0, 0x9b, 0xf9, 0x44, 0xcc,
}
Definition at line 233 of file aescmac.c.
Referenced by SymCryptAesCmacSelftest().
◆ SymCryptAesCmacAlgorithm
| const PCSYMCRYPT_MAC SymCryptAesCmacAlgorithm = &SymCryptAesCmacAlgorithm_fast |
◆ SymCryptAesCmacAlgorithm_fast
| const SYMCRYPT_MAC SymCryptAesCmacAlgorithm_fast |
Initial value:
