ReactOS 0.4.17-dev-1005-g171e1de
shake.c File Reference
#include "precomp.h"
#include "shake_pattern.c"
#include "cshake_pattern.c"
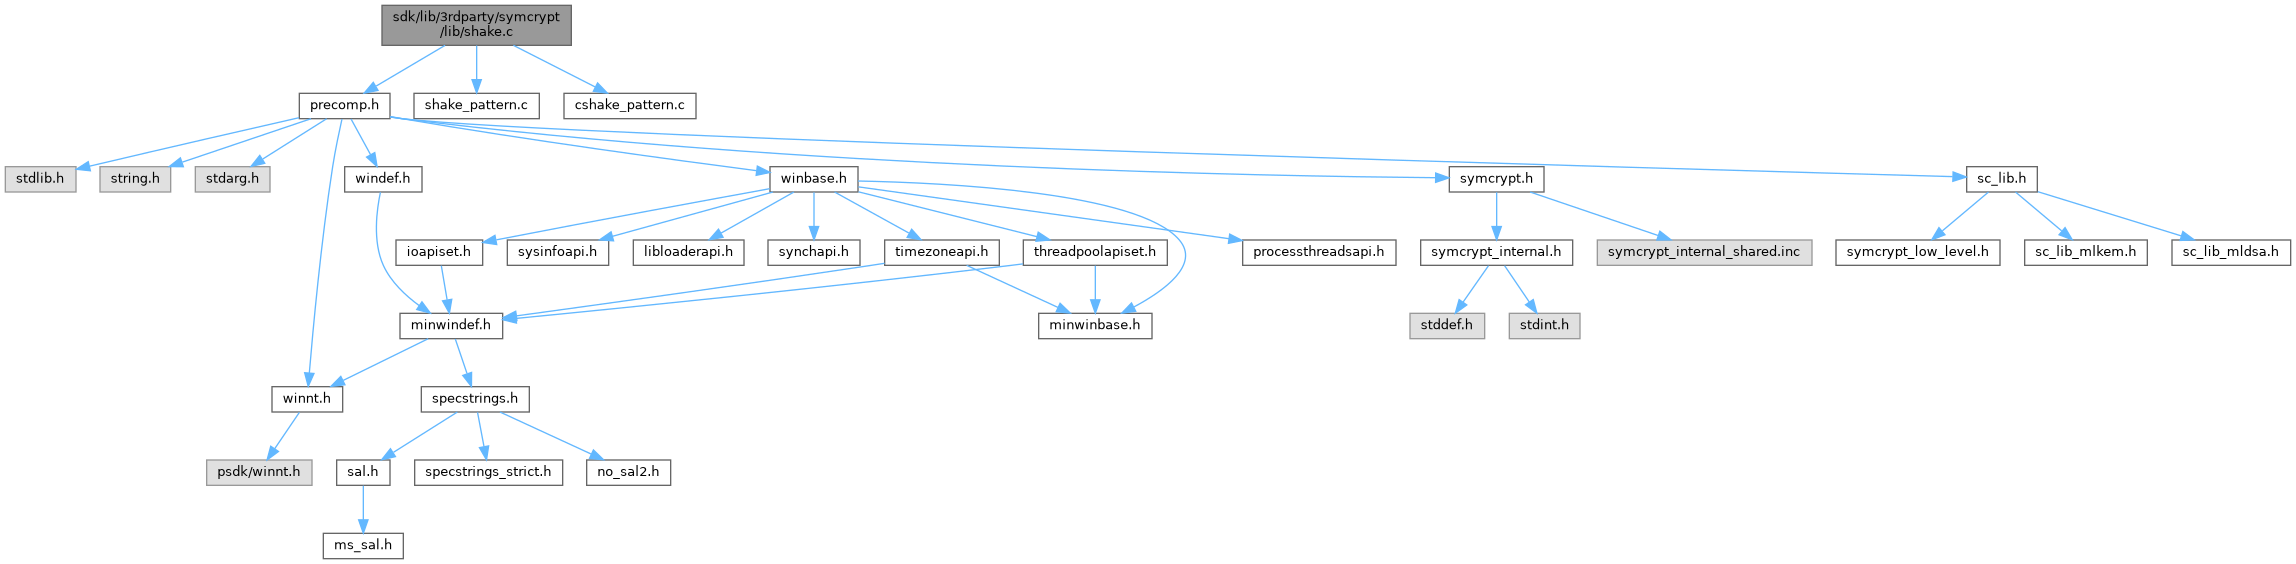
Include dependency graph for shake.c:

Go to the source code of this file.

Macros

#define Alg   Shake128
 
#define ALG   SHAKE128
 
#define SYMCRYPT_SHAKEXXX_INPUT_BLOCK_SIZE   SYMCRYPT_SHAKE128_INPUT_BLOCK_SIZE
 
#define SYMCRYPT_SHAKEXXX_RESULT_SIZE   SYMCRYPT_SHAKE128_RESULT_SIZE
 
#define Alg   Shake256
 
#define ALG   SHAKE256
 
#define SYMCRYPT_SHAKEXXX_INPUT_BLOCK_SIZE   SYMCRYPT_SHAKE256_INPUT_BLOCK_SIZE
 
#define SYMCRYPT_SHAKEXXX_RESULT_SIZE   SYMCRYPT_SHAKE256_RESULT_SIZE
 
#define Alg   CShake128
 
#define ALG   CSHAKE128
 
#define SYMCRYPT_SHAKEXXX_INIT   SymCryptShake128Init
 
#define SYMCRYPT_SHAKEXXX_STATE   SYMCRYPT_SHAKE128_STATE
 
#define SYMCRYPT_CSHAKEXXX_INPUT_BLOCK_SIZE   SYMCRYPT_CSHAKE128_INPUT_BLOCK_SIZE
 
#define SYMCRYPT_CSHAKEXXX_RESULT_SIZE   SYMCRYPT_CSHAKE128_RESULT_SIZE
 
#define Alg   CShake256
 
#define ALG   CSHAKE256
 
#define SYMCRYPT_SHAKEXXX_INIT   SymCryptShake256Init
 
#define SYMCRYPT_SHAKEXXX_STATE   SYMCRYPT_SHAKE256_STATE
 
#define SYMCRYPT_CSHAKEXXX_INPUT_BLOCK_SIZE   SYMCRYPT_CSHAKE256_INPUT_BLOCK_SIZE
 
#define SYMCRYPT_CSHAKEXXX_RESULT_SIZE   SYMCRYPT_CSHAKE256_RESULT_SIZE
 

Functions

VOID SYMCRYPT_CALL SymCryptShake128Selftest (void)
 
VOID SYMCRYPT_CALL SymCryptShake256Selftest (void)
 
VOID SYMCRYPT_CALL SymCryptCShake128Selftest (void)
 
VOID SYMCRYPT_CALL SymCryptCShake256Selftest (void)
 
VOID SYMCRYPT_CALL SymCryptCShakeEncodeInputStrings (_Inout_ PSYMCRYPT_KECCAK_STATE pState, _In_reads_(cbFunctionNameString) PCBYTE pbFunctionNameString, SIZE_T cbFunctionNameString, _In_reads_(cbCustomizationString) PCBYTE pbCustomizationString, SIZE_T cbCustomizationString)
 
SIZE_T SYMCRYPT_CALL SymCryptKeccakEncodeTimes8 (UINT64 uInput, _Out_writes_(cbOutput) PBYTE pbOutput, SIZE_T cbOutput, BOOLEAN bLeftEncode)
 
VOID SYMCRYPT_CALL SymCryptKeccakAppendEncodeTimes8 (_Inout_ SYMCRYPT_KECCAK_STATE *pState, UINT64 uValue, BOOLEAN bLeftEncode)
 
VOID SYMCRYPT_CALL SymCryptKeccakAppendEncodedString (_Inout_ PSYMCRYPT_KECCAK_STATE pState, _In_reads_(cbString) PCBYTE pbString, SIZE_T cbString)
 

Variables

const SYMCRYPT_HASH SymCryptShake128HashAlgorithm_default
 
const PCSYMCRYPT_HASH SymCryptShake128HashAlgorithm = &SymCryptShake128HashAlgorithm_default
 
static const BYTE shake128KATAnswer [SYMCRYPT_SHAKE128_RESULT_SIZE]
 
const SYMCRYPT_HASH SymCryptShake256HashAlgorithm_default
 
const PCSYMCRYPT_HASH SymCryptShake256HashAlgorithm = &SymCryptShake256HashAlgorithm_default
 
static const BYTE shake256KATAnswer [SYMCRYPT_SHAKE256_RESULT_SIZE]
 
static const BYTE cshake128KATAnswer [SYMCRYPT_CSHAKE128_RESULT_SIZE]
 
static const BYTE cshake256KATAnswer [SYMCRYPT_CSHAKE256_RESULT_SIZE]
 

Macro Definition Documentation

◆ Alg [1/4]

#define Alg   Shake128

Definition at line 169 of file shake.c.

◆ ALG [1/4]

#define ALG   SHAKE128

Definition at line 170 of file shake.c.

◆ Alg [2/4]

#define Alg   Shake256

Definition at line 169 of file shake.c.

◆ ALG [2/4]

#define ALG   SHAKE256

Definition at line 170 of file shake.c.

◆ Alg [3/4]

#define Alg   CShake128

Definition at line 169 of file shake.c.

◆ ALG [3/4]

#define ALG   CSHAKE128

Definition at line 170 of file shake.c.

◆ Alg [4/4]

#define Alg   CShake256

Definition at line 169 of file shake.c.

◆ ALG [4/4]

#define ALG   CSHAKE256

Definition at line 170 of file shake.c.

◆ SYMCRYPT_CSHAKEXXX_INPUT_BLOCK_SIZE [1/2]

#define SYMCRYPT_CSHAKEXXX_INPUT_BLOCK_SIZE   SYMCRYPT_CSHAKE128_INPUT_BLOCK_SIZE

Definition at line 173 of file shake.c.

◆ SYMCRYPT_CSHAKEXXX_INPUT_BLOCK_SIZE [2/2]

#define SYMCRYPT_CSHAKEXXX_INPUT_BLOCK_SIZE   SYMCRYPT_CSHAKE256_INPUT_BLOCK_SIZE

Definition at line 173 of file shake.c.

◆ SYMCRYPT_CSHAKEXXX_RESULT_SIZE [1/2]

#define SYMCRYPT_CSHAKEXXX_RESULT_SIZE   SYMCRYPT_CSHAKE128_RESULT_SIZE

Definition at line 174 of file shake.c.

◆ SYMCRYPT_CSHAKEXXX_RESULT_SIZE [2/2]

#define SYMCRYPT_CSHAKEXXX_RESULT_SIZE   SYMCRYPT_CSHAKE256_RESULT_SIZE

Definition at line 174 of file shake.c.

◆ SYMCRYPT_SHAKEXXX_INIT [1/2]

#define SYMCRYPT_SHAKEXXX_INIT   SymCryptShake128Init

Definition at line 171 of file shake.c.

◆ SYMCRYPT_SHAKEXXX_INIT [2/2]

#define SYMCRYPT_SHAKEXXX_INIT   SymCryptShake256Init

Definition at line 171 of file shake.c.

◆ SYMCRYPT_SHAKEXXX_INPUT_BLOCK_SIZE [1/2]

#define SYMCRYPT_SHAKEXXX_INPUT_BLOCK_SIZE   SYMCRYPT_SHAKE128_INPUT_BLOCK_SIZE

Definition at line 72 of file shake.c.

◆ SYMCRYPT_SHAKEXXX_INPUT_BLOCK_SIZE [2/2]

#define SYMCRYPT_SHAKEXXX_INPUT_BLOCK_SIZE   SYMCRYPT_SHAKE256_INPUT_BLOCK_SIZE

Definition at line 72 of file shake.c.

◆ SYMCRYPT_SHAKEXXX_RESULT_SIZE [1/2]

#define SYMCRYPT_SHAKEXXX_RESULT_SIZE   SYMCRYPT_SHAKE128_RESULT_SIZE

Definition at line 73 of file shake.c.

◆ SYMCRYPT_SHAKEXXX_RESULT_SIZE [2/2]

#define SYMCRYPT_SHAKEXXX_RESULT_SIZE   SYMCRYPT_SHAKE256_RESULT_SIZE

Definition at line 73 of file shake.c.

◆ SYMCRYPT_SHAKEXXX_STATE [1/2]

#define SYMCRYPT_SHAKEXXX_STATE   SYMCRYPT_SHAKE128_STATE

Definition at line 172 of file shake.c.

◆ SYMCRYPT_SHAKEXXX_STATE [2/2]

#define SYMCRYPT_SHAKEXXX_STATE   SYMCRYPT_SHAKE256_STATE

Definition at line 172 of file shake.c.

Function Documentation

◆ SymCryptCShake128Selftest()

VOID SYMCRYPT_CALL SymCryptCShake128Selftest ( void  )

Definition at line 146 of file shake.c.

147{
149 static const unsigned char Nstr[] = { 'N' };
150 static const unsigned char Sstr[] = { 'S' };
151
152 SymCryptCShake128( Nstr, sizeof(Nstr),
153 Sstr, sizeof(Sstr),
155 result, sizeof(result));
156
158
159 if (memcmp(result, cshake128KATAnswer, sizeof(result)) != 0)
160 {
161 SymCryptFatal('cshk');
162 }
163}
_ACRTIMP int __cdecl memcmp(const void *, const void *, size_t)
Definition: string.c:2807
GLuint64EXT * result
Definition: glext.h:11304
VOID SYMCRYPT_CALL SymCryptInjectError(PBYTE pbData, SIZE_T cbData)
const BYTE SymCryptTestMsg3[3]
Definition: selftest.c:8
static const BYTE cshake128KATAnswer[SYMCRYPT_CSHAKE128_RESULT_SIZE]
Definition: shake.c:137
_Analysis_noreturn_ VOID SYMCRYPT_CALL SymCryptFatal(UINT32 fatalCode)
#define SYMCRYPT_CSHAKE128_RESULT_SIZE
Definition: symcrypt.h:2087
VOID SYMCRYPT_CALL SymCryptCShake128(_In_reads_(cbFunctionNameString) PCBYTE pbFunctionNameString, SIZE_T cbFunctionNameString, _In_reads_(cbCustomizationString) PCBYTE pbCustomizationString, SIZE_T cbCustomizationString, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData, _Out_writes_(cbResult) PBYTE pbResult, SIZE_T cbResult)
unsigned char BYTE
Definition: xxhash.c:193

◆ SymCryptCShake256Selftest()

VOID SYMCRYPT_CALL SymCryptCShake256Selftest ( void  )

Definition at line 193 of file shake.c.

194{
196 static const unsigned char Nstr[] = { 'N' };
197 static const unsigned char Sstr[] = { 'S' };
198
199 SymCryptCShake256(Nstr, sizeof(Nstr),
200 Sstr, sizeof(Sstr),
202 result, sizeof(result));
203
205
206 if (memcmp(result, cshake256KATAnswer, sizeof(result)) != 0)
207 {
208 SymCryptFatal('cshk');
209 }
210}
static const BYTE cshake256KATAnswer[SYMCRYPT_CSHAKE256_RESULT_SIZE]
Definition: shake.c:184
#define SYMCRYPT_CSHAKE256_RESULT_SIZE
Definition: symcrypt.h:2144
VOID SYMCRYPT_CALL SymCryptCShake256(_In_reads_(cbFunctionNameString) PCBYTE pbFunctionNameString, SIZE_T cbFunctionNameString, _In_reads_(cbCustomizationString) PCBYTE pbCustomizationString, SIZE_T cbCustomizationString, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData, _Out_writes_(cbResult) PBYTE pbResult, SIZE_T cbResult)

◆ SymCryptCShakeEncodeInputStrings()

VOID SYMCRYPT_CALL SymCryptCShakeEncodeInputStrings ( _Inout_ PSYMCRYPT_KECCAK_STATE  pState,
_In_reads_(cbFunctionNameString) PCBYTE  pbFunctionNameString,
SIZE_T  cbFunctionNameString,
_In_reads_(cbCustomizationString) PCBYTE  pbCustomizationString,
SIZE_T  cbCustomizationString 
)

Definition at line 221 of file shake.c.

227{
228 SYMCRYPT_ASSERT((cbFunctionNameString > 0) || (cbCustomizationString > 0));
229
230 // left_encode( inputBlockSize ) for byte_pad function
231 //
232 // SymCryptKeccakEncodeTimes8 function encodes 8 times the value passed to
233 // it. Here, we want the actual value of pState->inputBlockSize to be encoded,
234 // hence the division by 8.
235 SymCryptKeccakAppendEncodeTimes8(pState, pState->inputBlockSize / 8, TRUE);
236
237 SymCryptKeccakAppendEncodedString(pState, pbFunctionNameString, cbFunctionNameString);
238 SymCryptKeccakAppendEncodedString(pState, pbCustomizationString, cbCustomizationString);
239
240 // Appending of Customization String may have already called the permutation
241 // if the appended data is aligned to input block size, in which case the zero
242 // padding has been done.
243 if (pState->stateIndex != 0)
244 {
246 }
247}
#define TRUE
Definition: types.h:120
VOID SYMCRYPT_CALL SymCryptKeccakZeroAppendBlock(_Inout_ PSYMCRYPT_KECCAK_STATE pState)
Definition: sha3.c:273
VOID SYMCRYPT_CALL SymCryptKeccakAppendEncodeTimes8(_Inout_ SYMCRYPT_KECCAK_STATE *pState, UINT64 uValue, BOOLEAN bLeftEncode)
Definition: shake.c:310
VOID SYMCRYPT_CALL SymCryptKeccakAppendEncodedString(_Inout_ PSYMCRYPT_KECCAK_STATE pState, _In_reads_(cbString) PCBYTE pbString, SIZE_T cbString)
Definition: shake.c:330
#define SYMCRYPT_ASSERT(_x)
Definition: symcrypt.h:10807
PSYMCRYPT_COMMON_HASH_STATE pState

Referenced by SYMCRYPT_XxxInit().

◆ SymCryptKeccakAppendEncodedString()

VOID SYMCRYPT_CALL SymCryptKeccakAppendEncodedString ( _Inout_ PSYMCRYPT_KECCAK_STATE  pState,
_In_reads_(cbString) PCBYTE  pbString,
SIZE_T  cbString 
)

Definition at line 330 of file shake.c.

334{
336 SymCryptKeccakAppend(pState, pbString, cbString);
337}
VOID SYMCRYPT_CALL SymCryptKeccakAppend(_Inout_ PSYMCRYPT_KECCAK_STATE pState, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData)
Definition: sha3.c:285

Referenced by SYMCRYPT_XxxExpandKeyEx(), and SymCryptCShakeEncodeInputStrings().

◆ SymCryptKeccakAppendEncodeTimes8()

VOID SYMCRYPT_CALL SymCryptKeccakAppendEncodeTimes8 ( _Inout_ SYMCRYPT_KECCAK_STATE *  pState,
UINT64  uValue,
BOOLEAN  bLeftEncode 
)

Definition at line 310 of file shake.c.

315{
316 BYTE encoding[1 + (1 + sizeof(UINT64))];
317 SIZE_T ret;
318
319 ret = SymCryptKeccakEncodeTimes8(uValue, encoding, sizeof(encoding), bLeftEncode);
320
321 SymCryptKeccakAppend(pState, encoding, ret);
322}
COMPILER_DEPENDENT_UINT64 UINT64
Definition: actypes.h:131
return ret
Definition: mutex.c:147
SIZE_T SYMCRYPT_CALL SymCryptKeccakEncodeTimes8(UINT64 uInput, _Out_writes_(cbOutput) PBYTE pbOutput, SIZE_T cbOutput, BOOLEAN bLeftEncode)
Definition: shake.c:254
ULONG_PTR SIZE_T
Definition: typedefs.h:80

Referenced by SYMCRYPT_XxxExpandKeyEx(), SYMCRYPT_XxxExtract(), SYMCRYPT_XxxResultEx(), SymCryptCShakeEncodeInputStrings(), and SymCryptKeccakAppendEncodedString().

◆ SymCryptKeccakEncodeTimes8()

SIZE_T SYMCRYPT_CALL SymCryptKeccakEncodeTimes8 ( UINT64  uInput,
_Out_writes_(cbOutput) PBYTE  pbOutput,
SIZE_T  cbOutput,
BOOLEAN  bLeftEncode 
)

Definition at line 254 of file shake.c.

259{
260 BYTE encoding[1 + sizeof(UINT64)];
261 SIZE_T ret = 0;
262
263 // longest encoding is 1 byte for length + 9 bytes for uInput * 8
264 SYMCRYPT_ASSERT(cbOutput >= (1 + sizeof(encoding)));
265 UNREFERENCED_PARAMETER(cbOutput);
266
267 //
268 // encoding[0] .. encoding[8] will contain (uInput * 8) in big endian form
269 encoding[0] = (BYTE)(uInput >> 61);
270 SYMCRYPT_STORE_MSBFIRST64(&encoding[1], uInput * 8);
271
272 SIZE_T length = 1; // number of bytes required to encode uInput
273 PCBYTE pbMsb = &encoding[sizeof(encoding) - 1]; // pointer to the most significant byte
274
275 // Locate the most significant non-zero byte
276 for (int i = 0; i < sizeof(encoding); i++)
277 {
278 // Do not early terminate on the most significant byte
279 if (encoding[i] != 0 && length == 1)
280 {
281 length = sizeof(encoding) - i;
282 pbMsb = &encoding[i];
283 }
284 }
285
286 ret = 1 + length;
287
288 if (bLeftEncode)
289 {
290 // length for left_encode
291 *pbOutput++ = (BYTE)length;
292 }
293
294 memcpy(pbOutput, pbMsb, length);
295
296 if(!bLeftEncode)
297 {
298 // length for right_encode
299 pbOutput[length] = (BYTE)length;
300 }
301
302 return ret; // total number of bytes written to pbOutput
303}
GLuint GLsizei GLsizei * length
Definition: glext.h:6040
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble const GLfloat const GLdouble const GLfloat GLint i
Definition: glfuncs.h:248
#define memcpy(s1, s2, n)
Definition: mkisofs.h:878
#define UNREFERENCED_PARAMETER(P)
Definition: ntbasedef.h:329
#define SYMCRYPT_STORE_MSBFIRST64(p, v)
Definition: symcrypt.h:312
const BYTE * PCBYTE

Referenced by SymCryptKeccakAppendEncodeTimes8().

◆ SymCryptShake128Selftest()

VOID SYMCRYPT_CALL SymCryptShake128Selftest ( void  )

Definition at line 52 of file shake.c.

53{
55
57
59
60 if (memcmp(result, shake128KATAnswer, sizeof(result)) != 0)
61 {
62 SymCryptFatal('shk1');
63 }
64}
static const BYTE shake128KATAnswer[SYMCRYPT_SHAKE128_RESULT_SIZE]
Definition: shake.c:43
#define SYMCRYPT_SHAKE128_RESULT_SIZE
Definition: symcrypt.h:1908
VOID SYMCRYPT_CALL SymCryptShake128(_In_reads_(cbData) PCBYTE pbData, SIZE_T cbData, _Out_writes_(cbResult) PBYTE pbResult, SIZE_T cbResult)

◆ SymCryptShake256Selftest()

VOID SYMCRYPT_CALL SymCryptShake256Selftest ( void  )

Definition at line 104 of file shake.c.

105{
107
109
111
112 if (memcmp(result, shake256KATAnswer, sizeof(result)) != 0)
113 {
114 SymCryptFatal('shk2');
115 }
116}
static const BYTE shake256KATAnswer[SYMCRYPT_SHAKE256_RESULT_SIZE]
Definition: shake.c:95
VOID SYMCRYPT_CALL SymCryptShake256(_In_reads_(cbData) PCBYTE pbData, SIZE_T cbData, _Out_writes_(cbResult) PBYTE pbResult, SIZE_T cbResult)
#define SYMCRYPT_SHAKE256_RESULT_SIZE
Definition: symcrypt.h:1964

Variable Documentation

◆ cshake128KATAnswer

const BYTE cshake128KATAnswer[SYMCRYPT_CSHAKE128_RESULT_SIZE]
static
Initial value:
= {
0x14, 0xe5, 0xdf, 0xf3, 0xae, 0xfd, 0xfe, 0x8e,
0xa6, 0xae, 0xed, 0xfd, 0x99, 0xe6, 0x84, 0x74,
0xbc, 0x61, 0xb9, 0xd6, 0x17, 0x4e, 0x9f, 0x4a,
0xe3, 0xbd, 0x87, 0xdf, 0x0e, 0xf2, 0x16, 0xdb,
}

Definition at line 137 of file shake.c.

Referenced by SymCryptCShake128Selftest().

◆ cshake256KATAnswer

const BYTE cshake256KATAnswer[SYMCRYPT_CSHAKE256_RESULT_SIZE]
static
Initial value:
= {
0x4d, 0xe8, 0x71, 0x6c, 0x4a, 0x16, 0x7e, 0x28, 0x2c, 0x18, 0xc5, 0x1e, 0xed, 0xa6, 0x00, 0xb8,
0x91, 0x92, 0x4f, 0xea, 0x2e, 0x20, 0x7f, 0x71, 0x2c, 0xfd, 0xe2, 0x95, 0xfd, 0x1c, 0x67, 0x32,
0x31, 0x49, 0x98, 0x23, 0xc0, 0x5e, 0x6a, 0xe3, 0x89, 0xad, 0x4d, 0xa2, 0x32, 0x9c, 0xc9, 0x2e,
0x0f, 0xd6, 0x90, 0xb9, 0xee, 0x91, 0x0e, 0x86, 0xf7, 0x1d, 0x03, 0x88, 0xb5, 0x95, 0x61, 0x95
}

Definition at line 184 of file shake.c.

Referenced by SymCryptCShake256Selftest().

◆ shake128KATAnswer

const BYTE shake128KATAnswer[SYMCRYPT_SHAKE128_RESULT_SIZE]
static
Initial value:
= {
0x58, 0x81, 0x09, 0x2d, 0xd8, 0x18, 0xbf, 0x5c,
0xf8, 0xa3, 0xdd, 0xb7, 0x93, 0xfb, 0xcb, 0xa7,
0x40, 0x97, 0xd5, 0xc5, 0x26, 0xa6, 0xd3, 0x5f,
0x97, 0xb8, 0x33, 0x51, 0x94, 0x0f, 0x2c ,0xc8
}

Definition at line 43 of file shake.c.

Referenced by SymCryptShake128Selftest().

◆ shake256KATAnswer

const BYTE shake256KATAnswer[SYMCRYPT_SHAKE256_RESULT_SIZE]
static
Initial value:
= {
0x48, 0x33, 0x66, 0x60, 0x13, 0x60, 0xa8, 0x77, 0x1c, 0x68, 0x63, 0x08, 0x0c, 0xc4, 0x11, 0x4d,
0x8d, 0xb4, 0x45, 0x30, 0xf8, 0xf1, 0xe1, 0xee, 0x4f, 0x94, 0xea, 0x37, 0xe7, 0x8b, 0x57, 0x39,
0xd5, 0xa1, 0x5b, 0xef, 0x18, 0x6a, 0x53, 0x86, 0xc7, 0x57, 0x44, 0xc0, 0x52, 0x7e, 0x1f, 0xaa,
0x9f, 0x87, 0x26, 0xe4, 0x62, 0xa1, 0x2a, 0x4f, 0xeb, 0x06, 0xbd, 0x88, 0x01, 0xe7, 0x51, 0xe4
}

Definition at line 95 of file shake.c.

Referenced by SymCryptShake256Selftest().

◆ SymCryptShake128HashAlgorithm

Definition at line 41 of file shake.c.

◆ SymCryptShake128HashAlgorithm_default

const SYMCRYPT_HASH SymCryptShake128HashAlgorithm_default
Initial value:
= {
NULL,
}
#define NULL
Definition: types.h:112
VOID SYMCRYPT_CALL SymCryptShake128Append(_Inout_ PSYMCRYPT_SHAKE128_STATE pState, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData)
#define SYMCRYPT_SHAKE128_INPUT_BLOCK_SIZE
Definition: symcrypt.h:1909
VOID SYMCRYPT_CALL SymCryptShake128Result(_Inout_ PSYMCRYPT_SHAKE128_STATE pState, _Out_writes_(SYMCRYPT_SHAKE128_RESULT_SIZE) PBYTE pbResult)
VOID SYMCRYPT_CALL SymCryptShake128Init(_Out_ PSYMCRYPT_SHAKE128_STATE pState)
VOID SYMCRYPT_CALL SymCryptShake128StateCopy(_In_ PCSYMCRYPT_SHAKE128_STATE pSrc, _Out_ PSYMCRYPT_SHAKE128_STATE pDst)
#define SYMCRYPT_FIELD_SIZE(type, field)
SYMCRYPT_MAGIC_FIELD SYMCRYPT_SHAKE128_STATE
#define SYMCRYPT_FIELD_OFFSET(type, field)

Definition at line 28 of file shake.c.

◆ SymCryptShake256HashAlgorithm

Definition at line 93 of file shake.c.

◆ SymCryptShake256HashAlgorithm_default

const SYMCRYPT_HASH SymCryptShake256HashAlgorithm_default
Initial value:
= {
NULL,
}
VOID SYMCRYPT_CALL SymCryptShake256StateCopy(_In_ PCSYMCRYPT_SHAKE256_STATE pSrc, _Out_ PSYMCRYPT_SHAKE256_STATE pDst)
VOID SYMCRYPT_CALL SymCryptShake256Result(_Inout_ PSYMCRYPT_SHAKE256_STATE pState, _Out_writes_(SYMCRYPT_SHAKE256_RESULT_SIZE) PBYTE pbResult)
VOID SYMCRYPT_CALL SymCryptShake256Append(_Inout_ PSYMCRYPT_SHAKE256_STATE pState, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData)
VOID SYMCRYPT_CALL SymCryptShake256Init(_Out_ PSYMCRYPT_SHAKE256_STATE pState)
#define SYMCRYPT_SHAKE256_INPUT_BLOCK_SIZE
Definition: symcrypt.h:1965
SYMCRYPT_MAGIC_FIELD SYMCRYPT_SHAKE256_STATE

Definition at line 80 of file shake.c.