Include dependency graph for hmacsha224.c:
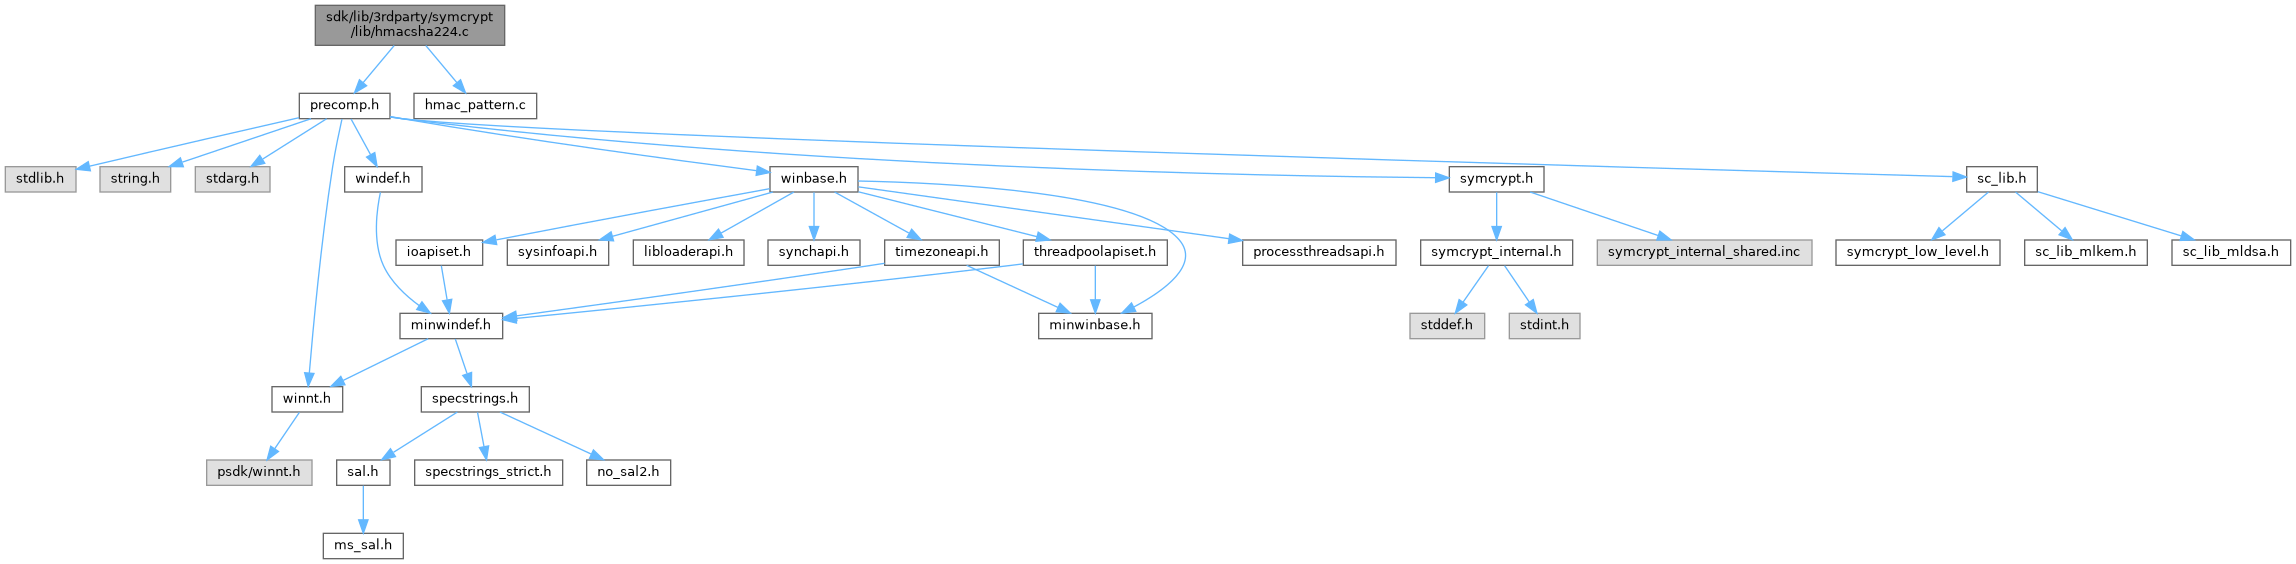
Go to the source code of this file.
Macros | |
| #define | SymCryptSha224AppendBlocks SymCryptSha256AppendBlocks |
| #define | ALG SHA224 |
| #define | Alg Sha224 |
| #define | SET_DATALENGTH(state, len) {state.dataLengthL = len;} |
Functions | |
| VOID SYMCRYPT_CALL | SymCryptHmacSha224Selftest (void) |
Variables | |
| const SYMCRYPT_MAC | SymCryptHmacSha224Algorithm_default |
| const PCSYMCRYPT_MAC | SymCryptHmacSha224Algorithm = &SymCryptHmacSha224Algorithm_default |
| static const BYTE | hmacSha224Kat [28] |
Macro Definition Documentation
◆ ALG
| #define ALG SHA224 |
Definition at line 11 of file hmacsha224.c.
◆ Alg
| #define Alg Sha224 |
Definition at line 12 of file hmacsha224.c.
◆ SET_DATALENGTH
| #define SET_DATALENGTH | ( | state, | |
| len | |||
| ) | {state.dataLengthL = len;} |
Definition at line 13 of file hmacsha224.c.
◆ SymCryptSha224AppendBlocks
| #define SymCryptSha224AppendBlocks SymCryptSha256AppendBlocks |
Definition at line 9 of file hmacsha224.c.
Function Documentation
◆ SymCryptHmacSha224Selftest()
| VOID SYMCRYPT_CALL SymCryptHmacSha224Selftest | ( | void | ) |
Definition at line 43 of file hmacsha224.c.
44{
45 SYMCRYPT_HMAC_SHA224_EXPANDED_KEY xKey;
47
50
52
54 {
56 }
57
58 //
59 // Normally we would wipe the expanded key structure here,
60 // but as this is a selftest with known data this is not needed.
61 //
62}
VOID SYMCRYPT_CALL SymCryptInjectError(PBYTE pbData, SIZE_T cbData)
_Analysis_noreturn_ VOID SYMCRYPT_CALL SymCryptFatal(UINT32 fatalCode)
SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptHmacSha224ExpandKey(_Out_ PSYMCRYPT_HMAC_SHA224_EXPANDED_KEY pExpandedKey, _In_reads_opt_(cbKey) PCBYTE pbKey, SIZE_T cbKey)
VOID SYMCRYPT_CALL SymCryptHmacSha224(_In_ PCSYMCRYPT_HMAC_SHA224_EXPANDED_KEY pExpandedKey, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData, _Out_writes_(SYMCRYPT_HMAC_SHA224_RESULT_SIZE) PBYTE pbResult)
SYMCRYPT_MAGIC_FIELD SYMCRYPT_HMAC_SHA224_EXPANDED_KEY
Definition: symcrypt_internal.h:1367
Variable Documentation
◆ hmacSha224Kat
Initial value:
= {
0x3e, 0x1c, 0x48, 0x2f, 0x66, 0x49, 0x67, 0xa9,
0xad, 0x4f, 0x76, 0x52, 0x36, 0xf8, 0x5a, 0x1f,
0x63, 0x5b, 0x34, 0xe9, 0x35, 0x71, 0x62, 0x35,
0xa2, 0x9e, 0x61, 0xb1
}
Definition at line 33 of file hmacsha224.c.
Referenced by SymCryptHmacSha224Selftest().
◆ SymCryptHmacSha224Algorithm
| const PCSYMCRYPT_MAC SymCryptHmacSha224Algorithm = &SymCryptHmacSha224Algorithm_default |
Definition at line 31 of file hmacsha224.c.
◆ SymCryptHmacSha224Algorithm_default
| const SYMCRYPT_MAC SymCryptHmacSha224Algorithm_default |
Initial value:
= {
sizeof(SYMCRYPT_HMAC_SHA224_EXPANDED_KEY),
sizeof(SYMCRYPT_HMAC_SHA224_STATE),
}
VOID SYMCRYPT_CALL SymCryptHmacSha224Append(_Inout_ PSYMCRYPT_HMAC_SHA224_STATE pState, _In_reads_(cbData) PCBYTE pbData, SIZE_T cbData)
VOID SYMCRYPT_CALL SymCryptHmacSha224Result(_Inout_ PSYMCRYPT_HMAC_SHA224_STATE pState, _Out_writes_(SYMCRYPT_HMAC_SHA224_RESULT_SIZE) PBYTE pbResult)
VOID SYMCRYPT_CALL SymCryptHmacSha224Init(_Out_ PSYMCRYPT_HMAC_SHA224_STATE pState, _In_ PCSYMCRYPT_HMAC_SHA224_EXPANDED_KEY pExpandedKey)
SYMCRYPT_MAGIC_FIELD SYMCRYPT_HMAC_SHA224_STATE
Definition: symcrypt_internal.h:1380
Definition at line 19 of file hmacsha224.c.
