ReactOS 0.4.17-dev-1005-g171e1de
aeskw.c File Reference
#include "precomp.h"
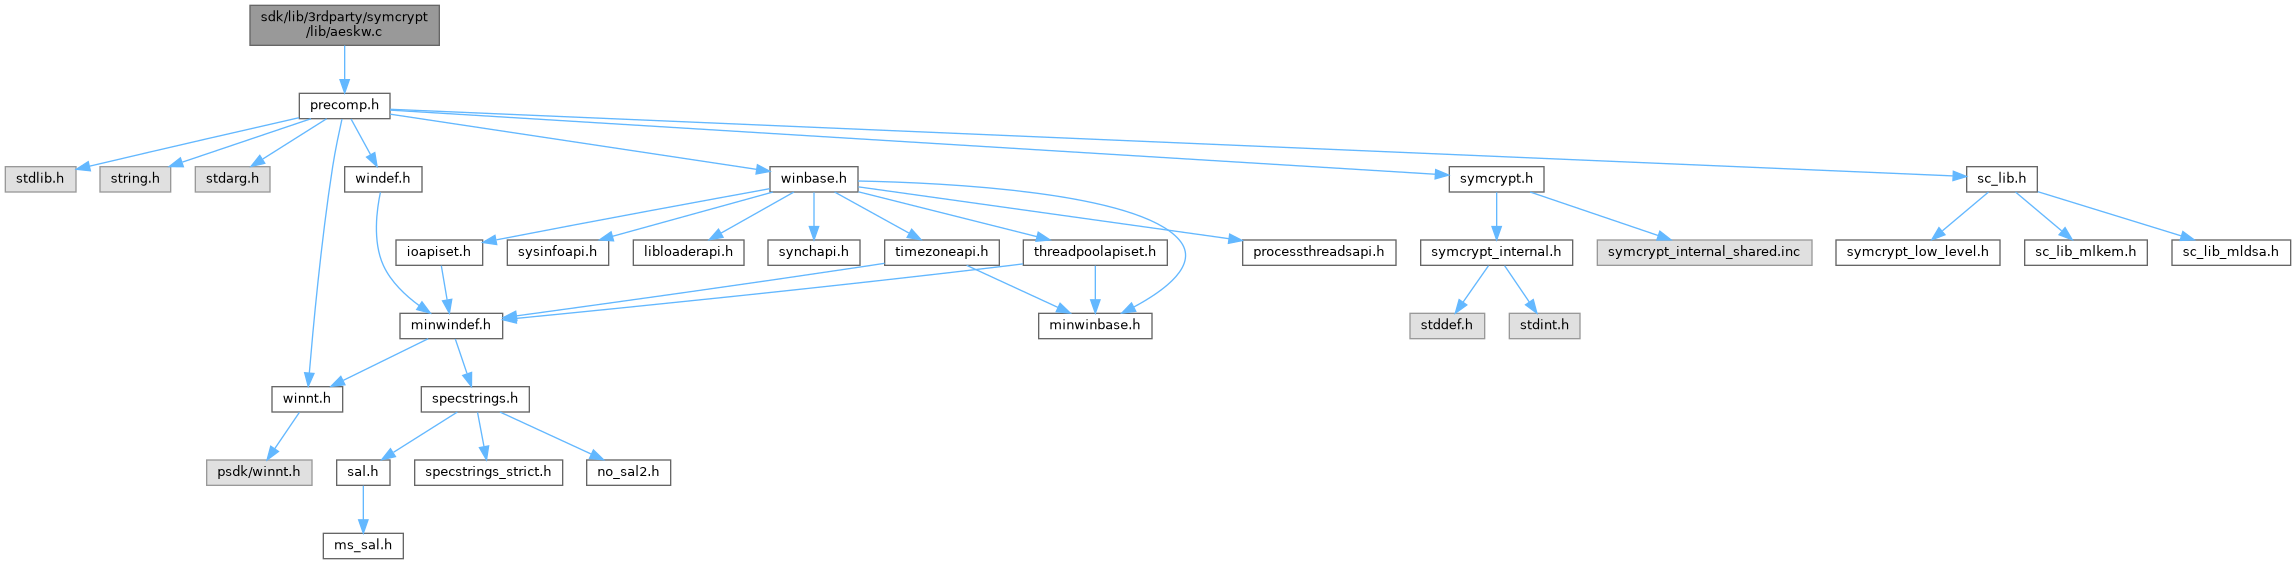
Include dependency graph for aeskw.c:

Go to the source code of this file.

Macros

#define SYMCRYPT_AES_SEMIBLOCK_SIZE   (SYMCRYPT_AES_BLOCK_SIZE / 2)
 

Functions

static VOID SYMCRYPT_CALL SymCryptAesKwxInternalWrap (_In_ PCSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _Inout_updates_bytes_(cbBuf) PBYTE pbBuf, UINT32 cbBuf)
 
static VOID SYMCRYPT_CALL SymCryptAesKwxInternalUnwrap (_In_ PCSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _Inout_updates_bytes_(cbBuf) PBYTE pbBuf, UINT32 cbBuf)
 
SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesKwEncrypt (_In_ PCSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _In_reads_(cbSrc) PCBYTE pbSrc, SIZE_T cbSrc, _Out_writes_to_(cbDst, *pcbResult) PBYTE pbDst, SIZE_T cbDst, _Out_ SIZE_T *pcbResult)
 
SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesKwDecrypt (_In_ PCSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _In_reads_(cbSrc) PCBYTE pbSrc, SIZE_T cbSrc, _Out_writes_to_(cbDst, *pcbResult) PBYTE pbDst, SIZE_T cbDst, _Out_ SIZE_T *pcbResult)
 
SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesKwpEncrypt (_In_ PCSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _In_reads_(cbSrc) PCBYTE pbSrc, SIZE_T cbSrc, _Out_writes_to_(cbDst, *pcbResult) PBYTE pbDst, SIZE_T cbDst, _Out_ SIZE_T *pcbResult)
 
SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesKwpDecrypt (_In_ PCSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _In_reads_(cbSrc) PCBYTE pbSrc, SIZE_T cbSrc, _Out_writes_to_(cbDst, *pcbResult) PBYTE pbDst, SIZE_T cbDst, _Out_ SIZE_T *pcbResult)
 

Variables

const UINT64 SymCryptAesKwDefaultICV = 0xA6A6A6A6A6A6A6A6
 
const UINT32 SymCryptAesKwpDefaultICV = 0xA65959A6
 
const SIZE_T SymCryptAesKWMinPlaintextLen = 16u
 
const SIZE_T SymCryptAesKWMaxPlaintextLen = (1u<<31)-8
 
const SIZE_T SymCryptAesKWMinCiphertextLen = 24u
 
const SIZE_T SymCryptAesKWMaxCiphertextLen = (1u<<31)
 
const SIZE_T SymCryptAesKWPMinPlaintextLen = 1u
 
const SIZE_T SymCryptAesKWPMaxPlaintextLen = (1u<<31)-8
 
const SIZE_T SymCryptAesKWPMinCiphertextLen = 16u
 
const SIZE_T SymCryptAesKWPMaxCiphertextLen = (1u<<31)
 

Macro Definition Documentation

◆ SYMCRYPT_AES_SEMIBLOCK_SIZE

#define SYMCRYPT_AES_SEMIBLOCK_SIZE   (SYMCRYPT_AES_BLOCK_SIZE / 2)

Definition at line 33 of file aeskw.c.

Function Documentation

◆ SymCryptAesKwDecrypt()

SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesKwDecrypt ( _In_ PCSYMCRYPT_AES_EXPANDED_KEY  pExpandedKey,
_In_reads_(cbSrc) PCBYTE  pbSrc,
SIZE_T  cbSrc,
_Out_writes_to_(cbDst, *pcbResult) PBYTE  pbDst,
SIZE_T  cbDst,
_Out_ SIZE_T *  pcbResult 
)

Definition at line 228 of file aeskw.c.

235{
236 SYMCRYPT_ERROR scError = SYMCRYPT_NO_ERROR;
237 PBYTE pbScratch = NULL;
238 UINT32 cbScratch = 0;
239
240 if( (cbSrc < SymCryptAesKWMinCiphertextLen) ||
242 ((cbSrc & (SYMCRYPT_AES_SEMIBLOCK_SIZE-1)) != 0) )
243 {
244 scError = SYMCRYPT_INVALID_ARGUMENT;
245 goto cleanup;
246 }
247
248 cbScratch = (UINT32) cbSrc;
250 {
251 scError = SYMCRYPT_BUFFER_TOO_SMALL;
252 goto cleanup;
253 }
254
255 pbScratch = SymCryptCallbackAlloc( cbScratch );
256 if( pbScratch == NULL )
257 {
258 scError = SYMCRYPT_MEMORY_ALLOCATION_FAILURE;
259 goto cleanup;
260 }
261
262 // set up input buffer as C
263 memcpy( pbScratch, pbSrc, cbSrc );
264
265 // decrypt input buffer in place
267
268 // check first semi-block has the expected value
270 {
271 scError = SYMCRYPT_AUTHENTICATION_FAILURE;
272 goto cleanup;
273 }
274
275 // copy decrypted buffer to output
278
279cleanup:
280 if( pbScratch != NULL )
281 {
282 SymCryptWipe( pbScratch, cbScratch );
283 SymCryptCallbackFree( pbScratch );
284 }
285 return scError;
286
287}
const UINT64 SymCryptAesKwDefaultICV
Definition: aeskw.c:31
static VOID SYMCRYPT_CALL SymCryptAesKwxInternalUnwrap(_In_ PCSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _Inout_updates_bytes_(cbBuf) PBYTE pbBuf, UINT32 cbBuf)
Definition: aeskw.c:116
const SIZE_T SymCryptAesKWMinCiphertextLen
Definition: aeskw.c:37
const SIZE_T SymCryptAesKWMaxCiphertextLen
Definition: aeskw.c:38
#define SYMCRYPT_AES_SEMIBLOCK_SIZE
Definition: aeskw.c:33
#define NULL
Definition: types.h:112
static void cleanup(void)
Definition: main.c:1335
void SYMCRYPT_CALL SymCryptCallbackFree(void *ptr)
Definition: implglue.c:42
void *SYMCRYPT_CALL SymCryptCallbackAlloc(SIZE_T size)
Definition: implglue.c:37
#define memcpy(s1, s2, n)
Definition: mkisofs.h:878
BYTE * PBYTE
Definition: pedump.c:66
UINT32 UINT32 UINT32 UINT32 cbScratch
VOID SYMCRYPT_CALL SymCryptWipe(_Out_writes_bytes_(cbData) PVOID pbData, SIZE_T cbData)
Definition: libmain.c:137
#define SYMCRYPT_LOAD_LSBFIRST64(p)
Definition: symcrypt.h:300
SYMCRYPT_ERROR
Definition: symcrypt.h:227
PCBYTE pbSrc
PCBYTE PBYTE pbDst
PCVOID pExpandedKey
uint32_t UINT32
Definition: typedefs.h:59

◆ SymCryptAesKwEncrypt()

SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesKwEncrypt ( _In_ PCSYMCRYPT_AES_EXPANDED_KEY  pExpandedKey,
_In_reads_(cbSrc) PCBYTE  pbSrc,
SIZE_T  cbSrc,
_Out_writes_to_(cbDst, *pcbResult) PBYTE  pbDst,
SIZE_T  cbDst,
_Out_ SIZE_T *  pcbResult 
)

Definition at line 172 of file aeskw.c.

179{
180 SYMCRYPT_ERROR scError = SYMCRYPT_NO_ERROR;
181 PBYTE pbScratch = NULL;
182 UINT32 cbScratch = 0;
183
184 if( (cbSrc < SymCryptAesKWMinPlaintextLen) ||
186 ((cbSrc & (SYMCRYPT_AES_SEMIBLOCK_SIZE-1)) != 0) )
187 {
188 scError = SYMCRYPT_INVALID_ARGUMENT;
189 goto cleanup;
190 }
191
193 if( cbDst < cbScratch )
194 {
195 scError = SYMCRYPT_BUFFER_TOO_SMALL;
196 goto cleanup;
197 }
198
199 pbScratch = SymCryptCallbackAlloc( cbScratch );
200 if( pbScratch == NULL )
201 {
202 scError = SYMCRYPT_MEMORY_ALLOCATION_FAILURE;
203 goto cleanup;
204 }
205
206 // set up input buffer as ICV1 || P
208 memcpy( pbScratch+8, pbSrc, cbSrc );
209
210 // encrypt input buffer in place
212
213 // copy encrypted buffer to output
214 memcpy( pbDst, pbScratch, cbScratch );
215 *pcbResult = cbScratch;
216
217cleanup:
218 if( pbScratch != NULL )
219 {
220 SymCryptWipe( pbScratch, cbScratch );
221 SymCryptCallbackFree( pbScratch );
222 }
223 return scError;
224}
const SIZE_T SymCryptAesKWMinPlaintextLen
Definition: aeskw.c:35
const SIZE_T SymCryptAesKWMaxPlaintextLen
Definition: aeskw.c:36
static VOID SYMCRYPT_CALL SymCryptAesKwxInternalWrap(_In_ PCSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _Inout_updates_bytes_(cbBuf) PBYTE pbBuf, UINT32 cbBuf)
Definition: aeskw.c:54
#define SYMCRYPT_STORE_LSBFIRST64(p, v)
Definition: symcrypt.h:308

◆ SymCryptAesKwpDecrypt()

SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesKwpDecrypt ( _In_ PCSYMCRYPT_AES_EXPANDED_KEY  pExpandedKey,
_In_reads_(cbSrc) PCBYTE  pbSrc,
SIZE_T  cbSrc,
_Out_writes_to_(cbDst, *pcbResult) PBYTE  pbDst,
SIZE_T  cbDst,
_Out_ SIZE_T *  pcbResult 
)

Definition at line 365 of file aeskw.c.

372{
373 SYMCRYPT_ERROR scError = SYMCRYPT_NO_ERROR;
374 PBYTE pbScratch = NULL;
375 UINT32 cbScratch = 0;
376 UINT32 cbPlaintext = 0;
377 UINT32 cbPad = 0;
378 UINT32 mVerificationError = 0; // Mask indicating whether the decrypted buffer is malformed
379 UINT32 mIsPlaintext = 0; // Mask for plaintext bytes in the final semi-block
380
381 if( (cbSrc < SymCryptAesKWPMinCiphertextLen) ||
383 ((cbSrc & (SYMCRYPT_AES_SEMIBLOCK_SIZE-1)) != 0) )
384 {
385 scError = SYMCRYPT_INVALID_ARGUMENT;
386 goto cleanup;
387 }
388
389 cbScratch = (UINT32) cbSrc;
391 {
392 scError = SYMCRYPT_BUFFER_TOO_SMALL;
393 goto cleanup;
394 }
395
396 pbScratch = SymCryptCallbackAlloc( cbScratch );
397 if( pbScratch == NULL )
398 {
399 scError = SYMCRYPT_MEMORY_ALLOCATION_FAILURE;
400 goto cleanup;
401 }
402
403 // set up input buffer as C
404 memcpy( pbScratch, pbSrc, cbSrc );
405
406 // decrypt input buffer in place
408 {
409 // special case for AES-KWP with small ciphertext
410 SymCryptAesDecrypt( pExpandedKey, pbScratch, pbScratch );
411 } else {
413 }
414
415 // Check if the decrypted buffer is of an expected form
416 // check bytes [0..3] are expected ICV
417 mVerificationError |= SYMCRYPT_LOAD_LSBFIRST32( pbScratch ) ^ SymCryptAesKwpDefaultICV;
418
419 // check bytes [4..7] are a valid plaintext length (i.e. computed cbPad in range [0,7])
420 cbPlaintext = SYMCRYPT_LOAD_MSBFIRST32( pbScratch+4 );
421 cbPad = (UINT32) cbSrc - cbPlaintext - SYMCRYPT_AES_SEMIBLOCK_SIZE;
422 mVerificationError |= (cbPad & 0xfffffff8);
423
424 // check that padding is all 0s
425 for( UINT32 i = 1; i<SYMCRYPT_AES_SEMIBLOCK_SIZE; i++ )
426 {
427 mIsPlaintext = SymCryptMask32LtU31(i, SYMCRYPT_AES_SEMIBLOCK_SIZE-(cbPad&7));
428 mVerificationError |= ((UINT32) pbScratch[ cbScratch-SYMCRYPT_AES_SEMIBLOCK_SIZE+i ]) & ~mIsPlaintext;
429 }
430
431 // Now if there was any verification error, we fail
432 if( mVerificationError != 0 )
433 {
434 scError = SYMCRYPT_AUTHENTICATION_FAILURE;
435 goto cleanup;
436 }
437
438 // We are variable time w.r.t. the plaintext length on success
439 if( cbDst < cbPlaintext )
440 {
441 scError = SYMCRYPT_BUFFER_TOO_SMALL;
442 goto cleanup;
443 }
444
445 // copy decrypted buffer to output
446 memcpy( pbDst, pbScratch+SYMCRYPT_AES_SEMIBLOCK_SIZE, cbPlaintext );
447 *pcbResult = cbPlaintext;
448
449cleanup:
450 if( pbScratch != NULL )
451 {
452 SymCryptWipe( pbScratch, cbScratch );
453 SymCryptCallbackFree( pbScratch );
454 }
455 return scError;
456
457}
const SIZE_T SymCryptAesKWPMinCiphertextLen
Definition: aeskw.c:42
const SIZE_T SymCryptAesKWPMaxCiphertextLen
Definition: aeskw.c:43
const UINT32 SymCryptAesKwpDefaultICV
Definition: aeskw.c:32
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble const GLfloat const GLdouble const GLfloat GLint i
Definition: glfuncs.h:248
#define SYMCRYPT_LOAD_MSBFIRST32(p)
Definition: symcrypt.h:303
VOID SYMCRYPT_CALL SymCryptAesDecrypt(_In_ PCSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _In_reads_(SYMCRYPT_AES_BLOCK_SIZE) PCBYTE pbSrc, _Out_writes_(SYMCRYPT_AES_BLOCK_SIZE) PBYTE pbDst)
Definition: aes-default.c:134
#define SYMCRYPT_LOAD_LSBFIRST32(p)
Definition: symcrypt.h:299
#define SYMCRYPT_AES_BLOCK_SIZE
Definition: symcrypt.h:4255
UINT32 SYMCRYPT_CALL SymCryptMask32LtU31(UINT32 a, UINT32 b)
Definition: scsTools.c:53

◆ SymCryptAesKwpEncrypt()

SYMCRYPT_ERROR SYMCRYPT_CALL SymCryptAesKwpEncrypt ( _In_ PCSYMCRYPT_AES_EXPANDED_KEY  pExpandedKey,
_In_reads_(cbSrc) PCBYTE  pbSrc,
SIZE_T  cbSrc,
_Out_writes_to_(cbDst, *pcbResult) PBYTE  pbDst,
SIZE_T  cbDst,
_Out_ SIZE_T *  pcbResult 
)

Definition at line 291 of file aeskw.c.

298{
299 SYMCRYPT_ERROR scError = SYMCRYPT_NO_ERROR;
300 PBYTE pbScratch = NULL;
301 UINT32 cbScratch = 0;
302 UINT32 cbPad = 0;
303
304 if( (cbSrc < SymCryptAesKWPMinPlaintextLen) ||
306 {
307 scError = SYMCRYPT_INVALID_ARGUMENT;
308 goto cleanup;
309 }
310
312 if( cbPad == SYMCRYPT_AES_SEMIBLOCK_SIZE )
313 {
314 cbPad = 0;
315 }
316
317 cbScratch = (UINT32) cbSrc + SYMCRYPT_AES_SEMIBLOCK_SIZE + cbPad;
318 if( cbDst < cbScratch )
319 {
320 scError = SYMCRYPT_BUFFER_TOO_SMALL;
321 goto cleanup;
322 }
323
324 SYMCRYPT_ASSERT( cbScratch >= 16 );
325
326 pbScratch = SymCryptCallbackAlloc( cbScratch );
327 if( pbScratch == NULL )
328 {
329 scError = SYMCRYPT_MEMORY_ALLOCATION_FAILURE;
330 goto cleanup;
331 }
332
333 // set up input buffer as ICV2 || len(P) || P || PAD
335 SYMCRYPT_STORE_MSBFIRST32( pbScratch+4, (UINT32) cbSrc );
336 // pad by unconditionally setting the last 8 bytes to 0
337 // then overwrite some or all of the padding bytes with plaintext
339 memcpy( pbScratch+8, pbSrc, cbSrc );
340
341 // encrypt input buffer in place
343 {
344 // special case for AES-KWP with small plaintext
345 SymCryptAesEncrypt( pExpandedKey, pbScratch, pbScratch );
346 } else {
348 }
349
350 // copy encrypted buffer to output
351 memcpy( pbDst, pbScratch, cbScratch );
352 *pcbResult = cbScratch;
353
354cleanup:
355 if( pbScratch != NULL )
356 {
357 SymCryptWipe( pbScratch, cbScratch );
358 SymCryptCallbackFree( pbScratch );
359 }
360 return scError;
361}
const SIZE_T SymCryptAesKWPMaxPlaintextLen
Definition: aeskw.c:41
const SIZE_T SymCryptAesKWPMinPlaintextLen
Definition: aeskw.c:40
GLsizei GLenum const GLvoid GLsizei GLenum GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLint GLint GLint GLshort GLshort GLshort GLubyte GLubyte GLubyte GLuint GLuint GLuint GLushort GLushort GLushort GLbyte GLbyte GLbyte GLbyte GLdouble GLdouble GLdouble GLdouble GLfloat GLfloat GLfloat GLfloat GLint GLint GLint GLint GLshort GLshort GLshort GLshort GLubyte GLubyte GLubyte GLubyte GLuint GLuint GLuint GLuint GLushort GLushort GLushort GLushort GLboolean const GLdouble const GLfloat const GLint const GLshort const GLbyte const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLdouble const GLfloat const GLfloat const GLint const GLint const GLshort const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort const GLdouble const GLfloat const GLint const GLshort GLenum GLenum GLenum GLfloat GLenum GLint GLenum GLenum GLenum GLfloat GLenum GLenum GLint GLenum GLfloat GLenum GLint GLint GLushort GLenum GLenum GLfloat GLenum GLenum GLint GLfloat const GLubyte GLenum GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLint GLint GLsizei GLsizei GLint GLenum GLenum const GLvoid GLenum GLenum const GLfloat GLenum GLenum const GLint GLenum GLenum const GLdouble GLenum GLenum const GLfloat GLenum GLenum const GLint GLsizei GLuint GLfloat GLuint GLbitfield GLfloat GLint GLuint GLboolean GLenum GLfloat GLenum GLbitfield GLenum GLfloat GLfloat GLint GLint const GLfloat GLenum GLfloat GLfloat GLint GLint GLfloat GLfloat GLint GLint const GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat GLint GLfloat GLfloat const GLdouble * u
Definition: glfuncs.h:240
#define SYMCRYPT_ASSERT(_x)
Definition: symcrypt.h:10807
VOID SYMCRYPT_CALL SymCryptAesEncrypt(_In_ PCSYMCRYPT_AES_EXPANDED_KEY pExpandedKey, _In_reads_(SYMCRYPT_AES_BLOCK_SIZE) PCBYTE pbSrc, _Out_writes_(SYMCRYPT_AES_BLOCK_SIZE) PBYTE pbDst)
Definition: aes-default.c:95
#define SYMCRYPT_STORE_LSBFIRST32(p, v)
Definition: symcrypt.h:307
#define SYMCRYPT_STORE_MSBFIRST32(p, v)
Definition: symcrypt.h:311

◆ SymCryptAesKwxInternalUnwrap()

static VOID SYMCRYPT_CALL SymCryptAesKwxInternalUnwrap ( _In_ PCSYMCRYPT_AES_EXPANDED_KEY  pExpandedKey,
_Inout_updates_bytes_(cbBuf) PBYTE  pbBuf,
UINT32  cbBuf 
)
static

Definition at line 116 of file aeskw.c.

120{
122 const UINT32 nSemiBlocks = cbBuf / SYMCRYPT_AES_SEMIBLOCK_SIZE; // n per SP 800-38F
123 UINT64 decryptionIdx = 6*(nSemiBlocks-1); // t per SP 800-38F
124 UINT64 lowHalfTemp = 0;
125
129
130 // Special case for first decryption
131 // Initialize the low half temporary with the first semi-block of input
132 lowHalfTemp = SYMCRYPT_LOAD_LSBFIRST64( pbBuf );
133
134 for( UINT32 outerLoopCnt = 0; outerLoopCnt < 6; outerLoopCnt++ )
135 {
136 for( UINT32 innerLoopCnt = nSemiBlocks-1; innerLoopCnt > 0; innerLoopCnt-- )
137 {
138 SIZE_T bufOffset = innerLoopCnt*SYMCRYPT_AES_SEMIBLOCK_SIZE;
139
140 // Update low half with decryptionIdx and store to low half of active block
141 lowHalfTemp ^= SYMCRYPT_BSWAP64( decryptionIdx );
142 SYMCRYPT_STORE_LSBFIRST64( activeBlock, lowHalfTemp );
143
144 // Initialize the high half of active block to semi-block from buf
145 memcpy( activeBlock+SYMCRYPT_AES_SEMIBLOCK_SIZE, pbBuf+bufOffset, SYMCRYPT_AES_SEMIBLOCK_SIZE);
146
147 // Decrypt activeBlock in place
148 SymCryptAesDecrypt( pExpandedKey, activeBlock, activeBlock );
149
150 // Store the high half of result back to semi-block from buf
151 memcpy( pbBuf+bufOffset, activeBlock+SYMCRYPT_AES_SEMIBLOCK_SIZE, SYMCRYPT_AES_SEMIBLOCK_SIZE );
152
153 // Update decryptionIdx
154 decryptionIdx--;
155
156 // Use the low half of the result to set the low half temporary
157 lowHalfTemp = SYMCRYPT_LOAD_LSBFIRST64( activeBlock );
158 }
159 }
160
161 SYMCRYPT_ASSERT( decryptionIdx == 0 );
162
163 // Special case for last decryption
164 // Store the final low half of decryption as the first semi-block of output
165 SYMCRYPT_STORE_LSBFIRST64( pbBuf, lowHalfTemp );
166
167 SymCryptWipeKnownSize( activeBlock, sizeof(activeBlock) );
168}
COMPILER_DEPENDENT_UINT64 UINT64
Definition: actypes.h:131
FORCEINLINE VOID SYMCRYPT_CALL SymCryptWipeKnownSize(_Out_writes_bytes_(cbData) PVOID pbData, SIZE_T cbData)
#define SYMCRYPT_ALIGN
ULONG_PTR SIZE_T
Definition: typedefs.h:80
unsigned char BYTE
Definition: xxhash.c:193

Referenced by SymCryptAesKwDecrypt(), and SymCryptAesKwpDecrypt().

◆ SymCryptAesKwxInternalWrap()

static VOID SYMCRYPT_CALL SymCryptAesKwxInternalWrap ( _In_ PCSYMCRYPT_AES_EXPANDED_KEY  pExpandedKey,
_Inout_updates_bytes_(cbBuf) PBYTE  pbBuf,
UINT32  cbBuf 
)
static

Definition at line 54 of file aeskw.c.

58{
60 const UINT32 nSemiBlocks = cbBuf / SYMCRYPT_AES_SEMIBLOCK_SIZE; // n per SP 800-38F
61 UINT64 encryptionIdx = 1; // t per SP 800-38F
62 UINT64 lowHalfTemp = 0;
63
67
68 // Special case for first encryption
69 // Initialize the low half of active block with the first semi-block of input
70 memcpy( activeBlock, pbBuf, SYMCRYPT_AES_SEMIBLOCK_SIZE);
71
72 for( UINT32 outerLoopCnt = 0; outerLoopCnt < 6; outerLoopCnt++ )
73 {
74 for( UINT32 innerLoopCnt = 1; innerLoopCnt < nSemiBlocks; innerLoopCnt++ )
75 {
76 SIZE_T bufOffset = innerLoopCnt*SYMCRYPT_AES_SEMIBLOCK_SIZE;
77
78 // Initialize the high half of active block to semi-block from buf
80
81 // Encrypt activeBlock in place
82 SymCryptAesEncrypt( pExpandedKey, activeBlock, activeBlock );
83
84 // Store the high half of result back to semi-block from buf
85 memcpy( pbBuf+bufOffset, activeBlock+SYMCRYPT_AES_SEMIBLOCK_SIZE, SYMCRYPT_AES_SEMIBLOCK_SIZE );
86
87 // Use the low half of the result and the next encryptionIdx to
88 // initialize the low half of the next encryption
89 lowHalfTemp = SYMCRYPT_LOAD_LSBFIRST64( activeBlock );
90 lowHalfTemp ^= SYMCRYPT_BSWAP64( encryptionIdx );
91 SYMCRYPT_STORE_LSBFIRST64( activeBlock, lowHalfTemp );
92
93 // Update encryptionIdx
94 encryptionIdx++;
95 }
96 }
97
98 SYMCRYPT_ASSERT( (encryptionIdx-1) == (nSemiBlocks-1)*6 );
99
100 // Special case for last encryption
101 // Store the final low half of encryption as the first semi-block of output
102 SYMCRYPT_STORE_LSBFIRST64( pbBuf, lowHalfTemp );
103
104 SymCryptWipeKnownSize( activeBlock, sizeof(activeBlock) );
105}

Referenced by SymCryptAesKwEncrypt(), and SymCryptAesKwpEncrypt().

Variable Documentation

◆ SymCryptAesKwDefaultICV

const UINT64 SymCryptAesKwDefaultICV = 0xA6A6A6A6A6A6A6A6

Definition at line 31 of file aeskw.c.

Referenced by SymCryptAesKwDecrypt(), and SymCryptAesKwEncrypt().

◆ SymCryptAesKWMaxCiphertextLen

const SIZE_T SymCryptAesKWMaxCiphertextLen = (1u<<31)

◆ SymCryptAesKWMaxPlaintextLen

const SIZE_T SymCryptAesKWMaxPlaintextLen = (1u<<31)-8

Definition at line 36 of file aeskw.c.

Referenced by SymCryptAesKwEncrypt().

◆ SymCryptAesKWMinCiphertextLen

const SIZE_T SymCryptAesKWMinCiphertextLen = 24u

◆ SymCryptAesKWMinPlaintextLen

const SIZE_T SymCryptAesKWMinPlaintextLen = 16u

Definition at line 35 of file aeskw.c.

Referenced by SymCryptAesKwEncrypt().

◆ SymCryptAesKwpDefaultICV

const UINT32 SymCryptAesKwpDefaultICV = 0xA65959A6

Definition at line 32 of file aeskw.c.

Referenced by SymCryptAesKwpDecrypt(), and SymCryptAesKwpEncrypt().

◆ SymCryptAesKWPMaxCiphertextLen

const SIZE_T SymCryptAesKWPMaxCiphertextLen = (1u<<31)

Definition at line 43 of file aeskw.c.

Referenced by SymCryptAesKwpDecrypt().

◆ SymCryptAesKWPMaxPlaintextLen

const SIZE_T SymCryptAesKWPMaxPlaintextLen = (1u<<31)-8

Definition at line 41 of file aeskw.c.

Referenced by SymCryptAesKwpEncrypt().

◆ SymCryptAesKWPMinCiphertextLen

const SIZE_T SymCryptAesKWPMinCiphertextLen = 16u

Definition at line 42 of file aeskw.c.

Referenced by SymCryptAesKwpDecrypt().

◆ SymCryptAesKWPMinPlaintextLen

const SIZE_T SymCryptAesKWPMinPlaintextLen = 1u

Definition at line 40 of file aeskw.c.

Referenced by SymCryptAesKwpEncrypt().